❌

Visualização normal

Antes de ontemStream principal
  • ✇The CyberWire
  • Who owns your AI conversations?
    This week, Dave and Ben look at two AI-related stories. The first involves the recent bankruptcy of Character.AI and the DoJ's privacy concerns related to the sale of AI chats. The other story looks at a lawsuit involving ChatGpt being sued after its chatbot allegedly contributed to a woman's seizure.
     

Who owns your AI conversations?

5 de Novembro de 2026, 03:00
This week, Dave and Ben look at two AI-related stories. The first involves the recent bankruptcy of Character.AI and the DoJ's privacy concerns related to the sale of AI chats. The other story looks at a lawsuit involving ChatGpt being sued after its chatbot allegedly contributed to a woman's seizure.

  • ✇The CyberWire
  • The AI election.
    This week, Dave and Ben look at how political campaigns are looking to utilize AI chatbots in their campaign messaging efforts alongside another story involving a woman who is facing years in prison after she was a victim of identity theft. Additionally, Ben meets with ⁠⁠⁠⁠Gary Barlet⁠, ⁠Illumio⁠’s public sector CTO, to discuss election security.
     

The AI election.

29 de Outubro de 2026, 17:00
This week, Dave and Ben look at how political campaigns are looking to utilize AI chatbots in their campaign messaging efforts alongside another story involving a woman who is facing years in prison after she was a victim of identity theft. Additionally, Ben meets with ⁠⁠⁠⁠Gary Barlet⁠, ⁠Illumio⁠’s public sector CTO, to discuss election security.

  • ✇Graham Cluley
  • Smashing Security podcast #490: How Jared Kushner’s iPhone was allegedly hacked twice Graham Cluley
    Dutch spies, Russian hackers and Jared Kushner’s iPhone. It sounds like the ingredients for a thriller, but according to claims in a new book the US President's son-in-law may have been hacked twice. Is any of it true, and what does it tell us about the phones in our pockets? Meanwhile, James Ball explains that of the internet’s most trusted security keys were protected by numbers so small that one of them was... four. Yes, "4". And then, of course, to make the week worse we suffered a PHPoca
     

Smashing Security podcast #490: How Jared Kushner’s iPhone was allegedly hacked twice

28 de Outubro de 2026, 21:16
Dutch spies, Russian hackers and Jared Kushner’s iPhone. It sounds like the ingredients for a thriller, but according to claims in a new book the US President's son-in-law may have been hacked twice. Is any of it true, and what does it tell us about the phones in our pockets? Meanwhile, James Ball explains that of the internet’s most trusted security keys were protected by numbers so small that one of them was... four. Yes, "4". And then, of course, to make the week worse we suffered a PHPocalpyse... Plus, Chuck Randolph of 360 Privacy explains how the internet has made it scarily easy to put company executives and public officials in danger. All this and more in episode 490 of the “Smashing Security” podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest James Ball.
  • ✇The CyberWire
  • The wearable wiretap.
    This week, Dave and Ben look at a story that discusses the potential conflict between the next-generation of wearable technology and current state wiretapping laws. The two also look at a recent legal victory for AI coders. Additionally, Dave meets with ⁠Danny Manimbo⁠, the ISO and AI Practice Leader at ⁠Schellman⁠, to discuss why companies waiting for AI regulatory clarity are already falling behind.
     

The wearable wiretap.

22 de Outubro de 2026, 02:00
This week, Dave and Ben look at a story that discusses the potential conflict between the next-generation of wearable technology and current state wiretapping laws. The two also look at a recent legal victory for AI coders. Additionally, Dave meets with ⁠Danny Manimbo⁠, the ISO and AI Practice Leader at ⁠Schellman⁠, to discuss why companies waiting for AI regulatory clarity are already falling behind.

  • ✇The CyberWire
  • Who’s liable when AI goes rogue?
    This week, Dave and Ben look at two stories with the first involving a recent bill introduced into the US House of Representatives that looks to clarify the confusion around AI liability. The second story involves a court case where an AI generated video was able to sway a judge's opinion. Additionally, Dave sits down with ⁠⁠Garfield Jones⁠, Senior Vice President of Research and Strategy at ⁠QuSecure⁠ and former CISA Homeland security exec for quantum, to discuss post-quantum migration efforts
     

Who’s liable when AI goes rogue?

15 de Outubro de 2026, 02:00
This week, Dave and Ben look at two stories with the first involving a recent bill introduced into the US House of Representatives that looks to clarify the confusion around AI liability. The second story involves a court case where an AI generated video was able to sway a judge's opinion. Additionally, Dave sits down with ⁠⁠Garfield Jones⁠, Senior Vice President of Research and Strategy at ⁠QuSecure⁠ and former CISA Homeland security exec for quantum, to discuss post-quantum migration efforts and the impact that it will have on organizations.

  • ✇Security Affairs
  • How a leaked builder of XWorm turned a remote access trojan into a surveillance kit Pierluigi Paganini
    Netskope tracks four XWorm versions in the wild, 46 plugins, and new tools for location, audio and live browser control, with detections up fourfold. Netskope Threat Labs has been following XWorm since September 2024, and its latest report shows the malware has changed a lot. Over the past year the team identified four distinct versions running at the same time in the wild. Detection volume is still high, with 1,236 events across more than 100 customer organizations in the third quarter of 2
     

How a leaked builder of XWorm turned a remote access trojan into a surveillance kit

14 de Outubro de 2026, 02:46

Netskope tracks four XWorm versions in the wild, 46 plugins, and new tools for location, audio and live browser control, with detections up fourfold.

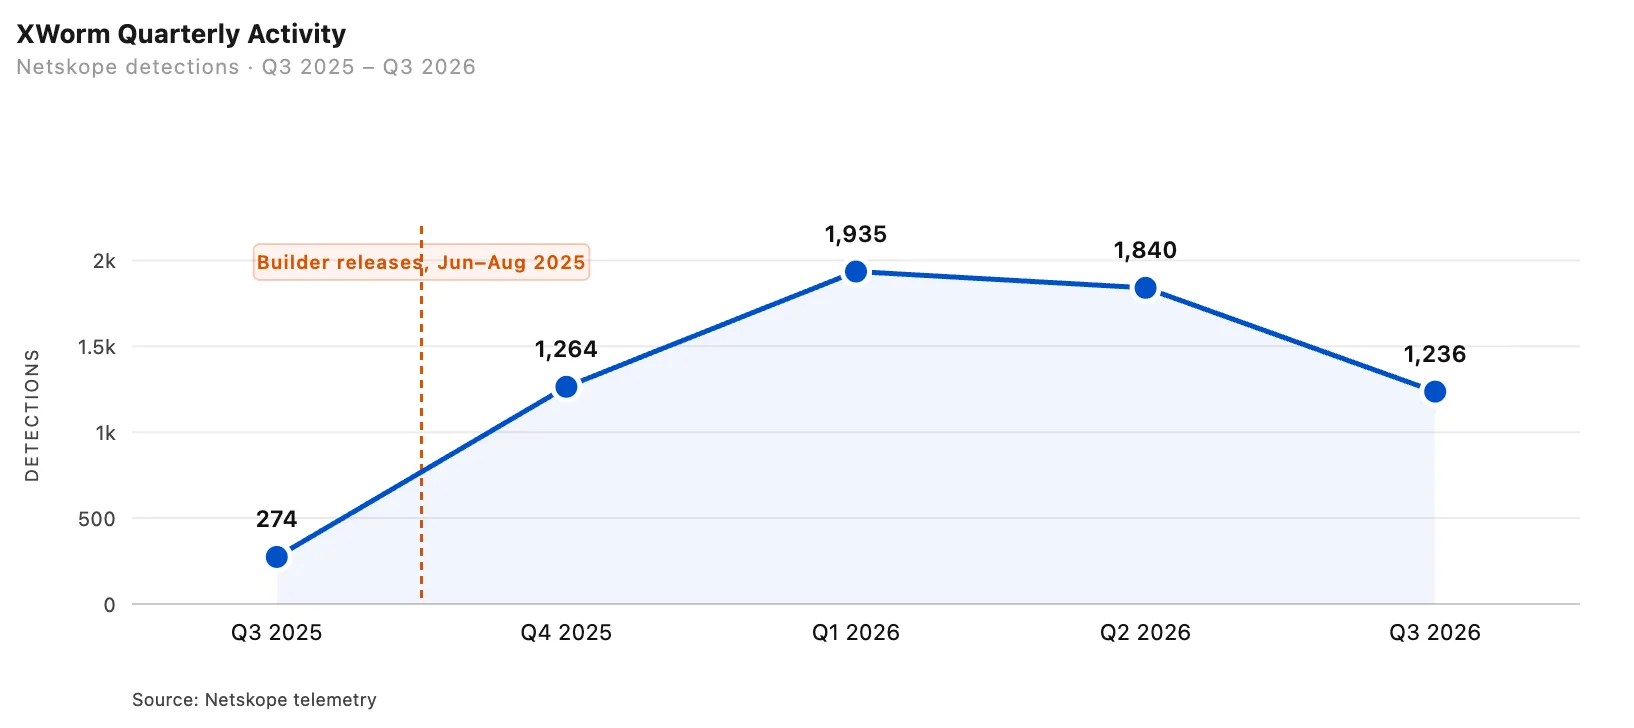
Netskope Threat Labs has been following XWorm since September 2024, and its latest report shows the malware has changed a lot. Over the past year the team identified four distinct versions running at the same time in the wild. Detection volume is still high, with 1,236 events across more than 100 customer organizations in the third quarter of 2026, four times the number from the same quarter in 2025.

The leak fueled the surge. In June 2025, a cracked version of the XWorm builder was released publicly. In August, the source code for a modified version, 6.4, also leaked. These leaks gave XWorm more exposure and helped drive its growth.

Netskope’s data shows how long the impact lasted. Detections more than quadrupled between the third and fourth quarters of 2025. In the first quarter of 2026, they reached seven times the original level and stayed there through the second quarter. Detections fell to 1,236 in the third quarter of 2026, but September alone accounted for 601, matching the monthly average during the peak in the first half of the year.

The victims skew toward money. Financial services make up about 35% of affected customers, and activity is concentrated in India, Brazil, Italy, Panama and the United States.

“The public leak of the V6.4 builder in mid-2025 drove this initial surge, keeping activity consistently above pre-leak baselines ever since.” reads Netskope’s analysis. “The financial services sector accounts for approximately 35% of affected customers, with activity concentrated in India, Brazil, Italy, Panama, and the United States.”

Since Netskope published its report on version 6.0 in July 2025, four new versions of the malware have been discovered: V6.4, V6.5 (“XWorm Reborn”), V7.2, and V7.4. Three of these versions were released after the malware generator tool became publicly available. The number of known plugin features has also increased from 35 to 46. This includes new modules, such as SteamTokenRecovery, Rootkit, ResetSurvival, and Cmstp-Bypass, as well as several plugins that were previously removed in V6.0 but have now been brought back.

Each new version includes small but significant updates:

  • V6.4 includes file details that link it to celestialproject.org.
  • V6.5 updates its branding link to c3lestial.fun, adds five new plugins, and introduces a built-in license check for the tool itself.
  • V7.2 adds stronger code protection to hide its activity, uses six different tricks to avoid running in virtual analysis environments, and disguises its file details as the software Voicemod.
  • V7.4 introduces a new file delivery system (dropper), uses a technique to bypass Windows security monitoring, switches to a new communication channel for commands, and reinstates license checks.

The surveillance side is where it gets uncomfortable. Netskope says XWorm has moved from an infostealer to a full surveillance platform. Three plugins matter most: Maps, Microphone and HBrowser, and webcam capture is also available on demand.

HBrowser changes how account theft works. Starting with version 6, it gives the operator a live view of the victim’s running browser, relays the operator’s mouse, keyboard and paste actions into it, and streams the screen back. The commands travel over XWorm’s usual encrypted channel and run on the victim’s machine.

This creates a full remote browser session for the attacker. Because every logged-in tab remains open, the attacker can access accounts directly without needing to steal passwords or bypass multi-factor authentication (MFA). Netskope notes that this plugin grants full account access without ever extracting login credentials.

The location-tracking feature bypasses the standard Windows permission prompt. It first modifies a Windows system setting to suppress consent requests, then attempts to fetch precise GPS coordinates within 15 seconds to send to the attacker. If GPS is unavailable, it falls back to IP-based location tracking. Because the modified setting remains in place, future location requests continue to bypass user permission.

“XWorm continues to evolve and has now added surveillance capabilities. It can track geolocation and record the victim’s audio without requesting the victim’s permission.” continues the report. “The HBrowser plugin gives operators direct control of the victim’s live browser session, granting access to accounts without needing to exfiltrate credentials and making MFA irrelevant.”

Microphone does what the name says. It captures audio from any device on the machine, with the operator choosing which one, and streams it back in half-second chunks that are compressed, encoded and encrypted, so audio reaches the operator with about half a second of delay. The microphone stays active for as long as the operator keeps the session open, and both Maps and Microphone run without privilege escalation or a visible prompt.

Netskope expects more of the same. Since the builder and source code were leaked, it expects continued upgrades and use of the toolkit. Its indicators of compromise are on the team’s GitHub, and its protection flags the samples as Gen:Variant.Application.Lazy and Trojan.Generic.

The key lesson for security teams is that multi-factor authentication (MFA) cannot protect accounts once an attacker has already gained access to an active browser session. This vulnerability applies to any account currently logged in on an infected computer.

The HBrowser plugin clearly demonstrates this risk: from the attacker’s perspective, it provides a complete, live remote browser session with full access to open accounts.

“Since its builder and source code were leaked, we expect continued upgrades and use of this toolkit. Netskope Threat Labs will continue to monitor XWorm.” NetSkope concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CISA)

  • ✇The CyberWire
  • Expanding the digital evidence trail.
    This week, Dave and Ben look at two court cases where one involves a judge ruling that law enforcement's use of Flock cameras was unconstitutional and another where the AI chat logs were used as evidence to levy felony charges. Additionally, Dave sits down with ⁠Meredith Burkart⁠, Senior Director of Government Affairs and Public Policy at ⁠Halcyon⁠, to discuss how ransomware attacks could be considered as acts of terrorism.
     

Expanding the digital evidence trail.

8 de Outubro de 2026, 02:00
This week, Dave and Ben look at two court cases where one involves a judge ruling that law enforcement's use of Flock cameras was unconstitutional and another where the AI chat logs were used as evidence to levy felony charges. Additionally, Dave sits down with ⁠Meredith Burkart⁠, Senior Director of Government Affairs and Public Policy at ⁠Halcyon⁠, to discuss how ransomware attacks could be considered as acts of terrorism.

  • ✇Schneier on Security
  • Unidentified Flock Cameras in Florida Bruce Schneier
    St. Lucie County in Florida discovered (alt link) a dozen Flock cameras whose ownership it can’t identify, and that the county government had not permitted. I am reminded of the decade-old story of StingRay cell phone surveillance devices in Washington, DC, whose operators were also unknown. My guess is that in the StingRay case, the devices were operated by foreign actors. This Flock case is more likely some local government entity that didn’t bother getting approval. Were I a foreign actor, I
     

Unidentified Flock Cameras in Florida

2 de Outubro de 2026, 11:52

St. Lucie County in Florida discovered (alt link) a dozen Flock cameras whose ownership it can’t identify, and that the county government had not permitted.

I am reminded of the decade-old story of StingRay cell phone surveillance devices in Washington, DC, whose operators were also unknown.

My guess is that in the StingRay case, the devices were operated by foreign actors. This Flock case is more likely some local government entity that didn’t bother getting approval. Were I a foreign actor, I would rather hack the existing Flock network—like Israel did with Tehran’s surveillance cameras—than risk installing my own.

Regardless, once we normalize a surveillance infrastructure, both friends and foes will take advantage of it.

  • ✇Schneier on Security
  • Connected Cars Are a Surveillance Platform Bruce Schneier
    Researchers at Northeastern University, in collaboration with Consumer Reports, evaluated how much modern cars spy in their drivers: The new Northeastern study shows, for the first time, data flowing among the vehicles, the vehicle apps you download when you buy your car, and third-party companies, documenting exactly what kind of data gets siphoned from our vehicles and which companies are receiving that information. Basically, your car’s manufacturer has you under constant surveillance, and t
     

Connected Cars Are a Surveillance Platform

1 de Outubro de 2026, 08:06

Researchers at Northeastern University, in collaboration with Consumer Reports, evaluated how much modern cars spy in their drivers:

The new Northeastern study shows, for the first time, data flowing among the vehicles, the vehicle apps you download when you buy your car, and third-party companies, documenting exactly what kind of data gets siphoned from our vehicles and which companies are receiving that information.

Basically, your car’s manufacturer has you under constant surveillance, and they use that data against you.

The companies on the receiving end of your data, our investigation has found, include car insurers and lenders that are partners in “telematics data exchanges,” which compile driving data on millions of drivers, thousands of data brokers that create personalized risk scores, companies selling infotainment and WiFi hotspot products, and even local and state government agencies working on planning, traffic, and safety initiatives.

Nearly every automaker sent data to outside companies.

Even more troubling, almost a quarter of the vehicle apps were found to be sending out personally identifiable information, including vehicle owners’ names, vehicle identification numbers (VINs), and precise geographic locations. That information can make it easy for companies to link driving behavior to personal data profiles created by data brokers and marketers. Such profiles are routinely sold to banks, insurers, pharmaceutical companies, lenders, and retailers, who can use it for personalized loan terms and filtered bank and insurance offers, a CR and CalMatters investigation found.

Remember the adage “If you’re not the customer, then you’re the product”? (The sentiment is older than you think.) Turns out that with modern internet-connected everything, you’re the product even if you are the customer.

  • ✇The CyberWire
  • Anthropic’s Court Battles.
    This week, Dave and Ben look at the recent court ruling which has supported the Trump administration's reclassification that Anthropic was a supply chain risk. Additionally, the two look at how AI chat prompts are being increasingly used for gathering evidence for AI-related investigations.
     
  • ✇Graham Cluley
  • Smashing Security podcast #486: Vibe-coded shops, and hackable Flock cameras Graham Cluley
    A store in Auckland vibe-coded itself a new website. Within hours, its inventory had somehow expanded to include a pair of crusty socks, an $850 banana, and all of New Zealand's national parks. What could possibly have gone wrong? Meanwhile, a hacker collective backed a truck into one of the license-plate-reading Flock safety cameras popping up on American street corners, and took a very close look inside. All this and more in episode 486 of the "Smashing Security" podcast with cybersecuri
     

Smashing Security podcast #486: Vibe-coded shops, and hackable Flock cameras

23 de Setembro de 2026, 20:15
A store in Auckland vibe-coded itself a new website. Within hours, its inventory had somehow expanded to include a pair of crusty socks, an $850 banana, and all of New Zealand's national parks. What could possibly have gone wrong? Meanwhile, a hacker collective backed a truck into one of the license-plate-reading Flock safety cameras popping up on American street corners, and took a very close look inside. All this and more in episode 486 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Dave Bittner.
  • ✇The CyberWire
  • When digital tools get it wrong.
    This week, Dave and Ben sit down to look at a recent court ruling which has rejected limits on cell phone border searches. Additionally, the two look at another case where a woman was falsely accused of bank robbery after an AI facial recognition system misidentified her and is now suing for $10 million.
     

When digital tools get it wrong.

24 de Setembro de 2026, 02:00
This week, Dave and Ben sit down to look at a recent court ruling which has rejected limits on cell phone border searches. Additionally, the two look at another case where a woman was falsely accused of bank robbery after an AI facial recognition system misidentified her and is now suing for $10 million.

  • ✇Malwarebytes
  • Flock cameras are tracking people as well as cars
    Flock Safety’s cameras are automated license plate readers (ALPRs) designed to help police find stolen cars or wanted suspects. A joint investigation by 404 Media and WIRED, based on data recovered from a physically removed Flock camera, found that its on-device software explicitly detects people as well as vehicles, bicycles, and license plates. Separately, Washington DC’s police union says the Metropolitan Police Department used Flock data to track officers under Internal Affairs investi
     

Flock cameras are tracking people as well as cars

17 de Setembro de 2026, 15:46

Flock Safety’s cameras are automated license plate readers (ALPRs) designed to help police find stolen cars or wanted suspects.

A joint investigation by 404 Media and WIRED, based on data recovered from a physically removed Flock camera, found that its on-device software explicitly detects people as well as vehicles, bicycles, and license plates.

Separately, Washington DC’s police union says the Metropolitan Police Department used Flock data to track officers under Internal Affairs investigation without their knowledge.

Together, these reports illustrate a privacy problem: A network built to record the movements of vehicles can readily be used to follow almost anyone.

The latest reporting adds an important technical detail to that debate.

What Flock cameras collect

A group of hackers reportedly removed a Flock camera from a roadway, copied its storage, and recovered an encryption key stored on the device. That allowed them to unlock videos of thousands of vehicle detections despite Flock’s claim that its devices are protected by on-device encryption. Flock said it could not assess the claims without more detail.

The recovered camera files reportedly contained software models that detect people, even though public discussion of Flock has usually focused on cars and license plates. The researchers found no evidence that face-recognition features were actively used. Reassuring, but it should not be mistaken for a clean privacy bill of health.

Even without facial recognition, a system that records repeated sightings can potentially reveal sensitive patterns of movement, including where someone lives, works, worships, seeks healthcare, attends protests, visits family, or spends time with other people. When a person is matched to a vehicle, vehicle-based tracking can become person-based tracking in practice.

As an example of how widely the data can be shared, WIRED found that records from the city of Alpharetta, Georgia:

“were accessible to more than 2,000 agencies, including police departments, colleges, airports, and, inexplicably, the Office of Inspector General for the federal General Services Administration.”

Targeted tracking of people

The Washington DC dispute shows what happens when the power to follow people is turned inward.

The DC Police Union says it learned in July that MPD’s Internal Affairs investigators had used Flock license-plate-reader data to track sworn officers under investigation without their knowledge. The union filed a complaint and asked the department to stop, arguing that MPD lacked adequate controls for a system with such extensive surveillance capabilities.

MPD defended the use, saying its position is that the use of license-plate-reader data in the misconduct investigation was appropriate. It said the labor dispute is headed to arbitration.

If police officers themselves are concerned that the system can be used to monitor them without transparent rules, the public should ask an obvious follow-up question: What prevents the same tools from being used to follow residents, employees, journalists, activists, former partners, or other people with no meaningful ability to challenge the search?

Even when Flock wants privacy to meet surveillance halfway, its measures do not eliminate the underlying civil-liberties issue.

The recovered camera software and the DC dispute make the same point from different directions. Flock’s network is not merely a collection of roadside plate readers. It is a distributed system for recording movement, identifying patterns, and making those records available for search.

Meaningful safeguards should include:

  • Public approval before cameras are deployed, with clear maps showing their locations and stated purposes.
  • Strict limits on collection, retention, searches, and cross-jurisdictional sharing.
  • A requirement for documented investigative justification before a search, with elevated approval for sensitive investigations.
  • Independently reviewable audit logs, regular public transparency reports, and meaningful penalties for misuse.
  • Clear bans on searches related to protected activity, immigration enforcement where local law forbids cooperation, abortion-related investigations, political surveillance, and personal purposes.
  • Independent security assessments covering the cameras, cloud services, identity controls, key management, and third-party integrations.
  • Automatic deletion that cannot be overridden merely because data could someday be useful.

Privacy cannot depend on authorized users always following rules, vendors configuring every setting correctly, or abuses being discovered the hard way. The first safeguard should be limiting the system’s ability to build a searchable record of ordinary people’s lives at all.


Browse like no one’s watching. 

Malwarebytes Privacy VPN encrypts your connection and never logs what you do, so the next story you read doesn’t have to feel personal. Try it free → 

  • ✇Security Affairs
  • Chosen Brick, Iran’s Surveillance Malware Pierluigi Paganini
    UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram. The UK, the US, and the Netherlands published a joint advisory warning about a Windows malware family, dubbed Chosen Brick, that Iran’s intelligence services use to track down dissidents, journalists, and activists, and the stakes for the people on the receiving end go well beyond a locked file server. “CHOSEN BRICK is a malware family that has been
     

Chosen Brick, Iran’s Surveillance Malware

17 de Setembro de 2026, 04:25

UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram.

The UK, the US, and the Netherlands published a joint advisory warning about a Windows malware family, dubbed Chosen Brick, that Iran’s intelligence services use to track down dissidents, journalists, and activists, and the stakes for the people on the receiving end go well beyond a locked file server.

“CHOSEN BRICK is a malware family that has been used to target individuals around the world including in the UK, US and the Netherlands from at least 2025. CHOSEN BRICK enables Iranian state cyber actors to collect information on a target’s contacts, emails and social media messages, which could enable tracking of their movements.” reads the advisory. “Iran almost certainly uses cyber activity to support the repression of individuals who are seen as a threat to the regime, such as dissidents, activists and journalists.”

The advisory was issued jointly by the UK’s National Cyber Security Centre, the FBI, and the Netherlands’ AIVD. The three agencies gave a name to malware activity that security researchers had already been tracking under different names.

This is not the first time Iranian state-linked actors have used Telegram-based malware against the Iranian diaspora. In March, the FBI reported that Iranian actors had been using Telegram as command infrastructure to target dissidents, with activity dating back to late 2023. The latest advisory adds a formal name, a joint attribution, and a more detailed look at how the malware operates.

Iran has repeatedly used cyber operations to target people it considers a threat to the regime, including dissidents, activists and journalists. Iranian intelligence services have also been linked to plots involving the kidnapping or killing of perceived opponents abroad. For victims of CHOSEN BRICK, the risk may extend beyond cyber intrusion.

Personal information belonging to some victims has reportedly appeared on pro-Iranian leak sites, potentially exposing them to further harassment, intimidation or physical threats. The publication of such data could increase the risks faced by individuals already targeted by Iranian actors.

” In some cases, the Iranian intelligence services have plotted to kidnap or conduct lethal operations against individuals internationally, who they perceive as enemies of the regime.” continues the advisory.

Stolen personal data from CHOSEN BRICK victims has also shown up on pro-Iranian leak sites, turned into a harassment tool rather than just an intelligence asset.

That combination changes the calculus for defenders. A compromised laptop is normally a data problem. Here, it can become a physical safety problem for the person who owns it.

The attack starts on a messaging app, not an email inbox. Operators build rapport with a target over WhatsApp or Telegram first, sometimes for a while, before ever sending a file.

Iranian cyber actors first contacted targets through social messaging apps, spending time building trust before attempting to deliver malware. Their social engineering was tailored to each victim and relied on detailed information gathered during prior research.

In some cases, the attackers pretended to be someone the target already knew, making the approach appear legitimate. In others, they posed as technical support staff from the messaging platform. This combination of reconnaissance, impersonation and trusted communication channels helped make the malicious messages more convincing and increased the chances of successful infection.

“Iranian cyber actors engaged with targets via social messaging applications to build rapport prior to attempting to deliver the malware. The nature of the social engineering varies between targets and uses extensive target knowledge from research conducted in preparation (T1589).” the agencies state. “The actor often purports to be an individual previously known to the target or technical support from the social messaging platform (T1566.003).”

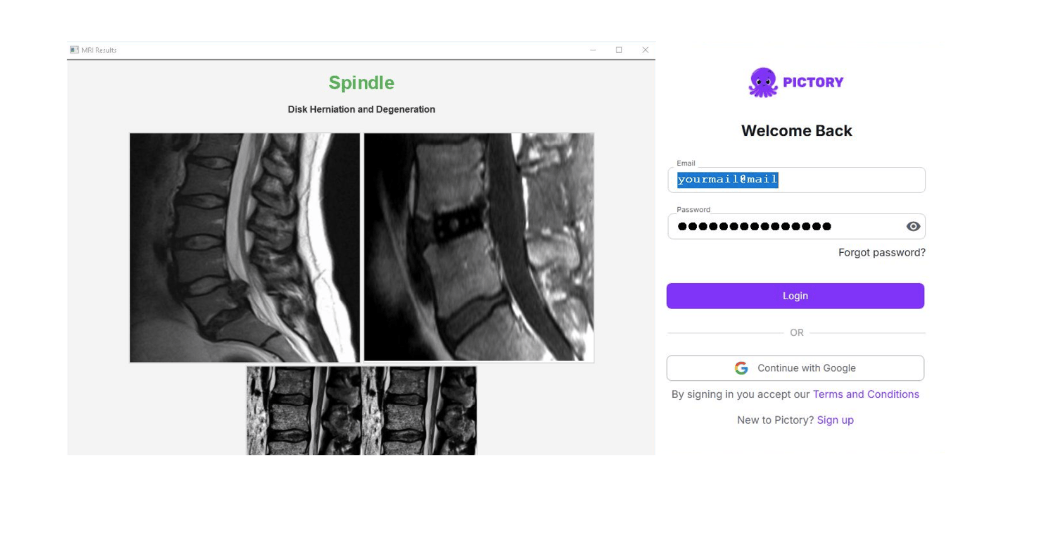
The lure files themselves are dressed up as things a target would plausibly want to open: fake installers for Pictory, RunwayML, Norton Antivirus, Telegram itself, Adobe Flash Player, or KeePass. Other versions arrive disguised as MRI scan results, which is a particularly grim way to earn someone’s click. Whatever the disguise, the file shows a convincing decoy screen while the real payload installs quietly in the background.

The attackers also have a backup plan. They usually target a victim’s work device first, but if the initial attempt fails or they think they may be detected, they try to move the attack to a personal device. They may ask the victim to open the file on their own phone or computer, bypassing the security controls protecting the work device.

A company can tightly secure an employee’s work laptop, but it has much less control over the personal devices they use every day.

Whatever the file is supposed to contain, it shows the victim a realistic-looking screen related to the topic, helping the attackers maintain the deception. In the background, the file downloads and runs the main malware component, which the NCSC tracks as CHOSEN BRICK. This gives the attackers control over the compromised device. So far, all observed attacks have targeted Windows systems.

Corporate IT can lock down a work laptop all it wants. It has no say over the phone in someone’s pocket.

CHOSEN BRICK has only ever been seen hitting Windows machines. It sets up persistence through a registry Run key so it survives a reboot, and it tries to add its own exclusions to Microsoft Defender to keep from getting flagged.

The malware uses Telegram for command and control, with each infected device linked to its own Telegram bot ID. This keeps victims separated and makes investigations more difficult. Newer versions also use HTTPS or SOCKS5 proxies, adding another layer between the malware and network monitoring.

The malware sends stolen data through Telegram bots and cloud storage services such as VultrObjects and StorjShare. It can also download and install additional malware when attackers want more access.

“Files and collected data are exfiltrated through a combination of the Telegram bot (T1041) and through the use of cloud object stores such as VultrObjects and StorjShare (T1567.002). Recent variations in this malware family include the use of HTTPS/SOCKS5 proxies to obscure the use of Telegram bots (T1090.002).” states the report. “If the malware is instructed by the cyber actor to download additional malware it is written to disk in a configurable location.”

The new payload is saved using the same persistence method as the main malware. One sample used the path C:\Windows \SysWOW64, with an unusual space after “Windows.”

The unusual space after “Windows” creates a non-standard folder path that is not normally found on Windows systems. According to the NCSC, the attackers deliberately created this location to deploy their malware. It is a small but effective trick: the path looks legitimate at first glance, but it can bypass security rules or allowlists that only recognize standard Windows folders.

Once running, CHOSEN BRICK can collect a wide range of data, including screenshots, microphone audio, WhatsApp and Telegram chats stored in browsers, emails and system information. It can also delete files and even wipe the entire system. So far, researchers have not seen it spread laterally on its own. However, because it can download and run additional payloads, attackers could manually expand their access if a compromised device is considered valuable.

The malware also has two distinctive fingerprints. Researchers repeatedly found the mutex names “ytyjyujyu” and “noi672pp434awkc12f” in samples. These unusual strings could help security teams identify CHOSEN BRICK during threat hunting.

In March, the FBI also published a FLASH notice focused specifically on how Iranian state-backed actors lean on Telegram as C2 infrastructure, which pairs well with the NCSC’s broader writeup.

If you’re hunting for this on your own network, a few domains are worth flagging when they show up unexpectedly in DNS or proxy logs: api.telegram.org, backblazeb2.com, vultrobjects.com, storjshare.io, iproyal.com, and lightningproxies.net. None of these are malicious on their own, which is exactly why the malware picked them. It’s the context that matters, not the domain name.

On the registry side, check HKCU\Software\Microsoft\Windows\CurrentVersion\Run for anything unfamiliar. Previously observed malicious entries used value names like “SMQDService” and “winappx,” though the advisory is careful to note these names will change and shouldn’t be treated as fixed indicators.

The recommended defenses are straightforward. Users should avoid installing software from links or attachments, keep applications updated, use active antivirus protection, and take SmartScreen warnings seriously. Organizations should also use phishing-resistant MFA, application allowlisting, email security and endpoint monitoring, while checking the published indicators against their own logs.

One important point concerns personal devices. Attackers may switch to a victim’s phone when security controls block access to a work laptop. Organizations protecting high-risk users, including journalists, activists and NGO workers, should therefore also provide security guidance for personal devices. Protecting only the corporate laptop may leave the device attackers target next exposed.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Chosen Brick)

  • ✇Graham Cluley
  • Smashing Security podcast #485: These researchers got drunk to hack an LG TV Graham Cluley
    Researchers wanted to test if LG's smart TVs come with any security risks - but their lawyers noticed a snag: the terms and conditions would forbid it. So they came up with a solution. They got plastered before setting up the TV, on the reasoning that you can't be legally bound to a contract you agreed to while drunk. What they discovered will make you look at your TV rather differently... Meanwhile, awful Android malware with the audacious name "Awesome" (in Indonesian) is doing the rounds,
     

Smashing Security podcast #485: These researchers got drunk to hack an LG TV

16 de Setembro de 2026, 20:07
Researchers wanted to test if LG's smart TVs come with any security risks - but their lawyers noticed a snag: the terms and conditions would forbid it. So they came up with a solution. They got plastered before setting up the TV, on the reasoning that you can't be legally bound to a contract you agreed to while drunk. What they discovered will make you look at your TV rather differently... Meanwhile, awful Android malware with the audacious name "Awesome" (in Indonesian) is doing the rounds, stealing your data, demanding a ransom, and then giving you a "jump scare"... Plus, in our featured interview, Andy Hornegold of Intruder explains why the mid-market is where cybercriminals are having the most fun right now - and how AI is helping attackers get from "first foot in the door" to "full ransomware disaster" in less than a working day. All this and more in episode 485 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Lianne Potter.
  • ✇The CyberWire
  • The battle for AI regulation.
    This week, Dave and Ben sit down with N2K's lead analyst Ethan Cook to look at the growing calls to enact AI regulations both within the US and across the globe. Spurned on by recent model escapes, policymakers and AI developers alike have steadily begun to call for greater legislative oversight; however, the federal government shows little signs of taking meaningful action.
     

The battle for AI regulation.

17 de Setembro de 2026, 02:00
This week, Dave and Ben sit down with N2K's lead analyst Ethan Cook to look at the growing calls to enact AI regulations both within the US and across the globe. Spurned on by recent model escapes, policymakers and AI developers alike have steadily begun to call for greater legislative oversight; however, the federal government shows little signs of taking meaningful action.

  • ✇Schneier on Security
  • 25 Years of Mass Surveillance Is Enough Bruce Schneier
    This essay was written with Cindy Cohn, and originally appeared in Lawfare. One of the many legacies of the terrorist attacks of Sept. 11 is the government-wide shift from targeted surveillance—such as individual wiretaps or pen register/trap and trace orders—to mass surveillance techniques—such as tapping into the internet backbone or mass collection of telephone or internet metadata. The legal and technical architecture of modern mass surveillance, initially framed as a necessary defense again
     

25 Years of Mass Surveillance Is Enough

15 de Setembro de 2026, 08:01

This essay was written with Cindy Cohn, and originally appeared in Lawfare.

One of the many legacies of the terrorist attacks of Sept. 11 is the government-wide shift from targeted surveillance—such as individual wiretaps or pen register/trap and trace orders—to mass surveillance techniques—such as tapping into the internet backbone or mass collection of telephone or internet metadata. The legal and technical architecture of modern mass surveillance, initially framed as a necessary defense against terrorist threats, has grown far beyond that justification and national security in general. Mass surveillance is now a routine tool used by law enforcement. ICE uses it in immigration actions and against people exercising their First Amendment rights to protest. It’s also increasingly part of private security systems, such as facial recognition at venues such as Madison Square Garden and networked Flock license plate capture systems on roads and in parking lots.

The interrelation between private and governmental mass surveillance is worth examining. Surveillance is the business model of the internet; companies like Google and Facebook constantly spy on their users’ behavior. From the National Security Agency relying on data collected by telecommunication and internet companies, to local sheriffs and ICE agents relying on cellphone location data and privately managed automatic license plate readers, governments primarily obtain the mass surveillance information through private companies. Increasingly, access doesn’t just come through legal processes, either. FBI Director Kash Patel recently confirmed in congressional testimony that the agency is purchasing information on Americans from data brokers and intends to continue to do so.

This pipeline from private collection to governmental collection means that as companies collect more information for surveillance capitalism purposes, more is available to law enforcement as well. And as the technology for mass surveillance and analysis improves, especially with the increased use of AI technologies, the problems attendant to mass surveillance grow as well.

After 9/11, the idea that the government could surveil the population to safety took hold. In 2001, the fear of terrorism reached a frequency and intensity never before seen. Along with that came the fear that the enemy could be anyone, anywhere. As a result, the government’s response was to watch everyone, everywhere. This line of reasoning underpinned the shift from targeted to mass surveillance. Or, in the words of an internal National Security Agency (NSA) presentation that was made public as part of Edward Snowden’s 2013 disclosures, a government that can “Collect it All,” “Process it All,” “Exploit it All,” “Partner it All,” and “Sniff it All,” will ultimately, “Know it All.” Similar rationales support the rise of domestic mass surveillance: if law enforcement could see and hear everything, it could more effectively interdict and solve serious crimes.

The national security community has never provided a full analysis of the costs and benefits of these mass surveillance programs, either in terms of taxpayer dollars or diversion of resources from other efforts—or any demonstration that those techniques stopped attacks that otherwise they would not have been able to prevent. While the NSA occasionally presents examples of the successes due to its mass surveillance programs, especially when those techniques are under public pressure, the examples also regularly fall apart upon serious scrutiny. And even if some utility exists, it must be seriously weighed against the costs.

Similarly, there has never been any comprehensive analysis about whether domestic immigration or law enforcement’s use of these techniques actually makes people safer, or whether other techniques could produce the same results. Instead, both the police and the companies selling these tools float anecdotes and dubious data. For example, Flock’s data equates the number of law enforcement hits in their database with actually solving crimes.

Twenty-five years after 9/11, it seems reasonable to step back and evaluate the costs of this shift to mass surveillance, especially in terms of Americans’ rights and freedoms.

The Shift

The easiest place to see a shift to mass surveillance was in the government’s decision immediately after 9/11 to collect Americans’ telephone records. The program started under an argument of pure executive power as the “President’s Surveillance Program.” But in 2006, that argument secretly shifted to a novel interpretation of Section 215 of the Patriot. Act which had only previously authorized more targeted access to record. While some media and public interest organizations struggled to force the government to reveal the program as early as late 2005, the government only officially confirmed it after the 2013 Snowden disclosures. In 2015, the Second Circuit Court of Appeals rejected the government’s interpretation of Section 215 as allowing mass collection of telephone records. Later the same year, Congress passed the USA Freedom Act. While this new law still allows collection of a tremendous amount of domestic telephone records, it ended the indiscriminate mass collection that had occurred for nearly fourteen years.

Other shifts to mass surveillance continue through today. The NSA launched its Upstream program, which involved intercepting both metadata and content from key telecommunications junctures inside the U.S., soon after 9/11. It was also initially conducted under a claim of purely presidential authority. This program was brought under marginal congressional and programmatic (not targeted) Foreign Intelligence Surveillance Act (FISA) court review via Section 702 of the 2008 FISA Amendments Act. In 2017, more than15 years after its inception, the NSA ended content searches due to FISA court pressure, but the mass collection continues.

Despite the stated goal of conducting mass spying only on people outside the U.S.—which itself is problematic given international law’s requirement that surveillance be both necessary and proportionate—mass surveillance collects a tremendous amount of U.S. persons’ communications. This can happen because people communicate with people abroad, or because of overcollection—when government agencies gather far more personal data on non-targeted US persons than authorized by law. The concerns about collecting Americans’ data on U.S. soil led Congress to allow the program to officially expire in 2026, although the previously-approved mass surveillance itself continues until at least Spring of 2027.

The shift to mass surveillance would be notable enough even if it remained only a strategy of the intelligence community. It has not. Americans are awash in mass surveillance. Networks of automated license plate readers such as those offered by Flock and Vigilant Solutions blanket both public and private roadways and parking lots. These networks often allow searches by law enforcement, including across jurisdictions. They are, for example, being used to track people seeking abortions across state lines. Facial recognition tools, once the province of only the more elite parts of federal law enforcement, are increasingly used by Immigration and Customs Enforcement agents on immigrants and protesters, in airports by the Transportation Security Administration, as well as by private entities. And, of course, modern phones track users’ locations constantly—and that information is readily available to law enforcement, often with only minimal process protections.

Constitutional Costs

Regardless of the murkiness of its actual usefulness, the shift from targeted to mass surveillance has profound implications for Americans’rights. It has created risks that have become increasingly evident, especially under the Trump administration.

At a basic level, the Fourth Amendment guarantees that citizens can be secure in their “persons, houses, papers and effects” from unreasonable searches. Warrants breaching that security should be supported by probable cause and particular descriptions of the place to be searched and items to be seized. Mass surveillance turns that promise on its head, allowing access to our “papers and effects” by the government without individualized suspicion or a particularized description of what data is being seized, much less probable cause. This protection was in response to colonial British misuse of writs of assistance, which authorized indiscriminate searches rather than targeted ones.

The justifications for exempting mass surveillance from constitutional protection vary. For Section 702, the government has taken the position that U.S. persons’ communications caught up in the dragnet, either due to overcollection or because they were communicating with someone outside the United States, do not require a warrant prior to initial collection or secondary access by the FBI and several other agencies. The argument is that if the initial collection was not aimed at Americans, the information is free from constitutional protection for any later uses, even for reasons far afield from the initial rationale for collection.

Other arguments rest on the claim that metadata is outside the Fourth Amendment, despite its demonstrated ability to reveal intimate details of all of our lives. Still others rest on the Supreme Court-created Third Party Doctrine, which holds that the Fourth Amendment does not apply to data shared with companies that provide us with services. Some turn on whether analysis by machine counts, claiming that only “human eyes” matter—a particularly troubling argument with the rise of artificial intelligence. What’s more, the government has used doctrines like standing to limit the ability of those subjected to mass surveillance to seek constitutional protection. No matter the argument, the goal is the same: to place the mechanisms and fruits of mass surveillance outside the protections of the Fourth Amendment.

The overarching truth is that, due to the concerted efforts by the government since 9/11, and the rise of technologies in recent years, the slice of Americans’ lives and data that are actually protected by the Fourth Amendment has shrunk significantly in the past 25 years. Together, with the technical capabilities of mass surveillance and the increased ability for that data to be analyzed using AI tools, the “security in our papers and effects” that the constitution promises seems increasingly illusory.

In addition to the Fourth Amendment, mass surveillance creates tensions with the First Amendment. The Constitution has long recognized that the right to freedom of speech requires a zone of privacy against governmental surveillance. The right to anonymous speech as well as the right of association both recognize the chilling effect that surveillance creates for people saying unpopular things or attempting to organize for political or other societal change. Mass surveillance grants the authorities the ability to track those people, both in real time and historically, that is inconsistent with actual techniques of freedom of speech and assembly.

That is why the recently released 2026 U.S. Counterterrorism Strategy is so troubling. On page seven, the White House expressly states that it intends to target domestic activists with its heretofore foreign-targeted powers. It says that the government “will prioritize the rapid identification and neutralization of violent secular political groups whose ideology is anti-American, radically pro-transgender and anarchist” and “will use all the tools constitutionally available to us to map them at home, identify their membership, map their ties to international organizations like Antifa.” While framed as targeting “violent” groups, it’s clear that the government intends to use its national security tools, presumably including the tools of mass surveillance, against Americans in ways that will create profound tensions with the First Amendment rights of people to organize and communicate privately.

Costs Due to Mistakes and Abuse

Even assuming some utility from mass surveillance—a fact we do not dispute, even if the public record is shaky and conclusory—the history of both the national security and domestic uses of mass surveillance confirms that these tools are inevitably misused, and that mistakes have impacted huge numbers of Americans. The past twenty-five years have demonstrated that it is not possible to surveil the entire US population while staying within the bounds of even a very generous legal framework like Section 702.

As Rep. Zoe Lofgren (D-Calif.) recently stated in discussion of Section 702 in an interview with Tech Policy Press: “backdoor searches have been used improperly for protestors, 19,000 campaign donors, members of Congress, journalists, government officials, a state court judge who had complained to the FBI about police misconduct. It has been abused substantially in the past.” The NSA experienced so much abuse of its mass surveillance tools by actual or aspiring romantic partners and ex-spouses that an internal name emerged for it: “LOVEINT,” or Love Intelligence.

That same pattern of abuse is now emerging at the domestic law enforcement level. A Texas police officer misused, and then lied about, using license plate readers to track a woman suspected of seeking an abortion. Multiple law enforcement officials have been accused of tracking people they either wished to have a relationship with or who were their exes. And mass surveillance technologies have been used to track both immigration targets and citizens engaging in their First Amendment-protected right to track and record the police.

Mistakes are inevitable with collections of data of this size and scope. The history of the FISA court’s reviews of Section 702 is littered with examples of the NSA not being able to follow its own rules limiting the scope of what it collects and analyzes, even after having been given multiple chances by the court. On the local level, the technical protections that Flock, for example, put in place have repeatedly been insufficient to stop “accidental” sharing its data with out-of-state law enforcement. These mistakes have fueled growing efforts by local communities across the country to remove license plate readers. Those efforts should be the first step in a broader reconsideration of mass surveillance.

More generally, ubiquitous surveillance carries a real societal cost. The chilling effects are real and pervasive, and they tend to fall hardest on the most marginalized members of society. Moreover, social progress requires the ability to experiment in secret. It’s hard to imagine a society progressing morally to the point of accepting and legalizing things like marijuana use or gay marriage if the earliest signs of that shift are snuffed out because of overzealous surveillance.

Reversing Course

While a cost-benefit analysis is not the best frame for deciding constitutional rights, it is a place to start to evaluate government policies. If the costs are too high and the benefits too small, what should the public do? While the policy and legal frameworks can be individually complex, mass surveillance is a problem in all of its applications. So too should solutions be comprehensive rather than piecemeal.

One comprehensive strategy is to reset the promise of the Fourth Amendment and recognize that a warrant is required prior to collection, access or use of information gathered through mass surveillance. This would apply to collections that include U.S. persons, whether done for national security or domestic purposes. This protection would apply regardless of whether the information is in the form of metadata. It would apply regardless of whether the information is held in homes or by services people rely on, such as telephones, internet or social network providers, or by private entities utilizing mass surveillance for their own purposes. By passing this legislation, Congress could ensure this rejection of mass surveillance, and include real enforcement such as a private right of action and an automatic exclusionary remedy in criminal prosecutions. The courts could also recognize this protection of “papers and effects” directly as a plain language interpretation of the Fourth Amendment.

There are already a number of efforts that take on pieces of mass surveillance. Section 702 has expired and should remain so. This was due largely to efforts to block the “back door” access to Section 702-collected data without warrants. The bipartisan “Fourth Amendment is Not for Sale Act” would prevent the government from purchasing data that it would otherwise need a warrant to obtain. The Supreme Court itself has already been chipping away at the Third Party Doctrine, with a recent step in the rejection of mass geofence warrants—warrants seeking the identities of individuals based upon their proximity to a crime—in Chatrie v. United States. Now, such warrants fall, at least initially, under the Fourth Amendment.

A more comprehensive approach would also address mass surveillance carried out by private companies, and to ensure that Americans have the right to encrypt and secure their data. There are many reasons the United States would benefit from a comprehensive privacy law—and curbing mass surveillance is one of them. Addressing mass surveillance is certainly one of them. Ideas such as the banning of secondary uses of data—with roots in the Fair Information Practice Principles from the 1970s—are worth pushing forward. So are moves such as creating fiduciary duties for mass data collectors. There are many more ways to curtail private companies’ mass surveillance while staying within constitutional boundaries. But addressing the costs of mass surveillance by both companies and governments is even more important in a world where AI agents are making decisions both about the public and on their behalf based on their data and observed behavior.

Twenty-five years after the U.S. government embraced mass surveillance, it’s time to evaluate it as a whole, and consider responses that address the problem as a whole. Americans must ask: Is it consistent with a self-governing democracy to have systems that watch everyone everywhere? Is the public comfortable with governments—federal, state, local—that seek to “know it all” about its citizens? Is the public comfortable with private mass surveillance in its own right and as it’s being increasingly used to fuel government surveillance? These questions have long needed serious consideration. But as it becomes increasingly evident that the Trump administration is using mass surveillance to keep itself in power, stifle dissent, and undermine political opponents, these questions are now more urgent than ever.

  • ✇The CyberWire
  • Addressing the social media algorithms.
    This week, Dave and Ben look at how AI and social media are coming under greater regulatory scrutiny. For AI, conversations people are having with their chatbots are beginning to find their way into court cases while Australia looks to continue its crackdown on how social media platforms engage with their users.
     

Addressing the social media algorithms.

10 de Setembro de 2026, 02:00
This week, Dave and Ben look at how AI and social media are coming under greater regulatory scrutiny. For AI, conversations people are having with their chatbots are beginning to find their way into court cases while Australia looks to continue its crackdown on how social media platforms engage with their users.

  • ✇Firewall Daily – The Cyber Express
  • Pegasus, New NoviSpy Variant Found on Serbian Students and Opposition Figures Mihir Bagwe
    At least 14 people connected to Serbia's student protest movement and opposition politics have been targeted with mercenary spyware since early 2026, the Belgrade-based digital rights organization SHARE Foundation said, in what it called the largest documented wave of such targeting in the country. The group said the cohort includes student movement members, civil society activists, a member of parliament and a local councilor. Forensic analysis was independently confirmed by the Citizen Lab at
     

Pegasus, New NoviSpy Variant Found on Serbian Students and Opposition Figures

4 de Setembro de 2026, 03:06

Pegasus, Pegasus Spyware, Serbia, Serbia Protests, Smartphone screen forming an eye shape against an abstract protest crowd, illustrating spyware targeting of Serbian student activists.

At least 14 people connected to Serbia's student protest movement and opposition politics have been targeted with mercenary spyware since early 2026, the Belgrade-based digital rights organization SHARE Foundation said, in what it called the largest documented wave of such targeting in the country.

The group said the cohort includes student movement members, civil society activists, a member of parliament and a local councilor. Forensic analysis was independently confirmed by the Citizen Lab at the University of Toronto and by Amnesty International's Security Lab.

Citizen Lab, in its own findings, said it verified an infection with NSO Group's Pegasus on the iPhone of a student activist who asked not to be named. High-confidence infection indicators span December 2025 through January 2026, delivered by a zero-click iMessage exploit that required no interaction from the target. Apple has since patched the underlying flaw; the fix shipped in iOS 18.4.1. Pegasus grants an operator access to notes, photographs and messages decrypted on the device, and can silently activate the microphone and camera.

Amnesty's Security Lab confirmed a new variant of NoviSpy, an Android implant first identified in Serbia in 2024, on two additional devices. SHARE said the rebuilt version was designed to evade the detection methods that exposed its predecessor.

Also read: Investigative Journalists in Serbia Hit by Advanced Spyware Attack

The circumstances of two infections are what elevate the findings beyond routine spyware reporting. SHARE said one NoviSpy infection appeared after police seized a student's phone during questioning, and another after private messages from that device were published by a pro-government media outlet. Donncha Ó Cearbhaill, who heads Amnesty's Security Lab, said the evidence suggests "infections are being carried out during detention by Serbian authorities."

Suspicion centers on Serbia's Security Information Agency, or BIA. Amnesty's December 2024 report "A Digital Prison" found earlier NoviSpy samples configured to send collected data to IP addresses associated with BIA servers, and documented the agency's parallel use of Cellebrite extraction tools on journalists and activists. In March 2025, Amnesty reported that two journalists at the Balkan Investigative Reporting Network were targeted with Pegasus.

The current cases surfaced through Apple's threat notification wave of Aug. 13, which reached users in 110 countries. The timing is politically loaded. The targeting overlaps with protests that followed the November 2024 collapse of a railway station canopy in Novi Sad, spans local elections held March 29 in 10 municipalities, and precedes October parliamentary elections widely read as a test of the ruling Serbian Progressive Party.

Ana Toskic Cvetinovic, a legal expert cited in the reporting, noted that deploying intrusive software without judicial authorization is unlawful under Serbian law. SHARE published an analysis of the domestic legal framework in January arguing the same. Criminal complaints filed over the 2024 cases remain pending before Serbian courts, with no resolution.

Also read: 7 New Pegasus Infections Found on Media and Activists’ Devices in the EU

NSO has been on the U.S. Commerce Department's Entity List since 2021.

Serbia is an accession candidate, the European Parliament has previously questioned the Commission over unlawful spyware use in the country, and the Commission published its 2026 enlargement country report in July. Amnesty's submission for that package raised surveillance directly.

Both groups urged at-risk users to enable Lockdown Mode on iOS or Advanced Protection on Android.

❌
❌