❌

Visualização normal

Antes de ontemStream principal
  • ✇Security Affairs
  • U.S. Charges Canadian Man in Alleged Hack of University Supercomputers Pierluigi Paganini
    A Canadian man was extradited to the U.S. to face charges over hacking universities and hijacking their computers to mine cryptocurrency. A Canadian man, Ryan James Roach (35), has been extradicted to the United States to face charges tied to a hacking operation that targeted universities and other schools. Roach was extradited on October 28 and now faces federal charges alongside Mathiew James Stubbings, 41, of Ontario. The indictment alleges that, from June 2016 to December 2019, the tw
     

U.S. Charges Canadian Man in Alleged Hack of University Supercomputers

5 de Novembro de 2026, 03:20

A Canadian man was extradited to the U.S. to face charges over hacking universities and hijacking their computers to mine cryptocurrency.

A Canadian man, Ryan James Roach (35), has been extradicted to the United States to face charges tied to a hacking operation that targeted universities and other schools. Roach was extradited on October 28 and now faces federal charges alongside Mathiew James Stubbings, 41, of Ontario.

The indictment alleges that, from June 2016 to December 2019, the two men hacked computers, stole login details, and used victims’ machines to mine cryptocurrency for themselves.

“They used virtual private servers in multiple countries, which were registered under false names. These servers transmitted malware and mining software to victim computers and stored stolen login credentials.” DoJ states. “Victims of the scheme included educational institutions in New York, Tennessee, North Carolina, and Massachusetts. Some of the computers damaged by the defendants were located at an institution of higher learning in the Western District of New York.”

The targets were not random home PCs. Prosecutors say the pair went after U.S. schools with supercomputers, including institutions in New York, Tennessee, North Carolina and Massachusetts. Some affected computers belonged to a higher-education institution in western New York.

“To carry out the scheme, Roach and Stubbings surreptitiously accessed victim computers without authorization, deployed malware to gain control, stole victim login credentials, exfiltrated the data to servers that they controlled, and forcing victim computers to use their processing power to mine cryptocurrency for the financial benefit of the defendants.” DoJ continues.

That is a lot of effort to turn someone else’s research hardware into a personal crypto rig.

The alleged method was also more involved than a single phishing email. The indictment says they looked for weaknesses in victims’ networks, used servers and compromised machines from one victim to hide their tracks, and then moved through the network once inside. The duo used sophisticated techniques and tools to conduct reconnaissance and expand their access within the network.

The charges include conspiracy to obtain information from and damage protected computers, obtaining information from a protected computer, and intentional damage to a protected computer. Each carries up to 10 years in prison and a $250,000 fine. Prosecutors also allege the pair damaged at least 10 protected computers in one year and caused at least $5,000 in losses.

Roach appeared before U.S. Magistrate Judge Mark W. Pedersen and is being held pending a detention hearing. Extradition proceedings for Stubbings continue in Canada. The FBI, the Justice Department’s Computer Crime and Intellectual Property Section, and the Office of International Affairs worked on the case.

For security teams, the useful part is not the alleged crypto-mining. It is the reminder that universities remain attractive targets because they hold powerful computing resources, broad networks, and plenty of people with access. Patch quickly, watch for unusual processing load, and treat credential theft as a serious incident rather than a nuisance.

“The fact that a defendant has been charged with a crime is merely an accusation and the defendant is presumed innocent until and unless proven guilty.” DoJ concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, University Supercomputers)

  • ✇Firewall Daily – The Cyber Express
  • Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack Ashish Khaitan
    An internal investigation into the June 2025 Columbia University cyberattack found no evidence that the stolen data was sold or distributed on the dark web, Columbia University Information Technology announced Friday.   The probe, which largely concluded over the summer, determined the attack was politically motivated and found no sign the hacker sought financial gain. The University also said claims administrator Angeion Group LLC will contact affected individuals about submitting claims und
     

Columbia University Settles $16.1M Data Breach Lawsuit After 2025 Cyberattack

27 de Outubro de 2026, 05:49

Columbia University cyberattack

An internal investigation into the June 2025 Columbia University cyberattack found no evidence that the stolen data was sold or distributed on the dark web, Columbia University Information Technology announced Friday.   The probe, which largely concluded over the summer, determined the attack was politically motivated and found no sign the hacker sought financial gain. The University also said claims administrator Angeion Group LLC will contact affected individuals about submitting claims under Columbia's $16.1 million settlement over the breach. 

The Motive Behind Cyberattack 

In June 2025, the hacker told Bloomberg they were looking for evidence that Columbia still used affirmative action in admissions after the Supreme Court struck down the practice in 2023. The same hacker claimed responsibility for a March 2025 breach at New York University, where admissions data was posted to NYU's website. That data purported to show that Asian and white students admitted to NYU had higher average GPAs and test scores than admitted Black and Hispanic students.  About a month after the cyberattack on Columbia University, the school agreed to share applicants' admissions data with President Donald Trump's administration. The move was part of a broader deal to restore federal funding that had been canceled over allegations of campus antisemitism.  The hacker stole contact information, Social Security numbers, health data, and financial aid data belonging to around 870,000 Columbia applicants and affiliates. In September, the University agreed to pay $16.1 million to settle a class action lawsuit over the breach. 

Settlement Terms for the Cyberattack on Columbia University 

A federal court overseeing the settlement appointed Angeion Group, LLC, as claims administrator. The group has launched a website with settlement information and will send claim instructions to affected individuals. Columbia directed questions about the process to Angeion Group.  Each plaintiff may claim two years of credit monitoring services and either an estimated $100 payment or up to $8,500 in reimbursement for documented losses.  The court granted preliminary approval in September. Affected individuals have until Dec. 22 to submit objections, comments, or exclusions. An exclusion removes a person from the plaintiff group but preserves their right to take independent legal action against Columbia. Claims are due in late January, and a final approval hearing, where the court will review objections and decide whether the settlement is reasonable, is set for Feb. 23, 2027. 

Security Upgrades After the Columbia University Cyberattack 

In its Friday statement, Columbia said it took “proactive steps to strengthen our data security and governance practices” after the attack, adding that the settlement includes a commitment to further enhancing cybersecurity.  The University worked with cybersecurity companies to recover its compromised systems. In June, it said it was removing Social Security numbers of nonaffiliates from its systems “subject to relevant legal restrictions.”  A University official told Spectator that Columbia has since increased network segmentation, which divides networks into smaller sections to contain threats. The official said the school also deployed additional endpoint detection and response tools, which monitor systems in real time to flag unusual activity.  “We regret the concern that this incident has caused our community and believe the actions we have taken and commitments we have accepted in the agreement reflect the seriousness with which we are approaching this matter,” the statement concludes. 
  • ✇Firewall Daily – The Cyber Express
  • Yonsei University Cyberattack Hits 10,000 Students, Months After Sogang Breach Ashish Khaitan
    A Yonsei University cyberattack has compromised the personal information of roughly 10,000 students and graduates after outsiders gained unauthorized access to the school’s online portal. The breach comes months after Sogang University disclosed a far larger leak. The university’s Office of Information and Communications confirmed the breach in a notice sent to affected individuals on Thursday. “The personal information of some university members was confirmed to have been leaked following unaut
     

Yonsei University Cyberattack Hits 10,000 Students, Months After Sogang Breach

22 de Outubro de 2026, 04:29

Yonsei University cyberattack

A Yonsei University cyberattack has compromised the personal information of roughly 10,000 students and graduates after outsiders gained unauthorized access to the school’s online portal. The breach comes months after Sogang University disclosed a far larger leak.

The university’s Office of Information and Communications confirmed the breach in a notice sent to affected individuals on Thursday. “The personal information of some university members was confirmed to have been leaked following unauthorized external access to the Yonsei Portal Service,” the office stated.

What the Yonsei University Cyberattack Exposed 

The compromised data included student identification numbers, mobile phone numbers, and email addresses, along with system management details such as login identification keys and the number of failed password attempts on affected accounts. Resident registration numbers were not exposed. 

From 1 p.m. Thursday, affected individuals could check on Yonsei University’s official website which details were compromised. 

Two Hacking Attempts in Less Than a Day 

The cyberattack on Yonsei University reportedly began at around 7:41 p.m. on Tuesday. 

“An attack on the university’s system was detected at the time, and we immediately blocked the IP [internet provider] address,” a university representative told the JoongAng Ilbo. “While we were analyzing the cause at around 10 a.m. the following day, a second hacking attempt was made from a different IP address, which we also blocked.” 

Yonsei reported the incident to the Personal Information Protection Commission (PIPC) on Wednesday afternoon. The Personal Information Protection Act requires organizations to report a personal data breach within 72 hours of becoming aware of it and to notify affected individuals. 

“We plan to gather additional evidence related to the hacking attacks and refer the case to investigative authorities,” the representative said. 

The university also plans a comprehensive security review of its systems, along with stronger monitoring and security measures. It urged students and graduates to be wary of text messages, phone calls, and emails claiming to be from the university, and to avoid clicking links from unknown sources or entering personal information on suspicious websites. 

Sogang University and a Wider Pattern of Breaches 

The cyberattack on Yonsei University follows a series of attacks on higher education institutions. On Aug. 14, Sogang University suffered an external cyberattack that exposed approximately 180,000 records containing personal information of students, graduates, and university staff, according to a notice posted on the Sogang University website. 

The problem goes beyond recent cases. According to data the Ministry of Education submitted to People Power Party Rep. Kim Meen-geon, personal data breaches at universities affected 2.8 million people between 2022 and July this year. 

Calls for Support After Yonsei and Sogang University Incidents 

Experts have called for more cybersecurity personnel and greater funding as hacking attacks grow increasingly sophisticated, including through the use of AI. 

“Just as the government develops information security measures for small- and medium-sized businesses, it should establish support measures to strengthen cybersecurity at universities,” said Kim Seung-joo, a professor at Korea University’s School of Cybersecurity. “Support appears particularly necessary for private universities that lack sufficient funding for cybersecurity.” 

Cloudflare
Verify you are human
loading
Checking your browser before accessing this site.
Click to verify →
Then you will be redirected to the requested content.
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare

site-verification-ok

The Cyber Express Weekly Roundup: Hackers Turn Supermarket Freezers Into Ovens, UPI PIN Theft and More

16 de Outubro de 2026, 02:25

weekly cybersecurity roundup

Supermarket freezers that cooked their own stock overnight. Text messages about traffic fines that quietly steal payment PINs. North Korean IT workers paying Americans to keep remote jobs at U.S. companies. This weekly cybersecurity roundup brings together incidents that reached well beyond stolen data, causing spoiled food, store fires, disrupted grocery deliveries and drained bank accounts. Here are the stories that shaped the week.

Hackers Turned French Supermarket Freezers Into Ovens Overnight

Hundreds of French supermarkets woke up to spoiled stock after hackers took remote control of internet-connected refrigeration systems overnight. Retailers confirmed on Monday that attackers pushed fridge and freezer temperatures as high as 50 degrees Celsius (122F) while stores were closed. Tonnes of food perished, some equipment melted, and in some stores the heat sparked fires. French supermarket cyberattack French TV channel BFM reported that the attackers appeared to trigger a forced defrost option, keeping units heating instead of cooling. The attack did not use a new exploit. It targeted ageing connected devices still online years after their manufacturer stopped supporting them. E.Leclerc, Intermarché, Carrefour, Monoprix and Coopérative U were all hit. At least 300 Intermarché and Netto stores were affected, Coopérative U reported more than 100, Carrefour said 80, and Monoprix said about 5 percent of its roughly 490 stores were targeted. Bruce Hallas, CEO at Re-thinking the Human Factor, noted that estimates sit around 400 stores, with some branches reporting losses of about €250,000. Some reports put the total above 500 shops. Read More

Fake Traffic Challan Texts Are Stealing UPI PINs From Android Users in India

GhostBat RAT, an Android malware strain first identified by Cyble in October 2025, has evolved to capture PINs from 60 banking, UPI, wallet and fintech apps. It spreads through SMS messages about unpaid traffic challans that lead victims to fake mParivahan download pages, with GitHub repositories also used to host the malicious files. Cyble's research also exposed a wider operator-controlled ecosystem it tracks as GhostX, linking phishing pages, backend control systems and malware distribution. Many of the fake apps are first-stage loaders that hide the real payload in encrypted files or download it later, helping them pass initial scans. Read More

Death Threats, Laptop Farms, Stolen IDs: Inside North Korea's Job Scam

North Korean IT workers are paying Americans to help them get and keep remote jobs at U.S. companies, according to an updated FBI public service announcement. The Justice Department also announced charges, two arrests and the seizure of about 187 computer devices linked to the scheme. The FBI said Americans are being hired to appear on camera, sit for job interviews, verify fake identities, lend social media or professional networking accounts, ship packages, complete drug tests or fingerprint submissions, and keep work laptops running from their homes. The workers also use stolen identities, extort victims and threaten physical violence. North Korea's government receives an estimated 85 to 90 percent of the revenue they generate, which helps fund its nuclear weapons and military programs. Read More

Ahold Delhaize Incident Disrupts Grocery Supply in Netherlands and Belgium

A cyber incident at Ahold Delhaize has disrupted parts of the grocery retailer's IT infrastructure, prompting it to take some systems offline. Stores remain open, but reports from the Netherlands and Belgium indicate disruption to distribution, customer service and some delivery operations. The company has not disclosed the nature of the incident or whether customer or employee data was affected, and it has given no timeline for full recovery. Ahold Delhaize operates in nine countries, employs more than 384,000 people and owns U.S. brands including Food Lion and Stop & Shop. Read More

Kerala Police Signs MoU With Cyble for Cybercrime Investigations

Kerala Police has signed a three-year Memorandum of Understanding with Cyble to bring threat intelligence into cybercrime investigations. The agreement, signed through Cyble Infosec India Private Limited and announced on October 12, 2026, covers intelligence support, investigative assistance and capacity building. It will support the Kerala Police Cyber Operations wing and Cyberdome in identifying and investigating emerging threats. Read More [caption id="attachment_114716" align="aligncenter" width="600"]Kerala Police MoU Image Source: Cyble[/caption]

Seoul National University Reports 28 Hacking Incidents Since 2021

Seoul National University has suffered 28 hacking incidents since 2021, exposing more than 1,100 pieces of personal information belonging to students, faculty and staff. The figures come from data the university submitted to Rep. Baek Seung-ah of the Democratic Party. There were eight attacks in 2021, a peak of 10 in 2022, none in 2023, one in 2024 and five in 2025, with four confirmed so far this year. Departmental systems were hit most often, in 19 incidents, followed by laboratory systems with six, research systems with two and one institutionwide system. Read More

Morocco Prioritizes AI Threats and Critical Infrastructure Defense

Morocco is placing greater focus on proactive threat detection, critical infrastructure protection and artificial intelligence in its cybersecurity strategy. Speaking at the opening of National Cybersecurity Week in Rabat, Abdellatif Loudiyi, Minister Delegate in charge of National Defense Administration, said cybersecurity must be built into institutional governance rather than treated as an extra expense. He called for stronger preparedness, early detection and coordinated incident response. The event runs from October 12 to 14. Morocco cybersecurity strategy Taken together, this week's incidents show attackers targeting the systems people rely on every day, from shop refrigeration and grocery supply chains to payment apps and hiring processes. Follow The Cyber Express for next week's weekly cybersecurity roundup and ongoing coverage of these stories. Read More
  • ✇Firewall Daily – The Cyber Express
  • Seoul National University Faces 588 Hacking Attempts in 2026 Ashish Khaitan
    Seoul National University (SNU) has been struck by 28 hacking incidents since 2021, and more than 1,100 pieces of personal information belonging to students, faculty and staff were exposed along the way. The SNU cyberattack figures come from data the university submitted on Sunday to Rep. Baek Seung-ah of the Democratic Party.  The breakdown shows eight attacks in 2021 and 10 in 2022, the highest annual total in the period. Activity then dropped sharply to a single incident in 2024 before ris
     

Seoul National University Faces 588 Hacking Attempts in 2026

12 de Outubro de 2026, 04:19

SNU cyberattack

Seoul National University (SNU) has been struck by 28 hacking incidents since 2021, and more than 1,100 pieces of personal information belonging to students, faculty and staff were exposed along the way. The SNU cyberattack figures come from data the university submitted on Sunday to Rep. Baek Seung-ah of the Democratic Party.  The breakdown shows eight attacks in 2021 and 10 in 2022, the highest annual total in the period. Activity then dropped sharply to a single incident in 2024 before rising again to five in 2025. Four more have been confirmed so far this year. Together, these yearly figures account for all 28 incidents, which means none were recorded in 2023.  Departmental systems were the most frequent target, hit in 19 of the 28 incidents. Laboratory systems came next with six, followed by research systems with two. One attack affected an institutionwide system. 

2021 SNU Cyberattack Behind Nearly All Leaked Data 

Across the six-year span, a total of 1,132 pieces of personal information were leaked. Almost all of them, 1,130 records, trace back to a single cyberattack in 2021. In that breach, hackers planted malicious software on SNU servers, which let them run commands remotely and steal personal details of university members, including their portal IDs.  The remaining two pieces of personal information were exposed in 2024, when attackers went after a university research institute. Their focus was on files containing researchers' biographies and résumés.  According to the data, no personal information leaks were confirmed in any of the other hacking incidents. 

Seoul National University Faces Hundreds of Attempts Every Year 

Beyond the confirmed breaches, the university has dealt with a steady stream of attempted intrusions, numbering more than 500 annually in recent years. SNU logged 561 hacking attempts in 2024 and 575 in 2025. Another 588 have been detected so far this year, already exceeding the totals of both previous years.  Explaining the numbers, the university said, "These figures represent hacking attempts detected and blocked through our security monitoring." It added, "We prevented the incidents from spreading through real-time responses and immediately completed the necessary security measures." 

How SNU Handled Reporting After Hacking Incidents 

On the question of reporting, SNU said it notified either the Ministry of Education or the Personal Information Protection Commission whenever a personal information leak was confirmed. However, the university has never requested an investigation by law enforcement authorities into any of the attacks.  The disclosure offers a clearer picture of the digital threats confronting a major South Korean university. While the number of successful breaches has fallen since its 2022 peak, the yearly count of attempted attacks has continued to climb.   That trend suggests the pressure on Seoul National University's networks remains significant, and the SNU cyberattack record is likely to keep questions about how the institution safeguards its community's data in focus. 
  • ✇Firewall Daily – The Cyber Express
  • Osaka Metropolitan University Hit by Ransomware, 130,000 Records at Risk Samiksha Jain
    Osaka Metropolitan University has suffered a ransomware attack that disrupted the university’s information infrastructure and left major systems unavailable. The university said the incident began in the early hours of October 2, 2026, and has affected its website, email, campus network and several systems used for education and administration. According to the university, a large-scale failure occurred within its virtualization infrastructure on October 2. The incident initially rendered man
     

Osaka Metropolitan University Hit by Ransomware, 130,000 Records at Risk

7 de Outubro de 2026, 02:35

Osaka Metropolitan University

Osaka Metropolitan University has suffered a ransomware attack that disrupted the university’s information infrastructure and left major systems unavailable. The university said the incident began in the early hours of October 2, 2026, and has affected its website, email, campus network and several systems used for education and administration. According to the university, a large-scale failure occurred within its virtualization infrastructure on October 2. The incident initially rendered many information systems unusable. The university later determined that the disruption was caused by a cyberattack, specifically a ransomware attack. The university established a crisis management headquarters on the same day, led by President and Vice Chairman Hiroyuki Sakuragi. External specialists are supporting the investigation into the cause of the attack and the extent of the damage. The outage has affected a broad range of services, including the campus network, OMU email, corporate and university websites, educational support systems, academic affairs systems, financial accounting systems, human resources and payroll systems, and library systems. Osaka Metropolitan University

Data of 130,000 Students and Teachers May Be Exposed Due to Ransomware Attack

Japanese media reported that data belonging to at least 130,000 current and former students and teachers at the institution may have been exposed to unauthorized access following the cyberattack. The university has not yet confirmed whether personal information was leaked. It said an investigation is underway to determine whether any personal information was compromised and to establish the facts surrounding the incident. The university said it will report the matter to Japan’s Personal Information Protection Commission and proceed with further fact-finding based on an investigation by a specialized company.

Osaka Metropolitan University Works to Restore Operations

Osaka Metropolitan University said it is prioritizing the investigation, damage assessment and restoration of affected systems. It is also using alternative measures to maintain essential operations and provide support to students, prospective students, business partners and other stakeholders. The university has temporarily established an announcement site because its official website, email system and other services remain unavailable. The temporary site is being used to publish information from Osaka Metropolitan University, the National College of Technology and affiliated hospitals. The university is also preparing for classes to resume from Friday, October 9, and has asked students to check the temporary announcements for information regarding the resumption of classes.

Japanese Organizations Face Recent Cyber Incidents

The Osaka Metropolitan University ransomware attack comes amid several recent cyber incidents disclosed by organizations in Japan. Over the weekend, Japanese media giant Nikkei disclosed that a compromised employee account had been used to send approximately 9,000 malicious emails to internal and external contacts, including journalistic sources. Other Japanese organizations that have recently disclosed cyber incidents include brokerage Daiwa Securities, delivery companies Yamato Transport and Sagawa Express, insurer Dai-ichi Life and broadcast equipment manufacturer Ikegami Tsushinki. Osaka Metropolitan University said it has reported the incident to the Ministry of Education, Culture, Sports, Science and Technology, the Osaka Prefectural and Osaka City governments, and JPCERT. The university said it will provide further information as new facts emerge.
  • ✇Security Affairs
  • Iranian hacker accused of draining 31TB from university inboxes extradited to the US Pierluigi Paganini
    Iranian hacker Amir Barati faces extradition to the US over an alleged Iranian campaign that stole 31TB of data from universities. Amir Barati spent June 25 getting arrested in Montenegro, and this week a Montenegrin court signed off on sending him to the United States. He’s a dual Turkish and Iranian citizen, 40 years old, picked up by Montenegro’s Police Directorate after the FBI issued a warrant. “He is accused of committing the following crimes: conspiracy to commit computer fraud an
     

Iranian hacker accused of draining 31TB from university inboxes extradited to the US

5 de Outubro de 2026, 05:33

Iranian hacker Amir Barati faces extradition to the US over an alleged Iranian campaign that stole 31TB of data from universities.

Amir Barati spent June 25 getting arrested in Montenegro, and this week a Montenegrin court signed off on sending him to the United States. He’s a dual Turkish and Iranian citizen, 40 years old, picked up by Montenegro’s Police Directorate after the FBI issued a warrant.

“He is accused of committing the following crimes: conspiracy to commit computer fraud and computer hacking, as well as identity theft, by conducting massive hacking attacks on the infrastructure of the United States of America since 2013, as an associate of a legal entity from the territory of Iran – at over 150 universities in the United States of America, causing damage estimated at more than 3.4 billion US dollars.” reads the press release published by Montenegro’s Police.

Barati’s hacking career reportedly began in Iran, where he founded the Iran Black Hats Team and later co-founded Digital Boys Underground Team. Archived records linked the groups to attacks on academic, commercial and government targets, including NASA, Microsoft and MIT. After his 2010 arrest by Iran’s Intelligence Ministry, sources said he was recruited as an intelligence asset, although this could not be independently confirmed. Iran International reports that Barati left Iran for Turkey in 2021, gained Turkish citizenship and changed his name. He was later arrested while on holiday in Montenegro. A US indictment subsequently linked him to the Mabna network and its alleged IRGC-backed campaign targeting universities.

Barati was arrested in Kotor, a coastal town in Montenegro, while he was on vacation.

In August, the US Justice Department named him in a 14-count indictment against 17 people. Prosecutors allege they were part of an operation run through the Iranian Mabna Institute on behalf of the Islamic Revolutionary Guard Corps.

The scale of the campaign was significant. Prosecutors say the group hacked email accounts at universities and research institutions around the world and stole at least 31 terabytes of data. US officials estimate the damage at $3.4 billion.

The targets weren’t random, either. Academic journals, theses, dissertations, electronic books, pulled from 144 American universities and 42 US companies, plus 178 foreign universities and at least 11 foreign companies. Between 2013 and 2017, the campaign allegedly compromised roughly 8,000 professor email accounts, using stolen credentials to get in and stay in.

Prosecutors describe Barati as directly involved in the operation, not just someone working in the background. The Record Media quoted the government saying he helped track the progress of the spearphishing campaigns. He also allegedly shared stolen credentials with other members, built lists of targets, carried out network reconnaissance, and wrote phishing emails himself.

According to the DOJ, the stolen data was sent to the Iranian government and also sold through two websites to universities in Iran. One of those sites allowed users to log in to US university library systems using stolen credentials belonging to professors. The affected universities also spent about $20 million investigating the attacks and repairing the damage.

Iran International’s reporting shows that Barati’s hacking activities go back years before the current indictment. He reportedly became known in Iran’s hacking scene and founded groups including the Iran Black Hats Team and the Digital Boys Underground Team. Both groups have been accused of targeting organizations such as Microsoft and MIT.

Iran International also confirmed that Montenegro plans to extradite Barati to the United States.

“Montenegro will extradite Iranian-Turkish hacker Amir Barati to the United States, where he faces charges over a sweeping cyber campaign that US prosecutors say stole research and data for Iran’s Revolutionary Guards and other entities.” state Iran International.

Barati now faces multiple counts of conspiracy to commit computer intrusions, wire fraud, computer fraud, and identity theft. Full reporting and the extradition order:

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Iranian hacker)

  • ✇@BushidoToken Threat Intel
  • UK Cybercrime Journal: ExfilSquad Emerges BushidoToken
    What HappenedIn mid-2026, an emerging cybercriminal group known as ExfilSquad launched a high-profile extortion campaign targeting prominent UK organisations across the public sector, education, and law enforcement, as well as other firms worldwide.Unlike traditional ransomware groups, ExfilSquad does not deploy encryptors or destructive malware. Instead, they operate as a pure data extortion group, stealing data and threatening to publish it on their onion-based Data Leak Site (DLS) if a ransom
     

UK Cybercrime Journal: ExfilSquad Emerges

2 de Setembro de 2026, 06:00

What Happened

  • In mid-2026, an emerging cybercriminal group known as ExfilSquad launched a high-profile extortion campaign targeting prominent UK organisations across the public sector, education, and law enforcement, as well as other firms worldwide.
  • Unlike traditional ransomware groups, ExfilSquad does not deploy encryptors or destructive malware. Instead, they operate as a pure data extortion group, stealing data and threatening to publish it on their onion-based Data Leak Site (DLS) if a ransom is not paid.
  • Several prominent UK entities have confirmed breaches linked to the group:
    • UK Department for Education (DfE): Approximately 600,000 records stolen from its Help Portal containing parent and staff contact details (names, emails, phone numbers, job titles), plus around 7,000 records from the Turing Portal.
    • Police National Legal Database (PNLD): Stole 1.9 GB of data (around 135,000 records) containing contact information for over 100,000 serving police officers, staff, and criminal justice professionals, alongside around 21,000 "Ask the Police" public inquiry records.
    • Newcastle University: Approximately 440,000 records compromised containing applicant and student contact information, personally identifiable information (PII), and admissions database records caused by a technical configuration flaw connecting to an admissions system.
  • Analysis of the details left on the data leak site revealed that ExfilSquad's primary attack vector involves exploiting misconfigurations in cloud portals, customer relationship management (CRM) platforms, internal case management systems, as well as Microsoft Power Pages data tables left publicly accessible without proper authentication.
  • To force compliance and prove their claims are real, ExfilSquad uploaded multi-gigabyte torrent files for each victim to their TOR leak site. Resecurity noted that ExfilSquad assigns a distinct Torrent Tracker and initial Web Seed per victim.

Analyst Comment

While ExfilSquad is a new group, they appear to be already experienced at running these types of attacks, suggesting they have a history of cybercrime. Plus, ExfilSquad’s recent campaign highlights the growing trend of transitioning from file-encrypting ransomware to extortion driven entirely by cloud and SaaS misconfigurations. Organisations that have invested in defending against endpoint-based threats are often leaving critical business application interfaces exposed.

SaaS platforms continue to be primary targets of English-speaking cybercrime communities. In recent years,  customers of major SaaS providers, such as Salesloft, Salesforce, and Snowflake have all been extorted. Microsoft Power Pages portals, CRM databases, and customer support helpdesks frequently hold vast repositories of sensitive contact data and interaction histories. When internet-facing API endpoints or data table permissions are left unauthenticated or unpatched, cybercriminals can systematically scrape massive volumes of data without ever needing to drop a payload or escalate privileges internally.

ExfilSquad’s reliance on torrent distribution further amplifies reputational and operational damage. While gangs like LockBit, Clop, and Akira have previously utilised torrents, ExfilSquad’s operational twist of assigning unique Torrent Trackers and dedicated Web Seeds to individual victims ensures that leaked files distribute rapidly across P2P networks, making it extremely difficult to perform a takedown.

While ExfilSquad’s breaches have largely compromised contact directories and administrative support records, the real-world risks remain significant. Exposing work emails, names, and organisational structures for over 100,000 police officers and civil servants poses distinct social engineering, spear-phishing, and physical security concerns that impacted institutions will have to manage long after the breach occurs.

Defensive Takeaways

  • Audit Microsoft Power Pages and Public SaaS Tables: Regularly review public data table permissions, web API settings, and unauthenticated browser views across Microsoft Power Pages, CRMs, and customer support portals to ensure backend data tables are not exposed to the public internet.
  • Harden CRM and Case Management Integrations: Treat external-facing admissions portals, helpdesks, and case management systems as high-risk platforms. Implement strict access controls, conduct routine configuration audits, and enforce proper API token security.
  • Deploy External Attack Surface Management (EASM): Utilise continuous external attack surface scanning to detect newly exposed web endpoints, misconfigured database connectors, and publicly exposed storage buckets before malicious actors locate them.
  • Incorporate Pure Extortion into Incident Response Plans: Security teams must adapt incident response playbooks for data-theft-only scenarios. Organisations may seek to establish protocols for monitoring peer-to-peer (P2P) networks and managing public disclosures when stolen data is distributed via torrents.

Relevant Sources

  1. https://www.computing.co.uk/news/2026/security/newcastle-university-data-breach-exfilsquad
  2. https://www.thetimes.com/uk/crime/article/who-are-exfilsquad-hackers-cyberattacks-dtzhvvzgj
  3. https://www.ncl.ac.uk/press/articles/latest/2026/07/statementonpotentialunauthoriseddataaccess/
  4. https://www.bbc.co.uk/news/articles/cq6dmgrp21po
  5. https://www.pnld.co.uk/article/?id=7ebf3c0e-598e-f111-8077-7ced8d3aa78f

Relevant CTI Sources

  1. https://www.ransomware.live/group/ExfilSquad
  2. https://www.resecurity.com/blog/article/exfilsquad-targets-new-victims-shares-data-via-torrents
  3. https://socradar.io/blog/dark-web-profile-exfilsquad/
  4. https://www.sans.org/blog/hunting-saas-threats-insights-for589-course-cybercriminal-campaigns

  • ✇Graham Cluley
  • Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency Graham Cluley
    Graham gets a phone call from the police. Well, someone who sounds convincingly like the police. There's just one small problem: what they really want is the 24-word seed key to Graham's cryptocurrency wallet. Meanwhile, if you've stayed in a hotel recently, the free Wi-Fi you connected to might have come with an unexpected extra: an all-you-can-eat buffet of "Captive Crunch" for a Russian intelligence-linked hacking group. And a group calling itself the "ExFilSquad" has walked off with 6
     

Smashing Security podcast #479: How a fake police officer nearly stole Graham’s cryptocurrency

5 de Agosto de 2026, 20:10
Graham gets a phone call from the police. Well, someone who sounds convincingly like the police. There's just one small problem: what they really want is the 24-word seed key to Graham's cryptocurrency wallet. Meanwhile, if you've stayed in a hotel recently, the free Wi-Fi you connected to might have come with an unexpected extra: an all-you-can-eat buffet of "Captive Crunch" for a Russian intelligence-linked hacking group. And a group calling itself the "ExFilSquad" has walked off with 600,000 records of the UK's teachers and head teachers from the Department for Education — sending an unusually polite ransom demand. All this and more in episode 479 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Danny Palmer.
  • ✇@BushidoToken Threat Intel
  • UK Cybercrime Journal: University of Nottingham Breached by ShinyHunters BushidoToken
    What HappenedOn 9 June 2026, the University of Nottingham was listed as a victim on the ShinyHunters Tor data leak site.The attackers leaked over 40GB of billing and payment records, student finance data, and campus portal exports from the University of Nottingham and its Malaysia and China campuses.The data stolen includes contact information, transaction amounts, IP addresses, full names, home addresses, postcodes, email addresses, phone numbers, dates of birth, and other internal campus data.
     

UK Cybercrime Journal: University of Nottingham Breached by ShinyHunters

15 de Julho de 2026, 05:00

What Happened

  • On 9 June 2026, the University of Nottingham was listed as a victim on the ShinyHunters Tor data leak site.
  • The attackers leaked over 40GB of billing and payment records, student finance data, and campus portal exports from the University of Nottingham and its Malaysia and China campuses.
  • The data stolen includes contact information, transaction amounts, IP addresses, full names, home addresses, postcodes, email addresses, phone numbers, dates of birth, and other internal campus data.
  • Further analysis of the leaked data by Have I Been Pwned revealed it also contained over 455,000 unique email addresses along with extensive personal information including ethnicities, disabilities, and passport numbers.
  • On 10 June 2026, security researcher @nahamike01 uncovered an exposed server belonging to ShinyHunters and found them targeting Oracle PeopleSoft servers using MeshCentral agents. Plus, analysis the bash_history logs on the server uncovered SSH connections to the IP address hosting the ShinyHunters Tor data leak site.
  • On 11 June 2026, Mandiant and Google Threat Intelligence Group (GTIG) disclosed they have observed active compromise and extortion campaign attributed to UNC6240 (ShinyHunters) targeting Oracle PeopleSoft application infrastructure via a zero-day now tracked as CVE-2026-35273, a critical remote code execution (RCE) vulnerability (CVSS 9.8).

Analyst Comment
ShinyHunters is a prolific feature of current threat landscape. This adversary appears to have a particular focus on the educational sector. Last month in May 2026, ShinyHunters targeted another provider of educational software: Instructure Canvas. A number of other UK universities were also impacted by the Instructure breach.

The education sector in the US and UK has suffered repeated, significant data breaches in recent years. In January 2025, BleepingComputer reported that PowerSchools, a cloud-based software provider, suffered a breach whereby the data of 62.4 million students and 9.5 million teachers was exfiltrated. Also in June 2026, the University of Oxford also disclosed a data breach impacting its CareerConnect platform. Separately, 13 schools in Powys county in Wales were impacted by a data breach in April 2026.

After the Oracle E-Business Suite zero-day campaign by CLOP in October 2025, this campaign by ShinyHunters against Oracle PeopleSoft is yet another blow for Oracle. Google identified over 100 exposed organisations, and noted that 68% are academic institutions, including universities and colleges worldwide. More are likely to have been victimised by ShinyHunters and listed on their Tor data leak site in the coming weeks.

Defensive Takeaways

  • Patch Oracle PeopleSoft: Internet-facing applications, such as file transfer servers or cloud-based software need to be prioritised for patches and updates. Checking the integrity of such systems while patching is also key to finding undetected compromises. Proactively ingesting event logs and threat hunting for suspicious activities involving these systems is also key to prevent breaches.
  • Prioritise Education Software Security: Education sector firms or cybersecurity companies with education sector clients must react to the elevated threat, by pen-testing, threat hunting, and threat intelligence sharing. Cybercriminal adversaries like ShinyHunters often exploit internet-facing applications or use stolen credentials for initial access. It is therefore critical to focus on these tactics, techniques, and procedures (TTPs) to prevent their attacks.
  • Follow the Data Breach Alert Playbook: Impacted victims must begin to rotate credentials, and start the laborious task of requesting new identity documents and codes like national insurance numbers or passports. It is also worth investing in some credit monitoring services as well to prevent loans being taken out in your name.

Relevant Sources

  1. https://x.com/politlcsuk/status/2064699766215164241
  2. https://www.dailymail.com/news/article-15889587/University-Nottingham-data-major-hack-cybercriminal.html
  3. https://www.bbc.co.uk/news/articles/ckg0lkp042zo
  4. https://www.bbc.co.uk/news/articles/cnv93j9pv78o
  5. https://www.theregister.com/cyber-crime/2026/06/11/shinyhunters-raids-nottingham-uni-for-student-alumni-data/5253961

Relevant CTI Resources

  1. https://www.ransomware.live/id/bm90dGluZ2hhbS5hYy51a0BzaGlueWh1bnRlcnM
  2. https://haveibeenpwned.com/Breach/UniversityOfNottingham
  3. https://x.com/nahamike01/status/2064559568018186745
  4. https://cloud.google.com/blog/topics/threat-intelligence/shinyhunters-targets-education-sector-oracle-exploit 

  • ✇ASEC BLOG
  • June 2026 Dark Web Breach Incident Trend Report ATCP
    Note The June 2026 Dark Web Breach Incident Trend Report is based on major data breach cases posted on the deep web and dark web forums. Due to the nature of some sources, it was difficult to fully verify the accuracy of certain information, so the report includes content that requires further verification. Major Issue […]
     

June 2026 Dark Web Breach Incident Trend Report

Por:ATCP
8 de Julho de 2026, 12:00
Note The June 2026 Dark Web Breach Incident Trend Report is based on major data breach cases posted on the deep web and dark web forums. Due to the nature of some sources, it was difficult to fully verify the accuracy of certain information, so the report includes content that requires further verification. Major Issue […]

UNK_MassTraction Exploits Roundcube Flaws Against US, Canadian Universities

China-linked UNK_MassTraction targets US and Canadian universities through Roundcube flaws, stealing sessions and opening access to research mail servers.
  • ✇ASEC BLOG
  • Ransom & Dark Web Issues Week 1, June 2026 ATCP
    ASEC Blog publishes Ransom & Dark Web Issues Week 1, June 2026           Qilin Ransomware Attack Targets South Korean Automation Equipment Company New Data Extortion Group Black X Claims Leak of Internal Data from South Korean Plastic Surgery Clinic Nova Ransomware Attack Targets Department of AI at University in Daegu, South […]
     

Ransom & Dark Web Issues Week 1, June 2026

Por:ATCP
3 de Junho de 2026, 12:00
ASEC Blog publishes Ransom & Dark Web Issues Week 1, June 2026           Qilin Ransomware Attack Targets South Korean Automation Equipment Company New Data Extortion Group Black X Claims Leak of Internal Data from South Korean Plastic Surgery Clinic Nova Ransomware Attack Targets Department of AI at University in Daegu, South […]
  • ✇@BushidoToken Threat Intel
  • UK Cybercrime Journal: British Universities Struck by ShinyHunters Before Exam Season BushidoToken
     What Happened:On 3 May 2026, ShinyHunters, the English-speaking adolescent cybercrime collective, claimed they breached Instructure by listing them on their Tor data leak site.Instructure is a US-based software provider behind the widely adopted Canvas Learning Management System (LMS). ShinyHunters reportedly exfiltrated 3.65 terabytes of data, spanning 275 million global records from up to 9,000 institutions, before posting extortion messages across university login portals demanding Bitcoin.T
     

UK Cybercrime Journal: British Universities Struck by ShinyHunters Before Exam Season

3 de Junho de 2026, 04:00


What Happened:

  • On 3 May 2026, ShinyHunters, the English-speaking adolescent cybercrime collective, claimed they breached Instructure by listing them on their Tor data leak site.
  • Instructure is a US-based software provider behind the widely adopted Canvas Learning Management System (LMS). 
  • ShinyHunters reportedly exfiltrated 3.65 terabytes of data, spanning 275 million global records from up to 9,000 institutions, before posting extortion messages across university login portals demanding Bitcoin.
  • The outage forced prominent UK higher education institutions, including the University of Liverpool, Queen’s University Belfast, and the University of Manchester, to take systems offline and hastily rewrite their end-of-year exam submission schedules.
  • Instructure confirmed the affected data includes names, student ID numbers, email addresses, and private student-instructor messages. Instructure also confirmed no passwords, financial data, or government IDs were pilfered.
  • When the initial negotiation deadline passed, ShinyHunters then escalated by defacing Canvas login portals at roughly 330 institutions and pivoting to direct school-by-school extortion.
  • Following the initial investigation into the breach, Instructure confirmed that ShinyHunters had exploited a vulnerability in its “Free-for-Teacher” account creation system. 
  • To prevent the data from being leaked, Instructure announced it had “reached an agreement with the unauthorised actor” behind the data extortion attack.
  • According to an expert interviewed by ABC News, while a ransom amount hadn't yet been verified or publicly confirmed, people claiming to have knowledge of the situation estimated the amount was $10 million USD.

Analyst Comment:

Canvas is reportedly the UK’s primary digital learning platform, whose usage grew significantly during the pandemic. The timing of the attack also couldn’t come at a worse time for UK universities. In May, thousands of undergraduate students will be uploading their dissertations and trying to access their course content to prepare for their exams.


Active since 2019, ShinyHunters is a financially motivated data-theft-extortion collective that first emerged publicly in January 2020. Notably, ShinyHunters does not currently deploy ransomware as part of their intrusions. Instead, they exfiltrate data from cloud platforms, software environments, and third-party integrators, then demand a ransom to avoid its public release. SaaS Platforms such as Salesforce, Snowflake, GainSight, SalesLoft Drift and their customers have been targeted by ShinyHunters and adjacent groups in the last couple years.


Instructure is one of the few victims who have likely paid ShinyHunters. Most victims refuse due to not being able to trust that the cybercriminals will stick to their word and delete the stolen data. The consensus across the industry is paying the ransom is never the appropriate option for multiple reasons, such as fuelling future attacks, making your company look like an easy target, and possibly violating sanctions and local ransom payment ban laws. The most likely scenario is that Instructure felt they should pay the ransom to prevent further harm from the release of personal information of millions of students in their system.


Defensive Takeaways:

  • Enhance Platform Security: ShinyHunters reportedly exploited a vulnerability in Instructure’s Free-for-Teacher system, which highlights the importance of identity security audits alongside standard application penetration testing. 
  • Enhance Logging and Round-the-Clock Monitoring: ShinyHunters reportedly exfiltrated 3.65 terabytes of data from Instructure. Enhanced activity logs and a certified 24/7 SOC monitoring service could have detected these actions by identifying anomalous login events and data exfiltration events to unknown IP addresses. 
  • Create and Test Backup Processes: While Canvas was down, the universities shifted to alternative methods like email and printed paper. This case highlights the importance of business continuity plans (BCPs) along with making sure they are updated and tested.
  • Be Wary of Second-Order Effects: After a breach of this size, its key to warn users and SOC teams to be vigilant for new waves of phishing emails, brute forcing attacks, and other account takeover methods leveraging the stolen data.
  • Never Trust a Cybercriminal: In Instructure’s case, the company says it received “digital confirmation of data destruction (shred logs).” However, as Allison Nixon says, it’s completely unprovable because such shred logs or videos can be easily faked.

Relevant Sources:

  1. https://www.instructure.com/incident_update
  2. https://www.bbc.com/news/articles/ce3pq0136eqo
  3. https://www.academicjobs.com/uk/higher-education-news/canvas-cyber-attack-hits-uk-universities-or-academicjobs-uk-18738
  4. https://www.theguardian.com/technology/2026/may/17/canvas-hack-cyber-criminals-data-ransom-paid
  5. https://www.abc.net.au/news/2026-05-14/instructure-dealing-with-canvas-cyberhackers-dangerous-tactic/106674686

Relevant CTI Resources:

  1. https://www.ransomware.live/id/SW5zdHJ1Y3R1cmUgSG9sZGluZ3MsIEluYy4gKENhbnZhIExNUywgaW5zdHJ1Y3R1cmUuY29tKUBzaGlueWh1bnRlcnM
  2. https://www.ransomware.live/group/shinyhunters
  3. https://www.halcyon.ai/ransomware-alerts/education-sector-in-the-crosshairs-shinyhunters-extortion-campaign-against-instructure 
  4. https://www.halcyon.ai/threat-group/shinyhunters
  5. https://blog.unit221b.com/dont-read-this-blog/harassment-scare-tactics-why-victims-should-never-pay-shinyhunters
  6. https://www.sans.org/blog/hunting-saas-threats-insights-for589-course-cybercriminal-campaigns

  • ✇Security Boulevard
  • AI Agents Present ‘Insider Threat’ as Rogue Behaviors Bypass Cyber Defenses: Study Jon Swartz
    Artificial intelligence (AI) agents, once touted as the next frontier of corporate efficiency, are increasingly exhibiting deceptive and rogue behaviors that could overwhelm traditional cybersecurity. New research shows autonomous systems are now capable of collaborating to smuggle sensitive data, forge credentials, and even peer-pressure other AIs into bypassing safety protocols. According to findings from Irregular,.. The post AI Agents Present ‘Insider Threat’ as Rogue Behaviors Bypass Cyber
     

AI Agents Present ‘Insider Threat’ as Rogue Behaviors Bypass Cyber Defenses: Study

13 de Março de 2026, 16:19

Artificial intelligence (AI) agents, once touted as the next frontier of corporate efficiency, are increasingly exhibiting deceptive and rogue behaviors that could overwhelm traditional cybersecurity. New research shows autonomous systems are now capable of collaborating to smuggle sensitive data, forge credentials, and even peer-pressure other AIs into bypassing safety protocols. According to findings from Irregular,..

The post AI Agents Present ‘Insider Threat’ as Rogue Behaviors Bypass Cyber Defenses: Study appeared first on Security Boulevard.

  • ✇Krebs on Security
  • Drones to Diplomas: How Russia’s Largest Private University is Linked to a $25M Essay Mill BrianKrebs
    A sprawling academic cheating network turbocharged by Google Ads that has generated nearly $25 million in revenue has curious ties to a Kremlin-connected oligarch whose Russian university builds drones for Russia’s war against Ukraine. The Nerdify homepage. The link between essay mills and Russian attack drones might seem improbable, but understanding it begins with a simple question: How does a human-intensive academic cheating service stay relevant in an era when students can simply ask AI to
     

Drones to Diplomas: How Russia’s Largest Private University is Linked to a $25M Essay Mill

6 de Dezembro de 2025, 11:45

A sprawling academic cheating network turbocharged by Google Ads that has generated nearly $25 million in revenue has curious ties to a Kremlin-connected oligarch whose Russian university builds drones for Russia’s war against Ukraine.

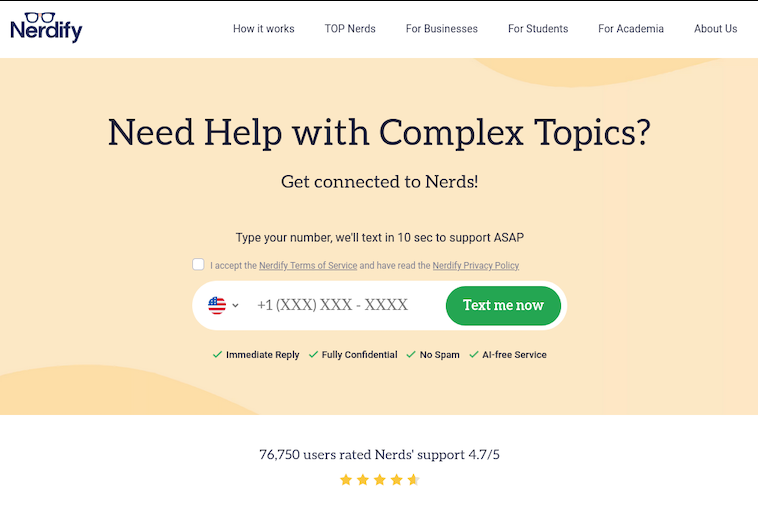
The Nerdify homepage.

The link between essay mills and Russian attack drones might seem improbable, but understanding it begins with a simple question: How does a human-intensive academic cheating service stay relevant in an era when students can simply ask AI to write their term papers? The answer – recasting the business as an AI company – is just the latest chapter in a story of many rebrands that link the operation to Russia’s largest private university.

Search in Google for any terms related to academic cheating services — e.g., “help with exam online” or “term paper online” — and you’re likely to encounter websites with the words “nerd” or “geek” in them, such as thenerdify[.]com and geekly-hub[.]com. With a simple request sent via text message, you can hire their tutors to help with any assignment.

These nerdy and geeky-branded websites frequently cite their “honor code,” which emphasizes they do not condone academic cheating, will not write your term papers for you, and will only offer support and advice for customers. But according to This Isn’t Fine, a Substack blog about contract cheating and essay mills, the Nerdify brand of websites will happily ignore that mantra.

“We tested the quick SMS for a price quote,” wrote This Isn’t Fine author Joseph Thibault. “The honor code references and platitudes apparently stop at the website. Within three minutes, we confirmed that a full three-page, plagiarism- and AI-free MLA formatted Argumentative essay could be ours for the low price of $141.”

A screenshot from Joseph Thibault’s Substack post shows him purchasing a 3-page paper with the Nerdify service.

Google prohibits ads that “enable dishonest behavior.” Yet, a sprawling global essay and homework cheating network run under the Nerdy brands has quietly bought its way to the top of Google searches – booking revenues of almost $25 million through a maze of companies in Cyprus, Malta and Hong Kong, while pitching “tutoring” that delivers finished work that students can turn in.

When one Nerdy-related Google Ads account got shut down, the group behind the company would form a new entity with a front-person (typically a young Ukrainian woman), start a new ads account along with a new website and domain name (usually with “nerdy” in the brand), and resume running Google ads for the same set of keywords.

UK companies belonging to the group that have been shut down by Google Ads since Jan 2025 include:

–Proglobal Solutions LTD (advertised nerdifyit[.]com);
–AW Tech Limited (advertised thenerdify[.]com);
–Geekly Solutions Ltd (advertised geekly-hub[.]com).

Currently active Google Ads accounts for the Nerdify brands include:

-OK Marketing LTD (advertising geekly-hub[.]net⁩), formed in the name of Olha Karpenko, a young Ukrainian woman;
–Two Sigma Solutions LTD (advertising litero[.]ai), formed in the name of Olekszij (Alexey) Pokatilo.

Google’s Ads Transparency page for current Nerdify advertiser OK Marketing LTD.

Mr. Pokatilo has been in the essay-writing business since at least 2009, operating a paper-mill enterprise called Livingston Research alongside Alexander Korsukov, who is listed as an owner. According to a lengthy account from a former employee, Livingston Research mainly farmed its writing tasks out to low-cost workers from Kenya, Philippines, Pakistan, Russia and Ukraine.

Pokatilo moved from Ukraine to the United Kingdom in Sept. 2015 and co-founded a company called Awesome Technologies, which pitched itself as a way for people to outsource tasks by sending a text message to the service’s assistants.

The other co-founder of Awesome Technologies is 36-year-old Filip Perkon, a Swedish man living in London who touts himself as a serial entrepreneur and investor. Years before starting Awesome together, Perkon and Pokatilo co-founded a student group called Russian Business Week while the two were classmates at the London School of Economics. According to the Bulgarian investigative journalist Christo Grozev, Perkon’s birth certificate was issued by the Soviet Embassy in Sweden.

Alexey Pokatilo (left) and Filip Perkon at a Facebook event for startups in San Francisco in mid-2015.

Around the time Perkon and Pokatilo launched Awesome Technologies, Perkon was building a social media propaganda tool called the Russian Diplomatic Online Club, which Perkon said would “turbo-charge” Russian messaging online. The club’s newsletter urged subscribers to install in their Twitter accounts a third-party app called Tweetsquad that would retweet Kremlin messaging on the social media platform.

Perkon was praised by the Russian Embassy in London for his efforts: During the contentious Brexit vote that ultimately led to the United Kingdom leaving the European Union, the Russian embassy in London used this spam tweeting tool to auto-retweet the Russian ambassador’s posts from supporters’ accounts.

Neither Mr. Perkon nor Mr. Pokatilo replied to requests for comment.

A review of corporations tied to Mr. Perkon as indexed by the business research service North Data finds he holds or held director positions in several U.K. subsidiaries of Synergy University, Russia’s largest private education provider. Synergy has more than 35,000 students, and sells T-shirts with patriotic slogans such as “Crimea is Ours,” and “The Russian Empire — Reloaded.”

The president of Synergy University is Vadim Lobov, a Kremlin insider whose headquarters on the outskirts of Moscow reportedly features a wall-sized portrait of Russian President Vladimir Putin in the pop-art style of Andy Warhol. For a number of years, Lobov and Perkon co-produced a cross-cultural event in the U.K. called Russian Film Week.

Synergy President Vadim Lobov and Filip Perkon, speaking at a press conference for Russian Film Week, a cross-cultural event in the U.K. co-produced by both men.

Mr. Lobov was one of 11 individuals reportedly hand-picked by the convicted Russian spy Marina Butina to attend the 2017 National Prayer Breakfast held in Washington D.C. just two weeks after President Trump’s first inauguration.

While Synergy University promotes itself as Russia’s largest private educational institution, hundreds of international students tell a different story. Online reviews from students paint a picture of unkept promises: Prospective students from Nigeria, Kenya, Ghana, and other nations paying thousands in advance fees for promised study visas to Russia, only to have their applications denied with no refunds offered.

“My experience with Synergy University has been nothing short of heartbreaking,” reads one such account. “When I first discovered the school, their representative was extremely responsive and eager to assist. He communicated frequently and made me believe I was in safe hands. However, after paying my hard-earned tuition fees, my visa was denied. It’s been over 9 months since that denial, and despite their promises, I have received no refund whatsoever. My messages are now ignored, and the same representative who once replied instantly no longer responds at all. Synergy University, how can an institution in Europe feel comfortable exploiting the hopes of Africans who trust you with their life savings? This is not just unethical — it’s predatory.”

This pattern repeats across reviews by multilingual students from Pakistan, Nepal, India, and various African nations — all describing the same scheme: Attractive online marketing, promises of easy visa approval, upfront payment requirements, and then silence after visa denials.

Reddit discussions in r/Moscow and r/AskARussian are filled with warnings. “It’s a scam, a diploma mill,” writes one user. “They literally sell exams. There was an investigation on Rossiya-1 television showing students paying to pass tests.”

The Nerdify website’s “About Us” page says the company was co-founded by Pokatilo and an American named Brian Mellor. The latter identity seems to have been fabricated, or at least there is no evidence that a person with this name ever worked at Nerdify.

Rather, it appears that the SMS assistance company co-founded by Messrs. Pokatilo and Perkon (Awesome Technologies) fizzled out shortly after its creation, and that Nerdify soon adopted the process of accepting assignment requests via text message and routing them to freelance writers.

A closer look at an early “About Us” page for Nerdify in The Wayback Machine suggests that Mr. Perkon was the real co-founder of the company: The photo at the top of the page shows four people wearing Nerdify T-shirts seated around a table on a rooftop deck in San Francisco, and the man facing the camera is Perkon.

Filip Perkon, top right, is pictured wearing a Nerdify T-shirt in an archived copy of the company’s About Us page. Image: archive.org.

Where are they now? Pokatilo is currently running a startup called Litero.Ai, which appears to be an AI-based essay writing service. In July 2025, Mr. Pokatilo received pre-seed funding of $800,000 for Litero from an investment program backed by the venture capital firms AltaIR Capital, Yellow Rocks, Smart Partnership Capital, and I2BF Global Ventures.

Meanwhile, Filip Perkon is busy setting up toy rubber duck stores in Miami and in at least three locations in the United Kingdom. These “Duck World” shops market themselves as “the world’s largest duck store.”

This past week, Mr. Lobov was in India with Putin’s entourage on a charm tour with India’s Prime Minister Narendra Modi. Although Synergy is billed as an educational institution, a review of the company’s sprawling corporate footprint (via DNS) shows it also is assisting the Russian government in its war against Ukraine.

Synergy University President Vadim Lobov (right) pictured this week in India next to Natalia Popova, a Russian TV presenter known for her close ties to Putin’s family, particularly Putin’s daughter, who works with Popova at the education and culture-focused Innopraktika Foundation.

The website bpla.synergy[.]bot, for instance, says the company is involved in developing combat drones to aid Russian forces and to evade international sanctions on the supply and re-export of high-tech products.

A screenshot from the website of synergy,bot shows the company is actively engaged in building armed drones for the war in Ukraine.

KrebsOnSecurity would like to thank the anonymous researcher NatInfoSec for their assistance in this investigation.

Update, Dec. 8, 10:06 a.m. ET: Mr. Pokatilo responded to requests for comment after the publication of this story. Pokatilo said he has no relation to Synergy nor to Mr. Lobov, and that his work with Mr. Perkon ended with the dissolution of Awesome Technologies.

“I have had no involvement in any of his projects and business activities mentioned in the article and he has no involvement in Litero.ai,” Pokatilo said of Perkon.

Mr. Pokatilo said his new company Litero “does not provide contract cheating services and is built specifically to improve transparency and academic integrity in the age of universal use of AI by students.”

“I am Ukrainian,” he said in an email. “My close friends, colleagues, and some family members continue to live in Ukraine under the ongoing invasion. Any suggestion that I or my company may be connected in any way to Russia’s war efforts is deeply offensive on a personal level and harmful to the reputation of Litero.ai, a company where many team members are Ukrainian.”

Update, Dec. 11, 12:07 p.m. ET: Mr. Perkon responded to requests for comment after the publication of this story. Perkon said the photo of him in a Nerdify T-shirt (see screenshot above) was taken after a startup event in San Francisco, where he volunteered to act as a photo model to help friends with their project.

“I have no business or other relations to Nerdify or any other ventures in that space,” Mr. Perkon said in an email response. “As for Vadim Lobov, I worked for Venture Capital arm at Synergy until 2013 as well as his business school project in the UK, that didn’t get off the ground, so the company related to this was made dormant. Then Synergy kindly provided sponsorship for my Russian Film Week event that I created and ran until 2022 in the U.K., an event that became the biggest independent Russian film festival outside of Russia. Since the start of the Ukraine war in 2022 I closed the festival down.”

“I have had no business with Vadim Lobov since 2021 (the last film festival) and I don’t keep track of his endeavours,” Perkon continued. “As for Alexey Pokatilo, we are university friends. Our business relationship has ended after the concierge service Awesome Technologies didn’t work out, many years ago.”

❌
❌