 Entrar

The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More


A severe DreamHost security breach exposed customer FTP credentials and webmail accounts, prompting urgent password rotations and website file audits.
Related Posts:
The post DreamHost Security Breach Exposes FTP and Webmail Data appeared first on Daily CyberSecurity.
DigiCert confirmed unauthorized access to an internal business system containing archived customer information due to a security misconfiguration that exposed the application to the internet. This incident affected business contact details and, in some cases, identity documents. However, DigiCert said its certificate authority services, including CertCentral, DigiCert ONE, customer login credentials, and issued certificates, were […]
The post DigiCert Confirms Data Breach After Security Misconfiguration Exposes Customer Personal Information appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
An Amadeus airline data breach compromised passenger travel records across Malaysia Airlines, JAL, ANA, and Cathay Pacific via compromised credentials.
Related Posts:
The post Amadeus Airline Data Breach Hits Major Global Carriers appeared first on Daily CyberSecurity.
Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.
International Press – Newsletter
Binance Says User Funds Are ‘Completely Safe’ After $3.5 Billion Drains From Its Hot Wallets
Police arrest two suspects in AI-powered bank fraud that cost victims €380,000
M365 Token Spray and Replay Campaign Compromises Business Email Accounts
Ukrainian National Sentenced to 70 Months in Prison for Multi-Million Dollar Ransomware Conspiracies
deepveindrilling.com: Magento CMS block loader hits 953 stores
“Bulletproof” website domain seized in international law enforcement operation
Trezor warns of suspected crypto-theft implant in hardware wallet
Polymarket halts trading after crypto-draining script breach, $2.5M traced
Malware
CLAUDE CODE FOUND SPYWARE ON MY FAMILY’S PHONES AND A BACKDOOR ON MY MAC
Tricks from the Past deployed via signed ChatGPT and Claude binaries
Hacking
PHP2Shell exploitation observed: packet-to-process RCE evidence
Beyond the Inbox: How Threat Actors Abuse Microsoft Teams External Chat for Initial Access
Not Only ARTEX: The Different Levels AI is Used in Attacks Targeting Japan
Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability
Discovering and exploiting vulnerabilities in critical, real-world software with Claude
Putting Claude Code in a box: a sandboxed dev container for Zed
Hackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security Patch
The Last Proof of Human Craft: Forging a Microsoft Edge Full Chain with Logic Bugs Only!
Pentagon treating military base freezer malfunctions as suspected cyberattack, officials say
GitLab security incident: attempted exploitation of CVE-2026-97229
Intelligence and Information Warfare
Alibaba’s Qwen AI caught trying to contact server in China
Hackers can gain control of cameras and DVRs through cloud access
Disruptions ‘inevitable’ as AI-powered cyber threats grow, Australian Signals Directorate says
Operation FlashHole: Lazarus breaks security, defies control
Hackers Sympathetic to Russia Are Hitting Utilities and Factories
Alleged Israeli spy company heavily targeted Starlink users, sources say
North Korea Steals USD 6.36 Billion From Binance in the Largest Hack in History
Mapping the Political Influencer Industry and the Problems it Causes for Democracy
Cybersecurity
NIS 2 Italy: Key Deadlines, Board Duties and What ACN Expects From Companies
The Two Things CISOs Should Be Thinking About In The Wake Of The PHP Nightmare
Code-execution flaw in UEFI firmware affects most servers on planet Earth
2026 County Election Website Security Census: Key Findings
Cloud Exposure Index 2026: 484,142 open buckets mapped
ENGIE: Data leak via a tool belonging to its business partners
Beyond Framework Signatures: Understanding AI-Driven Intrusions
I Think The Military Commissary’s Freezers Were Hacked
Manifestos, Fear, and ‘Loser Thinking’: Inside Proton’s AI Reckoning
Passkeys Are Better Than Passwords. But They Are Not Enough
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, newsletter)
Northflank urged customers to rotate all platform secrets after reports of unauthorized AI API key use, warning that environment variables across workloads, secret groups, and global settings may have been exposed.
Northflank is investigating a security incident involving reported misuse of AI keys but has not confirmed the entry point, identified an attacker, or disclosed affected customers. Its credential rotation warning remains precautionary, not confirmation of widespread theft.
Northflank’s published timeline begins with a Wiz threat alert at 11:43 UTC on October 30, 2026. Engineers reviewed the alert one minute later and deployed an initial network policy patch at 12:02 UTC.
Further patches followed at 12:50 and 13:05 UTC, and the team requested support from the Wiz incident response team at 13:00 UTC.
The timeline does not explain what those patches fixed. A network policy change alone does not establish how attackers entered the platform or reached customer secrets.
Northflank subsequently instructed users to treat environment variables as compromised and restrict public access to add-ons where enabled. Environment variables can hold API keys, database passwords, and other application credentials.
Similar exposure concerns surfaced in the recent Railway security incident, where customers were also advised to replace stored secrets after possible unauthorized access.
Northflank said the reported activity may fit a wider pattern of attacks targeting AI credentials. It pointed to similar IP addresses in Wiz’s “Black October” report, which described incidents across nine AI developer platforms during October.
Wiz found a shared focus on stored environment variables but identified no single vulnerability connecting the attacks. The financial risk comes from LLMjacking, where attackers use stolen credentials to consume paid AI services at the victim’s expense.
Previous reporting on LLMjacking attacks shows how compromised cloud keys can support unauthorized model access and resale. However, Northflank has not published a confirmed loss total or linked its incident to a named resale operation.
Customers should revoke existing credentials through the issuing providers, generate replacements, and update affected Northflank secrets and workloads.
Northflank also asked users to review AI provider usage and billing records for unexpected activity, then report suspicious usage to its support team and the relevant provider.
Secret rotation is now available for PostgreSQL, MongoDB, MySQL, Redis, MinIO, and RabbitMQ add-ons. Northflank also enabled audit logs for all customers, including free users, giving more teams access to records that may help their investigation.
The immediate priority is replacing all potentially exposed credentials, not only AI keys already showing abuse. Northflank’s latest guidance still covers secrets across workloads, shared secret groups, and global settings while its investigation remains open.
Give your SOC the alert context to stops incidents quickly. Integrate Threat Intel from 16K SOCs.
The post Northflank Security Breach Leads to Unauthorized AI API Key Usage, Customers Urged to Rotate Secrets appeared first on Cyber Security News.


Personal details of thousands of U.S. Department of Homeland Security (DHS) employees are now online after a hacker stole reams of data in a data breach that occurred earlier this year and nobody had disclosed.
“The breach includes names, job titles, and work contact information, such as email addresses, cell phone numbers, and office locations, of more than 40,000 people who work for the federal department, including border and immigration agents, cybersecurity staffers, and senior department officials.” TechCrunch reports.
The incident impacted border and immigration agents, cybersecurity staff and senior department officials. DHS confirmed it is aware of a potential breach and is investigating, saying it takes threats to employees seriously and will provide updates when more information is available.
“DHS is aware of a potential breach and is actively working to address the situation swiftly and effectively. We take all security threats against our employees and officers seriously and will work to ensure all are properly protected. We will update the public when more information is available,” a DHS spokesperson told SecurityWeek.
The hacker, who uses the name Department of Peace, claims to have stolen the data from an Okta single sign-on system. DHS uses this service to give employees and contractors across its agencies access to the department’s central network. The system also stores IT and login records for each account, showing which systems and internal apps each person can access. The hacker left a note with the leaked data, seen by TechCrunch, saying that if others have their information, it is only fair to share theirs. The malicious actor did not reveal how the U.S. agency was breached.
More than half of the records, around 21,000, belong to U.S. Customs and Border Protection (CBP) employees working at airports and other ports of entry. Another 10,000 belong to Immigration and Customs Enforcement (ICE) and its Homeland Security Investigations unit, while just under 1,000 are linked to the cybersecurity agency CISA. Thousands of other records belong to DHS headquarters and agencies such as U.S. Citizenship and Immigration Services and the Federal Protective Service.
DDoSecrets says the leaked database identifies officials involved in undercover operations and key DHS personnel overseeing renditions and deportations. Department of Peace said the leak was a response to the government’s actions against ICE. Crimew described the database as an unprecedented view of DHS’s organizational structure, helping researchers identify employees, their roles and reporting lines. They said it could also support investigations and future Freedom of Information Act (FOIA) requests.
DDoSecrets co-founder Emma Best said the database, called Icepick, identifies officials involved in covert operations, internal investigations and deportation programs. Ryan Shapiro of Property of the People added that employee contact details could help researchers submit more targeted FOIA requests. Best said the data could also support journalism, congressional inquiries, legal challenges and community investigations.
“Rather than an indiscriminate directory of every DHS employee, Icepick identifies many of the architects and drivers of DHS policy and operations,” said journalist and DDoSecrets cofounder Emma Best. “The leak is extraordinary but deceptive in its simplicity as it identifies the officials responsible for overseeing covert and undercover operations, the government’s hunt for leakers and the failed BlueLeaks investigation — along with key personnel in DHS’s ever-escalating rendition and deportation programs.”
“By replacing the regime’s anonymity with accountability, Icepick and the tool developed by maia are catalyst for investigations, empowering journalists, Congressional inquiries, legal challenges, community action and Freedom of Information Act requests,” added Best.
DHS is investigating a potential breach. Okta says it has no evidence its systems or data were compromised.
The breach follows other attacks on U.S. government agencies that exposed FBI records and military personnel data. It is also the second DHS breach this year, after the same hacker claimed to have stolen thousands of government contracts.
Journalist maia arson crimew shared the data with DDoSecrets. TechCrunch verified some records, which suggest the database was copied around mid-August. The leak covers about one-fifth of DHS’s 220,000 employees.
The records reveal access to tools including Microsoft 365, ChatGPT, Penlink surveillance software and Mobile Fortify, a facial recognition app used by CBP and ICE. Around 4,500 accounts belong to a Headspace user group, while more than 2,000 Homeland Security Investigations employees appear in Penlink-related groups.
Researchers say the contact details could help journalists file targeted Freedom of Information Act requests. However, exposing employees’ phone numbers and office locations also creates security and privacy risks.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, DHS)
Hackers reduced the GMO Internet ransom demand from $50M to $1M and leaked victim files after the Japanese conglomerate ignored multiple bug warnings.
Related Posts:
The post GMO Internet Ransom Demand Slashed After Cloud Breach appeared first on Daily CyberSecurity.
French multinational energy company ENGIE warned customers in France that attackers accessed personal information through a sales tool used by some business partners. The exposed data includes contact details and energy contract information that could help fraudsters impersonate the supplier.
The company says its internal IT systems weren’t compromised and banking information wasn’t affected. It has blocked the attackers’ access, notified the relevant authorities and contacted affected customers, according to a spokesperson who spoke to BleepingComputer.
According to notification emails sent to affected customers, the incident involved a tool used by partners to sell the company’s electricity and natural gas offers.
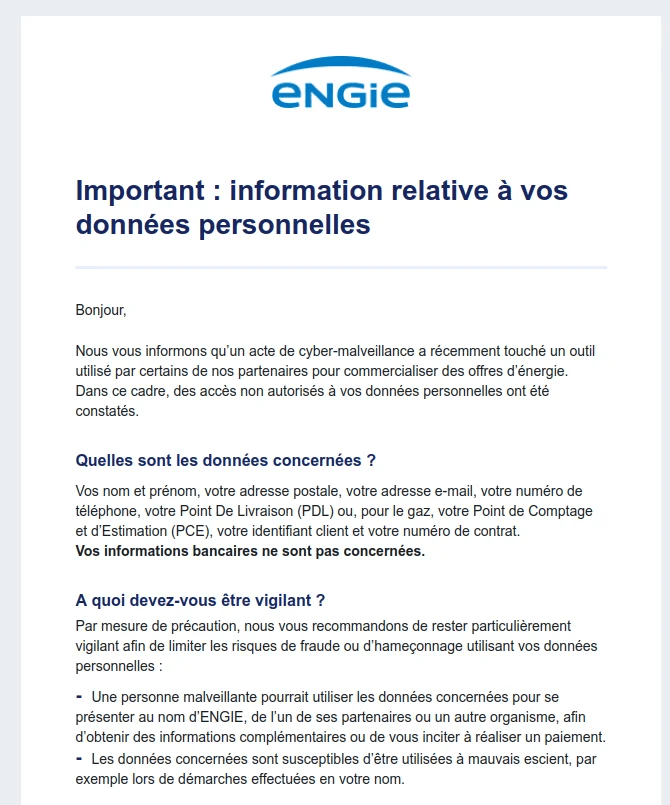
The notification confirms that attackers gained unauthorized access to personal information stored in the sales tool.
“We are informing you that an act of cyber-malice recently affected a tool used by some of our partners to market energy offers. As part of this incident, unauthorized access to your personal data was identified.” reads the notification.
The compromised information includes customers’ names, postal addresses, email addresses, telephone numbers, customer IDs, contract numbers and energy supply identifiers.
The company hasn’t disclosed the partner or platform involved. It also hasn’t revealed how many customers were affected, when the intrusion began, or when it was discovered.
For electricity customers, these include the delivery point identifier (PDL). For gas customers, they include the metering and estimation point (PCE).
ENGIE says financial information wasn’t affected and that its investigation indicates the exposure was limited to contact details and certain contract information.
That reduces one category of risk but doesn’t eliminate financial fraud. Attackers can use accurate customer information to persuade victims to disclose additional data or make payments.
Anyway, the exposed data could support impersonation scams. The company warned customers to watch for attempts to obtain further information or induce payments. A contract number, however, doesn’t prove that a caller is legitimate. It may simply show that the person has access to an exposed record.
Customers should verify unexpected requests through trusted channels, even when the sender knows their personal details.
ENGIE hasn’t attributed the attack to a specific group, and at this time no ransomware group has claimed responsibility for the attack.
Experts recommend visiting ENGIE’s official website or app directly instead of signing in through links received by email.
Customers should also be cautious with unexpected calls and messages. If someone requests a payment, password or additional personal information, they should end the exchange and verify the request using independently obtained official contact details.
Customers should never share SMS verification codes, passwords or banking details with someone who contacts them unexpectedly.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, data breach)
Coinbase has disclosed that a security incident at analytics provider Amplitude exposed contact information belonging to a small subset of its customers. The cryptocurrency exchange said it found no evidence of unauthorized access to Coinbase systems and confirmed that customer funds were not impacted.
In its official statement, Coinbase Support said the incident also affected other Amplitude customers. The company is notifying impacted users and regulatory agencies under its legal obligations. However, its public update did not identify the other businesses involved or explain how the exposure happened.
“Coinbase has not had a data breach,” the company said, drawing a distinction between its own systems and information held by an outside provider. That distinction matters because customer data can be exposed through a vendor without attackers gaining access to the exchange itself.
Coinbase has not confirmed the number of affected customers or provided a complete list of exposed data fields. Reports have mentioned email addresses and phone numbers, but the official statement refers only to customer contact data. Readers should not treat those reported fields as a confirmed inventory.
Coinbase has not had a data breach.
— Coinbase Support (@CoinbaseSupport) October 28, 2026
Amplitude, an analytics vendor, experienced a security incident which impacted a small subset of Coinbase customer contact data, among other Amplitude customers.
We’ve found no evidence of unauthorized access to Coinbase systems, and…
Reporting by Cryptopolitan cited a claim from SlowMist security researcher 23pds that more than 70,000 users were affected. Coinbase has not verified that figure. Its statement also did not name an attacker, disclose an entry method, or establish when the Amplitude incident began.
Coinbase’s statement does not say that passwords, private keys, or transaction records were exposed. It also does not provide a detailed technical account of the incident. Those gaps make it important to separate confirmed company statements from broader claims circulating online about the event.
The Coinbase Amplitude security incident highlights third-party risk. Analytics services help businesses understand how people use their products. When customer information reaches an outside provider, the security of that provider becomes part of the wider data protection picture, even when the main platform remains secure.
This event should not be confused with the separate Coinbase data theft disclosed in May 2025. Cyber Security News reported that attackers paid overseas support personnel to obtain customer information in that earlier case. There is no established connection between that incident and the current Amplitude exposure.
Contact data alone does not provide direct access to cryptocurrency wallets. However, it can help scammers reach customers with convincing messages about account restrictions, suspicious transactions, or urgent security checks. Knowing that someone uses Coinbase can make a fake support message seem more believable and harder to dismiss.
Cyber Security News previously covered another Coinbase cyberattack involving employees targeted with fake messages. That earlier case provides context for the risks of impersonation, but it does not establish how the Amplitude incident occurred. No public evidence reviewed for this report confirms phishing caused this vendor incident.
Customers should check security notices through the Coinbase app or by visiting its website directly rather than following unexpected links. Coinbase’s support scam guidance says staff will never ask for passwords or verification codes, request remote access, or tell customers to send cryptocurrency to an external address.
The immediate concern is therefore possible follow-up fraud, not a confirmed compromise of Coinbase wallets. Affected users should review their notification for specific details and remain cautious about unsolicited contact. Further disclosures are needed to establish the full scope of the exposure, the information involved, and the cause of the incident.
The post Coinbase Customer Data Exposed Via Analytics Vendor Amplitude Security Incident appeared first on Cyber Security News.

Sony Network Communications disclosed a data breach that exposed 2,585,481 customer records linked to its So-net and Plala (S Course) internet services. The breach, announced on October 27, 2026, compromised passwords for 54,401 email addresses. However, it did not affect primary membership passwords or credit card information. The compromised database contained 2,141,986 records from So-net […]
The post Sony Data Breach Exposes 2.58 Million Customer Records and 54,401 Email Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
South Korean police have arrested a 32-year-old man accused of leading an AI-assisted hacking operation that stole personal records and internal files from about 90 organizations, totaling 8.2 million records.
Targets included hospitals, private academies, golf courses, universities, and large companies’ affiliates. Investigators said the group used stolen data to pressure victims into paying money.
The Seoul Metropolitan Police Agency announced the case on October 26. The alleged ringleader, identified as “A,” was arrested on October 15 and referred to prosecutors on October 23 while in custody.
Six other suspects remain under investigation and are not in custody, according to reporting on the police findings. Police said the attacks began in September 2025 and continued into October 2026. Although the suspect did not study information technology, he taught himself hacking through online material.
He worked in penetration testing at a security company between 2019 and 2022. That background gave him practical experience before the alleged criminal campaign.
The suspect initially used conventional hacking tools to identify website weaknesses. Investigators said he began using generative AI more widely in late August 2026, expanding the operation.
Around 60 of the targeted organizations were reportedly breached with help from AI tools, rather than every intrusion involving AI from the outset.
Reporting identified the software as ARTEX, an AI penetration testing framework also linked to separate attacks against South Korean financial institutions.

Cybersecurity News previously covered how hackers targeting South Korean banks exposed their attack tools, providing context about the framework and its use.
However, the shared tool does not establish that the same people carried out both campaigns. Public reporting also does not provide a complete attack chain for these 90 breaches.
The reports reviewed disclose no confirmed vulnerability list, malware details, or evidence that AI independently completed every intrusion.
After stealing information, the group allegedly sent threatening messages to affected organizations. The suspects warned that public disclosure could damage company reputations and lead to government fines.
Police identified 38 organizations connected to the extortion attempts, with combined demands reaching 360 million won, according to Yonhap News Agency.
That figure represents money demanded, not a confirmed total paid. The reported scheme focused on threatening to release stolen information. Available accounts do not describe a ransomware deployment or establish that the attackers encrypted victims’ systems.
The investigation followed a victim complaint in June. Police traced activity through affected organizations’ server logs and used an internal AI analysis system to examine evidence. Investigators recovered stolen information and continued checking whether copies had reached the dark web or supported further crimes.
Authorities described the arrests as South Korea’s first large-scale generative AI hacking case of this kind. The suspect’s prior testing experience remains important when assessing that claim. The case shows an experienced operator adopting AI, not proof that an untrained user could reproduce the same results.
The arrests follow wider concern about breaches in South Korea’s financial sector and security checks. Across both stories, investigators are examining AI’s role while key technical details remain undisclosed. For readers, separating confirmed breaches from claims of fully autonomous hacking remains essential to understanding the threat accurately.
Give your SOC the alert context to stops incidents quickly. Integrate Threat Intel from 16K SOCs.
The post Hacker Uses AI to Breach 90 South Korean Organizations and Steal 8.2 Million Records appeared first on Cyber Security News.

The University of Copenhagen has confirmed a data breach that exposed personal information belonging to about 525,000 people after hackers accessed a university test environment.
The affected database contained full names, Danish national identity numbers, work and private telephone numbers, and personal email addresses. The university is still examining the full extent of the exposure.
The attack was detected on October 20, 2026, and publicly disclosed on October 23. According to the university’s official security notice, the university has brought the incident under control and blocked the attackers’ access.
According to reports, the October 25 update confirmed the exposure of ID card PINs belonging to around 20,000 staff and students, with no evidence of disrupted university operations.
The university issued replacement codes and confirmed that this finding was part of the original incident, not a separate attack. It delayed announcing the compromised codes until it changed them.
The university restricted access to selected critical campus locations on October 23, reopening them after replacing affected PIN codes, as the investigation expanded to physical access control data.
The university should not add the 20,000 affected cardholders to the reported 525,000 people as a separate group. The university described them as affected staff and students within the same incident, rather than announcing a new total.
The confirmed entry point was a test environment. However, the university has not disclosed how the hackers gained access, which software was involved, or whether stolen login details or a software flaw enabled the intrusion. Its statement also does not establish that the hackers downloaded or published every exposed record.
The incident highlights the risks of keeping real personal information in testing systems. A related University of Sydney data breach involved historical personal records stored in an online code library intended for software development. That case similarly placed sensitive information inside a development resource.
A separate Dell test platform breach offers a useful contrast. Dell said its affected demonstration environment mainly contained synthetic data and was separated from customer systems. These cases illustrate why the contents and boundaries of test systems matter when assessing a breach’s impact.
The exposed identity and contact details could support targeted phishing and social engineering. Messages that include a person’s real name or other private details may appear credible, so affected people should independently verify unexpected requests rather than trust the information included in them.
The university has reported the incident to the Danish Data Protection Agency and is keeping other relevant authorities informed. It says the breach falls within the scope of GDPR and continues to investigate its extent. Further updates are expected once investigators establish a clearer picture of what happened and which information was affected.
Give your SOC the alert context to stops incidents quickly. Integrate Threat Intel from 16K SOCs.
The post University of Copenhagen Data Breach Exposes 525,000 People’s Personal Data, Including Phone Numbers appeared first on Cyber Security News.

