Separate actions also take place outside fence and across Europe in backlash against impact of AI boom
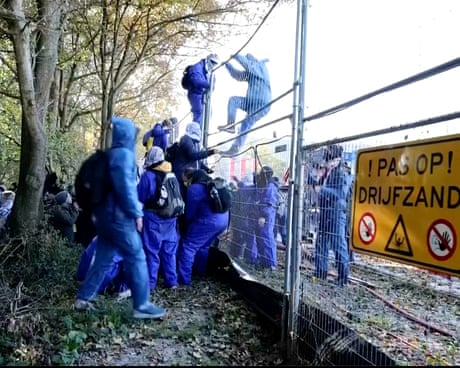
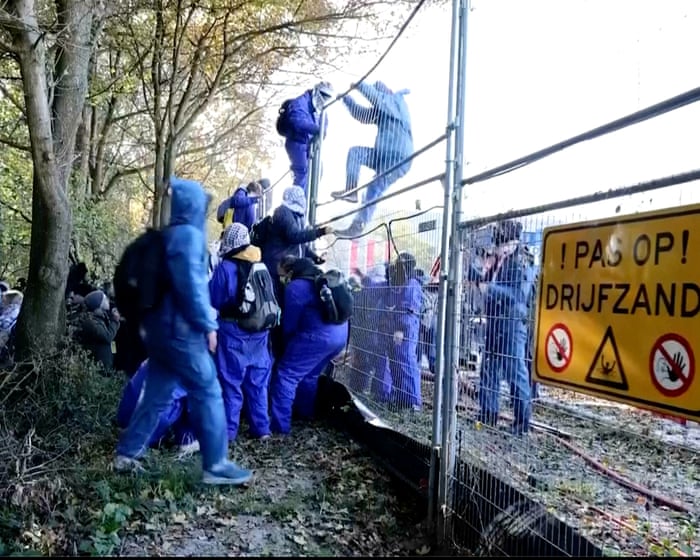
Activists have stormed the site of a Microsoft datacentre being built in Amsterdam, as the backlash to the social and environmental harms of the AI boom spreads across Europe.
Protesters from Geef Tegengas, a Dutch direct action group, clashed with police while breaking into a construction site at Westpoort, Amsterdam, where some members climbed a crane, lit flares and tied helium balloons to equipment.
Microsoft is developing the Windows 11 27H2 update, focusing on core system stability, new wallpapers, and 64-bit speed via Intel APX register expansion.
Microsoft launches Windows 11 Cloud Rebuild, a native recovery tool that downloads fresh system images and drivers directly from the cloud without USB media.
Hackers are exploiting stolen Microsoft Entra ID application credentials to infiltrate Microsoft 365 and Azure environments, impacting 27 organizations via managed service providers (MSPs) and their downstream clients. Todyl’s MXDR team is monitoring this ongoing campaign, referred to as Key Eater. Since November 1, 2026, the attackers have targeted approximately 45 app registrations across about […]
An organized fraud operation using paid advertisements, Microsoft Azure hosting, and centrally managed telephone numbers to distribute counterfeit Microsoft support pages. The investigation links one backend serving the kit to Mandarin-speaking developers and registration details referencing Hubei, China. Those findings suggest operational connections, not definitive attribution. Crucially, the identified backend appeared in detections at 11 […]
Microsoft’s analysis of approximately 383,000 disclosed vulnerabilities shows that attackers overwhelmingly favor weaknesses enabling system takeover rather than exploiting vulnerabilities indiscriminately. The research identifies 2,056 CVEs linked to real-world exploitation, roughly 0.5% of the population, highlighting why vulnerability management must prioritize demonstrated attacker utility over disclosure volume or severity scores alone. Covering vulnerabilities published from […]
Microsoft has resolved a known issue that prevented some users from activating the Smart App Control security feature after installing the October 2026 KB5127648 Windows 11 security update. [...]
Microsoft resolved a Windows 11 issue that blocked non-admin users from connecting via Remote Desktop when Administrator protection was enabled, releasing fixes on October 28, 2026, for connection failures with error 0xC000000D.
The bug appeared after the September 22 non-security preview update, KB5124010, or later updates. Affected users could see the message, “The token that was passed to the function is invalid.”
Microsoft’s release health notice identifies enterprise-managed computers acting as Remote Desktop hosts as the main systems affected.
Microsoft opened its investigation on October 13. As detailed in Cyber Security News’ earlier coverage of the Remote Desktop connection failures, the problem prevented standard users from reaching remote systems where Administrator protection was active. The failure could occur regardless of how administrators enabled that feature.
Microsoft lists Windows 11 versions 24H2, 25H2, 26H1, and 26H2 as affected platforms. Its notice does not list Windows Server as affected by this particular issue. That scope matters because other recent Remote Desktop problems have involved different Windows releases and separate update failures.
Administrator protection limits how applications gain administrator rights. Instead of leaving those rights available throughout a session, it grants temporary access for approved tasks.
Microsoft Fixes Windows 11 Remote Desktop Failures
Cyber Security News’ explanation of Windows 11 Administrator protection describes how this approach helps reduce the risk of malware making unwanted system changes.
The setting may already be active in managed environments. Microsoft says its Windows 11 24H2, 25H2, and 26H2 security baselines enable Administrator protection by default unless an organization changes the policy. Businesses using those baselines should therefore check affected hosts rather than assume the feature was never enabled.
According to Microsoft’s release health advisory, updates released on or after October 28 resolve the issue. Systems running an applicable fixed update no longer need the temporary workaround. Microsoft recommends installing the latest security update available for the device to receive relevant fixes and improvements.
The KB5127936 release notes explicitly confirm the Remote Desktop repair. This non-security preview update applies to Windows 11 25H2 and 26H2, raising their builds to 26200.9818 and 26300.9818, respectively.
Administrators managing other affected versions should check the package offered for their specific Windows release instead of treating KB5127936 as a universal installer.
For affected computers still running older updates, Microsoft allows administrators to temporarily turn off Administrator protection through their existing management tools. The documented workaround involves resetting the “User Account Control Type Of Admin Approval Mode” policy through Microsoft Intune or Group Policy.
Because this workaround turns off a security feature, it should remain temporary. After deploying the appropriate fixed update, IT teams should verify Remote Desktop access using a non-admin account and review any policy changes made during troubleshooting. This confirms remote access works without leaving the earlier workaround in place unnecessarily.
Microsoft has resolved an issue in Windows 11 that prevented non-administrator users from connecting to devices with Administrator protection enabled. This fix was included in KB5127936, released on October 28, 2026, and is part of subsequent updates. While this issue is urgent for affected organizations, Microsoft has categorized the release as a preview update rather […]
Microsoft has resolved a known issue that prevents non-admin users from connecting to devices via Remote Desktop when the "Administrator protection" security feature is enabled. [...]
Microsoft urged Entra ID administrators to migrate from SMS and voice authentication in Entra ID to passkeys before retirement begins on February 1, 2027, to reduce phishing risks and prevent sign-in disruptions.
The reminder, published on October 27 under Message Center notice MC1528000, follows July announcements. Retirement covers Worldwide and Government Community Cloud environments and should finish in early February 2027. Administrators should not wait until the change reaches their tenant before preparing affected users.
According to the Microsoft retirement notice, users with another registered sign-in method will use that method. They will not need to register a passkey to continue accessing their accounts. This makes checking existing authentication methods an important first step for administrators.
Users whose only registered method is SMS or voice face a different process. Microsoft says they can use their existing method one final time to verify their identity. They must then register a passkey to keep signing in, making preparation important for organizations with many phone-dependent accounts.
The announcement continues the shift covered in Cybersecuritynews.com’s report on Microsoft making passkeys the default in Entra ID. However, this retirement applies specifically to Microsoft-provided phone authentication, not a complete ban on SMS and voice across Entra ID.
Microsoft Urges Passkey Migration
SMS and voice authentication remain exposed to phishing and SIM-swap attacks. Criminals can trick users into sharing verification codes or take control of an authentication phone number. Moving away from these methods reduces reliance on phone networks and codes that attackers can capture.
As Microsoft’s passkey documentation explains, passkeys use public-key cryptography under FIDO standards. The user’s authenticator keeps the private key, while the service stores the public key. During sign-in, the authenticator signs a challenge after the user unlocks it with a PIN or biometric check.
The credential works only with the website or application it was created for, helping prevent fake login pages from stealing reusable sign-in secrets. Cybersecuritynews.com’s coverage of UNC3944’s SIM-swap attacks shows why reducing dependence on phone-based verification matters.
Administrators should identify users relying on SMS or voice, prioritize accounts without another registered method, and help users adopt passkeys or another supported option. Microsoft also asks organizations to notify employees and helpdesk teams about the deadline and the registration process.
Organizations that need to retain phone authentication can configure a customer-managed telecom provider through the Microsoft Security Store.
Microsoft’s provider guidance says configuration will be available starting October 30, 2026. Customers must review coverage, pricing, support, and contractual terms before deployment.
Existing customer-managed providers are unaffected. Organizations that do not use Microsoft-provided SMS or voice need no action for this retirement. At the same time, affected customers must migrate or configure their provider before February 1.

 Entrar