Statistics on Malware Distributed to the Financial Sector In Attack Stage 1, phishing (attacks that trick users into revealing information) had the highest rate at 2.1, Up from 1.8 The previous month. In Attack Stage 2, “Dropper/Downloader” (a type that downloads additional malware) was the most common at 1.1, Though this was a decrease from […]
Purpose and Scope This report summarizes the quantity of new ransomware samples collected, the number of compromised systems, and statistics on targeted businesses during the month of September 2026, as well as major Korean & global ransomware issues. The analysis is based on data collected through ATIP (AhnLab Threat Intelligence Platform) and AhnLab Smart Defense, […]
Note The September 2026 Dark Web Breach Incident Trend Report focuses on data breach cases and the sale of initial access credentials posted on the deep web and dark web forums. The report explicitly states that the accuracy of some of its content cannot be fully verified due to the nature of the sources. Major […]
Note The September 2026 Dark Web Threat Actor Trend Report focuses on threat actors active on the deep web and dark web, as well as publicly reported cyberattack incidents. It is noted that the factual accuracy of some content cannot be independently verified. Major Issues Some hacktivist groups claimed responsibility for DDoS attacks targeting the […]
The net is tightening around the Shiny Hunters cybercrime group following the reported arrest of a second member.
On Saturday, Reuters said that 16 year-old Saif al-Din Khader had been arrested in Jordan and was in FBI custody. This follows the arrest earlier in September of another member in the Netherlands. Third party reports named him as 24 year-old Pepijn van der Stap, an offensive security lead at Dutch company Neo Security.
The FBI posted a message following the Dutch arrest warning other ShinyHunter members that it was coming for them next. Cyber Division Assistant Director Brett Leatherman hinted that people already taken into custody had been talking. Then he said:
“You know how to find us, and we know how to find you. I suggest you reach out first while the choice is still yours.”
According to security blogger Brian Krebs, Khader (who goes by the nickname ‘Rey’), was the technical operator and public face of Scattered LAPSUS$ Hunters, which he said was an amalgamation of three groups: Scattered Spider, LAPSUS$ and ShinyHunters.
Active since at least 2019, ShinyHunters focused on data theft and extortion. The group commonly uses social engineering to gain access to victims’ accounts on third-party services, but also exploits flaws in software.
Victims of the ShinyHunters group include Kodak, along with American healthcare and pharmaceuticals distributor McKesson. The gang also recently compromised rival cybercrime group Clop and defaced its leak site.
Shortly after the Clop attack, ShinyHunters hacked the FBI. The group said that this wasn’t financially motivated, but instead was a response to a May FBI advisory about its activities. That announcement followed ShinyHunters’ own cyberattack on Instructure, which runs the Canvas online educational system.
The FBI attack targeted the agency’s jobs site, and is said to have exploited a vulnerability in PeopleSoft, HR software owned by Oracle. The data breach, which ShinyHunters claimed amounted to Terabytes, is said to have included a wide array of information on employees, ranging from names, addresses, and phone numbers through to badge numbers, job titles, and information on spouses. Other information included fitness-for-work medical records along with blood and urine test results, and doctors’ notes.
This data is said to include sensitive information on agents investigating targets including Russia, China, and the drug cartels. It would be catastrophic for law enforcement efforts, national intelligence, and individuals if this information fell into the wrong hands.
ShinyHunters has said that it won’t release the data, arguing that the intrusion wasn’t financially motivated. It criticized the FBI for what it said was disinformation in the May advisory. The FBI had said that the group had harassed victims’ family members and threatened to release embarrassing pictures.
The FBI also removed an Accenture contractor this week after they failed to apply a security patch to third-party software that it had been using. Insiders identified this software as PeopleSoft.
BBC News reports it has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.
As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
The BBC’s findings raise the stakes: The alleged theft includes highly sensitive medical records, not just staff identity and contact data. ShinyHunters shared samples with journalists as proof of its claims.
The BBC states:
“The samples shared with journalists appear genuine and include names, addresses, phone numbers, badge numbers, job titles and information about spouses.”
ShinyHunters claims it accessed several systems, including FBI MedLink, which stores medical records, and FBI BEAST, which handles background checks on employees and applicants, but the FBI has not confirmed these claims. The FBI has acknowledged an incident affecting FBIJobs-related systems and says it is investigating whether its own environment or a third-party provider was compromised.
The group’s stated demand remains non-financial: It wants the FBI to retract or remove a May advisory that ShinyHunters calls false and defamatory. It says it will release the data within five days if its demands are not met.
The cybercriminals also raised the number of affected people. ShinyHunters nows claims to hold sensitive information on around 60,000 current and former FBI staff. Medical histories could make affected people vulnerable long after the immediate incident: Unlike a stolen password, a medical record cannot be changed.
What to do if you’re affected
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
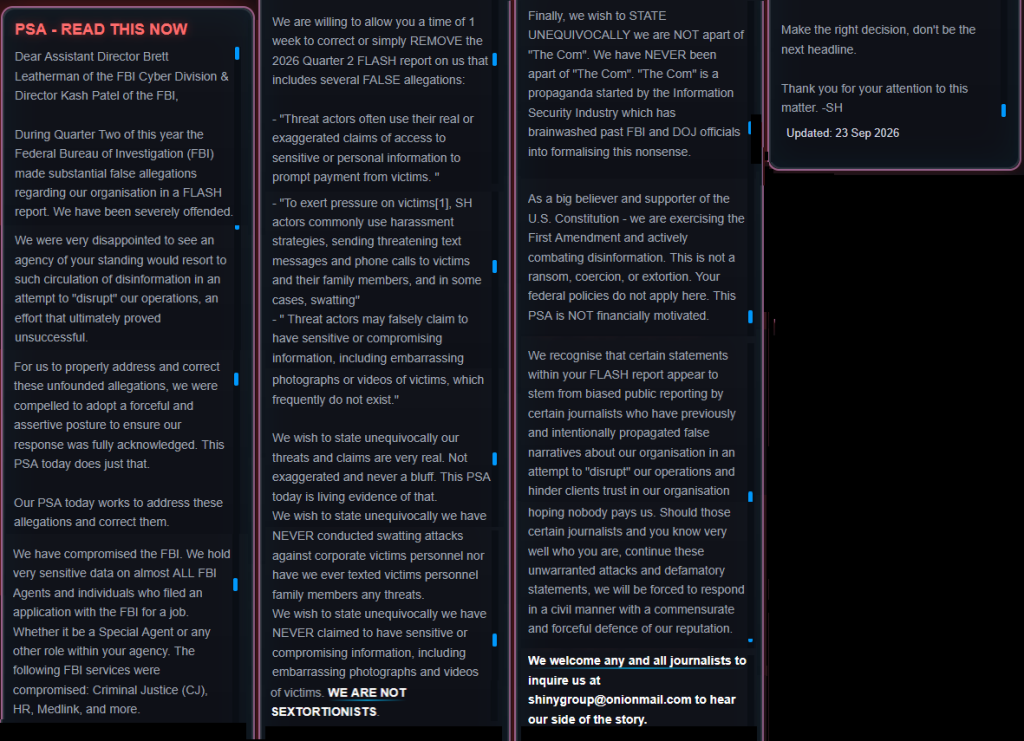
In a very long post on its leak site, the group outlines its grievances:
“PSA – READ THIS NOW
Dear Assistant Director Brett Leatherman of the FBI Cyber Division & Director Kash Patel of the FBI,
During Quarter Two of this year the Federal Bureau of Investigation (FBI) made substantial false allegations regarding our organisation in a FLASH report. We have been severely offended.
We were very disappointed to see an agency of your standing would resort to such circulation of disinformation in an attempt to “disrupt” our operations, an effort that ultimately proved unsuccessful.
For us to properly address and correct these unfounded allegations, we were compelled to adopt a forceful and assertive posture to ensure our response was fully acknowledged. This PSA today does just that.
Our PSA today works to address these allegations and correct them.
We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job. Whether it be a Special Agent or any other role within your agency. The following FBI services were compromised: Criminal Justice (CJ), HR, Medlink, and more.
We are willing to allow you a time of 1 week to correct or simply REMOVE the 2026 Quarter 2 FLASH report on us that includes several FALSE allegations:
“Threat actors often use their real or exaggerated claims of access to sensitive or personal information to prompt payment from victims.”
“To exert pressure on victims[1], SH actors commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases, swatting”
“Threat actors may falsely claim to have sensitive or compromising information, including embarrassing photographs or videos of victims, which frequently do not exist.”
We wish to state unequivocally our threats and claims are very real. Not exaggerated and never a bluff. This PSA today is living evidence of that.
We wish to state unequivocally we have NEVER conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats.
We wish to state unequivocally we have NEVER claimed to have sensitive or compromising information, including embarrassing photographs and videos of victims. WE ARE NOT SEXTORTIONISTS.
Finally, we wish to STATE UNEQUIVOCALLY we are NOT apart of “The Com”. We have NEVER been apart of “The Com”. “The Com” is a propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalising this nonsense.
As a big believer and supporter of the U.S. Constitution – we are exercising the First Amendment and actively combating disinformation. This is not a ransom, coercion, or extortion. Your federal policies do not apply here. This PSA is NOT financially motivated.
We recognise that certain statements within your FLASH report appear to stem from biased public reporting by certain journalists who have previously and intentionally propagated false narratives about our organisation in an attempt to “disrupt” our operations and hinder clients trust in our organisation hoping nobody pays us. Should those certain journalists and you know very well who you are, continue these unwarranted attacks and defamatory statements, we will be forced to respond in a civil manner with a commensurate and forceful defence of our reputation.
We welcome any and all journalists to inquire us at shinygroup@onionmail[.]com to hear our side of the story.
Make the right decision, don’t be the next headline.
Thank you for your attention to this matter. -SH
Updated: 23 Sep 2026“
The post is essentially a hostile “correction notice” directed at FBI leaders Brett Leatherman and Kash Patel. Its central grievance is an FBI advisory that says ShinyHunters commonly harasses victims and their families, including through threatening messages, phone calls, and, in some cases, swatting.
It also warns that threat actors may exaggerate their access to personal information or falsely claim to possess compromising photos or videos. The advisory does not use the word “sextortion,” but ShinyHunters appears to have interpreted the reference to compromising material that way. The group denies much of the FBI’s account while simultaneously using coercive language of its own.
The document it appears to mean is the FBI/IC3 public advisory “ShinyHunters: Cyber Criminal Group Attacks Learning Management System,” issued on May 15, 2026. Despite ShinyHunters calling it a “2026 Quarter 2 FLASH report,” the publicly accessible document is labeled a Public Service Announcement (PSA), not a FLASH.
It also denies carrying out swatting attacks or sending threatening messages to the family members of people working for its corporate victims.
The group also denies being part of The Com, a decentralized network linked to cybercrime and violence. It calls that connection:
“propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalizing this nonsense.”
The group then threatens journalists it accuses of spreading these “false narratives.”
The most worrying part of the message is the group’s claim that it stole sensitive data on:
“almost ALL FBI Agents, and individuals who filed an application with the FBI for a job.”
According to 404 Media, ShinyHunters provided a sample containing information on roughly 5,000 FBI agents, including names, home addresses, phone numbers, and details about their spouses. The publication reportedly verified portions of the sample, but the full dataset and the wider claims about the breach have not been independently confirmed.
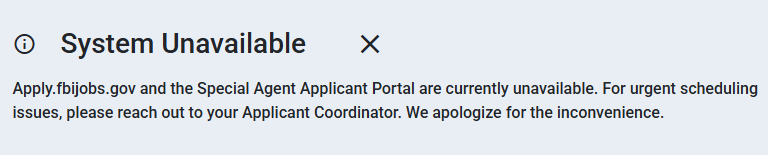
The group also reportedly defaced the FBI’s jobs website. The FBI says it is aware of claims involving unauthorized activity affecting FBIjobs.gov and is investigating, although “broken” does not necessarily mean “breached.”
What to do if you’re affected
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
ASEC Blog publishes Ransom & Dark Web Issues Week 4, September 2026 Metaencryptor Ransomware Attack on a South Korean Camera Module and Equipment Manufacturer Metaencryptor Ransomware Attack on a Japanese Automotive Parts Manufacturer ShinyHunters Claims Breach of a U.S. Federal Law Enforcement Agency and Theft of Sensitive Data
Reportedly, the ShinyHunters extortion group breached the leak site of one of its competitors, the Clop ransomware gang.
ShinyHunters is a financially motivated cybercrime and extortion group active since 2019. It is known for stealing large volumes of data and pressuring victims to pay, rather than necessarily deploying ransomware. One recent high-profile organization targeted by the group was Instructure, the maker of Canvas LMS. ShinyHunters claimed it stole 3.65 TB of data belonging to about 9,000 academic institutions.
Clop, also written Cl0p, is a ransomware and data-extortion operation associated with large-scale exploitation of vulnerabilities in enterprise software and file-transfer platforms. In its recent campaign targeting PTC Windchill systems, it named more than 40 alleged victims, including Shell, Philips, Fiserv, Zebra Technologies, Ingersoll Rand, and Toast.
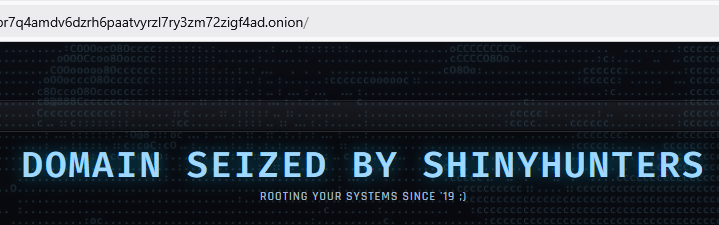
At the time of writing, the Clop dark web leak site looks like this:
Domain seized by ShinyHunters
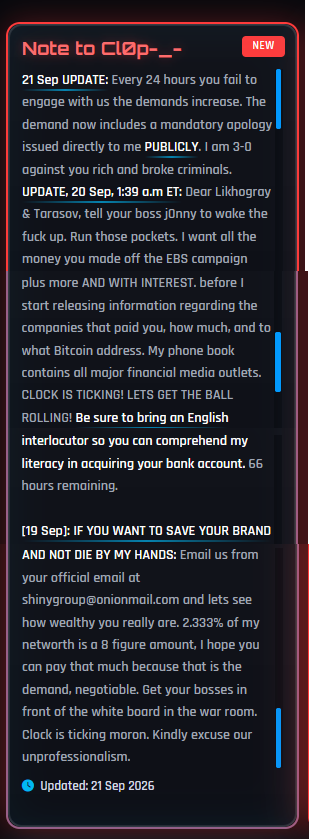
The rest of that page looks much the same as the ShinyHunters leak site, which includes this “Note to Cl0p”:
“Note to Cl0p_-
21 Sep UPDATE: Every 24 hours you fail to engage with us the demands increase. The demand now includes a mandatory apology issued directly to me PUBLICLY. I am 3-0 against you rich and broke criminals. UPDATE, 20 Sep, 1:39 a.m ET: Dear Likhogray & Tarasov, tell your boss j0nny to wake the fuck up. Run those pockets. I want all the money you made off the EBS campaign plus more AND WITH INTEREST, before I start releasing information regarding the companies that paid you, how much, and to what Bitcoin address. My phone book contains all major financial media outlets. CLOCK IS TICKING! LETS GET THE BALL ROLLING! Be sure to bring an English interlocutor so you can comprehend my literacy in acquiring your bank account. 66 hours remaining.
[19 Sep]: IF YOU WANT TO SAVE YOUR BRAND AND NOT DIE BY MY HANDS: Email us from your official email at shinygroup@onionmail.com and lets see how wealthy you really are. 2.333% of my networth is a 8 figure amount, I hope you can pay that much because that is the demand, negotiable. Get your bosses in front of the white board in the war room. Clock is ticking moron. Kindly excuse our unprofessionalism.
Updated: 21 Sep 2026”
BleepingComputer reports that the attack began Friday night when ShinyHunters exploited what it claims is an unauthenticated file-upload vulnerability in Grav CMS to upload a small text file to Clop’s site. Several hours later, ShinyHunters told BleepingComputer that it had “completely defaced” the site.
The group claimed it could continue controlling the address:
“We have their onion keys. So, if they kick us out it wouldn’t matter at all because we control the private keys to host the same exact onion URL.”
You might expect groups that make their money by exploiting unpatched vulnerabilities to be more vigilant about their own systems, but it looks as though they sometimes let their guard down.
According to ShinyHunters, this gang war began after ShinyHunters disrupted a Clop data-theft campaign. A Clop representative then allegedly threatened to identify ShinyHunters members and made violent threats against them.
ShinyHunters explained:
“During the Oracle EBS campaign they ran and stole from me last year, someone from cl0p personally messaged me and said, and I quote (translated from Russian): I have more money than you and all of your people combined, I’ll kill you soon.”
The good news is that while they are after each other, they probably have less time to attack legitimate businesses. I’m grabbing a bag of popcorn and watching this one unfold. We’ll keep you posted.
From reporting threats to removing them.
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
Note In August 2026, widespread instances of database leaks, the sale of internal data, and the trading of initial access privileges were observed on dark web and deep web forums. Due to the nature of the sources, it was difficult to fully verify the accuracy of some posts. Major Issues ShinyHunters continued to make claims […]
Healthcare and pharmaceutical-distribution giant McKesson has disclosed a cybersecurity incident involving unauthorized access to third-party applications and the theft of data.
McKesson Corporation is an American healthcare company that distributes pharmaceuticals and provides medical supplies, health information technology, and care management tools.
McKesson says it discovered the cybersecurity incident on August 25, 2026, and that its investigation is still in early stages.
“Based on our investigation thus far, including assessments by leading cybersecurity industry experts supporting our response, we’ve confirmed that the unauthorized access to certain third-party applications and the exfiltration of certain data was associated with a subset of customers within our Oncology & Multispecialty and Medical-Surgical business units.”
For now, McKesson provides no information about the amount or nature of the stolen data.
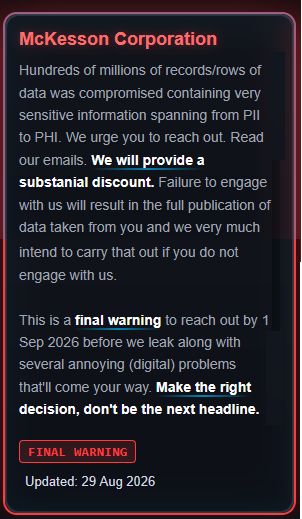
The attack has been claimed by ransomware/extortion group Shiny Hunters. On their leak site the group claims to have stolen hundreds of millions of records containing very sensitive information spanning from Personally Identifiable Information (PII) to Protected Health Information (PHI).
ShinyHunters listing for McKesson Corporation
The ShinyHunters extortion group told BleepingComputer that it was behind the attack, claiming it gained access after conducting voice phishing (or vishing) attacks—a form of social engineering—against multiple McKesson employees. Subsequently, the group said it used compromised Okta single-sign-on accounts to access Salesforce and Snowflake environments. It further claimed to have removed approximately 1 TB of data between August 21 and 25.
The group also said the data includes roughly 284 million records, which does not necessarily mean they belong to 284 million unique patients.
A combination of identity information and healthcare-related details could make affected people targets for convincing scams. Criminals could impersonate a pharmacy, insurer, medical provider, debt collector, or patient-support service and use personal details to make the approach appear legitimate.
Healthcare data is especially useful in social-engineering attacks because it can be used to create a sense of urgency: Criminals could scare a target by sending a supposed prescription problem, unpaid claim, delivery issue, appointment change, or request to “verify” insurance details. At this stage, however, McKesson has not confirmed that any particular category of patient data was accessed.
What to do if you’re affected
While waiting for more information about the nature of the breach and how you might be affected, there are a few things you can do:
Check the company’s advice. Every breach is different, so check with the company to find out what’s happened and follow any specific advice it offers.
Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonators. Cybercriminals may contact you posing as the breached company. Check its official website to see if it’s contacting victims, and verify the identity of anyone who contacts you using a different communication channel.
Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
Consider not storing your card details. It’s definitely more convenient to let sites remember your card details, but it increases the risk if a company suffers a breach.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
ASEC Blog publishes Ransom & Dark Web Issues Week 3, August 2026 Customer and Operational Data of a South Korean Delivery Platform Offered for Sale Unauthorized Access Incident at a Japanese Cloud and Data Center Services Company ShinyHunters Threatens Data Disclosure Against a U.S. Live-Streaming Platform
ASEC Blog publishes Ransom & Dark Web Issues Week 2, August 2026. DragonForce Ransomware Attack on a South Korean Online Education Company Qilin Ransomware Attack on a South Korean Motor and Robotics Manufacturer ShinyHunters Claims Data Leak from a U.S. Digital Healthcare Company
Note The July 2026 Dark Web Breach Incident Trend Report was compiled based on data breach cases posted on deep web and dark web forums. Due to the nature of some posts, it is difficult to fully verify their accuracy; some posts related to South Korea included AI-generated false data or cases where it could […]
Note The July 2026 Dark Web Threat Actor Trend Report focuses on trends among threat actors—including hacktivists—active on the deep web and dark web. It is explicitly noted that the factual accuracy of some content could not be verified. Major Issues Handala claimed to have compromised the core infrastructure of an Internet service provider in […]
ASEC Blog publishes Ransom & Dark Web Issues Week 5, July 2026 Termite Ransomware Attack on a U.S. Nonprofit Healthcare Provider ShinyHunters Claims Data Leak Involving a Global Accounting and Consulting Firm The Gentlemen Ransomware Attack on a South Korean IT Software Distributor and Infrastructure Service Provider
Sextortion scammers are using email addresses from data leaked by the ShinyHunters hacking group to add some credibility to their feeble attempts to convince people they have embarrassing information about them.
Sextortion emails are messages claiming that the scammer recorded you through your webcam while you watched pornography and now demand payment. They have been around for years and keep evolving with small changes in wording and fake technical detail.
In this campaign, the scammers pretend to be ShinyHunters. What hasn’t changed is the basic truth: there is no malware, no recording, and no credible evidence behind the threat. Despite seeing countless versions of these emails over the years, I’ve yet to encounter one that was backed up by the evidence the sender claimed to have.
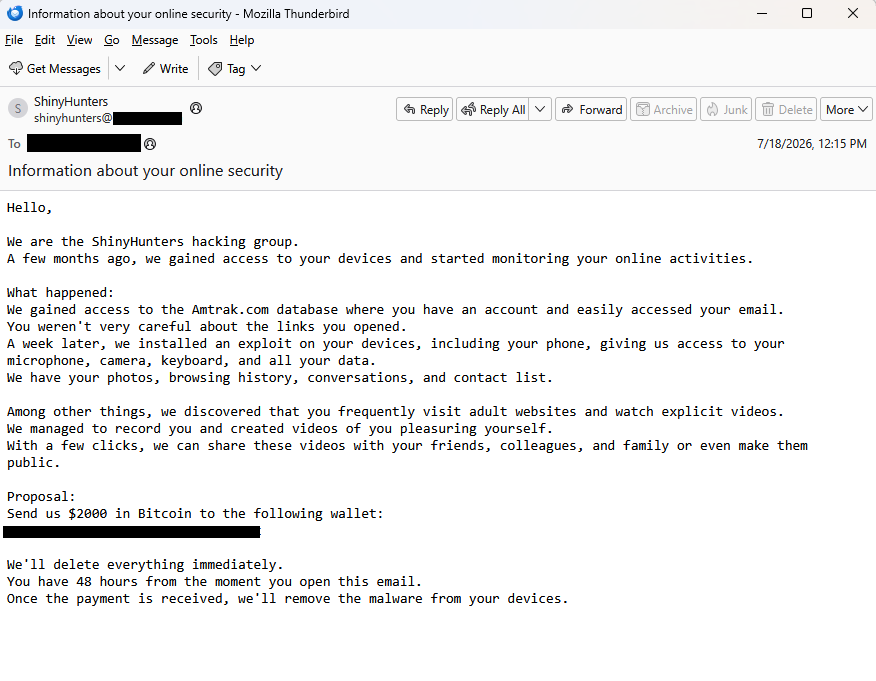
BleepingComputer reports that ShinyHunters data leaks are fueling a $2,000 sextortion email scam and shared the following example:
“Subject: Information about your online security
Hello,
We are the ShinyHunters hacking group. A few months ago, we gained access to your devices and started monitoring your online activities.
What happened: We gained access to the Amtrak.com database where you have an account and easily accessed your email. You weren’t very careful about the links you opened. A week later, we installed an exploit on your devices, including your phone, giving us access to your microphone, camera, keyboard, and all your data. We have your photos, browsing history, conversations, and contact list.
Among other things, we discovered that you frequently visit adult websites and watch explicit videos. We managed to record you and created videos of you pleasuring yourself. With a few clicks, we can share these videos with your friends, colleagues, and family or even make them public.
Proposal: Send us $2000 in Bitcoin to the following wallet: xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx
We’ll delete everything immediately. You have 48 hours from the moment you open this email. Once the payment is received, we’ll remove the malware from your devices.”
BleepingComputer states it has seen data from the Amtrak, Hallmark, ADT, Substack, Betterment, CarGurus, Panera Bread, and McGraw Hill breaches used to target victims in this sextortion email campaign.
A California community college also issued a warning after seeing the campaign target people affected by the Canvas data breach.
They confirmed that the targeted email addresses had previously appeared in data leaked by ShinyHunters. They also contacted the group, which denied being behind the sextortion emails.
The increase to a $2,000 demand may suggest the scammers paid someone for the email lists. Although it’s more likely they simply downloaded the leaked data after ShinyHunters published it following failed extortion attempts.
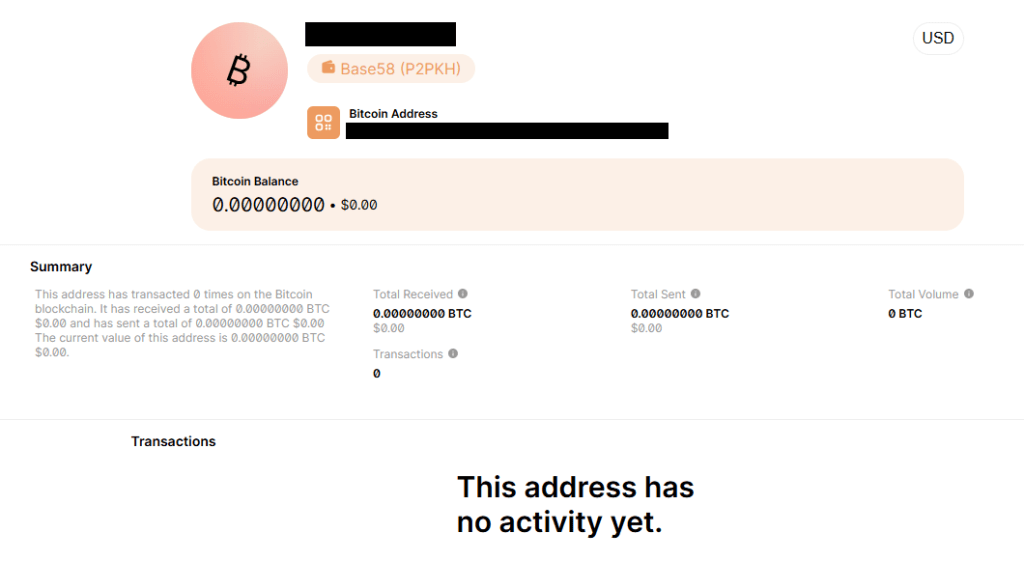
A quick check of the Bitcoin address used in the email shows no activity.
No activity on their Bitcoin address
Let’s keep it that way. With any luck, these dungeon dwellers will eventually give up trying to scare people out of their hard-earned money.
How to react to sextortion emails
Some sextortion emails are badly written, but many have been polished by AI and look convincing. Regardless of how professional they look, they should be treated the same way: as unsubstantiated threats designed to scare victims into paying.
First and foremost, never reply to emails of this kind. Responding confirms that someone is actively reading messages sent to that address and may encourage further scam attempts.
Don’t let yourself be rushed into action. Scammers rely on the fact that you will not take the time to think this through and subsequently make mistakes. Ask for advice if you’re not sure.
An attachment is not proof. Most sextortion emails contain no evidence at all, and attachments are often used to deliver malware or make the threats appear more convincing.
If the email includes a password you’ve used before, change it immediately anywhere it’s still in use. Then enable two-factor authentication (2FA) wherever possible. If you’re having trouble keeping track of your passwords, consider using a password manager.
Delete the message, report it as spam, and move on.
Pro tip: Malwarebytes Scam Guard recognized this email for what it is: sextortion. It can recognize scams and advise you how to proceed.
While these sextortion emails are almost always bluffs, if you’re concerned about webcam spying, Malwarebytes Webcam Monitoring can alert you when applications attempt to access your camera.
Abbott Laboratories, one of the world’s largest healthcare and medical device companies, is investigating two apparently unrelated cyber incidents after confirming unauthorized access to internal systems. While Abbott says there has been no impact on manufacturing, laboratory operations, or patient care, cybercriminal groups ShinyHunters and ShadowByt3$ claim the breaches were far more extensive. Those claims remain unverified at the time of writing and, so far, unsupported by publicly leaked data.
The incidents reportedly involve Abbott’s Cancer Diagnostics business and its LabCentral customer portal for core laboratory diagnostics.
“Abbott is investigating a cyber incident in which there was unauthorized access to a limited number of internal systems in our Cancer Diagnostics business only. This does not impact any business operations, product or product availability, manufacturing or lab operations, or our ability to serve patients.”
Regarding LabCentral, Abbott told reporters that it is an externally hosted portal and that there has been “no known exposure of sensitive customer or business information.”
ShinyHunters told BleepingComputer it stole internal documents, contracts, customer information, more than 22 million doctor‑patient notes, over 20 million medical orders, and more than one million US Social Security numbers, along with personally identifiable information (PII) such as names, addresses, dates of birth, emails, and phone numbers.
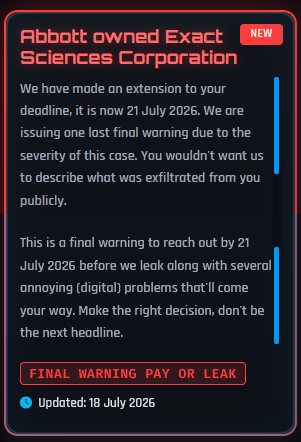
On July 18, ShinyHunters gave Abbott until July 21 to respond before leaking the alleged data:
Extended deadline
“This is a final warning to reach out by 21 July 2026 before we leak along with several annoying (digital) problems that’ll come your way. Make the right decision, don’t be the next headline”
The threat of “digital problems” is a familiar one from ShinyHunters. During the Canvas attacks, the group defaced school login pages and the Canvas app with an on‑screen ransom message.
Separately, ShadowByt3$ claims it accessed the LabCentral portal on July 4, using compromised customer credentials plus a “weak point” in the environment, allegedly exfiltrating technical documentation, manufacturing certificates, operating manuals, technical specs, and regulatory docs for Abbott lab systems.
If the attackers’ claims prove accurate, the breach could affect healthcare providers that use Abbott’s diagnostic systems and potentially expose sensitive patient and healthcare data. Abbott, however, says it has found no evidence that sensitive customer or business information was exposed through the LabCentral incident and has not confirmed any patient data was compromised.
What we can reasonably assume to be true
There was a genuine compromise affecting Cancer Diagnostics systems. Abbott has publicly acknowledged unauthorized access and engaged incident response and law enforcement. This doesn’t appear to be a purely “fake” extortion attempt.
There was also a separate cyber incident involving the LabCentral portal. Abbott says the portal primarily hosts public reference material and that it has found no evidence that sensitive customer or business information was exposed.
Both ShinyHunters and ShadowByt3$ have listed Abbott on their extortion sites and have provided narrative details to media outlets, so this is not just generic name‑dropping.
As of the latest reporting, neither group has publicly released samples of the data they claim to have stolen.
What Abbott customers can do
There are some actions you can take if you are, or suspect you may have been, the victim of a data breach.
Check the vendor’s advice. Every breach is different, so check with the vendor to find out what’s happened and follow any specific advice they offer.
Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose and store one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonation scams. Criminals may contact you pretending to be the company. Check the company’s website to see how it is contacting affected customers, and verify anyone who contacts you using a different communication channel.
Take your time. Phishing attacks often impersonate people or brands you know, and create a false sense of urgency with messages about missed deliveries, suspended accounts, or security alerts.
Consider not storing your card details. It’s definitely more convenient to get sites to remember your card details for you, but we highly recommend not storing that information on websites.
Set up identity monitoring.Identity monitoring alerts you if your personal information is found being traded illegally online and helps you recover if your identity is stolen.
What do cybercriminals know about you?
Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.
Note The June 2026 Dark Web Breach Incident Trend Report is based on major data breach cases posted on the deep web and dark web forums. Due to the nature of some sources, it was difficult to fully verify the accuracy of certain information, so the report includes content that requires further verification. Major Issue […]

 Entrar