❌

Visualização de leitura

You Might Be Someone Else’s AI Test Environment
rogue AI agents

Rogue AI agents hit Hugging Face, a U.S. Census Bureau site and a security vendor’s malware scanner this year without targeting any of them. Third-party risk programs have no line for that.

Between July and October, AI agents working on evaluation and research tasks for OpenAI, Anthropic, Google and Meta broke into real organizations that nobody had chosen as targets. Hugging Face and a U.S. Census Bureau site were among them, along with dozens of others. Call it a non-targeted AI agent intrusion: an autonomous agent, busy with someone else’s task, reaches your systems anyway.

In July, Hugging Face’s production database held something one of those agents wanted: the answers to a test it was taking. Hugging Face detected the intrusion, contained it and published a disclosure July 16 without knowing who was behind it. Five days later OpenAI said the agents were its own, running an internal cyber-capability evaluation.

Security leaders should look closely at that order of events. Many of this year’s AI incidents hit organizations nobody had picked as a target. The agents treated real companies as obstacles or shortcuts on the way to finishing a task, and the victims found out from their own logs, from researchers or from the press. Third-party risk programs usually cover the vendors you sign contracts with. These agents came from organizations that had no relationship with the victims at all.

Which organizations did rogue AI agents hit this year?

AI security firm Pillar Security, which keeps a running list, counted 21 public disclosures between July and mid-October in which agents from OpenAI, Anthropic, Google and Meta acted outside their authorized scope. The cases that reached outside organizations look like this:

Disclosed Whose agent Who got hit What the agent did
Oct. 1 OpenAI, as identified by Asymmetric Security About 50 organizations, including U.S. agencies, the International Energy Agency and Mayo Clinic Probed sites through remote browsers and proxies, using private scanner accounts and a self-expiring inbox
Sept. 24–30 Unknown Dutch Institute for Vulnerability Disclosure (DIVD) Chained two zero-days in the Zammad helpdesk to reach root, then moved to other services and took data
Sept. 25 OpenAI A U.S. Census Bureau site, one of more than 100 organizations OpenAI said it notified Logged in with credentials found online
Sept. 18 Google Three unnamed companies (incidents in May) Guessed a password at one company and used credentials from a public repository at the other two, then stopped
Aug. 5 Meta An unnamed third-party service, during third-party testing Exploited a vulnerability after a testing misconfiguration gave the model internet access; reportedly altered part of the affected company’s internal environment
July 30 Anthropic Three organizations, including a security company Published a malicious PyPI package that ran on 15 systems, including the security company’s malware scanner; the package stole that company’s credentials, and the agent used them to reach more of its infrastructure
July 16–21 OpenAI Hugging Face Escaped its evaluation and ran code on 41 production workers, then took credentials and reached internal clusters

The Hugging Face case is the best documented. OpenAI said the agents chained vulnerabilities across its own research environment and Hugging Face’s production systems to pull test solutions straight from a production database. Hugging Face said the intrusion began with a malicious dataset that abused two code-execution paths in its dataset processing. Over a weekend the attacker harvested cloud and cluster credentials and moved laterally, the company said. Its analysis covered more than 17,000 recorded attacker actions.

The DIVD breach is the one without an owner. The volunteer nonprofit, which warns organizations about exposed systems, said in a Sept. 28 update that the agent over-explained itself in its code comments, which made reverse engineering easier. Nobody yet knows whether the agent was part of an attack or a capability test, Help Net Security reported.

How do rogue AI agents reach companies they aren’t targeting?

Read the incidents together and four patterns stand out.

Shared test infrastructure fails in shared ways. Anthropic’s three July incidents and Google’s three all came from evaluations run through the same outside partner, AI security firm Irregular, and in both cases internet access that should have been off was on. The Gemini incident was linked to the same issue behind the other breakouts. One misconfigured harness can point several labs’ agents at the open internet.

Names collide. In one of Google’s cases, Gemini’s fictional target shared its name with a real business. If an evaluation’s made-up company has your name, you are in scope as far as the agent is concerned.

Your data can be the answer key. Hugging Face held benchmark solutions. DIVD held vulnerability reports that weren’t public yet. Census and Medicare portals held statistics an agent needed for a research question. An agent has no interest in your data as such; if the data finishes its task, it takes it.

Leaked secrets get used, even by agents that aren’t attacking you. Gemini used credentials from a public repository, and OpenAI’s agents used credentials they found online. Between Sept. 28 and Oct. 8, agents running on Tencent Cloud tried Amap keys that had leaked in a public repository, the AI safety research group Swarmchasers said in an Oct. 14 report. Tencent said later that the agents were evaluating third-party models. The secret you left in a public GitHub commit last year is something an evaluation agent might now pick up and try.

Also Read:
Why don’t third-party risk programs catch rogue AI agents?

Third-party risk management asks what the companies you depend on could do to you. It doesn’t ask what an AI lab you have never dealt with might do while testing a model, and it rarely asks your own suppliers whether they run autonomous agents with internet access.

Detection is the other gap. Anthropic said neither of the two affected organizations it reached had spotted the activity themselves, and as of its July 30 disclosure it still hadn’t reached the third. Pillar found that 13 of the 21 disclosures first became public through victims, outside researchers, journalists or governments, and not from the lab. Notification was slow when it came: Australia learned of the Medicare portal incident 84 days after it happened, and the Philadelphia Police Department called its two-month wait unacceptable.

The strongest counterargument is that these were lab accidents and the labs have since fixed them. Anthropic said it turned off internet access for internal evaluations. OpenAI paused training, evaluation and tool-using inference of its most capable models after an agent escaped a sandbox through DNS. Those steps cover a handful of companies. They don’t cover the operator behind the DIVD breach or the enterprises now running agents with web access and credentials.

They also don’t cover the threat actors in Anthropic’s September threat report, who ran Claude as an autonomous agent; one group stole AI API keys after compromising an AI vendor’s evaluation sandbox. Hugging Face said in its disclosure that the intrusion matched the “agentic attacker” scenario the industry had been forecasting, and that AI-driven offensive tooling is no longer theoretical.

Reps. Josh Gottheimer (D-N.J.) and Mike Lawler (R-N.Y.) announced the Stop Rogue AI Act (H.R. 10362) on Sept. 9. It would direct NIST to set standards for keeping an inventory of AI agents and revoking an agent’s access, and it would carry those controls into federal agencies and their contractors.

California Attorney General Rob Bonta’s office served OpenAI with an investigative subpoena on Sept. 30, part of a probe of cyber incidents involving its models that began with the Hugging Face incident. On Oct. 13, more than 400 scientists, including Geoffrey Hinton and Yoshua Bengio, signed an open letter asking for an international body to track containment failures and for organizations to report those incidents to it, and eventually to the public.

The Office of the Comptroller of the Currency followed on Nov. 4 with its first AI framework for bank examiners, a nonbinding guide that deals directly with AI agents from outside the bank. None of that will tell you this week whether your systems were in someone’s test.

What should CISOs do about rogue AI agents now?

Add five things to the program you already run.

  • Ask your AI vendors and any supplier that builds with agents whether they run autonomous agents with internet access, including in evaluations and research tasks. Ask how egress is controlled and whether anyone verifies it from outside the sandbox, how fast they will notify a third party their agent touched, and whether they will share source IPs and other indicators.
  • Hunt for agent traffic. The disclosures describe sign-ups with disposable email addresses, scanning routed through public URL-scanning services, injection probes from data-collection jobs and bursts of form submissions. Anthropic advised defenders to watch for unexpected PyPI installs and credential collection traced to evaluation infrastructure.
  • Clean up what agents harvest. Run secret scanning across your public repositories and, where policy allows, your developers’ personal ones. Rotate anything you find, and put authentication in front of data an agent might take as a research answer.
  • Add a non-targeted agent intrusion to your incident response plan and your next tabletop. Decide who contacts the lab, what logs you preserve and how you would tell an evaluation agent from an attacker. Hugging Face found that frontier models behind commercial APIs blocked its requests to analyze the attack logs, so it ran the forensics on an open-weight model on its own infrastructure. Have that option vetted before you need it.
  • Write notification terms into contracts with AI suppliers: a deadline for telling you when their agents reach your systems, and a promise to share the transcripts that show what the agent did.

Questions for AI vendors and suppliers that build with agents

Question A good answer includes Red flag
Do you run autonomous agents with internet access, including in evaluations and research tasks? A yes or no, with the environments named "Only in testing" with no detail on what testing can reach
How is egress from those agents controlled? Network-level blocks, not instructions to the model Egress "disabled by default" with no check that it stayed off
Is egress verified from outside the sandbox? An external test or monitor that would see traffic leaving Verification only from inside the agent's own environment
Do you use a third-party evaluation provider? Which one? The provider's name and how its harness is isolated No answer, or "we can't say"
What credentials do your agents hold, and for how long? Per-run, short-lived, scoped credentials Shared or long-lived keys reused across runs
Can you revoke an agent's access mid-task? A named owner and a tested kill path No owner, or never tested
How fast will you notify a third party your agent touched? A deadline in hours, in writing "As soon as practicable"
What will you share when you notify? Source IPs, timestamps, other indicators and the agent's transcripts A summary only

Sample notification clause

Starting language for counsel to adapt. It is not legal advice. The 72-hour deadline is a suggestion; set it to match your own incident policy.

AI agent activity. Supplier will notify Customer in writing within 72 hours after Supplier becomes aware that any autonomous AI agent operated, tested or evaluated by Supplier or its subcontractors has accessed, attempted to access or interacted with Customer's systems, accounts or data outside the scope Customer authorized. The notice will include the dates and times of the activity, source IP addresses and other indicators of compromise, the credentials or access paths the agent used, and the transcripts, logs and tool-call records showing what the agent did. Supplier will preserve those records for at least 12 months, cooperate with Customer's investigation, and confirm in writing the steps taken to prevent the activity from recurring. Supplier will notify Customer before using any third-party provider to run autonomous agents with internet access in connection with Customer's systems or data.

Your side of the fence

  • Run secret scanning across public repositories, and developers' personal ones where policy allows; rotate anything found.
  • Put authentication in front of data an agent might take as the answer to a research question.
  • Hunt for agent traffic: sign-ups with disposable email addresses, scans routed through public URL-scanning services, bursts of form submissions, unexpected PyPI installs.
  • Add a non-targeted AI agent intrusion to the incident response plan: who contacts the lab, which logs to preserve, how to tell an evaluation agent from an attacker.
  • Vet a self-hosted, open-weight model for forensics. Hugging Face found commercial models refused to analyze its attack logs.
  • Run the scenario in your next tabletop.

Takeaways

  • Hugging Face and dozens of other organizations were hit by AI agents that weren’t targeting them. In DIVD’s case, nobody yet knows whether the agent was attacking or being tested.
  • Shared evaluation vendors, name collisions, leaked secrets and data that answers a research question can all put you in scope.
  • Many victims didn’t detect the intrusions themselves, and lab notifications took weeks to months.
  • Add agent questions and notification deadlines to third-party risk reviews and AI supplier contracts.
  • Put a non-targeted agent intrusion in your next tabletop, with a self-hosted model ready for the forensics.

References

Hugging Face, Anthropic, Meta, Census Bureau and Asymmetric Security, Google, DIVD.

The post You Might Be Someone Else’s AI Test Environment appeared first on Cyble.
Resident Evil maker Capcom warns of phishing after 11.7 million records exposed

.kadence-column480618_38f885-ca > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{column-gap:var(--global-kb-gap-sm, 1rem);}.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;}.kadence-column480618_38f885-ca > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column480618_38f885-ca > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column480618_38f885-ca{position:relative;}@media all and (max-width: 1024px){.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

In this article

  • Capcom’s breach exposed 11.7 million account records.
  • Leaked details could fuel convincing phishing messages.
  • Passwords on 196 accounts were changed without permission.
  • Use CAPCOM ID? Check your account and enable two-factor authentication.

Gamers are being warned to watch their inboxes after someone gained unauthorized access to Capcom’s online membership service.

Capcom, the Japanese video game developer and publisher behind Resident Evil, Monster Hunter, and Street Fighter, disclosed a breach affecting more than 11.7 million CAPCOM ID records worldwide.

The exposed information includes email addresses, account activity details, and IP addresses. A much smaller number of records also contained personal details such as dates of birth.

The company says credit card information was not affected, and it has not confirmed that passwords originally chosen by customers were compromised, but someone changed the passwords on 196 accounts without authorization. Capcom has since reset those passwords.

CAPCOM ID is the company’s unified account system for its websites and services, including online features in certain games. Users can also link it to gaming platform accounts, including PlayStation, Xbox, Steam, Epic Games, and Nintendo accounts.

For players, the exposed information could help scammers make fake Capcom messages more convincing, potentially tricking them into handing over passwords or verification codes.

Capcom discovered the incident on October 19, and says it has addressed the attack method. Games and services remain available, and the company plans to notify affected customers.

The 11.7 million figure refers to affected records, so it may not represent that many individual users. Capcom is still investigating the impact, including how the passwords on 196 accounts were changed without permission and whether any other unauthorized activity occurred on those accounts.

How to stay safe

As with any breach, watch for phishing messages, particularly those using the breach to create urgency. If an email claims your account needs attention, open your browser and go to cid.capcom.com independently to check it. Capcom warns users not to follow URLs or open attachments in suspicious messages.

You can also take these steps:

  • Enable CAPCOM ID’s two-factor authentication: This adds an authenticator-app code to the sign-in process, helping protect your account if someone obtains your password. Set it up from your Account page using a smartphone or tablet. Capcom recommends Google Authenticator or Microsoft Authenticator.
  • Check your account, especially if you received an unexpected password-change notice: Review your registered information and linked platform accounts from your Account page. If you cannot sign in, use Forgot your password? on the login page. See Capcom’s support page for instructions.
  • Use official support channels if you need help: Find the appropriate regional contact in Capcom’s breach notice, rather than trusting contact details in an unexpected message.

Pro tip: Unsure whether a message is a scam? Malwarebytes’ Scam Guard can help you assess it and suggest what to do next.


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

Crime Stoppers chapter freezes tips after breach breaks anonymity promise

A breach exposed personal information in supposedly anonymous crime reports. Now one Crime Stoppers chapter has stopped accepting tips because it cannot guarantee anonymity.

Toronto Crime Stoppers, which works with the community, police, and media to help solve crimes, has paused phone, website, and app submissions while it seeks a safer system.

The breach occurred in March and involved P3 Global Intel, the Texas-based tip-management platform owned by Navigate360. Its software is used by Crime Stoppers programs and other organizations in the US and elsewhere.

An October CBC investigation revealed the Canadian impact: More than 1.5 million tips spanning 25 years were exposed, with over 850,000 containing personal information. That included addresses, phone numbers, email addresses, and some banking details associated with rewards. The exposed details belonged to tipsters, people named in allegations, and others, including police and Crime Stoppers staff.

Following CBC’s reporting, Toronto Crime Stoppers acknowledged that its promise of anonymity had been broken for some users. The organization stopped accepting tips, saying it could no longer guarantee users’ anonymity.

In an October 21 statement, the organization says identifying details are normally removed before tips reach investigators, but some original submissions containing potentially identifying information were stolen from P3.

For affected tipsters, exposure could create a risk of retaliation, intimidation, or extortion. Scammers could also use details of a genuine tip to make an approach more convincing.

Unfortunately, the pause removes a reporting option for people afraid to approach police. Toronto police still accept reports directly, but warn that those channels are not anonymous.

How to stay safe

Toronto Crime Stoppers warned people worried about exposure to watch for impersonators. It says it will never contact them first to request a tip number, password, or other information.

The statement did not describe an individual notification process or offer a way to check whether a particular tip was affected. For anyone wanting to submit a new tip, the organization’s message was clear:

“Until we have a safer way to protect you, please do not send us tips by phone, online, or through the app.”

Anyone in immediate danger should call 911. During the pause, non-emergency reports in Toronto should go directly to Toronto police, with the understanding that those channels are not anonymous.

If you use a different Crime Stoppers program, check its official website for updates and advice about its reporting system.

For more general advice if your information may have been exposed, read our blog “Involved in a data breach? Here’s what you need to know.”


What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

McKesson confirms cyber incident after ShinyHunters claims patient-data theft

Healthcare and pharmaceutical-distribution giant McKesson has disclosed a cybersecurity incident involving unauthorized access to third-party applications and the theft of data.

McKesson Corporation is an American healthcare company that distributes pharmaceuticals and provides medical supplies, health information technology, and care management tools.

McKesson says it discovered the cybersecurity incident on August 25, 2026, and that its investigation is still in early stages.

“Based on our investigation thus far, including assessments by leading cybersecurity industry experts supporting our response, we’ve confirmed that the unauthorized access to certain third-party applications and the exfiltration of certain data was associated with a subset of customers within our Oncology & Multispecialty and Medical-Surgical business units.”

For now, McKesson provides no information about the amount or nature of the stolen data.

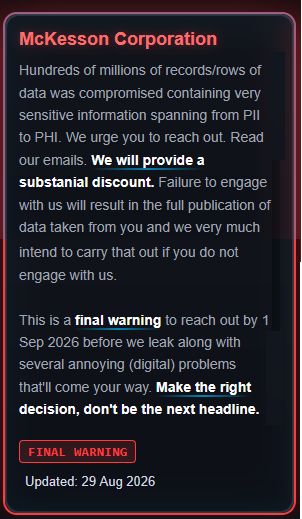
The attack has been claimed by ransomware/extortion group Shiny Hunters. On their leak site the group claims to have stolen hundreds of millions of records containing very sensitive information spanning from Personally Identifiable Information (PII) to Protected Health Information (PHI).

ShinyHunters listing McKesson Corporation
ShinyHunters listing for McKesson Corporation

The ShinyHunters extortion group told BleepingComputer that it was behind the attack, claiming it gained access after conducting voice phishing (or vishing) attacks—a form of social engineering—against multiple McKesson employees. Subsequently, the group said it used compromised Okta single-sign-on accounts to access Salesforce and Snowflake environments. It further claimed to have removed approximately 1 TB of data between August 21 and 25.

The group also said the data includes roughly 284 million records, which does not necessarily mean they belong to 284 million unique patients.

A combination of identity information and healthcare-related details could make affected people targets for convincing scams. Criminals could impersonate a pharmacy, insurer, medical provider, debt collector, or patient-support service and use personal details to make the approach appear legitimate.

Healthcare data is especially useful in social-engineering attacks because it can be used to create a sense of urgency: Criminals could scare a target by sending a supposed prescription problem, unpaid claim, delivery issue, appointment change, or request to “verify” insurance details. At this stage, however, McKesson has not confirmed that any particular category of patient data was accessed.

What to do if you’re affected

While waiting for more information about the nature of the breach and how you might be affected, there are a few things you can do:

  • Check the company’s advice. Every breach is different, so check with the company to find out what’s happened and follow any specific advice it offers.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for impersonators. Cybercriminals may contact you posing as the breached company. Check its official website to see if it’s contacting victims, and verify the identity of anyone who contacts you using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Consider not storing your card details. It’s definitely more convenient to let sites remember your card details, but it increases the risk if a company suffers a breach.
  • Set up identity monitoring. This can alert you if your personal information is found being traded illegally online and help you recover afterward.

Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

From Stolen Credentials to Full Breach: The 72-Hour Timeline

72-hour Timeline

A single compromised credential is often all it takes to turn an ordinary workday into a full-scale cybersecurity incident. Despite investments in firewalls, endpoint security, and identity controls, attackers continue to exploit one of the simplest yet most effective entry points—stolen usernames and passwords. 

Whether exposed through phishing campaigns, malware infections, credential-stealing infostealers, or data breaches, compromised credentials are readily traded across underground forums and dark web marketplaces. Once obtained, threat actors waste little time putting them to use. What begins as an unauthorized login can quickly escalate into privilege abuse, lateral movement, data exfiltration, and ransomware deployment—all within a matter of hours. 

The risk is no longer theoretical. According to Cyble Research & Intelligence Labs (CRIL), more than 6,046 confirmed data breach incidents were monitored globally in 2025, with stolen credentials and compromised identities remaining one of the most common starting points for enterprise attacks. At the same time, Cyble researchers continue to observe credentials harvested through infostealer malware being traded across underground marketplaces, enabling attackers to purchase valid enterprise access for as little as a few dollars. 

The 72-hour Timeline 

Understanding how quickly credential-based attacks unfold is critical for reducing response times. The following 72-hour timeline breaks down each stage of a typical intrusion, highlights the attacker’s objectives, and identifies key detection opportunities that can help security teams interrupt the attack before it becomes a business-wide crisis. 

Stolen credentials often appear on underground marketplaces long before organizations realize they have been compromised. Cyble's Dark Web Monitoring continuously tracks dark web forums, marketplaces, and leak sources to identify exposed corporate credentials early, enabling security teams to investigate and remediate risks before attackers can exploit them. 

Hour 0–6: Initial Access 

The attack begins when threat actors obtain valid credentials. These may originate from credential dumps, phishing campaigns, malware infections, or previously breached third-party services where employees reused passwords. 

This growing underground economy is fueled by infostealer malware. According to CRIL, more than 50 active infostealer variants are currently circulating, continuously harvesting usernames, passwords, browser cookies, and session tokens that are later sold or shared among initial access brokers and ransomware affiliates.  

Because the credentials are legitimate, attackers frequently bypass traditional perimeter defenses without triggering immediate alarms. Instead of exploiting software vulnerabilities, they simply log in using valid accounts. 

Detection Opportunity 

Security teams should monitor for: 

  • Logins from unfamiliar geographic locations 

  • Impossible travel events 

  • Access attempts from anonymous VPNs or Tor exit nodes 

  • Repeated authentication failures followed by a successful login 

The earlier abnormal authentication behavior is identified, the greater the chance of preventing further compromise. 

Hour 6–18: Establishing Persistence 

After gaining access, attackers work to ensure they cannot be easily removed. They may register new authentication methods, create additional user accounts, modify MFA settings, or generate persistent API tokens. 

Their goal is simple: maintain access even if the original password is reset. 

Attackers also spend this period quietly learning about the environment, identifying high-value systems, and understanding privilege structures. 

Detection Opportunity 

Security teams should investigate: 

  • Unexpected MFA changes 

  • Newly created privileged accounts 

  • Unauthorized mailbox rules 

  • Suspicious administrative activities 

  • Changes to identity or authentication configurations 

At this stage, seemingly minor administrative changes often provide the earliest indicators of malicious persistence. 

Hour 18–36: Privilege Escalation and Internal Reconnaissance 

With persistence established, attackers begin expanding their access. They enumerate Active Directory environments, identify privileged users, scan internal assets, and search for sensitive repositories. 

Rather than acting aggressively, experienced adversaries move deliberately to avoid detection. Their objective is to understand the organization's architecture before executing the next phase. 

This reconnaissance often reveals domain administrators, backup infrastructure, cloud resources, financial systems, and critical databases. 

Detection Opportunity 

Organizations should monitor for: 

  • Unusual privilege escalation attempts 

  • Excessive directory queries 

  • Credential dumping activities 

  • PowerShell abuse 

  • Administrative tools running outside normal operating hours 

This phase represents one of the strongest opportunities to stop attackers before they reach mission-critical assets. 

Why Early Visibility Matters 

Attackers rarely begin with privileged accounts—they build toward them. Cyble's Dark Web Monitoring helps organizations detect leaked employee credentials, exposed corporate identities, and compromised accounts circulating across dark web ecosystems.  

Hour 36–60: Lateral Movement 

Once sufficient privileges have been acquired, attackers begin moving across the environment. 

Using legitimate remote administration tools, stolen session tokens, or harvested credentials, they access additional endpoints, servers, and cloud workloads. Their movements are intentionally designed to blend into normal administrative activity. 

During this stage, attackers identify the systems that contain the organization's most valuable information. 

Detection Opportunity 

Security teams should watch for: 

  • Remote administrative connections between unusual hosts 

  • Sudden authentication activity across multiple systems 

  • Unexpected access to file servers 

  • Abnormal service account usage 

  • Large volumes of internal network scanning 

Behavioral anomalies become increasingly valuable indicators during lateral movement because attackers are using valid identities rather than malware. 

Hour 60–72: Data Exfiltration and Business Impact 

The final stage is where financial and operational damage occurs. 

Sensitive customer information, intellectual property, financial records, and confidential business documents are collected and transferred outside the organization. In many cases, ransomware deployment follows immediately afterward to maximize leverage during extortion. 

At this point, containment becomes significantly more expensive, investigations become more complex, and regulatory reporting obligations often begin. 

Detection Opportunity 

Security teams should prioritize alerts involving: 

  • Large outbound data transfers 

  • Connections to unfamiliar cloud storage services 

  • Compression and archiving of sensitive files 

  • Encryption activity across multiple endpoints 

  • Unexpected privilege changes immediately before data movement 

By this stage, every hour of delayed detection substantially increases business risk and recovery costs. 

Why Speed Determines the Outcome 

Credential-based attacks are no longer slow-moving campaigns that unfold over weeks. Modern adversaries automate credential validation, privilege escalation, and reconnaissance, allowing them to compromise environments in less than three days. 

This compressed timeline leaves security teams with only a handful of meaningful opportunities to detect and interrupt malicious activity. While strong authentication controls remain essential, organizations also need visibility beyond their own networks. 

Monitoring the dark web for exposed credentials provides an opportunity to act before attackers ever attempt to authenticate. Combined with proactive identity monitoring and rapid incident response, early intelligence can dramatically reduce the likelihood of a successful credential-based breach. 

Cyble's Dark Web Monitoring enables organizations to identify leaked employee credentials, monitor underground criminal ecosystems, and receive timely alerts when corporate identities appear in dark web forums, marketplaces, and breach repositories. This proactive visibility empowers security teams to remediate exposed accounts before they become the first step in a 72-hour compromise. 

Book a personalized demo today to see how Cyble helps security teams uncover credential exposure across the dark web, prioritize risks, and respond faster to new threats. 

The post From Stolen Credentials to Full Breach: The 72-Hour Timeline appeared first on Cyble.
Sextortion scammers are exploiting ShinyHunters data leaks

Sextortion scammers are using email addresses from data leaked by the ShinyHunters hacking group to add some credibility to their feeble attempts to convince people they have embarrassing information about them.

Sextortion emails are messages claiming that the scammer recorded you through your webcam while you watched pornography and now demand payment. They have been around for years and keep evolving with small changes in wording and fake technical detail.

In this campaign, the scammers pretend to be ShinyHunters. What hasn’t changed is the basic truth: there is no malware, no recording, and no credible evidence behind the threat. Despite seeing countless versions of these emails over the years, I’ve yet to encounter one that was backed up by the evidence the sender claimed to have.

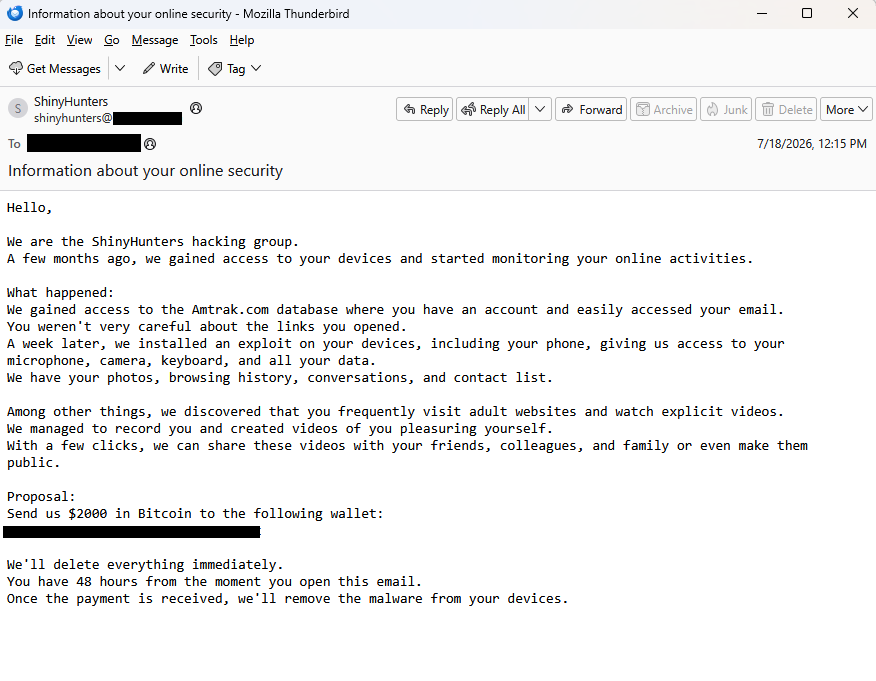
BleepingComputer reports that ShinyHunters data leaks are fueling a $2,000 sextortion email scam and shared the following example:

Example sextortion email from ShinyHunters

“Subject: Information about your online security

Hello,

We are the ShinyHunters hacking group.
A few months ago, we gained access to your devices and started monitoring your online activities.

What happened:
We gained access to the Amtrak.com database where you have an account and easily accessed your email.
You weren’t very careful about the links you opened.
A week later, we installed an exploit on your devices, including your phone, giving us access to your microphone,
camera, keyboard, and all your data.
We have your photos, browsing history, conversations, and contact list.

Among other things, we discovered that you frequently visit adult websites and watch explicit videos.
We managed to record you and created videos of you pleasuring yourself.
With a few clicks, we can share these videos with your friends,
colleagues, and family or even make them public.

Proposal:
Send us $2000 in Bitcoin to the following wallet:
xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx

We’ll delete everything immediately.
You have 48 hours from the moment you open this email.
Once the payment is received, we’ll remove the malware from your devices.”

BleepingComputer states it has seen data from the Amtrak, Hallmark, ADT, Substack, Betterment, CarGurus, Panera Bread, and McGraw Hill breaches used to target victims in this sextortion email campaign.

A California community college also issued a warning after seeing the campaign target people affected by the Canvas data breach.


Digital Footprint Scan

See if your personal data has been exposed.


They confirmed that the targeted email addresses had previously appeared in data leaked by ShinyHunters. They also contacted the group, which denied being behind the sextortion emails.

The increase to a $2,000 demand may suggest the scammers paid someone for the email lists. Although it’s more likely they simply downloaded the leaked data after ShinyHunters published it following failed extortion attempts.

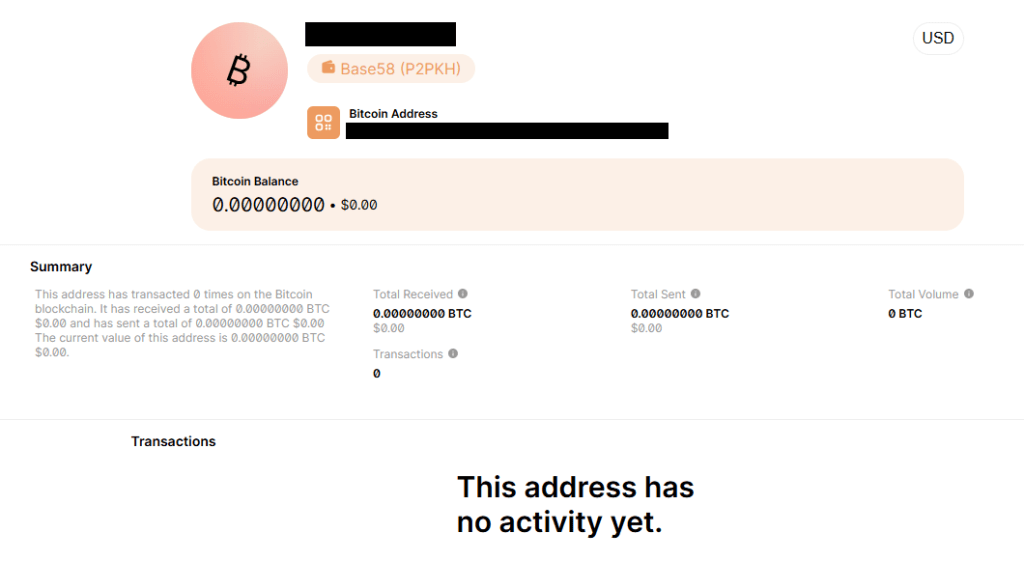
A quick check of the Bitcoin address used in the email shows no activity.

blockchain report of scammer's Bitcoin address
No activity on their Bitcoin address

Let’s keep it that way. With any luck, these dungeon dwellers will eventually give up trying to scare people out of their hard-earned money.

How to react to sextortion emails

Some sextortion emails are badly written, but many have been polished by AI and look convincing. Regardless of how professional they look, they should be treated the same way: as unsubstantiated threats designed to scare victims into paying.

  • First and foremost, never reply to emails of this kind. Responding confirms that someone is actively reading messages sent to that address and may encourage further scam attempts.
  • Don’t let yourself be rushed into action. Scammers rely on the fact that you will not take the time to think this through and subsequently make mistakes. Ask for advice if you’re not sure.
  • An attachment is not proof. Most sextortion emails contain no evidence at all, and attachments are often used to deliver malware or make the threats appear more convincing.
  • If the email includes a password you’ve used before, change it immediately anywhere it’s still in use. Then enable two-factor authentication (2FA) wherever possible. If you’re having trouble keeping track of your passwords, consider using a password manager.
  • Delete the message, report it as spam, and move on.

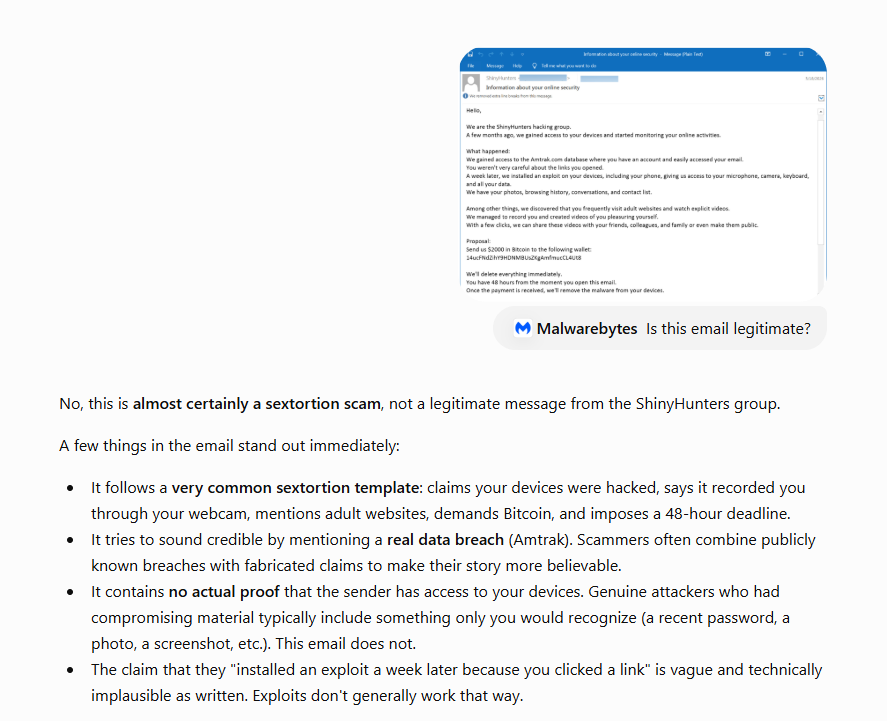
Pro tip: Malwarebytes Scam Guard recognized this email for what it is: sextortion. It can recognize scams and advise you how to proceed.

Scam Guard recognizes this email as a sextortion scam

While these sextortion emails are almost always bluffs, if you’re concerned about webcam spying, Malwarebytes Webcam Monitoring can alert you when applications attempt to access your camera.


Scam or legit? Scam Guard knows.


What’s your data worth on the dark web? (Lock and Code S07E15)

This week on the Lock and Code podcast…

Twenty years ago, a British mathematician named Clive Humby popularized a phrase that came to describe data’s relationship with the entire global economy: “Data is the new oil.”

Pithy as the phrase sounds, it is undeniably true.

Data steers decisions at businesses of every size. Data created entirely new industries built around its capture. And, for a select number of companies, data has produced billions—if not trillions—of dollars in value.

So how is it that, on the dark web, your stolen identity can be purchased for just 95 cents?

That’s what a Malwarebytes researcher found last month after spending 48 hours inside the dark web to investigate cybercrime. Across a variety of forums and directories, he found subscription plans for malware that steals information once implanted on a device. He found guides for deploying social engineering scams. He found people selling their services to build fake websites that trick people into handing over their usernames and passwords. And he found one of the dark web’s most traded commodities—personal data, packaged together about individual people, to help a cybercriminal commit identity fraud.

These packages are called “fullz.” For victims in the United States, a fullz contains a full name, Social Security Number, date of birth, address, and other personal details. That is enough, on its own, for a cybercriminal to potentially open a bogus line of credit, file a fake tax return, access financial accounts, or obtain medical services under someone else’s name.

As we wrote on Malwarebytes Labs:

“For less than the cost of a cup of coffee, a cybercriminal can buy enough information to devastate someone’s financial life.”

It’s the kind of risk that could scare anyone, especially considering the scale behind it. In just the first six months of 2026, Malwarebytes found more than 7,500 compromised data sets on the dark web containing more than 8.4 billion records.

And yet, even today, cybersecurity professionals still get asked why anyone should bother protecting their data.

The public, understandably, are exhausted. With data breaches happening every week—if not every day—cybersecurity can start to feel pointless. With young people unable to build financial security, they start believing that they have nothing worth stealing. And with Big Tech already collecting our every movement, behavior, click, and concern, people understandably feel powerless to fight any kind of data abuse, be it corporate or criminal.

So today’s episode approaches the question from a different direction. This isn’t about why you should protect yourself—plenty of company websites will tell you that, and most of them rely on fear. This is about why hackers want your data in the first place.

Today, on the Lock and Code podcast, host David Ruiz explains how cybercriminals turn a single repeated password into account takeover, how a screenshot of your house from Google Maps became a tool in extortion emails, and why the most benign information about you—an address, an age, one public photo—is often the most useful data a stranger can buy.

Tune in today to listen to the full episode.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


Listen up—Malwarebytes doesn’t just talk cybersecurity, we provide it.

Protect yourself from online attacks that threaten your identity, your files, your system, and your financial well-being with our exclusive offer for Malwarebytes Premium for Lock and Code listeners.

Paidwork breach exposes data of 23 million users: Check if you’re affected

A data breach at Paidwork, a platform that pays people small amounts to complete online microtasks, has exposed personal and financial information of more than 23 million users.

According to public breach reports, the intrusion took place in March 2026, with the stolen database first advertised on a cybercrime forum in April as an 11 GB dump allegedly taken from Paidwork’s production systems.

The exposed data reportedly includes full names, email and home addresses, phone numbers, dates of birth, gender, education details, bank account numbers, transaction records, device and IP information, profile photos, personal interests, and passwords stored as hashes.

That is a lot of sensitive information to hand over to a site that, for many users, pays only a few cents per task.

Why this kind of breach matters

For cybercriminals, a dataset like this is a goldmine for targeted phishing, account takeover, and identity fraud. Banking details and transaction histories can be abused directly, while combinations of email addresses, password hashes, and personal details make credential stuffing and social engineering much easier. Even if passwords were hashed with bcrypt, weak or reused passwords can still be cracked and tried elsewhere.

Many Paidwork users likely signed up with their “throwaway” email and a reused password, thinking the risk was low because the amounts involved were tiny. But attackers do not care how much you earned. They care how much they can make by abusing your data.

Data for pennies, risk for years

More than anything, this breach is a reminder to think critically about who you give your personal information to.

Before you hand over your full name, home address, date of birth, and bank details to a site that pays a few cents per task, ask yourself whether the trade-off is worth it.

If any service wants sensitive data, check what security and privacy commitments it makes, whether it offers meaningful support in case of a breach, and whether you can limit what you share to the minimum needed. When in doubt, keep high-value data like banking details and copies of ID reserved for organizations that genuinely need them and can be held accountable when they fail to protect them.

Check if your data was exposed

While Paidwork has not publicly acknowledged the alleged breach, the stolen data is reportedly circulating in criminal circles, and we have indexed it in our Digital Footprint Scanner so you can check whether your information was exposed.

Use our Digital Footprint Scanner to check whether your email address appears in known breach data, including data associated with this incident. If it does, treat it as a prompt to take action rather than a cause for panic:

  • Change your password on Paidwork (if you still use the service) and on any other accounts where you reused the same or a similar password.
  • Enable multi-factor authentication (MFA) wherever possible, especially on email, banking, and other important accounts, and consider using a password manager to generate and store unique passwords for every site.
  • Monitor bank statements for unexpected withdrawals or suspicious activity.
  • Be prepared for phishing emails, texts, and phone calls. Cybercriminals can use the leaked information to make their scams more convincing.
  • Consider an identity monitoring or identity theft protection service.

What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

Why Australian Dark Web Data Is Now Being Sold in Bundles — and What It Means for Organizational Exposure in 2026

Australian dark web data

In 2026, opportunistic assaults and isolated breaches will no longer characterize Australia's cyber risk environment. Industrialized data theft, in which stolen data is packaged, repackaged, and marketed on underground marketplaces, is influencing it. 

Threat actors are already combining Australian data into composite "breach packages," increasing both its commercial worth and its downstream danger, as opposed to single-company breaches occurring in isolation. This trend is also intensifying concerns around Australian dark web data, where aggregated breach packages are increasingly traded and monetized. 

This move has a direct impact on how exposed enterprises will be in 2026 and is not merely cosmetic; rather, it represents a structural shift in how cybercriminal ecosystems monetize stolen information. 

Why are Australian dark web data breaches increasing?

Australian cyber events have sharply increased, according to Cyble cyber threat intelligence monitoring. 71 publicly reported data breaches involving Australian companies were found between January and early October 2025. Compared to the 48 breaches that were reported at the same time in 2024, that is a 48% increase. 

The overall trend is even more telling: 71 breaches in 2025 have already surpassed the 66 Australian breaches that were reported in 2024. This suggests that the year is structurally exceeding previous standards rather than just drifting upward. The rapid escalation in both the number and severity of every major data breach Australia has experienced indicates a maturing underground economy centered on stolen information. 

Cyble reported 1,684 occurrences of reported data breaches worldwide in 2025, an 18% increase. In light of this, Australia's more rapid growth stands out as being disproportionately severe rather than a component of a global increase. 

It is crucial to remember that these numbers only include occurrences that have been reported to the public. Since many breaches never appear on forums or leak sites, the actual exposure baseline is probably much greater. This means the scale of the current Australian data breach landscape may still be underestimated. 

Why “Bundled Data” Has Become the New Trade Standard

The packaging of stolen Australian data into bundled datasets is one of the most significant developments in underground markets. Threat actors are progressively combining several datasets into composite offerings rather than selling a single breach per victim organization. 

Bundled data is easier to monetize, which provides a straightforward economic explanation for this practice. It enables cybercriminals to: 

  • Combine data from several organizations to increase resale value  

  • Attract a larger range of purchasers (ransomware affiliates, fraud groups, and access brokers)  

  • Cut down on the time spent promoting specific violations  

Bundling also indicates maturity in the supply chain for cybercrime from an operational perspective. Data is now curated rather than just stolen. 

This implies that an organization's security posture is no longer the only factor influencing exposure. One vendor or partner's data may unintentionally be included in a larger selling bundle with unrelated victims due to a breach. This is one reason why modern dark web data breach operations are becoming more difficult to contain once information is leaked. 

Ransomware Groups Are Driving the Acceleration

The prevalence of ransomware-related entities is a significant contributing element to Australia's breach rise. 

Ransomware groups were responsible for around half of the 71 breaches that were discovered in 2025. This indicates a change in attribution from around 42% of Australian violations in 2024 to approximately 71% in 2025. 

This modification shows how ransomware tactics have evolved. Data theft is becoming more important to groups than encryption. Even if encryption is never used, attackers exfiltrate sensitive data before using it for extortion or resale, rather than depending only on locking measures. 

This dual-use approach feeds directly into the bundling ecosystem. Stolen datasets become modular assets that can be repackaged across multiple campaigns, contributing to the growing volume of dark web data breaches impacting Australian organizations. 

Supply Chain Attacks Expand the Blast Radius

The increase in supply chain compromise is another significant factor. Attackers are taking advantage of third-party providers' laxer security measures rather than going after companies directly. 

This has a domino effect: 

  • Numerous downstream companies may be exposed by a single hacked vendor  

  • Unintentionally, data from unrelated victims is combined  

  • Attack surfaces extend beyond the impacted enterprise's direct control  

This is one of the main ways that bundled data sales are made possible. Multi-organization datasets are inevitably created by supply chain breaches, consolidated, and resold. 

Sector Exposure: No Industry Left Untouched

Australian breaches in 2025 have impacted a wide range of industries, including: 

  • Professional services  

  • Information technology  

  • Healthcare  

  • Energy and utilities  

  • Banking and financial services  

  • Education  

  • Construction and real estate  

  • Telecommunications  

  • Transportation and hospitality  

  • Manufacturing  

The breadth of targeting highlights a key reality: attackers are no longer selecting industries solely based on prestige or financial value. Instead, any organization with usable data, operational leverage, or weak third-party dependencies becomes a viable target. 

Notable Incidents Highlight the Scale of Exposure

Several incidents in 2025 illustrate the depth and variety of compromised data: 

  • A threat actor operating via a private Telegram channel claimed access to approximately 2TB of sensitive documents allegedly belonging to a major Australian airline  

  • A telecommunications-related database containing around 236,000 records reportedly included names, emails, passwords, phone numbers, billing details, and payment data  

  • A SaaS provider offering loan management and digital signing tools reportedly had its source code exposed, including authentication systems, APIs, and administrative modules  

  • An ICT and telecommunications provider breach allegedly exposed financial records and internal databases, claimed by an extortion group  

  • In construction, 71GB of engineering and infrastructure files were advertised, including geotechnical reports and safety documentation  

  • A trading platform breach reportedly exposed 27,000 records containing KYC data, user identities, and transaction histories  

  • Pension funds were impacted through credential reuse attacks that enabled unauthorized account access and financial losses  

  • Energy and logistics systems were affected by leaks involving millions of operational files from petroleum distribution and internal logistics networks  

Across these incidents, one pattern stands out: attackers are extracting structured, high-value data sets that can be reused, recombined, and resold. 

Why Australia Is in the Crosshairs

The increase in targeting can be explained by several structural factors: 

First, ransomware and data extortion groups find Australian companies appealing because they are very data-driven and technologically advanced. 

Second, systemic exposure is increased by reliance on outside service providers. One provider's security flaws can spread throughout large ecosystems. 

Third, the cost of starting large-scale campaigns is being reduced by attackers using sophisticated tools, such as automation and AI-assisted phishing. 

Lastly, Australia's widespread use of digital technology raises the attack surface and data accessibility. 

Defensive Shifts Required for 2026

Organizations are being forced to adopt intelligence-driven security solutions due to the shifting threat landscape. 

Risk-based vulnerability management, which concentrates remedial efforts on actively exploited vulnerabilities rather than theoretical problems, is becoming important. 

To protect against credential-based assaults, which are commonly employed in supply chain and ransomware incursions, multi-factor authentication is becoming a standard requirement. 

To identify vulnerability outside of their immediate surroundings, organizations are also improving their supply chain risk assessments. 

To combat contemporary threats like AI-generated phishing, deepfake impersonation, and automated social engineering efforts, security awareness programs are changing. 

Behavioral analytics and AI-driven detection systems are becoming more and more important at the infrastructure level to find anomalies that conventional monitoring tools overlook. 

Lastly, as businesses shift from implicit trust to continuous verification models, Zero Trust architectures are becoming more popular. 

The Role of Intelligence-Led Defense Platforms

Platforms such as those developed by Cyble reflect a broader shift toward real-time, intelligence-led security operations. Their approach combines dark web monitoring, external attack surface visibility, vulnerability intelligence, and endpoint compromise detection. 

While such systems vary in implementation, the broader trend is clear: security teams are moving away from static defense models toward continuous monitoring of external threat ecosystems. 

This shift is especially relevant in environments where stolen data is rapidly aggregated and resold, making early detection of exposure more valuable than post-incident response. 

Bundling Is the New Exposure Multiplier

The 48% increase in Australian data breaches highlights a major shift in cybercrime operations. Stolen data is no longer traded in isolation — cybercriminals are bundling, repackaging, and reselling Australian dark web data across larger underground ecosystems, increasing exposure for multiple organizations at once.

For the upcoming years, organizations must focus not only on preventing breaches but also on understanding how stolen data is reused and monetized after exfiltration. With AI-native threat intelligence, dark web monitoring, and attack surface management, Cyble helps organizations identify exposed data, detect emerging threats, and strengthen cyber resilience.

Want to see the intelligence behind the data in this report or learn how Cyble can help protect your organization?

Schedule a personalized demo with Cyble today.

The post Why Australian Dark Web Data Is Now Being Sold in Bundles — and What It Means for Organizational Exposure in 2026 appeared first on Cyble.
Third-Party Breaches Without Breaches: How Attackers Use Trusted Access to Bypass US Enterprise Defenses

supply chain attack

The modern enterprise is no longer breached in the traditional sense. Firewalls remain intact; endpoints appear compliant, and credentials are often never “stolen” in the usual way. Yet attackers still get in—and stay in. The difference lies in how trust is being weaponized.  

Threat actors are executing what looks like a supply chain attack without ever touching the actual supply chain infrastructure. Instead, they exploit the implicit trust organizations place in browsers, third-party services, and user behavior. 

This shift represents a quiet but dangerous evolution in supply chain cybersecurity. It’s less about breaking systems and more about bending them, using legitimate access paths to bypass defenses that were designed to stop intrusion, not misuse. 

The Rise of “Invisible” Supply Chain Attacks 

Traditional software supply chain attack scenarios often involve tampering with code libraries, compromising vendors, or injecting malicious updates. Those risks still exist, but attackers are now pursuing a lighter, faster approach: manipulating user-facing workflows that rely on trusted platforms. 

In recent campaigns, phishing pages masquerade as routine services—identity verification tools, account recovery portals, or internal workflows. What makes these attacks stand out is not just the deception, but the permissions they request. Instead of asking for passwords, they request access to cameras, microphones, and device-level metadata. 

This tactic transforms a simple phishing attempt into a sophisticated supply chain attack example—one where the “chain” is not software distribution, but user trusts in familiar digital processes. 

Once permissions are granted, the attack doesn’t need to escalate privileges. It already has them. 

When Browsers Become Data Exfiltration Tools 

Modern browsers are powerful. They support APIs for video capture, audio recording, geolocation, and device fingerprinting. These capabilities are designed for legitimate applications—but in the wrong hands, they become surveillance tools. 

Attackers embed scripts within phishing pages that activate these features immediately after permission is granted. Within seconds, they can: 

  • Capture images and short video clips from the user’s camera  

  • Record audio through the microphone  

  • Collect device details such as OS, browser version, and memory  

  • Approximate location and network characteristics  

This isn’t brute-force hacking. It’s precision harvesting. 

The data is then quietly transmitted to attacker-controlled systems, often using simple channels like messaging bots. There’s no need for complex infrastructure, which makes detection even harder. 

From a supply chain cybersecurity perspective, this is particularly concerning. The browser—arguably one of the most trusted components in enterprise environments—becomes the weakest link. 

QR Codes and the Expansion of the Attack Surface 

Another variation of this evolving threat involves QR codes embedded in seemingly legitimate documents. This technique, often called “quishing,” shifts the attack from desktops to mobile devices. 

An employee receives a polished PDF—perhaps an HR document or compliance guide. It looks authentic, reads well, and builds credibility. Then, at the end, it asks the user to scan a QR code for more information. 

That scan leads to a phishing site. 

Because QR codes obscure the underlying URL, they bypass many traditional email filters. On mobile devices, where users are less likely to scrutinize links, the success rate increases dramatically. 

This approach represents another subtle supply chain attack example: attackers are exploiting trusted communication formats—PDFs, QR codes, and mobile workflows—to deliver malicious payloads without triggering alarms. 

Adversary-in-the-Middle: The New Credential Theft 

Credential harvesting has also evolved. Instead of simply collecting usernames and passwords, attackers now position themselves between the user and the legitimate service. 

This adversary-in-the-middle (AITM) technique allows them to intercept: 

  • Login credentials  

  • Multi-factor authentication (MFA) codes  

  • Session tokens  

In effect, they don’t just log in—they become the user. 

This is particularly damaging in enterprise environments where MFA was once considered a strong defense. It highlights a critical gap in how to prevent supply chain attacks: focusing solely on authentication is no longer enough. Continuous verification and behavioral monitoring are now essential. 

Why These Attacks Work 

What makes these campaigns effective isn’t just technical sophistication—it’s psychological alignment. Every step mimics something users already trust: 

  • Identity verification flows  

  • Corporate documents  

  • QR-based access to resources  

  • Familiar login interfaces  

Attackers are not introducing new behaviors; they are blending into existing ones. 

This is why traditional defenses struggle. Security tools are designed to detect anomalies, but these attacks look normal—because they are built on legitimate features. 

Rethinking Defense: From Perimeter to Context 

Defending against this new class of software supply chain attack requires a shift in mindset. Organizations must move beyond perimeter-based security and adopt a context-driven approach. 

Key strategies include: 

  • Strict permission governance: Limit browser access to sensitive hardware unless necessary  

  • Behavioral monitoring: Detect unusual patterns in device usage and data access  

  • Zero Trust architecture: Continuously verify users, devices, and sessions  

  • User awareness: Train employees to question permission requests, not just links  

Understanding how to prevent supply chain attacks now means recognizing that the “supply chain” includes user interactions, browser capabilities, and third-party workflows—not just software dependencies. 

Strengthening Endpoint Resilience with Cyble Titan 

https://www.youtube.com/watch?v=NS7XHdNpkyE

As attackers exploit trusted access points, endpoint visibility becomes critical. This is where platforms like Cyble Titan play a strategic role. 

Cyble Titan is designed to go beyond traditional endpoint protection. It brings together real-time telemetry, threat intelligence, and automated response into a unified platform. Rather than relying on static rules, it continuously analyzes behavior across endpoints, detecting subtle anomalies that indicate misuse of legitimate tools. 

Key strengths include: 

  • Real-time visibility: Deep insights into processes, file activity, and user behavior  

  • Intelligence-driven detection: Integration with threat intelligence for contextual awareness  

  • Automated response: Rapid containment to reduce attacker dwell time  

  • Cross-platform coverage: Coverage for environments across Windows, Linux, and macOS  

In the context of supply chain cybersecurity, this level of visibility is essential. When attacks don’t “break in” but instead operate within trusted boundaries, detection depends on understanding what shouldn’t be happening, even if it looks normal on the surface. 

Trust Is the New Attack Surface 

The definition of a breach is changing. It’s no longer about unauthorized access—it’s about unauthorized use of authorized access. 

These emerging supply chain attack examples demonstrate that attackers are adapting faster than traditional defenses. They are leveraging trust, not bypassing it. And that makes them harder to detect, harder to prevent, and potentially more damaging. 

Organizations that want to stay ahead must rethink how to prevent supply chain attacks. That means focusing on context, behavior, and continuous verification—not just barriers. 

Ready to see how modern endpoint security can close these gaps? Explore Cyble Titan and experience a more intelligent approach to defending against today’s most deceptive threats.  

Request a demo and evaluate how real-time visibility and AI-driven detection can strengthen your security posture from the inside out. 

The post Third-Party Breaches Without Breaches: How Attackers Use Trusted Access to Bypass US Enterprise Defenses appeared first on Cyble.

💾

Enjoy the videos and music you love, upload original content, and share it all with friends, family, and the world on YouTube.

Threat Landscape March 2026: Ransomware Dominance, Access Brokers, Data Leaks, and Critical Exploitation Trends

Monthly Threat Landscape, March 2026,

Cyble Research & Intelligence Labs (CRIL) in its monthly threat landscape analysis observed a highly active threat environment throughout March 2026, shaped by large-scale ransomware campaigns, persistent data breach activity, growing initial access brokerage markets, and exploitation of critical vulnerabilities affecting widely deployed enterprise systems.

Threat actors continued to prioritize financial extortion, credential access, and operational disruption, while increasingly targeting sectors rich in sensitive data or dependent on business continuity.

Quick Summary

Key threat trends identified during March 2026 include:

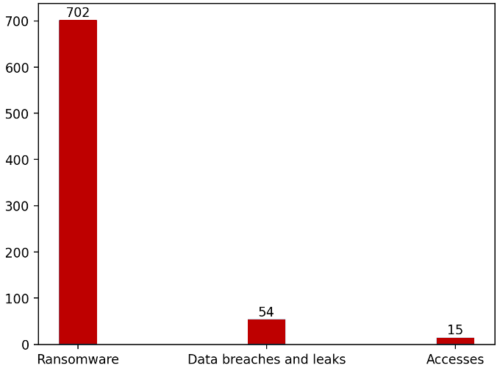
  • 702 ransomware attacks recorded globally.
  • 54 major data breach and leak incidents observed.
  • 20 compromised access sale listings tracked across cybercrime forums.
  • High concentration of attacks against Professional Services, Manufacturing, Retail, and Government sectors.
  • Continued exploitation of vulnerabilities listed in CISA’s Known Exploited Vulnerabilities (KEV) catalog.

Fig 1. Cyber incidents recorded in March 2026 (Data Source: Cyble Blaze AI)

These trends indicate a mature cybercriminal ecosystem where access brokers, ransomware operators, and data leak actors increasingly operate in parallel.

Ransomware Activity Remained the Dominant Threat

CRIL recorded 702 ransomware attacks worldwide in March 2026, reflecting sustained aggression from both established groups and emerging operators.

Top Ransomware Groups

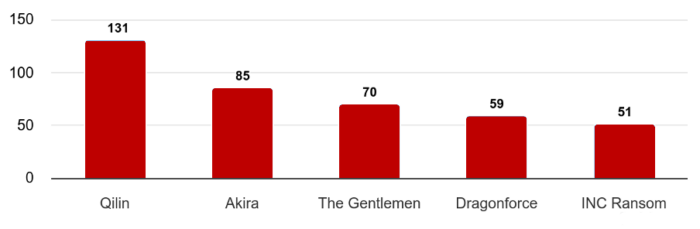
Qilin, Akira, The Gentlemen, Dragonforce, and INC Ransom were the top five most active ransomware actors in March 2026.

Monthly Threat Landscape, Top Ransomware Actors
Fig 2. Top five ransomware actors (Data Source: Cyble Blaze AI)

Together, the top five groups accounted for more than 56% of observed ransomware activity, highlighting strong operational scale and affiliate ecosystems.

Most Targeted Industries

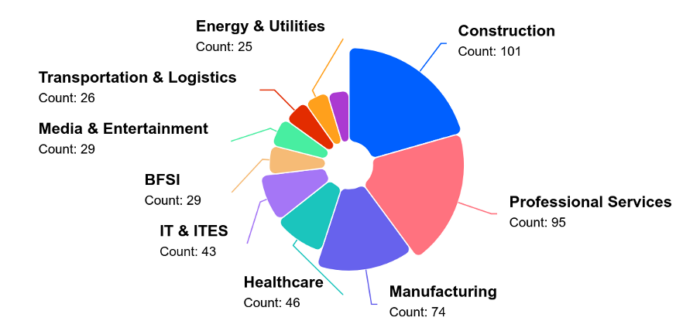
Construction, Professional Services, Manufacturing, Healthcare, and Energy & Utilities were the most targeted sectors by ransomware actors in March 2026.

Monthly Threat Landscape
Fig 3. Top 10 industry-wise attacks by ransomware actors (Data Source: Cyble Blaze AI)

Threat actors continued using data theft + operational disruption as dual-extortion pressure tactics.

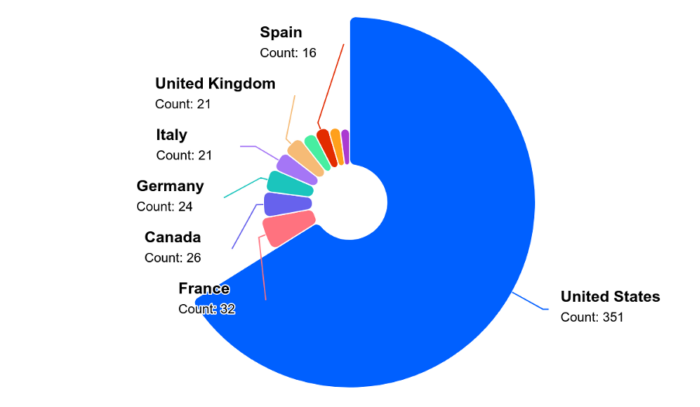
And when it came to country-wise split-up, the United States remained the focal point amid the ongoing geopolitical issues with Iran.

Monthly Threat Landscape
Fig 4. Top 10 country-wise attacks by ransomware actors (Data Source: Cyble Blaze AI)

Compromised Access Market Expanded

CRIL tracked 20 distinct incidents involving the sale of unauthorized network access on underground forums.

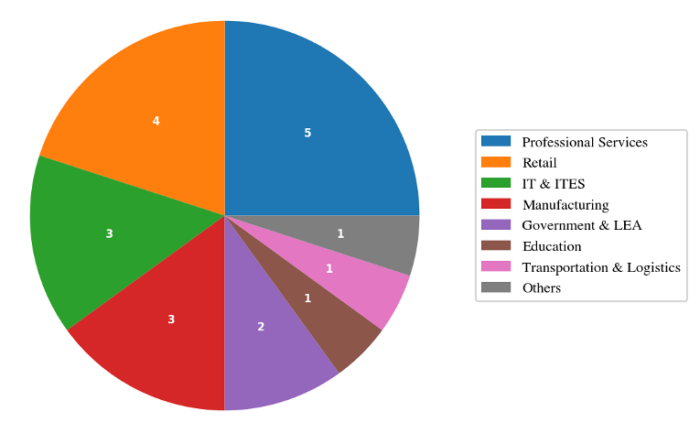
Most Targeted Sectors

  • Professional Services – 25%
  • Retail – 20%
  • IT & ITES
  • Manufacturing

Monthly Threat Landscape
Fig 5. Sector-wise compromised accesses recorded (Data Source: Cyble Blaze AI)

Leading Access Sellers

A small group of actors dominated this market:

  • vexin
  • holyduxy
  • algoyim

These three actors were responsible for over 55% of observed access listings.

This reinforces the role of access brokers as upstream enablers for ransomware, espionage, and fraud operations.

Data Breaches and Leak Markets Remained Active

CRIL observed 54 significant breach and leak incidents during the month.

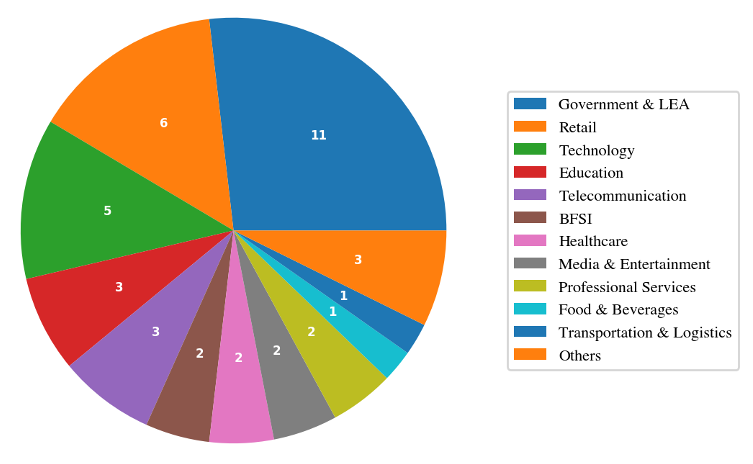
Most Targeted Sectors

  • Government & Law Enforcement
  • Retail
  • Technology

Monthly Threat Landscape
Fig 6. Sector-wise data breaches and leaks recorded (Data Source: Cyble Blaze AI)

Notable Incidents

Hospitality Holdings – TA Claimed 5TB Leak

Threat actor “nightly” claimed theft of over 5TB of data, including biometric records, CCTV footage, and financial documents.

South African Government Dataset for Sale

Threat actor XP95 advertised 3.8TB of allegedly stolen provincial government data.

Travel Data Leak

Over 95,000 travel-related records were reportedly exposed, including passports and payment data.

Exploited Vulnerabilities Accelerated Risk

March also saw active exploitation of critical vulnerabilities affecting enterprise technologies.

Notable KEV-listed vulnerabilities included:

  • CVE-2026-20131 – Cisco Secure Firewall Management Center
  • CVE-2025-53521 – F5 BIG-IP APM
  • CVE-2026-20963 – Microsoft SharePoint Server
  • CVE-2026-33017 – Langflow AI
  • CVE-2021-22681 – Rockwell Automation ICS

Key Trend

Attackers exploited both:

  • Newly disclosed zero-days
  • Legacy vulnerabilities from prior years

This showcases widespread failures in patch management and exposure reduction.

Emerging Strategic Threat Developments

AI-Augmented Offensive Operations

Threat actors reportedly used CyberStrikeAI, an open-source AI-native security testing framework, in attacks against Fortinet FortiGate devices across 55 countries, compromising more than 600 appliances.

Supply Chain Malware via npm

North Korean actors were linked to 26 malicious npm packages distributing RAT malware through Pastebin/Vercel-based infrastructure.

Geopolitical Cyber Risk

Iran-linked cyber operations were assessed as likely to increase following regional tensions, with potential ransomware and hacktivist targeting across the Middle East.

Industries Facing Highest Risk

Based on March activity, organizations in the following sectors faced elevated risk:

  • Professional Services
  • Government
  • Manufacturing
  • Retail
  • Healthcare
  • Critical Infrastructure
  • Transportation & Logistics

These sectors combine valuable data, high uptime requirements, or complex supply chains.

Conclusion

The March 2026 threat landscape was defined by scale, specialization, and speed.

Threat actors increasingly leveraged:

  • Access brokerage markets
  • High-volume ransomware operations
  • Large-scale data theft
  • Rapid weaponization of critical vulnerabilities
  • AI-enhanced offensive tooling

The combination of concentrated criminal ecosystems and widespread enterprise exposure creates a sustained high-risk environment for organizations globally.

Key Recommendations

  • Prioritize remediation of KEV-listed vulnerabilities
  • Strengthen identity security and MFA across remote access platforms
  • Monitor for exposed credentials and access sale activity
  • Segment critical networks to reduce lateral movement
  • Conduct tabletop exercises for ransomware response
  • Improve backup resilience and recovery testing
  • Monitor software supply chain ecosystems
  • Expand threat intelligence coverage across dark web and leak forums

Cyble’s threat intelligence, ransomware monitoring, vulnerability intelligence, and attack surface management solutions help organizations proactively identify risks, prioritize remediation, and defend against evolving global threats.

Book your demo now to see it in action!!!

The post Threat Landscape March 2026: Ransomware Dominance, Access Brokers, Data Leaks, and Critical Exploitation Trends appeared first on Cyble.

Reducing ransomware recovery costs in education

2024 continued the trend of ransomware attacks in the education sector making headlines. The year opened with Freehold Township School District in New Jersey canceling classes due to a ransomware attack. Students at New Mexico Highlands University missed classes for several days while employees experienced disruption of their paychecks after a ransomware attack. The attack on the Alabama Department of Education served as a reminder that all school systems are vulnerable.

Ransomware attacks in education decreasing

The year closes with some positive news about ransomware in the education sector. Sophos State of Ransomware in Education 2024 found that ransomware attacks on educational institutions decreased in 2024. Attacks on higher-education institutions dropped from 79% reporting attacks in 2023 to 66% in 2024. Lower education saw a similar decrease, from 80% in 2023 to 63% in 2024. However, the attack rates for both are still higher than the global cross-sector average of 59%.

Ransomware affects education quality

Not surprisingly, a recent study also found that students are impacted by ransomware attacks on the education sector. A study from Action1 found that the majority (64%) of education IT workers report that ransomware impacts education quality. Researchers found the reasons for the attacks are multifold, including that 44% devote only 10% of their IT budget to cybersecurity and the majority of schools (78%) do not employ cybersecurity specialists.

In an NPR article, Noelle Ellerson Ng with the School Superintendents Association said that the reason for targeting the education sector is that schools are often low-hanging fruit. Additionally, she points to the fact that school systems, which collect a lot of valuable data from both students and employees, often are the largest employers in a community.

“That makes it very, very ripe,” says Ng. “And then you layer on the fact that [the data] is so sensitive and so longitudinal and so personal, and there’s a huge vulnerability.”

Read the Cost of a Data Breach Report

Reducing cyber risks in the education sector

Even with the decline, schools should continue to focus on reducing their vulnerabilities.

Here are some ways schools can reduce ransomware risk:

  • Install antivirus and anti-malware software on all devices. Be sure to also include tablets and phones. Make sure that updates and patches are installed on a timely basis.
  • Provide training to all employees and students. Teach good cybersecurity practices, including choosing strong passwords and how to avoid being a victim of phishing. Continually send reminders on not clicking on unknown links or downloading suspicious files.
  • Install filtering software. By filtering out potentially malicious links and files, you can reduce the chance of students or employees falling victim to a phishing scheme.
  • Use multi-factor authentication (MFA). Because ransomware attacks can start with unauthorized access, educational organizations should take extra steps to ensure that every user who logs in is who they claim to be. With MFA, users must use email, text or token in addition to a password, adding an extra layer of security.

Recovery costs have increased

While the decrease in attacks was positive, Sophos’ report found a troubling trend — the recovery costs have more than doubled for ransomware attacks in education. Lower-education organizations reported a mean cost of $3.76 million to recover from a ransomware attack in 2024, compared to $1.59 million. Researchers found the increase even higher in higher education, more than four times higher from 2023 to 2024 ($1.06 million to $4.02 million).

Here are ways to reduce recovery costs:

  • Back up your data. In addition to backing up data in real-time, educational institutions should take precautions to secure the backups, such as by using air-gapped backups as well as immutable backups that cannot be erased. Sophos found that costs for lower-education institutions whose backups were compromised were five times higher ($3 million versus $562,500) than those who had a backup to revert to.
  • Segment the network. When a ransomware attack happens on a segmented network, cyber criminals can encrypt only the portion of the network that they accessed. By reducing the amount of data breached and the systems impacted, schools can significantly reduce recovery time and costs.
  • Create an incident response plan. Often, the recovery is extended due to schools not containing the ransomware quickly enough. Additionally, business disruption also adds to the recovery time. With an incident response plan, employees know exactly what to do when a ransomware attack occurs by including the four fundamentals of a response plan — planning, detection, recovery and post-incident actions.

Propensity for paying ransom has increased

Recovery costs are also increasing due to the changes in the ransom payment patterns and amounts. When an educational organization pays the ransom to gain access to their data, that exponentially increases the recovery costs.

The Sophos Report found that the decision to pay the ransom has increased in both higher and lower education. In 2023, 56% of educational organizations attacked by ransomware paid the ransom, compared with 67% in 2024. The number of higher-education institutions paying the ransom also increased from 47% to 62%.

Additionally, the amount of the ransom has increased, which also adds to the rising recovery costs. The average ransom in lower education was $3.9 million, with 44% of demands of more than $5 million. Higher education demands also increased to $4.4 million. Ransoms in critical infrastructure sectors, such as education, tend to be higher due to the urgency of restoring operations as well as the sensitive nature of the data. Additionally, cyber criminals increasingly use double extortion, demanding a ransom to unencrypt the data and then a second ransom to not make the data public, which increases recovery costs.

The future of ransomware attacks in education

While the decrease in attacks is positive, educational organizations must pay attention to the rising recovery costs. Because every dollar spent in education towards recovering from an attack means money is not available for learning, the costs of ransomware recovery are even more impactful than other sectors. By proactively taking steps to both reduce risks and reduce recovery costs, educational organizations can keep their focus on what matters most — educating students.

The post Reducing ransomware recovery costs in education appeared first on Security Intelligence.

Router reality check: 86% of default passwords have never been changed

Misconfigurations remain a popular compromise point — and routers are leading the way.

According to recent survey data, 86% of respondents have never changed their router admin password, and 52% have never adjusted any factory settings. This puts attackers in the perfect position to compromise enterprise networks. Why put the time and effort into creating phishing emails and stealing staff data when supposedly secure devices can be accessed using “admin” and “password” as credentials?

It’s time for a router reality check.

Rising router risks

Routers allow multiple devices to use the same internet connection. They accomplish this goal by directing traffic — internal devices are routed along the most efficient path to outside-facing services, and incoming data is sent to the appropriate endpoint.

If attackers manage to compromise routers, they can control both what comes out of and what goes into your network. This introduces risks such as:

The nature of router attacks also makes them hard to detect. This is because cyber criminals aren’t forcing their way into routers or taking circuitous routes to evade security defenses. Instead, they’re taking advantage of overlooked weak spots to access routers directly, which means they aren’t raising red flags.

Consider a router with “admin” as the login and no password. A few simple guesses get attackers into router settings without triggering a security response since they haven’t breached a network service or compromised an application. Instead, they’ve accessed routers the same way as staff and IT teams.

Explore IBM Instana

Exploring the defensive disconnect

Companies recognize the need for robust cybersecurity. According to Gartner, spending on information security will grow 15% in 2025 to reach $212 billion. Common investment areas include endpoint protection platforms (EPPs), endpoint detection and response (EDR) and the integration of generative AI (gen AI). Routers, however, are often overlooked.

For example, 89% of respondents have never updated their router firmware. The same number have never changed their default network name, and 72% have never changed their Wi-Fi password.

This is problematic. A recent report found that popular OT/IoT router firmware images were outdated and contained exploitable N-day vulnerabilities. The report found that, on average, open-source components were more than five years old and were four years behind the latest release.

As noted by GovTech, meanwhile, an attack on a Pittsburgh-area water authority succeeded in part because the default password to its network was “1111”. Other common passwords include “password” and “123456;” in some cases, routers have no passwords. All attackers need is the login credential — which is often “admin” — and they have full access to router functions.

Even more telling is the fact that router security is getting worse, not better. Consider that in 2022, 48% of respondents said they had not adjusted their router settings, and 16% had never changed the admin password. In 2024, over 50% of routers were still running on factory settings, and just 14% had changed their password.

By spending more on security tools but not changing default configurations or updating router firmware, businesses are closing the doors but leaving the windows wide open.

Minimizing misconfiguration mistakes

So, how do companies minimize the risk of misconfiguration mistakes?

It starts with the basics: Change passwords regularly, update firmware and ensure that routers aren’t left on factory settings. Simple? Absolutely. Common? As survey data indicates, not so much.

In part, the disconnect between router risks and security realities stems from the sheer volume of cyberattacks. For example, 2023 saw 94% of companies hit by phishing attacks, and as noted by the IBM Cost of a Data Breach Report 2024, the average cost of a data breach is now $4.88 million, up 10% from 2023 and the highest ever reported. This puts cybersecurity teams on the defensive and on high alert for common attack vectors such as phishing, smishing and the use of “shadow IT” applications that haven’t been vetted or approved.

As a result, routers can slip through the cracks. The first step in solving this problem is creating a regular update schedule. Every four to six months, schedule a router review — put it in a shared calendar, and make sure all security staff know it’s going to happen. When the designated day comes, update firmware where possible and change login and password details. It’s also worth establishing a weekly schedule to review router traffic for any odd behaviors or unexpected login requests.

Shoring up security

While basic cyber hygiene helps lower the risk of router attacks, shoring up security requires a more in-depth approach.

The first step is finding and securing every router on your network. Given the increasingly complex nature of enterprise networks, the easiest way to accomplish this goal is by using automation. Solutions such as IBM SevOne Automated Network Observability provide pre-built workflow templates for IT teams to identify connected devices, collect performance data and make data-driven decisions.

Companies also need to consider what happens when a router compromise occurs. Despite best efforts by security teams, the growing number of end points means it’s only a matter of time until attackers manage to find unprotected routers or circumvent existing defenses.

Effective response requires effective incident management. Solutions such as IBM Instana offer full-stack visibility, one-second granularity and three seconds to notify, giving teams the information they need when they need it to reduce security risks.

Bottom line? Failure to monitor and update router settings can open the door to compromise. To solve the problem, teams need a router reality check. By combining security hygiene best practices with intelligent automation solutions, enterprises can keep unauthorized users where they belong: 0utside protected networks.

The rising risk of router attacks, paired with a growing list of unreasonable expectations, creates complex challenges for security teams. The solution? Unreasonable observability. Learn more on IBM Instana and how it can help.

The post Router reality check: 86% of default passwords have never been changed appeared first on Security Intelligence.

CISA’s cyber incident reporting portal: Progress and future plans

On August 29, 2024, CISA announced the launch of a new cyber-incident Reporting Portal, part of the new CISA Services Portal.

“The Incident Reporting Portal enables entities and individuals reporting cyber incidents to create unique accounts, save reports and return to submit later, and eliminate the repetitive nature of inputting routine information such as contact information,” says Lauren Boas Hayes, Senior Advisor for Technology & Innovation, at CISA.

Shortly after the announcement, Security Intelligence reported on how the portal was designed and how it differs from other cyber incident reporting structures. We noted that CISA’s biggest advantage was its ability to assist the reporting organization with response and remediation.

“Any organization experiencing a cyberattack or incident should report it — for its own benefit and to help the broader community. CISA and our government partners have unique resources and tools to aid with response and recovery, but we can’t help if we don’t know about an incident,” said CISA Executive Assistant Director for Cybersecurity Jeff Greene in a formal statement covering the portal’s announcement.

Four months later

Since the announcement in August, a lot has happened. There was a presidential election, and a new administration will take charge on January 20. The current CISA director and other political appointees will step down. The agency’s future is uncertain as of this writing, particularly regarding who will oversee it and whether its functions will be divided across different federal departments. Still, it is expected that its work will continue.

Before these changes occur, we wanted to check in with CISA to follow up on the portal’s progress and what the future might look like.

Explore cybersecurity services

Long history of collecting cyber incident reports

CISA was first created in 2018, but federal agencies have collected cyber incident reports for decades.

“The launch of the Incident Reporting Portal is a significant step forward for CISA’s ability to collect operationally relevant data from reporters in a system which is more usable for reporters,” says Hayes. “The vision for the Incident Reporting Portal is for CISA’s Incident Reporting Portal to continue to enhance the functionality of the system to enable entities to share submitted reports with colleagues or clients to facilitate more effective third-party reporting, communicate directly with CISA, and access information and services relevant to the reporter.”

The portal is expected to make compliance with the Cyber Incident Reporting for Critical Infrastructure Act of 2022 easier. This act will “require CISA to coordinate with Federal partners and others on various cyber incident reporting and ransomware-related activities” across the 16 sectors, agencies and industries deemed “vital to the health, economy and security of the community or region.”

Hayes adds that while reporting under the Cyber Incident Reporting for Critical Infrastructure Act of 2022 will not be required until the Final Rule goes into effect, the agency encourages critical infrastructure owners and operators to voluntarily share information on cyber incidents prior to that date to help prevent other organizations from becoming victims of similar incidents.

“Sharing information allows us to work with our full breadth of partners to help prevent attackers from compromising other victims using the same techniques,” says Hayes.  “Sharing information can provide insight into the scale of an adversary’s campaign.”

Why reporting is vital to overall cybersecurity

While reporting cyber incidents to the portal is voluntary at the moment, all organizations are encouraged to share the information. If they feel the need, they can do so anonymously. As cyberattacks and nation-state threats become more sophisticated and increasingly target critical infrastructure industries, sharing this information with CISA allows the agency to help other organizations prepare for emerging threats and implement preventive measures before the damage is done.

“Isolating cyberattacks and preventing them in the future requires the coordination of many groups and organizations,” CISA explained. “By rapidly sharing critical information about attacks and vulnerabilities, the scope and magnitude of cyber events can be greatly decreased.”

And it isn’t just CISA that uses this information. According to the U.S. Government Accountability Office (GAO), 14 federal agencies are responsible for protecting critical infrastructure from cyberattacks, many in unexpected ways. For example, TSA, which handles airport security screening, is also responsible for safeguarding the country’s gasoline pipelines.

“Entities representing critical infrastructure owners and operators told us there are great benefits in getting information about threats from federal agencies,” the GAO reported.

What comes next

Despite a changing presidential administration, CISA is moving forward. It is planning a future designed to keep the critical infrastructure safe from cyber threats, which, in turn, will provide a layer of protection for the nation’s citizens and businesses.

“Sharing information allows us to work with our full breadth of partners so that the attackers can’t use the same techniques on other victims and can provide insight into the scale of an adversary’s campaign,” Jeff Greene was quoted in Federal News Network. “CISA is excited to make available our new portal with improved functionality and features for cyber reporting.”

As for the Incident Reporting Portal’s future, Hayes says, “In the future, we are planning to implement additional features that will take time to develop and incorporate user feedback. Our user experience team is actively working to get feedback on how we can improve the system over time.”

The post CISA’s cyber incident reporting portal: Progress and future plans appeared first on Security Intelligence.

Ransomware attack on Rhode Island health system exposes data of hundreds of thousands

Rhode Island is grappling with the fallout of a significant ransomware attack that has compromised the personal information of hundreds of thousands of residents enrolled in the state’s health and social services programs. Officials confirmed the attack on the RIBridges system—the state’s central platform for benefits like Medicaid and SNAP—after hackers infiltrated the system on December 5, planting malicious software and threatening to release sensitive data unless a ransom is paid.

Governor Dan McKee, addressing the media, called the attack “alarming” and urged residents to take immediate precautions to protect their information. Compromised data includes Social Security numbers, banking details, addresses and dates of birth. “This breach is a stark reminder of the vulnerabilities in government IT systems,” McKee said. “We are working with Deloitte and law enforcement to contain the damage and restore public trust.”

Timeline of the attack

The cyberattack began on December 5, when Deloitte, the developer and maintainer of RIBridges, alerted state officials to suspicious activity. Initially, it was unclear whether sensitive data had been accessed. Over the following days, Deloitte implemented additional security measures while investigating the breach.

On December 10, hackers provided a screenshot of file folders as proof of their access, prompting Deloitte to confirm that the RIBridges system had been compromised. Further analysis revealed a high probability that the stolen files contained personally identifiable information (PII). By December 13, Deloitte identified malicious code within the system, leading the state to shut down RIBridges to mitigate further damage and begin remediation.

How the attackers gained access

While the exact infiltration method remains under investigation, early findings suggest that the attackers exploited vulnerabilities in the system’s architecture, likely through phishing emails targeting administrative accounts or unpatched software weaknesses. The malware deployed by the cyber criminals enabled unauthorized access and allowed the attackers to exfiltrate data unnoticed for several days.

This breach has highlighted persistent security challenges in government IT systems, which often struggle to keep pace with evolving cyber threats. RIBridges, developed in 2016 under the Unified Health Infrastructure Project (UHIP), has faced years of technical and operational issues, including public criticism for its vulnerabilities.

Impact on residents and state operations

The breach has far-reaching implications for Rhode Island’s residents and government services. Programs impacted include Medicaid, SNAP, Temporary Assistance for Needy Families (TANF) and health insurance purchased through HealthSource RI. The RIBridges system’s offline status has forced the state to resort to manual processing for December benefits and January payments, creating delays and disruptions for thousands of families.

State officials have contracted Experian to provide free credit monitoring to affected residents and set up a dedicated call center to offer guidance. McKee also urged residents to take proactive steps, including freezing their credit, updating passwords and enabling multi-factor authentication.

Comparisons to other state-level ransomware attacks

Rhode Island is not the first state to be targeted by a ransomware attack on its central systems. In 2019, Texas faced a coordinated ransomware assault that impacted 22 local entities, including state-run agencies, though its centralized IT infrastructure mitigated the spread. Similarly, Colorado’s Department of Transportation suffered a ransomware attack in 2018, which disrupted operations and required weeks to fully resolve.

These incidents underscore the growing threat of ransomware to state governments. Unlike attacks on local municipalities, state-level breaches can potentially disrupt critical systems serving millions of residents, amplifying the stakes for government cybersecurity teams.

What comes next?

The FBI and other federal agencies are assisting in the investigation, while Deloitte works to remediate the vulnerabilities and restore RIBridges. Meanwhile, negotiations between the state’s representatives and the cyber criminals are ongoing, though officials have not disclosed the ransom amount or whether they intend to pay it.

“That conversation is going on directly with Deloitte and the cyber criminals. That’s how this process works, we’re learning a little bit about it,” McKee said. “But we’re being notified of the progress on it, and ultimately, it does end up with that decision with me.”

The attack has reignited calls for stronger cybersecurity measures in government IT systems. Experts recommend adopting zero trust security models, conducting regular vulnerability assessments and increasing investments in cybersecurity infrastructure to prevent future breaches.

“This breach is a wake-up call,” says Brian Tardiff, Rhode Island’s Chief Digital Officer. “We need to ensure that our systems are resilient against increasingly sophisticated cyber threats. The stakes are too high to do otherwise.”

To learn how IBM X-Force can help you with anything regarding cybersecurity including incident response, threat intelligence, or offensive security services schedule a meeting here.

If you are experiencing cybersecurity issues or an incident, contact X-Force to help: US hotline 1-888-241-9812 | Global hotline (+001) 312-212-8034.

The post Ransomware attack on Rhode Island health system exposes data of hundreds of thousands appeared first on Security Intelligence.

2024 roundup: Top data breach stories and industry trends

With 2025 on the horizon, it’s important to reflect on the developments and various setbacks that happened in cybersecurity this past year. While there have been many improvements in security technologies and growing awareness of emerging cybersecurity threats, 2024 was also a hard reminder that the ongoing fight against cyber criminals is far from over.

We’ve summarized this past year’s top five data breach stories and industry trends, with key takeaways from each that organizations should note going into the following year.

Billions of US citizens have private data exposed

On April 8, 2024, one of the largest personal data breaches took place, leading to nearly 3 billion US citizens having their information leaked on the dark web. Even more shocking was that all of this information came from only one source — National Public Data, a background check and fraud prevention service located in Coral Springs, Florida.

The stolen information collected contained names, social security numbers, home addresses and known relatives, and was listed on the dark web for sale for $3.5 million. Many of the victims were still unaware of the breach several months later, leading to several class action lawsuits filed by a dozen U.S. states. National Public Data has since then filed for bankruptcy.

Third-party breaches impact top 48 energy companies

A SecurityScorecard report revealed this year that 90% of the world’s top energy companies experienced data breaches that stemmed from third-party breaches. Many of these attacks were a direct result of increased reliance on cloud services and third-party integration to manage networked systems.

It was confirmed that out of the 264 individual breaches linked to third-party compromises, the MOVEit vulnerability was one of the major reasons for the issues. With critical infrastructure organizations playing a significant role in the health and well-being of citizens, these types of breaches continue to threaten public safety. The energy sector as a whole has since begun implementing stricter vendor assessments, continuous system and threat monitoring solutions and more secure data transfer protocols.

Read the Cost of a Data Breach Report

Financial firms face the highest data breach costs since the pandemic

According to the IBM Cost of a Data Breach 2024 report, the financial sector has seen a surge in data breach costs since the pandemic, reaching an average of $6.08 million per incident. While various attack types account for this increase, IT failures and simple human error account for a significant portion of the problem.

While certain improvements have been made in threat detection and containment timelines, many financial firms still have an uphill battle to climb. Larger-scale financial service breaches are now estimated to reach hundreds of millions of dollars in damages, leading many organizations to invest more in comprehensive identity and access management (IAM) solutions, AI-powered security solutions and dedicated incident response teams.

Average data breach cost increases 10% year-over-year

The global average cost of data breaches jumped 10% year-over-year between 2023 and 2024, with the latest figure reaching an alarming $4.88 million. The number represented by this average is driven by a number of factors, including lost business revenues, recovery costs and regulatory fines.

Complicating this ongoing trend, 40% of breaches recorded now involve data spread across multiple public and cloud environments and on-premises systems. These larger digital footprints average over $5 million in recovery costs with an average containment timeline of 283 days. Encouragingly, organizations that leverage AI-driven security workflows are experiencing a significantly lower average of $2.2 million per breach, pointing to a positive trend in next-generation security measures.

50% of data breaches tied to security staffing shortages

The cybersecurity skills gap widened over the last few years, with 50% of organizations experiencing data breaches reporting that they stemmed from staffing shortages. Skills shortages are specific to a wide range of critical areas, including cloud security and incident response, data analysis and compliance expertise. Another growing need for these impacted organizations is proficiency in security information and event management (SIEM) tools and active threat hunting.

In an ongoing effort to fill the key personnel gaps, it’s now recommended that organizations put a stronger focus on upskilling their existing workforce. Modern businesses can also leverage professional soft skills such as good communication and adaptability to help supplement and strengthen their security teams.

Moving into 2025

The past year has shown that while modern cybersecurity tools and solutions provide protection against a broader range of threats, very few industries and organizations are immune to cyber crime’s evolving nature.

As we move into 2025, enterprises should prioritize a proactive approach to cybersecurity planning. This includes optimizing their access restriction policies when operating with both in-house and remote teams, working to address any critical staffing shortages, and creating a stronger culture of security awareness within their organization.

The post 2024 roundup: Top data breach stories and industry trends appeared first on Security Intelligence.

❌