Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published. Become a member and support our work here.
In September, CBS News obtained new images of the aftermath of attacks on US bases in the Middle East from active service members. One told the news channel: “This is major damage to our bases that hasn’t been communicated to the American public. “We’re standing there with our eyes closed getting punched in the face,” they added.
While reports have detailed how Iran used Russian intelligence, including satellite imagery, to identify US troops, ships and aircraft, Bellingcat found that publicly available mapping platforms also reveal detailed and potentially sensitive information about US military bases in the Middle East.
Google Maps and other online mapping services contain dozens of labels identifying facilities including headquarters, accommodation, gyms and fuel points. Publicly available photographs and videos, including material published by the US military, provide further details about how these facilities are used.
Experts told Bellingcat that such information could have helped inform Iranian targeting decisions by revealing where personnel gather and how bases operate. However, they cautioned that Iran would also have had access to other sources of intelligence. Reporting from Reuters earlier this year also highlighted how US officials believed commercially available location data was being used to target US troops in war zones.
The bases examined by Bellingcat are not secret and have operated for years in a region where US forces maintained a strong sense of security. Joseph Jarnecki, a research fellow at the Royal United Services Institute, said the US had been able to maintain aerial superiority and was understood to have significant air defence capabilities, but that Iran’s missile and drone campaign has undermined both assumptions.
Iranian strikes have damaged at least 20 US military sites across Qatar, Bahrain, the United Arab Emirates (UAE), Jordan, Kuwait, Iraq and Saudi Arabia since the conflict began in February this year.
Governments can request that Google blur or remove sensitive information from its services and Google publishes data on government requests for content removal.
Bellingcat contacted the US Department of Defense who asked us to reach out to CENTCOM about the details in this story. We also contacted Google. However, we did not receive responses to questions from these respondents before publication.
We examined four of the largest and most heavily affected US military installations by Iran’s missile and drone campaign: Camp Buehring and Camp Arifjan in Kuwait, Muwaffaq Salti Air Base in Jordan and Al Udeid Air Base in Qatar. At each one, we found publicly available Google Maps information providing details about facilities inside the bases and how they are used.
A map detailing four US bases that were attacked by Iran during 2026 conflict.
Camp Buehring
At Camp Buehring in Kuwait, Google Maps identifies what is labelled as the main headquarters building, as well as a gym and a self-help facility, all of which were among locations destroyed by recent Iranian strikes. In addition to Google Maps place markers there are dozens of reviews and user-uploaded photographs.
Left: Screengrab showing “Camp Beuhring Main HQ, Bldg. 100” Google Maps label. Right: Same building seen destroyed on satellite image published by Iran’s Tasnim news agency.
Bellingcat verified that this was a headquarters building by matching the flagpoles and layout in a photo published by the US military’s Defense Visual Information Distribution Service (DVIDS) showing soldiers posing in front of the building to the Google Maps satellite image.
Geolocation diagram using dvids photo to verify Google Maps Buehring main headquarters location, confirming the accuracy of the Google Maps place marker.
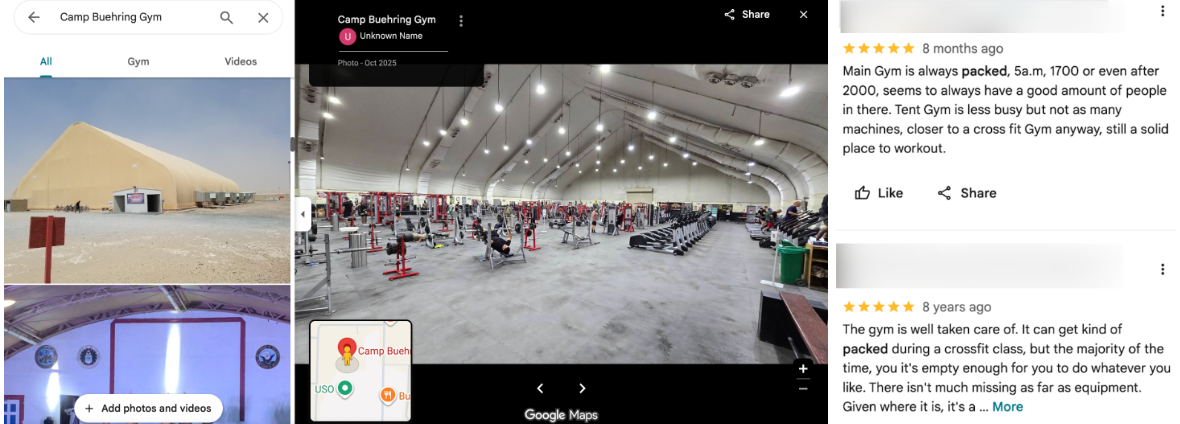
We also identified details about one of the camp’s gyms, including the building’s layout and roof structure, as well as Google reviews that indicate when it is busiest.
Left: Google Maps label showing “Camp Beuhring Gym” Right: Destroyed gym building on satellite image published by Iran’s Tasnim news agency on 6 April 2026.
Among the images published by CBS News in September was that of a heavily damaged tent-like structure with smoke rising from it. Bellingcat matched the location of this image to the above satellite imagery, verifying that it shows the gym building pinned on Google Maps.
Exclusive images released showing damage to E-3 Sentry AWACS aircraft at Prince Sultan Air Base in Saudi Arabia, plus damage to US military camps Arifjan and Buehring in Kuwait from Iranian strikes. Images sent to CBS by active US military personnel. (IRIB News) https://t.co/1urA44f4xz
Left: Google Maps shows images of the gym’s interior and exterior. Right: Google Maps reviews indicate when the gym is busy (names blurred by Bellingcat).
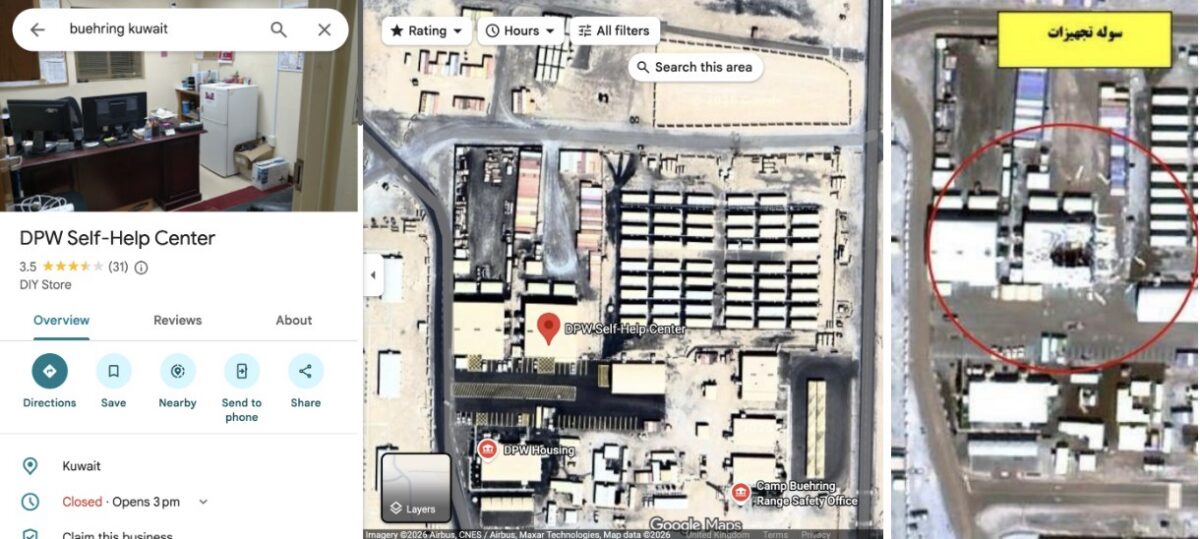
A building labeled on Google as “DPW Self-Help Center” was also destroyed at Camp Buehring. Its Google Maps listing includes opening hours, and a photo posted by a Master Sergeant in 2017 labeled “My office in Kuwait” shows the interior of an office. Some of the notices on the walls inside the office are legible, including what appears to be a floor plan.
Left: Google maps “DPW Self-Help Center” listing. Right: Same building seen destroyed on a satellite image published by Iran’s Tasnim news agency on April 6, 2026.
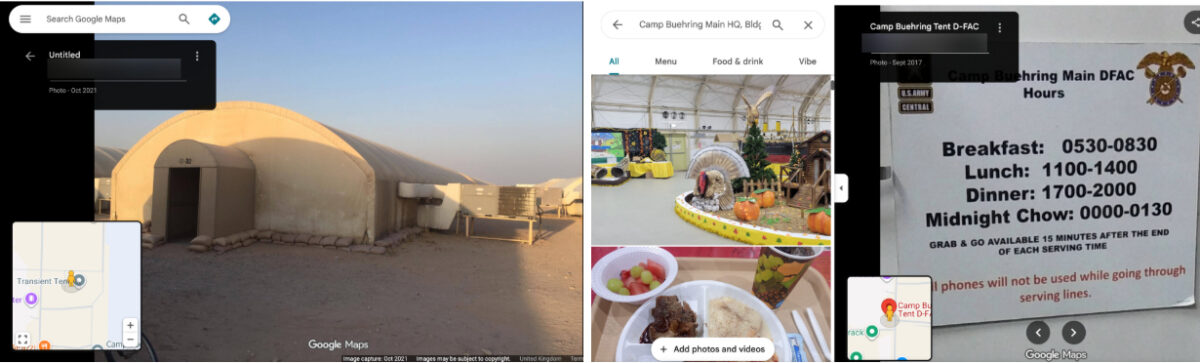
A Google Maps placemark labelled “Transient Tent” identifies a large accommodation area, while another review includes a ground-level photograph of one of the tents. The dining facility can also be seen from the inside, including information regarding meal times.
Left: Google image that appears to show an accommodation area. Right: Photos of the dining facility, including information on meal times (names blurred by Bellingcat).
William Goodhind of Contested Ground, a visual forensics consultancy that uses OSINT and satellite imagery to analyse military sites, said the information available on Google Maps could reveal “the camp’s layout, the division between secure and non-secure areas, confirms likely accommodation areas, and shows day/time periods of low and high activity.”
Camp Arifjan
A satellite image of Kuwait’s Camp Arifjan, captured by Planet on March 4, 2026 and published by the The Washington Post, shows damage to numerous structures at the base. Bellingcat compared the image with publicly available mapping data to identify two damaged facilities.
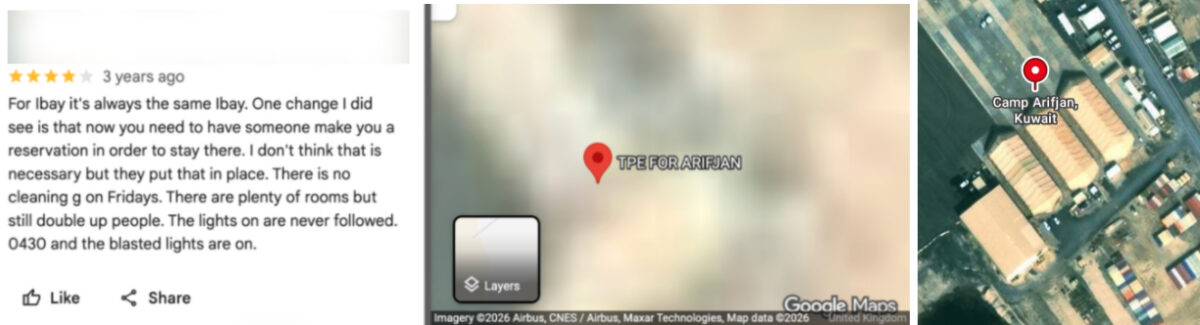
A Google Maps listing for a lodging facility labelled “TPE FOR ARIFJAN” includes a soldier’s review discussing room reservations, accommodation shortages and cleaning schedules, indicating that the building was used for military housing. Although Google’s satellite imagery of the base is blurred, the facility is visible in unblurred Bing Maps imagery using coordinates obtained from its Google Maps listing. The satellite image published by The Washington Post shows heavy damage to the facility.
Left and centre: Blurred Google Maps satellite image with Google review (name blurred by Bellingcat). Right: Unblurred Bing maps satellite image showing the same location.
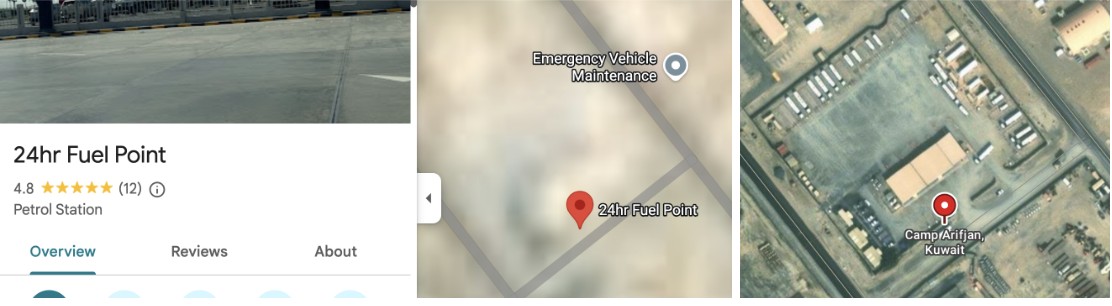
A “24hr Fuel Point” tagged on Google Maps is also blurred, but when the coordinates are copied and pasted into Bing Maps a clear satellite image of the fuel station appears. This facility is also seen destroyed on the satellite imagery published by The Washington Post.
Left and centre: Blurred Google Maps satellite image with Google review. Right: Unblurred Bing Maps satellite image.
Bellingcat contacted Microsoft to ask why the facility was not blurred out in the Bing Maps service. A spokesperson said: “When an entity requests removal from visibility on Bing Maps, we work through our process and act accordingly.”
Muwaffaq Salti Air Base
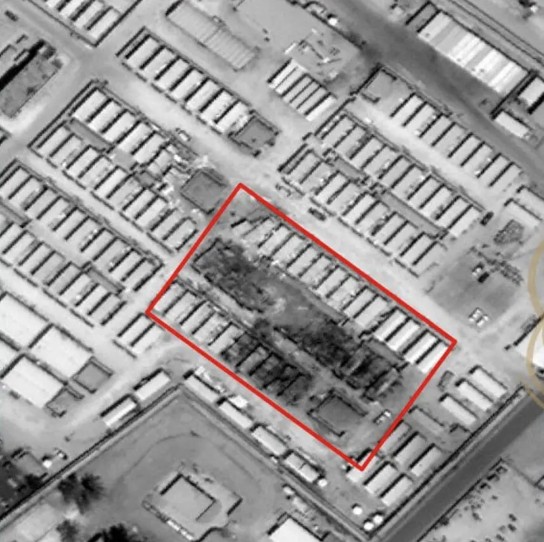
Three US service members were killed in Iranian ballistic missile strikes on Muwaffaq Salti Air Base in Jordan on July 17, 2026. The strikes appear to have caused extensive damage to a barracks in the north of the base, with satellite imagery released by Iran showing at least 20 structures destroyed.
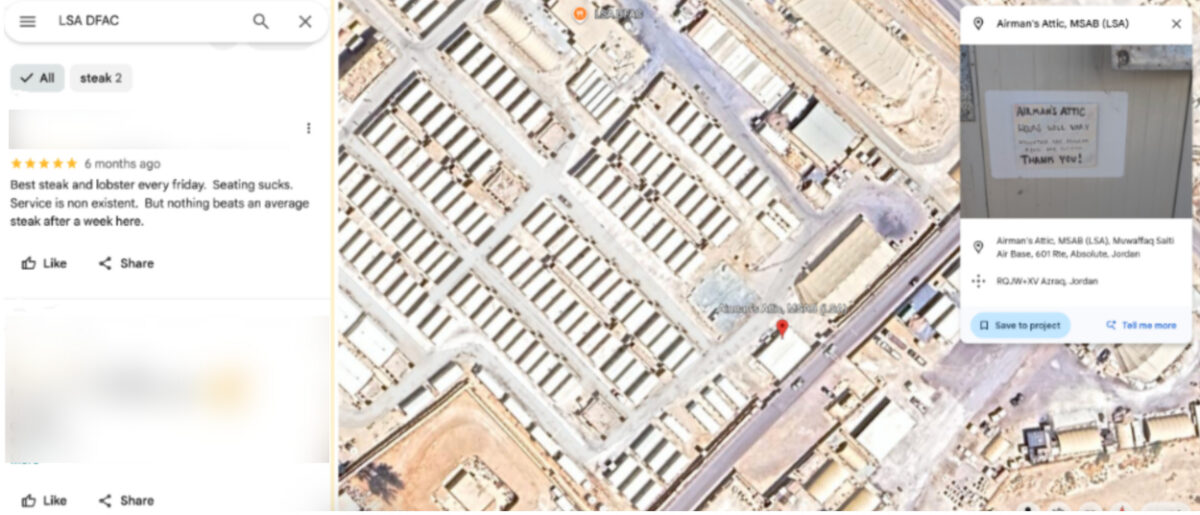
Less than 40 metres from the nearest destroyed structure, and within the same living quarters area, Google Maps reveals the location of an “Airman’s Attic”. These are volunteer-run thrift shops for US Air Force personnel.
A five-star review posted last year by a soldier includes a ground-level image of the facility, showing uniform drop-off points and fortifications along the perimeter. The listing provides information about the area’s use, while photographs of the shop’s exterior make it possible to match the satellite imagery to the location on the ground.
A Sky News investigation also found that 80 percent of the runs shared publicly on the sporting app Strava at Muwaffaq Salti Air Base during the April ceasefire started or finished in this northern barracks.
Satellite image showing damage, highlighted in red, published by Iran’s Fars News Agency.
Less than 100 meters from the destroyed area, “LSA DFAC” is pinned on Google maps. “DFAC” is the standard US military acronym for “dining facility”, according to Stars and Stripes. Several Google reviews also discuss the steak being served in this location.
Left: Google reviews for the dining facility (names blurred by Bellingcat). Right: Google Earth satellite image with the Airman’s Attic and dining facility visible in the area targeted by Iran.
Al Udeid Air Base
Similar mapping information is available for Al Udeid Air Base in Qatar, the largest US military installation in the Middle East.
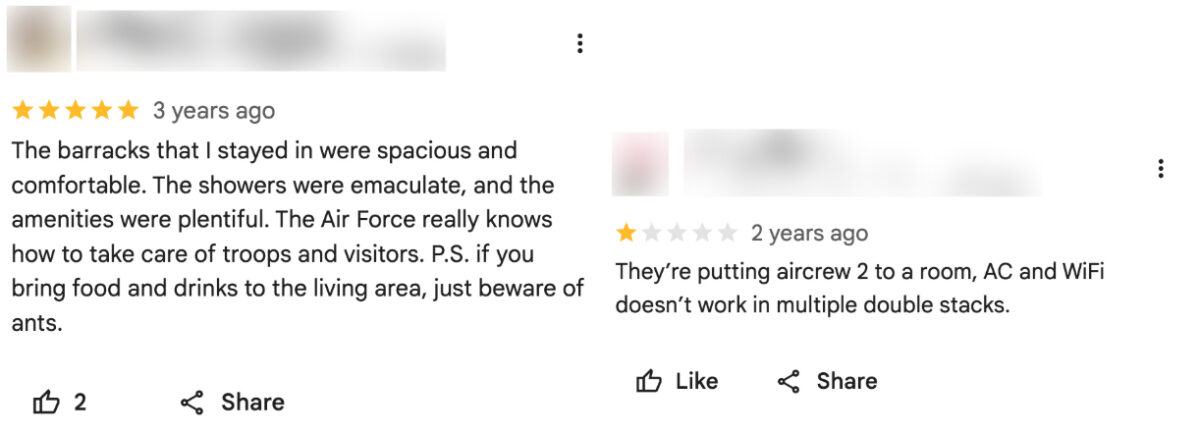
The base appears unblurred on Google Maps and entries on the platform identify the functions of numerous buildings. These include lodging facilities, which videos and reviews indicate are used by US Air Force crews and show the interior layout of the facility.
Google reviews for “Al Udeid Lodging” indicate the presence of US Air Force crews (names blurred by Bellingcat).
Meanwhile, Russia’s Yandex Maps details the site of two cinemas, a bar and a school on the base. This appears to match information provided on Google Maps.
While Al Udeid Air Base was damaged during Iranian attacks earlier this year, the areas that were struck do not appear to be among those listed on Google.
Business Insiderreported that a geodesic dome that housed secure communications equipment was hit in the strikes. ABC News detailed how another building had been damaged near the centre of the base. Google Maps shows a large warehouse-like structure at the location where ABC News reported this strike.
A New Reality in the Middle East
Former US Air Force targeting specialist Wes J. Bryant said the problem facing US bases in the Middle East reflected a broader assumption within the military that bases in allied countries were safe from serious attack. He said the belief that these were rear-area bases where “nothing’s going to happen out here” was a fundamental miscalculation, and that the Google Maps issue was an example of the military failing to account for that vulnerability.
Matthew Savill, Director of Military Sciences at the Royal United Services Institute, said Western militaries do not have consistent policies governing what information can be publicly posted about sensitive sites. He said the issue needs to be considered before a conflict begins, rather than when attacks are already underway. “The start point should be, can we enforce operational security discipline?” Savill pointed to restrictions already in place at some UK military facilities, including Faslane, a naval base that houses the UK’s nuclear submarines, where he said personnel are not permitted to use mobile phones on site.
Savill told Bellingcat that the different pieces of data available on Google Maps, even if outdated, provided a “pattern of life” about US bases in the Middle East. But he added that the use of Google to help with the military targeting of Western bases is not new, saying he encountered the issue while deployed to Iraq more than 20 years ago.
“When I was in Iraq, we knew for a fact that insurgents and militants had been using commercial imagery, including Google Earth, to try and map our bases,” he said. “We have known for more than 20 years that there is a vulnerability that if you don’t stop the collection and layering of data early on, that your bases can be heavily mapped.”
The use of open-source information to support military targeting has been documented in Ukraine. In 2022, Foreign Policy detailed how Ukrainian private intelligence company Molfar used photographs of Russian soldiers published by Russian media alongside Google Earth satellite imagery to identify their location. Molfar passed its findings to Ukrainian intelligence, and the site was subsequently struck by the Ukrainian military.
The security risks of publicly mapping military installations were recognised by the US military in 2008, when the Pentagon banned Google’s Street View from documenting the interiors of its bases. Since the Iran war started, US military commanders have also warned service members about posting photographs and videos from bases after Iranian attacks, cautioning that such footage could help Iran assess the effects of its strikes.
Iranian attacks have forced US personnel to evacuate many additional locations that were deemed too vulnerable to further strikes.
Bellingcat’s Jake Godin, Charlotte Maher and Merel Zoet contributed to this report.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published. Become a member and support our work here.
An online ad for Ben McAdams, the Democratic candidate for Congress in Utah, emphasised that he could be trusted because he “fought back against MAGA”.
What’s interesting is that both ads were ultimately paid for with money from the same organisation – Leading the Future (LTF), a Super PAC which opposes regulations that “constrain” innovation in AI. The network has received US$125 million in funding in total from OpenAI president Greg Brockman, his wife Anna Brockman, tech-focused venture capital firm Andreessen Horowitz (a16z) and a16z’s founders, Federal Election Commission (FEC) filings show.
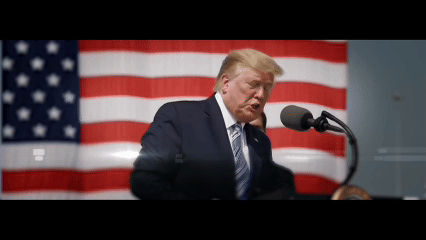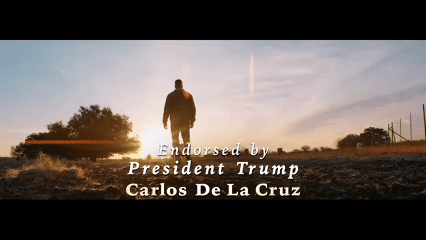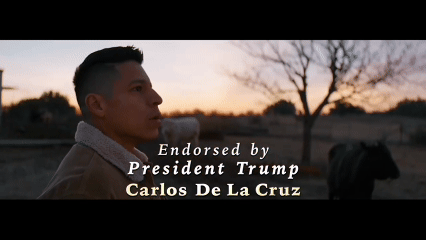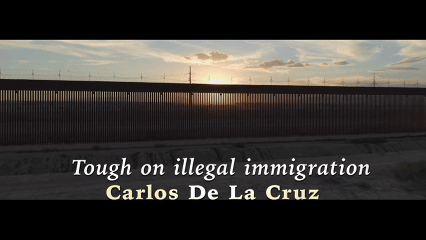
Like the ads run by organisations funded by LTF, the Super PACs funded by PFA also ran ads that appeared supportive or critical of Trump depending on the voters they were targeting.
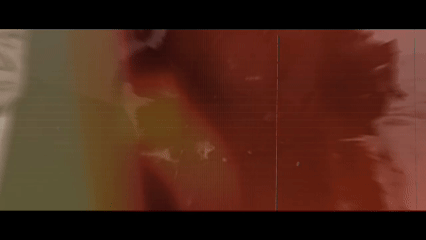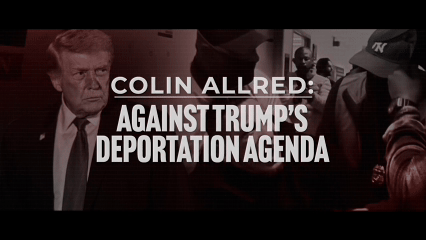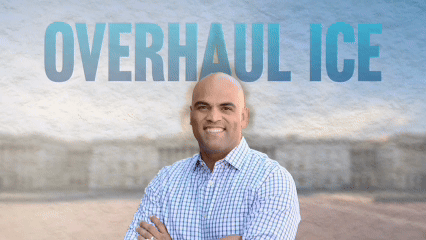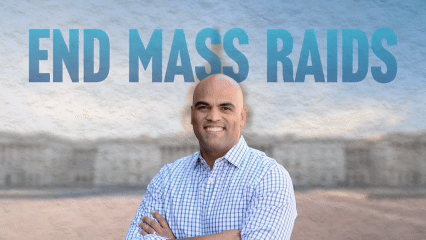
Ads in support of Republican Carlos De La Cruz (above) and Democrat Colin Allred (below) in Texas, paid for by Defending Our Values PAC, and Jobs and Democracy PAC, respectively. Source: Defending Our Values PAC / Jobs and Democracy PAC / Google Ad Transparency Center
None of these ads mentions AI.
As the US 2026 midterm elections approach on Nov. 3, Super PAC spending on political advertising has reportedly soared to record highs, surpassing US$11 billion last week and exceeding the amount spent on any other election cycle to date.
Super PACs are a particular type of political action committee (PAC) that may receive unlimited contributions from individuals, corporations, labour unions and other PACs for the purpose of financing independent expenditures and other independent political activity.
In this year’s elections, LTF’s and PFA’s Super PACs, funded by the AI industry heavyweights, have played an outsized role in supporting or opposing candidates through advertising. But as polls show distrust of AIcrosses party lines, the advertisements that Silicon Valley’s leaders are paying millions of dollars to try to sway the results in their chosen candidates’ favour often do not mention AI at all.
Photo: Reuters/Shannon Stapleton
While LTF is a registered Super PAC itself, FEC filings show it mainly disburses money to other Super PACs in its network which run political ads.
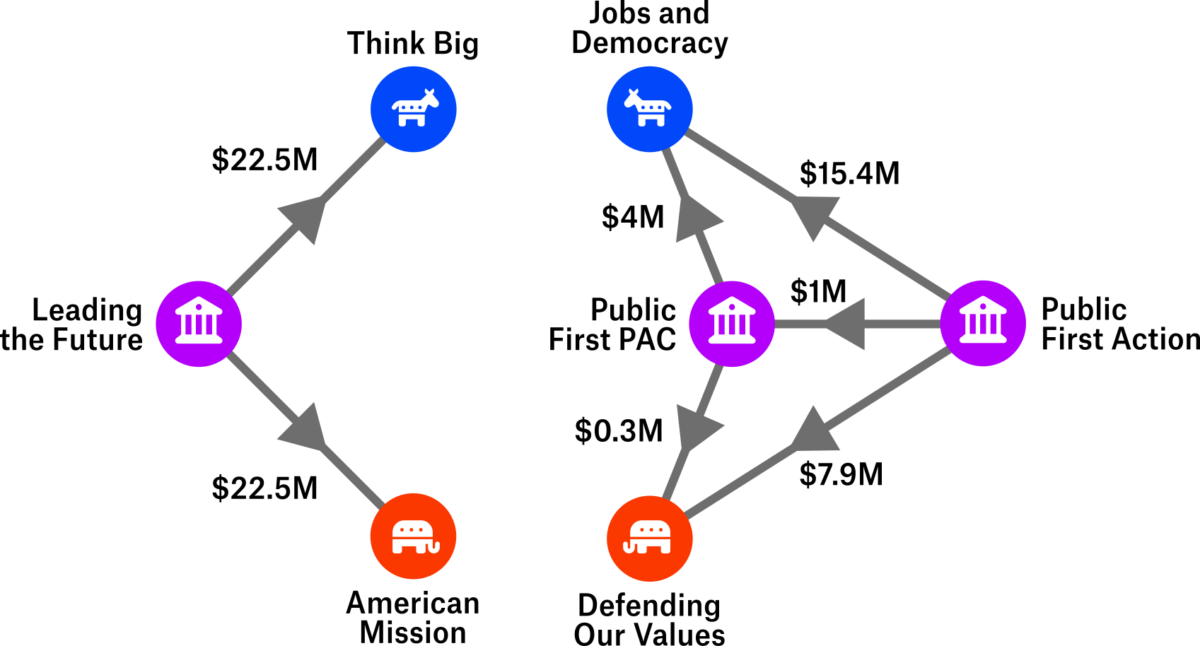
Of about $52 million that LTF has disbursed to date, $20 million went to Think Big, which targets the Democratic voter base, and another $20 million went to American Mission, which focuses on Republicans.
PFA, meanwhile, is registered as a “social welfare”, or 501(c)(4), organisation. This type of non-profit is not required to disclose its donors or disbursements. However, PFA contributes funds to three Super PACs: the bipartisan Public First PAC, Jobs and Democracy for Democratic candidates and Defending Our Values for Republicans. FEC filings for these Super PACs show Public First PAC received $1 million, Jobs and Democracy received $15.4 million and Defending Our Values received $7.9 million from PFA. Public First PAC’s FEC filings also show that $4 million of its $4.4 million in disbursements disclosed so far went to Jobs and Democracy, while another $300,000 went to Defending Our Values.
Disbursements to Think Big, American Mission, Jobs and Democracy and Defending Our Values from Leading the Future, Public First PAC and Public First Action. Graphic: Bellingcat
Super PACs are allowed to accept unlimited contributions from other political committees, and other similar networks of Super PACs have been observed in the current election cycle, such as cryptocurrency-linked Fairshake and its affiliated Super PACs.
Only ads supporting or opposing two candidates mentioned AI, and none mentioned data centres, a top issue this election cycle. A New York Times analysis of 95 video ads paid for by the same four Super PACs, using data gathered by media tracking firm AdImpact, had similar findings. FEC rules state that Super PACs can spend money to support or oppose a candidate, but cannot coordinate with the candidate or their campaign on this. There is no evidence that any of the candidates or campaigns for which the Super PACs ran ads have coordinated with them.
Michael Beckel, Director of Money in Politics Reform at cross-partisan political reform group Issue One, told Bellingcat that voters are at a disadvantage when special interests fund Super PACs running ads that don’t mention the priority issues of those underwriting them.
“Special interests seem keen on moving voters with messaging around hot-button issues, all while advancing a specific policy agenda that viewers of ads are kept in the dark about,” he said. The result of this, Beckel added, was that “the industry gains a stronger hand in Washington, while voters get little chance to judge the agenda their votes could help advance”.
A representative for PFA stated: “We endorse officials who support regulating AI. The aligned PACs run ads on the issues that matter most immediately to voters in each race, and for most electorates right now that means the economy, affordability, public safety, and other issues that they are facing on a daily basis.”
Jobs and Democracy, Defending Our Values, LTF, Think Big and American Mission did not respond to questions about their political advertising as of publication.
A recent survey by think tank Data for Action and non-profit Guardrails Action found that about three-quarters of likely voters would be less inclined to vote for a candidate if they found out they had accepted a donation from an AI Super PAC.
The ads distributed by the AI-backed Super PACs supporting or opposing 29 candidates mentioned economic issues such as taxes, the cost of living, consumer rights and local jobs or small businesses. Another 16 mentioned immigration or law enforcement and 17 mentioned US President Donald Trump or his “Make America Great Again” (MAGA) movement.
Like the ads mentioning Trump, those on immigration were sharply divided in messaging depending on whether they were targeting Democratic or Republican voters, even when they were paid for by the AI Super PACs in the same network.
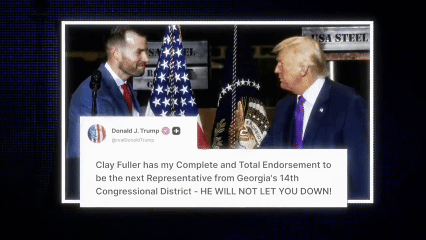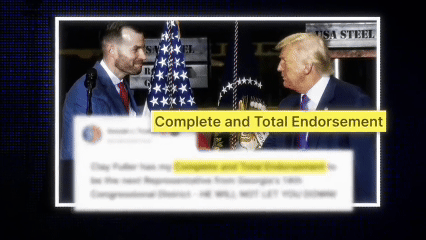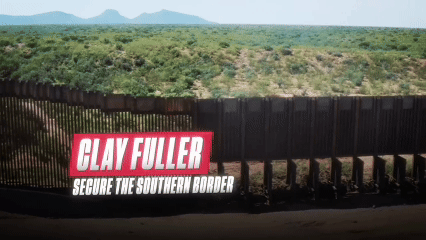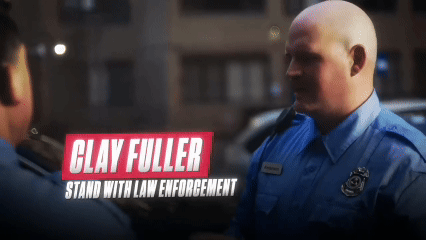
LTF’s Think Big sponsored an ad for Democratic candidate Jeremy Moss in Michigan that talks about how he stood up to Immigration and Customs Enforcement (ICE), while American Mission’s ad for Republican Clay Fuller in Georgia mentions how he is focused on securing the southern border.
Ads for Moss (above) and Fuller (below) sponsored by Think Big and American Mission respectively. Source: Think Big / American Mission / Google Ad Transparency Center
We found similar messaging in ads mentioning immigration that were paid for by Super PACs in PFA’s network. Defending Our Values ran an ad in support of Republican John Cowan in Georgia emphasising that he will combat illegal immigration, whereas Jobs and Democracy’s ad for Democrat Valerie Foushee in North Carolina said she was “leading the fight to hold ICE accountable”.
Ads for Cowan (above) and Foushee (below) sponsored by Defending our Values and Jobs and Democracy respectively. Source: Defending Our Values PAC / Jobs and Democracy PAC / Google Ad Transparency Center
For the ads that did mention AI, almost all were in support of Alex Bores’ primary in New York. PFA’s Jobs and Democracy PAC ran 152 ads supporting Bores’ candidacy, at least some of which mentioned that he was in favour of safeguards on AI and holding Big Tech accountable.
LTF’s Think Big, on the other hand, ran 22 ads opposing Bores’ candidacy. While they did not mention his stance on AI, many of Think Big’s ads focused on him receiving funding from Anthropic, “dark money Super PACs” and his former employer Palantir, the software giant whose technology, including a new AI system, is used in ICE’s immigration enforcement operations.
Ads supporting Bores sponsored by Jobs and Democracy. Source: Jobs and Democracy PAC / Google Ad Transparency Center
Ads opposing Bores, sponsored by Think Big. Source: Think Big / Google Ad Transparency Center
Jobs and Democracy’s advertiser page also showed two ads for Josh Gottheimer in New Jersey that focused on the threats of AI scams and AI-generated media, urging voters to call Gottheimer to tell him to “stand strong for AI safeguards”.
Ad for Josh Gottheimer that mentions AI, listed on Jobs and Democracy PAC’s Google Ads Transparency Center advertising page. Source: Jobs and Democracy PAC / Google Ad Transparency Center
Major donors to LTF that Bellingcat reached out to – Greg Brockman, a16z, and a16z founders Marc Andreessen and Ben Horowitz – did not respond to requests for comment on their funding to the Super PACs as of publication. We could not find any publicly available contact information for Anna Brockman, but we also asked about her contributions to LTF in questions to her husband.
OpenAI did not respond to questions about the Brockmans’ contributions to LTF as of publication. However, the company published a statement on the topic in June, which said “OpenAI does not direct the activities of LTF, or have visibility into their operations” and that “any engagement with that organisation has been in a personal capacity, not on behalf of the company”.
PFA’s main public donor, Anthropic, did not respond to Bellingcat’s queries about its funding for PFA and PFA’s political advertising as of publication. It said in a statement on its website in July that its donations to PFA were “to help promote policies that will maintain meaningful safeguards, sustain America’s AI leadership, and demand transparency from the companies building the most powerful AI models”.
Unknown Vendors
Federal campaign finance laws require federal political committees to file periodic campaign finance reports disclosing their receipts and disbursements.
Our analysis of FEC filings for LTF and the Super PACs in its network revealed that they were channelling more than $36.4 million in total towards four companies that were newly set up, with no apparent online presence outside of these filings.
A complaint to the FEC by the non-profit Campaign Legal Center (CLC) in May cited American Mission and Think Big’s payments to Summit Ridge and Lantern Productions, alleging that the Super PACs had “unlawfully evaded federal reporting requirements by funnelling their payments for goods and services through shell companies set up to conceal how the super PACs are actually spending their money”. The FEC has not yet ruled on the complaint. LTF, American and Think Big did not respond to Bellingcat’s queries about the complaint as of publication.
FEC filings show that LTF paid a company called Prusik Partners LLC more than $966,000 for operational expenditures for a range of services including communications and strategy consulting, as well as legal fees.
The network’s Democrat-focused Super PAC, Think Big, paid a company called Lantern Production Consultants LLC more than $20 million, based on filings for disbursements from Aug. 20, 2025 to Oct. 14, 2026.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
The payments included $3.17 million for operational expenditures for a range of services such as media consulting and research, and another $17 million for independent expenditures. The FEC defines an independent expenditure as one that pays for “a communication that expressly advocates for the election or defeat of a clearly identified candidate”. The highest independent expenditures paid to Lantern ($8 million) were to oppose Bores’ candidacy, the filings show.
Think Big also declared in its filings that it had paid a company called Blue Horizon Compliance Consultants LLC almost $55,700 for “compliance consulting”.
Republican-focused American Mission, on the other hand, paid a company called Summit Ridge Media LLC more than $13 million, based on filings for disbursements from Aug. 20, 2025 to Oct. 14, 2026.
This included $2.2 million for operating expenditures such as polling and website services, and $10.9 million in independent expenditures, with the highest amount (about $960,400) going towards communications in support of James Morris Kingston, the Republican candidate for the House of Representatives in Georgia.
Bellingcat found that all four of these LLCs listed mailing offices and office supply goods stores in Nevada as their mailing addresses. We could not find records of them doing business with any entity outside of the LTF network – in fact, they appeared to have no online presence aside from their names appearing in the filings and business registrations.
Despite their addresses being listed in Nevada, none of the companies could be found in the state’s public business registry. Instead, Bellingcat found registrations for Prusik, Lantern Production and Summit Ridge across the country – in Delaware.
While Delaware is the second-smallest state in the US, more than half of all Fortune 500 companies are incorporated there according to the Delaware Secretary of State. The state’s business-friendly laws mean companies can reportedly incorporate in minutes and are only required to name a representative – who can be a paid agent unrelated to the business – in public registration documents, not the beneficial owners.
Articles of incorporation from the Delaware Secretary of State showed that Prusik was registered on July 22, 2025, while Lantern Production and Summit Ridge were both registered on Oct. 30, 2025. We also found a Delaware registration for a company called “Blue Horizon Compliance Group LLC”, registered on Oct. 30, 2025. While the name differs slightly from the Blue Horizon Compliance Consultants LLC that Think Big declared payments for, the registration was signed by the same agent listed in the documents for Lantern Production and Summit Ridge.
Subscribe to the Bellingcat newsletter
Subscribe to our newsletter for first access to our published content and events that our staff and contributors are involved with, including interviews and training workshops.
The filings show that all of these companies – including Blue Horizon Compliance Group, if this was indeed the same entity referred to in Think Big’s filings – began receiving payments from the Super PACs within two to three months of their business registrations.
Saurav Ghosh, CLC’s Director of Federal Campaign Finance Reform, told Bellingcat that the group filed the complaint because “when groups funded by big corporate special interests evade transparency laws, voters lose”.
“Federal reporting requirements help ensure transparency in our elections and protect voters’ legal right to know where the money is going,” Ghosh said. “Secret spending schemes like this make it virtually impossible to ensure that our elected officials are staying accountable to voters instead of wealthy special interests.”
We were unable to reach out to the LLCs as none of them had phone numbers or email addresses listed online. LTF, Think Big, and American Mission did not respond to questions about the LLCs, including whether “Blue Horizon Compliance Consultants LLC” listed in Think Big’s filings was the same company as Delaware-registered “Blue Horizon Compliance Group LLC”. However, a WIRED story on these same LLCs quoted a spokesperson from LTF as saying that the complaint was “a desperate ploy for attention from Public First, Anthropic, and the groups aligned with their outside organisations”. WIRED also quoted a Public First spokesperson denying that the group had anything to do with the complaint.
Beckel suggested that stricter transparency measures relating to Super PAC spending would help inform and empower voters. For instance, Congress could pass legislation to require ads to include the names of the top donors, he said, adding that similar rules had been passed with cross-partisan support in places like Alaska and Arizona.
“Congress would be doing voters a huge service by passing more robust transparency requirements for political ads. Voters deserve to know who is behind the ads they’re seeing,” Beckel said.
About the Data
Google Ads Analysis
We reviewed ads available through Google’s Ads Transparency Center. These are ads served on Google platforms like Search, Display, Gmail and YouTube. We filtered specifically for ads shown between Jan. 1 and Oct. 23, 2026 in the US.
We focused only on video ads classified as political advertisements, not text- or image-based ads. We looked at ads purchased by the following advertisers: Think Big, THINK BIG, American Mission, Jobs and Democracy PAC, JOBS AND DEMOCRACY PAC, Defending Our Values PAC and DEFENDING OUR VALUES PAC.
In total, there were 336 advertisements in the dataset: 86 from Think Big, 57 from American Mission, 22 from Defending Our Values and 171 from Jobs and Democracy. Each ad listed on the platform was counted individually, although many of these were duplicates of the same ad that was run over a different period or platform. Some of the ads have also been removed for ad policy violations, but we were able to see which candidates they were for because they appeared when searching for ads specific to those candidates within the advertiser’s page.
For the coding of themes, we looked at whether each of the themes mentioned (AI, data centres, economy, Trump, and immigration or law enforcement) appeared in any of the ads for each candidate. This does not account for how many times each theme may have appeared in ads for a candidate.
Our notes on the Google ad data and count of themes for each candidate can be found here.
For the accompanying map showing spending by each Super PAC by state, we used data from the Google Ad Transparency Center showing the total spend per advertiser and the spending range per ad to estimate the spend per ad (as the data does not show the exact spend per ad). For each advertiser, we separately added up the minimum and maximum spend amounts for all ads. We then calculated where in that range the total spend fell (e.g. 45 percent between the minimum and maximum spend). The per ad spend was estimated by applying this same proportion to the range of each ad and rounding down to the nearest dollar.
FEC Campaign Finance Data
Data from FEC filings for LTF, Think Big and American Mission are based on disclosures from Aug. 20, 2025 to Oct. 14, 2026. Data from FEC filings for Public First, Defending Our Values and Jobs and Democracy are based on disclosures for Jan. 1, 2026 to Sept. 30, 2026, which were the latest available as of publication.
The amounts LTF and PFA contributed to their associated Super PACs are based on the recipient Super PACs’ receipts for contributions from “Leading the Future”, “Public First”, “Public First Action” and “Public First Action, Inc”.
Links to the source pages for these filings, as well as the data we exported for our analysis, are available here.
Data visualisations by Galen Reich. Melissa Zhu contributed research to this piece.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published.
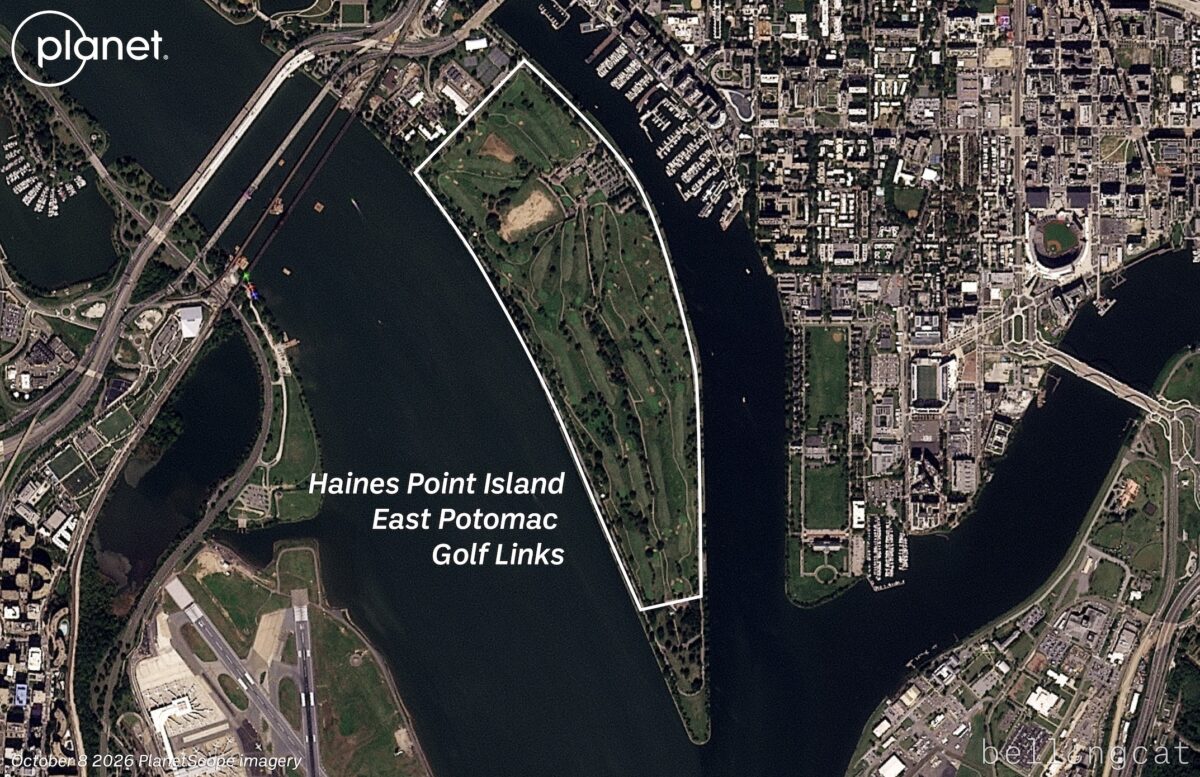
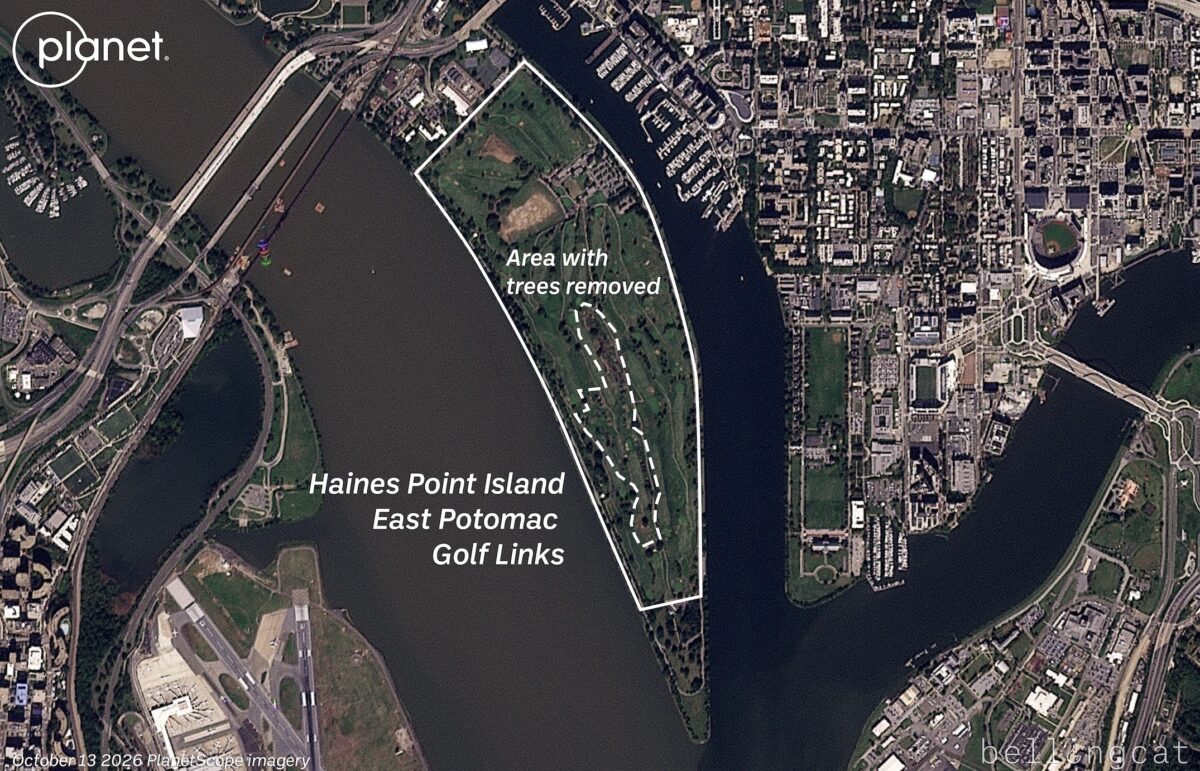
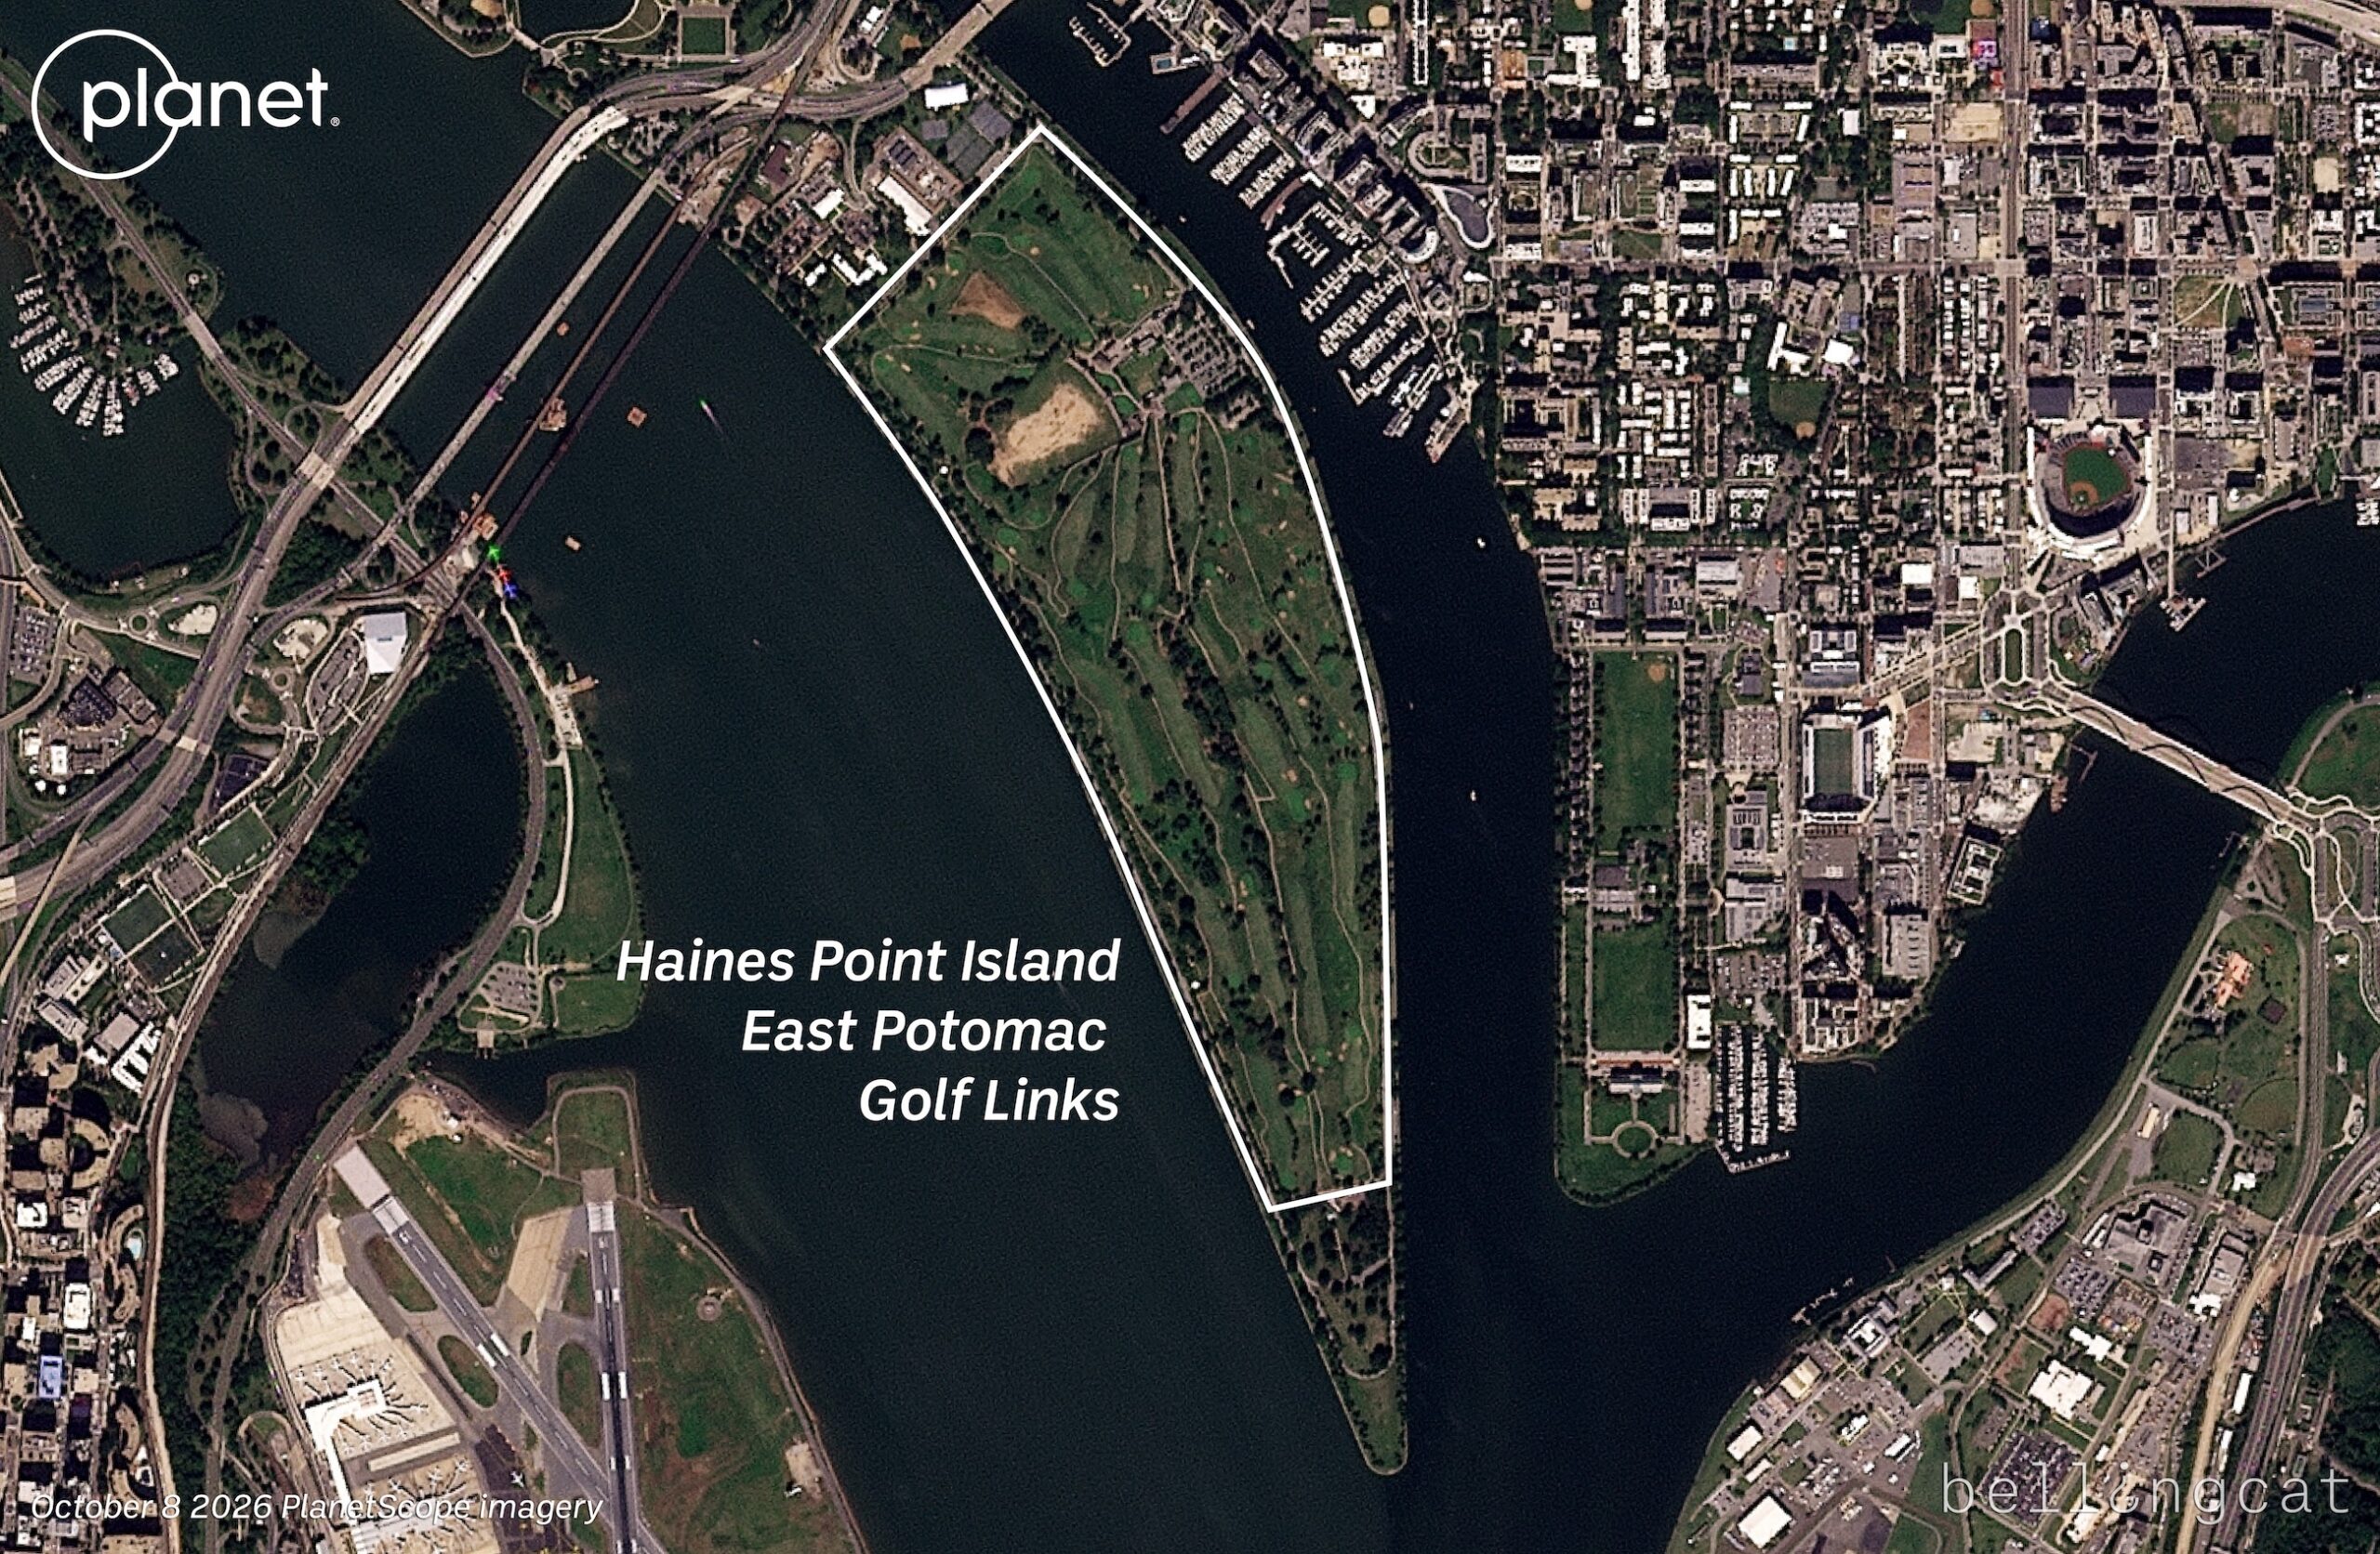
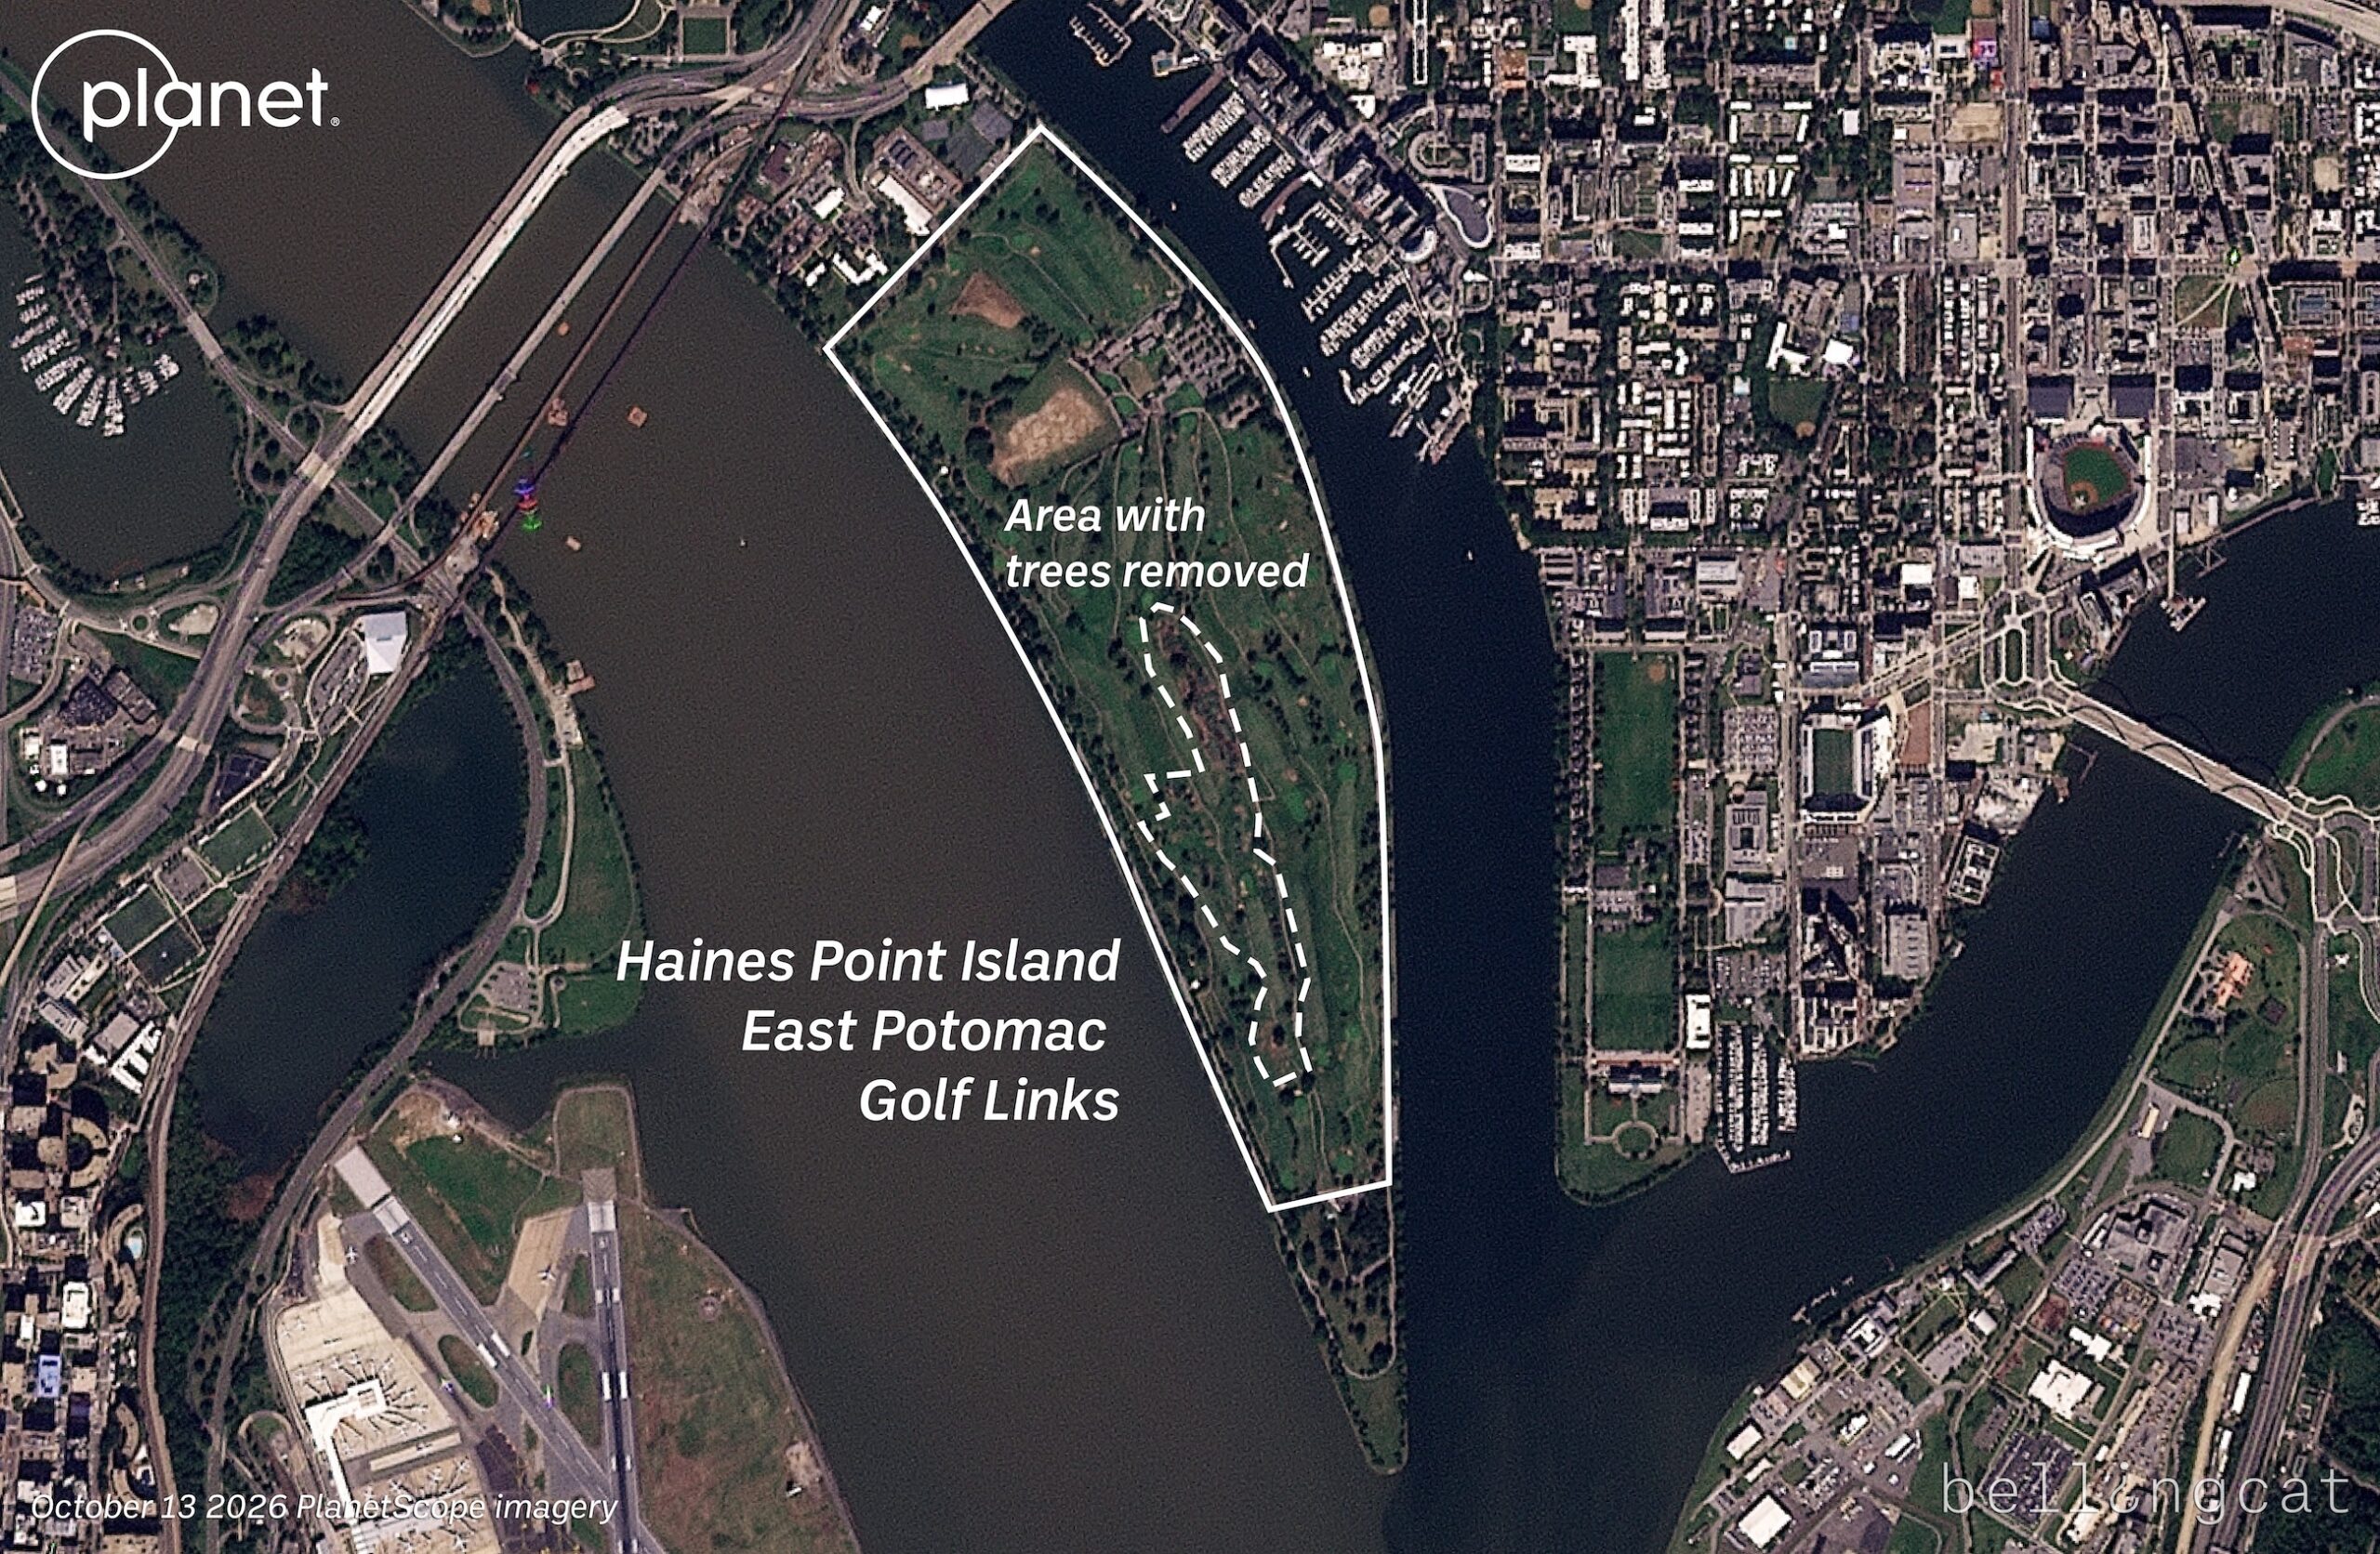
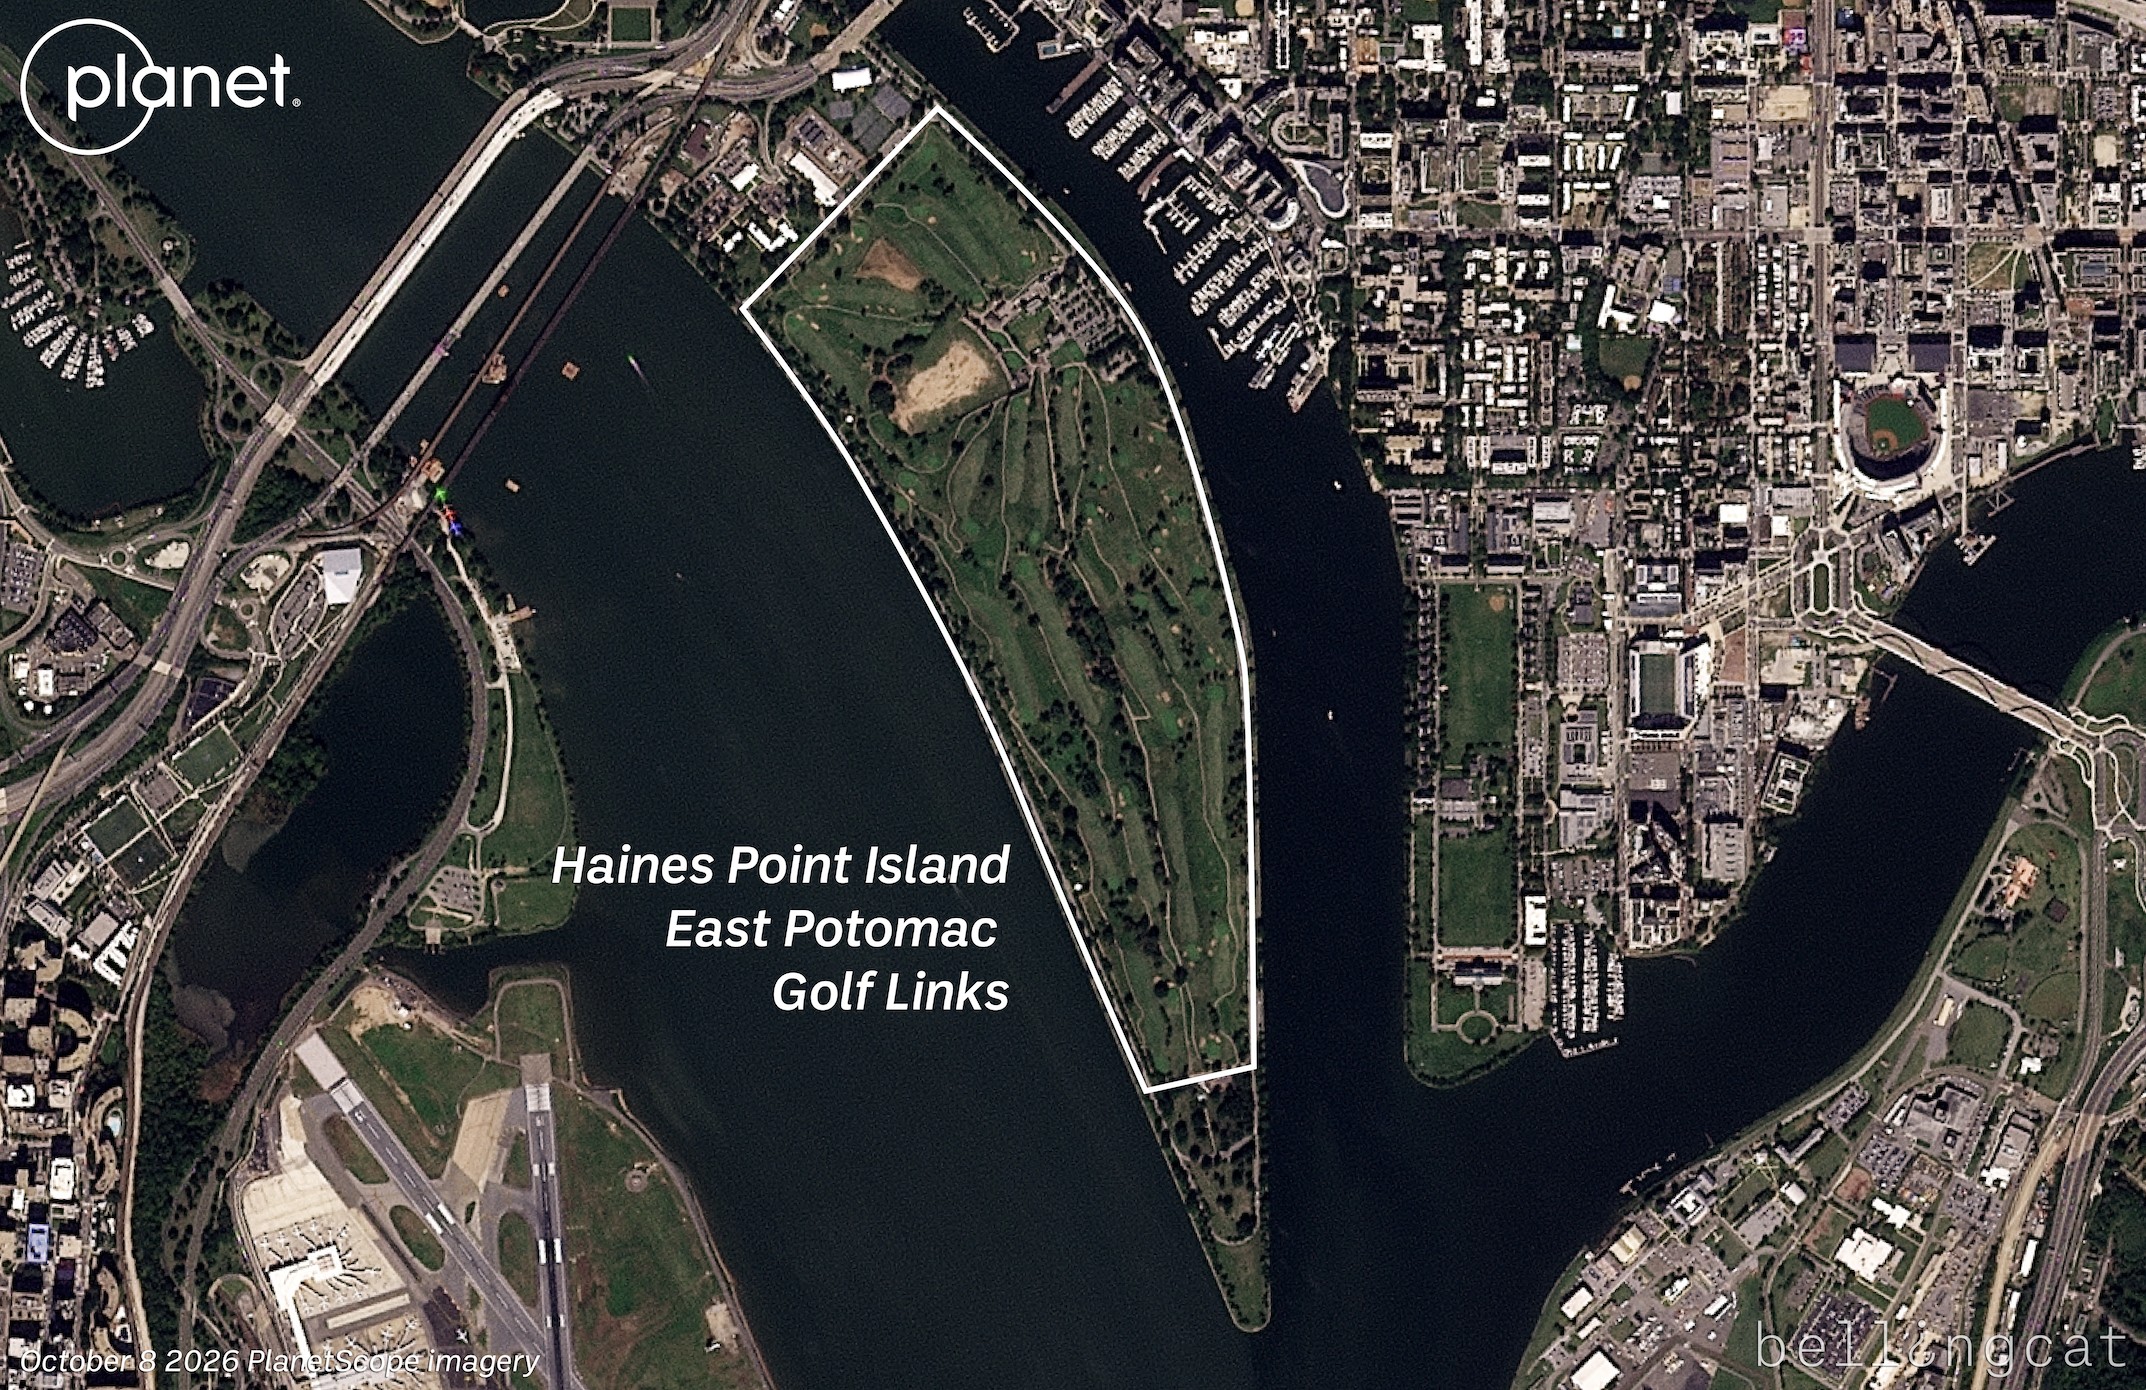
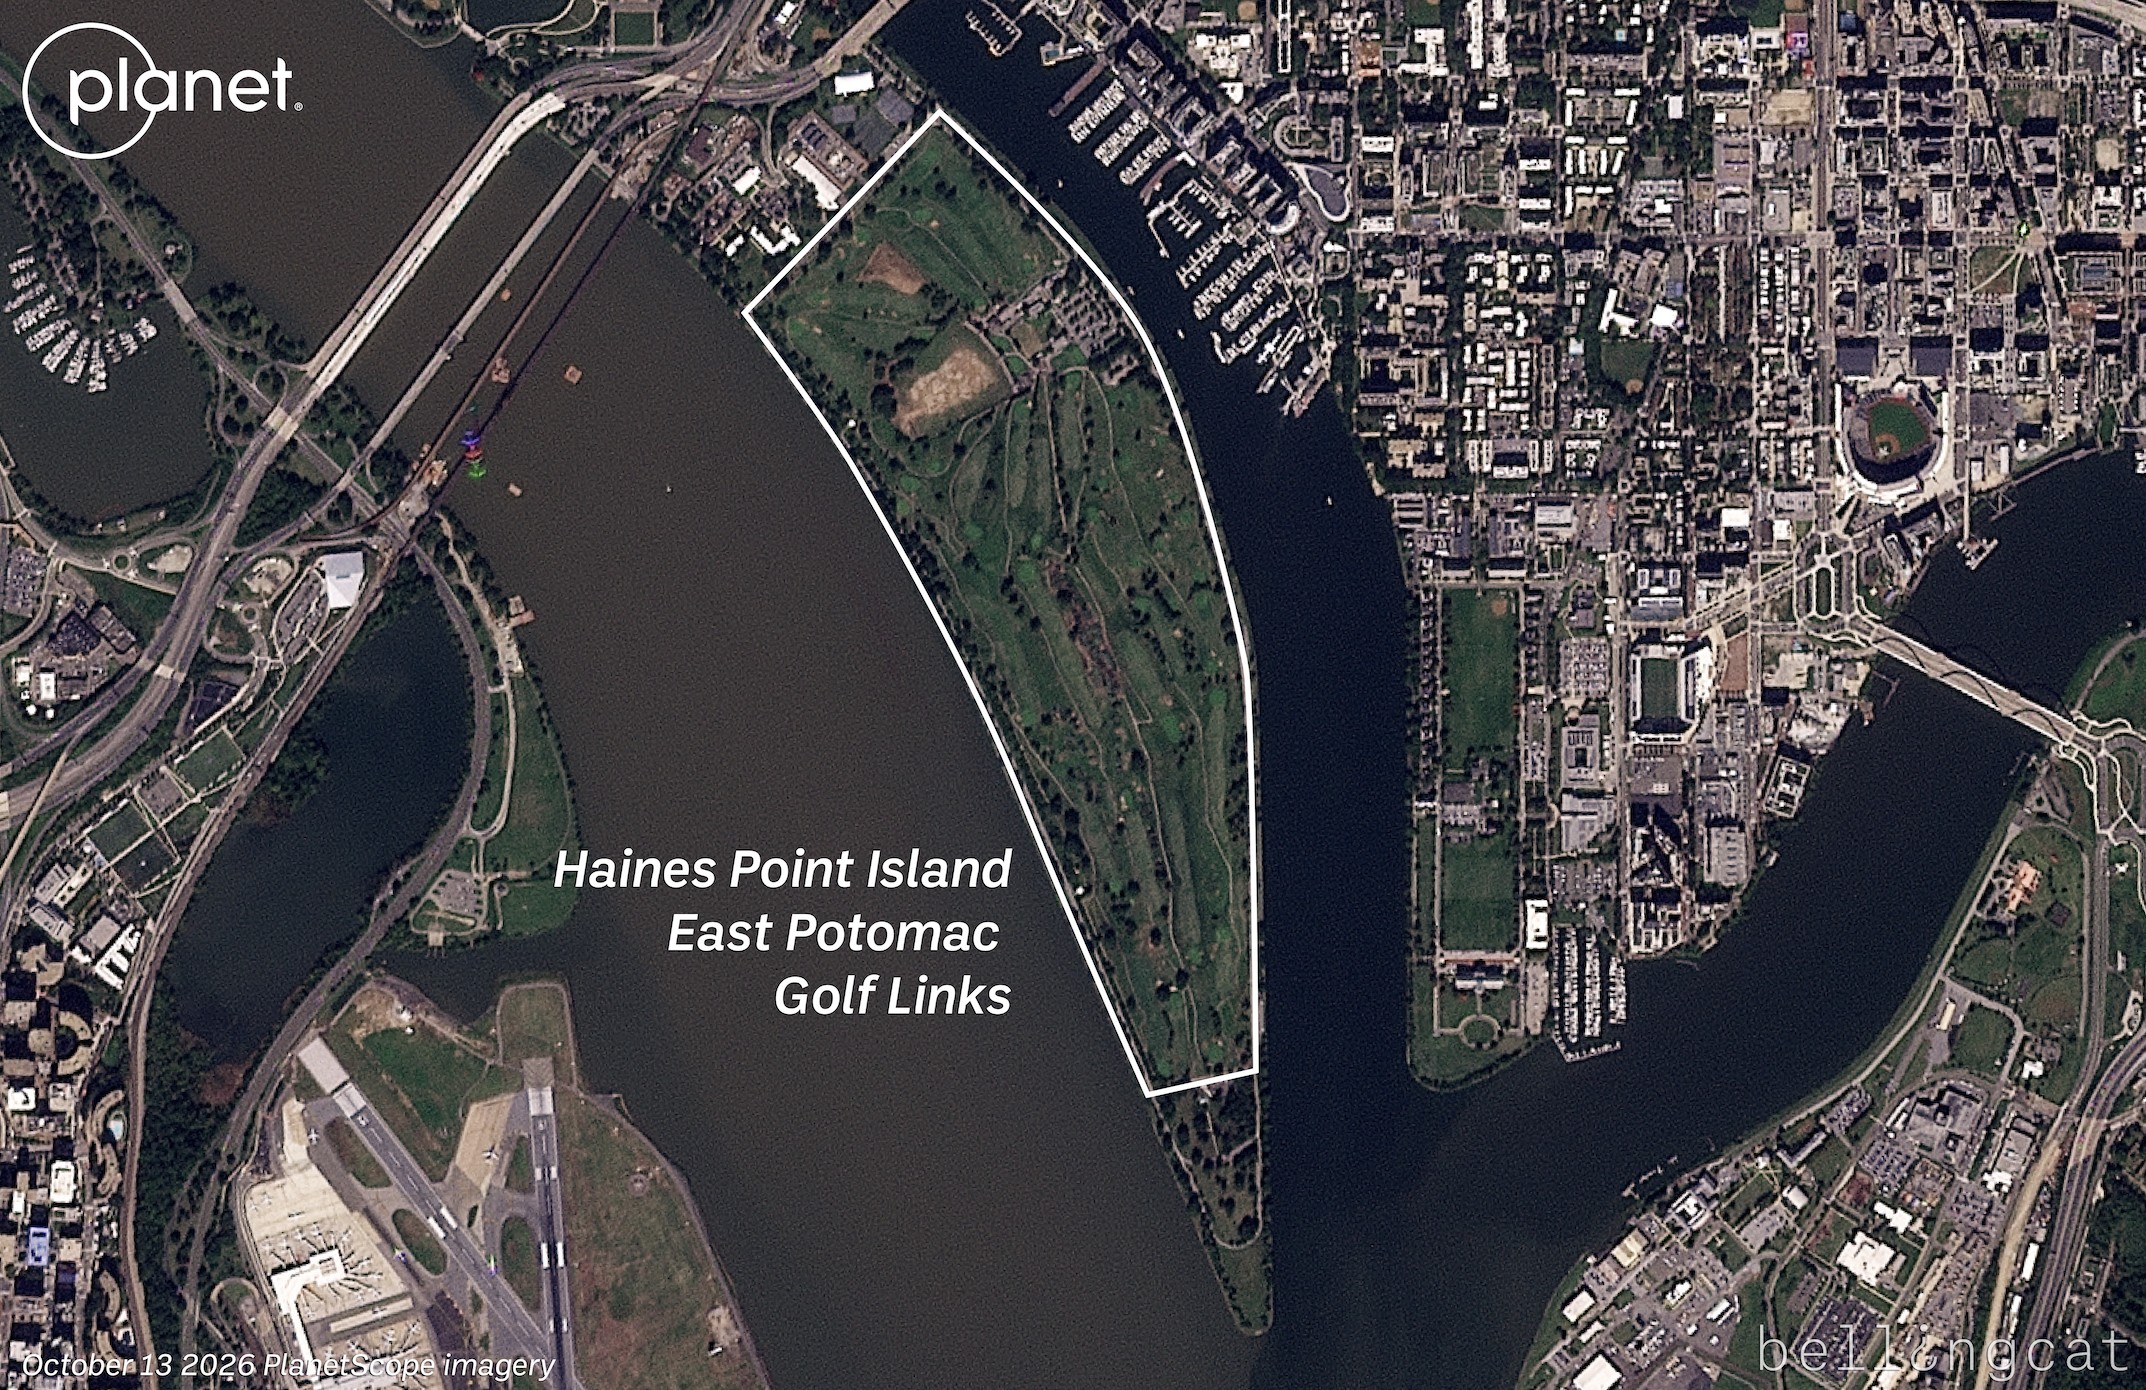
Satellite imagery obtained by Bellingcat lays bare the extent of tree-felling at a Washington DC golf course that President Trump is reportedly seeking to transform into a championship-level course, despite moves to protect the site by conservationists.
The extent and circumstances surrounding the rapid changes prompted a judge to call an emergency hearing earlier this week, banning any further changes until later this month.
Reports on Wednesday detailed that 430 trees were cut down at the East Potomac Golf Links which is owned by the Federal government and managed by the National Park Service (NPS). This is despite a judge reportedly stating earlier this year that no more than 10 trees at the course could be cut down without first notifying the court.
NPR reported that officials notified the court just before 5pm on Friday Oct. 9 of plans to remove up to 529 trees in phases starting the next day on Saturday Oct. 10. That prompted US District Court Judge Ana Reyes to call an emergency hearing on Oct. 12. By that time, 430 trees had reportedly been cut down.
Reyes is reported to have said she was “furious” with the Justice Department for the lack of time afforded the court and plaintiffs before the tree removal was carried out.
She was also reported to have said that the government’s actions had cost it “all of its credibility with me in this case.”
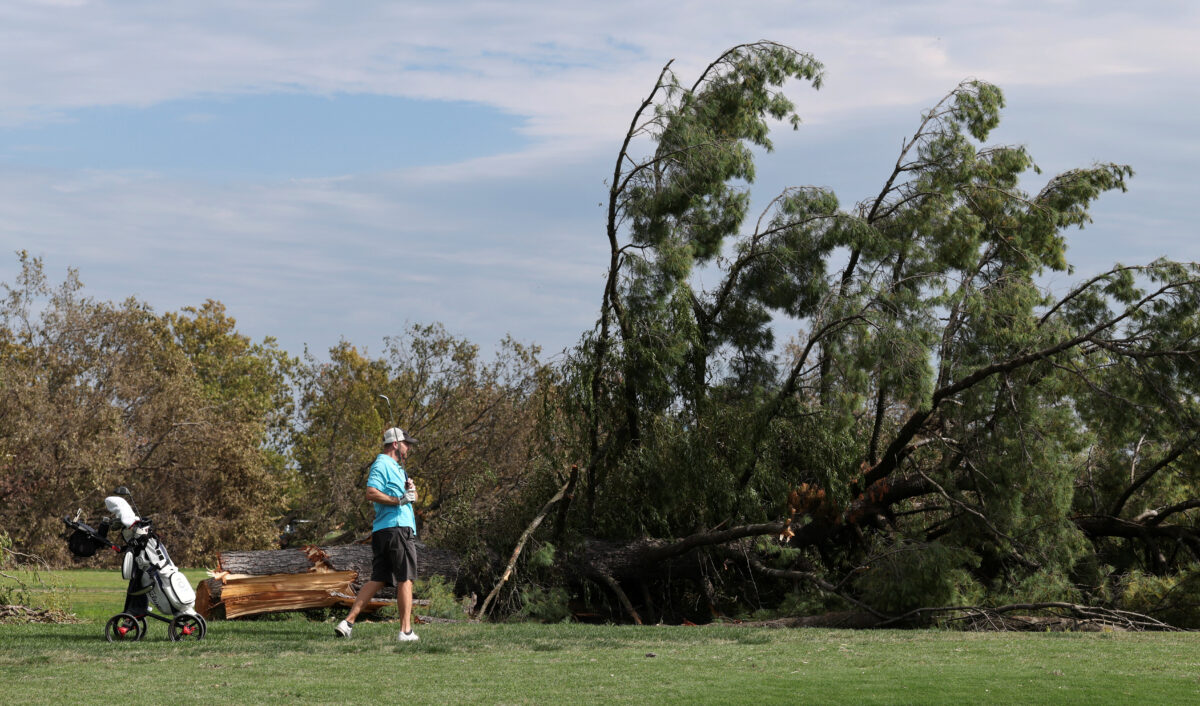
Images taken at the course earlier this week show trunks and branches strewn out across fairways.
Just total devastation wrought on East Potomac Park this past weekend.
450+ trees. For an admin that professes to support “beautification” of DC, that’s sure not what we or anybody else who has seen what they did on Saturday would describe it as.
East Potomac is (was?) a thriving, beautiful gem in the heart of Washington DC. A beautiful, public, accessible place that hundreds of thousands use annually. The assault on this place should infuriate every American.
The impacts of what took place Saturday will take years to fix. We cannot sit idly by while this admin treats our public lands like they are for the taking.
Reuters reported that an organisation called The DC Preservation League said in a February 2026 lawsuit that President Donald Trump was flouting environmental laws to “irreparably destroy a priceless piece of American history” so he could “convert a public recreation space into an exclusive, high-end golf course.”
Kevin Griess, an NPS official, reportedly stated at Monday’s hearing that tree removal was part of a 2019 plan that predates Trump’s aims for the course and sought to restore links-style vegetation.
Bellingcat contacted NPS as well as the Department of Justice but did not receive a response before publication.
A golfer hits toward felled trees at the East Potomac Golf Links. REUTERS/Kevin Lamarque
The changes to the golf course are not the only ones President Trump has sought in Washington DC and the surrounding area since the beginning of his second term. In October last year demolition began on the East Wing of the White House with the aim of building a new ballroom claiming it was “the safest building ever built.”
Trump has also proposed a 250-foot-tall “Triumphal Arch” to be built just outside the Arlington National Cemetery in Virginia.
Correction: This article was updated on October 15 to reflect that a judge told the US government not to cut down more than 10 trees before providing notice. The article previously said that no more than 10 trees could be felled without the court’s approval. The headline has also been changed to reflect this.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published.
US non-profits whose founding leaders or organisations have been associated with India’s controversial Rashtriya Swayamsevak Sangh (RSS) – or initiatives the Hindu nationalist group has endorsed – received millions of dollars over recent years through grants that allow donors to remain anonymous, a Bellingcat analysis has found.
The right-wing and Hindu nationalist volunteer organisation is widely considered the ideological parent of India’s ruling Bharatiya Janata Party (BJP). Prime Minister Narendra Modi, a former RSS worker, is one of its most famous supporters.
But the RSS’ vision of India as a Hindu nation is controversial both at home and abroad: it was previously banned in India three times, and a bipartisan US commission on religious freedom recently called for the US government to sanction the group “for their responsibility and tolerance of severe violations of religious freedom”. Almost a hundred US politicians, both Democratic and Republican, recently pledged not to take funding from RSS-linked entities.
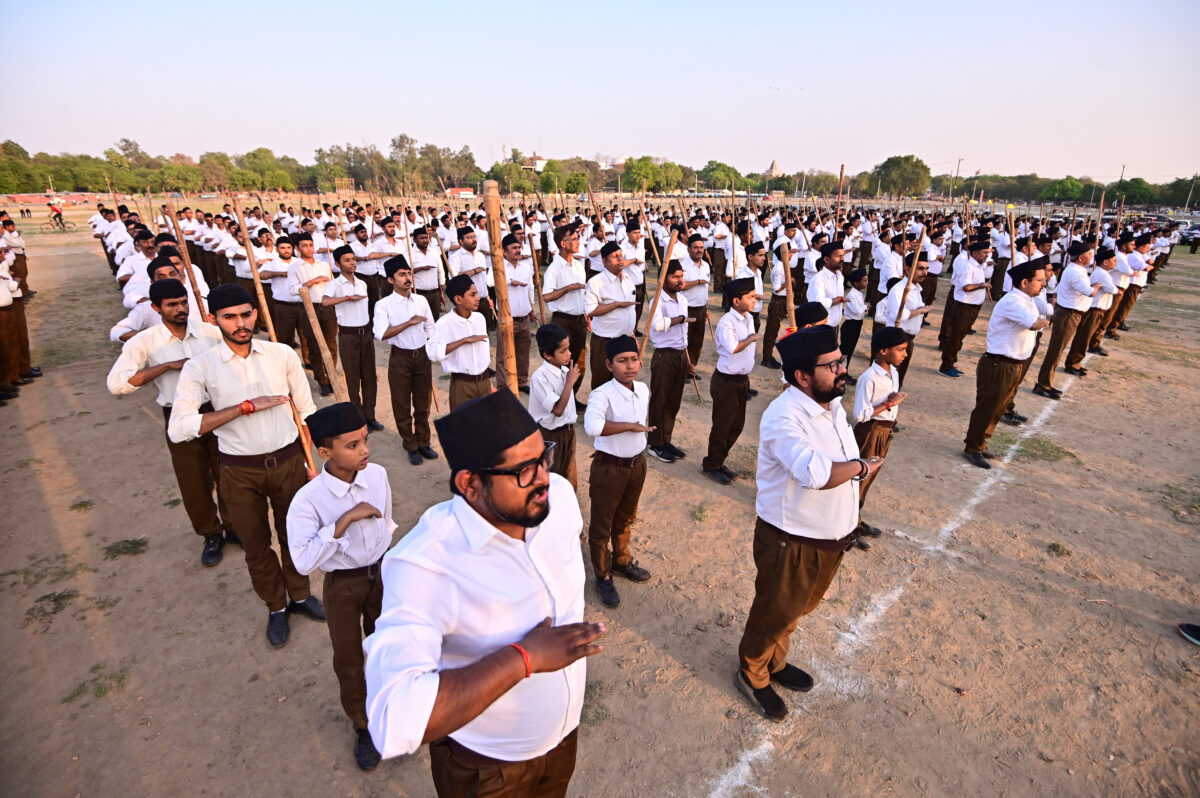
India’s far-right Hindu nationalist volunteer group RSS remains an unregistered entity in India. Source: Prabhat Kumar Verma/ZUMA Press Wire via Reuters Connect
“The RSS functions without independent oversight of its resources, finances, influence, and activities,” said Dr Angana P Chatterji, an anthropologist and scholar of South Asia studies at the University of California, Berkeley. “This is not proportional to the vast power, reach, and influence it possesses. Its leadership and cadre are protected from accountability and scrutiny,” she added.
The RSS had not responded to multiple requests for comment, as of publication.
Bellingcat identified two US-registered non-profits that appeared to have past and present ties to the RSS, or organisations associated with them, based on the non-profits’ or RSS websites and publications, as well as statements by the non-profits’ founders and spokespeople. The non-profits were the Ekal Vidyalaya Foundation of USA Inc (Ekal USA) and Sewa International Inc (referred to as Sewa USA).
We looked at all Form 990s – tax returns that US non-profit organisations are required to file annually – listing Ekal USA and Sewa USA as grant recipients, as well as the Form 990s of the charities themselves, from 2020 to 2024. As of September, the latest available Form 990s for Sewa USA were for the fiscal year ending December 2024, while Ekal USA also filed a form for the fiscal year ending December 2025, which was excluded for consistency, although the same pattern was observed during this period.
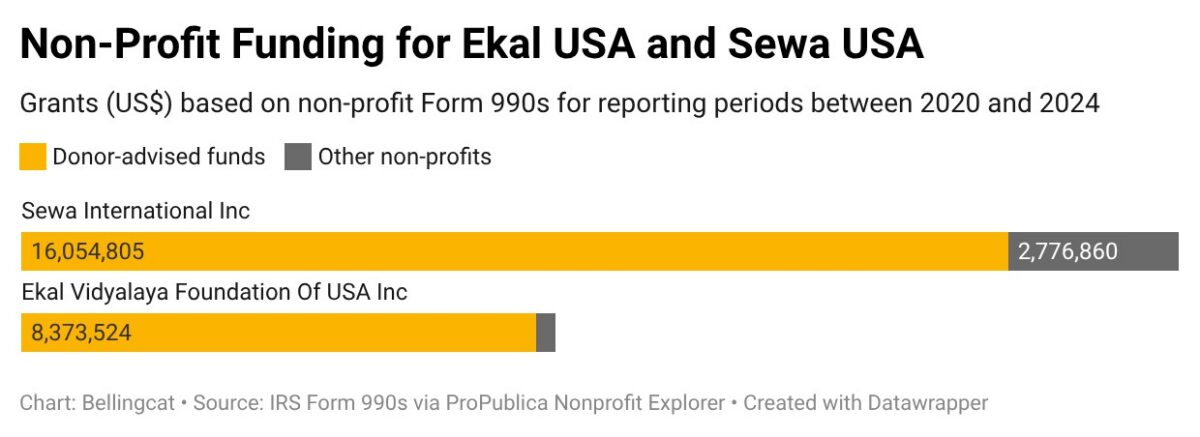
This analysis showed that the charities received at least US$24.4 million from 34 organisations that manage donor-advised funds (DAFs), or 20.7 percent of the total $117.8 million they reported receiving in contributions and grants during this period.
The actual amount from DAFs may be higher, as we excluded filings that covered partial years outside of this period – for example, June 2019 to June 2020. The filings from the two charities we identified were based on the calendar year.
The Form 990s also revealed that the vast majority of the money spent by these two charities on grants to other organisations or individuals was in India or the South Asia region rather than in the US: Ekal USA donated $33.7 million in foreign grants – all of which went towards the Ekal Vidyalaya project in India according to its filings – and none in domestic grants in the five years from 2020 to 2024, while Sewa USA reported $29.7 million in foreign grants and $622,613 in domestic grants during the same period.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
DAFs are common vehicles for people in the US who want to make donations to charitable causes while receiving tax relief or benefits. Donors do not control the money once they donate it but can advise on which charities the money eventually ends up at.
These funds are legally maintained and operated by non-profit sponsoring organisations. As public charities, DAF sponsor organisations detail the amounts and recipients of grants that they make on behalf of their donors in their Form 990s. However, they do not disclose who their donors are, and donors can choose to remain anonymous. (Note: Bellingcat USreceives grants from donor-advised funds, and some grants do not disclose the name of the grant recommender. However, many of our donors are listed on our funding page.)
There are many more organisations reportedly linked to the RSS that are not included in this analysis, but we focused on these two because of the large amounts of grants they received through DAFs, with the original sources of the funds untraceable from public information, as well as evidence pointing to both historical and current connections between them and the RSS or organisations associated with the RSS.
It is worth noting that some of the evidence we found pointing towards a connection between the two charities and the RSS or organisations associated with the RSS was from before or after the period we analysed (2020 to 2024). There is no evidence that DAF grants funded the RSS, only that they went to organisations that appear to have connections with the RSS. Experts told us that DAF grants undergo less regulatory scrutiny than other charitable donations and that DAF sponsor organisations have discretion over whether to restrict or permit donations to certain recipients.
Ekal USA
Houston, Texas-based Ekal USA is a non-profit that describes its mission in its Form 990s as “to provide free elementary education and free primary healthcare to children in remote and rural India”. The USA branch of Ekal Vidyalaya, according to its website, was founded in 2001 as part of efforts to “reach out to the global diaspora” in order to achieve a goal to “expand the reach of Ekal to 100,000 villages”.
RSS chief Mohan Bhagwat has appeared at multiple Ekal Vidyalaya events in India promoting the initiative over the years, as far back as 2014 and most recently in May.
Ekal USA was started in the late 1990s as a programme of the Vishwa Hindu Parishad of America (VHPA), or World Hindu Council of America, VHPA spokesperson Shyam Tiwari told Bellingcat in an email response. He added that it was set up as an independent organisation in early 2000. According to VHPA’s website, Ekal USA was established in 2002.
VHPA is based in the US, while the similarly named Vishwa Hindu Parishad (VHP) is in India. VHP lists VHPA in the “Hindus Abroad” section of its website. A 2017 article from VHPA’s magazine states that late founder Mahesh Mehta was trained by the RSS since he was 10 years old, and that the VHPA was born after Mehta was advised by the former supreme leader of the RSS to “build VHP in USA”. The national spokesperson of VHP in India, Vinod Bansal, said that it is an independent organisation that “sometimes shares ideology” with VHPA.
RSS’ website states that VHP was launched to organise Hindus and “reconvert all those who had been knowingly or unknowingly proselytised to alien faiths and are now desirous of coming back to the Hindu fold”. Bansal referred to VHP as an “independent part of the RSS” and an “ideological brother”.
Ekal USA Chairman-Advisor Subhash Gupta wrote in an Ekal USA publication this year that in the ‘80s and ‘90s, he was “president of the VHP’s Houston chapter” and “often received many high-profile guests from RSS and VHP”.
Gupta did not respond to requests for comment as of publication.
From 2020 to 2024, Ekal USA reported receiving more than $48.4 million in contributions and grants. Of this amount, at least $8.3 million was from DAF grants, based on Form 990s that listed Ekal USA as a grantee.
According to Ekal USA’s Form 990s, it transferred $33.7 million in foreign grants during this period and none in domestic grants for organisations or individuals. The forms also show that all the foreign grant money went towards building Ekal Vidyalaya schools in India. The rest of its expenses involved operational costs such as staff salaries.
The Ekal Vidyalaya movement has been criticised over reports that allege the schools are used to indoctrinate millions of India’s poorest and most vulnerable children and women with Hindu nationalist ideology, including that Muslims and Christians are “enemies of Hinduism”. Ekal Vidyalaya in India did not respond to multiple requests for comment.
Ekal USA did not respond to Bellingcat’s questions about these reports or any relationship it may have with the RSS. However, on its FAQ page, the group states that it does not teach religion in its schools and “does not discriminate based on caste, religious affiliation or linguistic affiliations”.
Sewa USA
Sewa USA, also based in Houston, describes itself as a “Hindu faith-based, humanitarian, nonprofit service organisation” and is listed under the heading of “Sewa Movement” on the website of India-based charity group Sewa International.
Sewa USA Vice President of Public Affairs Rakhi Israni told Bellingcat over email that the organisation “does not operate as a branch or affiliate of the RSS” or participate in political activity.
But multiple pages on the organisation’s website appear to indicate a connection between the non-profit and the RSS. In 2022, Sewa USA reposted an article on its website referring to Sewa International as “the US-based charitable non-profit organisation with links to the Rashtriya Swayamsevak Sangh (RSS)”. In a press release about the death of its founding member Ved Prakash Nanda in 2023, it noted that Nanda was “immersed in the ideals of the [RSS]”. And two different blog posts from 2021 and 2024 on Sewa USA’s website had volunteers citing RSS-led activities as the starting point for their involvement.
In addition, Sewa USA has also posted multiple times on social media and its website about an India-based organisation – Sewa Bharati – that appears to have the support of the RSS.
Sewa USA referred to Sewa Bharati as a “sister organisation” in an X post in 2014, and its regional chapter in Purvanchal as a “partner organisation” in a Facebook post in 2022.
On its website, Sewa USA said in a post that volunteers from its “partner organisations in India” had participated in rescue operations related to the 2023 train accident in Odisha, and listed several initiatives by Sewa Bharati in India. It also launched a fundraiser for families affected by floods in Maharashtra in September 2025, which mentioned that over 100 Sewa Bharati volunteers were already on the ground clearing debris and assisting communities.
“Foreign grants awarded to partner agencies in India, including service-oriented NGOs like Sewa Bharati, are strictly project-based, fully audited, and evaluated based on measurable humanitarian impact in education, health, and disaster relief,” Israni told Bellingcat.
Subscribe to the Bellingcat newsletter
Subscribe to our newsletter for first access to our published content and events that our staff and contributors are involved with, including interviews and training workshops.
RSS’ website links directly to the main website of Sewa Bharati through a tab on its main navigation bar labelled “Sewa”, and Sewa Bharati is mentioned in RSS’ 2016 annual report under the heading “Seva Vibhag”, a Sanskrit term for “service department”.
A blog post on Sewa Bharati’s website from December 2024 about an event the group organised described Indian Defence Minister Rajnath Singh as highlighting the role of RSS leaders in establishing Sewa Bharati in his address and noting that “RSS not only builds the nation but also the individual”. RSS Joint General Secretary Alok Kumar also spoke at the Sewa Bharati event, according to the blog post.
In response to Bellingcat’s queries, Israni said that Sewa USA had “no role in Sewa Bharati’s governance or operations”. Sewa Bharati did not respond to multiple requests for comment as of publication.
Sewa USA received almost $69.4 million in contributions and grants from 2020 to 2024, according to its Form 990s. Filings listing Sewa USA as a grantee show that at least $16 million was from DAFs. In its expenditure statements, Sewa USA reported giving $29.7 million in foreign grants to groups in South Asia during this period and about $622,613 in grants domestically in the US, while the rest of its expenditures included operational costs such as salaries and travel. It is not specified in the forms how much funding, if any, Sewa USA transferred to Sewa Bharati during this period, and Sewa USA did not respond to questions about any amounts transferred as of publication.
‘Cause-Neutral’ Funding
Experts told Bellingcat that there was less regulatory scrutiny of grants distributed through DAFs than some other types of charitable donations.
“For donor-advised funds, there’s actually less oversight by the IRS because donor-advised funds are considered public charities rather than private foundations,” said Samuel Brunson, a law professor at Loyola University Chicago.
“If a private foundation were giving money to organisations in India, that would be a little bit trickier. But if it’s a public charity … there’s not really a ton of oversight on that as long as the money that the US tax-exempt organisation is giving meets its charitable purpose.”
Lloyd Hitoshi Mayer, a law professor at the University of Notre Dame who specialises in non-profits, said that it was “irrebuttably presumed” that funds granted to US organisations with the non-profit 501(c)(3) tax status were being used for good charitable purposes.
“The existing federal tax laws related to donor-advised funds put some restrictions on what grants donor-advised fund sponsor organisations, which actually control the funds, can make. But the big exception is that Congress said, ‘If you make a grant to a Section 501(c)(3) charity, you’re good.’ You don’t have to do any additional oversight.”
Some DAF sponsor organisations have previously faced criticism for granting money to charities that have promoted homophobic, anti-immigrant or anti-Muslim views. Several were also criticised for pausing funding to the Southern Poverty Law Centre earlier this year, although this case demonstrated how DAFs can prevent funds from going to some groups recommended by donors, if the DAFs deem them unsuitable.
Brunson told Bellingcat that DAF sponsor organisations “absolutely have the right and ability” to halt processing donations to certain organisations. “Whether we want them to do that or not is a separate question,” he said.
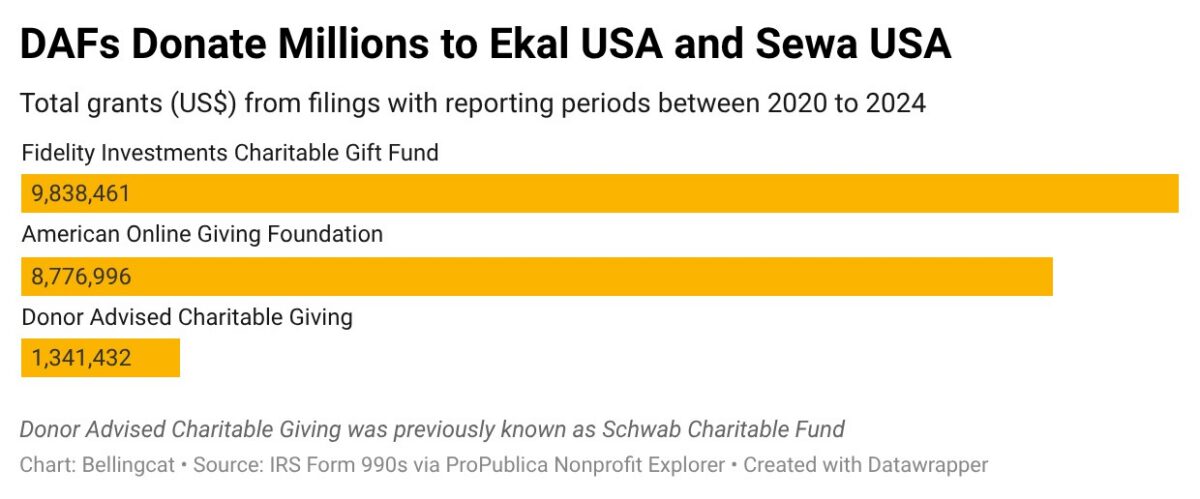
Bellingcat reached out to the top three DAF sponsor organisations that donated to the two non-profits we identified – Fidelity Investments Charitable Gift Fund (Fidelity Charitable), American Online Giving Foundation (AOGF) and Charles Schwab-affiliated Donor Advised Charitable Giving (DAFgiving360; known before 2024 as Schwab Charitable) – to ask about their internal policies on assessing charities receiving donations through their funds. In total, the three DAFs accounted for almost $20 million, or 81.7 percent, of the DAF grants to Ekal USA and Sewa International for full reporting years between 2020 and 2024.
Fidelity Charitable, AOGF and DAFgiving360 all told Bellingcat that they had due diligence processes in place when evaluating non-profits.
Fidelity Charitable’s website states that it is a “cause-neutral” charity, but it ensures grants are used solely for charitable purposes. AOGF said non-profits must comply with eligibility requirements regarding hate speech, discrimination and the use of funds.
Meanwhile, DAFgiving360 said that a grant recipient may be subject to monitoring or placed under temporary suspension “due to circumstances that DAFgiving360 deems appropriate”, such as if there is a public interest consideration or if the recipient does not further DAFgiving360’s mission.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Sign up here to receive Bellingcat’s biggest investigations by emailas soon as they are published.
Illustration by Oisín Mac Con Iomaire
On a June night in 1996, in a basement apartment in Boston’s Chinatown, a killer put a pistol to the back of a young man’s head and pulled the trigger. The victim’s body was wrapped in quilts, lowered into the trunk of a car and driven about 20 miles southwest of the city, where it was dumped in the woods. It lay undiscovered through two New England winters until a dog walked home carrying a human bone.
For three decades, authorities did not release the victim’s name to the public. He is listed in the National Missing and Unidentified Persons System (NamUs) as #UP12385, one of 202 unidentified people recorded in the state of Massachusetts. The circumstances of his discovery are reduced to five words: “Skeletal remains found in woods.” The case remains unsolved.
Bellingcat spent more than a year investigating in an effort to put a name to the victim. Using open sources, including freedom-of-information requests and newspaper archives, as well as interviews with investigators who worked on the case, we pieced together the story of the man’s life and death in an era before the internet kept a digital record. In total, we submitted 27 public records requests to 18 local, state and federal law enforcement agencies. We also contacted more than two dozen investigators, prosecutors, crime victims, journalists, experts and community groups connected to the case, though most said they did not recall the 30-year-old murder.
We learned that authorities identified the victim as Fu Chun Wang, a 26-year-old undocumented Chinese immigrant who did not speak English. We also learned of a sweeping investigation into Chinese organised crime in New England in the late 1990s. Authorities suspected Wang was a member of the Fukienese Flying Dragons, a gang the FBI described at the time as a “violent offshoot” of the larger Flying Dragons crime ring.
Fu Chun Wang’s mugshot. Source: Released by Sharon Police Department
Based in New York’s Chinatown, the Fukienese Flying Dragons were active across much of the East Coast. The gang trafficked migrants, extorted and robbed businesses, kidnapped for ransom and murdered rivals. Authorities believed Wang belonged to the Boston faction of the group, which was suspected of carrying out home invasions targeting Asian and Asian-American restaurant owners and staff across New England in 1996.
Heavily redacted FBI documents and correspondence between local and state authorities show that a federal operation investigating the home invasions uncovered information about Wang’s murder and other crimes. The operation, whose name is redacted, was led by the US Attorney for the District of New Hampshire.
Authorities suspected that the Boston-based members of the Fukienese Flying Dragons were also involved in prostitution, illegal gambling and kidnappings in multiple states. Investigators examined possible ties between the gang and a suspect in one of Boston’s deadliest mass killings: the 1991 Chinatown Massacre.
According to these newly released files, investigators received information that Wang had been murdered by members of his own gang shortly after Boston Police arrested and charged him for using credit cards stolen in one of the home invasions. While some gang members were identified as suspects and investigated, none were ever charged and convicted for the murder.
A Dog with a Bone
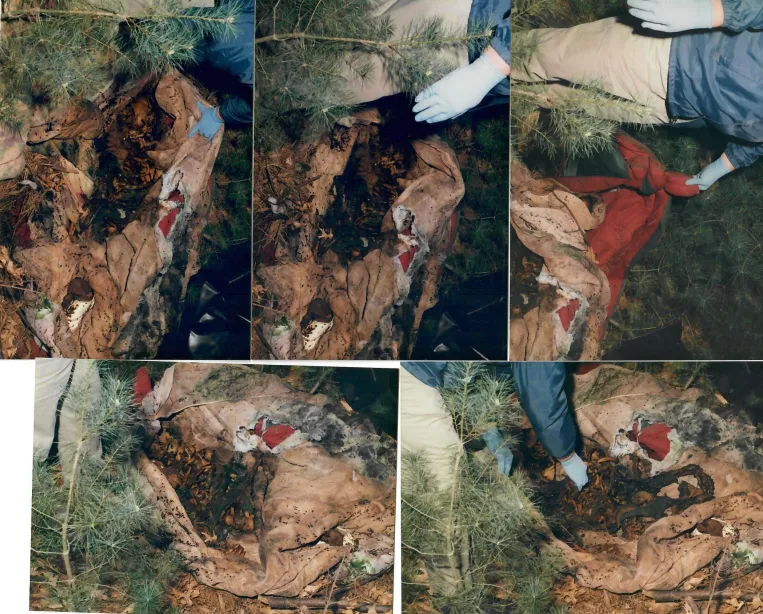
On April 10, 1998, a resident in Sharon, an affluent suburb southwest of Boston, called the police. Their black Labrador retriever had returned from the woods carrying a large bone. Four days later, testing by the coroner’s office in Boston determined it was a human femur likely belonging to an adult male. Police searched the woods, where a detective uncovered more bones near a bundle of quilts. Inside, they found a decomposed skeleton.
A coroner ruled that the victim was a man in his twenties or thirties who was possibly Asian or Native American. He had long black hair with blonde streaks. There were at least two overlapping bullet holes in the back of his skull. Local media reported at the time that the victim had been shot “execution style”. A single, corroded .380 calibre shell casing was found inside the quilt. The victim was wearing a green-and-white striped rugby shirt, denim jeans and white leather sneakers on the night he died. Loose change, a pocket knife and a tarnished set of keys were found nearby on the forest floor.
Blurred
Crime scene photos showing remains found in the woods, near the intersection of Walpole Street and Bluff Head Road, in April 1998. Source: Sharon Police Department
A botanist from Harvard University determined the body had likely been in the woods for at least 18 months. Experts from The Smithsonian Institution told police that forensic facial reconstruction would be “of questionable value” due to the damage caused by the gunshot injuries.
Before his murder, open source records of Wang’s life amounted to a few scattered data points: interactions with authorities, apartment rentals, a loan application and a hospitalisation following a car accident.
Police reports after his death show investigators pieced together a patchy collection of biographical data. He was from a family of five in Dongshan, a village in the southeastern Chinese province of Fujian, and was likely born into poverty. During his autopsy, it was noted that his teeth showed signs he had been “undernourished” as a child. He moved to the US to work in the restaurant industry and eventually joined a gang.
A January 1994 Immigration and Naturalisation Service (INS) record containing Wang’s fingerprints. Source: Released by Sharon Police Department
Wang migrated at a time when thousands of Fujianese were arriving in the US every month in search of a better life. Like many migrants at the time, he entered the country without documentation. By 1994, when Wang met with immigration authorities in Boston, he gave his address as an apartment on East Broadway in New York’s Chinatown. Two years later, he was issued an employment authorisation card. Boston Police would learn from the Immigration and Naturalisation Service (INS) that Wang had been granted political asylum.
Search results on Ancestry.com suggest that prior to living in Massachusetts, Wang had also lived in Virginia and Vermont. Records from the Sharon Police Department corroborate these findings. In Virginia, police learned that he worked in restaurants and had applied for a loan to buy a car, a 1994 green Mitsubishi Mirage.
In Vermont, Wang worked at a Chinese restaurant called Men-at-Wok until he was injured in a car accident in May 1996. After he was reported missing a month later, his car sat unclaimed in an auto body shop in Vermont until a bank sought to reclaim it.
Wang’s INS employment authorisation card. Source: Released by Sharon Police Department
Unclaimed checking and savings accounts at Fleet National Bank are listed under Wang’s name and the Quincy address in the Massachusetts unclaimed property database. The amount of money in these accounts is not publicly available, but the presence of unclaimed funds in his name, along with his abandoned car, are some of the many indicators that he met with foul play.
‘We’ll Kill Your Family’
In the summer of 1996, Chinese restaurant owners and their staff in suburban Boston and New Hampshire were terrorised by a wave of violent home invasions and robberies. Police described the suspects as “an organised group of Asian individuals”.
Composite sketches of two suspects in a July 1996 home invasion in Merrimack, NH based on witness descriptions. Source: Merrimack Police Department
The modus operandi was often the same. In the early morning hours, young men barged into rooming houses while Chinese restaurant workers slept. Sometimes they robbed the business owners’ homes. Armed with guns and knives, the intruders tied up their victims before stealing cash and valuables. One woman who was attacked at knifepoint told police an assailant threatened: “Shut up or I will kill you”. In another case, a victim was stabbed.
The assailants were described as young men or teenagers. In several cases, victims reported that they spoke Fuzhou, also known as Foochow, a language originating from eastern Fujian Province.
Jim Keating, a retired Sharon Police detective, told Bellingcat that many Asian gang extortions and robberies in the Boston area at the time were not reported. “They were all afraid of these guys, because they said, ‘We’ll come back and we’ll kill your family.’ And they would.”
In the span of a few months in 1996, similar robberies occurred in the Massachusetts towns of Bedford and Westborough, as well as Malden, a city about 10 kilometres north of Boston. These were followed by home invasions in the bordering state of New Hampshire, in Wolfeboro, Merrimack, Lebanon and Manchester. It is unclear if the home invasions and robberies were connected, but Bellingcat’s review of historic newspaper clippings and newly released police documents suggest that at least one other gang may have been responsible for some of the crimes.
In response to the crime spree, local, state and federal law enforcement agencies coordinated investigative efforts. Bellingcat obtained files detailing a federal operation led by the US Attorney for the District of New Hampshire. It included agents from the FBI, INS, Drug Enforcement Administration, Bureau of Alcohol, Tobacco, Firearms and Explosives, Customs Service, Border Patrol and Royal Canadian Mounted Police, along with officers from state, county, and local law enforcement agencies in New England.
Local media coverage of the home invasions in 1996. Source: Janet Wilson, The Boston Globe
Ben Leong, a retired Boston Police detective, said Asian gangs committing robberies, extortion and home invasions against restaurant owners and their staff were common in the 1990s. He said many of these crimes went unreported for cultural reasons, over fears of gang retaliation, and because victims did not trust law enforcement.
“Back then there were many factions of gangs,” he said. “The gang members were recruited throughout the country, nationally and internationally. Law enforcement was always playing catch up to identify the prevalent groups, and the individual members and leaders committing illegal activity.”
Leong, who is president of the International Organisation of Asian Crime Investigators and Specialists (IOACIS), said authorities had a better understanding of gang culture in Boston by around 1996 when local, state and federal agencies began sharing information.
Murdered in Chinatown
On June 9, 1996, one day after a home invasion in Wolfeboro, New Hampshire, Boston police were called to a Macy’s department store when a man tried to use credit cards stolen in the robbery to buy jewellery and electronics. He was arrested and booked on charges of receiving stolen property. The man was Fu Chun Wang.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
In Sharon Police records, Wang was described as “very depressed” and “possibly suicidal”. He told a Boston Police detective that he urgently needed to send $1,000 to his family in China. Other records said his father was ill and needed money. Files found on Judyrecords.com, a free database that purports to include more than 770 million US court case records, show that Wang was arraigned and a court appointed a defence attorney to him. He was bailed out after pleading not guilty.
Less than two weeks later, on June 21, Wang was reported missing to the Quincy Police Department in Massachusetts. The police report said Wang was last seen in Boston’s Chinatown on June 13, two days after he left jail. Police records indicate that a female friend of Wang’s had asked an attorney to file the missing persons report. The attorney who reported him missing told Bellingcat that he did not remember Wang.
The Sharon Police Department’s murder case file notes that within weeks of finding the human remains in the woods, they received information from Boston Police and the FBI that “Wang was murdered in Chinatown” in June 1996 and “his body [was] never found”.
Investigator’s handwritten notes about Wang’s case. Source: Sharon Police Department
Not all documents were released to Bellingcat, and some names were redacted. Fragmentary notes and witness statements provide the only clues to Wang’s final days. In handwritten records, Sharon Police said a man who was described as the “head of [an] Asian gang in Boston” had Wang killed over the New Hampshire breaking-and-entering incident.
A note in the Sharon Police file described a witness to Wang’s murder as a “Flying Dra” and a “NY gangster”. Retired detective Jim Keating confirmed to Bellingcat that Wang, along with his associates and killer, were suspected members of the Fukienese Flying Dragons. He said he believed Wang was murdered because he posed a risk to the gang following his arrest.
Investigator’s notes describing a witness as a gang member. Source: Sharon Police Department
Documents released by the Merrimack Police Department and Sharon Police Department said that an inmate in New York who, in 1997, was serving a 25-year sentence for attempted kidnapping, offered to share information about Wang’s murder with the FBI in return “for a reduction (sentence)”. The inmate implicated the gang in at least two 1996 New Hampshire home invasions and also gave authorities information about the murder.
The account is heavily redacted but includes a note that the US Attorney for New Hampshire was making arrangements to interview the man. Police in New Hampshire said they believed the inmate “was truthful in his statements and has knowledge about the murder of Mr Wang”. Keating confirmed to Bellingcat that he and investigators from other law enforcement agencies traveled to New York to interview the man. He said the inmate, a suspected member of the Fukienese Flying Dragons, gave a statement on Wang’s murder.
Keating said that investigators had learned of a dispute on the night of the murder between Wang and the gang’s leader. He said Wang had planned to run an illegal gambling operation at an apartment, which the gang boss was using as a prostitution venue. This led to an argument at another location, and when Wang left for the apartment the boss followed him.
But Keating said that based on the information gathered throughout the investigation, he believes the primary motive for Wang’s murder was his arrest over the use of credit cards stolen in the Wolfeboro home invasion. With that arrest, Wang presented a risk to the rest of the gang because investigators could tie them to the home invasions. “Wang broke the basic rules by taking something that was identifiable and using it, and that’s what the whole damn thing was about,” Keating said.
Crime scene photos of the basement unit on Oxford Place in Boston’s Chinatown where Wang was murdered. Source: Sharon Police Department
Keating told Bellingcat that the crime scene had been damaged by flooding after the murder. He said he used a power saw to cut off the bottom of a door in the unit and that lab testing revealed the presence of Wang’s blood.
Investigators also worked to confirm Wang’s identity by testing the DNA of the remains found in the woods. In a 1999 case summary written by a Massachusetts State Police Trooper, it was noted that the FBI was attempting to locate Wang’s parents through police in China.
Three months later, the FBI’s Hong Kong office sent a communique to Boston confirming that the Chinese Ministry of Public Security and Interpol had located Wang’s parents. Wang’s mother, it said, was willing to provide a DNA sample for comparison.
The FBI communique is the final document in the newly released files that details the efforts to confirm Wang’s identity with DNA. However, Keating told Bellingcat that a DNA sample was obtained from Wang’s mother in China. It was brought back to the US for testing and confirmed to be a match, he said. “I don’t know when the DNA was collected or who did it. But I know that they did that,” Keating said. “There is no question about who he was.”
Bellingcat contacted both the Norfolk and the Suffolk County District Attorneys to confirm the DNA match, but did not receive a response to questions about DNA testing or the victim’s identity. Other former law enforcement officers named in the files released to Bellingcat have not responded to requests for comment.
One document included in the murder file references discussions between homicide investigators and the FBI about charging Wang’s killer with home invasion offences. The note discusses the potential to have a witness testify against Wang’s suspected killer. It is unknown whether he was ever charged.
The Shooter
The man authorities suspected of shooting Wang, or ordering his killing, was described in the documents as the head of the Fukienese Flying Dragons in Boston. Police said he was an undocumented immigrant from Fujian Province who ran a sex trafficking ring.
A redacted note in the Sharon Police Department murder file references Wang’s suspected killer as “a player” in the Chinatown Massacre, an infamous 1991 case in which five men were shot dead in a basement gambling parlour in Boston. In another note in the case file, investigators wrote that he was “thought to be a federal informant”.
The name of the gang boss was redacted in the police file released to Bellingcat.
Keating said Wang’s identity was confirmed by DNA and that blood evidence, corroborated by witness statements, placed his killing in the Boston Chinatown apartment. The retired Sharon detective said at that point, the Boston Police Department and the Suffolk County District Attorney’s Office should have, respectively, taken over the investigation and prosecution of the case.
The Boston Police Department did not respond to questions from Bellingcat. It does not include the killing in its list of unsolved homicides.
The Suffolk County District Attorney’s Office said it did not have records for Wang’s murder. “Unfortunately, after a thorough search with assistance from our homicide unit, no responsive records could be located,” it said.
In response to Bellingcat’s original public records request, the Norfolk County District Attorney’s office, which covers Sharon, said the files were exempt from public disclosure because they pertained to “an active and ongoing criminal investigation”.
A spokesman for the office said last week that the circumstances surrounding the remains of an adult male discovered in Sharon in April 1998 “remain under investigation” by a state police detective assigned to the Norfolk District Attorney’s Unsolved Case Unit.
The FBI confirmed that the agency assisted state and local partners in an operation investigating home invasions in the late 1990s but did not answer questions about Wang’s murder or his suspected killer. “Given that we’re not the lead, we’ll refer you to Massachusetts State Police,” a spokeswoman said.
Massachusetts State Police referred questions to the Suffolk and Norfolk County District Attorney’s offices.
It remains a mystery why Wang’s killer was never charged and prosecuted for his murder. “They got away with so much. Blatantly got away with so much,” Keating said of the gang. “Killing people for these guys was like … these guys were all expendable.”
The Norfolk District Attorney’s Office encouraged anyone with any information about the case to contact the Massachusetts State Police Tip Line or the Sharon Police Department.
Melissa Zhu contributed research to this article.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Sign up here to receive Bellingcat’s biggest investigations by emailas soon as they are published.
Satellite images obtained and analysed by Bellingcat show over five miles of new road constructed in Big Bend National Park in southwestern Texas, part of a US Customs and Border Protection (CBP) “Smart Wall” installation, which includes roads, barriers, lighting and cameras.
The project was paused earlier this week after pushback from local residents, politicians and environmental groups.
The roads have been built adjacent to the Rio Grande, through the river’s floodplain and riparian forest, and include construction adjacent to Cottonwood Campground, Santa Elena Canyon, and Mariscal Canyon in the National Park.
Planet Labs satellite imagery captured on August 15 and August 19 shows new roads cleared through the riparian forest around the Rio Grande in Big Bend National Park.
The map above traces the new road construction in yellow. An unannotated version of the satellite image showing the new road can be found here while a before image of the same area where no road is visible can be seen here.
The new road extends to Cottonwood Campground, one of four campgrounds in Big Bend National Park.
The road can be seen crossing the riparian forest and smaller drainages before joining the campground access road. Imagery also appears to show bright yellow construction equipment staging in the campground area, where bulldozers were previously seen.
Planet Labs satellite imagery captured on August 19 shows a new road near Cottonwood Campground in Big Bend National Park. Hover to compare to Planet satellite imagery from September 2022. Note that the removal of cottonwood trees in the campground is unrelated to CBP construction activity.
In the southernmost part of Big Bend National Park, additional new road construction is also visible near Mariscal Canyon and connecting to Talley Road.
CBP planning documents indicate that this section of the border will receive a four-to-six foot tall vehicle barrier in addition to the “smart wall” lighting and camera systems. Talley Road currently provides access to riverside backcountry campsites and hiking and boating access to Mariscal Canyon on the Rio Grande.
Planet Labs satellite imagery captured on August 18 shows a new road near Mariscal Canyon in the southernmost part of Big Bend National Park.
The map above traces the new road construction in yellow. An unannotated version of the satellite image showing the new road can be found here. A before image of the same area where no road is visible can be seen here.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
CBP Commissioner Rodney Scott described the construction activities as “survey and design work” in an August 13 statement. He also stated that CBP is “building one new access road, improving existing roads, installing detection technology, and placing vehicle barriers in limited, strategic locations.”
The Big Bend Border Patrol Sector sees the fewest migrant apprehensions of any part of the US southern border, according to CBP’s own data.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Cristiano Ronaldo during Portugal’s losing game against Spain earlier this month. Source: Imagn Images via Reuters Connect
Football fans wagered more than US $14 billion on the FIFA World Cup through prediction markets Polymarket and Kalshi, a Bellingcat analysis has found.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
On the crypto-based Polymarket, which provides more information about individual trading accounts than its rival American site Kalshi, we also found that just 1% of users collected the vast majority of winnings during the tournament.
Users traded on almost 60,000 outcomes across both sites during the competition, betting on everything from the sponsor of the Golden Boot winner to whether Cristiano Ronaldo would shed a tear during a Portugal match.
The World Cup, held in the US, Canada and Mexico over June and July, was forecast to be the biggest betting event in history, with a predicted $50 billion in wagers.
Unlike traditional sports betting sites, prediction markets resemble stock exchanges where users trade, via an order book, on whether a real-world event will happen. Prices fluctuate based on what the market believes the probability of that event is. The sites charge fees on each sports trade.
With 48 teams playing 104 games, the World Cup was slated to be the biggest gambling event of all time. Source: Polymarket
The prediction market industry has faced criticism over its vulnerability to insider trading, potential market manipulation and concerns about fueling unregulated gambling. The Wall Street Journal also reported in May that a small number of individuals using algorithmic trading models were taking home an outsized share of winnings.
This would appear to align with Bellingcat’s World Cup analysis, where a small percentage of accounts made most of the winnings. However, the level of detail we were able to obtain did not allow us to see accounts that had utilised algorithmic methods.
Both Polymarket and Kalshi make events and volume data available for programmatic extraction – making it useful for open source analysis. Bellingcat’s data analysis examined all 104 matches as well as the World Cup winner event that was hosted on each platform.
On Polymarket, users traded a total of $10 billion ($5.7 billion on individual games and $4.3 billion on which country would win). The largest game on Polymarket was the Spain vs Argentina final ($212 million), followed by the France vs Spain semi-final ($165 million) and the England vs Argentina semi-final ($142 million).
On Kalshi, users traded a total of more than $4.3 billion ($4.1 billion on the games and $200 million on the winner).
Bellingcat’s analysis also found that 1% of Polymarket trading accounts collected 86% of all winnings during the World Cup, and the bottom 50% of winners shared just 0.1% of profits. The typical winning account on Polymarket made $21, while the typical losing account lost $32 (measured by the median, which is less affected by a handful of exceptionally large wins and losses). More than 12% of traders (14,500) who bet on two or more games lost every bet. The Polymarket account that won the most across all games made a profit of more than $13 million, while the biggest loser lost $11.6 million.
We were unable to run the same win-loss analysis for Kalshi because trading account overviews are not publicly available.
The top teams, by trading volume, across both sites were Argentina ($1.068 billion), Spain ($876 million) and France ($836 million). The top players were Argentina’s Lionel Messi ($40 million), France’s Kylian Mbappé ($36 million) and Norway’s Erling Haaland ($16 million).
How We Calculated the Volume
Polymarket displays the actual traded volume on its site, the total US dollar amount of shares bought and sold since the market started.
Kalshi does not display the traded volume. Instead, it shows the notional volume, which counts every contract traded at the maximum payout value of $1. This means that a token bought for $0.20 will be presented as $1 extra in a user’s displayed volume. This makes the total monetary volume appear higher on Kalshi’s website. To achieve a fair comparison between both platforms, we implemented a heuristic to reconstruct Kalshi’s markets’ volume. We used the daily average price for each market over their duration and multiplied it by the number of contracts traded on that day, the sum of which gives us the values used in this piece. We applied this formula for the more than 21,000 World Cup markets.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
This investigation is a collaboration between Bellingcat and New Zealand news site The Press. You can read The Press’ piece here.
Content warning: This article discusses non-consensual sexually explicit content and child sexual abuse material.
In 2024, a former track and field coach in Boston, Massachusetts, was sentenced to five years in jail for attempting to trick and extort more than 100 women, including student-athletes he coached, into sending him intimate photos.
According to the 2021 criminal complaint, Steve Waithe stole photos from some of the student-athletes’ phones under the pretence of “filming their form” at practices and meets. He also approached some victims via fake online accounts, telling them he had found their images on a forum site called “leakedbb.com” (“LeakedBB”) and offering to help them remove these photos if they provided more images for “reference”.
Authorities said Waithe also hired and paid another man in October 2020 to hack into the Snapchat accounts of women he coached or had other relationships with in an effort to steal and distribute nude images online.
In one post, according to the US Attorney’s Office, Waithe wrote: “Does anyone want to trade nudes? I’m talking girls you actually know. Could be exes or whatever. I have quite a few and [am] down to trade over snap[chat] or something.”
Legal documents do not name the sites on which Waithe distributed these images, but Bellingcat found a cached version of a November 2020 post with that exact wording on LeakedBB – the same site he allegedly used to try to trick victims. Another cached LeakedBB thread posted a few months later shows the same user offering to trade nudes of athletes, including “a lot that I actually know”.
Screengrab from LeakedBB, showing a user asking to trade nudes of “girls you actually know”; redaction by Bellingcat
Such posts were not unusual on the site: multiple archived pages show the forum’s users either requesting Snapchat hacks or offering to help others hack Snapchat accounts, sometimes for a fee.
In the criminal case against Waithe, the ownership of LeakedBB is never discussed, but a Bellingcat investigation can reveal that payment streams, company records and website domain information appear to lead back to one individual: Jitendra Maharaj, a Christchurch-based former pilot and co-founder of a cryptocurrency start-up, Pay It Now (PIN), which reportedly billed itself as the “Stripe of crypto payments”.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
Our New Zealand publishing partner The Press sent an email to Maharaj on June 4 outlining our findings in detail and inviting him to respond. Maharaj did not reply to this.
However, by June 6, LeakedBB was down. As of publication, the website remains inaccessible.
The Press later received an email from a Christchurch-based lawyer representing Maharaj, who said their client was in Fiji for a family member’s funeral. The lawyer requested that we wait until his return on June 23.
When The Press visited his residence – a two-storey family home in Christchurch’s affluent Aidanfield suburb – on June 25, Maharaj said he did not know who was behind LeakedBB or operated it and that he was not sure if the website was down.
He said he did not respond to the email queries and had not spoken to his lawyers about them because “all the evidence against me just sounded really weird” and it seemed like there was “some kind of targeted attack out on me” based on “manufactured evidence or something that’s pointing me to this garbage”. However, he refused to comment on the record about most of the specific evidence linking him to the site and referred these questions to his lawyer.
He also claimed that he had been contacted by people “trying to harass me to get me to send them money”, but declined to provide details on the record.
Jitendra Maharaj at the entrance of his residence on June 25, 2026. Source: Iain McGregor/The Press
Despite a further extension of the deadline until July 6 – more than a month after we first reached out – Maharaj and his lawyer had not provided any statement directly addressing the specific evidence linking him to the site as of publication.
PIN, the company Maharaj co-founded, did not respond to The Press’ requests for comment. However, there is no suggestion that PIN has any knowledge of or involvement in LeakedBB.
Profiting Off ‘Leaks’
LeakedBB was set up in 2019 and built a sizeable following over the next seven years, averaging an estimated two million visits a month from March to May this year. The board statistics shown on LeakedBB’s homepage in May displayed 2.2 million registered users and more than 2.6 million posts.
Screengrab of the board’s statistics as of May 26, 2026; personal information redacted by Bellingcat
Google’s Transparency Report shows it received more than 95,000 individual requests for over 350,000 pages on LeakedBB to be delisted from search results. This resulted in Google de-listing more than 169,000 pages from its search results, according to the report.
Shortly after the site went offline, a Reddit post noting the outage and asking for alternatives trended in the “hot” section of a piracy subreddit, accumulating almost 700 votes in a week. In response to a question by one commenter asking what the site was, another person replied: “Not only did it have ‘onlyfans’ content, also amateur, asian, arabic, celebrity and other hacked phone/icloud content from other sites.”
This comment accurately summarised some of the content on the site. In LeakedBB’s early days, it had sections for other types of “leaked” content such as computer programmes and eBooks. But within months, the forum’s discussions were almost exclusively about pornographic images and videos that members claimed had been leaked – implying that it was non-consensual, hacked or stolen content.
The most popular section on the forum contained content that claimed to be from sites such as OnlyFans and Fansly, which, if shared without the original creators’ consent, would be a violation of their intellectual property.
Reba Rocket, co-owner and chief operating officer of Takedown Piracy, a company that helps both adult performers and private individuals remove non-consensually shared explicit media, said sites like LeakedBB cause financial harm to legitimate content creators.
“People would not shove a DVD into their coat pocket and walk out of the store – that’s something tangible that they know they’re doing something wrong, whereas watching something on the internet for free doesn’t have that same connected moral,” she said.
Other sections on LeakedBB featured threads requesting or promoting content that often appeared to show women who did not have anything to do with the adult industry, which the posts claimed were leaked, hacked or even obtained through blackmail.
One post advertised images of girls from 29 US states: “There’s names and Facebook information if you want that,” the member, “Master Leaker”, posted. “There’s also two girls that got blackmailed into sending more nudes as well!”
LeakedBB user advertising a large file of “girls from 29 different states”; personal information redacted by Bellingcat
In the “Requests” section, users shared clothed images of women or social media handles of potential victims, and asked if others had leaked content of them. In one recent post looking for a “Florida Milf”, a user wrote: “She may go by the name [redacted]. Looks like the daughter graduated from [redacted]. Anyone have content of her? Sex tapes?”
Some users also posted nude or intimate images of women they had found elsewhere, asking for help finding out their real identities. “Who is she?” or “Can anyone ID?” were some common questions in the posts.
Non-consensual intimate image sharing (NCII), colloquially referred to as “revenge porn”, is far from new. It is a known problem on Reddit, where, in 2022, a BBC investigation found “thousands” of such images being shared despite the platform’s attempts to crack down on the issue.
LeakedBB, however, seemed to take the opposite approach: instead of trying to moderate or prevent users from posting what appeared to be NCII, it sought to profit from and reward it.
Except for preview images, most of the content users shared in the “leaks” section was behind a paywall and could only be accessed with memberships costing up to US$99.99 or by redeeming credits.
The site rewarded members with credits for posting “leaked” content, as well as when other members spent credits to “unlock” their content. These credits could be used to access links that users could otherwise only view with a paid upgrade, or redeemed for cryptocurrency at varying rates (the most frequent contributors had the option to cash out the equivalent of up to $0.15 for each thread they posted).
There was also an annual Christmas contest, with last year’s total prizes worth over $4,000 in cryptocurrency for users who posted or liked the most threads.
Screengrab of a forum announcement on LeakedBB posted on Dec. 7, 2025.
Rocket said LeakedBB had “damaged many people”, including clients of her company. “Those specific clients are not in the adult industry,” she said, “but LeakedBB seemed more than happy to share their non-consensual content”.
The “leaks” were often posted with women’s purported real names, locations and social media accounts, as well as preview images showing their uncovered faces. One poster said sharing a woman’s social media details “adds to the experience”.
“For me, it makes my jerk-off sesh feel more personal, as if she’s an actual person I know rather than a moviestar/pornstar,” the post said.
Screengrab of a post where a LeakedBB user shared content of a woman, including her socials; personal information redacted by Bellingcat
There were more than 80 responses to this thread, mostly thanking the original poster for sharing the content. One of them, however, claimed to be the woman shown in the images: “Please remove this link. These photos were illegally stolen from me. This constitutes revenge porn and violates US law. Police are already involved. Not only is it illegal but just gross.”
Allison Mahoney, the founder and managing attorney at ALM Law in New York and Colorado, told Bellingcat she received calls about cases involving NCII “all the time”.
“It kind of amazes me, given the amount of media attention this has gotten over the years, that people are still engaging in this type of abuse so cavalierly,” said Mahoney, whose firm specialises in providing legal services for abuse survivors and children harmed in welfare systems.
Mahoney and Rocket agreed that sites sharing NCII often had real-world implications for victims, especially when images were posted alongside personal information, including names, contact information and professions.
“We have clients who … their children were kicked out of Catholic school, or they lost their mainstream job, or relationships ended, or families cut them off simply because content was posted online without their consent and viewed by others,” Rocket said.
Mahoney said online abuse can turn into offline abuse when victims have their personal information, like their name, profession and contact information, posted with their images. She has seen clients who had strangers show up at their homes or places of work, threatening their physical safety – a situation she said was “really terrifying”.
In July last year, LeakedBB closed a marketplace it had hosted for more than five years, which allowed users to sell leaks and services to each other. Lucifer NightStar, the administrator account on the site, said there were allegations of people selling “UA [underage] material”, which was “not something we want on [LeakedBB]”.
Screengrab of a post where Lucifer NightStar explained why the marketplace section had been shut down.
On one section of the forum, which was specifically for sharing content from other sites that hosted leaked pornographic content, LeakedBB had a disclaimer: “Please note that posting any content on any one below the legal age of 18 is against the law. We have a zero tolerance policy on such things and your account will immediately be banned / reported.”
But this warning did not appear on other sections of the forum, including those featuring threads of “amateur nudes” described as having been leaked. Some threads on the forum, which remained accessible shortly before the entire site was taken down, also described images of “young teens”.
While it is not known if those descriptions are accurate, in a recent post on Reddit a person asked for help taking down non-consensual photos they said were taken when they were a minor, hacked from Snapchat, and posted on LeakedBB, among other sites.
“I am in school to become a teacher and searched my name on google. If you go down a bit these websites come up,” they wrote. “I am so devastated and can’t believe this has happened to me.”
While speaking to The Press outside his residence on June 25, Maharaj said that when it came to publishing non-consensual pornography and child sexual abuse imagery, “It should be obvious anyone’s against that.”
Who Is Lucifer NightStar?
Lucifer NightStar was the username for the only account with the title of “Administrator” on the LeakedBB forum. This user posted FAQs for the site and almost every forum announcement throughout its history.
The URL of this account’s profile page shows the user ID (UID) of “1”. According to documentation for MyBB, a free and open source forum software that LeakedBB has credited for powering the site, the first user of the forum is assigned the UID “1” and has super administrator privileges – meaning their account cannot be deleted, banned or otherwise altered by regular administrators.
While the profile did not state the user’s location, it did show a local timestamp based on the user’s timezone settings, which matched GMT+12 – a timezone used in several countries in Oceania, including New Zealand and Fiji.
Lucifer NightStar’s recent posts generally avoid mentioning non-consensual intimate imagery, focusing on administrative updates and issues, troubleshooting and the annual Christmas contest. However, in the first few months of the forum’s existence, the user posted a thread with a “LeakedBB Exclusive” of “leaked Kiwi girls”.
One of Lucifer NightStar’s first posts on LeakedBB, sharing content described as “leaked Kiwi girls”.
In another discussion thread from 2020, Lucifer NightStar vouched for a user’s ability to “influence” another member’s ex-girlfriend to share nudes.
(Top) LeakedBB user offering their services to obtain nudes from another user’s ex-partner; (Below) A response from Lucifer NightStar vouching for this user being a “premium collector”. Personal information redacted by Bellingcat
Maharaj did not respond to The Press and Bellingcat’s question about whether he was Lucifer NightStar. However, one of the administrator’s posts led us to a clue pointing to Maharaj’s possible connection with LeakedBB.
Logica Ltd and MyBBplugins
In one post in May 2021, responding to a user reporting problems paying with Apple Pay, Lucifer NightStar shared a screenshot of what the payment screen should look like. A company name was visible in this image: “Logica LTD”.
Screenshot of a forum post by Lucifer NightStar on how to pay for a premium upgrade for LeakedBB using Apple Pay, showing the company name “Logica LTD”.
New Zealand company records show that Logica Limited was registered by Maharaj in February 2021, just months before this post. The company address is also in Christchurch, where Maharaj lives.
(Note: This is a different company from Logica Partners Limited, based in Auckland, which has no apparent connection with Maharaj or LeakedBB and is unrelated to this investigation.)
The records from the New Zealand Companies Office show that Maharaj has been the sole director of Logica Limited since its incorporation. He stated on his LinkedIn profile that he was self-employed as the CEO of Logica NZ from May 2020 to August 2021.
(Maharaj’s LinkedIn profile appears to have been deleted between June 13 and June 15, after The Press and Bellingcat’s initial enquiries and during the period his lawyer said he was in Fiji attending a family member’s funeral.)
Left: Screengrab of Jitendra’s work history from LinkedIn; right: Company registration information for Logica Limited (redaction by Bellingcat). Sources: LinkedIn, New Zealand Companies Office
But that was not the only connection to Logica Limited. On May 4, 2022, a YouTube user with the display name “LeakedBB” uploaded a video on how to pay for memberships on the site. This video was also embedded on LeakedBB’s homepage.
The video showed how users could pay by credit card. When they clicked to purchase a membership, LeakedBB would redirect them to another website to buy a digital avatar pack with a price corresponding to their selected membership tier.
After purchasing this “referral product”, users were encouraged to leave a comment and a positive rating to receive an “extra bonus month”. Archived versions of the website show view counts in the tens of thousands for some of these avatar packs.
The thumbnails of the “digital avatars” as well as their price and description, as shown in the video, were identical to those shown on the archived version of a site, logica.nz, which is recorded as Logica Limited’s website on OpenCorporates. This site also lists “Logica LTD” in its copyright information at the bottom of its landing page.
(Bellingcat last accessed a live version of the video on June 15. By July 1, we noticed that the video had been removed by the uploader.)
Left: YouTube video on how to purchase upgrades on LeakedBB. Right: Archived purchase screen of the same avatar pack on Logica.nz
In a forum thread on LeakedBB dedicated to explaining alternative ways to pay for membership, hundreds of users posted that they had just purchased the “Mystic Avatar Pack” or the “Pixel Avatar Pack” to gain access to the site. One user included screenshots of their purchase, showing the site URL to be “logica.nz”. Other users also stated that they had made the purchase on this website and were waiting to receive their upgrades.
Shared screenshot from a LeakedBB user who purchased a “Pixel Avatar” pack in exchange for membership, showing that they left a comment, like other users, on the purchase page on logica.nz. Personal information redacted by Bellingcat
This website’s landing page now displays only a note stating that it is under maintenance. However, according to archives captured by the Internet Archive, it was still selling “digital avatar packs” in March 2025.
This type of payment structure not only conceals the nature of the transaction from the payment processor (as non-consensual content violates most platforms’ terms of service), but it also hides the transactions for the user, as payments are not described as being made to “LeakedBB” on bank statements.
When asked about the links between LeakedBB and Logica Limited, Maharaj only told The Press at the doorstep interview on June 25 that “Logica was my company. I cannot say what happened there right now”.
According to the New Zealand Companies Register, Logica Limited is in good standing, with its most recent annual filing submitted by Maharaj in March 2026.
The Domain Name System (DNS) records of LeakedBB revealed another connection that seems to point back to Maharaj. Using online investigations tool DNSlytics, we viewed DNS records for the website and found that in 2020, the MX (mail exchange) record for LeakedBB.com was set to LeakedBB.net. An MX record is the mail server set up to accept emails for that domain. For LeakedBB.com, this was later changed to ProtonMail.
While the WHOIS ownership of LeakedBB.net is obscured, we found it on a list of sites that had DNS certificates issued by another site, mybbplugins.com. A DNS certificate is used to prove ownership of a domain and requires an administrator to validate that certificate.
According to WHOIS records from cyberthreat intelligence platform DomainTools, mybbplugins.com was publicly registered to Maharaj from December 2011 to February 2019, after which the registrant information was redacted.
The same site also issued a DNS certificate for a domain bearing Maharaj’s name (jitendramaharaj.com) as well as two domains that include part of his first name, jit-pay.cc and thejitshow.com. DNS certificates for these domains were issued between 2016 and 2021, according to free Certificate Transparency monitoring site crt.sh. Both “leakedbb” and the domain names linked to Maharaj’s name (i.e. “jitendramaharaj”, “jit-pay” and “thejitshow”) were also used as subdomains for mybbplugins.com, records from DomainTools show.
Another link appeared when we inspected the code of the oldest saved archive of the payment screen on LeakedBB, from November 2019, which showed a ProtonMail address associated with the PayPal form at the time with a string of seven digits as the username.
This string of seven digits is an exact match for what appears to be part of a Fiji-based phone number listed on WHOIS records for websites registered to Maharaj’s name including mybbplugins.com, from 2008 to 2011. It is unclear whether Maharaj was using this phone number in 2019, by the time LeakedBB was set up, and a different Fiji-based phone number was used with his name when the registration for mybbplugins.com was renewed in 2016.
Top: The archived HTML code for LeakedBB’s payment page, with a ProtonMail email linked to its PayPal account. Bottom: The WHOIS domain registry for mybbplugins.com, registered to Maharaj in 2011, with a phone number matching the digits to the ProtonMail email. Graphic: Galen Reich
Explore some of the links between Maharaj and LeakedBB:
Graphic: Galen Reich
From MyBB to LeakedBB
Bellingcat also found several other apparent connections between Maharaj and other applications hosting adult content.
An account with the username “Jitendra M.” has been posting on the MyBB community forum since 2008, with the account ID originally using the username “Darkmew”. An archived capture of this account’s profile information showed a date of birth and a location in Fiji.
This date of birth matches the one listed on a Facebook profile Bellingcat found under Maharaj’s name. His LinkedIn profile also shows that prior to moving to Christchurch, he worked in Nadi, Fiji, and he has listed addresses in the city for some of the domains registered to his name, as well as an email with a Fijian domain. This user also mentions that they are a pilot.
Jitendra M.’s profile bears a “former staff” label, indicating that he used to work for MyBB. A previous commit (save) of a file containing details of MyBB team members shows that the full name associated with this account’s user ID and username was “Jitendra Maharaj”, and his website was listed as jitendra-maharaj.com.
Archived versions of this site show photos and details that match those from Maharaj’s public social media profiles and interviews. For example, a 2011 capture shows that he mentioned being a pilot at a company called Pacific Sun. Pacific Sun was later rebranded as Fiji Link, and Maharaj’s LinkedIn profile, before it was deleted, stated that he worked for Fiji Link from 2009 to 2015. A blog post on the site also refers to mybbplugins.com as the author’s “newest endeavour”.
Left: Archived profile of “Darkmew”’s profile on MyBB; Right: Screengrab of information from a Facebook profile under Maharaj’s name, which has either been made private or deleted as of publication.
Very shortly after joining the MyBB community forum in Feb 2008, Jitendra M. asked about using MyBB for “warez” (an internet slang term for pirated digital content) and/or adult content. He stated that he was “interested in using it for a [sic] adult forum”.
During this time, he also posted asking about streaming videos from a server and how to use a PayPal account without a credit card for “people putting money into my account for services I provide”. In late 2008, Jitendra M. purchased a web domain, reaperscrypt.info, which Wayback Machine archives show hosted pornographic content while it was online in 2009. This domain was publicly registered to Maharaj from November 2008 to January 2010.
In 2013, he posted about selling the mybbplugins.com domain. However, as previously mentioned, Maharaj’s name was still publicly registered as the owner of the domain until February 2019, when registration data was redacted.
Top: Post by Jitendra M. about using MyBB for warez and adult sites using MyBB; Bottom: Post about selling mybbplugins.com
Bellingcat was able to view Facebook and Instagram accounts under Maharaj’s name and showing his profile picture in early May. These accounts painted a picture of a family man, with his public photos mainly showing his wife and children. His Facebook account had been either deleted or made private by May, and his Instagram account, while still active, has not been updated since 2013.
Archives of an X account using the same username as Maharaj’s Facebook and Instagram accounts also show several posts from November 2019 promoting LeakedBB.
Archived tweets from an account, using the same username as what appeared to be Maharaj’s former Facebook and Instagram accounts, which posted links to LeakedBB in November 2019. Personal information redacted by Bellingcat
The “Darkmew” username that Jitendra M. originally used was also used for a GitHub account which hosts a repository described as the “official repository for Pay it Now – PIN Token”. This account, which now redirects to an account with the username “JitMaharaj”, has also forked (or copied) two apps created by other people: one to create a subscription platform “like onlyfans.com” that uses cryptocurrency for payments; the other designed to scrape and report illicit content from LeakedBB.
Screengrabs from the “JitMaharaj” GitHub account, which forked repositories for an application designed to create a platform “like ‘onlyfans.com’, and another to report illicit content from LeakedBB.
These forked repositories were among 38 visible on JitMaharaj’s account on June 17, but by July 1 – after a June 22 query from The Press asking Maharaj whether he owned this account – there were only 25 repositories listed on this account. The two repositories mentioned above were among those removed.
Maharaj did not respond to questions about whether he owned any of the accounts or domains mentioned in this section.
‘Hiding Behind Screens’
Mahoney said that successfully removing clients’ images from platforms like LeakedBB was a time-consuming task. “Some sites, usually the sites hosted overseas, will just ignore the request and won’t take them down,” she said.
In the US, which accounted for almost half (40 percent) of LeakedBB’s web traffic in May, the Take it Down Act recently came into effect. The new federal law requires platforms to quickly remove non-consensually shared intimate imagery when it is reported.
However, there has been little discussion of the law on LeakedBB. One user asked in the “Help” forum how this act would affect the site and its members back in October 2025, but Lucifer NightStar never responded to this post.
LeakedBB user asking about the Take It Down Act
Rocket said having content removed for her US-based clients could be difficult when the platforms were based overseas: “A lot of it depends on where the platform is hosted, who runs their ad network and who is monetising – who their payment processors are,” she said.
LeakedBB accepted cryptocurrency payments through NOWPayments, a cryptocurrency payments gateway based in the Netherlands and Estonia. The purchase page for its subscription plans, which allowed users to gain unrestricted access to the site, redirected to a NOWPayments purchase screen to transfer cryptocurrency to LeakedBB.
In response to questions from Bellingcat, NOWPayments confirmed that LeakedBB’s activities violated its terms of service. The payments provider said it had deactivated LeakedBB’s account and blacklisted the platform immediately, as of June 4.
LeakedBB did have a form for people to request that their content be taken down under the Digital Millennium Copyright Act (DMCA), a US copyright law. However, this required victims to submit personal information such as a physical address and a business email address, and stated that it would reject requests that used email addresses from free services like Google and ProtonMail. Such details appear to go beyond those required for DMCA takedown requests on other sites: for example, Google only requires a first and last name, and an email address from any domain.
In one Reddit thread discussing the difficulty of removing content from LeakedBB under the DMCA, someone commented: “Some of this seems fairly standard, some of it seems like it’s designed to make people not request a takedown for fear of doxing [sic] themselves.”
On the page to submit DMCA takedown requests, LeakedBB also stated that successful requests would lead to them removing content hosted on their servers, but not links to third-party hosting providers – which is how a large portion of the content was made available to the website’s users.
In New Zealand, where Maharaj is based, posting intimate imagery without consent is illegal under the Harmful Digital Communications Act. People face up to two years imprisonment or a fine up to NZ$50,000 (US$29,200), while for a company, the fine can be as high as NZ$200,000.
Netsafe is the only approved body in the country that handles complaints under this act. The agency’s chief online safety officer Sean Lyons told The Press that the law was quite novel and other jurisdictions were “envious” when it was enacted – it was able to respond to generative AI technology that didn’t exist when it was written, and gave New Zealand courts powers to issue takedown orders, even in other countries.
Still, Lyons said the law had its limitations: it was mostly intended for use where one individual was harming another, and if the responsible party was overseas, the law’s efficacy largely relied on responsible platforms doing the right thing.
“There are times when within our process, we will have contacted platforms or hosts and they will have said, ‘Who the heck are you?’…[Or] ‘We know what we’re doing, we are quite comfortable with what we are doing, and we don’t give a stuff about what it is that you are telling us, or about New Zealand law, or about the harm.’”
Mahoney and Rocket agreed that current laws were limited in their effectiveness against sites like LeakedBB.
“The fact of the matter is there are places where … until there is an enforceable international law, that content is going to be available forever, which means there is a risk of it being shared forever,” Rocket said.
Mahoney said image-based abusers have also become more sophisticated over time: “Technology is advancing, and the law is always playing catch-up,” she said.
But she suggested that identifying those responsible for the abuse could have a deterrent effect: “The anonymity that people have hiding behind screens really contributes to this and emboldens people to act in ways that are very abusive to people.
“If people understand that there’s a risk that their identity and their bad behaviour will be revealed, the hope is that it will curtail some of this and dissuade people from engaging in this type of conduct, which is so, so harmful to the victims.”
If you are a victim or know anyone who is affected by image-based abuse, resources and support are available through StopNCII.org.
Galen Reich and Melissa Zhu from Bellingcat and Michael Wright from The Press contributed to this article.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
In high school, Ashley Delgado dreamed of becoming a doctor and one day buying her father a Rolls-Royce. “She wanted to heal people,” said her father, James Taylor. She had a high GPA, Taylor added, and did especially well in science and Latin.
In her mid-20s, Ashley suffered a leg injury and was prescribed OxyContin. The painkiller marked the beginning of a yearslong descent through addiction — from prescription opioids to methamphetamine, then heroin, and finally, fentanyl.
With her family’s support, Ashley spent time in a rehabilitation facility in her hometown of Cleveland, Ohio, and in recovery she moved into a sober living home. But on an early summer morning in 2023, Ashley’s body was found on a dead-end street just outside the city. One sandal was missing. Tucked inside her bra was a folded scrap of paper containing a tan powder. She was 29.
Ashley Delgado died in August 2023. Source: Supplied
“I have lost my father, my grandmother — that hurts,” Taylor said. “But when you lose your child, that’s the worst thing on the planet, because they’re not supposed to go before you.”
Toxicology tests would later show a mix of substances in Ashley’s system, including protonitazene and metonitazene, powerful synthetic opioids from a little-known class of drugs known as nitazenes. Her death was ruled accidental.
Before his daughter’s fatal overdose, Taylor had never heard of nitazenes. Developed in the 1950s as potential painkillers, the drugs never reached the market because they were deemed unsafe for medical use. He was shocked to learn they could be up to 40 times more potent than fentanyl and 500 times stronger than heroin.
Nitazenes are predominantly sold online, both on the clear web and dark web, and are often laced into other substances to increase their potency. Experts say this puts unsuspecting users seeking more common drugs, such as oxycodone, fentanyl, or stimulants like cocaine, at risk of fatal overdoses.
Left: Ashley, aged about 5, with her father James Taylor in Cleveland, Ohio. Right: Ashley and her dog, Gucci, after graduating from high school in 2012. Source: Supplied
The US Drug Enforcement Administration (DEA) started tracking nitazene-related seizures around 2014, but it wasn’t until 2019 that it saw a marked increase. Since then, federal authorities have scheduled dozens of nitazenes as illegal substances, launched undercover operations, filed indictments, and imposed tariffs on China, where many of the laboratories manufacturing and supplying nitazenes and fentanyl are known to reside.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
Yet, figures provided to Bellingcat by the United Nations Office on Drugs and Crime (UNODC) show the United States has reported 26 different kinds of nitazenes since 2019 — the second highest number globally, after Canada.
And data from the Centers for Disease Control and Prevention (CDC) on nitazene-involved overdose deaths suggest that cases continue to rise. More than 1,100 fatalities have been confirmed through the CDC’s State Unintentional Drug Overdose Reporting System (SUDORS), but experts believe the number of Americans who have died from them since 2019 could be as high as 2,000.
Alex Krotulski, the director of the Centre for Forensic Science Research and Education in Pennsylvania, told Bellingcat that deaths are underreported because nitazenes were not routinely tested for.
“There are only limited forensic toxicology labs that test for nitazenes, so if a nitazene was present and the lab didn’t test for it, the number wouldn’t appear in SUDORS,” he said. “Also, for labs that do test for nitazenes, they have missed cases prior to their testing.” The most recent years for which there is CDC data, 2023 and 2024, show they were the deadliest, with 747 confirmed deaths.
A Bellingcat investigation last year found more than 1,000 nitazenes advertisements populating online marketplaces, forums and the dark web. Source: Bellingcat
In this months-long open source investigation, Bellingcat combed through dozens of criminal court proceedings, filed national, state, and county-level Freedom of Information requests, and obtained scores of medical examiner reports to produce the most detailed account yet of how nitazenes are infiltrating US borders and destroying lives.
The investigation found that, despite efforts to curb their spread across the country, nitazenes are proliferating online. It also shows that, by the time nitazenes reach American users, they are almost always mixed with several other drugs, including methamphetamines, cocaine and, most notably, fentanyl.
As of this year, 48 of 50 US states have reported nitazene seizures.
Less Fentanyl, More Nitazenes
Fentanyl is by far the biggest opioid killer in the US. With more than a quarter of a million deaths since 2021 and about 200 fatalities a day, fentanyl is one of the country’s most urgent public health crises. But drug experts warn that nitazenes can be even more potent and are being mixed with fentanyl and other substances, creating increasingly lethal combinations.
The Faces of Fentanyl memorial exhibit, at the DEA’s headquarters in Arlington, Virginia, displays more than 7,000 photos of people who have lost their lives to fentanyl poisoning or overdose. Source: DEA
“We’re always concerned about fentanyl being mixed in with other drugs — cocaine, meth, heroin,” said Frank Tarentino, Associate Chief of Operations for the DEA’s Northeast Region. “You add nitazenes to that and it makes it exponentially more dangerous and frightening for drug law enforcement, parents, caregivers, educators, and the young.”
Data obtained from the DEA’s National Forensic Laboratory Information System (NFLIS) show reports of confirmed seizures of nitazenes rising sharply — from 43 positive tests in 2019 to almost 2,000 in 2024 (the most recent year for which figures are available). By March this year, more than 8,000 nitazene reports had been recorded since 2019. But experts said that not all laboratories can test for nitazenes — which come in many forms including powders, pills, and sprays — and many don’t feed into the NFLIS system, meaning these numbers are almost certainly an underestimate.
We asked the DEA for a breakdown of reports of nitazenes by state. Ashley Delgado’s home state of Ohio stands out. NFLIS data from 2019 to 2024 indicate that more than a third of all positive nitazene laboratory reports nationally are linked to Ohio.
Separate data from the CDC shows Ohio has also recorded the highest number of nitazene-related overdose deaths in the US since 2021. In 2020, there were just four fatalities linked to the drug; in 2021 that number rose to 90. Between 2022 and 2024, according to government data, there were 200 more deaths.
“It is a risk to our community,” said AmandaLynn Reese, chief programme officer at Harm Reduction Ohio, a non-profit that supports people who use drugs. “There’s been several instances of nitazenes being reported within the community, and I think we’re going to see more of that, especially as we’re seeing less fentanyl.”
To learn more about what was happening in Ohio, Bellingcat filed a public records request for county-level figures to the state’s Bureau of Criminal Investigation (BCI). The data shows that the counties of Scioto, Butler and Cuyahoga — areas long affected by the opioid crisis — account for almost half of all nitazene detections across the state, by weight.
In the 2000s, Portsmouth in Scioto County became known as the “pill mill capital” of America due to widespread overprescribing of opioids. More recent data continue to show Scioto with one of the highest rates of drug overdose deaths in the state. In Cuyahoga County, which includes Cleveland, drug-related mortality rates tripled the national average in 2022.
Two years ago, Ohio’s Governor Mike DeWine issued executive orders to schedule nine different nitazenes and legalised the use of tools to test for drugs including nitazenes.
The reasons why Ohio has been so hard hit are still not fully understood. “Ohio’s geography has long been a suspected contributing factor,” said Erin Reed, director of RecoveryOhio, a statewide initiative coordinating Ohio’s response to addiction. The organisation cited a 2001 article pointing to Ohio’s unique geographic and infrastructural features — including vast land, air and sea transportation networks — as key reasons for the state being a hub for drug trafficking.
Local organisations like Harm Reduction Ohio are pushing for more drug-checking services, education, and greater accessibility to testing strips and life-saving medications like Naloxone, a drug that is used to reverse an opioid overdose. “People are going to use drugs,” Reese said. “We don’t know the supply, but those are ways you can engage in your drug use to increase safety and reduce harm.”
Dealer’s Choice
Bellingcat obtained medical examiner reports from Cuyahoga County for all nitazene-related deaths in 2023 and 2024, which provide an insight into how the drugs are being consumed. The autopsy records show that 45 people — 31 men and 14 women aged 29 to 72 — died after taking nitazenes over the two-year period. Among them were university graduates and former athletes, an Army veteran, an ironworker and an addiction counselor.
Just before Christmas in 2024, a young man from Cleveland died after taking drugs that included etonitazene. A couple of weeks earlier, the body of an elderly woman was found in her home after she ingested drugs that included metonitazene and protonitazene. In the summer, a mother of two children in her thirties consumed a similar lethal mix. All except one of the 45 deaths was ruled accidental.
And in every instance, nitazenes were detected alongside fentanyl, and often with a cocktail of other drugs such as heroin, cocaine, methamphetamine and benzodiazepines. The reason for this wide variety, Tarentino, the DEA agent said, is that dealers often mix nitazenes into other drugs to make them more powerful and addictive, and ultimately to give them a competitive edge.
“It becomes a brand,” he said. “The unfortunate circumstance that we find ourselves in is that the dealer’s choice becomes a deadly decision.” Not only are these mixtures deadly — they can also be highly profitable.
“We used to see organisations that were predominantly selling and transporting cocaine or just heroin or just methamphetamine,” Tarentino said. “Now, we’re seeing organisations move coke, heroin, meth, fentanyl, pills, powder – everything. So we see these poly-drug organisations, and then we see these poly-drug mixtures.” Source: DEA
Court records analysed by Bellingcat show nitazenes have been sold at prices ranging from roughly US $4,000 to $12,000 per kilogram. But Tarentino said the DEA’s internal estimate puts $12,000 at the lower end of the range, with prices going up to as much as $40,000. Given their potency, even small quantities can be diluted into hundreds of thousands — or potentially millions — of doses once mixed and pressed into pills. “A little bit can go a long way,” Tarentino said, “and they can make a lot of money.”
A Freedom of Information Act request to the US Customs and Border Protection (CBP) revealed that in 2024 and 2025 — the only years for which the agency has monitored nitazenes separately — 41 consignments of the drug were intercepted. The data shows that most of these shipments arrived by mail, primarily from mainland China, Hong Kong and the United Kingdom. The quantities tended to be small, ranging from less than 1 gram to almost 700 grams.
The UK has also recorded anincrease in high-strength nitazenes in recent years. John Fahey, a spokesman for the National Crime Agency, said criminals used the UK as a “transit point” for shipping illicit drugs and that officials were working closely with US law enforcement on nitazene-related cases. Source: DEA
But that’s not always the case. An analysis of US federal court records linked to prosecutions of nitazenes indicates that roughly 90 kilograms of material containing nitazenes in different forms (powder and pills) have been seized over the past three years. Nearly two-thirds of that amount, about 60 kilograms, stem from a single case.
In that case, prosecutors allege that a man named Valkar Singh drove a blue Maserati from Canada into the US carrying six industrial-sized buckets with more than 100,000 pills containing isotonitazene. According to court filings, Singh transported the drugs to a Bronx, New York address, where he was arrested by undercover law enforcement officers.
Tarentino, who is familiar with the Singh case but could not comment on it specifically, said a lot of work is being done to prevent drugs being smuggled across the Canadian border. “Canada has become a major concern, but also a major partner in trying to stop the synthetic opioids that are coming into the United States,” he said.
Lawyers for Singh, who has pleaded guilty and is awaiting sentencing, declined to comment.
Photos of buckets containing isotonitazenes in the trunk of Singh’s car. Pills only contain trace levels of active ingredients, meaning the exact quantity of nitazenes is unknown. Still, experts say this seizure was significant, considering the drug’s potency. Source: US District Court for the Southern District of New York
The scale of the alleged seizure makes this case an outlier. Of 46 federal cases identified by Bellingcat between 2021 and 2025, the next highest nitazenes seizure was about 9 kilograms. By comparison, data provided by the European Union Drugs Agency shows roughly 18 kilograms of nitazene-related seizures (pills, powder, liquid) across the EU between 2019 and 2023.
“It’s very large,” said Jared Brown, scientific affairs officer at the UNODC. “One hundred thousand pills is probably at the limit of what we hear about in terms of maximum types of quantities that get seized.”
The evidence suggests that most buyers are individual dealers who purchase relatively small quantities online, rather than organised criminal groups. “It’s street-level or mid-level dealers [in the US] that are introducing the nitazenes into the drug supply, not the big drug traffickers,” said Philip Berry, a visiting senior lecturer at King’s College London who formerly worked in counter-narcotics at the UK Home Office.
Court documents show that buyers can easily find nitazene suppliers online: on dark web marketplaces, standalone chemical supplier websites, or even on social media platforms. The suppliers often market the drugs by listing their chemical identifier and social media contact details. Often, the ads include an image of a young Asian woman striking a pose.
Buyers are often individual dealers who contact sales representatives via encrypted channels and negotiate a deal. In those conversations, representatives will sometimes disclose how they claim to evade customs, for example by declaring the product as cosmetics or electronic accessories.
Ads for nitazenes — such as these ones Bellingcat viewed this month — are found on dozens of sites, from social media platforms to prominent Asian-headquartered marketplaces that target international buyers. Source: Bellingcat
A detailed account that illustrates this modus operandi comes from the 2023 case against a man named Will Catis in Florida — the state with the second highest number of confirmed nitazene reports. Court documents show that a basic internet search led Catis to multiple nitazene advertisements listed by Jiangsu Bangdeya New Material Technology Co., LTD, a Chinese company sanctioned by the US Treasury for offering illicit substances for sale, including fentanyl and protonitazene.
Catis purchased approximately four kilograms of nitazenes from Jiangsu Bangdeya in batches no larger than 500 grams. The drugs were sent via the US Postal Service to Deerfield Beach, Florida. Once received, Catis mixed the nitazenes with other drugs, pressed the substance into a brick and sold it to other drug traffickers. Catis was jailed for 12 years after pleading guilty to possessing and intending to distribute nitazenes.
One court case from Florida describes how a couple who lived in a converted garage bedroom in Hernando County bought nitazenes through the mail from Chinese companies they contacted online. Jacob Spinoza and his girlfriend Veronica Jo Barback regularly abused the drugs and distributed them locally, according to court documents. Both pleaded guilty. Spinoza was sentenced to nine years in prison, and Barback received a three-year sentence.
Jacob Spinoza and Veronica Jo Barback under the influence of nitazenes. Court records said Spinoza survived more than 20 overdoses in 2022. Source: US District Court Middle District of Florida
Another notable case reveals how a man allegedly ran a drug trafficking operation from a prison in Ohio. Investigators said Brian Lumbus Jr worked with a middleman, Giancarlo Miserotti, who contacted drug manufacturers in China to get nitazenes shipped through Italy to avoid custom checks. Once in Ohio, the plan was to distribute the drugs to other states, court documents said.
But law enforcement agents were listening in on conversations between Lumbus and other members of the drug network, who expressed caution about the potency of nitazenes. “Man, we got to be careful … somebody died,” Lumbus said in one phone conversation, according to court documents. “Ohhh … it was too strong,” Miserotti responded. “I think the ratio of the pink [metonitazene] was thick.”
Lumbus is awaiting trial. Miserotti was arrested in Italy in 2023 and sentenced to more than 13 years in prison.
Arms Race
Enforcement actions have targeted the online marketplace ecosystem. In June 2025, Archetyp Market, a major dark web platform used to sell drugs, was dismantled in a coordinated operation involving Europol. US authorities have also indicted several China-based companies and individuals accused of offering nitazenes and related synthetic opioids for sale. Still, advertisements for nitazenes continue to litter online markets, constantly adapting to new regulatory regimes.
Nitazenes, such as this listing for etonitazene, which is up to 500 times stronger than heroin, are openly advertised online. Source: Bellingcat
In July 2025, China placed the majority of nitazenes under national control. Tightened regulations — both in China and the US — have tried to stem the flow of nitazenes. But drug experts warn that manufacturers are already exploiting loopholes in China’s regulations by marketing chemically similar synthetic opioids known as “orphines.”
Jared Brown, of UNODC, said orphines are also thought to come from China and are about as powerful as fentanyl. “Orphines have just enough of the molecule difference that it isn’t covered by the core definition that China has made,” he said.
This is not the first time Chinese synthetic opioid manufacturers have adapted to regulations. In 2019, China banned all fentanyl-related substances, including some major precursors. The number of distinct fentanyl analogues reported to the UNODC subsequently plummeted, while reports of nitazenes quickly picked up. Now that China is clamping down on nitazenes, orphines are on the rise. More than 150 cases involving orphines were reported in the US between 2024 and 2025, the majority of which are in Illinois.
“Always adapting, always changing – we call them ‘shape shifters’,” said Tarentino. “They’re this global Hydra that are always changing, evolving and adapting to their environment and taking full advantage of all of these different loopholes and vulnerabilities that exist.”
Reporting for this story was supported by the Fund for Investigative Journalism.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
This investigation is part of a collaboration between Bellingcat, Evident Media and CalMatters. You can watch Evident’s investigative video here, and read CalMatters’ report here.
In early January 2025, a gardener named Ernesto Campos was pulled over by Border Patrol agents in the city of Bakersfield, California.
The agents were a long way from home: Bakersfield is over 240 miles (386km) from the US border with Mexico.
They were there as part of Operation Return to Sender, a Border Patrol surge in the city that acted as a portent of what was to come across the US in 2025.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
Video footage shows one agent threatening to break Campos’ car window as they believed he was transporting an undocumented individual.
Campos filmed the agents, who he said slashed his tyres before arresting him and a passenger. The agents’ faces later appeared on local news reports detailing the incident.
Ten months later, two of the agents visible in footage recorded by Campos were filmed in Chicago as Border Patrol agents descended on the city for what was dubbed “Operation Midway Blitz”.
An image from court documents shows a Border Patrol agent unholstering his gun at an incident in Evanston, Illinois.
A federal judge in Illinois said in November that the use of force by federal agents in Chicago – including the use of tear gas and other less lethal munitions on multiple occasions – “shocks the conscience”.
A restraining order issued by that Illinois judge was vacated on appeal earlier this month. But what took place on the streets of Chicago also happened in other locations, with some of the same agents involved.
Bellingcat has worked with our partners at Evident Media and CalMatters to analyse over 85 hours of social media and bodycam footage, as well as court documents and incident reports, to try to unpack the actions of Border Patrol agents across the country.
With agents often masked and badge or identification numbers not always visible, understanding exactly who has enforced the immigration surges of the past year has been difficult. This, in turn, has made public questioning and accountability around use-of-force incidents challenging.
Subscribe to the Bellingcat newsletter
Subscribe to our newsletter for first access to our published content and events that our staff and contributors are involved with, including interviews and training workshops.
Nonetheless, we observed over 25 agents who appeared in more than one city, either by recognising their faces or matching badge numbers that were visible on their vests or arm patches. Many were seen alongside former Border Patrol Commander at Large, Gregory Bovino, on at least one occasion.
But this is likely just a fraction of the agents who moved around the country to take part in Border Patrol surges in cities like Los Angeles, Chicago and Minneapolis. When speaking to reporters in January, Border Czar Tom Homan said he had spoken to some agents who had “been in theatre for eight months”. Many wore masks in the videos viewed by Bellingcat, and it was not always possible to identify number patches from social media or bodycam footage alone.
Although some of the agents we logged appeared on neighbourhood walkabouts or in footage where little happened, others could be seen using force on multiple occasions. For this story, we have focused on the actions of five agents whom we have been able to identify and who appear to have repeatedly used force in at least two, but often more, locations. We have decided to name those we have been able to identify just as we would name any officer involved in incidents like those detailed. But these were by no means the only agents whom we saw using force across one or multiple cities.
The footage we analysed also appears to show a steady escalation of violence and confrontational incidents as 2025 progressed, culminating in widespread use-of-force incidents in Chicago and Minneapolis, where two people, Renee Good and Alex Pretti, were killed by Immigration and Customs Enforcement (ICE) and Border Patrol agents, respectively, in early 2026.
Agents on the Move
While former Border Patrol Commander at Large Gregory Bovino is no longer in a national role, some of the agents observed and documented for this report appear to have travelled from his El Centro sector over the past year.
These included agent Timothy Donahue and Georgy Simeon, who were filmed by Ernesto Campos in Bakersfield. Donahue was the agent who was subsequently pictured pointing his gun at citizens just outside Chicago after a traffic incident (Donahue stated in his incident report that his car was rammed by an activist – something also described in Illinois federal judge Sara Ellis’ opinion – although Donahue’s report made no mention of punching a man in the face or unholstering his weapon). It was Simeon, meanwhile, who was filmed slamming a man to the ground after grabbing him by the throat.
Donahue was also spotted in social media footage in Los Angeles in June last year pushing a citizen who was blocking his vehicle, as well as grabbing a man on an immigration raid inside a car wash.
The Chicago publication, Unraveled Press, previously reported that Donahue was the owner of a social media account that made seemingly racist and sexist posts. Bellingcat and others have checked this account and found that an old profile picture showed an image of Donahue. Bodycam footage from outside a detention centre near Chicago also showed Donahue tackle a journalist from Unraveled without apparent warning.
Footage from Donahue’s own bodycam on Oct. 3 also appears to show him compiling an incident report with ChatGPT. The possibility of CBP agents using ChatGPT to compile incident reports was addressed by Judge Ellis in her ruling issuing a restraining order in November. She wrote that using ChatGPT to write reports “undermines their credibility and may explain the inaccuracy of some reports filed by CBP officers”.
The evidence doesn’t enable us to determine if Donahue used ChatGPT to compile the Oct. 31 incident report in which he did not mention he punched a man and unholstered his gun.
Bodycam footage released with court documents shows a Border Patrol agent using ChatGPT to compile an incident report.
Our reporting partners CalMatters emailed and called Donahue prior to publication. The email received no response. Donahue answered his cellphone but said, “never, ever call my cellphone again,” and hung up.
Simeon did not respond to emailed questions prior to publication, and calls to a number listed under his name went unanswered.
The Department of Homeland Security (DHS) did not respond to questions posed about the actions of Donahue and Simeon detailed in this report or the agency’s use-of-force policies. They also did not respond to questions about whether it was permissible for agents to use generative AI platforms like ChatGPT to compile incident reports.
While the actions of Donahue and Simeon made news reports in various cities, the pair were far from alone in having their actions filmed and documented across the country.
Kristopher Hewson, a supervisory agent based out of Bovino’s El Centro sector, was seen on bodycam footage in Chicago spraying an individual who was being held down by agents with what he detailed in his incident report as oleoresin capsicum (OC), also known as pepper spray, from what appears to be just a few inches away. The individual was on the ground and had one hand behind his back, but agents could be heard asking for his other hand during the incident. Hewson said in his incident report (see here and here) that the individual had been resisting arrest, but he also stated that he deployed the pepper spray from two feet away. Bodycam footage (see below) showed the canister beside the individual’s head right after a burst of spray can be heard.
Bodycam footage shows an individual being held down before pepper spray is released while he remains on the ground. Annotations after 15 seconds made by Bellingcat.
Hewson, who wore a mask but was identifiable in several videos by the C-29 ID number on his uniform, was later spotted in Minneapolis. He also said his name during one incident that allowed us to find other bodycam footage releases that belonged to him. In one video, his mask slipped, which allowed us to compare his face to images on his social media accounts.
Court testimony revealed that he was present in Los Angeles during a Border Patrol surge in the city in the summer of 2025. He was also seen alongside Bovino on numerous occasions, including in Chicago, where Bovino can be heard greeting him by saying, “Hey, Hewson”, in one video captured by the filmmaker Jeff Perlman.
In bodycam footage from Chicago a man can be heard saying that the person Hewson pepper-sprayed was his son, who was just 15 years old. This appears to be backed up by an incident report showing the individual’s date of birth. A short time later, Hewson can be heard shouting “get back or you will be gassed” at a group of protesters immediately before deploying tear gas towards them. As he throws the canister, a person can be heard shouting, “You’re not de-escalating shit, bro”. Hewson stated in his incident report (see here and here) that he gave a warning that CS gas was coming, but he did not detail how that warning was virtually instantaneous.
All of these actions came two weeks after a judge issued a temporary restraining order on Oct. 9, preventing agents from using chemical agents on protesters and journalists unless there was an imminent threat of physical danger to federal forces. While that order was lifted in March 2026, it was still in force during the incidents detailed in this story.
Hewson was seen in Minneapolis in early 2026 alongside Bovino. He was captured on footage marching towards and tackling a Target employee, a teenage US citizen, who was directing insults at agents. A melee ensued at the front door of the Target store before two people were handcuffed and taken away by agents. Hewson’s C-29 number was visible as he led one of the men away. Both of those arrested were later released.
Hewson was questioned as part of a preliminary injunction hearing in Chicago, where, among other things, he stated (pages 183 and 184) that protesters have the right to shout and even swear at officers as long as they aren’t impeding their ability to carry out their work. He also said during questioning that tear gas “doesn’t harm people” (page 189). Multiple individuals who were impacted by the release of gas and chemical irritants in Chicago stated otherwise in incidents detailed in Judge Ellis’ ruling.
When reached on the phone by CalMatters, Hewson said he could not comment. DHS did not respond to questions posed about the actions of Hewson detailed in this report or the agency’s use-of-force policies.
El Paso Agents
Hewson was present and visible in footage when ex-Border Patrol Commander at Large Bovino appeared to push and manhandle a protester who crossed his path on Nicollet Avenue in Minneapolis.
Also beside Bovino and Hewson that day were two officers based out of El Paso bearing the ID numbers EZ-2 and EZ-17. Both of these agents are seen wearing vests of the Border Patrol Tactical Division (BORTAC), a specialised unit that, according to the CBP, has a selection process “designed to mirror aspects of the US Special Operations Forces’ selection courses”.
Bellingcat and Evident Media previously reported how EZ-17 fired less lethal munitions at protesters from close range a day after Renee Good was shot and killed by an Immigration and Customs Enforcement (ICE) officer in Minneapolis.
EZ-17 was accompanied during that incident by EZ-2, who could be seen spraying a chemical irritant in the face of a man who appeared to have thrown a snowball at him. EZ-2 was also seen throwing two female protesters to the ground outside Roosevelt High School in Minneapolis on Jan. 7.
Both EZ-17 and EZ-2 were present in Chicago. EZ-17 was seen passing a tear gas canister to Bovino at an incident in the city’s Little Village neighbourhood on Oct. 23.
The Chicago publication, Unraveled, previously identified EZ-17 as Edgar Vazquez and EZ-2 as Michael Sveum. Bellingcat was able to corroborate these identifications using similar techniques. Firstly, for Vazquez we compared images on his Facebook page with footage from EZ-2’s bodycam, which showed Vazquez inside a vehicle without a mask.
Ernesto Vazquez photo taken from Facebook (left) and image taken from bodycam footage in Chicago (right). Source: CBP via Loevy.com
EZ-2 was identified in a similar manner. Bodycam footage from EZ-2 showed him looking at his phone. On the lockscreen was a picture of a man smiling and wearing a blue jacket. That same picture was posted on Sveum’s social media accounts and appeared to have been taken at an ultramarathon event whose organisers posted Sveum’s name alongside that same image.
Bodycam footage (left) shows a lockscreen with a picture of a man that matches images seen on archived posts from the social media accounts of Michael Sveum.
When reached by phone by CalMatters reporters, Vazquez said that he could not comment. Sveum hung up immediately after CalMatters’ reporter introduced himself. DHS did not respond to questions posed about the actions of Vazquez or Sveum detailed in this report or the agency’s use-of-force policies.
Dozens of other incidents where agents appeared to escalate rather than de-escalate situations, as well as use force or less lethal munitions, were logged as part of this investigation. This included agents pointing guns at protesters (see here and here) as well as using violent force and less lethal munitions on protesters, journalists and bystanders.
Bovino himself appeared to instigate confrontations with people, such as in Chicago, when he can be seen throwing a man to the ground before agents pounce on him, although he stated during his Illinois deposition that he did not think such actions represented a use-of-force incident.
The former Border Patrol Commander at Large told CalMatters that he could not speak to the media without DHS approval prior to publication of this story. Requests sent to DHS to speak with Bovino went unanswered.
‘Unusual and Beyond the Pale’
According to John Roth, a former DHS Inspector General, and Steve Burnell, a former DHS General Counsel, the events of the past year, involving masked agents descending on select cities, have eroded trust and credibility in DHS and law enforcement.
While both agreed that there had to be professional immigration enforcement operations, they said that has to be done in a way that is responsible and ensures accountability when lines are crossed.
“This is sort of a scary Orwellian thing”, Roth said. “I don’t think the public understands how unusual and beyond the pale it is to have these roving sort of groups of masked agents, out there handling the public.”
Burnell said that the inability to identify agents carrying out their work as enforcement officers was a particular concern: “At the end of the day, ICE and everybody at DHS are public servants. They’re supposed to be working for the public. And, you know, if somebody is working for you, you should have a right to know who they are, and you should have a right to hold them accountable and protest what they’re doing.”
Roth and Burnell both served under President Barack Obama and during President Donald Trump’s first term. The pair have testified to Congress in recent months, raising the alarm about what they see as a dismantling of accountability at DHS. Prominent members of the US government, including President Trump, have offered repeated support to Border Patrol agents, even after the death of protesters such as Renee Good.
Our partners at Evident and CalMatters showed Roth and Burnell some of the footage described in this report. While they refrained from commenting on individual incidents, Roth described the footage generally as “difficult to watch”.
“The question I’d ask. Have [agents] inserted themselves into something that requires them to use force,” said Roth. “In which case that would be a violation of DHS policy,” he added, referring to use-of-force policies that detail how law enforcement officers may use force when no “reasonably, safe and feasible alternative appears to exist”.
“It’s actually DHS policy that you [are required] to attempt to de-escalate when that’s possible. I mean, they don’t have a duty to retreat, but they do have a duty not to insert themselves into a place where use of force is necessary,” Roth said.
Burnell described a lot of what has happened over the past year as a type of “dominance display”.
“It’s there to send a message. And that is not de-escalatory. It’s the opposite,” he said.
Bellingcat, CalMatters and Evident Media jointly sought to contact DHS as well as all of the agents mentioned in this story prior to publication.
We asked DHS whether any of the incidents detailed in this report violated DHS use-of-force policies or whether those policies had been updated under the current administration.
We also asked if DHS was taking any action or providing further training to agents to ensure the public’s constitutional rights are respected during immigration enforcement operations carried out by Border Patrol.
DHS did not respond before publication.
Youri van der Weide, Kolina Koltai and Eoghan Macguire from Bellingcat, as well as Sergio Olmos from CalMatters and Kevin Clancy from Evident Media, contributed reporting to this piece.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
US President Donald Trump said on January 2 that the US was “locked and loaded and ready to go”. Trump was talking aloud about intervening in Iran if it continued a violent crackdown on demonstrators who had taken to the streets over spiralling inflation and ongoing repression.
On Saturday, February 28, the United States and Israel launched a large-scale attack against Iran, killing Supreme Leader Ayatollah Ali Khamenei and targeting military infrastructure throughout the country. President Trump initially told Iranians they should seize control of the government but on Tuesday this week said: “If you’re going to go out and protest, don’t do it yet. It’s very dangerous out there. A lot of bombs are being dropped.” Almost 800 Iranians have been killed in US and Israeli strikes so far, according to the Iranian Red Crescent.
While the US has released a list of military targets, including IRGC headquarters and missile systems, Bellingcat has reviewed strikes against another type of target inside the Islamic Republic — police stations.
Experts told the New York Times that strikes against these facilities may be part of an effort to motivate Iranians to challenge the regime, although satellite analysis alone doesn’t allow us to tell if it is the US, Israel or both nations who have targeted police stations.
Mapping Targeted Police Stations
Using medium-resolution PlanetScope satellite imagery from Planet Labs, Bellingcat has been able to locate at least 15 local police stations or similar buildings that were struck between March 1 and March 3. Videos and photos shared on social media also show the aftermath of some of these strikes.
Comparing the March 1 PlanetScope satellite imagery with imagery taken on March 3, it’s possible to make out visible signs of building destruction throughout Tehran. Some of these sites have already been widely-reported on, including the strike on Supreme Leader Ali Khamenei’s compound and official residence.
But Bellingcat reviewed damage to a number of smaller buildings throughout Tehran and cross-referenced the locations with data on Google Maps, Open Street Maps and Wikimapia where we found that several were listed as police stations. The majority of sites we identified are in dense urban areas.
Video shared by Iranian state broadcaster Tasnim News showed the aftermath of a strike on what it describes as a “diplomatic police station” near Ferdowsi Square — one of downtown Tehran’s main intersections. Another video taken at the same location shows at least two people on the ground with a large amount of damage to nearby buildings. Geolocation of the videos puts them at 35.7032, 51.4189, adjacent to a school and office buildings.
An annotated image from Google Earth showing where a police station was destroyed in an airstrike. Video from Iran’s Tasnim News shows buildings that match those in the satellite imagery.
Another video, geolocated by a volunteer with Geoconfirmed — a volunteer geolocation collective — shows a heavily damaged police station near Tehran’s Grand Bazaar. PlanetScope imagery from March 3 shows heavy damage to the area around the police station.
Photos and video from the Golestan Palace, a UNESCO World Heritage Site that sits adjacent to the police office, shows that it also sustained damage.
Iran’s Police and Law Enforcement
Iran’s security apparatus includes a network of police, plain clothes officers, civilian militia battalions known as Basij and the Islamic Revolutionary Guard Corps. During recent protests security forces were seen shooting protestors on the streets, and many of those killed showed signs of being shot in the head.
Iran has experienced several waves of anti-regime protests over the past 15 years, all of which have been put down by the authorities who have not shied away from using extreme violence to contain them.
Although the Financial Times reported speaking to a Tehran resident that said one of the police stations we identified, in the Gisha neighborhood, had hosted a branch of Iran’s morality police, it is thus far unclear from the satellite data whether any of the police stations had any particular role during the recent protests.
Trevor Ball, Logan Williams and Felix Matteo Lommerse contributed reporting to this piece for Bellingcat. Anisa Shabir and StéphanieLadel contributed from Bellingcat’s Volunteer Community.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.

 Entrar

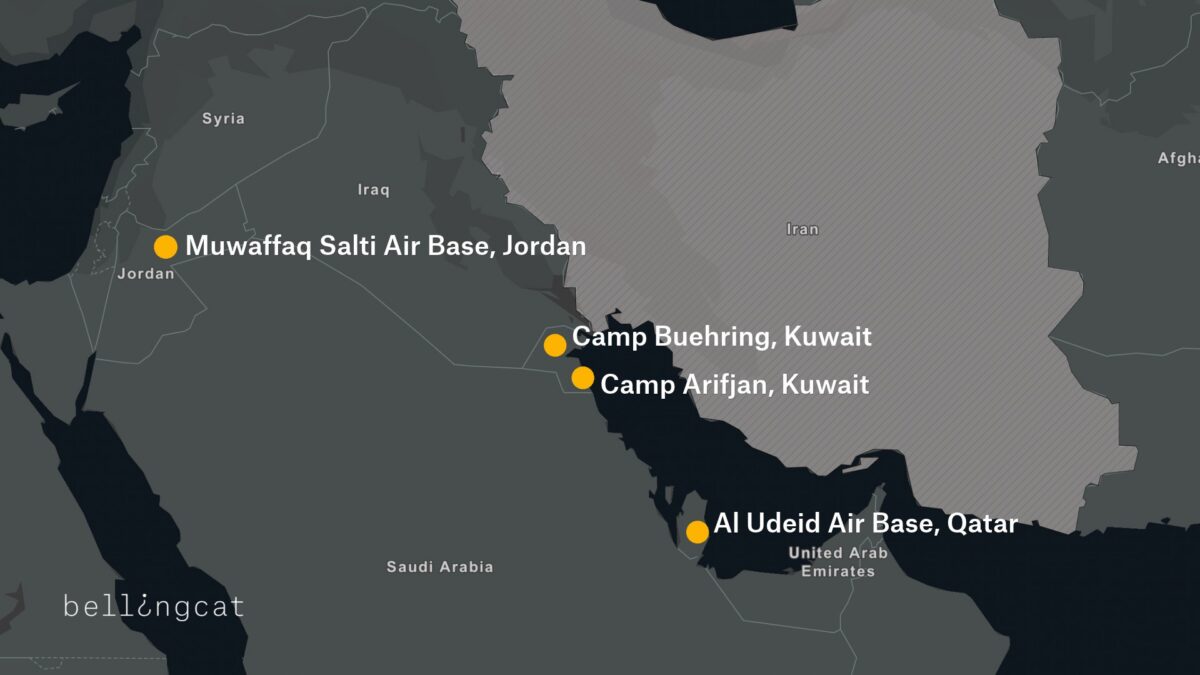
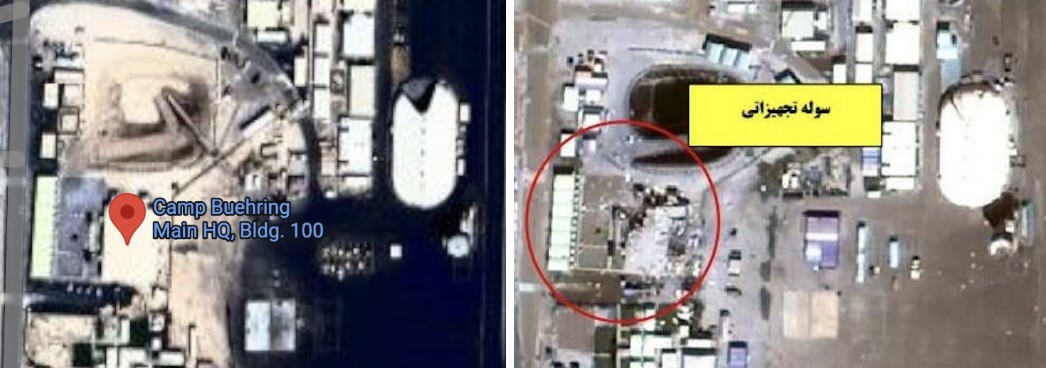
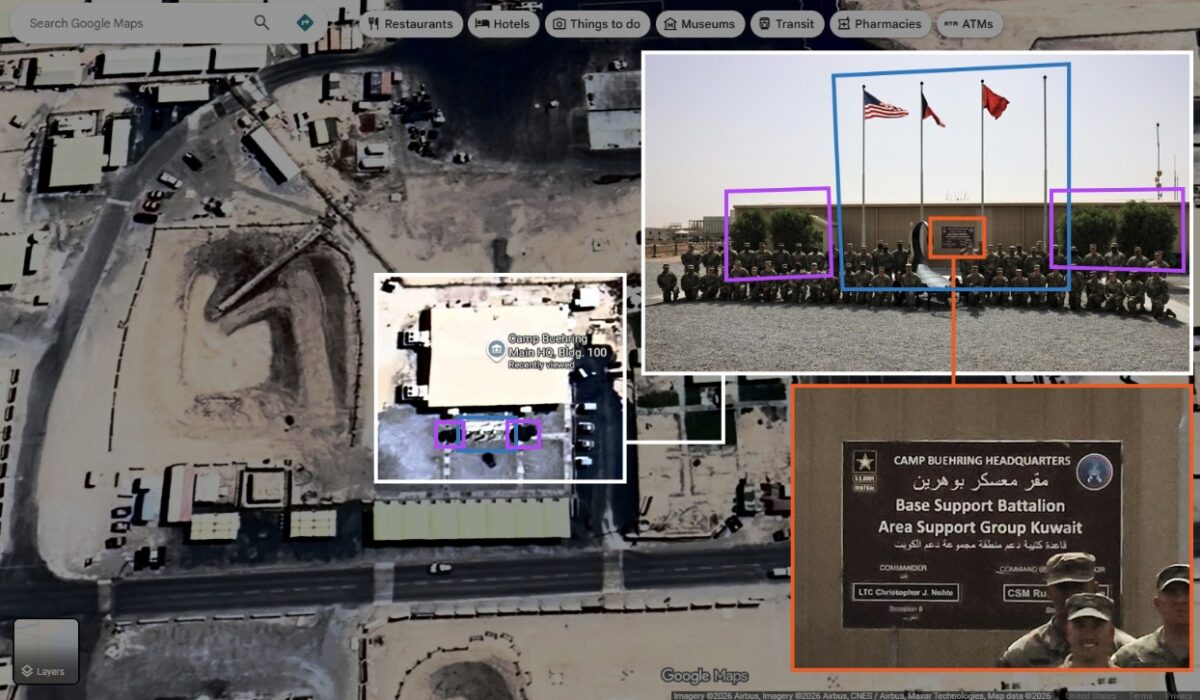
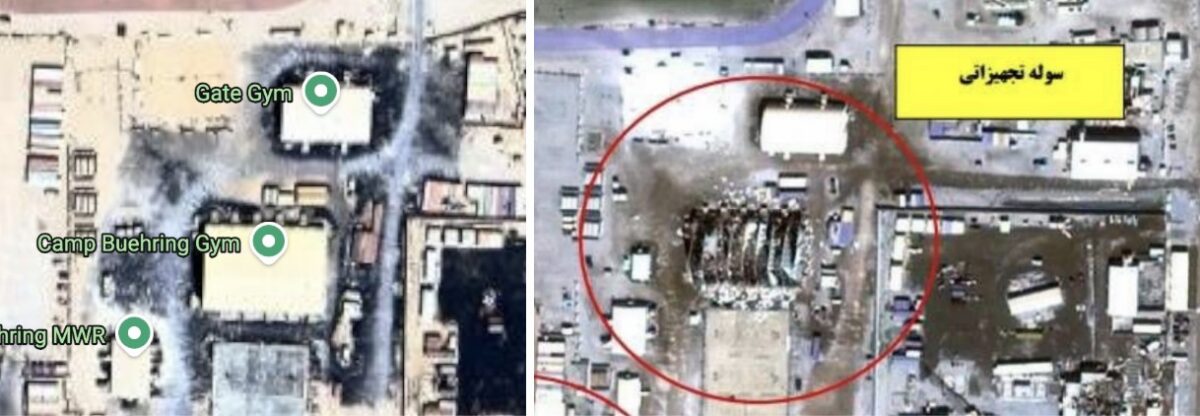
Exclusive images released showing damage to E-3 Sentry AWACS aircraft at Prince Sultan Air Base in Saudi Arabia, plus damage to US military camps Arifjan and Buehring in Kuwait from Iranian strikes. Images sent to CBS by active US military personnel. (IRIB News) https://t.co/1urA44f4xz