❌

Visualização de leitura

Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware

A new XLoader infection chain. It hides the credential stealer inside an embedded LuaJIT interpreter. It moves it into another Windows process through shared-section injection. The campaign uses business-themed email lures. It also delivered Agent Tesla, Remcos and XWorm . The chain starts with order and payment emails. One Greek-language message has a subject starting […]

The post Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Releases Emergency Fix for Windows 11 Remote Desktop Connection Failures

Microsoft has resolved an issue in Windows 11 that prevented non-administrator users from connecting to devices with Administrator protection enabled. This fix was included in KB5127936, released on October 28, 2026, and is part of subsequent updates. While this issue is urgent for affected organizations, Microsoft has categorized the release as a preview update rather […]

The post Microsoft Releases Emergency Fix for Windows 11 Remote Desktop Connection Failures appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Microsoft Releases Emergency Windows Updates to Revoke Trust in Compromised eMudhra Certificates

Microsoft has released an emergency Windows update to remove trust in certificates associated with compromised eMudhra certificate authority keys. The out-of-band update, issued on October 26, 2026, eliminates seven certificates from the Windows trust list. Following this, the same removals were applied to Microsoft Edge on October 27, as stated by the Microsoft Security Response […]

The post Microsoft Releases Emergency Windows Updates to Revoke Trust in Compromised eMudhra Certificates appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Hijack Camera Management Software to Deploy Reverse Shells and Hidden Windows Malware

Attackers are compromising camera management software to gain remote access, run malicious DLLs through a legitimate Windows component, and maintain persistent footholds in enterprise environments. The incidents show how overlooked surveillance applications can become entry points into broader corporate networks. Huntress observed several intrusions during September and October involving CMS.exe, a camera management application installed […]

The post Hackers Hijack Camera Management Software to Deploy Reverse Shells and Hidden Windows Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
BRONZE SANDCASTLE Hackers Steal Active Directory Database Using Hidden Windows Backdoors

BRONZE SANDCASTLE intrusions involving hidden Windows backdoors and the theft of the Active Directory database. The suspected China-based group combines legitimate applications, malicious DLLs, and encrypted payloads to execute code inside trusted processes while limiting artifacts available to conventional file scanning. Investigations covering August 2025 through August 2026 identified victims in the Philippines, Taiwan, Afghanistan, […]

The post BRONZE SANDCASTLE Hackers Steal Active Directory Database Using Hidden Windows Backdoors appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Google Pays $250,000 for AI-Assisted Chrome Exploit Enabling Windows Code Execution

Google has awarded XBOW $250,000 for creating an AI-assisted exploit chain that enabled code execution outside the Chrome browser’s renderer sandbox on Windows. This reward marks the first full-chain payout for Chrome under Google’s vulnerability reward program, introduced in April 2026. According to XBOW, all three vulnerabilities involved have since been fixed. Google Pays $250,000 […]

The post Google Pays $250,000 for AI-Assisted Chrome Exploit Enabling Windows Code Execution appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Windows BitLocker Vulnerabilities Could Allow Attackers to Bypass Security Protections and Escalate Privileges

Three Windows BitLocker vulnerabilities, as described in the provided advisory, could let attackers elevate privileges or bypass security protections under various access conditions. Microsoft is the assigning authority, with a release date of October 13, 2026, and all three vulnerabilities are rated Important. Two require existing local privileges, while the third requires physical access. We […]

The post Windows BitLocker Vulnerabilities Could Allow Attackers to Bypass Security Protections and Escalate Privileges appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Former Employee Sentenced for Damaging Employer’s Windows Network Infrastructure

A former infrastructure engineer has been sentenced to 32 months in federal prison for damaging his employer’s computer network and demanding a ransom in Bitcoin. Daniel Rhyne, 59, of Kansas City, Missouri, received the sentence from U.S. District Judge Michael A. Shipp on September 28, 2026, in Trenton, New Jersey. Rhyne previously pleaded guilty to […]

The post Former Employee Sentenced for Damaging Employer’s Windows Network Infrastructure appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New Windows Malware Built to Survive Takedowns With a Hidden P2P Command Network

AvisLoader, a newly observed Windows malware loader designed to maintain operator access even when conventional command-and-control infrastructure is disrupted. Instead of relying on a fixed domain, IP address, or centralized server, the malware uses the encrypted Tox peer-to-peer messaging network to receive commands and deliver follow-on payloads. The discovery highlights a growing challenge for defenders: […]

The post New Windows Malware Built to Survive Takedowns With a Hidden P2P Command Network appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Chinese APT Clones Legitimate Websites to Deliver Chrome and Windows Zero-Day Exploits

A third Chinese threat actor has been linked to phishing campaigns that cloned trusted websites and chained Chrome and Windows zero-day exploits to deploy a previously undocumented backdoor. The activity occurred on September 3 and 4, 2026, while the targeted vulnerabilities remained unpatched in Google Chrome. It followed Volexity’s September 9 disclosure that UTA0560 and […]

The post Chinese APT Clones Legitimate Websites to Deliver Chrome and Windows Zero-Day Exploits appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
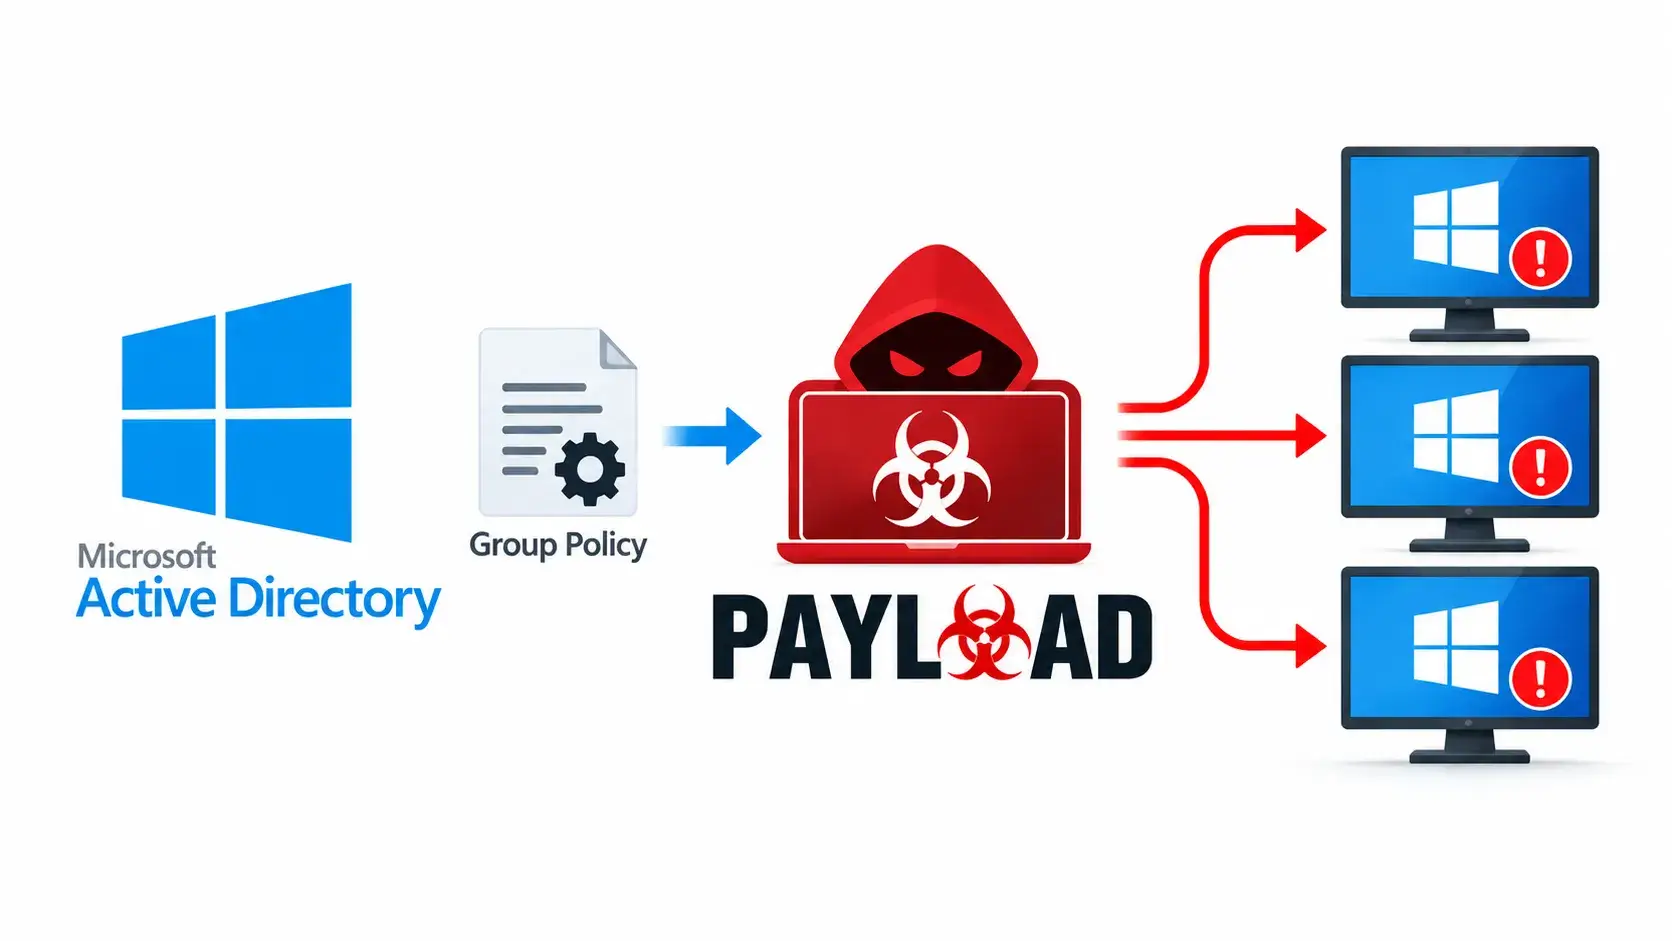
PAYLOAD Ransomware Abuses Active Directory Group Policy to Disrupt Entire Windows Domain

A ransomware incident in which attackers used Active Directory Group Policy to disrupt operations without deploying a Windows encryptor or leaving malware running on endpoints. In April 2026, the attackers accessed a FortiGate SSL VPN using compromised domain credentials, then gained domain-admin-equivalent rights. PAYLOAD Ransomware On April 13, Kaspersky’s Global Emergency Response Team (GERT) created […]

The post PAYLOAD Ransomware Abuses Active Directory Group Policy to Disrupt Entire Windows Domain appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New Rapuncel Infostealer Abuses Microsoft-Signed Driver to Disable 145 Security Tools

A newly identified information-stealing campaign, tracked as Rapuncel, is exploiting a Microsoft-attested kernel driver to terminate up to 145 antivirus (AV) and endpoint detection and response (EDR) processes. This allows attackers to steal browser credentials, cryptocurrency wallet data, chat tokens, and Windows credentials. Researchers from the LastPass Threat Intelligence, Mitigation, and Escalation team, in collaboration […]

The post New Rapuncel Infostealer Abuses Microsoft-Signed Driver to Disable 145 Security Tools appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New SETTRA Ransomware Uses MeshAgent RMM and BYOVD to Encrypt Windows Systems

A newly observed ransomware operation dubbed SETTRA is abusing the legitimate MeshAgent remote monitoring and management platform for persistence while using recovery-inhibition and defense-evasion techniques to maximize the impact of Windows encryption attacks. Huntress investigated two SETTRA incidents in July and September 2026, uncovering a repeatable operational pattern involving victim-specific ransomware binaries, Windows log clearing, […]

The post New SETTRA Ransomware Uses MeshAgent RMM and BYOVD to Encrypt Windows Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Chinese-Speaking Hackers Use Noodle RAT Backdoor to Spy on Windows and Linux Systems

Chinese-speaking threat actors are continuing to rely on Noodle RAT, a cross-platform remote access trojan designed to maintain covert access to compromised Windows workstations and Linux servers. Also tracked as ANGRYREBEL and Nood RAT, the malware has been active since at least mid-2016 but was long mistaken for variants of Gh0st RAT, Rekoobe, and other […]

The post Chinese-Speaking Hackers Use Noodle RAT Backdoor to Spy on Windows and Linux Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
PAPERMILL Malware Campaign Abuses Signed Notepad++ to Deliver VenomRAT to Windows Users

A newly identified phishing operation tracked as PAPERMILL is abusing a legitimately signed Notepad++ executable, DLL sideloading, and layered in-memory loaders to install VenomRAT on Windows systems. The campaign uses tax-audit lures aimed at Indian recipients and reflects a broader China-nexus pattern of tax-themed malware activity, although the available evidence does not support definitive attribution […]

The post PAPERMILL Malware Campaign Abuses Signed Notepad++ to Deliver VenomRAT to Windows Users appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
AsyncRAT Malware Abuses AutoIt and PowerShell to Hide Inside Legitimate Windows Process

A five-stage AsyncRAT campaign that chains a socially engineered batch file, hidden PowerShell execution, AutoIt abuse and process injection to conceal a .NET remote-access trojan inside Microsoft’s legitimate charmap.exe process. The infection begins with a lure named “Right-click to open Invoice Details.bat”, which relies on user interaction to trigger execution. While the precise delivery method […]

The post AsyncRAT Malware Abuses AutoIt and PowerShell to Hide Inside Legitimate Windows Process appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Steal Active Directory Password Hashes Without Attacking Domain Controllers Directly

Threat actors are increasingly exploiting Active Directory replication mechanisms to steal password hashes without directly compromising a domain controller. This technique, known as DCSync, allows attackers with privileged domain credentials to impersonate a legitimate domain controller and request sensitive directory replication data. Unlike noisy attacks that use malware on servers or attempt to extract credentials […]

The post Hackers Steal Active Directory Password Hashes Without Attacking Domain Controllers Directly appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Windows BitLocker Flaw Lets Attackers Execute Code on Vulnerable Systems

Microsoft disclosed CVE-2026-69449, an Important-severity vulnerability in Windows BitLocker. This issue is classified as a heap-based buffer overflow (CWE-122) and may allow remote code execution (RCE). Microsoft released details about this vulnerability on September 8, 2026. The CVSS 3.1 base score is 6.7, with a temporal score of 5.8. Windows BitLocker Flaw The vulnerability uses […]

The post Windows BitLocker Flaw Lets Attackers Execute Code on Vulnerable Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Windows Defender ShieldCrash 0-Day Lets Attackers Read Arbitrary Files as SYSTEM

A newly published proof-of-concept (PoC) called ShieldCrash reveals an unpatched vulnerability in Microsoft Defender that allows a local attacker to gain arbitrary file-read access in the SYSTEM context. This disclosure, attributed to the researcher known as MSNightmare, comes shortly after Microsoft addressed an elevation-of-privilege flaw in the Microsoft Malware Protection Engine, tracked as CVE-2026-69414, referred […]

The post Windows Defender ShieldCrash 0-Day Lets Attackers Read Arbitrary Files as SYSTEM appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
BYOTC Attack Abuses Trusted Windows Clients to Access Privileged Kernel Driver Operations

A newly documented Windows attack pattern, dubbed Bring Your Own Trusted Caller (BYOTC), shows how attackers can bypass driver-level authorization controls without exploiting a traditional memory-corruption flaw. Instead of attacking a privileged kernel driver directly, an adversary compromises or abuses the legitimate user-mode application that the driver already trusts. The technique expands on the well-known […]

The post BYOTC Attack Abuses Trusted Windows Clients to Access Privileged Kernel Driver Operations appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
❌