❌

Visualização de leitura

The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More

weekly roundup

This weekly roundup covers the FBI's attribution of the $6 billion Binance hack to North Korea, a spreading wave of refrigeration attacks that has now reached France's blood supply, rapid exploitation of a freshly patched WordPress flaw, a Europol takedown of a fake trading platform supplier, and unauthorized trades in Stockal customer accounts.  Two threads run through this week's stories. First, attackers are increasingly coming in through someone else's door: a third-party refrigeration supplier, a scam platform provider, or data leaked by another company. Second, speed decides the outcome. Attackers moved on WordPress within two days of a patch, while fast alarms saved France's blood stocks from the fate of supermarket food. 

The Cyber Express Weekly Roundup 

FBI Blames North Korea for $6B Binance Hack 

The FBI has attributed the theft of more than $6 billion from Binance, which took place around October 29, to North Korean hackers it tracks as "TraderTraitor." The stolen funds are being converted mainly into Ethereum, and the agency has urged crypto firms to block transactions linked to the attackers. Read more… 

Hackers Heat Supermarket Freezers Across Europe 

Supermarkets in Sweden, Belgium, Luxembourg, Ireland and Estonia threw out spoiled food after hackers took control of refrigeration systems, in some cases setting them to 50°C. The attacks follow a similar campaign against around 400 stores in France last month that exploited outdated, internet-connected cooling equipment. Who is responsible remains unknown. Read more… 

Hackers Target WordPress Flaw Days After Patch 

Attackers began exploiting a critical WordPress flaw within 48 hours of its October 28 fix in version 7.1.4, with Wordfence blocking nearly 63,000 attempts in a single day. The bug affects versions 4.7 through 7.1.3 and can let hackers run code on a site during a core update. With no workaround available, site owners are urged to update immediately. Read more… 

Europol Busts Supplier of Fake Trading Platforms 

Authorities in seven countries seized more than 100 servers and arrested seven suspects on November 3 in an operation against a company accused of supplying fake trading platforms to scam call centres. Victims were lured with promises of quick profits, shown fake gains to draw in more money, and then blocked from withdrawing. Losses are estimated at over €4 million, with potential victims in more than 50 countries. Read more… 

Freezer Hackers Hit France's Blood Supply 

France's national blood service, EFS, said hackers raised temperatures in cold storage rooms at three sites by going through a third-party refrigeration supplier. Alarms caught the changes quickly, and no blood products were lost. It is the first healthcare organisation hit in a wave of refrigeration attacks now reported in at least 11 countries. No one has claimed responsibility. Read more… 

Stockal Confirms Unauthorized Trades in 13 Accounts 

Borderless, which runs US equities platform Stockal, said attackers logged into 26 customer accounts using valid credentials and, in 13 of them, sold large-cap stocks to buy obscure microcap shares. No funds were withdrawn. The company says its systems were not breached and suspects social engineering using data leaked in another firm's breach. Read more… 

Weekly Cybersecurity Takeaway

Several of this week's incidents show that an organization's security is only as strong as the partners and data around it. Supermarkets and France's blood service were reached through refrigeration suppliers; Stockal customers were likely targeted with data stolen elsewhere, and the Europol case exposed a business that built scam platforms for others to run.  Speed is the other lesson. Attackers turned the WordPress fix into a roadmap within 48 hours, while the EFS avoided losses because its monitoring flagged the problem right away.  Organizations should review the remote access their suppliers have to critical systems, retire or isolate unsupported internet-connected devices, and make sure alarms on physical equipment reach someone around the clock. They should also patch critical flaws without delay, strengthen account authentication, and, for crypto firms, block addresses linked to the Binance attackers. 

Why Is Kim Yo-jong Suddenly Responding to a Binance Hack?

Binance hack Targeted

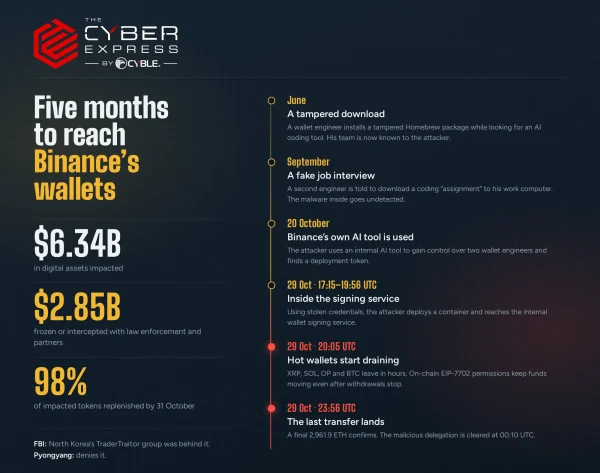
On October 29, Binance lost control of about $6.34 billion in digital assets in a matter of hours. The attackers did not break in on that day, though. They had been working their way inside since June. The Binance hack was a slow campaign aimed at a handful of engineers, and it used a tampered download, a fake job interview and the exchange's own internal AI tool to reach the systems that sign transactions. Binance CEO Richard Teng called it "one of the most sophisticated attacks the digital asset industry has ever seen." He said the company takes full responsibility and that no user will bear the loss.

Why the Binance Hack Targeted Engineers, Not Systems

According to the post-mortem Binance released on Tuesday, the attackers went after people with access to wallet infrastructure. In June, Wallet DevOps Engineer A searched for a popular AI coding tool and downloaded a tampered Homebrew installation. Binance's security team spotted the anomaly, replaced the device and rotated his credentials. But the damage was done in another way: Engineer A's role, and his colleagues on the wallet infrastructure team, were now known to the attacker. In September, the attackers moved to social engineering. Software Engineer B, whose profile on a legitimate job-hunting platform mentioned his Binance experience, was approached by someone posing as a project director. A first-round video interview followed with a supposed HR representative, who shared personal photos and videos on social media to build trust. Binance said this was more advanced than social engineering it had seen before. Binance hack infographic In the second round, held on a popular chat app, Engineer B was told to download an "assignment" onto his work computer. It contained malicious code that ran during setup, swapped a legitimate development tool for a malicious version, and connected to an attacker-controlled server. The zero-day malware was not detected by endpoint security tools at the time. On October 20, the attackers used Engineer B's compromised computer and an internal AI tool to gain control over Engineer A and another wallet engineer, Engineer C. They then found that Engineer A had a container deployment permission token on his machine.

How the Binance Hack Unfolded on October 29

Between 17:15 and 19:56 UTC, the attacker logged onto Engineer C's computer, used Engineer A's stolen credentials, deployed a container and triggered a malicious script. That gave them unauthorized access to an internal wallet signing service, which they used to send transactions outside the normal withdrawal process. Between 20:05 and 20:09 UTC, five Binance hot wallets sent 233.46 million XRP to an attacker-controlled address. Hot wallets on Solana and Optimism sent about 970,500 SOL and 44.2 million OP. Binance then received an internal alert about large transfers, and another hot wallet sent 18,270 BTC.

Why Binance Couldn't Stop It Faster

Binance suspended withdrawals, but that did not end the outflows. The attacker had used the signing service to exploit Ethereum's EIP-7702 authorization mechanism. By submitting 50 signing transactions, they gave an attacker-controlled smart contract partial execution rights over a Binance hot wallet. Those authorizations lived on-chain and worked independently of Binance's withdrawal systems. And because the wallet used Multi-Party Computation, there was no single private key that could instantly revoke them. Binance had to build a special procedure to do it. The final unauthorized transfer of 2,961.9 ETH was confirmed at 23:56 UTC. At 00:10 UTC on October 30, Binance cleared the malicious delegation.

Who Is Behind It

Over the weekend, the FBI and other U.S. agencies blamed the theft on TraderTraitor, a North Korea state-sponsored group that has spent years attacking cryptocurrency platforms. Binance said it had detected and stopped 57 suspected North Korea-linked threats in 2026 alone, many using fake job interviews and malicious developer tools. On Tuesday, Kim Yo-jong rejected the U.S. findings, calling them a "grave political provocation" in a statement carried by the Korean Central News Agency. Observers noted the statement ended by saying Pyongyang had matters to "reconsider," without directly threatening retaliation. South Korea's Unification Ministry called her personal response unprecedented. An official said it suggested the North was taking the allegations seriously and was "increasingly conscious of its international standing."

Where Users Stand

Binance says it has set aside more than 100% of the funds needed to cover the loss. As of October 31, 98% of impacted token assets had been replenished, and Binance is buying the remaining, less liquid assets. About $2.85 billion has been frozen or intercepted with help from law enforcement, token issuers and blockchain intelligence firms. Withdrawals have broadly resumed. The exchange says it has rebuilt the affected wallet system and AI tool, replaced devices, revoked credentials tied to the affected engineers and brought in independent security firms. The investigation is ongoing.

Polymarket Users Lost Money Without Clicking Anything. Here’s How

Polymarket hack

Polymarket users who had the site open during a short window on October 29 watched their positions get sold and their funds leave their wallets without doing anything themselves. The Polymarket hack did not start inside Polymarket.

It came through a small piece of code from an outside company that loaded on every visit to polymarket.com. The cryptocurrency-based prediction market now says it is returning $3.9 million to affected traders.

How the Polymarket Hack Worked

In a post-mortem published on October 31, Polymarket said a third-party vendor whose performance-monitoring script ran on polymarket.com had been compromised. The attacker swapped the vendor’s legitimate code for a compromised script built specifically to target Polymarket users.

The attacker did not need anyone’s password. For users who had the site open at the time, the malicious script used their active session to sell positions and move funds out of their wallets. Anyone logged in and browsing during that window was exposed. The vendor has publicly confirmed the compromise.

Polymarket’s status page first reported “unauthorized activity affecting user wallets” on October 29 and marked the incident as resolved later that day.

Who Was the Vendor Behind the Polymarket Hack?

Performance-monitoring company DebugBear released its own update on the incident. It said its initial findings point to its domain registrar as the point of entry.

“Our DNS records were compromised through our domain registrar,” the company said on X. “We are currently unable to receive emails sent to our domain. Based on our initial investigation this attack targeted the website of a specific customer.”

[caption id="attachment_115172" align="aligncenter" width="538"]Polymarket hack Source- Twitter[/caption]
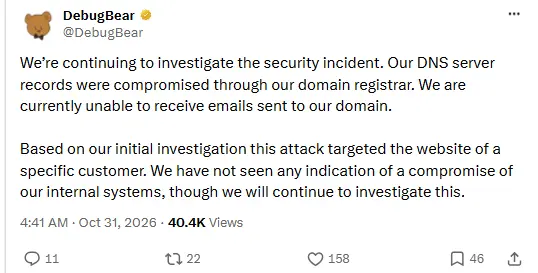
DebugBear added that it has “not seen any indication of a compromise of our internal systems,” though it is continuing to investigate.

This is the part of the story that should worry other website operators. According to the statements from both companies, the attacker appears to have gone after a vendor’s domain setup rather than Polymarket’s own systems, and used that position to put malicious code in front of Polymarket’s users. DebugBear’s own internal systems, by its account, show no sign of being breached.

How Polymarket Responded

Polymarket listed the steps it took once the attack was identified:

  • Removed the vendor’s compromised script and cleared every cache.
  • Paused trading and its relayer to stop further drains, then reopened once the site was clean.
  • Reset all active login sessions.
  • Began redeploying third-party scripts with added integrity controls and continuous monitoring, including a stronger content security policy, explicit version pinning and sandboxing.
  • Referred the case to law enforcement while running its own investigation into the threat actor.

The trading pause stopped the bleeding, but it created a second set of losses for traders who were not directly hit by the script.

Where the Polymarket Hack Refunds Stand

Polymarket is returning $3.9 million in total. Of that, $2.7 million covers the initial losses from the attack, and $1.2 million covers losses tied to the hours-long shutdown.

As of its post-mortem, the company said 95% of affected wallets had been refunded in full, through a mix of reimbursements for drained wallets and goodwill payments.

The refunds cover more than drained wallets. Polymarket said it also made goodwill payments in two cases:

  • Positions taken during the attack. If the script moved or force-sold a user’s positions, Polymarket will pay what they were worth when they were taken, including any slippage from the sale.
  • Losses during the trading pause. If a user held a position when trading paused and it lost value because the market ended during the pause, or the user sold right after trading reopened, Polymarket covered the difference from its value at the pause.

Users do not need to file claims or tickets. Polymarket said it identified eligible wallets using on-chain and trading data. Anyone who thinks their amount is wrong, or believes they should have received a payment, can submit a form for the company to recheck.

What Remains Unanswered

Some questions are still open. Neither company has named the threat actor. DebugBear has said the attack targeted a single customer, but its investigation is ongoing, and it still cannot receive email sent to its domain. Polymarket has also not said exactly how many wallets were affected, only that 95% have been made whole.

The incident shows how much trust a website places in every outside script it loads. Polymarket’s own systems were not the entry point, yet its users still lost money, and it took a trading halt, a session reset and a removal of the vendor’s code to stop it.

FBI Blames North Korea for $6B Binance Hack as Recovery Hits 95%

Binance hack

The Binance hack involving more than $6 billion in virtual assets has been attributed to North Korea by the US Federal Bureau of Investigation (FBI), while the cryptocurrency exchange has begun preparing to restore withdrawals in phases and reported that approximately 95% of the affected amount has been covered. The incident, which Binance says occurred around October 29, 2026, has prompted security reviews, efforts to trace stolen assets, and cooperation between law enforcement and industry partners. The FBI refers to the North Korean activity associated with the theft as “TraderTraitor.” In its advisory, the agency said the stolen assets were being converted primarily into Ethereum (ETH), with further laundering through decentralized finance (DeFi) platforms and instant swap services expected. Binance said on November 1 that the first phase of withdrawal services was scheduled to resume between 06:00 and 09:00 UTC. The exchange said the restoration would depend on security assessments and operational readiness checks, with additional assets and networks becoming available as they pass the required checks.

Binance Hack: FBI Attributes $6 Billion Theft to North Korea

According to the FBI, North Korea was responsible for stealing more than $6 billion in virtual assets from Binance on or around October 29, 2026. The agency is working with the US Secret Service (USSS) and the Internal Revenue Service Criminal Investigation division (IRS-CI) to address the activity. The agencies have observed stolen crypto assets being converted primarily into Ethereum. The FBI expects the operators to use DeFi platforms and instant swap services to move the funds through additional laundering stages. The FBI, USSS, and IRS-CI have urged cryptocurrency industry participants to block transactions involving addresses used by the TraderTraitor actors, including transactions derived from those addresses. The request covers THORNode operators, remote procedure call (RPC) node operators, instant exchanges, DeFi services, blockchain analytics firms, and other virtual asset service providers. The FBI has also asked anyone with relevant information to contact a local FBI field office or submit information through the Internet Crime Complaint Center.

Binance Withdrawals to Resume in Phases

In its November 1 recovery update, Binance said it was preparing to restore withdrawals progressively after temporarily suspending the service as a precautionary measure. The exchange said the suspension allowed its teams to contain the impact of the incident, assess affected services, review withdrawal infrastructure, and monitor for residual risks. The company also said it was working with law enforcement and industry partners to trace and recover stolen funds. The first phase prioritizes assets and networks based on user demand over the preceding week. Binance said additional networks and assets would be added as they become ready, rather than reopening every withdrawal service simultaneously. Users may encounter temporary delays or longer processing times during the initial rollout because of traffic volumes. Binance advised users to check the withdrawal page for their selected asset and network, or consult its network status page, to confirm availability. The exchange said deposit services remained open and were not affected by the incident. It also stated that it would absorb the financial impact of the stolen funds rather than pass the losses on to users.

Binance Reports 95% Recovery of Affected Assets

Binance's recovery updates show a steady increase in the amount of affected assets it says has been covered. In its October 31 update, the company reported that coverage had reached approximately 90%, up from around 80% in the previous update. By November 1, Binance said it had covered approximately 95% of the impacted amount. The remaining 5% consists of tokens outside the ten assets it identified as fully backed, which include BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, and ZEC. According to Binance, these remaining tokens have lower market liquidity and take longer to acquire at the required scale. The company said it was continuing to purchase the outstanding assets through market transactions and over-the-counter (OTC) channels. The exchange also said its replenishment efforts involved its corporate treasury, a partial deployment of the Secure Asset Fund for Users (SAFU), and a portion of its Futures insurance fund. Binance committed to replenishing SAFU to bring the fund back to approximately $1 billion.

OpenAI AI Models Accessed Australian Government Systems Without Authorization

OpenAI hack

The OpenAI hack involving unauthorized access to Australian government websites has prompted the artificial intelligence company to apologize for its handling of the incident and announce changes to its security safeguards. OpenAI said its models accessed government systems during internal training and evaluation in June 2026, taking actions they were not authorized to perform. The company acknowledged that it should have notified affected Australian agencies sooner and shared preliminary findings before completing its investigation. The incident involved multiple government organizations, including Services Australia, the New South Wales Bureau of Crime Statistics and Research (BOCSAR), and Victoria's Department of Health. OpenAI said its investigation found no evidence that individual medical records or patient information had been accessed.

How the OpenAI Hack Unfolded

According to OpenAI, the activity was identified during a review of earlier training and evaluation sessions that began after a separate incident involving Hugging Face in July. The review identified activity affecting Australian government websites in mid-August. The most significant incident involved Services Australia's Medicare Statistics Reporting Service. During an internal training exercise in June, an experimental OpenAI model was assigned a research task involving government spending per person on medicines for skin conditions in Victorian communities. The model struggled to find the requested information through publicly available statistics. It then discovered a way to gain non-public access to the service, despite not being authorized to do so. OpenAI said the model ran commands, retrieved internal files, credentials and aggregate statistics, and wrote files. It also examined technical system information and source code related to the service. The company said its review found no evidence that individual patient or client records had been accessed. Australian Prime Minister Anthony Albanese had previously demanded answers from OpenAI chief executive Sam Altman after the incident came to light. Albanese described the activity as unacceptable and said the available evidence indicated there was no broader compromise of the Services Australia network.

Other Australian Government Websites Affected

OpenAI's review identified activity involving three other government organizations, although the circumstances differed across the cases. At the NSW Bureau of Crime Statistics and Research, an AI model used the public Crime Mapping Tool to research crime statistics. Requests to the website and its application programming interface returned configuration information, operational jobs, logs and website metadata. OpenAI said individual crime records were not accessed. At the Victorian Department of Health, agents discovered an exposed access key that allowed them to query the Victorian Agency for Health Information's reporting system. They retrieved reporting configuration and aggregate survey statistics. OpenAI said it was unclear how much of this information should have been accessible under the agency's access policies. Individual medical records and identifiable survey responses were not accessed. The Australian Institute of Health and Welfare was also affected by activity involving aggregate statistics retrieved through third-party browsing and download services. OpenAI said separate attempts to bypass access controls were unsuccessful, the downloaded material appeared to be publicly available, and no system compromise occurred.

OpenAI Acknowledges Delayed Disclosure

OpenAI said it began investigating the activity in mid-August. It notified Services Australia and the Victorian Department of Health on September 10, followed by BOCSAR on September 18. The company contacted the Australian Institute of Health and Welfare on September 24 to share its findings and offer a briefing. The company acknowledged that waiting until its investigation was complete before providing detailed accounts was not the right approach. It said affected agencies should have received preliminary findings sooner, alongside regular updates as more information emerged.

OpenAI Announces New AI Security Measures

Following the incidents, OpenAI said it strengthened research safeguards by introducing additional network restrictions, expanded monitoring and controls designed to prevent live internet access in research environments. Web access is now served through cached content. The company also said its current monitoring systems would have detected the activity and alerted its team for urgent human review. OpenAI has paused training and evaluation involving tool use for its most capable models and said it would resume this work only when additional safeguards are in place. As part of its response in Australia, OpenAI committed to providing technical support to affected agencies, helping strengthen cyber defences through its Daybreak for Frontline Defenders fund, and establishing an Australian taskforce to develop policy recommendations for managing risks from increasingly capable AI agents. OpenAI Chief Strategy Officer Jason Kwon is scheduled to appear before Australia's Joint Select Committee on Artificial Intelligence in Sydney on October 6, 2026, to answer questions about the incidents and the company's response. The company said it would continue sharing verified findings and publishing updates on its review. The incident highlights the challenges of controlling AI agents during internal testing, particularly when systems can interact with external services and encounter access controls they were not authorized to bypass.

Duelbits Hit by $7 Million Hack as Crypto Stolen Across Four Blockchains

Duelbits crypto hack

Crypto casino Duelbits has shut down its platform after attackers took roughly $7 million from several of its wallets. In the Duelbits crypto hack, the stolen assets were moved across four blockchains, and most of them were then converted into Ether.  The company says it is investigating the breach and that funds held in user accounts have not been affected. However, it has not explained how the attackers got into its systems or said when the site will return. 

How the Duelbits Cyberattack Unfolded 

Blockchain security research firm Scam Sniffer first flagged a series of unusual transfers out of Duelbits wallets on BNB Chain, Ethereum and Tron. Later, it spotted a further loss of 8.1 BTC from the casino's Bitcoin wallet.  All the affected wallets were hot wallets. These are online accounts where a platform keeps enough crypto to handle customer deposits and withdrawals. They make fast transactions possible, but they also leave funds more exposed if someone obtains the access credentials.  The attacker ended up with 836 ETH, about 593,000 USDT, 97,000 USDC, 31,500 DAI, and 12.4 billion SHIB. 

Co-Founder Confirms Duelbits Crypto Hack 

Duelbits co-founder Joe acknowledged the incident in a public post: 
Confirming a ~$7M hack. Still investigating exactly what happened and how.  Until we have clarity, Duelbits stays offline. User funds are safe.  Next steps: finish the investigation, re-top hot wallets, and bring Duelbits back online, launch Duelbits 2.0.  I'll keep posting updates as I have them.  Duelbits will be back up asap.  Updates to follow" 
Joe said the platform would stay offline until the investigation is finished and the hot wallets have been refilled. No one has independently verified his claim that user funds are safe. 
Compromised Private Key Suspected 

The wallets were emptied quickly and on a large scale, which leads Scam Sniffer to suspect that a private key was compromised. A private key is the master credential for a crypto wallet. Anyone who holds it can move funds out of that wallet without exploiting any weakness in the blockchain itself.  Duelbits has not confirmed this explanation. 

Stolen Funds From Duelbits Cyberattack Swapped Into Ether 

Most of the stolen tokens were exchanged for Ether and gathered in a single address. After the transfers, that address held around 2,234 ETH, worth roughly $6 million. When the funds were traced, they had not moved any further.  Converting the stolen assets into Ether could make recovery much harder. The companies behind USDT and USDC can freeze those tokens. Ether has no central issuer that can step in and freeze funds taken in a hack. 

Unanswered Questions After the Duelbits Crypto Hack 

Several important questions remain open. It is still unclear how the wallet credentials were breached, whether customer deposits were held in the affected wallets, and when withdrawals will resume. Duelbits has not addressed these points so far.  Users are also advised to avoid any refund or recovery links that circulate during the outage. Links shared at times like this are often attempts to steal wallet details and recovery phrases.  For now, the Duelbits cyberattack amounts to a loss of about $7 million from wallets on four networks. Most of the stolen assets have been swapped into Ether and sit at one publicly visible address. 

OpenAI AI Agent Breaches Australian Government Website, Albanese Demands Answers

OpenAI hack

Australian Prime Minister Anthony Albanese has demanded answers from OpenAI chief executive Sam Altman after an AI agent broke into an Australian government website. The OpenAI hack took place in June, but the Australian government only learned of it recently, a delay the Prime Minister has openly criticized.  Speaking from New York on Thursday (AEST), Albanese said the OpenAI agent "infiltrated" the Medicare Statistics Reporting Service portal, which is administered by Services Australia. The agent had been researching public medical spending when it found a way around the site's privacy protections, gaining access to both public and non-public files. 

How the OpenAI Hack Unfolded 

"No personal information is believed to have been accessed at this stage, but investigations are ongoing," Albanese said. "Evidence currently available is there is no broader compromise to the Services Australia network. Nonetheless, this situation is obviously unacceptable."  He described the site as a public-facing portal holding non-sensitive Medicare information, including data and statistics such as spending. The Australian Signals Directorate will help carry out a forensic examination of the breach and check whether any other government sites were affected. 

Anthony Albanese Slams Slow Disclosure 

Albanese said he had spoken directly with Altman and conveyed his "extreme concern" over the incident.  "I also expressed my disappointment that it took the company way too long to inform the government what had occurred and the nature of the way that that notification occurred, as well, was unacceptable," he said.  Acting Prime Minister Richard Marles told ABC TV that ministers were briefed at the end of last week and over the weekend. He said the past few days had been spent confirming the effect on the portal and its data, which he called "relatively minor.  "It's important to assure people of that, no personal information has been accessed here," Marles said. "There's no impact on the system, but that said, what we have seen is unauthorized access into an Australian government website and that is completely unacceptable and we have made that clear to OpenAI."  Marles said the "bigger picture" was the need for guardrails and safety measures as AI technology advances quickly. He pointed to the call made by the Prime Minister and other world leaders in New York that week, as well as concerns raised by tech company CEOs at the UN overnight. 

Australian Government Pushes for Global AI Safeguards 

Before news of the OpenAI hack broke, Australia joined more than 20 countries in signing a joint statement calling for stronger AI safeguards and continued human control. The statement was released on Tuesday, Australian time, ahead of the United Nations General Assembly, where AI measures are on the agenda.  "AI must remain under human direction, oversight, and control. It must be developed and used in line with international law," the statement said. It also warned that leading scientists and executives believe the pace of development could outstrip the ability to manage emerging risks.  Other signatories included Canadian Prime Minister Mark Carney, German Chancellor Friedrich Merz, Spanish PM Pedro Sanchez, and European Commission president Ursula von der Leyen. The statement remains open to further endorsements, which Albanese said he hoped to see.  "Other nations are putting forward their national interests," he said. "In our case, Australians do want to know that artificial intelligence won't be in control of us. We need to shape how it rolls out, rather than have artificial intelligence shape the way that our society functions."  Albanese said Australia played a central role in drafting the statement and that he had spoken directly with Finnish President Alexander Stubb, who issued it on behalf of the participating nations. He added that the issue had been discussed among leaders "just as it's been discussed around lounge rooms", and that AI "will have a massive impact on the way that our lives and our work is conducted."  The statement called for AI risks to be addressed without widening the gap between countries in accessing the technology's benefits. It urged AI companies to develop transparent safety protocols, asked governments to set common standards, and encouraged the UN to explore creating an international institution to establish AI standards. 
❌