 Entrar

The 2026 Infostealer Intelligence Shortlist: Top 10 Vendors Security Teams Should Know


Cyble, a global AI-native cybersecurity company, has signed a Memorandum of Understanding (MOU) with the Cyber Security Council of the United Arab Emirates to strengthen national threat intelligence capabilities. The agreement was announced in Abu Dhabi in September 2026 and formalizes a strategic collaboration between Cyble and the federal entity responsible for strengthening the UAE's cybersecurity posture.
The MOU marks a significant milestone in Cyble's engagement with the UAE's national cybersecurity ecosystem, bringing together a global cybersecurity provider and a national authority tasked with protecting the country's digital environment.
The MOU establishes a framework for Cyble to support the Council's mission of protecting the UAE's digital infrastructure. The collaboration centers on delivering advanced threat intelligence, early warning capabilities, and actionable insights into emerging cyber risks facing government and critical infrastructure entities across the country. These focus areas are intended to help the Council anticipate and respond to threats before they escalate into significant incidents.
The partnership reflects the UAE's continued commitment to building a resilient, forward-looking cybersecurity posture at the national level. It also positions Cyble as a trusted technology partner in that effort.
By working closely with the Council, Cyble aims to strengthen visibility into threat actors, malicious campaigns, and vulnerabilities that could affect the UAE's most critical systems and services. This visibility is expected to support the Council's broader objective of maintaining a secure and stable digital environment for government and critical infrastructure operators.
Beenu Arora, CEO and Co-Founder of Cyble, described the agreement as more than a routine partnership announcement. He called it a strategic validation of Cyble's capabilities at the national cybersecurity level and a potential gateway to the UAE government and critical infrastructure ecosystem. This is not just a partnership announcement. It is a strategic validation of Cyble's capabilities at the national cybersecurity level and potentially a gateway to the UAE government and critical-infrastructure ecosystem," said Arora.
Arora added that working alongside the Cyber Security Council underscores the trust placed in Cyble's threat intelligence platform and reflects the growing importance of proactive, intelligence led defense in protecting nations against increasingly sophisticated cyber threats.
Dr. Mohamed Al Kuwaiti, Chairman of the Cyber Security Council of the United Arab Emirates, said the Council is committed to building strategic partnerships with world class technology providers that strengthen the UAE's cyber resilience at every level. He noted that the MOU with Cyble reflects a shared commitment to safeguarding the nation's digital infrastructure through advanced threat intelligence and proactive, intelligence led defense, ensuring the UAE remains at the forefront of global cybersecurity readiness.
"This MOU with Cyble reflects our shared commitment to safeguarding the nation's digital infrastructure through advanced threat intelligence and proactive, intelligence-led defense — ensuring the UAE remains at the forefront of global cybersecurity readiness," said Dr. Mohamed Al Kuwaiti.
The agreement builds on Cyble's broader strategy of deepening engagement with government and regulatory bodies across the Middle East. It reinforces the company's position as a trusted partner to national cybersecurity authorities navigating an increasingly complex threat landscape, and it adds to a growing list of engagements between Cyble and public sector organizations in the region.
Cyble Vision, the company's threat intelligence platform powered by Blaze AI, will play a central role in the collaboration. The platform is designed to deliver rapid detection, automated analysis, and contextual insights into ransomware, phishing, fraud, and other evolving threats relevant to national security priorities. Through this platform, Cyble intends to provide the Council with tools that support faster identification and analysis of threats targeting the UAE's digital infrastructure.
Cyble is a global, AI-native cybersecurity company specializing in threat intelligence, digital risk protection, and dark web monitoring. Its flagship platform, Cyble Vision, powered by Blaze AI, delivers rapid threat detection, automated analysis, and contextual insights into ransomware, phishing, and fraud.
Media Contacts: enquiries@cyble.com | +1 678 379 3241 | www.cyble.com
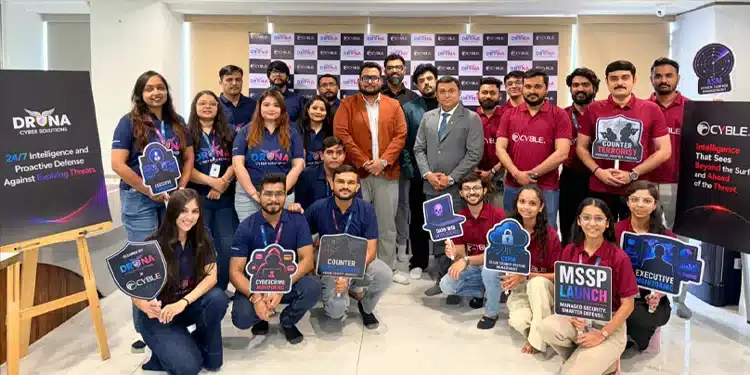
The AI-Powered Intelligence for Cyber Defense initiative was formally launched Tuesday at DRONA Cyber Solutions' Command and Control Centre, where the companies presented a live technical demonstration showing how an intrusion attempt can be detected, investigated and contained.
The launch comes as India faces a growing cybercrime burden. India recorded 28.15 lakh cybercrime cases in 2025, a 24 percent increase over the previous year, with reported losses reaching ₹22,495 crore. The government's 1930 cybercrime helpline received 32.4 million calls during the year. Of the complaints filed, 55,484 were converted into FIRs.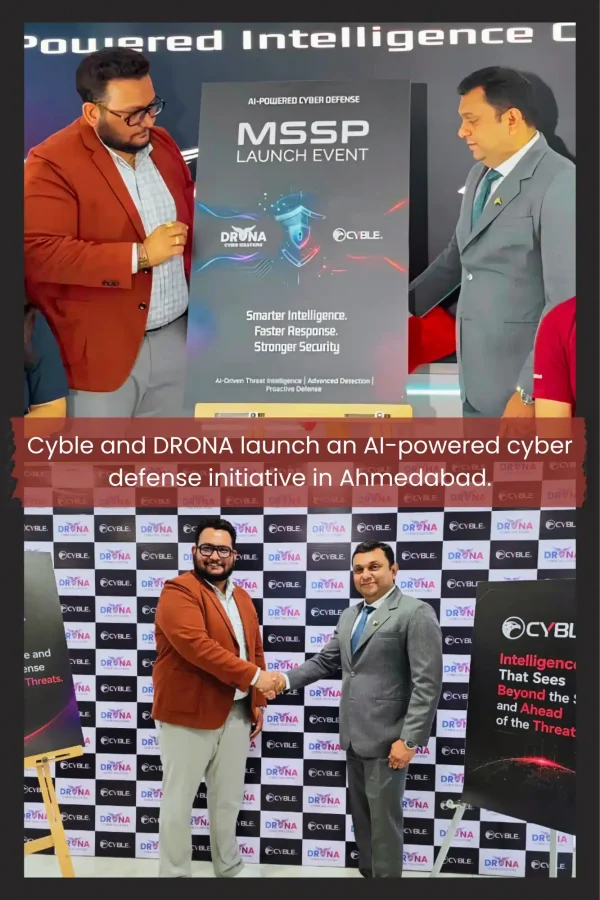 While large enterprises and banks increasingly have dedicated security teams, budgets and incident response capabilities, many manufacturers, hospital chains, schools and mid-sized businesses, particularly across Tier-2 and Tier-3 cities, continue to operate without comparable security resources.
The final containment action was authorised by a human analyst rather than executed automatically. The demonstration brought together multiple capabilities. Cyble Vision provided the initial detection through continuous monitoring of criminal marketplaces and leak sites.
Cyble Hawk supported the investigative process and attribution, while Cyble Titan handled endpoint enforcement, using hardware-level integrity checks to support its assessment. DRONA analysts remained at the centre of the process, making decisions that the system was deliberately not permitted to make independently. Mandar Patil, Executive Vice President at Cyble, said the initiative was designed to address a longstanding gap between threat detection and action for mid-sized businesses.
"India is not short of alerts. It is short of what happens next," Patil said. "We have spent a long time in this industry watching mid-sized businesses get told about a threat and then having nowhere to take that information. What we are launching today is not another alert. It is a complete chain — intelligence before the attack, investigation that would stand up to scrutiny, enforcement on the device, and a person accountable for the decision at the end of it."Dhruv Pandit, Co-Founder and CEO of DRONA Cyber Solutions, said the initiative reflects the operational needs of organisations that require immediate action rather than another security dashboard.
"A factory owner calling us at two in the morning does not want to be shown a dashboard," Pandit said. "He wants to know what happened, he wants it contained, and he wants someone to take responsibility for what happens next."
The session brought together speakers from Cyble and DRONA Cyber Solutions to examine areas including dark web threat intelligence, government and PSU cybersecurity projects, digital forensics and incident response (DFIR), and the transition of threat intelligence from information to action.
Mandar Patil and Augustin Kurian of Cyble discussed the dark web threat intelligence landscape. Prathmesh Pawar spoke about government and PSU cybersecurity projects, while Brijesh Kapadiya addressed DFIR and Vijay Mali discussed moving threat intelligence from information to action. The keynote was delivered by Prof. Dr. Kapil Kumar, Coordinator, Department of Biochemistry and Forensic Science.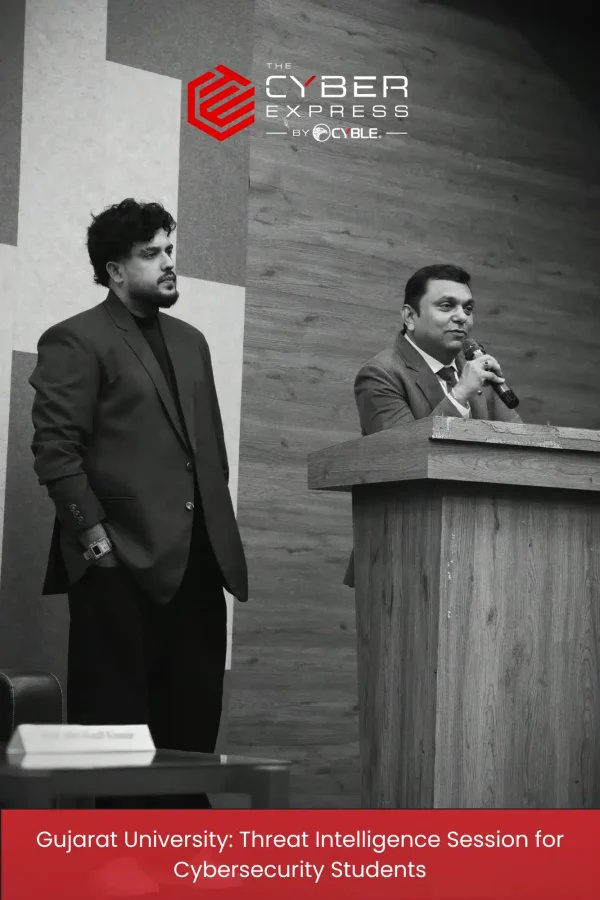
The session highlighted several practical aspects of cybersecurity work. The dark web was discussed not simply as a hidden part of the internet, but as a structured ecosystem requiring dedicated intelligence-gathering and threat-discovery methods. DFIR was presented as an area where speed and process are as important as technical expertise.
Another key takeaway was the importance of turning threat intelligence into action. Rather than treating intelligence as information alone, the session focused on how it can inform practical security decisions.
Patil told students that the cybersecurity industry faces a shortage of professionals with practical skills in analysing and validating threat intelligence."The gap this industry has is not a gap of ideas. It is a gap of people who know how to do the work," Patil said. "What separates a useful analyst from an alert-reader is the ability to ask whether a piece of intelligence is actually true before you act on it."Augustin Kurian, Editor-in-Chief of The Cyber Express, told students that threat intelligence and journalism share an emphasis on verification.
Every story we publish about a breach, a ransomware group or a leaked database starts exactly where today's demonstration started — with intelligence somebody had to go and find, verify, and decide was worth acting on," Kurian said. The instinct we have tried to build at The Cyber Express is the same instinct a good analyst needs: do not report, and do not act on, what you have not verified.The programme also involved technical and production teams supporting the session. Screen, sound and lighting were handled by the technical team under the guidance and supervision of Aditya More, while Misha Alagiya, Kavya Maharaja, Pathak Ami, Omi and Nandini supported stage management and photography.
"India's exposure is too large for any single partnership to take credit for solving," Patil said. "What matters is whether more of these collaborations exist a year from now, and whether the businesses we are talking about today — the ones without a security team — actually have somewhere to turn."
The AI-Powered Intelligence for Cyber Defense initiative will be delivered through DRONA's Ahmedabad command centre, with the companies indicating an intent to extend the service model to customers elsewhere in India over time.
The initiative also folds into DRONA's existing Cyber Yodha Campaign, a national programme aimed at building 50 integrated cybersecurity command centre labs and training more than 100,000 defenders.