
 Entrar

One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire
Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each.
Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail.
On September 1, Volexity detected a spear-phishing campaign by UTA0560 targeting several NGOs. The emails sent victims to a legitimate US university website, which had a cross-site scripting flaw that attackers used to redirect visitors to their own servers.
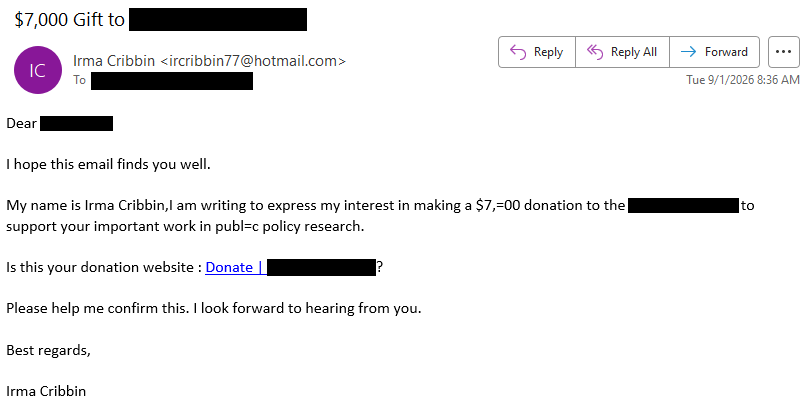
The victims were then exposed to a multi-stage attack using a Chrome zero-day CVE-2026-85046. Volexity later found JungleBamboo (also known as APT31, Violet Typhoon, or TA412) using the same exploit chain against different targets. The code was the same, but the infrastructure and final malware were different.
“The exploit first gains arbitrary read/write within the V8 sandbox through the Type confusion vulnerability (CVE-2026-85046), then combines a separate WebAssembly defect to escape the V8 sandbox (CVE-2026-87491). It then exploits a third vulnerability in the Windows kernel (CVE-2026-85880) to escape Chrome’s sandboxed renderer process and inject code into the Chrome browser process.” reads the report published by Volexity. “From there, exploit-chain users can deploy a payload of their choice. Volexity observed two distinct clusters of activity using the exploit chain to deliver different payloads:
- UTA0560 downloaded and deployed the GRIMWEDGE JScript backdoor providing host reconnaissance, file and process management, command execution, and payload delivery capabilities.
- JungleBamboo deployed SUPERSTOMP, a loader that installed the LONGTALE credential-stealing Chrome extension.”
Victims only saw an image of a donation form made to look like it belonged to the targeted organization. In reality, the page was there to steal, not collect, donations.
The core Chrome flaw, CVE-2026-85046, was reported to the Chromium project by a private researcher on August 4, 2026. A fix landed in the open-source Chromium codebase not long after. Google Chrome itself, though, hadn’t shipped that fix yet when the phishing started.
” This created an unusual patch gap: The vulnerability was known and fixed upstream, making it an N-day at the Chromium source level, but there was no patch release for Google Chrome users.” continues the report. “Therefore, the exploit was effectively a zero-day against Google Chrome.”
Someone was watching the Chromium source repository closely enough to catch a fix before most users ever got it, and turned it into a working exploit within weeks. Volexity researchers found byte-for-byte identical shellcode across both campaigns. UTA0560 and JungleBamboo weren’t independently reinventing the same exploit; they were running the same one.
The exploit page was far more sophisticated than it first appeared. It accepted 13 URL parameters to support testing, breakpoints, telemetry, and controlled rollouts.
That level of preparation doesn’t look like a quick attack put together on the fly. It suggests the attackers had built a proper development and testing framework, which was either left in place or deliberately used in the live campaign.
Once code execution lands, the two operators split. UTA0560 used its access to drop a custom loader chain ending in GRIMWEDGE, a JScript backdoor running entirely in memory inside msiexec.exe. It’s compact, under 250 lines, but it covers the basics: file operations, process management, command execution, and file upload.
JungleBamboo took a different route. It deployed a loader Volexity calls SUPERSTOMP, which installs a malicious Chrome extension named LONGTALE. The extension masquerades as a Google Gemini assistant and logs every keystroke, steals cookies and session tokens, and takes screenshots when it spots keywords supplied by its command server.
LONGTALE has no remote code execution command at all. It doesn’t need one. Volexity assesses the credential and session theft alone gave JungleBamboo everything it needed, and extensions like this tend to slip past detection more easily than a standalone executable.
Chrome has spent the last year hardening exactly the kind of tampering SUPERSTOMP relies on. Per-preference encrypted hashes arrived in November 2025, and a full-profile integrity check followed in June 2026. SUPERSTOMP still gets through, by stripping the new hashes, forging the older legacy HMAC values Chrome still accepts as a fallback, and letting Chrome’s own migration logic re-authenticate the tampered profile as legitimate.
“Chrome enables this legacy fallback method by default in its releases as of September 8, 2026; only compiling Chromium from source disables it.” Volexity states. “This technique was added to one of the most popular GitHub repositories relating to silent installation of Chrome extensions on August 6, 2026.”
Worth noting: this exact technique showed up in a popular GitHub repository for silent Chrome extension installs on August 6, 2026, weeks before JungleBamboo’s campaign. The line between public research and operational tradecraft keeps getting shorter.
The attribution work here is tidy. UTA0560’s link to its March 2026 campaigns rests on three points: the same phishing sender address, the same hosting IP for its exploit infrastructure, and a per-host beacon naming scheme that mirrors what UTA0560 used six months earlier.
“Volexity assesses with low confidence that the exploit chain may have been sold, or otherwise provided, to different end-users in China, hence the near-simultaneous campaigns conducted by separate threat actors using distinct post-exploitation malware. Volexity assesses with medium confidence that the short time window offered by the Chrome patch delay necessitated that these threat actors reuse the core exploit code without modification.” states the report. “Furthermore, the payloads used by each threat actor were compiled using different toolsets, suggesting entirely different development environments preferred by each malware developer.”
Proofpoint reported similar findings around the same time. It calls the exploit kit BlueMoon and says JungleBamboo first used it on August 28, several days before Volexity detected the campaign.
Proofpoint identified four different groups using the same code within about two weeks. One, tracked as UNK_LateNight, targeted US aerospace companies with the ShadowPad backdoor. Another, UNK_DoubleCheck, targeted a manufacturing company in Vietnam.
Proofpoint also found an interesting clue about how the exploit may have been developed. Some code artifacts suggest the attackers could have used AI during development. There’s no proof of that, but the diagnostic logs, handover notes, and debugging comments look unusual for a professionally developed exploit.
Google patched CVE-2026-85046 in the Stable Channel update on September 3, moving users to Chrome 152.0.7977.82 or .83, alongside eleven other fixes. CISA added the flaw to its Known Exploited Vulnerabilities catalog the next day, with a September 18 deadline for federal systems to remediate. If your fleet hasn’t relaunched Chrome since early September, it’s worth checking the version number rather than assuming the auto-update did its job.
Volexity’s closing point is the one to actually remember here, and it’s not really about UTA0560 or JungleBamboo specifically.
“As large language models become more popular and effective for rapid vulnerability research and exploit development, Volexity assesses with high confidence that patch-gap vulnerabilities present an even greater risk, as they create an additional time window for threat actors to conduct exploitation campaigns.” concludes the report.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Chrome)


