Security Blind Spots Identified by AI The large-scale data breaches disclosed in quick succession in South Korea and Japan in October 2026 mostly originated not from internal core systems, but from peripheral entry points such as externally exposed web services, app backend APIs, and outsourced SaaS (services provided by third-party vendors via the cloud, such […]
PHP2Shell attacks have surged into the millions, but no successful exploitation is confirmed. Patch it immediately.
On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives in the PHP engine itself rather than in any application, and allows unauthenticated remote code execution via crafted HTTP requests.
Cloudflare researchers observed tens of thousands of exploit attempts within 45 minutes of public disclosure, hundreds of thousands within two hours, and millions by October 22.
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
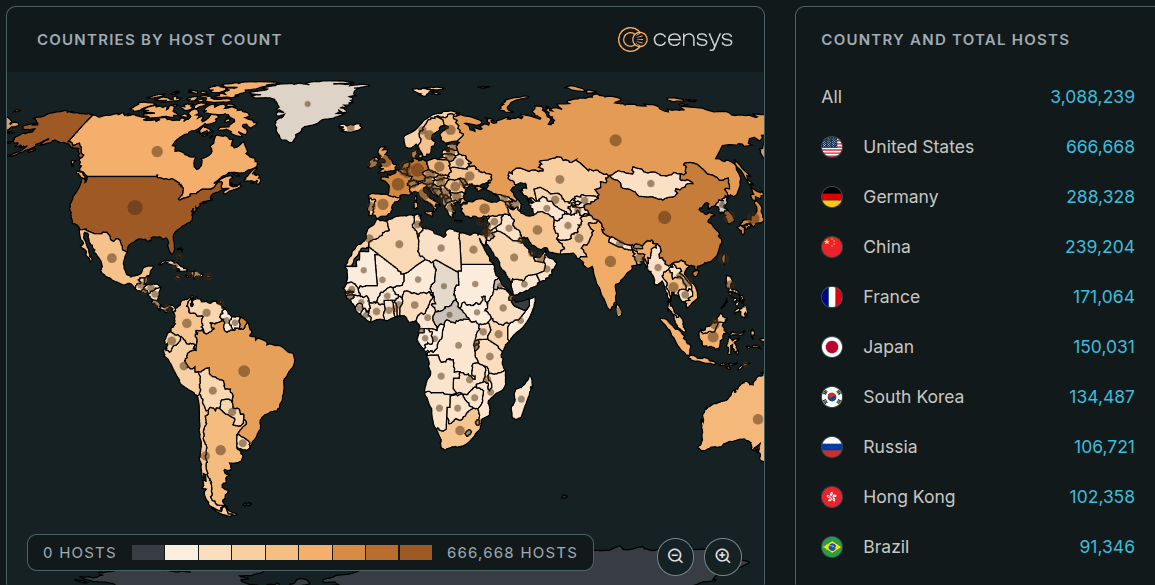
As of October 23, Censys counts over 34.4 million PHP services still running vulnerable versions. Governments, hospitals, and schools across Asia, Europe, and North America have preemptively taken services offline rather than wait.
Below is an image showing the hosts potentially vulnerable to CVE-2026-109618 and/or CVE-2026-109619.
Security firms using honeypots report the same pattern: attackers are scanning many servers and trying to exploit the PHP flaws, but no successful remote code execution has been confirmed in real-world attacks. Sophos says this suggests that attackers are also struggling to exploit the vulnerabilities. Even its own security team needed more effort than expected, despite using AI, to develop a working exploit.
However, the risk is growing. VulnCheck researchers have developed an exploit that bypasses ASLR, a security feature that randomizes where code is stored in memory. By combining both vulnerabilities, they can use a memory leak to bypass this protection and run code on the target system. The exploit works, even though there is no evidence of widespread use yet.
The attempts that have been caught so far are mostly scanning, fingerprinting, and botnet delivery attempts. Cowrai’s analysis of PHP2Shell traffic in the wild found connections to a Mirai variant called Potassium, which contacts a C2 server, checks for an HTTP 200 response, then downloads a Linux executable as a follow-on payload.
“The payload, a likely Mirai botnet variant known as Potassium, was not delivered since the exploitation attempt was unsuccessful due to being blocked by Sophos countermeasures.” states the report published by Sophos. “However, analysis of the sample revealed that is an updated and significantly expanded version of the Mirai-derived botnet variant identified in early 2026.”
The malware can download additional files and disrupt networks. It contacts a hard-coded command-and-control server, checks that the server responds successfully, and downloads a file designed to run on Linux. If normal address lookup fails, it can use public DNS servers such as Google DNS and Cloudflare DNS. Like other Mirai malware, it can also launch distributed denial-of-service (DDoS) attacks.
Arctic Wolf found that both malware samples had Ethereum Name Service (ENS) resolution disabled, meaning the feature was available but not active.
“ENS resolution was disabled in both samples, indicating that the capability was present but inactive.” states Arctic Wolf. “If enabled in future variants, it could complicate disruption by reducing reliance on registrars and DNS providers, requiring defenders to block the ENS names, RPC infrastructure, and resolved command-and-control addresses.”
The botnet’s developers have already added the ability to use ENS to find command-and-control (C2) servers. This could help them keep their infrastructure online and make it harder for authorities to take down their domains, but the feature has not yet been enabled.
Sophos blocked the attempted Potassium delivery before it succeeded. But analysis of the sample itself showed it’s a significantly expanded version of the Mirai variant spotted earlier in 2026, with added DDoS capabilities and fallback DNS resolution using public servers like 8.8.8.8 and 1.1.1.1 hardcoded as backup.
PHP2Shell is being compared to Log4Shell because it affects a huge number of systems. The flaw is in PHP itself, so it can affect websites, content management systems and shared hosting services. Even a basic WordPress site with no extra plugins is at risk if it uses a vulnerable PHP version.
Fixes are available in PHP versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Older versions, including 7.4, 8.0 and 8.1, need fixes provided by their software distributors or an upgrade to a supported version.
Cisco Talos notes that scanning for flaws and using public exploit code is easier than building attacks into custom tools. Advanced attackers may still be developing those tools, so administrators should use this time to patch vulnerable systems.
“The true impact of this vulnerability will take time to evaluate.” concludes Talos. “These types of vulnerabilities that impact core technologies tend to cascade into other platforms and applications as they evaluate impact and provide associated patching, harkening back to the waves of exploitation that we saw after Log4J.”
AWS detected PHP2Shell exploit attempts four days before disclosure, highlighting the risk of attackers exploiting critical flaws before patches arrive.
Attackers attempted to exploit two critical PHP vulnerabilities four days before the flaws became public, according to Amazon Threat Intelligence.
“Amazon Threat Intelligence identified a PHP2Shell exploitation attempt dating to Oct. 17, 2026, in MadPot telemetry, four days before public disclosure of CVE-2026-109618 and CVE-2026-109619.” reads the report published by Amazon team.”The exploit attempt originated from an IP address associated with a commercial anonymization network. While the vulnerability was under embargo, the targeting of a honeypot from an anonymized IP address suggests the activity was conducted by a threat actor, though it remains unclear how the actor acquired exploit information prior to disclosure.”
The activity began on October 17, 2026, and appeared in telemetry from MadPot, AWS’s network of honeypots designed to attract and study malicious activity. The company said the first attempt targeted a honeypot from an IP address linked to a commercial anonymization network. The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, were still under embargo at the time.
AWS believes the use of anonymized infrastructure suggests a threat actor was behind the activity. However, the company hasn’t established how the attacker obtained information about the vulnerabilities before their public disclosure, nor has it confirmed that the early attempts would have succeeded against real-world systems.
The first attempt wasn’t an isolated event. AWS detected multiple proof-of-concept exploits on October 21, with the earliest appearing at around 02:00 UTC, roughly 12 hours before the scheduled public release and patch at 14:00 UTC.
Between 02:00 and 08:00 UTC that day, AWS observed further attempts against MadPot from additional anonymized infrastructure. The payloads and anonymization services varied, leading the company to suspect that multiple actors were involved.
After the embargo ended and PHP released the fixes, more proof-of-concept exploits appeared within hours. AWS reported that attackers used them against its sensors almost immediately, describing PHP2Shell as being broadly exploited in the wild.
The findings show why the date of a public security advisory can’t always serve as the starting point for an incident investigation. In this case, defenders had to account for activity that began before they could publicly identify the vulnerabilities.
“The actual payloads and choices in anonymization infrastructure varied, suggesting these were multiple actors.” continues the report. “Technical analysis is ongoing, and it’s unclear if any of these attempts would have succeeded in real-world systems.”
PHP2Shell refers to two critical flaws in the PHP runtime that can allow unauthenticated remote code execution. An attacker may be able to send a specially crafted web request and run commands on a vulnerable server without first logging in.
PHP published fixes on October 21. The corrected releases are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, according to the official PHP security notice.
The vulnerabilities affect PHP itself, rather than a specific website application. As a result, updating WordPress, Drupal or another application won’t fix the underlying problem if the server continues to run a vulnerable PHP runtime.
AWS says there is no configuration-only workaround that fully addresses both flaws. Organizations should install the fixed PHP version as soon as possible and check whether their hosting provider, operating system vendor or container image has supplied the necessary update.
For systems that can’t be patched immediately, AWS suggests considering whether blocking multipart file uploads is practical. Administrators should assess the impact on their applications before applying that restriction, and they shouldn’t treat it as a replacement for installing the fixes.
AWS recommends reviewing web server logs for suspicious requests, particularly POST requests containing the PHP_SESSION_UPLOAD_PROGRESS string in multipart form data. Security teams should also look for unexpected processes launched by PHP and unexplained changes to files on web application servers.
These checks matter because an attack may leave evidence beyond the original HTTP request. Unexpected command interpreters, newly created files or unusual process activity can help investigators determine whether an attacker progressed beyond probing a vulnerable endpoint.
AWS also published six IP addresses associated with observed activity:
103.216.220.92, observed on October 17
31.223.184.166, observed on October 21
37.19.200.5, observed on October 21
134.209.159.64, observed on October 21
103.114.163.188, observed on October 21
95.217.98.37, observed on October 21
These addresses require careful handling. AWS warns that some belong to shared anonymization infrastructure and aren’t exclusive to PHP2Shell activity, so organizations should investigate matching events rather than automatically blocking every address.
The Cloudflare analysis of PHP2Shell provides additional context. Cloudflare said it had deployed web application firewall protections before public disclosure and had already observed attack traffic targeting its customers, including attempts to change payloads to evade those protections.
A web application firewall can help reduce exposure, but it doesn’t replace patching. Defenders should combine updated software with log analysis, process monitoring and checks for suspicious file changes.
AWS draws a broader lesson from the incident: organizations shouldn’t assume that exploitation begins only after a vulnerability becomes public. The October 17 activity shows that attackers may obtain or develop exploit information while a flaw is still under coordinated disclosure.
Attackers are using AI to develop exploits faster, sometimes within hours of a patch being released. Security teams need to patch critical systems quickly and investigate attacks from the earliest known date. For PHP2Shell, AWS recommends checking logs and activity from October 17 onward, including suspicious behavior that detection tools may not yet recognize.
Overview Immediately after the PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619 were disclosed on October 21, 2026, a large number of repositories named “php2shell” were created in a short period of time on GitHub, a code repository platform. Of the top 100 repositories (excluding forks) found by searching for “php2shell,” 99 addressed these vulnerabilities, and nearly all […]
On October 22, 2026, the PHP Security Team announced in an advisory that it would release security updates addressing the vulnerabilities CVE-2026-109618 and CVE-2026-109619. Although the causes of the two vulnerabilities differ, they are both remote code execution vulnerabilities that allow an unauthenticated threat actor to execute arbitrary code remotely. AhnLab SEcurity intelligence Center (ASEC) […]
Governments and cyber-security agencies worldwide are urging website operators to patch PHP2Shell, two critical PHP flaws tracked as CVE-2026-109618 and CVE-2026-109619. Found with AI, the bugs enable remote code execution and Heartbleed-style memory disclosure. A fix arrived on Wednesday afternoon.
Several agencies told organizations unable to patch in time to consider pulling their sites. Finland temporarily shut its government’s public web services. In the Netherlands, the cyber-security agency, the National Institute for Public Health and the Environment, and the Tweede Kamer, parliament’s lower house, all went offline.
The US National Security Agency echoed this on X: “These vulnerabilities often provide a direct path to the server’s file system or database.” The White House said federal agencies were working with leading AI labs to speed up a fix, while Japan’s Prime Minister Sanae Takaichi urged people on X to check whether their public websites ran on PHP.
“We have taken down a number of other systems as a precautionary measure until they can be safely patched,” the Wikimedia Foundation said, leaving parts of Wikipedia unreachable on Wednesday. Edinburgh council’s website and pages for BBC programmes, including Doctor Who and The Traitors, also went dark, though neither has confirmed a PHP link. DeviantArt said only that it was “temporarily down for maintenance.”
How AI found CVE-2026-109618 and CVE-2026-109619
Researchers at Calif and Wiz uncovered the flaws. Calif and the PHP Foundation were part of OpenAI’s Patch the Planet program, which offered AI tools to find and fix PHP flaws. Wiz called them the “most severe vulnerabilities ever discovered” by AI. OpenAI described them as “one of the most impactful security issues in recent memory,” adding that its own researcher spotted the issue around the same time.
The bugs sat undetected for over a decade before surfacing August, after a few weeks of AI-assisted work. “Frontier models were critical to making this process practical, enabling us to develop and adapt working exploits across multiple applications in hours,” Wiz said. It estimates “roughly 70%” of the internet is affected; a figure not independently verified.
The PHP Foundation planned to disclose PHP2Shell later this month with a full patch, but details leaked on social media on Tuesday, forcing a rushed announcement.
Early PHP2Shell Attacks Emerging
The UK’s National Cyber Security Centre (NCSC) and its EU and Australian counterparts urged PHP users to apply the fixes. “Where immediate remediation is not feasible, organizations should consider taking the system offline until it can be fully mitigated,” the NCSC said. Japan’s national cyber-security office and EU officials issued similar warnings.
“PHP is everywhere. It quietly powers WordPress, Drupal, Joomla, and Magento sites, shared hosting platforms, control panels, and an awful lot of software that doesn’t even advertise that it runs PHP under the hood,” said security firm Huntress.
Affected versions remain unclear, though CERT-EU said CVE-2026-109618 and CVE-2026-109619 could reach back to PHP 5, launched in 2004. The update covers only the latest versions; users on PHP 8.1 or older should upgrade. Built for web development, PHP runs server-side on a large share, though not all, of the internet.
Verify you are human
Checking your browser before accessing this site.
Click to verify →
Then you will be redirected to the requested content. Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare
On October 21, 2026, the PHP project released versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to fix two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both rated CVSS v4.0 9.2. The two flaws are known together as PHP2Shell. They were disclosed by the security firms Calif and Wiz and by OpenAI, working with the PHP security team, after AI-assisted auditing turned an out-of-memory weakness that a 2024 audit had flagged but could not prove exploitable into working remote code execution.
Both vulnerabilities sit in PHP's memory management and error handling, code that nearly every request touches, and the earliest affected path dates to PHP 5.4.0. An unauthenticated attacker can execute code on the web server or read its process memory, including passwords, tokens, and API keys belonging to other requests. On Apache with mod_php, the attack runs before any application code executes, which means an application with no bugs of its own is still exposed. As of October 21, 2026, no verified proof-of-concept code is available publicly. Attack attempts have been observed by Cloudflare after the leak, but no confirmed in-the-wild compromise has yet been reported.
While upgrading every PHP runtime remains the primary control, SentinelOne agent detects attackers’ post-exploitation activities. Once an attacker has code execution on the web server process, the behavior that follows web server flaws: execute shell commands, drop and invoke webshells, download and execute custom payloads and outbound connections. On managed hosts, the Singularity™ agent and Singularity AI SIEM detection content look for such behaviors, and Purple AI® can be used to hunt for it during the patching window. The separate memory-disclosure path runs no code on the host, so it leaves no process behavior to detect; that path is instead surfaced through web server, WAF, and CDN telemetry forwarded into AI SIEM.
This report details PHP2Shell's mechanism, affected versions, and confirmed activity, and outlines how SentinelOne customers can strengthen their defenses.
Key Highlights
The flaw is in PHP itself, not in any application. WordPress, Drupal, Joomla, Magento, Laravel, and other web applications are all exposed on an affected PHP version, because the vulnerable code is in the runtime beneath them.
The patch is the only complete fix. PHP states plainly that no configuration change fully closes the vulnerability. Every interim mitigation reduces one attack path and leaves others open.
The unauthenticated path runs before your code does. On Apache with mod_php, a single crafted HTTP request triggers the flaw during request startup, so application-level controls never see it. PHP assesses the risk as highest for mod_php.
Memory disclosure leaks secrets without a shell. One path reads live worker memory and returns passwords, tokens, API keys, and certificates with no code execution, which makes it quieter than a shell and harder to catch with execution-focused tooling.
End of Life PHP will not get a patch. Organizations running PHP 8.1 and prior will not receive an official release. Source-only backports exist for 7.4, 8.0, and 8.1, and distribution or LTS vendors may offer fixed packages.
Leverage SentinelOne platform post-exploitation coverage. The detection by the agent is agnostic to the vulnerability and exploit chain and focuses on attackers activity following the exploit, including but not limited to, installation and usage of webshells, command executions and outbound connection behavior that follows the code execution.
Organizations should take the following steps immediately:
Update every PHP runtime to a fixed version and restart Apache, PHP-FPM, and any long-running workers.
Inventory internet-facing PHP, including the copies bundled inside appliances, control panels, and vendor software.
Isolate end-of-life PHP (8.1 and older) from the internet until it can be upgraded.
Rotate credentials, tokens, and keys that a PHP worker could hold in memory on any exposed, unpatched system.
Monitor the official PHP changelog for relevant updates
What is PHP2SHELL
PHP2Shell is a family of memory-safety vulnerabilities in core PHP, grouped under two CVEs that share one root cause. When PHP hits a fatal condition such as exhausting its configured memory limit, it does not unwind cleanly. It abandons the current operation with a “longjmp” out of the C call stack, so no cleanup runs and nothing records that a data structure was left half-built. A later cleanup routine, or a later request, then trusts that state.
CVE-2026-109618 is the out-of-memory case. PHP marks request data as valid before allocating memory for it. If that allocation hits the memory limit and fails, the entry is left pointing to uninitialized heap memory. When the failed request runs its cleanup routine, it processes these stale bytes, leading to corruption..
CVE-2026-109619 is the stale-state case. When a fatal error occurs, PHP fails to clean up properly, leaving a global pointer pointing to memory that has already been freed. Because worker processes handle multiple requests, a subsequent request on the same worker can interact with this freed memory before initialization resets it – resulting in a use-after-free condition. Session upload progress (enabled by default) is a confirmed trigger for this behavior.
Both flaws were discovered through AI-assisted auditing under OpenAI's “Patch the Planet” program. Calif and OpenAI independently reported the root cause to the PHP security team on August 11, 2026, and Wiz reported additional attack vectors on August 24, 2026. PHP first saw signs of the underlying out-of-memory problem during a 2024 audit by OSTIF and Quarkslab, but no exploitation path was proven at the time and the fix stalled. The PHP Foundation has since described that delay as a structural failure in its security process.
On October 20, the two CVE identifiers leaked on social media. PHP released a patch on October 21, 2026.
PHP2SHELL at a Glance
Attribute
Detail
Tracking
CVE-2026-109618, CVE-2026-109619 (PHP2Shell)
Vulnerability Class
Memory safety: use-after-free and improper handling of exceptional conditions (CWE-416, CWE-755)
Severity
CVSS v4.0 9.2, Critical, for both CVEs
Affected
PHP 5.4.0 through the release before each branch's fix. Nearly every version released in a decade is affected by at least one issue
Attack Vector
Unauthenticated, network, over a single crafted HTTP request
Impact
Remote code execution as the web worker, or disclosure of sensitive process memory
Exploitation Status
As of October 21, 2026: no verified proof-of-concept code is available publicly, attack attempts observed by Cloudflare after the leak, no confirmed in-the-wild compromise reported.
Affected and Fixed PHP Versions
PHP Branch
Vulnerable
First Fixed Release
8.5
< 8.5.12
8.5.12
8.4
< 8.4.27
8.4.27
8.3
< 8.3.36
8.3.36
8.2
< 8.2.35
8.2.35 (branch reaches end of life December 31, 2026)
8.1 and older
All releases
No official fix. Source backports only for 7.4, 8.0, and 8.1
Affected and Fixed PHP Versions
PHP Branch
Vulnerable
First Fixed Release
8.5
< 8.5.12
8.5.12
8.4
< 8.4.27
8.4.27
8.3
< 8.3.36
8.3.36
8.2
< 8.2.35
8.2.35 (branch reaches end of life December 31, 2026)
8.1 and older
All releases
No official fix. Source backports only for 7.4, 8.0, and 8.1
Am I Affected?
Assume exposure for any PHP runtime below the fixed version for its branch. Check the version the web server actually loads, which can differ from the command-line version, using php --version for the CLI and the equivalent for PHP-FPM or the Apache module. Linux distributions and LTS vendors received the patch in advance, and a packaged build may carry the fix under an older version number, so confirm against your vendor's advisory rather than the version string alone.
PHP states that all installations serving web requests are at risk, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP, and LiteSpeed, and rates the risk highest for mod_php. Do not use configuration to rule out exposure. PHP validated mod_php code execution with default input and memory limits, and states that no configuration change is a complete mitigation. OpenAI has published a PHP version checker, which should be reviewed before you run it.
How The Two CVEs Differ
CVE-2026-109618
CVE-2026-109619
PHP title
RCE via OOM corruption
RCE via stale global state
Trigger
Out-of-memory during request startup, such as multipart parsing
A fatal error, including out-of-memory or an execution timeout, that leaves request state published
Requests needed
One. The invalid state is processed during the same request's shutdown
Two. One request poisons the worker, a later request on the same worker consumes the stale state
Confirmed code execution
mod_php with default PHP input and memory limits. PHP-FPM is susceptible by source analysis, with no complete exploit demonstrated
mod_php through the PHP 8.5 fatal backtrace and session upload progress paths. PHP-FPM through session upload progress, which needs a suitable application operation
Interim setting
memory_limit=-1 set administratively, plus a low post_max_size
session.upload_progress.enabled=0, and fatal_error_backtraces=0 on PHP 8.5
Limit of the setting
Partial. An underlying allocation failure can still reach the vulnerable path
Partial. Blocks the confirmed paths only
Why This Matters
A flaw in PHP itself reaches far further than a flaw in any one application. PHP is widely used across the internet, and it is embedded in content management systems, control panels such as cPanel and Plesk, and a variety of vendor applications. The hard part of this response is not applying the patch. It is finding every runtime that needs it.
The patch is also the only complete fix, and a large share of PHP cannot receive it. PHP 8.1 and older are at end of life, and Talos estimates from open-source data that around half of internet-facing PHP runs on branches with no official update. Those systems need to be upgraded to a supported branch or taken off the internet, not merely reconfigured.
Exploitation is also hard to see. The memory-disclosure path returns secrets from live worker memory without running code at all, which Wiz notes makes it harder to catch with tools focused on malicious code execution. Because the flaws execute below the application layer, Wiz also reports that application logs may contain little context, and the clearest traces are in web server and PHP error logs rather than in application telemetry.
Attack Chain
Stage 1: Reaching the Flaw Over an Unauthenticated Request
The attacker sends a crafted multipart HTTP request that places PHP's memory under pressure or forces a fatal error during request startup. A chunked or lengthless request slips past the post_max_size check, and empty file controls with deeply nested field names expand a small request body into large internal allocations.
Stage 2: Corrupting Worker State
The forced out-of-memory condition or fatal error interrupts PHP in a context that does not account for the early exit. For CVE-2026-109618, Apache with mod_php runs its request shutdown unconditionally and processes the partially initialized state as if it were valid. For CVE-2026-109619, a global pointer is left referring to freed request memory, and a later request on the same worker consumes it.
Stage 3: Code Execution or Memory Disclosure
With the heap arranged to reclaim the freed or invalid memory with attacker-controlled bytes, the corrupted state becomes a memory-corruption primitive that yields code execution as the web worker. PHP confirmed complete remote code execution against mod_php with default input and memory limits. On a separate path, the attacker instead reads live worker memory and extracts passwords, tokens, API keys, and certificates belonging to other requests, returned through the PHPSESSID response cookie, with no code execution at all.
Stage 4: Post-Exploitation
Code runs with the privileges of the web server worker, commonly www-data. From there, operators drop a web shell into the web root, spawn shells and tooling such as sh, bash, python, curl, and wget, and move laterally using any credentials recovered through memory disclosure.
Hardening Recommendations
These steps apply to any PHP estate, independent of security vendor. Patching is the only complete remediation. Everything else reduces exposure during the window before every runtime is updated.
Patch Every PHP Runtime and Restart Workers
Update to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35, or to the fixed package from your Linux distribution or hosting provider.
Restart Apache, PHP-FPM, and every long-running PHP worker after updating. The running process keeps the vulnerable code until it is restarted.
Remember that updating an application, CMS, or framework does not update the PHP runtime beneath it.
Assess Your Exposure
Inventory every PHP runtime: web servers first, then vendor appliances, Windows software that bundles php.exe or php-cgi.exe, control panels such as cPanel and Plesk, and any WordPress, Drupal, Joomla, or Magento install.
Isolate end-of-life PHP (8.1 and older) behind a VPN or take it off the internet until it is upgraded to a supported branch.
Apply Interim Settings Only as a Bridge
For CVE-2026-109618, set memory_limit=-1 administratively so applications cannot override it, and keep post_max_size low. Do not substitute RLIMIT_AS or RLIMIT_DATA, which can trigger the vulnerable path.
For CVE-2026-109619, set session.upload_progress.enabled=0, and on PHP 8.5 set fatal_error_backtraces=0, applied before request parsing and followed by a worker restart.
Treat all of these as partial. PHP confirms there is no complete configuration mitigation, and hiding diagnostics with error_reporting, display_errors, or the @ operator does not help.
Constrain the Request at the Edge
At the proxy or web application firewall, enforce limits on decoded request size, input field count, multipart part count, header count per part, and nesting depth, including requests that arrive without a usable Content-Length.
Enable your WAF or reverse proxy vendor's managed rules for PHP2Shell, which several vendors published on October 21, and test first because rules can block legitimate traffic.
Treat the WAF as a layer, not a fix: Cloudflare saw attackers mutating payloads to bypass its rules.
If an application does not use multipart form data, block multipart requests to it before they reach PHP.
Limit Worker Reuse and Blast Radius
Lower PHP-FPM pm.max_requests so workers recycle more often, reducing how long the corrupted state can persist.
Use a cgroup memory.max as an availability boundary that kills only the affected worker, not the whole pool.
Apply SELinux or AppArmor policies to restrict what a web worker can execute.
Rotate Secrets Reachable in Process Memory
Assume any credential, session token, API key, or certificate held by a PHP worker on an exposed, unpatched system may have been disclosed.
Rotate them now rather than after confirmed compromise, because memory disclosure leaves little trace.
Hunt for Post-Exploitation
Review the web root for newly created files and web shells, and watch for new cron jobs, scheduled tasks, and accounts.
Alert on PHP worker processes (php-fpm, php-cgi, httpd, apache2, w3wp) spawning shells, interpreters, or download tools, including cmd.exe and powershell.exe on Windows.
In web server and PHP error logs, look for unusual multipart requests followed by memory-limit fatal errors or repeated HTTP 500 responses, and for unexplained PHP worker churn (Wiz).
Check response headers for unexpectedly large or malformed PHPSESSID cookies, which Wiz identifies as a sign of the memory-disclosure path.
Enable log_errors, a working error_log, and error_reporting=E_ALL in startup configuration for an isolated audit, as PHP recommends, and treat a clean log as supporting evidence rather than proof of safety.
Treat these signals as leads, not verdicts. They come from public research rather than confirmed attack traffic, and memory-limit errors and HTTP 500s also occur on healthy systems.
How SentinelOne Protects You
PHP2Shell executes inside the web server worker process, below the application. SentinelOne’s visibility begins where that worker runs on a host with the agent installed. The agent cannot see internal application activity which doesn’t interact with the OS or other processes as the memory-disclosure path. What SentinelOne can address is the behavior of the code executed by the attacker.
The Behavior After Exploitation
Code execution through a web server worker process has the worker’s privileges. From there the sequence is familiar. The attacker runs host and user discovery, pulls a second-stage payload with a built-in download utility, writes a web shell into the document root so a fragile memory bug does not have to be triggered twice, opens an outbound connection to attacker infrastructure, and reads application configuration files for database credentials.
Detection on the Host
The Singularity agent builds a storyline of every process group activity on a host, including the web server workers PHP2Shell targets. These workers have a predictable life: they answer HTTP requests. They do not normally start /bin/sh, run reconnaissance commands, download executables into /tmp, write new .php files into the web root, or open outbound connections to arbitrary hosts. Behavioral detection looks for that deviation from the worker’s normal behavior. With the policy mode set to protect, the agent can terminate the process tree and quarantine dropped artifacts.
Detection in Singularity AI SIEM
Platform detection content looks at what happens on the host after exploitation, not at the request body.
Attacker Step
Telemetry
Visible Indicators
Code execution in the worker
Process creation
Web server and script-interpreter processes spawning system shells, enumeration utilities (id, whoami, uname, hostname), or sensitive file reads
Tooling download
Process Creation, File Creation
Downloaders (curl, wget, interpreters) fetching to world-writable paths, and executables written and then run from /tmp
Webshell drop
File creation
Web server processes writing .php, .jsp, .sh, or other script files into web-served directories, correlated with the inbound HTTP connection that preceded it
Reverse shell and C2
Process Creation, IP Connect
Shell processes with socket-redirection patterns (/dev/tcp, nc, socat) and unexpected outbound connections from web workers
Novel child process
First-seen analytics
A PHP or web server process spawning a child it has never spawned in that environment
Correlation rules tie these together. An inbound HTTP connection followed by a file drop or process spawn from the same worker is the shape of a successful PHP2Shell chain.
Visibility at the Edge
The memory-disclosure path never starts a process, so host telemetry alone will not see it. It can leave traces in web server, WAF, and CDN logs: unusual multipart requests followed by memory-limit errors or bursts of HTTP 500s, malformed or oversized PHPSESSID cookies, and unexplained worker churn. Singularity AI SIEM can ingest those sources alongside endpoint data if you forward them. Existing content covers allowed web shell uploads, successful POSTs to server-side scripts that have never received them before, and web shell command execution at the network layer.
Hunt with Purple AI While You Patch
Patching is the only complete fix, and the Hardening section covers interim settings. While that work runs, analysts can ask Purple AI questions such as:
Show me web server workers that spawned a shell in the last 72 hours.
Show me new files written to web roots by php-fpm.
Show me hosts with a spike in 500 responses followed by a child process from Apache.
Show me outbound connections from www-data to destinations we have never seen.
The 500-response question depends on web server logs being ingested.
Confirm Agent Saturation on Web-Facing Servers
Confirm the agent is deployed, healthy, and in protect mode on every server that serves PHP, including internet-facing Linux hosts.
Conclusion
The exploitation picture for PHP2Shell is moving quickly. As of October 21, 2026, no verified proof-of-concept code is available publicly. Attack attempts have been observed by Cloudflare after the leak, but no confirmed in-the-wild compromise has yet been reported. SentinelOne is monitoring PHP2Shell activity and will update this report as exploitation evidence, vendor guidance, and detection content change.
SentinelOne recommends customers follow vendor guidance and prioritize patching as the primary defensive tactic. Interim settings, WAF rules, and detection reduce risk while it is deployed. Update every PHP runtime to 8.5.12, 8.4.27, 8.3.36, or 8.2.35, restart the workers, and confirm the fix is running on the version the web server actually loads. Move PHP 8.1 and older to a supported branch or off the internet, and rotate any secrets that a worker on an unpatched, exposed system could have held in memory.
SentinelOne Black October Webinar
Disclaimer
Information contained herein is current as of October 21, 2026, and is subject to change as patch releases and threat activity evolve. Recipients should not rely solely on this report for security decisions and should consult with their security teams and SentinelOne account representatives for current guidance.
Expect to see quite a few websites serving error pages today: Nearly 70 percent of websites need to update their core software to fix a pair of vulnerabilities that allow an attacker to seize full control over affected servers. Experts say there are working exploits for the flaws, and that these critical bugs are already being exploited in the wild.
Image: Shutterstock.com, Sashkin.
The flaws at issue are present in PHP, the programming language that powers sites running on a large number of web publishing systems, including Drupal, Magento, Joomla and WordPress. Earlier today, PHP released an emergency security update to fix two critical bugs that can allow an attacker to execute code of their choosing on a vulnerable server.
Reutersreports that government websites in Europe and elsewhere went offline today after the PHP vulnerabilities were disclosed. Cloudflare said it has already detected some exploitation of the flaw, and that at 3:02 am (UTC) it implemented web application firewall rules to protect websites from attack traffic seeking to exploit the bugs, which could cause a denial of service condition, remote code execution, and data exposure.
OpenAI, which was involved in the vulnerability research and outreach, said “given the severity of these flaws and PHP’s widespread use, we consider this one of the most impactful security issues in recent memory.”
Censys, a company that tracks the technology used by Internet hosts, said a recent scan identified approximately 2.58 million Internet facing hosts and 54.9 million web properties running PHP.
Security experts at Wiz said every PHP version released in the last decade is affected by at least one of these vulnerabilities [full disclosure: Wiz is an advertiser on this blog].
“These findings rank among the most severe vulnerabilities discovered in PHP, and arguably in software history,” reads a blog post published today by a team of researchers at Wiz, which was one of several organizations credited with discovering the vulnerabilities. “The underlying flaws had been present for decades, but demonstrating their exploitability required an exceptionally complex chain of steps, at the edge of what human researchers could practically achieve. Frontier AI models substantially reduced that barrier, turning a longstanding flaw into an exploit.”
The Wiz researchers say it is likely the PHP vulnerabilities will be mass-exploited to install web-based backdoors or “web shells,” which give attackers a web-based panel that allows them to remotely control infected sites. Wiz said that prior to the PHP bugs being publicly disclosed, the company worked with the PHP team, Calif and OpenAI to measure the size of the problem and coordinate patch verification and disclosure.
The PHP zero-day vulnerabilities are being tracked by their CVE numbers, CVE-2026-109618 and CVE-2026-109619, and they affect all web servers running PHP 5.4 or later. The bugs are fixed in PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35.
According to Wiz, PHP is so deeply embedded in many web applications that we are likely to see organizations struggling to patch these vulnerabilities for some time to come, comparing this PHP vulnerability pair with the Log4Shell weakness that emerged in 2021 — a widespread, severe-as-it-gets security flaw in Log4j, a popular Java logging framework.
“A vulnerability in core PHP reaches far beyond a single application,” the Wiz researchers wrote. “PHP runs across clouds, hosting providers, content-delivery networks and millions of independently managed servers. Reducing exposure before the technical details became public required coordinated work across that entire ecosystem.”
The SANS Internet Storm Center is keeping an eye on major software platforms that are shipping updates to deal with these PHP flaws. For example, Ubuntu just released updated PHP packages. For a technical deep-dive on these vulnerabilities that tells the timeline of the discovery of these bugs in a comic book style, check out this post from Calif, another technology company credited with finding the PHP flaws.
A snapshot of php2shell.censys.com, the website Censys set up to track the PHP vulnerabilities.
This is a fast-moving story. Updates will be noted here with timestamps.
Update, 2:30 pm ET: Add figures from Censys and a link to Calif’s writeup.
PHP will release emergency fixes for two critical RCE flaws rated 9.2, as researchers warn of potential risks to exposed and unsupported systems.
PHP is preparing an emergency security release for two critical vulnerabilities that could let attackers execute code remotely on affected servers. The update is scheduled for today, October 21 at 14:00 UTC, after details of the flaws leaked online ahead of their planned disclosure.
I have successfully recreated & lab/field tested CVE-2026-109618 / CVE-2026-109619
The PHP security team confirmed both vulnerabilities carry a CVSS v4.0 score of 9.2. It hasn’t yet published their technical details, confirmed the affected versions, or identified the releases that will fix them. The official PHP announcement says the full information will accompany the security updates.
“The PHP security team would like to give advance notice of an upcoming security release. It is scheduled for Wednesday, 21 October 2026 at 14:00 UTC. It addresses two critical vulnerabilities, both rated CVSS v4.0 9.2.” states the announcement.
“All PHP users are encouraged to prepare now so they can upgrade as soon as the release is available. We reserve the right to release earlier should details of either vulnerability become public, or should evidence of active exploitation appear in the wild. Full details, affected versions, and the fixed versions will be published with the release.”
Researchers dubbed the vulnerabilities as php2shell, using the identifiers CVE-2026-109618 and CVE-2026-109619. The identifiers and the claim that the flaws allow remote code execution come from reports outside PHP’s initial advisory, rather than from a published technical analysis by the project.
According to the Hacker News, the two critical PHP vulnerabilities would be disclosed on October 22. The post described them as remote code execution flaws with CVSS scores of 10.0 and said they affected versions dating back to PHP 5.
Researchers at watchTowr subsequently confirmed that the vulnerabilities were real and said the information had leaked before the agreed disclosure date. The company also reported that it had reproduced one of the flaws, CVE-2026-109618, but withheld technical details while patches remained unavailable.
PHP published its advance security notice later that day, setting the release for Wednesday, October 21, one day before the date reported in the leak. The team also reserved the right to release the fixes earlier if technical details became public or it found evidence of active exploitation.
The difference between the reported severity scores matters. The leaked information cited CVSS 10.0, while PHP officially rated both vulnerabilities 9.2 under CVSS version 4.0. Until the vendor publishes its technical advisory, the official score is the one administrators should use when describing PHP’s assessment.
The main concern is the possibility that the flaws affect a wide range of PHP installations. Reports have suggested that versions from PHP 5 onward could be vulnerable, but watchTowr’s FAQ explicitly notes that the scope hasn’t been confirmed by an official vendor advisory.
“The report claims the vulnerability affects every PHP version from PHP 5 onward, though this scope has not been confirmed by an official vendor advisory. No specific configuration or feature requirement has been described in the available report.” states watchTowr.
“Until PHP publishes an official advisory, security teams cannot determine which specific deployments face the greatest exposure; every organization running PHP in production should prepare to act quickly once a fix is confirmed.”
Administrators also don’t yet know which PHP components are involved or whether exploitation depends on a particular configuration or deployment mode. Those details will determine how attackers could reach the vulnerable code and which systems need the most urgent attention.
PHP’s supported versions policy adds another complication. The project currently supports four release branches, PHP 8.2 through 8.5, while older branches no longer receive security updates from the PHP project.
The anticipated fixes are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, according to tracking by Mallory. These version numbers were predictions ahead of the release, not confirmed package versions in PHP’s advance notice.
If the vulnerabilities affect older releases, organizations running PHP 8.1, 8.0, 7.x or 5.x may not receive an upstream fix. They may need to upgrade to a supported branch, apply any security updates provided by their operating system vendor, or restrict access to affected systems until they can remediate them.
Research by Mallory highlights the scale of the potential problem. Using Shodan data collected on October 20, the company identified about 884,000 internet-facing hosts reporting PHP 8.1 or an older version, representing roughly 59% of the 1.5 million hosts that disclosed a PHP version in their HTTP banners.
These figures don’t establish that every host is vulnerable. The count identifies systems running older PHP versions that may not receive a direct fix from the PHP project if the reported scope is confirmed. Another 740,000 hosts reported PHP without revealing a version, making it harder to assess the full exposure.
The numbers also count hosts, not individual websites or organizations. Shared hosting can place many websites on the same server, while software vendors and hosting providers may bundle PHP into products that administrators don’t recognize as PHP installations.
That makes asset discovery an important first step. Security teams should check web servers, Windows systems, vendor appliances, hosting control panels such as cPanel and Plesk, and applications that include their own PHP runtime.
PHP hasn’t published a workaround in its advance notice. Until the fixes become available, organizations should identify their PHP installations and prepare to install the correct update as soon as the vendor publishes it.
Internet-facing systems should take priority, particularly servers running business-critical applications or processing sensitive information. Administrators should also check with their Linux distribution and hosting provider, since vendors sometimes backport security fixes without changing the upstream version number in the way expected.
For installations running end-of-life PHP, the options are less comfortable. Organizations should plan an upgrade or reduce exposure by taking vulnerable services offline, restricting access through a VPN or IP allowlist, or placing them behind a web application firewall while a longer-term fix is prepared.
CERT-EU’s security advisory recommends considering the isolation of internet-facing applications from public networks when immediate patching isn’t possible.
“CERT-EU strongly recommends identifying PHP-based applications and preparing to patch as soon as fixed versions become available.”states CERT-EU. “Where immediate remediation is not feasible, organisations should consider isolating internet-facing applications from public networks until a fix can be applied.”
This is a precautionary measure, not a confirmed workaround for either PHP vulnerability.
Monitoring process activity can also help identify suspicious behavior. On Linux, security teams should investigate PHP-related processes such as php-fpm, php-cgi, httpd or apache2 launching unexpected shells, interpreters or download utilities, including sh, bash, python, curl and wget.
Florian Roth’s open-source process-watcher can log programs launched by PHP processes and record their command lines. It provides visibility into process activity, but it doesn’t block an exploit or prevent a malicious command from running.
If an investigation uncovers suspicious activity, teams should isolate the affected server, preserve PHP and web server logs, and check for newly created files in web roots, web shells, unexpected scheduled tasks, cron jobs and user accounts. Those steps can help determine whether an attacker has already gained access, rather than simply whether a server was exposed.
As of October 21, Huntress said it hadn’t observed exploitation in attacks against its partner environments and hadn’t developed or reproduced a proof of concept. watchTowr’s FAQ also listed no reported exploitation and no vendor patch at the time of its update.
That doesn’t mean administrators can safely wait to assess their exposure. Once technical details and fixes become public, attackers may be able to develop working exploits more quickly, particularly if the vulnerabilities affect widely deployed versions of PHP.
A previous PHP flaw illustrates how quickly the situation can change. When CVE-2024-4577, which affected PHP running in CGI mode on Windows, became public in June 2024, Akamai reported exploit attempts against its honeypot servers within 24 hours.
The scheduled release should answer the questions administrators still face: which versions are affected, which components contain the flaws, whether exploitation requires a particular configuration, and which updates fix each issue. Until then, the priority is straightforward: know where PHP runs, prepare the updates, and avoid leaving internet-facing systems on unsupported versions without additional protection.

 Entrar

 (@eastdakota)