❌

Visualização de leitura

Millions of California students’ sensitive data stolen in breach

Personal information belonging to millions of current and former California public school students has been stolen from a system operated by Educational Testing Service (ETS).

ETS is a nonprofit organization that helps run the state’s standardized tests under contract with the California Department of Education (CDE). It has begun notifying students and families after an unauthorized party accessed and copied student information from an ETS-operated secure file transfer protocol (SFTP) site. CDE is distributing the ETS breach notice to help affected individuals receive information about the incident and available resources.

An investigation determined that an unauthorized party used compromised login details to ​access the site and copy files containing California student information at various ​times between May 22 and September 18.

The CDE says the breach includes all students enrolled during the previous three school years, although the affected population is not limited to that group. The information involved varies by individual but may include:

  • Student names
  • Statewide Student Identifiers (SSIDs)
  • Dates of birth
  • Home addresses
  • Demographic information
  • Disability and program participation information
  • Statewide assessment information, including test scores

According to the CDE, over 5.7 million students were enrolled in California ​public schools during the 2025–2026 school year alone.

Not every affected student had every category of information exposed. However, this is clearly more than a list of names and email addresses: The stolen files can reveal highly personal information about a student’s education and disabilities.

CDE says Social Security numbers, financial account information, passwords, and parent or guardian information were not involved. ETS says it has found no evidence so far that the stolen information has been made public.

How to stay safe

ETS, at CDE’s direction, is notifying affected students and families. If your information or your child’s information was involved, follow the instructions in the notification and:

  • Verify any communication about the incident through official channels.
  • Consider enrolling in the two years of free identity-protection services. Parents or legal guardians can enroll affected minors, while affected adults can enroll themselves. Check the instructions for the appropriate age group.
  • Watch for messages that use details about your child or their school to sound convincing. Don’t share passwords, security codes, or payment details in response to an unsolicited message or call. 
  • For more advice, read our blog “Involved in a data breach? Here’s what you need to know.”

Pro tip: Students, faculty, and staff at participating US universities can get free security software through the Malwarebytes Student Protection Program. Visit malwarebytes.com/student to check your eligibility and sign up. 


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 
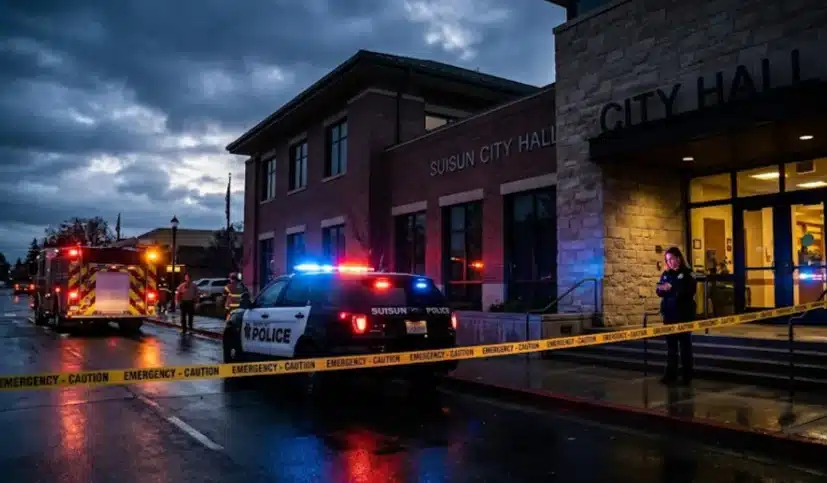
Suisun City Declares Emergency After Cyberattack Disrupts Systems

Suisun City Emergency

The Suisun City emergency declared by local officials followed a cyberattack that forced the Northern California municipality to shut down its information technology network, disrupting some communications used by public safety agencies. The incident has placed the California city of roughly 30,000 residents among communities confronting the growing threat of cyberattacks against essential local services.  The Suisun City Council declared a state of emergency Saturday after the attack compromised the city's computer systems. Officials said the network shutdown was necessary to contain the threat and preserve potential evidence for a federal investigation into the incident.  Although the Suisun City cyberattack affected communications operations involving both the fire and police departments, city officials said there was no imminent danger to the public. They also emphasized that public safety services continued to operate despite the disruption.  One of the most significant effects involved the handling of emergency communications, including the routing of 911 calls. Suisun City dispatchers began receiving emergency police and fire calls through the Solano County dispatch center as officials worked around the damaged municipal network. 

Suisun City Emergency Response Shifts Dispatch Operations 

The Suisun City emergency response required officials to temporarily move some communications functions outside the city's own computer infrastructure. By Sunday morning, online city services and internal municipal operations remained unavailable while cybersecurity specialists investigated the attack.  Those experts were also working to restore the affected systems. The decision to take the network offline was intended not only to stop the cyberattack from spreading but also to protect evidence that could assist federal investigators in determining how the intrusion occurred and who was responsible.  City officials described the attack as apparently the first incident of its kind to affect Suisun City. The municipality is located about 55 miles north of San Francisco and has a population of approximately 30,000. 

California City Attack Highlights Broader Cyber Threats 

The California city incident also comes amid federal investigations into a separate wave of cyberattacks involving municipal water systems in a dozen states.  Late last month, the FBI, the Environmental Protection Agency and the Cybersecurity and Infrastructure Security Agency warned that cyberattackers had remotely accessed online infrastructure used by water and wastewater systems in at least seven states. Federal agencies said the hackers believed to be affiliated with Iran were targeting internet-connected industrial controllers with the goal of “to cause disruptive effects within the United States.”  The risks became apparent in Minnesota, where 30 water systems were affected by a cyberattack. Officials reported dramatic declines in water levels before backup systems were activated to prevent further disruption.  While the water-system attacks are separate from the Suisun City cyberattack, the incidents illustrate the expanding range of public infrastructure that can be exposed when essential services depend on connected computer networks.

Suisun City Cyberattack Comes Amid Funding Concerns 

The recent attacks have also prompted calls for greater federal support for cybersecurity efforts. Last week, a bipartisan group of lawmakers urged the restoration of federal funding for Department of Homeland Security programs intended to coordinate cybersecurity efforts across multiple states.  The lawmakers' concerns reflect the increasingly interconnected nature of cyber threats. An attack may occur within one municipality or state, but the technology and infrastructure involved can be linked to broader systems and networks that cross jurisdictional boundaries.  Gov. Gavin Newsom's office, in a statement to The Times, said there was no evidence that California water systems were among those targeted in the recent series of attacks. The governor's office nevertheless argued that cybersecurity efforts conducted independently by individual states are less effective than a coordinated federal approach.  “Cyber threats do not stop at state lines, and no state can defend against them alone,” the governor's office said.  The statement also pointed to reductions in the federal cybersecurity workforce and cuts affecting critical programs. According to the governor's office, those changes have weakened partnerships, threat intelligence capabilities and technical assistance intended to protect essential services nationwide.  “Federal cuts to the nation’s cybersecurity workforce and critical programs have weakened the partnerships, threat intelligence and technical support that help protect essential services across the country,” the governor's office said. “Reducing these capabilities while cyber threats continue to grow leaves every state, and the nation, less prepared for the next attack.” 

Californians can tell data brokers to DROP their information

California has launched the Delete Request and Opt‑out Platform (DROP), a state‑run portal that lets residents send deletion and opt‑out requests to all registered data brokers in one place.

DROP was created under California’s Delete Act, which forces data brokers to register with the California Privacy Protection Agency (CPPA) or face fines. Currently over 600 data brokers are in the registry.

Data brokers collect and sell extensive personal information, including financial details, online behaviors, and location data. This data is often gathered without explicit consent, raising concerns about privacy and transparency.

DROP is a state service that sends a standardized deletion/opt‑out request to all data brokers registered with the California Privacy Protection Agency. Starting August 1, 2026, registered data brokers in California are required to access DROP and have 90 days to delete a person’s records after a request.

How to use DROP

You’ll need to provide at least one reachable email address and/or mobile phone to verify your identity and track the request. Be ready to provide basic personal data (name, address, contact details) that brokers are likely to have and that DROP uses to match your records.

  • Go to the DROP portal.
  • Use the “Get Started” button on the homepage.
  • Accept the terms and conditions presented by the platform by using the “I accept” button.
  • You’ll need to verify that you are a California resident: you can either input your personal information manually, or authenticate via Login.gov, which allows identity verification through a federal login. If you receive the message “Unable to verify” your status as a California resident, click the link on screen to “Request a review of your eligibility.”
  • After residency verification, create a deletion request:
    • Provide your email address and/or phone number to verify contact details.
    • Fill in basic information (name, address, etc.) so brokers can locate your records.
  • Submit your request through DROP and you’ll receive a DROP ID that lets you track the status of your request online. Store that number somewhere.

Now, it’s up to the data brokers. They now have 90 days to delete your records and comply with opt‑out obligations. If you run into a problem there is a dedicated help site.

For non-Californians

Some other states—like Oregon, Texas, and Vermont—also require data broker registration, though only California currently offers a centralized platform like DROP. If you live in such a state, check your attorney general’s website or privacy office for a “data broker registry” or opt‑out guidance, and follow their listed processes to submit requests directly to each broker.

Even without DROP, US residents can still reduce data broker collection and sale of their data, but it requires more manual work. Where no centralized government tool exists, you can identify brokers by searching for “data broker opt‑out” and review lists from privacy advocacy groups.

For each broker you’ll have to submit individual requests:

  • Use their web forms, email addresses, or postal addresses to request:
    • Deletion of your data, and
    • Opt‑out from sale or sharing of your data.

You’ll need to provide enough information to match your record (e.g., name, address, email, phone) but avoid oversharing additional sensitive data.

It’s advisable to maintain a spreadsheet with dates, brokers, and confirmations. Most privacy laws specify response deadlines, often 30–45 days, though this varies by state.

Sounds like a lot of work? Malwarebytes Personal Data Remover can help.

How to reduce future data broker collection

This is probably the only field where “security by obscurity” works.

Use multiple email addresses where you reserve one for financial/critical accounts and use aliases or disposable emails for newsletters, shopping, and registrations, making it harder for brokers to build a unified profile.

A VPN encrypts your traffic and hides your IP address, reducing the ability of websites and analytics firms to link activity to a stable, location‑based identifier.

For non‑critical services, avoid providing full legal names, exact home addresses, or phone numbers if they’re not strictly necessary. This is especially true for rewards and loyalty programs.


Your name, address, and phone number may already be for sale.  

Data brokers collect and sell your personal details to anyone willing to pay. Malwarebytes Personal Data Remover finds them and gets your information removed, then keeps watch so it stays that way. 

❌