 Entrar

Fake Apps, Real Spies: How Iran Tracks Dissidents Through Telegram


The UK, the US, and the Netherlands published a joint advisory warning about a Windows malware family, dubbed Chosen Brick, that Iran’s intelligence services use to track down dissidents, journalists, and activists, and the stakes for the people on the receiving end go well beyond a locked file server.
“CHOSEN BRICK is a malware family that has been used to target individuals around the world including in the UK, US and the Netherlands from at least 2025. CHOSEN BRICK enables Iranian state cyber actors to collect information on a target’s contacts, emails and social media messages, which could enable tracking of their movements.” reads the advisory. “Iran almost certainly uses cyber activity to support the repression of individuals who are seen as a threat to the regime, such as dissidents, activists and journalists.”
The advisory was issued jointly by the UK’s National Cyber Security Centre, the FBI, and the Netherlands’ AIVD. The three agencies gave a name to malware activity that security researchers had already been tracking under different names.
This is not the first time Iranian state-linked actors have used Telegram-based malware against the Iranian diaspora. In March, the FBI reported that Iranian actors had been using Telegram as command infrastructure to target dissidents, with activity dating back to late 2023. The latest advisory adds a formal name, a joint attribution, and a more detailed look at how the malware operates.
Iran has repeatedly used cyber operations to target people it considers a threat to the regime, including dissidents, activists and journalists. Iranian intelligence services have also been linked to plots involving the kidnapping or killing of perceived opponents abroad. For victims of CHOSEN BRICK, the risk may extend beyond cyber intrusion.
Personal information belonging to some victims has reportedly appeared on pro-Iranian leak sites, potentially exposing them to further harassment, intimidation or physical threats. The publication of such data could increase the risks faced by individuals already targeted by Iranian actors.
” In some cases, the Iranian intelligence services have plotted to kidnap or conduct lethal operations against individuals internationally, who they perceive as enemies of the regime.” continues the advisory.
Stolen personal data from CHOSEN BRICK victims has also shown up on pro-Iranian leak sites, turned into a harassment tool rather than just an intelligence asset.
That combination changes the calculus for defenders. A compromised laptop is normally a data problem. Here, it can become a physical safety problem for the person who owns it.
The attack starts on a messaging app, not an email inbox. Operators build rapport with a target over WhatsApp or Telegram first, sometimes for a while, before ever sending a file.
Iranian cyber actors first contacted targets through social messaging apps, spending time building trust before attempting to deliver malware. Their social engineering was tailored to each victim and relied on detailed information gathered during prior research.
In some cases, the attackers pretended to be someone the target already knew, making the approach appear legitimate. In others, they posed as technical support staff from the messaging platform. This combination of reconnaissance, impersonation and trusted communication channels helped make the malicious messages more convincing and increased the chances of successful infection.
“Iranian cyber actors engaged with targets via social messaging applications to build rapport prior to attempting to deliver the malware. The nature of the social engineering varies between targets and uses extensive target knowledge from research conducted in preparation (T1589).” the agencies state. “The actor often purports to be an individual previously known to the target or technical support from the social messaging platform (T1566.003).”
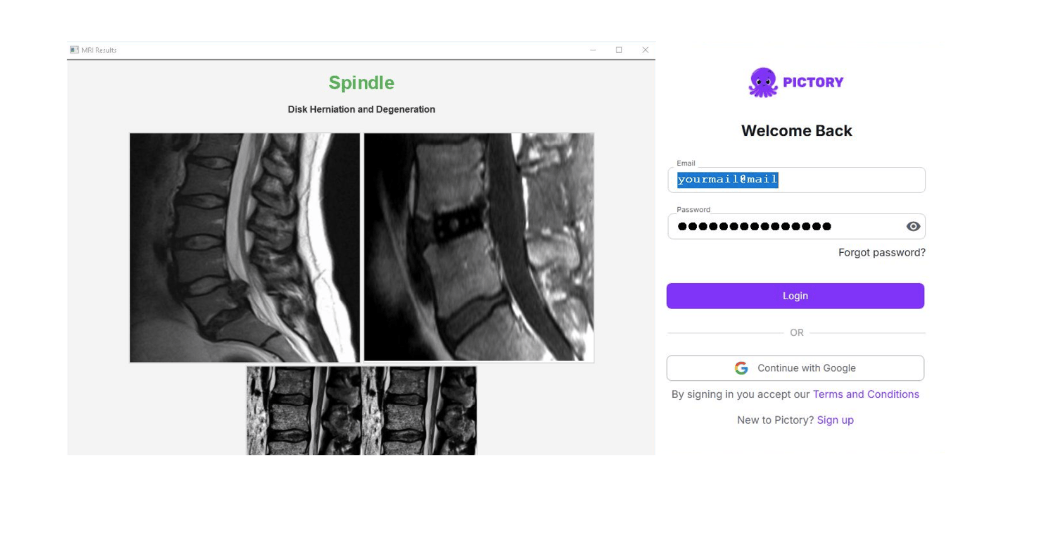
The lure files themselves are dressed up as things a target would plausibly want to open: fake installers for Pictory, RunwayML, Norton Antivirus, Telegram itself, Adobe Flash Player, or KeePass. Other versions arrive disguised as MRI scan results, which is a particularly grim way to earn someone’s click. Whatever the disguise, the file shows a convincing decoy screen while the real payload installs quietly in the background.
The attackers also have a backup plan. They usually target a victim’s work device first, but if the initial attempt fails or they think they may be detected, they try to move the attack to a personal device. They may ask the victim to open the file on their own phone or computer, bypassing the security controls protecting the work device.
A company can tightly secure an employee’s work laptop, but it has much less control over the personal devices they use every day.
Whatever the file is supposed to contain, it shows the victim a realistic-looking screen related to the topic, helping the attackers maintain the deception. In the background, the file downloads and runs the main malware component, which the NCSC tracks as CHOSEN BRICK. This gives the attackers control over the compromised device. So far, all observed attacks have targeted Windows systems.
Corporate IT can lock down a work laptop all it wants. It has no say over the phone in someone’s pocket.
CHOSEN BRICK has only ever been seen hitting Windows machines. It sets up persistence through a registry Run key so it survives a reboot, and it tries to add its own exclusions to Microsoft Defender to keep from getting flagged.
The malware uses Telegram for command and control, with each infected device linked to its own Telegram bot ID. This keeps victims separated and makes investigations more difficult. Newer versions also use HTTPS or SOCKS5 proxies, adding another layer between the malware and network monitoring.
The malware sends stolen data through Telegram bots and cloud storage services such as VultrObjects and StorjShare. It can also download and install additional malware when attackers want more access.
“Files and collected data are exfiltrated through a combination of the Telegram bot (T1041) and through the use of cloud object stores such as VultrObjects and StorjShare (T1567.002). Recent variations in this malware family include the use of HTTPS/SOCKS5 proxies to obscure the use of Telegram bots (T1090.002).” states the report. “If the malware is instructed by the cyber actor to download additional malware it is written to disk in a configurable location.”
The new payload is saved using the same persistence method as the main malware. One sample used the path C:\Windows \SysWOW64, with an unusual space after “Windows.”
The unusual space after “Windows” creates a non-standard folder path that is not normally found on Windows systems. According to the NCSC, the attackers deliberately created this location to deploy their malware. It is a small but effective trick: the path looks legitimate at first glance, but it can bypass security rules or allowlists that only recognize standard Windows folders.
Once running, CHOSEN BRICK can collect a wide range of data, including screenshots, microphone audio, WhatsApp and Telegram chats stored in browsers, emails and system information. It can also delete files and even wipe the entire system. So far, researchers have not seen it spread laterally on its own. However, because it can download and run additional payloads, attackers could manually expand their access if a compromised device is considered valuable.
The malware also has two distinctive fingerprints. Researchers repeatedly found the mutex names “ytyjyujyu” and “noi672pp434awkc12f” in samples. These unusual strings could help security teams identify CHOSEN BRICK during threat hunting.
In March, the FBI also published a FLASH notice focused specifically on how Iranian state-backed actors lean on Telegram as C2 infrastructure, which pairs well with the NCSC’s broader writeup.
If you’re hunting for this on your own network, a few domains are worth flagging when they show up unexpectedly in DNS or proxy logs: api.telegram.org, backblazeb2.com, vultrobjects.com, storjshare.io, iproyal.com, and lightningproxies.net. None of these are malicious on their own, which is exactly why the malware picked them. It’s the context that matters, not the domain name.
On the registry side, check HKCU\Software\Microsoft\Windows\CurrentVersion\Run for anything unfamiliar. Previously observed malicious entries used value names like “SMQDService” and “winappx,” though the advisory is careful to note these names will change and shouldn’t be treated as fixed indicators.
The recommended defenses are straightforward. Users should avoid installing software from links or attachments, keep applications updated, use active antivirus protection, and take SmartScreen warnings seriously. Organizations should also use phishing-resistant MFA, application allowlisting, email security and endpoint monitoring, while checking the published indicators against their own logs.
One important point concerns personal devices. Attackers may switch to a victim’s phone when security controls block access to a work laptop. Organizations protecting high-risk users, including journalists, activists and NGO workers, should therefore also provide security guidance for personal devices. Protecting only the corporate laptop may leave the device attackers target next exposed.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Chosen Brick)
