❌

Visualização de leitura

NSO Spyware Pegasus Hit a Serbian University Rector Six Days Before Snap Elections

Citizen Lab confirmed Pegasus on a Serbian rector’s iPhone 6 days before elections, raising the known civil society spyware target count to 16.

The Citizen Lab published a research note confirming that the iPhone of Vladan Đokić, Rector of the University of Belgrade, was infected with NSO Group’s Pegasus spyware sometime in 2026. The infection used a zero-click exploit, meaning Đokić did nothing to trigger it. No tap, no opened file, nothing.

“In collaboration with the SHARE Foundation, we found with high confidence that Professor Vladan Đokić, Rector of the University of Belgrade, and prominent supporter of the Serbian student movement, was hacked with NSO Group’s Pegasus spyware in 2026.” states Citizen Lab.

Đokić became a prominent figure in Serbia’s student-led pro-democracy movement after refusing to facilitate a government crackdown on protesters. Serbian authorities raided his offices on March 31, seizing computers and servers. The Citizen Lab found the infection with high confidence and describes the investigation as ongoing.

The timing raises questions. The discovery came just six days before Serbia’s snap parliamentary elections on October 25. Until September, Đokić had been publicly named as a possible candidate to lead the Student List. Since he spoke out against the crackdown, pro-government media have repeatedly attacked him.

Citizen Lab explained what a Pegasus infection means. Once installed, the spyware can give its operator the same access to a device as its owner. This includes private and encrypted messages, and the ability to turn on the microphone and camera without the owner’s knowledge.

“With the assistance of the SHARE Foundation, the Citizen Lab analyzed forensic artifacts collected from Vladan Đokić’s Apple iPhone at his request and with his consent.” reads the report. “We found with high confidence that it was infected with NSO Group’s Pegasus spyware in 2026. The infection leveraged a zero-click exploit.”

In a statement published by the university, Đokić called the spyware “another attempt of intimidation.” He called for an independent investigation, the public release of its findings, and criminal prosecution of those responsible.

“Additionally, we note that Rade Bajić, who, as a prosecutor, investigated official corruption in a failed project in Belgrade, received an Apple Threat Notification.” continues Citizen Labs.

The Citizen Lab also flagged Rade Bajić, a senior prosecutor who worked on the “Generalštab” case, a corruption investigation into the removal of heritage protections from a Belgrade site to clear the way for a luxury development backed by a company linked to Jared Kushner, President Trump’s son-in-law. Bajić says he was removed from the investigation in November 2025 without explanation, and spoke at a student protest in February denouncing political interference in the case.

He received an Apple Threat Notification on August 13 and a reminder on August 27. The Citizen Lab treats this as a high-confidence indicator that his device was likely targeted with mercenary spyware. Forensic analysis of his device is still ongoing and no confirmation of infection has been published yet.

These two cases bring the known total to at least 16 members of Serbian civil society targeted or infected with commercial spyware in 2026. In September, the SHARE Foundation, with support from Citizen Lab and Amnesty International, reported an earlier wave of attacks. The victims included a student protester confirmed to have been infected with Pegasus, opposition party members, and local officials. Those cases occurred around the period leading up to Serbia’s March local elections. The latest confirmed case was discovered just six days before the October parliamentary elections.

Serbia’s security service dismissed the September reports as purely trivial sensationalism and said it operates within Serbian law. Citizen Lab did not identify who was behind the attack on Đokić’s phone. Pegasus is sold only to governments and state agencies, which limits the number of possible operators.

If you received an Apple Threat Notification, treat your device as compromised until a technical expert confirms otherwise. In Serbia, contact the SHARE Foundation. Everywhere else, Access Now’s Digital Security Helpline supports journalists, human rights defenders, and activists. Enable Lockdown Mode on your iPhone immediately, keep iOS updated, and get your close contacts and colleagues screened as well.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Pegasus)

AdFection: Beyond the Click: Citizen Lab Exposes Ad-Delivered Spyware Networks

Spyware vendors use online ad infrastructure to profile targets and deliver exploits without requiring users to click anything.

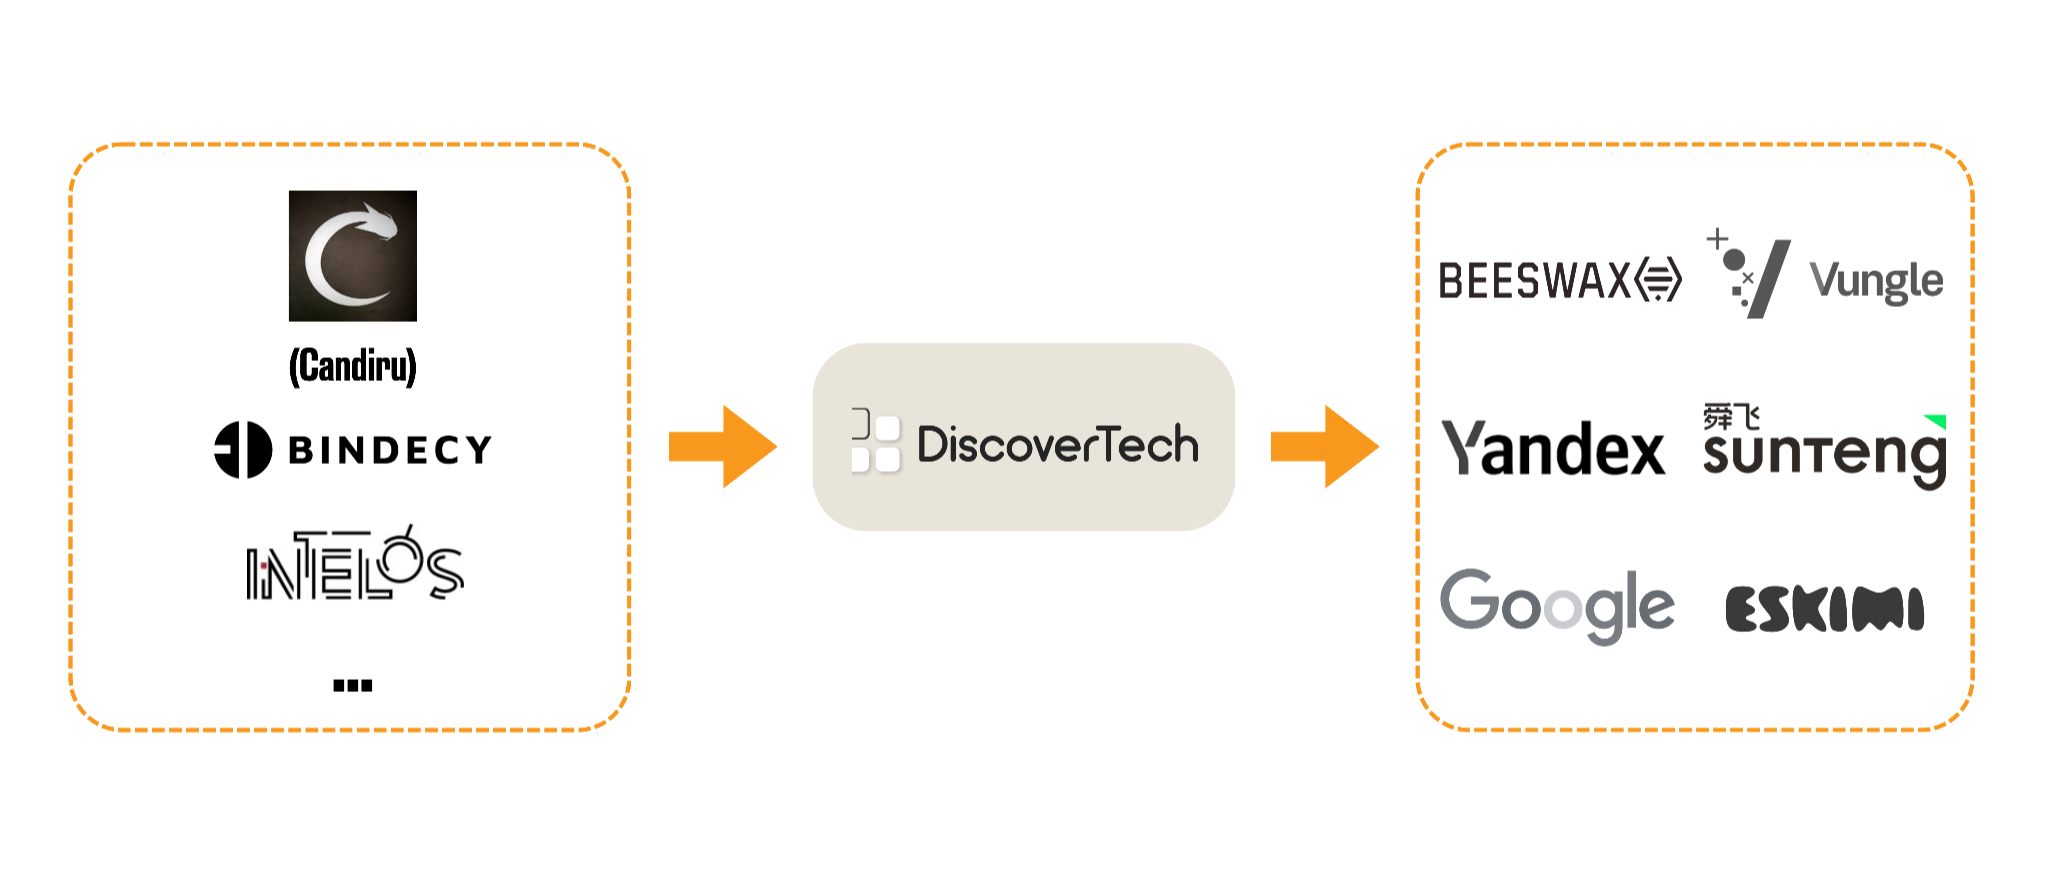
The investigation links Discover-Tech to Candiru, an Israeli spyware vendor that the US government placed on its Entity List in 2021. Candiru has since used the name Integrity Labs. Citizen Lab also identified links involving other surveillance companies, including Bindecy and Intelos, suggesting that Discover-Tech’s infrastructure served more than one customer.

The researchers examined almost four billion advertising bid records covering March to June 2026. During that period, Discover-Tech’s MyDSP platform bid on nearly 3.77 billion ad impressions and won about 442 million, with advertisements appearing across more than 120,000 websites and 70,000 mobile apps.

“We reviewed bidding data for MyDSP for four months (March through June 2026). In this period, Discover-Tech’s MyDSP bid on 3,770,286,576 impressions, and appeared to win 441,954,291 (11.7%). About 76.7% of the bids were for ad impressions in mobile apps, and 23.3% for impressions in the web browser.” reads the report published by Citizen Lab. “The database shows a total of three advertisers, with nine total combinations between advertiser and an advertiser domain name.”

Reuters, citing Citizen Lab and advertising security firm Confiant, reported that the company’s wider advertising activity reached more than 120,000 websites and 75,000 apps, potentially exposing hundreds of millions of people to its tracking infrastructure.

The distinction between exposure and infection matters. Most advertisements didn’t necessarily deliver spyware, and seeing one doesn’t prove a device was compromised. But the system gave Discover-Tech a way to profile users at scale and select particular devices for more intrusive operations.

“In 2024 and 2025, international news network Al Jazeera was targeted in a series of zero-click attacks that we link with high confidence to Candiru’s spyware delivered via Discover-Tech’s ads. At least 45 devices within Al Jazeera were targeted in these attacks.” continues the report.

Citizen Lab reached this finding by examining network logs supplied by the broadcaster. The researchers linked the activity in 2024 and 2025 to Candiru spyware delivered through Discover-Tech advertisements, providing technical evidence of a real operation rather than a theoretical attack scenario.

The advertising records also showed impressions on networks associated with sensitive organizations, including the Pentagon, NATO, the United Nations, the European Commission and the International Criminal Court. Researchers identified activity involving government, defense, media and critical-infrastructure networks across several countries.

These findings don’t mean that every organization whose network displayed an advertisement suffered a spyware infection. They do show that advertising infrastructure can reach people working in environments where their identities, communications and device activity have intelligence value.

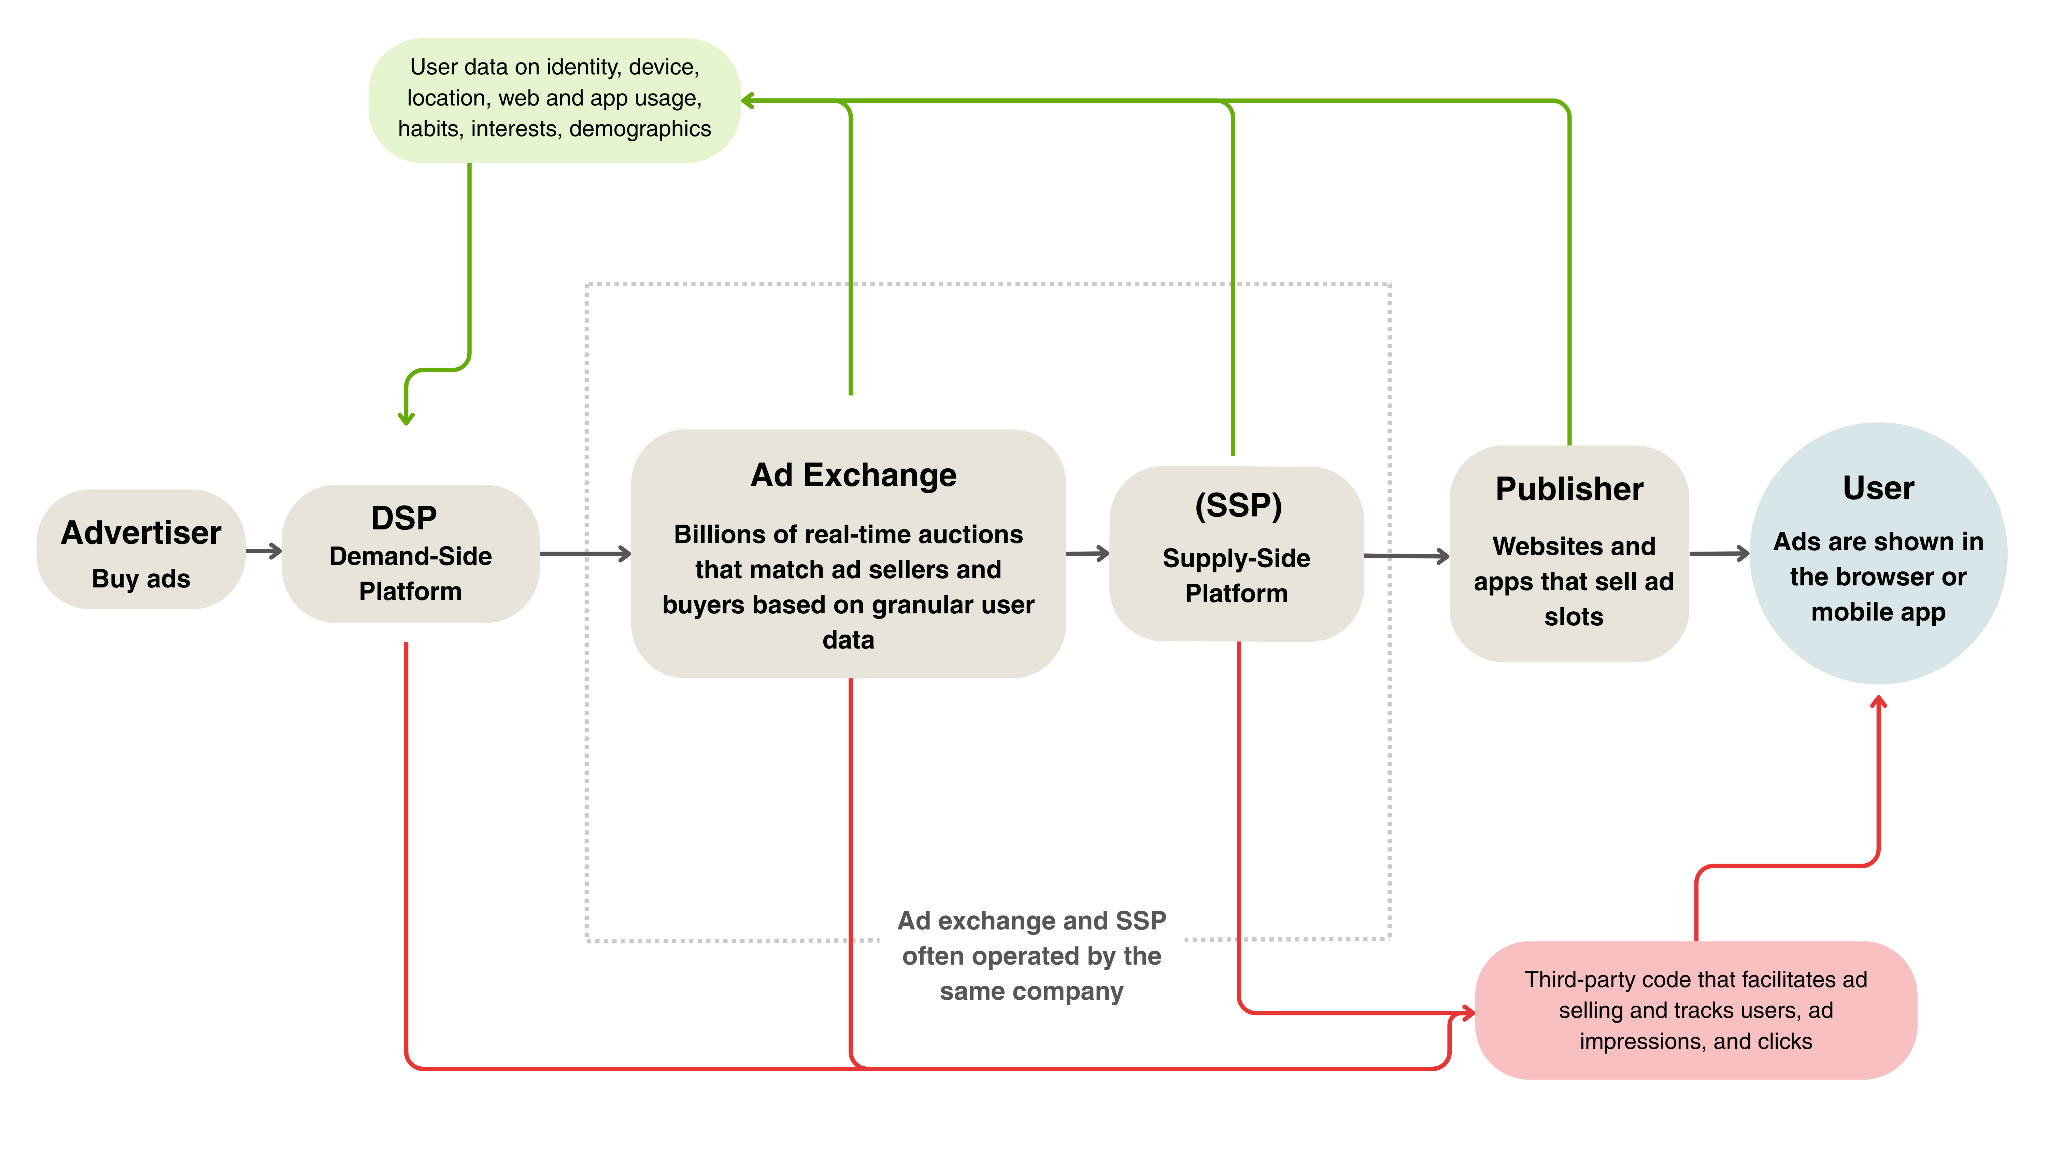
This creates a problem for security teams. Traditional defenses focus on malicious attachments, suspicious links, vulnerable software and unauthorized network connections. AdFection adds another route: code delivered through a service that users and organizations routinely allow because it supports ordinary web browsing.

Advertising identifiers, IP addresses, browser characteristics and other technical signals can help operators distinguish one device from another. When combined with targeted advertising, these signals can support reconnaissance and help an operator decide which users merit further attention. In intelligence terms, the same infrastructure can support both broad collection and selective exploitation.

Discover-Tech’s access to major advertising platforms helped its operations appear legitimate. Citizen Lab found that Google and the advertising industry association IAB Europe had listed the company among approved vendors for years, despite links to people and businesses associated with the surveillance industry.

Following the investigation, Google terminated Discover-Tech’s access to its advertising exchanges, while IAB Europe suspended its vendor status. Beeswax removed the company from its platform, and Vungle, operated by Liftoff, paused its access while reviewing the findings. Eskimi also blocked its accounts and domains.

These actions matter, but they don’t resolve the underlying problem. The advertising industry relies on complex chains of buyers, exchanges, publishers and third-party scripts, often with limited visibility into what each component does when an advertisement loads. A company can pass routine checks while using targeting rules to deliver different code to different users, making malicious behavior harder to detect through automated scanning alone.

Organizations should treat online advertising as a potential attack surface, particularly on devices used by executives, intelligence personnel, journalists and employees with access to sensitive systems. Blocking advertisements and tracking requests at the network gateway can reduce exposure, while managed devices should disable ad personalization where possible and use browsers with strong tracking protections.

Security teams should also review traffic generated when advertisements load, looking for unexpected connections to external infrastructure or suspicious scripts. Organizations facing elevated targeting risks should consider stricter controls on advertising, browser extensions and third-party content, especially on systems used to access confidential information.

The larger lesson is that a familiar user experience doesn’t guarantee a safe technical process. A banner promoting a phone or a pair of earbuds may look entirely ordinary, while the code behind it performs tracking or checks whether the device matches a target. The victim doesn’t need to click anything, and that’s precisely what makes this technique difficult to spot.

“The distribution of spyware via targeted ads represents a security risk not only for potential victims but also for states and civil society at large.” continues the report. “Two major U.S. security agencies, the National Security Agency (NSA) and the Cybersecurity and Infrastructure Security Agency (CISA), have warned already in 2018 and 2020 that adversaries may leverage malicious ads to deploy malware on devices, and thus both recommended that government agencies and other organizations use ad-blocking software.”

This is the central warning from Citizen Lab’s investigation: online advertising is no longer just a privacy concern. Under the right conditions, it can become an operational tool for espionage.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, spyware)

❌