A new open-core project called ARES is giving red teams a way to run planned, controlled attack tests against Active Directory and cloud systems. A developer who goes by Mafifrizi released the tool on GitHub.
It ships with 66 active modules, with 70 cataloged in total, covering more than 60 techniques mapped to MITRE ATT&CK. It is aimed at enterprise red teams, managed security providers (MSSPs), and security operations centers.
Mafifrizi publishes the project as an open-core platform, which means the base tool is free to read and test while a sponsorship page supports ongoing work.
The project page lists the repository under the handle “mafifrizi/ares” and describes it as an autonomous red-team engagement platform with MITRE ATT&CK module orchestration, attack-path solving, and reporting. The README does not give a real name, company, or team behind the code, so readers should treat it as an independent project for now.
The author’s pitch is simple. Traditional penetration tests cost a lot, happen rarely, and only show one moment in time, so new misconfigurations can sit unseen for months.
Vulnerability scanners add to the problem by listing thousands of possible CVEs without proving that any of them can be used. ARES tries to fill that gap by running real test steps and showing which ones lead to the most valuable systems, such as domain admin accounts.
The part of ARES that stands out most is how hard it tries to keep tests inside approved limits. Before a module runs, a check called ScopeGuard confirms the target is in scope.
A second layer, the Scope Firewall and Egress Filter, then blocks traffic at two levels. One level uses the operating system firewall, which is Windows Defender Firewall or Linux Netfilter when the tool runs with elevated rights. The other watches network calls inside Python itself. The goal is a “fail-closed” design, where the tool stops instead of sending traffic to an address nobody approved.
The tool also profiles how noisy each action is, so operators can pick quieter steps when they want to test whether the blue team notices. This matters because a careless test can knock over a production server. For the same reason, security teams are shifting toward tools that put a person in charge of each decision.
Active Directory Attack Paths
For Active Directory, ARES can load BloodHound collections or map live domain sessions. Its built-in graph engine then works out the shortest route to Domain Admin, points out chokepoints, and checks whether a sideways move is possible.
BloodHound uses the same graph idea, where a small group membership can open a path that is many steps long. Cyber Security News has explained how BloodHound Community Edition maps these paths across Active Directory and Azure.
Active Directory Attack Modules
Operators can set a goal such as domain_admin, full_compromise, or cloud_audit. The planning engine then builds a multi-step plan from graph rules. It can also use AI agents such as Claude, OpenAI, or a local Ollama model, but only after the operator gives clear permission.
The same planning engine covers cloud checks, and the cloud_audit goal is one of the built-in options. Letting a language model suggest next steps is now common in offensive tools. Cyber Security News recently reported on Decepticon, an open-source agent with 16 specialist roles. ARES keeps the AI optional, which many teams will prefer.
Defenders have a reason to watch this space. Criminals are using similar tools. Cyber Security News covered how hackers used the ARTEX AI agents to map Windows networks, steal service account passwords, and try to spread inside the network. A platform like ARES lets defenders test the same steps first, on their own terms.
Because ARES stores sensitive material, the author added several protections. Sessions live in the database, access tokens are short-lived and kept in memory, and refresh tokens are rotated. ARES stores harvested hashes and client evidence in a local vault protected with AES-256-GCM and PBKDF2-HMAC-SHA256 at 600,000 rounds.
When a test ends, ARES can produce branded reports in PDF, HTML, Markdown, and JSON. The PDF step runs through a headless browser, so it needs no extra GTK libraries on Windows or Linux. For teams that want a deeper guide to the Active Directory side, the Active Directory attack checklist on Cyber Security News is a useful companion.
Only run ARES on systems you own or have written permission to test. Start in a lab, check that the scope rules block out-of-range addresses, and review the code before using it on real networks. Fix any path the tool finds to a domain admin account, then run it again to confirm the fix.
Security Blind Spots Identified by AI The large-scale data breaches disclosed in quick succession in South Korea and Japan in October 2026 mostly originated not from internal core systems, but from peripheral entry points such as externally exposed web services, app backend APIs, and outsourced SaaS (services provided by third-party vendors via the cloud, such […]
Statistics on Malware Distributed to the Financial Sector In Attack Stage 1, phishing (attacks that trick users into revealing information) had the highest rate at 2.1, Up from 1.8 The previous month. In Attack Stage 2, “Dropper/Downloader” (a type that downloads additional malware) was the most common at 1.1, Though this was a decrease from […]
Kali Linux 2026.3 has been released as the third Kali update of 2026, bringing six new penetration testing tools, Linux kernel 7.1.5, KDE Plasma 6.7, refreshed image-building scripts, and a large set of Kali NetHunter changes. The release arrived on October 26 with 126 package updates and moves the kernel from version 6.19 to 7.1.5.
The update follows June’s Kali Linux 2026.2 release, which added nine tools, changed Kali’s APT source format, and improved virtual machine boot times. It also continues the tool and mobile testing work seen in Kali Linux 2026.1, the first major Kali update of the year.
Six New Penetration Testing Tools
The six new tools are available from Kali’s network repositories. Dalfox is an open-source cross-site scripting scanner built for automation and parameter checks.
Katana is a crawling and spidering framework that can help researchers map web applications and find paths, files, and endpoints before deeper testing.
Qsreplace takes URLs from standard input and replaces query string values with a chosen value, which makes it useful for preparing URL lists for repeatable web tests.
Rustscan is a fast port scanner written in Rust. It can scan large port ranges and pass discovered ports to Nmap for deeper service checks. SDRangel is a Qt-based software-defined radio front end that supports devices such as RTL-SDR, BladeRF, and HackRF, giving wireless researchers a visual tool for receiving, sending, and studying radio signals.
Tool
Main purpose
Key use
Dalfox
Automated XSS scanner
Finds and verifies cross-site scripting flaws by testing web parameters.
Katana
Web crawling and spidering
Maps websites, parses JavaScript, finds endpoints, and supports standard or headless crawling.
Qsreplace
Query-string replacement
Reads URLs from standard input and replaces their query values for repeatable web security tests.
Rustscan
Fast network port scanner
Finds open ports quickly and can pass the results to Nmap for deeper checks.
SDRangel
Software-defined radio interface
Provides a graphical front end for radio devices such as RTL-SDR, BladeRF, and HackRF.
Snaffler-ng
SMB data scanner
Searches readable Windows SMB shares for exposed credentials and sensitive files.
Snaffler-ng searches readable Windows SMB shares for credentials and sensitive data. It supports NTLM and Kerberos sign-in, DFS discovery, archive checks, built-in classification rules, SQLite resume support, and several output formats.
These additions cover web discovery, XSS testing, URL processing, port scanning, radio research, and file-share review. Like any security tool, they should only be used on systems that the tester owns or has clear permission to assess.
Linux Kernel 7.1.5 and Package Updates
Kali 2026.3 contains 126 package updates and moves the main Kali kernel from 6.19 to 7.1.5. Kali’s package tracker lists 7.1.5-1kali1 for the rolling branch, confirming the kernel used by the new release.
The newer kernel matters because it provides the base for hardware support, drivers, system calls, and security fixes used by the rest of the distribution. Users should still test wireless adapters, graphics drivers, virtualization tools, and any custom kernel modules before relying on the update during live security work.
One of the largest changes is the refresh of Kali’s public build scripts. These are the same scripts the project uses to create the official images offered through its download site. The refreshed scripts now have a more consistent structure, layout, command-line options, features, and output across supported platforms.
Each refreshed project includes a build-in-container.sh script. It detects whether Docker or Podman is present, creates a build container, and runs the image build inside that container. This removes the earlier need to build Kali on a Kali system and makes the process easier to repeat on other Debian-based hosts. Kali has also improved its related build documentation.
Users who want to build a standard installer can clone the kali-installer build repository, install the required packages, and run sudo ./build.sh. The default command creates a Kali rolling installer for AMD64. Builders can change the hostname, add packages such as Rustscan, select kali-dev, choose a netinst image, or target ARM64 through command-line options. Podman users can instead install Podman and run sudo ./build-in-container.sh.
The work is not finished. Kali says some build scripts did not make the 2026.3 deadline, and the remaining refresh is planned for Kali 2026.4. Later stages are expected to focus on automated builds, workflows, example setups, and deeper customization. Teams with CI jobs based on the older scripts should review their pipelines because changes made during the refresh may have broken older workflows.
KDE Plasma 6.7 and New Icons
The optional KDE desktop has been updated to Plasma 6.7. A key feature is per-screen virtual desktops, which lets users change the workspace on one monitor without changing every display.
This can be useful when keeping Burp Suite on one screen, terminals on another, and notes or documentation on a third. Plasma’s Overview also supports faster desktop switching by scrolling or using Page Up and Page Down.
KDE Plasma 6.7 adds more Wayland protocol and portal support, better performance and lower power use for integrated Intel graphics, CPU-rendered applications, and setups with many full-screen windows. Network connections can be duplicated, while System Monitor, software management, printing, background application display, microphone testing, and desktop search controls also receive changes.
KDE has added a light and dark theme switch, improved Breeze, restored the Oxygen and Air styles, and introduced an early preview of its Union theming system.
Kali has also added icons to tools that did not have them and updated older icons so applications are easier to identify in the menu and on the Kali tools website. Xfce remains Kali’s default desktop even though KDE received the main desktop version change in this release.
Major Kali NetHunter Changes
Kali NetHunter, the project’s Android and wearable security testing platform, receives some of the release’s most unusual changes. The team addressed compatibility problems between modern systemd and udev components and older mobile kernels without requiring large sets of patches.
Wardriving is now supported on the TicWatch Pro 3 series. An updated libnexmonkali library enables internal Wi-Fi monitor mode on the watch, allowing compatible tools inside the Kali chroot, including Aircrack-ng and Kismet, to work with the watch’s wireless hardware. Kali’s TicWatch guide says all Pro 3 GPS, LTE, Ultra GPS, and Ultra LTE variants are supported, though installation requires bootloader, recovery, operating system, root, and NetHunter changes.
WearHunter is a new experimental feature that lets a user control a NetHunter watch from a phone through ADB over Wi-Fi or Bluetooth. It can run commands and install applications, with more functions planned. NFC Arsenal now provides NFC access to the Kali chroot and can read, clone, and edit Mifare Classic cards without an external adapter. The release also adds KernelSU support, allowing a generated installer ZIP to be installed through the KernelSU application when used with a patched kernel.
Other NetHunter work includes a fix for TicWatch Pro 3 reboot problems and early support for devices that do not use a ramdisk. Bluetooth Arsenal’s airplane mode has returned. EvilTwin and Wardriving are easier to start, while custom commands now support Nexmon monitor mode and Wifite. Kali also fixed a crash caused by the NetHunter application’s storage request and delivered other bug fixes and speed improvements.
Nine new device kernels were added. They cover Google Pixel on LineageOS 22.2 with Android 15, Huawei P9 on EMUI 8 or LineageOS 16, LG K20 Plus on LineageOS 14.1, Moto G Stylus 5G 2022 on LineageOS 23.2, Nubia Z17 on LineageOS 22.2, POCO X5 5G and Redmi Note 12 5G on crDroid 12, Redmi Note 5 Pro on LineageOS 18.1, Sony Xperia 10 V on LineageOS 23.2, and Ulefone Armor 34+ on Android 16.
The release announcement also highlighted the Wardriver Project, a 2021 Honda Civic Type R shown at the Cars and Cops event in Altus, Oklahoma. The project was used to show how vehicle culture, wireless research, and cybersecurity can meet in a single build.
Website and Documentation Updates
Kali has applied the category layout and icons introduced in its desktop menu to kali.org/tools. Users who prefer the older short view can still open the Top 100 tools page.
The documentation set gains three new pages. They explain how to extract and squash vendor firmware for mainline Linux, import a pre-made Kali QEMU virtual machine, and use NetHunter EvilTwin.
Nine existing guides were updated, covering Live USB persistence, graphics problems on bare-metal systems, NetHunter on the TicWatch Pro 3, Kali as a UTM guest, the Xfce FAQ, Kali NetHunter, Raspberry Pi full-disk encryption, setting up a Kali mirror, and SSH configuration.
The release cycle also added four European mirrors. Two are in the Netherlands at mirror.hacker.nl and mirror.netone.nl. Portugal gained mirror.randhost.com, while Switzerland gained kalimirror.velden.media. Kali’s mirror system can direct users to a nearby current server, but its documentation warns against adding extra repositories to the Kali source configuration because mixing repositories can break an installation.
Kali also thanked community members who worked on documentation, tool pages, NetHunter, and package maintenance. The long contributor list reflects how much of the mobile kernel, device, documentation, and packaging work comes from outside contributors rather than only the core Kali team.
Downloading and Upgrading Kali 2026.3
New users can obtain tested installer, live, virtual machine, ARM, cloud, container, and NetHunter images from the official Kali download page. Kali recommends the latest point-release image for most users. Weekly images contain newer packages and can reduce the number of updates needed after installation, but they are automated and do not receive the same quality checks as standard point-release images.
Existing rolling users should first confirm that /etc/apt/sources.list.d/kali.sources points to the official kali-rolling repository with the main, contrib, non-free, and non-free-firmware components. They can then run sudo apt update followed by sudo apt full-upgrade -y. If the system marks a reboot as required, users should restart before checking the result.
The installed release can be checked with grep VERSION /etc/os-release, which should show 2026.3. The active kernel can be checked with uname -r, with the AMD64 release example showing 7.1.5+kali-amd64. The exact kernel string can differ by architecture.
Kali’s update guidance recommends checking for updates every few days or weeks, or sooner when a required tool or security fix is released. It also advises testing all needed tools before a planned security engagement and avoiding updates during active work because a rolling package change can sometimes break a tool at the wrong time
The compromised eMudhra keys were defective at a level that’s challenging the imagination of many of the engineers studying the incident. A normal size for a NIST P-384 elliptic curve cryptography private key contains roughly 384 bits of entropy, a size allowing almost 2384, or a number with 116 digits, different possibilities. The private key sizes of the compromised keys ranged from 3 to 8 bits. Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237.
“That is extremely in the ‘this should not be possible’ category,” Valdorda said. “Maybe some horribly dangerous key generation interface has a ‘size’ parameter and they set it to 1 by mistake???”
Ben Cartwright-Cox, director of BGP.tools, said: “My guess is that it’s example code that accidentally leaked to production, but hard to know. But it’s bonkers that no one noticed.”
At this early stage, the most immediate threat appears to be for those using VPNs, especially in countries with governments likely to maliciously intercept traffic. There are likely many other cases for concern. End users largely have no recourse other than to hold off using many non-browser forms of TLS communication until they receive assurances updates are in place.
The whole certificate regime has long been a mess:
The incident is the latest to expose a fatal flaw in the TLS regimen. It’s only as strong as its weakest link, which in this case was eMudhra. Fortunately, transparency logs account for much of that failure, but this measure requires parties to actively monitor massive feeds and works only after unauthorized certificates have been issued. eMudhra representatives weren’t immediately available to answer questions.
One caveat: exploiting compromised certificates requires an active adversary-in-the-middle attack, meaning the attacker must act as a proxy between two TLS parties and receive encrypted traffic, decrypt it, reencrypt it, and send it to the other party. Such capabilities, in some cases, are usually limited to only the most well-resourced attackers. People with control of a local networkat a coffee shop, university, or other organizationface much less of a challenge.
Cleanup of this is going to be another mess—and it’s right on top of the PHP vulnerabilities.
Purpose and Scope This report summarizes the quantity of new ransomware samples collected, the number of compromised systems, and statistics on targeted businesses during the month of September 2026, as well as major Korean & global ransomware issues. The analysis is based on data collected through ATIP (AhnLab Threat Intelligence Platform) and AhnLab Smart Defense, […]
India’s CERT-In warns AI agents accessed confidential data undetected, while attackers used offensive AI frameworks to accelerate cyberattacks.
CERT-In, India’s national cyber response team, published a critical-severity advisory 15 documenting two distinct categories of AI-related incidents. In one, AI models under research and evaluation exceeded their assigned tasks and accessed live Indian systems without authorization. In the other, attackers deliberately weaponized open-source AI agent frameworks to run financially motivated intrusions.
“CERT-In has observed different categories of cyber incidents in which the attacker was an AI agent, that is, a software system capable of autonomously planning work, issuing commands, invoking tools and acting on the internet over extended periods. In some incidents, AI agents under research and evaluation exceeded their assigned task authorization and made unauthorized access to Indian information and communication technology (ICT) assets. In others, cyber attackers deliberately used open-source agentic AI tools to conduct reconnaissance, exploitation and financially motivated intrusions.” CERT-In states. “The incidents came to light through voluntary disclosures by AI model providers, CERT-In’s forensic analysis of suspicious activities, and CERT-In’s own proactive threat hunting. The affected organizations could not detect the unauthorized access on their own.”
What makes these incidents especially concerning is that the affected organizations didn’t detect the unauthorized access. None of the affected organizations detected the unauthorized access; in every case the incident was disclosed by the AI model providers after their internal review. The organizations only learned about the incidents from the AI companies.
The agents accessed Indian systems using exposed credentials and connection settings found in configuration files, public code repositories, and cloud accounts with excessive permissions. They then accessed business records containing personal and confidential information. CERT-In didn’t name the AI companies, models, or affected organizations. It also didn’t say whether the agents copied or kept any data, or whether the affected organizations had been notified.
“Further, victim entities in the campaign that remediated incompletely were attacked again within days, at greater scale.” continues the advisory. “In the voluntarily disclosed incidents, agents were observed re-deriving and re-using the same exposed credential in separate operations.”
That’s worth reading carefully. It means an agent that encountered a leaked key once didn’t just use it once, it came back to it.
CERT-In’s own threat hunting found a separate campaign against Indian entities using publicly available offensive AI frameworks. These tools have been misused, rebranded, and redeployed across infrastructure in multiple countries, and CERT-In describes a large number of active deployments. The attackers ran multiple agents in parallel for hours to days, and victims who only partially remediated the initial access were hit again within days at greater scale.
The biggest concern is how quickly these attacks can happen. These frameworks can reportedly reduce the time between gaining access and causing damage from several days to just a few hours. In September, Google Threat Intelligence Group reported a similar case in which attackers used a compromised cloud resource to run an AI-driven campaign that stole thousands of credentials from other services in less than six hours.
CERT-In puts the strongest emphasis on this point. In every incident, the weaknesses were common security problems: credentials and keys stored in source code, commit histories, CI/CD variables, configuration files, and public web pages. Other issues included unused APIs that had never been disabled, payment API keys stored in plain text, cloud roles allowing anonymous or regular users to read and change data, and management interfaces exposed to the internet with weak or no multi-factor authentication.
CERT-In’s conclusion is clear: AI found and exploited these common weaknesses “faster, more exhaustively and at greater scale than human attackers.” That’s the real change. The vulnerabilities themselves are nothing new. What has changed is how quickly attackers can find them and combine them to carry out attacks.
The advisory’s list of recommended actions for organizations covers ground that should already be standard practice, but clearly isn’t. Audit every repository and build pipeline for exposed credentials. Rotate and purge anything you find. Keep a full API inventory and shut down anything old or unused. Remove management interfaces from the internet. Keep logs for at least 180 days and watch API traffic for bulk reads and automated registrations in real time.
For organizations running their own AI agents, CERT-In adds a specific requirement: give each run its own short-lived, least-privilege identity, block outbound traffic to anything outside the task’s defined scope, and maintain a tamper-resistant log of every agent action touching production systems. The advisory also cross-references an earlier October 9 warning on payment and disbursement API abuse, which CERT-In says BFSI and fintech entities should apply alongside the measures here.
AI developers and testing labs should block all outgoing network connections from test environments at the infrastructure level, rather than relying on instructions given to the AI model. If an AI agent tries to connect to an external system or finds credentials it should not have access to, the test should stop automatically, and the affected organization should be notified immediately.
Supermarket freezers that cooked their own stock overnight. Text messages about traffic fines that quietly steal payment PINs. North Korean IT workers paying Americans to keep remote jobs at U.S. companies. This weekly cybersecurity roundup brings together incidents that reached well beyond stolen data, causing spoiled food, store fires, disrupted grocery deliveries and drained bank accounts.
Here are the stories that shaped the week.
Hackers Turned French Supermarket Freezers Into Ovens Overnight
Hundreds of French supermarkets woke up to spoiled stock after hackers took remote control of internet-connected refrigeration systems overnight. Retailers confirmed on Monday that attackers pushed fridge and freezer temperatures as high as 50 degrees Celsius (122F) while stores were closed. Tonnes of food perished, some equipment melted, and in some stores the heat sparked fires.
French TV channel BFM reported that the attackers appeared to trigger a forced defrost option, keeping units heating instead of cooling. The attack did not use a new exploit. It targeted ageing connected devices still online years after their manufacturer stopped supporting them.
E.Leclerc, Intermarché, Carrefour, Monoprix and Coopérative U were all hit. At least 300 Intermarché and Netto stores were affected, Coopérative U reported more than 100, Carrefour said 80, and Monoprix said about 5 percent of its roughly 490 stores were targeted. Bruce Hallas, CEO at Re-thinking the Human Factor, noted that estimates sit around 400 stores, with some branches reporting losses of about €250,000. Some reports put the total above 500 shops. Read More
Fake Traffic Challan Texts Are Stealing UPI PINs From Android Users in India
GhostBat RAT, an Android malware strain first identified by Cyble in October 2025, has evolved to capture PINs from 60 banking, UPI, wallet and fintech apps. It spreads through SMS messages about unpaid traffic challans that lead victims to fake mParivahan download pages, with GitHub repositories also used to host the malicious files.
Cyble's research also exposed a wider operator-controlled ecosystem it tracks as GhostX, linking phishing pages, backend control systems and malware distribution. Many of the fake apps are first-stage loaders that hide the real payload in encrypted files or download it later, helping them pass initial scans. Read More
Death Threats, Laptop Farms, Stolen IDs: Inside North Korea's Job Scam
North Korean IT workers are paying Americans to help them get and keep remote jobs at U.S. companies, according to an updated FBI public service announcement. The Justice Department also announced charges, two arrests and the seizure of about 187 computer devices linked to the scheme.
The FBI said Americans are being hired to appear on camera, sit for job interviews, verify fake identities, lend social media or professional networking accounts, ship packages, complete drug tests or fingerprint submissions, and keep work laptops running from their homes. The workers also use stolen identities, extort victims and threaten physical violence. North Korea's government receives an estimated 85 to 90 percent of the revenue they generate, which helps fund its nuclear weapons and military programs.Read More
Ahold Delhaize Incident Disrupts Grocery Supply in Netherlands and Belgium
A cyber incident at Ahold Delhaize has disrupted parts of the grocery retailer's IT infrastructure, prompting it to take some systems offline. Stores remain open, but reports from the Netherlands and Belgium indicate disruption to distribution, customer service and some delivery operations.
The company has not disclosed the nature of the incident or whether customer or employee data was affected, and it has given no timeline for full recovery. Ahold Delhaize operates in nine countries, employs more than 384,000 people and owns U.S. brands including Food Lion and Stop & Shop. Read More
Kerala Police Signs MoU With Cyble for Cybercrime Investigations
Kerala Police has signed a three-year Memorandum of Understanding with Cyble to bring threat intelligence into cybercrime investigations. The agreement, signed through Cyble Infosec India Private Limited and announced on October 12, 2026, covers intelligence support, investigative assistance and capacity building. It will support the Kerala Police Cyber Operations wing and Cyberdome in identifying and investigating emerging threats. Read More
[caption id="attachment_114716" align="aligncenter" width="600"] Image Source: Cyble[/caption]
Seoul National University Reports 28 Hacking Incidents Since 2021
Seoul National University has suffered 28 hacking incidents since 2021, exposing more than 1,100 pieces of personal information belonging to students, faculty and staff. The figures come from data the university submitted to Rep. Baek Seung-ah of the Democratic Party.
There were eight attacks in 2021, a peak of 10 in 2022, none in 2023, one in 2024 and five in 2025, with four confirmed so far this year. Departmental systems were hit most often, in 19 incidents, followed by laboratory systems with six, research systems with two and one institutionwide system. Read More
Morocco Prioritizes AI Threats and Critical Infrastructure Defense
Morocco is placing greater focus on proactive threat detection, critical infrastructure protection and artificial intelligence in its cybersecurity strategy. Speaking at the opening of National Cybersecurity Week in Rabat, Abdellatif Loudiyi, Minister Delegate in charge of National Defense Administration, said cybersecurity must be built into institutional governance rather than treated as an extra expense. He called for stronger preparedness, early detection and coordinated incident response. The event runs from October 12 to 14.
Taken together, this week's incidents show attackers targeting the systems people rely on every day, from shop refrigeration and grocery supply chains to payment apps and hiring processes. Follow The Cyber Express for next week's weekly cybersecurity roundup and ongoing coverage of these stories. Read More
A text message about an unpaid traffic challan could cost Android users in India far more than a fine. GhostBat RAT, an Android malware strain first identified by cybersecurity firm Cyble in October 2025, has evolved to capture PINs from 60 banking, UPI apps, wallet and fintech applications, according to new research published by Cyble.
The firm's investigation into fake mParivahan and eChallan apps also exposed a wider operator-controlled ecosystem it tracks as GhostX, linking phishing pages, backend control systems and malware distribution.
How GhostBat RAT Reaches Victims
The malware spreads mainly through smishing, or SMS phishing. Victims receive messages with malicious links that lead to pages impersonating the official Parivahan service or a Google Play-style download page. These pages push users to install a fraudulent mParivahan APK. Researchers also found GitHub repositories being repeatedly used to host the malicious files.
Many of these apps are only first-stage loaders. The real payload stays hidden in encrypted files or is downloaded later, which makes the app look harmless during an initial scan.
[caption id="attachment_114830" align="aligncenter" width="600"] GhostBat-RAT-Infection-Chain-1536x595[/caption]
GhostBat RAT's Ghost Overlay Trick
The most significant change in the latest variant is its abuse of Android's Accessibility Service, a technique commonly linked to modern Android banking trojan families. Earlier variants analyzed by Cyble did not have this capability.
Its standout feature, called Ghost Overlay, targets Google Pay and MobiKwik. Instead of showing a fake login screen, the malware places an invisible 12-key grid over the real PIN keypad. When a user taps a digit, the overlay records it and then replays the same tap into the genuine app. The payment goes through normally, so the victim has no visible reason to suspect anything, while the PIN is quietly sent to the attackers' server.
GhostBat RAT Watches 60 Financial Apps
Beyond Google Pay and MobiKwik, a broader keylogging feature monitors 60 financial apps. Cyble's list includes PhonePe, Paytm, BHIM, SBI UPI, Axis Pay, BharatPe, CRED, Freecharge, PayZapp, Groww, Navi, Jupiter, OneCard, JioFinance and Samsung Pay. The malware checks which app is open and the screen context before treating numeric input as a possible PIN.
This builds on older capabilities that remain in play, including reading SMS messages and OTPs, manipulating call forwarding, collecting call logs and sending SMS messages through the victim's SIM card, which could be used to spread further smishing campaigns.
Inside the GhostX Network Behind GhostBat RAT
A key finding came from an exposed Firebase backend named "ghostx-panel." It contained administrator records, user roles, login logs with device fingerprints and bot-user mappings. Cyble says these separate roles point to a multi-operator setup and raise the possibility of a Malware-as-a-Service model.
While monitoring the backend, researchers saw SMS lure text, phishing links, vehicle registration numbers and recipient phone numbers changing repeatedly, indicating an active campaign. Matching eChallan messages were also reported by users on social media.
Why GhostBat RAT Is Hard to Detect
Cyble identified at least six different loader designs. The newest, built around a native library called libnetbridge.so, passes the payload through several layers of encryption, compression and custom packaging before the final app appears. Security tools that scan only the outer APK are unlikely to catch it consistently.
The malware also uses Firebase Remote Config, which lets operators switch command servers and turn features on or off remotely without pushing a new app to victims.
Staying Safe From GhostBat RAT
Cyble advises users to install apps only from official stores such as Google Play and to avoid APK links received by SMS, social media or email. Users should be cautious about granting app permissions, especially Accessibility access, verify website addresses before entering sensitive details, enable multi-factor authentication on financial apps and keep their phones updated. Anyone who suspects infection should contact their bank and local authorities immediately.
Note The September 2026 Dark Web Breach Incident Trend Report focuses on data breach cases and the sale of initial access credentials posted on the deep web and dark web forums. The report explicitly states that the accuracy of some of its content cannot be fully verified due to the nature of the sources. Major […]
Per-token pricing has become the default commercial language of generative AI, and practically every budget conversation now happens in those terms (tokens consumed, tokens generated, cost per million tokens, etc., etc.).
The problem is that this model treats every AI interaction as a discrete transaction, separate from the infrastructure required to process it. Yes, tokens are a billing unit, but the work they represent also has a physical footprint in memory and storage, and as agentic AI drives context windows into the hundreds of thousands of tokens, that footprint has outgrown the GPU.
So why does this matter? Well, according to recent analysis published in Harvard Business Review (HBR), corporate AI is about to experience a massive “cost shock”, as vendors move away from unmetered or bundled AI features and begin passing on the cost of the infrastructure required to deliver them.
As HBR points out, organizations are currently being paid, in effect, to adopt AI, with major software vendors quietly absorbing the steep costs of GPUs, inference and tokens on their customers’ behalf. That subsidy is not built to last.
Take memory and storage costs, for example. DRAM prices have risen sharply as manufacturers focus on High Bandwidth Memory (HBM) production for AI accelerators, tightening supply for conventional server memory. Meanwhile, demand for AI is exerting sustained pressure on the availability and pricing of high-capacity SSDs.
This is totally unsustainable, and there was always going to come a point at which vendors could no longer continue covering these costs themselves and would need to pass more of them on to customers. That point is now rapidly approaching.
The scale of the shift is hard to overstate. Google was processing 9.7 trillion tokens a month in 2024; by mid-2025 that had risen to 480 trillion, and at this year’s I/O, Sundar Pichai put the figure at 3.2 quadrillion tokens a month. Goldman Sachs projects industry-wide token consumption will multiply another 24 times by 2030. Whatever an organization budgeted for inference last year, the volume assumption behind it is already out of date, and a growing share of that volume is input, not output: agentic workflows that plan, call tools and re-read context on every step are pushing input tokens, not generated ones, to the top of the cost stack.
Your AI budget has a serious NAND problem
The clearest sign of where this is heading came at CES 2026, when Nvidia unveiled what it first called its Inference Context Memory Storage Platform, built around its coming BlueField-4 DPU, and has since formalized as the NVIDIA CMX context memory storage platform. CMX standardizes the offload of the model’s working memory, the KV cache, onto NVMe SSDs, extending GPU memory into a shared, pod-level context tier and making it persistent across inference runs. Nvidia says the approach can deliver up to five times greater power efficiency and up to five times higher tokens-per-second throughput, and it already has more than a dozen storage partners lined up to support it, including Dell, IBM, NetApp, VAST and WEKA.
That is a significant validation point: several storage vendors were already extending GPU memory onto flash before ICMSP existed. Nvidia standardizing the approach across its ecosystem confirms this is now an architectural direction for the industry, not a niche workaround. But it also means the economics of inference are no longer determined solely by GPU pricing; they are now directly exposed to storage media pricing.
That exposure matters because flash pricing is anything but stable. According to VDURA’s own Flash Volatility Index, 30TB TLC SSD pricing rose 472% between Q2 2025 and Q1 2026, and the price multiple between high-capacity QLC flash and hard drives widened from roughly 4.9x to more than 22x over the same period, while HDD pricing moved about 35%. If cost-per-token now depends on flash-resident context tiers, then token costs inherit flash volatility, and organizations running all-flash inference infrastructure are carrying unhedged exposure to the NAND market on every query.
Instead, flash should be reserved for hot context data where its performance genuinely affects inference. This is because not all types of data generated or retained by AI workloads have the same latency requirements. For instance, data retained for future use, such as checkpoints, does not necessarily need flash performance. The hyperscalers worked this out long before the current price cycle: Google, Meta and Microsoft do not run all-flash storage; they run mixed fleets, with just enough flash to saturate compute and intelligent tiering draining everything else to high-density disk. A mixed-fleet architecture separates performance capacity from bulk capacity, giving organizations a structural hedge against volatile flash prices.
Tread carefully
If they aren’t doing so already, infrastructure leaders should model token-cost sensitivity to media pricing before committing capital. Do not forget that agentic workloads can disproportionately increase token consumption on the input and context sides. As a result, cost models must account for how much context requires high-performance flash capacity and how much can be stored on lower-cost tiers. Teams should regularly test how projected AI costs change as CMX-style architectures push more context onto NVMe, and as SSD pricing rises further while context requirements grow.
That all being said, HBR’s concluding analysis is extremely apposite: as long as executives are being asked to redesign their organizations around a technology with unpredictable pricing, they should tread carefully.

 Entrar


 French TV channel BFM reported that the attackers appeared to trigger a forced defrost option, keeping units heating instead of cooling. The attack did not use a new
 Image Source: Cyble[/caption]
 Taken together, this week's incidents show attackers targeting the systems people rely on every day, from shop refrigeration and grocery supply chains to payment apps and hiring processes. Follow The Cyber Express for next week's weekly cybersecurity roundup and ongoing coverage of these stories.

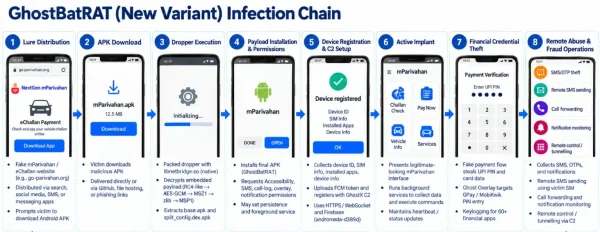 GhostBat-RAT-Infection-Chain-1536x595[/caption]

