GM agrees to a $220 million settlement over drivers' data. Learn how connected-car information was allegedly shared and what vehicle owners should know.
Content The AhnLab SEcurity intelligence Center (ASEC) observed and classified attacks targeting MS-SQL servers and MySQL servers installed on Windows operating systems via the ASD infrastructure. This report summarizes the damage status, attack status, and the types of malware used in the attacks, based on logs identified in the third quarter of 2026. Purpose and […]
A Medyc cyberattack has exposed personal data belonging to patients in Poland after attackers exploited an SQL injection vulnerability in software developed by Qbusoft, the company behind the Medyc medical records and practice management platform. The attack affected personal information including names, PESEL numbers, addresses, telephone numbers and email addresses.
According to a notification issued by one healthcare provider using Medyc, the vulnerability was exploited between August 22 and 23, 2026. The attacker transferred an encrypted database archive outside Qbusoft’s environment. The incident was detected during the night of September 8 to 9.
How the Medyc Cyberattack Happened
An SQL injection vulnerability can allow an attacker to manipulate an application’s database queries and access information stored in the underlying database.
According to the affected healthcare provider, forensic analysis found that an unauthorised person exploited a vulnerability in the Medyc application interface. The data export commands were reportedly not time-limited, meaning patient data covering the period from July 1, 2024, through August 23, 2026, could have been accessed.
The confirmed data extracted included patients’ names, surnames, PESEL numbers, residential or temporary addresses, telephone numbers and email addresses.
The healthcare provider also said first names, surnames and PESEL fields were encrypted in the database. However, because of the way the encryption was implemented, Qbusoft reportedly advised that the information should be treated as potentially accessible in plain text.
Medical Records Remain Under Investigation
The incident has also raised concerns about access to sensitive medical data.
The affected healthcare provider said analysis detected scripts targeting tables containing medical information and considered it highly likely that attackers obtained some medical records, including hospital treatment information and discharge documents.
However, Qbusoft later provided a different update. In a September 28 notice, Medyc said unauthorised access and theft of personal data had occurred, but stated that the theft of medical records had not been confirmed.
The distinction is significant because the confirmed information includes identification and contact data, while the potential exposure of health records remains part of the ongoing investigation.
Qbusoft Takes Security Measures
Following detection of the attack, Qbusoft said it fixed the exploited vulnerability and cut off the attacker’s access.
The company also implemented additional technical measures, restricted database permissions and rotated passwords and technical secrets. Its infrastructure was placed under continuous monitoring.
Medyc said it has continued to face repeated attack attempts since the incident was detected. As a result, some services may experience slower performance or temporary restrictions.
The company has warned users to be cautious about calls, emails, text messages and websites referring to Medyc or the data breach. Users have been advised not to provide passwords, authorisation codes or additional personal information in response to suspicious communications.
Polish Authorities Investigate the Incident
The incident has been reported to Polish authorities, including the Personal Data Protection Office (UODO) and police. Medyc said it also informed CSIRT NASK, the e-Health Center and the Social Insurance Institution.
Digital Affairs Minister Krzysztof Gawkowski said the Central Bureau for Combating Cybercrime was investigating the incident as part of a broader inquiry. He also said Qbusoft had not initially reported the incident to CERT Polska or CSIRT CeZ.
[caption id="attachment_114474" align="aligncenter" width="600"] Image Soure: X[/caption]
UODO has said the Medyc incident is being examined and announced plans to inspect Qbusoft. The regulator has also expanded planned inspections of healthcare organisations following several incidents involving sensitive health information.
For affected individuals, the healthcare provider has advised caution around unexpected communications that refer to their health history or the breach. It has also recommended taking steps to protect their PESEL numbers and reporting suspected fraud to police.
Ireland’s DPC fined Google €403 million over GDPR violations involving location data, transparency, retention and user control.
Ireland’s Data Protection Commission (DPC) just fined Google €403 million, and the case behind it goes back six years, to a set of complaints that never really went away.
The DPC launched the investigation in February 2020 after receiving complaints from several European consumer groups, including BEUC, about how Google handled location data. The investigation covered the period from 25 May 2018, when the GDPR came into force, to 4 February 2020.
“The scope of the Inquiry concerned Google’s processing of location data in three specific features – “Web & App Activity”, “Location History” and “Location Accuracy” between the date of application of the GDPR, 25 May 2018 to 4 February 2020.” reads the DPC’s press release.
Three specific features sat at the center of it: Web & App Activity, Location History, and Location Accuracy. Web & App Activity tracks what a signed-in user does across Google’s own services, sites and apps included, and location data is part of that mix. Location History goes further, following a device’s movements over time and building a private Timeline map of everywhere that phone has been, even when the person isn’t actively using any Google service.
Location Accuracy works differently from the other two. It’s a feature baked into Android itself, sharpening location beyond what raw GPS alone provides, and it applies to anyone running the OS regardless of whether they’ve ever signed into a Google account. That last point matters, because it means the reach of this feature extends past Google’s own user base entirely.
The Commissioners, Dr Des Hogan, Mr Dale Sunderland and Ms Niamh Sweeney, found several problems with how Google handled location data. They said the processing behind Web & App Activity and Location History did not meet the GDPR requirements for lawfulness and fairness. They also found that Google could not show that its Location Accuracy feature complied with the rules on lawfulness, fairness and transparency. Transparency was a problem across all three features, and the company also kept location data for longer than allowed.
That’s four separate violations stacked on the same underlying data. Not one narrow technical slip, but a pattern spanning collection, retention and disclosure all at once.
“Location data is a type of personal data which is processed by way of location tracking, and includes data collected or processed by Google, which by itself or in conjunction with other information an individual’s location can be inferred.”said Deputy Commissioner Graham Doyle. “Location data can bring both benefits and harms to individuals. It can greatly enhance the utility of online services, but it can also reveal a significant amount of information about an individual, including information that is inherently private.”
Knowing where someone is makes plenty of ordinary services genuinely more useful, better maps, better local search, faster delivery estimates. But the same data point, tracked continuously, tells you where someone works, who they see, what they believe, and what they might be hiding. There’s no version of location tracking that’s neutral by default.
The GDPR provides strong protection for personal data across the EEA and requires companies to process this data in a lawful, fair and transparent way.
According to the DPC, Google’s failures meant that users may not have known their location data was being used to target them with ads or build profiles about their interests. This could have reduced their control over their own data. The fact that Google kept location data for longer than necessary made the problem worse.
That’s the practical harm regulators actually care about. Not abstract privacy philosophy, but a real information gap: people not knowing their movements were being converted into ad targeting or interest profiles they never agreed to. If you don’t know it’s happening, you can’t opt out, correct it, or challenge it. The consent mechanism only works if the person on the other end actually understands what they’re consenting to.
Ireland’s Data Protection Commission (DPC) gave Google six months to bring its data processing practices in line with the GDPR. This is not Google’s first dispute with the Irish regulator, and the company is likely to face further scrutiny as location and behavioral data remain important to its advertising business. The investigation also took six years from the initial complaint to the final decision, showing how long GDPR enforcement cases can take.
The €403 million penalty ranks as the fourth-largest EU privacy fine issued by Ireland’s data protection regulator. The DPC has previously imposed even larger penalties on companies including TikTok and Meta, with Meta receiving a record €1.3 billion fine over the transfer of European users’ data to the US.
The Data Protection Commission (DPC) has fined Google €403 million following an inquiry into its processing of Google location data under three features: Web & App Activity, Location History and Location Accuracy. The inquiry examined location data processing between May 25, 2018, when the GDPR came into application, and February 4, 2020.
The DPC launched the own-volition inquiry in February 2020 after receiving complaints from several European consumer rights organisations, including BEUC. The DPC acted as the Lead Supervisory Authority for Google Ireland Limited.
Google Location Data Processing Under GDPR Review
The inquiry examined how Google processed location data through the three specified features and assessed whether the processing complied with requirements under the GDPR.
The DPC's final decision found that Google infringed the GDPR in relation to the lawfulness and fairness of its processing of location data through Web & App Activity and Location History.
The regulator also found that Google failed to meet its accountability obligations regarding Location Accuracy. According to the decision, Google was unable to demonstrate compliance with the GDPR principles of lawfulness, fairness and transparency in its processing of personal data through the feature.
The DPC further identified transparency breaches across all three features.
Findings Cover Data Retention and Transparency
The Google GDPR fine also relates to the retention of location data. The DPC found issues with Google's retention of location data through Web & App Activity and Location History.
The regulator said that location data is personal data that can allow an individual's location to be inferred, either from the data itself or in combination with other information.
Deputy Commissioner Graham Doyle said location data can provide benefits by improving the utility of online services, but can also reveal significant information about individuals, including information that is inherently private.
The DPC said Google's failures could have resulted in individuals being unaware that their location data was being used, including for purposes such as influencing them with advertisements or inferring their interests. It said this could result in individuals losing control over their personal data.
The regulator also said that retaining users' location data for longer than necessary aggravated this loss of control.
What the Three Google Features Do
Web & App Activity is a Google Account setting available to Google Account holders. When enabled, it processes information related to activity on Google services, including websites and applications. This information can include browsing history, search history and location data.
Location History tracks a user's location while they have a compatible mobile device. Users must opt in to the service. It can process data to infer information such as places visited, activities and routes between locations.
The feature also uses Google's Timeline function, which displays a private map through Google Maps showing where users have travelled. The location information is saved for signed-in devices even when the user is not using a Google service.
Location Accuracy is an Android OS feature designed to determine a device's location more accurately than relying only on GPS inputs. Unlike the other two features, it is available to Android users regardless of whether they have a Google Account.
Google Ordered to Change Processing
The DPC imposed administrative fines totalling €403 million and ordered Google to bring its processing into compliance within six months.
The decision was made by Data Protection Commissioners Dr Des Hogan, Dale Sunderland and Niamh Sweeney. The DPC also acknowledged the cooperation and assistance of its peer supervisory authorities during the inquiry.
The regulator said the full decision will be issued in due course.
Note In August 2026, widespread instances of database leaks, the sale of internal data, and the trading of initial access privileges were observed on dark web and deep web forums. Due to the nature of the sources, it was difficult to fully verify the accuracy of some posts. Major Issues ShinyHunters continued to make claims […]
The Kentucky Administrative Office of the Courts (AOC) has confirmed that Kentucky Appellate Court data was compromised in a cybersecurity breach traced to a third-party vendor. West Publishing Corporation, operating as Thomson Reuters Court Management Solutions (Thomson Reuters CMS), informed the AOC that the incident originated within file systems tied to its C-Track case management platform.C-Track is the system relied upon by the Kentucky Supreme Court and the Kentucky Court of Appeals to manage case records. Because Kentucky does not currently use third-party vendors for trial court e-filing, trial-level records that were never part of an appeal remain unaffected. The exposure is limited to Kentucky Appellate Court data that had been stored within Thomson Reuters CMS/C-Track infrastructure.According to Thomson Reuters CMS, an unauthorized third party gained access to and obtained court data from C-Track systems across several states, not Kentucky alone. The AOC noted that Kentucky's Appellate Courts continued to function normally throughout the incident and were not operationally disrupted.
The Kentucky Appellate Court Data Breach Incident
The AOC said it currently has no indication that the unauthorized party shared or distributed Kentucky's data with any outside individual or entity. Thomson Reuters CMS has stated it is coordinating with third-party cybersecurity specialists and law enforcement, and has assured every affected jurisdiction, including Kentucky, that mitigation measures have been implemented to reduce the risk of future unauthorized access.Any individuals ultimately confirmed to be affected by the data breach will be contacted directly by Thomson Reuters CMS. Those notified will receive additional details about the incident along with 12 months of complimentary credit monitoring and identity theft protection, funded by the company.
Scope of Impact Still Under Review
Thomson Reuters CMS is currently working through each affected court system individually, reviewing what data was exposed and determining which people or organizations warrant notification. The company has indicated this review will take time given the multi-state scope of the breach.The AOC, however, has pressed for a faster timeline, telling Thomson Reuters CMS that it expects prompt resolution and swift notification to anyone impacted. As of now, the total number of individuals or organizations affected — if any — has not been determined. Thomson Reuters CMS has committed to covering all costs associated with the breach and will handle notification once affected parties are identified.
AOC Response and Oversight
The AOC emphasized that safeguarding information entrusted to Kentucky's Judicial Branch remains a core responsibility. As the investigation proceeds, the office says it is closely tracking developments, evaluating any potential consequences for the Judicial Branch, and following its established cybersecurity protocols to protect the appellate case management system tied to the Kentucky Supreme Court and Court of Appeals.The AOC is also taking part in ongoing status briefings with the National Center for State Courts and is coordinating with officials in other states affected by the same Thomson Reuters CMS/C-Track breach, as the response to this data breach continues to unfold on a multi-jurisdictional scale.
The afterlife of our information is a recent phenomenon, and some of the companies with the most to sort through are still just figuring it out.
As far back as 2007, Facebook was forced to reckon with mass grief when users asked the company to maintain the profile pages of the 32 victims killed by a school shooter at Virginia Tech that year. Those pages became de facto memorials for loved ones to fill with comments, and today, memorialization has become a full-fledged feature on both Facebook and Instagram. Platforms like YouTube, Pinterest, and LinkedIn—launched with likely zero strategy for a user’s death—now have procedures for next-of-kin to request that a deceased person’s account be deactivated.
Now, think about all the other ways your data can linger after death.
Every year, people accumulate more and digital stuff—email addresses, social media profiles, contact lists, domain names, subscription services, online banking accounts, and the phones, laptops, and tablets that hold it all—and every year, as that digital stuff accumulates, it compounds into ever more problems for someone else to sort out. Here, a small industry of digital estate planners have cropped up, helping families retrieve and preserve anything valuable, no matter how digital, from Spotify playlists, to poignant social media posts that mattered, to the photos stored on a phone.
And where retrieval fails, artificial intelligence has offered an attempt at comfort. The chatbot service Replika launched in 2015 after its founder uploaded a dead friend’s text messages. HereAfter AI reportedly let users upload voice recordings to power a chatbot that sounded and spoke like the deceased. Film studios have pursued the same idea for entertainment, seeking to portray deceased actors in future films.
Surprisingly, almost none of this activity is governed by law, said Tamara Kneese, author of the 2023 book “Death Glitch: How Techno-Solutionism Fails Us in This Life and Beyond.”
“By and large, there is not a great legal mechanism for protecting the privacy rights of the dead,” said Kneese. “It may not be just that a grieving loved one decides to use a bunch of your data from all of your podcasts to create a chatbot to simulate interacting with you after you’re dead, but it may be that a company chooses, in some way, to use an aspect of your personality, of your demeanor, of your voice, of your likeness after your death without anyone really being aware.”
Today, on the Lock and Code podcast with host David Ruiz, we speak with Kneese—Senior Research Scientist at Partnership on AI—about who owns a person’s data after they die, why every platform has invented its own private policy for the dead, and how the technology built to keep the dead close can vanish just as suddenly as they did.
Or worse yet, as Kneese warned for those relying heavily on certain technologies in grief:
“The company gets sold to someone else or disappears, goes bankrupt, and you no longer have that outlet or place for interaction when you’re mourning another time.”
Healthcare technology giant CareCloud has confirmed that a data breach earlier this year impacted more than 3.75 million people, making it one of the largest healthcare data incidents disclosed this year.
The New Jersey-based company, which provides electronic health record (EHR) and practice management services, first flagged the intrusion in an SEC filing back in March, but the true scope only became clear this month when the Department of Health and Human Services (HHS) breach tracker updated the affected total from roughly 345,000 to 3,756,469 individuals.
CareCloud says an unauthorized third party accessed one of its Amazon Web Services (AWS) environments between March 10 and March 16, 2026. The intrusion caused an eight-hour disruption to one of the company’s six EHR environments before systems were restored that same evening. During a forensic investigation, CareCloud determined that the attacker claimed to have exfiltrated data from databases within that environment.
The stolen data reportedly includes both identity and medical information:
Full names, postal addresses, and dates of birth
Social Security numbers (SSNs) and driver’s license or passport numbers
Medical records and health insurance information
Bank account and financial details, plus full credit card data (including CVV) for a limited subset of victims
What affected customers should do
Anyone receiving a breach notification letter should take it seriously, given the combination of medical, identity, and financial data involved.
If you think you’ve been affected by a data breach, here are steps you can take to protect yourself:
Check the company’s advice. Every breach is different, so check with the company to find out what’s happened and follow any specific advice it offers.
Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonators. Cybercriminals may contact you posing as the breached company. Check its official website to see if it’s contacting victims, and verify the identity of anyone who contacts you using a different communication channel.
Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
Consider not storing your card details. It’s definitely more convenient to let sites remember your card details, but it increases the risk if a company suffers a breach.
A DGFiP cyberattack has exposed sensitive tax and cadastral information after attackers allegedly used stolen credentials to access systems belonging to France's Directorate General of Public Finances. The French Public Finances Directorate said investigations found that data linked to 678,000 individuals and professionals had been consulted and extracted during intrusions in June and July 2026.
The DGFiP cyberattack incidents were identified after a malicious actor claimed illegitimate access to the French tax authority's information system on August 12 and 13. DGFiP said the intrusions involved the usurpation of identifiers belonging to a DGFiP agent and an authorized third party.
DGFiP Cyberattack Exposed Taxpayer Information
After detecting the intrusions, DGFiP immediately suspended access to the accounts involved. Initial access controls did not identify data theft, which the authority attributed to the sophistication of the attack.
A subsequent investigation established that the compromised access points had been used to consult and extract information concerning 678,000 individuals and professionals.
The exposed information included reference tax income, family quotient and withholding tax rate for individuals. For businesses, the accessed information included company names and SIREN numbers. Cadastral data, including addresses and property sizes, was also accessed.
DGFiP said online accounts belonging to individual and professional users were not compromised, and user IDs and passwords were not affected.
The authority notified France's data protection regulator, CNIL, after identifying the data breaches.
Cadastral Data Leak Claim Targets DGFiP
Separately, a hacker using the alias ZeroBytes claimed an attack against DGFiP's Professional Cadastral Data Server (SPDC).
According to the claim cited by FrenchBreaches, the alleged extraction contains 252,149 lines of data representing 2,041,778 people, with multiple holders potentially associated with the same property plot.
The claimed dataset reportedly includes names, surnames, sex, dates and places of birth, addresses, land identifiers, cadastral sections and parcel numbers, as well as information about rights held on properties.
The claim would therefore link individuals to personal information and real estate assets.
However, the figures and technical details in this second claim remain allegations by the cybercriminal. The claim that the system could contain information relating to approximately 20 million citizens is also an estimate made by ZeroBytes and does not establish that this number of people was affected.
Investigation Into French Tax Authority Attack Continues
DGFiP said additional security measures were implemented after investigators uncovered new information. These included preventative shutdowns of access to sensitive information systems.
Investigations remain underway to determine the precise nature and volume of data extracted and the number of users affected.
DGFiP teams are working with France's economic and financial ministries, the High Official for Defence and Security and the National Agency for Information Systems Security, ANSSI.
The authority said it will contact affected individuals and professionals directly from the following week by email or letter. Those notifications will identify the information that may have been accessed or extracted and outline any precautionary measures where applicable.
DGFiP also said it will file a complaint and provide further information as the investigation progresses.
The separate cadastral data breach claim remains subject to confirmation, including the alleged number of affected people, duration of access, methods used to bypass authentication, the full scope of extracted information and whether access remained active when the claim was published.
The confirmed DGFiP investigation and the separate ZeroBytes claim therefore present different sets of figures and allegations, with the full scope of the incidents still being determined.
France’s tax authority confirmed a cyberattack exposed taxpayer data as officials investigate the breach’s scope and an unverified 678,000-record claim.
Samsung plans to ban Smart TV apps containing residential proxy software after researchers found apps could route traffic through users’ home connections.
While monitoring attack cases targeting MS-SQL servers, the AhnLab SEcurity intelligence Center (ASEC) identified an instance in which the Larva-26009 threat actor installed the XMRig CoinMiner. While the installation of CoinMiner is common in attack cases targeting MS-SQL servers, in this particular attack case, the attacker installed VShell and GotoHTTP to gain control over the […]
Twenty years ago, a British mathematician named Clive Humby popularized a phrase that came to describe data’s relationship with the entire global economy: “Data is the new oil.”
Pithy as the phrase sounds, it is undeniably true.
Data steers decisions at businesses of every size. Data created entirely new industries built around its capture. And, for a select number of companies, data has produced billions—if not trillions—of dollars in value.
So how is it that, on the dark web, your stolen identity can be purchased for just 95 cents?
That’s what a Malwarebytes researcher found last month after spending 48 hours inside the dark web to investigate cybercrime. Across a variety of forums and directories, he found subscription plans for malware that steals information once implanted on a device. He found guides for deploying social engineering scams. He found people selling their services to build fake websites that trick people into handing over their usernames and passwords. And he found one of the dark web’s most traded commodities—personal data, packaged together about individual people, to help a cybercriminal commit identity fraud.
These packages are called “fullz.” For victims in the United States, a fullz contains a full name, Social Security Number, date of birth, address, and other personal details. That is enough, on its own, for a cybercriminal to potentially open a bogus line of credit, file a fake tax return, access financial accounts, or obtain medical services under someone else’s name.
As we wrote on Malwarebytes Labs:
“For less than the cost of a cup of coffee, a cybercriminal can buy enough information to devastate someone’s financial life.”
It’s the kind of risk that could scare anyone, especially considering the scale behind it. In just the first six months of 2026, Malwarebytes found more than 7,500 compromised data sets on the dark web containing more than 8.4 billion records.
And yet, even today, cybersecurity professionals still get asked why anyone should bother protecting their data.
The public, understandably, are exhausted. With data breaches happening every week—if not every day—cybersecurity can start to feel pointless. With young people unable to build financial security, they start believing that they have nothing worth stealing. And with Big Tech already collecting our every movement, behavior, click, and concern, people understandably feel powerless to fight any kind of data abuse, be it corporate or criminal.
So today’s episode approaches the question from a different direction. This isn’t about why you should protect yourself—plenty of company websites will tell you that, and most of them rely on fear. This is about why hackers want your data in the first place.
Today, on the Lock and Code podcast, host David Ruiz explains how cybercriminals turn a single repeated password into account takeover, how a screenshot of your house from Google Maps became a tool in extortion emails, and why the most benign information about you—an address, an age, one public photo—is often the most useful data a stranger can buy.

 Entrar


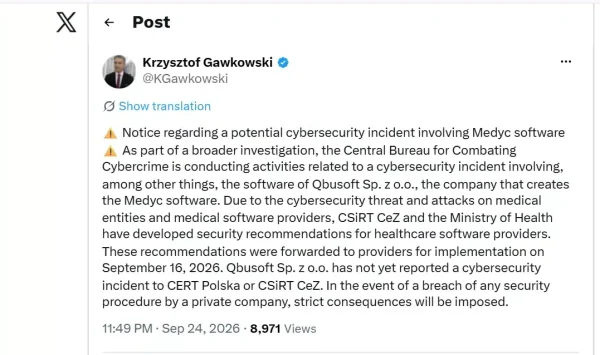 Image Soure: X[/caption]
UODO has said the Medyc incident is being examined and announced plans to inspect Qbusoft. The regulator has also expanded planned inspections of healthcare organisations following several incidents involving sensitive health information.
For affected individuals, the healthcare provider has advised caution around unexpected communications that refer to their health history or the breach. It has also recommended taking steps to protect their PESEL numbers and reporting suspected