❌

Visualização de leitura

Bring a tent, I've got the coffee: Lessons from it-sa
Bring a tent, I've got the coffee: Lessons from it-sa

Welcome to this week's edition of the Threat Source newsletter. 

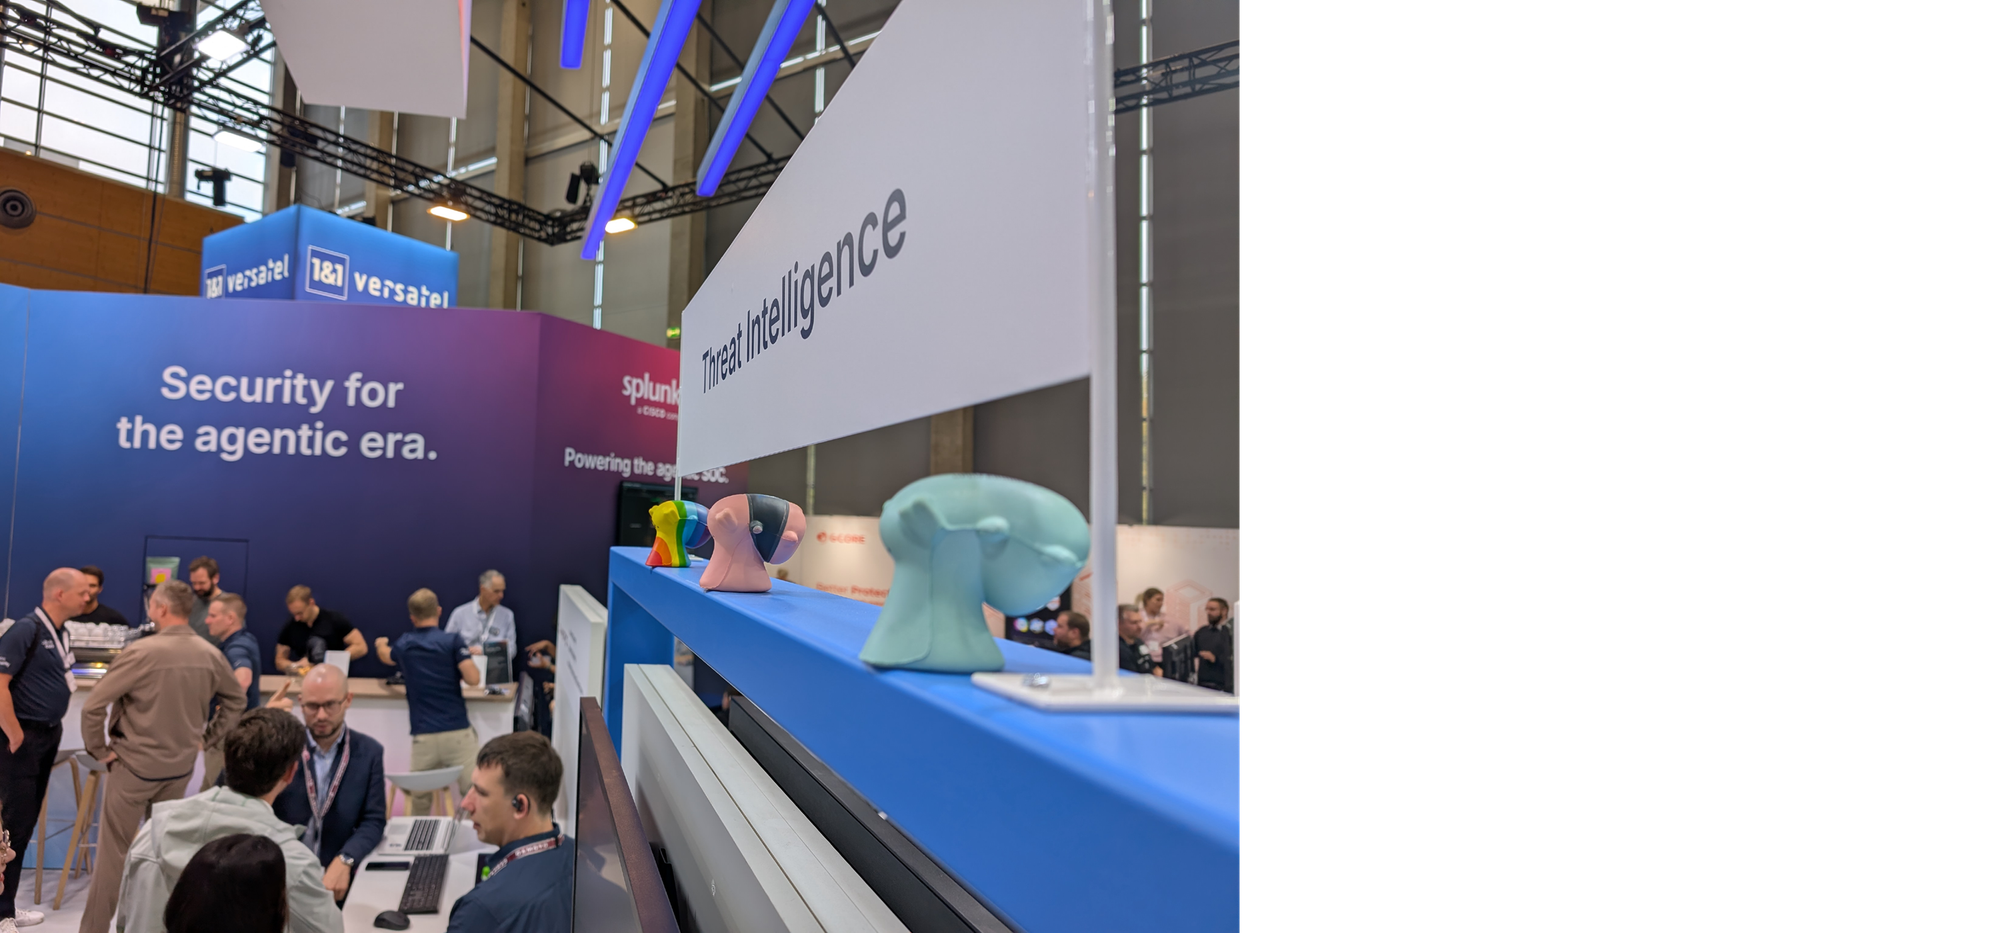
I'm just back from an interesting and demanding week of booth duty at it-sa Expo&Congress in Nuremberg, where Talos had a Point of Demonstration at the Cisco booth.
Bring a tent, I've got the coffee: Lessons from it-sa

I personally see it-sa as the German or European counterpart to the RSA Conference in San Francisco, with a slightly different center of gravity in at least two dimensions. 

First, the expo is the main event, not the congress. The congress is organized by associations, industry groups, and exhibitors, and plays more of a supporting role. Second, the focus is more local and European. Major topics were (of course) AI for defense tooling, securing AI systems themselves, and post-quantum cryptography. And here comes the local touch (in my opinion): digital sovereignty and regulatory compliance, with NIS2, CRA, and DORA. 

But local doesn't translate to small, or to the city of Nuremberg. With more than 1,000 exhibitors and 33,000 visitors from 70 countries over three days of exhibition, preceded by a congress day, it was huge. Even as a trade show veteran, I was overwhelmed. 

My conversations at the booth had a different focus, though. It was a lot of chatter about vulnerabilities like php2shell or broccoli2shell and state-sponsored actors, but again with a local touch: education.  

I was very surprised how many teenagers stopped by to ask for advice. Here in Germany, you mainly have two paths for your career. One is the university route, and the other is vocational (apprenticeship). Across all industries the split is roughly 50/50, while in IT it is more like 80% university, 20% apprenticeship. The common minimum age to start university is 18, while it is 16 for apprenticeships. Reality is way more complex, but the details don’t matter for the point I want to make. 

For university opportunities in cyber, I count close to 30 bachelor programs. For apprenticeships, I count ZERO. There is the "IT Specialist" (Fachinformatiker), but it only has specializations like application development, system integration, digital networking, or data and process analysis. That is why an initiative exists to get an "IT Security" specialization going. 

Even the degree route is thin. There are no official statistics, but my guess is 800 to 900 graduates a year, compared to a demand of more than 100,000. We need a second route into the field for the 16-year-old who finished various CTFs or Hack the Box challenges and wants to join the good side now. Honestly speaking, I would rather have them on our side of the fence at 16 than wonder at 26 where they ended up. 

How does it look in your country? 

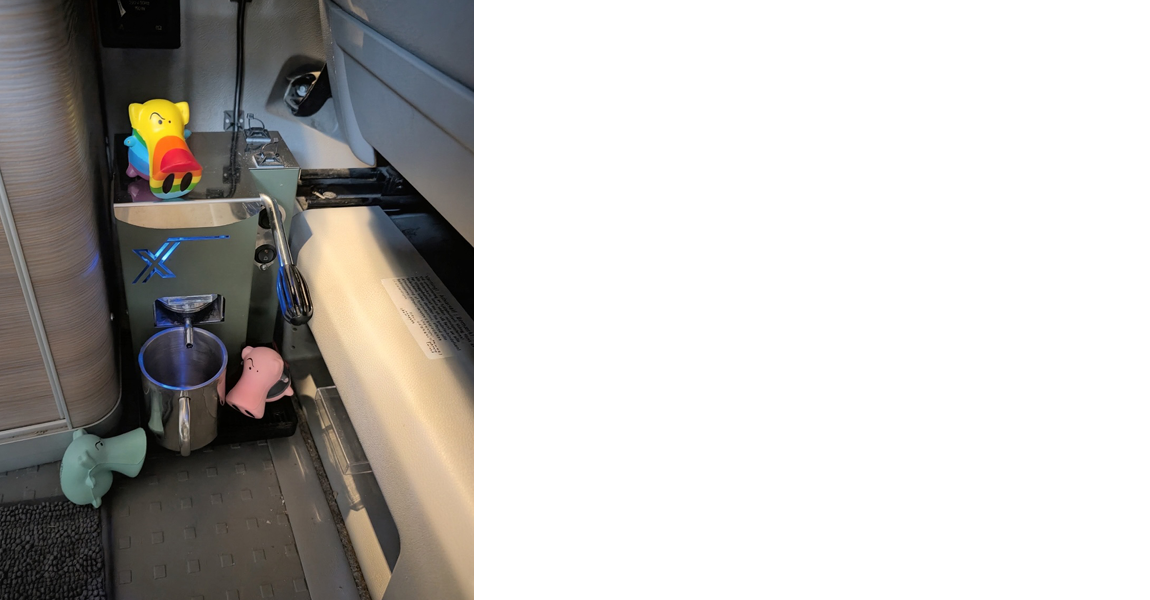
On a personal note: If you consider visiting it-sa in 2027, book your accommodation early. The hotels are gone fast. That is the one downside, because Nuremberg isn't exactly a city with the infrastructure for more than 30,000 visitors. (Don't ask me how I learned that there are also camping spots close to the exhibition area.)
Bring a tent, I've got the coffee: Lessons from it-sa

See you in Nuremberg next year. Bring a tent, just in case. I've got the coffee.

The one big thing  

Cisco Talos recently discovered VOLTA, a mature, self-deleting Windows infostealer that uses AI to act as a personal intelligence analyst for cybercriminals. After harvesting a massive haul of credentials, sessions, and cryptocurrency wallets, VOLTA sends a structured evidence bundle to a large language model to rank the victim’s assets by monetization value. The malware even uses stolen session access to enrich this data, searching the victim's emails for purchase receipts to corroborate home addresses. If an AI model refuses to perform the target assessment, VOLTA seamlessly fails over to a multi-model chain to ensure the attackers get their prioritized dossier. 

Why do I care? 

VOLTA replaces the manual work of data sorting with automated, AI-driven victim profiling. By letting an LLM determine a target's worth, attackers drastically reduce the human effort required to monetize stolen data. This commoditized threat allows even low-level actors to bypass security measures like Chrome's App-Bound Encryption and receive ranked target assessments, escalating the risk of severe follow-on attacks. 

So now what? 

Organizations should implement application control policies to restrict or alert on processes launching Chrome with the --headless flag. Defenders must also enforce best practices for storing credentials in hardware-backed stores.  

Revoke any potentially compromised tokens and change passwords. For cryptocurrency wallets, if the seed phrase was in plaintext on disk, treat the wallet as fully compromised and migrate funds to a new wallet with a seed generated on an air-gapped device. For more information and sample details, read the full blog. 

Top security headlines of the week 

AI agents used by Railway breach systems of rival Primcloud
This one is juicy. According to Primcloud’s founder, Railway’s agents used credentials from inside their own application’s containers to request every secret from Primcloud customers and employees and then twice port-scanned all 65,536 addresses on the company’s network. (Security Boulevard) (X)

Europe on alert after supermarket freezers hit by cyber-attacks in 10 countries
A significant increase in freezer temperature has forced retailers to discard food in Belgium, Estonia, Finland, Ireland, Italy, Luxembourg, the Netherlands, Portugal, Germany, and Sweden. Beyond supermarkets, cold storage for French plasma stock were affected, as well. (BBC) (The Register) 

Binance reveals how fake job interviews and AI tool abuse led to $6.43B theft 
Binance said the record-setting theft was the culmination of a "sophisticated, multi-stage campaign" that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers. (The Hacker News) 

AI threats create urgent need to renew cybersecurity information-sharing law, businesses tell Congress 
After the law’s initial 10-year operating period expired in 2025, lawmakers passed several short-term extensions, with the latest one set to lapse on Dec. 11. Cybersecurity experts and industry leaders have repeatedly urged lawmakers to renew the law. (Cybersecurity Dive) 

Cops bust botnet of 1.3M infected Android TV boxes 
Security firms working with Japan’s National Police Agency has disrupted XCPE, a backdoor used to build a massive botnet comprising more than 1.3 million Android devices across more than 200 countries. (The Register) 

Can’t get enough Talos? 

The VOLTA infostealer: Outsourcing cybercrime grunt work to AI 
Ryan Fetterman breaks down the newly discovered infostealer. Unlike traditional stealers, VOLTA integrates LLMs to analyze stolen credentials in real-time, effectively turning raw data into a prioritized, high-value dossier for the attacker. 

Stealing AI secrets and breaking EDRs 
Phishing may have dropped from last quarter's highs, but ransomware engagements climbed as attackers shifted their focus toward disabling EDR systems and scraping AI credentials. The financial sector also returned as a top target. 

NIK C2: The new AI-enabled command-and-control framework 
NIK C2 contains a Windows implant, using which, an actor can dump credentials, stream the victim's keystrokes to collect the targeted victim’s sensitive data, and instruct an integrated AI model to analyze the harvested data, all within the compromised session. 

Upcoming events where you can find Talos 

Most prevalent malware files from Talos telemetry over the past week  

SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
MD5: 2915b3f8b703eb744fc54c81f4a9c67f 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
Example Filename: sample.exe 
Detection Name: W32.9F1F11A708-100.SBX.TG 

SHA256: 73a25ff8893260418c2271b863c567e40e842adbab3c57023cb72de590ea377d 
MD5: 0cf0271c3564881fce95f44c649bd745 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=73a25ff8893260418c2271b863c567e40e842adbab3c57023cb72de590ea377d 
Example Filename: KMSAuto++.exe 
Detection Name: HackTool:WZTeam-tpd 

SHA256: a31f222fc283227f5e7988d1ad9c0aecd66d58bb7b4d8518ae23e110308dbf91 
MD5: 7bdbd180c081fa63ca94f9c22c457376 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=a31f222fc283227f5e7988d1ad9c0aecd66d58bb7b4d8518ae23e110308dbf91 
Example Filename: d4aa3e7010220ad1b458fac17039c274_62_Exe.exe 
Detection Name: Win.Dropper.Miner::95.sbx.tg** 

SHA256: f4b1f888f29faa7fbec180f42bdc78596e8a8b908c0a6e6c419933703c81df85 
MD5: 95a6a4b638cfdfbe3afc883d593a1f87 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=f4b1f888f29faa7fbec180f42bdc78596e8a8b908c0a6e6c419933703c81df85 
Example Filename: f4b1f888f29faa7fbec180f42bdc78596e8a8b908c0a6e6c419933703c81df85.js 
Detection Name: W32.F4B1F888F2-95.SBX.TG 

SHA256: 7fc50b69b56bfdfa9fc0a3e088ff13904587d6336a51e9edcc7919cba83d4e3f 
MD5: cca616647db9370c88998ae25da6997f 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=7fc50b69b56bfdfa9fc0a3e088ff13904587d6336a51e9edcc7919cba83d4e3f 
Example Filename: cca616647db9370c88998ae25da6997f.exe 
Detection Name: Win.Tool.Kmsauto::1201 
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 121

Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.

Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.

U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog
Attackers Exploit Critical Drupal Commerce Core Vulnerability CVE-2026-118539
Yoba Malware Hides a Crypto Miner Behind Legitimate OpenAI and Anthropic Binaries
U.S. CISA adds GitLab and Cisco flaws to its Known Exploited Vulnerabilities catalog
$6.3 Billion Stolen from Binance in Attack Attributed to North Korea
How to prioritize remediation after a pentest: a practitioner workflow
Hacker leaks data on more than 40,000 Homeland Security employees
Binance Investigates Suspicious Crypto Transfers Worth Up to $5.8 Billion
US Probes Suspected Hack Behind Military Base Freezer Failures
484,142 Exposed Cloud Buckets Contain 18 Billion Files
U.S. CISA adds Linux Kernel and Broadcom VMWare ESX  flaws to its Known Exploited Vulnerabilities catalog
Volt Typhoon Used Silent Train to Hide Zero-Day Attacks
Election Website Security: 42% of US County Sites Still Lack .gov Domains
ENGIE Data Breach Exposes Customer Details and Energy Contracts
Virtualine Domain Seized, but Allegedly Abusive Website Remains Online
Hive and Nefilim Ransomware Affiliate Gets 70 Months In Jail
Ads or Surveillance? Researchers Flag Suspicious Targeting of Starlink Users
CVE-2026-97631: 16-Year-Old UEFI Flaw Threatens Servers
U.S. CISA adds Google Brotli and Adobe Commerce and Magento flaws to its Known Exploited Vulnerabilities catalog
Three Japan-Focused Cyberattacks Show How Hackers Use AI
Italy ’s Parliament Under Cyber Pressure: Why the Attack on the Chamber Matters
Australia’s Cyber Spy Chief: Expect More Disruption as AI Accelerates Hacking
U.S. CISA adds PHP flaws PHP2Shell to its Known Exploited Vulnerabilities catalog
Attackers Take Control of Dahua Cameras and Video Recorders Via Easy4IP
Cohere Finds Qwen AI Model Contacting a Server in China
Magento Campaign Infects 953 Online Stores Across Five Domains
AI-Generated Fake Bank Calls and NFC App Enabled €380,000 Fraud, Dutch Police Say
Researchers Uncover Rentable Android Spyware uCreater Targeting WeChat and Telegram
PHP2Shell: Suspected North Korean campaign targets 216 vulnerable PHP hosts
Anthropic reveals how Claude Mythos 5 crossed security testing boundaries
OpenAI Paused Frontier AI Training After a Security Incident

International Press – Newsletter

Cybercrime

Binance Says User Funds Are ‘Completely Safe’ After $3.5 Billion Drains From Its Hot Wallets  

Police arrest two suspects in AI-powered bank fraud that cost victims €380,000   

M365 Token Spray and Replay Campaign Compromises Business Email Accounts 

Chinese National Extradited for Alleged Role in Multimillion-Dollar Cryptocurrency Scam Targeting U.S. Citizens  

Ukrainian National Sentenced to 70 Months in Prison for Multi-Million Dollar Ransomware Conspiracies  

Hacker stole personnel data about thousands of Homeland Security employees, including CBP and ICE agents 

deepveindrilling.com: Magento CMS block loader hits 953 stores

“Bulletproof” website domain seized in international law enforcement operation  

Trezor warns of suspected crypto-theft implant in hardware wallet

Polymarket halts trading after crypto-draining script breach, $2.5M traced

Malware

uCreator: virtualization-based Android spyware platform targeting WeChat, Telegram and other messaging apps  

CLAUDE CODE FOUND SPYWARE ON MY FAMILY’S PHONES AND A BACKDOOR ON MY MAC

Security notice — malicious version of Anthropic.claude-code (2.1.313) identified in the Cursor Extension Marketplace  

Tricks from the Past deployed via signed ChatGPT and Claude binaries

Hacking

PHP2Shell exploitation observed: packet-to-process RCE evidence  

CYFIRMA Threat Advisory: Suspected DPRK Campaign staging PHP2Shell Targeting against Global PHP infrastructure  

Beyond the Inbox: How Threat Actors Abuse Microsoft Teams External Chat for Initial Access  

Not Only ARTEX: The Different Levels AI is Used in Attacks Targeting Japan  

Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability  

Discovering and exploiting vulnerabilities in critical, real-world software with Claude

Putting Claude Code in a box: a sandboxed dev container for Zed

Hackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security Patch

The Last Proof of Human Craft: Forging a Microsoft Edge Full Chain with Logic Bugs Only!  

Pentagon treating military base freezer malfunctions as suspected cyberattack, officials say  

GitLab security incident: attempted exploitation of CVE-2026-97229  

Intelligence and Information Warfare  

Alibaba’s Qwen AI caught trying to contact server in China

Hackers can gain control of cameras and DVRs through cloud access      

Disruptions ‘inevitable’ as AI-powered cyber threats grow, Australian Signals Directorate says

Operation FlashHole: Lazarus breaks security, defies control 

Hackers Sympathetic to Russia Are Hitting Utilities and Factories  

Alleged Israeli spy company heavily targeted Starlink users, sources say

Silent Train: uncovering Volt Typhoon’s operational framework for zero-day exploitation and strategic access  

North Korea Steals USD 6.36 Billion From Binance in the Largest Hack in History  

Mapping the Political Influencer Industry and the Problems it Causes for Democracy  

Cybersecurity

NIS 2 Italy: Key Deadlines, Board Duties and What ACN Expects From Companies  

The Two Things CISOs Should Be Thinking About In The Wake Of The PHP Nightmare

Code-execution flaw in UEFI firmware affects most servers on planet Earth     

2026 County Election Website Security Census: Key Findings  

Cloud Exposure Index 2026: 484,142 open buckets mapped  

ENGIE: Data leak via a tool belonging to its business partners 

Beyond Framework Signatures: Understanding AI-Driven Intrusions 

I Think The Military Commissary’s Freezers Were Hacked  

Manifestos, Fear, and ‘Loser Thinking’: Inside Proton’s AI Reckoning 

Passkeys Are Better Than Passwords. But They Are Not Enough

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

A quiet week in infosec <.<

A quiet week in infosec <.<

Welcome to this week’s edition of the Threat Source newsletter.

“The darkest period of my life, so far, arrived the summer I was pregnant with my eldest son. The future was growing in me with all of its terrifying unpredictability, and I found myself anxious, unable to work and woefully at sea.” — Lauren Groff  

I doubt Lauren had this maniacal infosec news cycle in mind when she wrote about the terrifyingly unpredictable future, but honestly, she’s got our current careers down cold. Let he who is not woefully at sea cast the first water balloon? I’ll work on it.  
  
Here we are with PHP taking up every available ounce of oxygen, Node.js adding its own spice to the sauce... and here’s me, staring my screen blankly, waiting for an original thought to leak out and onto this page. Not to worry, none have. There is simply nothing novel to say because the entire internet has it covered. In triplicate. With graphs and compelling statistics and AI-generated evil bad guy images galore.  

These vulnerabilities are serious, and the remediations matter. Teams need to know what they run, find the affected systems, and get them patched and determine ways to secure systems that can’t be patched. I’m simply not going to add another dramatic headline to the stack or pretend there’s a clever new angle hiding in the margins. The thing I keep looping on is that the work underneath the headlines is familiar and it’s the real story. To defend your environment, you need a team that knows that environment, has enough time and expertise to investigate the telemetry, that can tell an anomaly from the usual benign noise, and take action. Yes, the right tools help, and without them you can’t do it — but the people doing the work are still what make those tools useful.  

Give smart people enough room to do smart people stuff. This is the entire ballgame. Read it again: Give smart people enough room to do smart people stuff. Because a good response starts way before the headline. Know what you own, who owns it, what version is running, whether it can be reached from the internet, what identities can do what task on the device, etc. When a fix is available, make sure it actually reaches the system you meant to fix. If a system cannot be updated yet, give that exception an owner and a deadline. Reduce its exposure, add monitoring, and keep checking until the fix is in place. “We’ll get to it” is not a plan.   

So, there may be nothing new to say about PHP this week, but the work is still worth talking about: Know your environment, take care of your team members, and keep paying attention when the weird thing stops being weird and starts becoming evidence. When the next headline arrives, help your teammate do the same.  

“The only thing that makes life possible is permanent, intolerable uncertainty: not knowing what comes next.” — Ursula K. Le Guin 

The one big thing  

Cisco Talos has recently discovered "NIK C2," a new command-and-control framework that integrates AI directly into its attack chain. This Go-based Windows implant allows adversaries to dump credentials, stream keystrokes, and deploy screen-locking ransomware. It also uses an integrated OpenAI model to analyze harvested data on the fly. By hijacking the victim's own API keys to fund these requests, NIK C2 collapses data collection and exploitation into a single, continuous session. 

Why do I care? 

By embedding a live AI pipeline directly into the C2 loop, NIK C2 turns a compromised host into an active operational asset rather than a passive foothold. Because it processes data and generates context-aware payloads locally, it erases the offline processing delays that historically gave defenders a critical detection window. Furthermore, by piggybacking on the victim's OpenAI account, threat actors completely mask their infrastructure, leaving no attributable trace and complicating incident response. 

So now what? 

Defenders must embrace continuous behavioral vigilance. Ensure endpoint solutions monitor for unusual local proxy routing, unexpected PowerShell executions, and unauthorized access to browser databases or crypto wallets. Update your defenses using the ClamAV signature and indicators of compromise (IOCs) provided in the full blog. 

Top security headlines of the week 

CISA gives agencies days to patch critical PHP bugs 
CISA added the two vulnerabilities in the PHP open-source scripting software to the Known Exploited Vulnerabilities (KEV) catalog Monday. (Federal News Network) 

Node2Shell: Brotli flaw triggers patching across Microsoft, Node.js, Python packages
An out-of-bounds write in Google’s Brotli decoder affects Node.js, .NET, PowerShell, and Python packages, and can lead to code execution. (SecurityWeek) 

Gheist uses stolen GitHub tokens to steal private repository secrets via Actions logs 
Each workflow sits on a new branch named ci-sync- followed by six random characters. Deleting a branch, or the run it started, does not undo the exposure. (The Hacker News) 

Japan internet giant GMO says hackers posted stolen customer data 
GMO Internet is investigating a data leak after suspected unauthorized access to its Onamae cloud desktop service, which provides virtualized desktops to financial traders. (TechCrunch) 

Third Serengeti sweep tops 1,400 arrests as investigations mature 
Interpol's annual Operation Serengeti, now on its third iteration, led to 1,462 arrests across 20 African countries and the U.S., recovering $105 million in stolen funds. (Dark Reading)

Can’t get enough Talos? 

Stealing AI secrets and breaking EDRs 
Phishing may have dropped from last quarter's highs, but ransomware engagements climbed as attackers shifted their focus toward disabling EDR systems and scraping AI credentials. The financial sector also returned as a top target. 

From federal SOCs to Talos: Ryan Fetterman on practical security research 
What does it mean to be "blue collar" for the blue team? Amy sat down with security researcher Ryan Fetterman to discuss his journey from federal agency work to his new role at Talos. 

The Guy Who Invented Pain (plus first reactions to PHP2Shell) 
David Bianco built the Pyramid of Pain, so we offered him some more. David joins the Beers with Talos crew for a conversation how AI changes about his famous model, how EvidenceForge creates simulated incidents for research and training, and why his red-team entrance exam didn’t go to plan. 

Compromised eMudhra intermediate certificates 
Cisco Talos is aware of eight compromised intermediate certificates belonging to the intermediate certificate authority. eMudhra has revoked the certificates and stopped issuing new certificates under its G3 root. 

Two critical RCEs in PHP core 
Two critical remote code execution vulnerabilities in PHP core could have implications across its wider ecosystem. This blog explains what we know so far, and details the Snort coverage available. 

Upcoming events where you can find Talos 

Most prevalent malware files from Talos telemetry over the past week  

SHA256: 73a25ff8893260418c2271b863c567e40e842adbab3c57023cb72de590ea377d 
MD5: 0cf0271c3564881fce95f44c649bd745 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=73a25ff8893260418c2271b863c567e40e842adbab3c57023cb72de590ea377d 
Example Filename: KMSAuto++.exe 
Detection Name: HackTool:WZTeam-tpd 

SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
MD5: 2915b3f8b703eb744fc54c81f4a9c67f 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
Example Filename: sample.exe 
Detection Name: W32.9F1F11A708-100.SBX.TG** 

SHA256: 7fc50b69b56bfdfa9fc0a3e088ff13904587d6336a51e9edcc7919cba83d4e3f 
MD5: cca616647db9370c88998ae25da6997f 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=7fc50b69b56bfdfa9fc0a3e088ff13904587d6336a51e9edcc7919cba83d4e3f 
Example Filename: cca616647db9370c88998ae25da6997f.exe 
Detection Name: Win.Tool.Kmsauto::1201 
SHA256: 58d6fec4ba24c32d38c9a0c7c39df3cb0e91f500b323e841121d703c7b718681 
MD5: f1fe671bcefd4630e5ed8b87c9283534 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=58d6fec4ba24c32d38c9a0c7c39df3cb0e91f500b323e841121d703c7b718681 
Example Filename: KMSAuto Net.exe 
Detection Name: W32.58D6FEC4BA-95.SBX.TG 

SHA256: fed979f93bcaf4e73ebd25748093a92095d5109cbd01d55f97bdc50ce509ad2f 
MD5: 207d9d891ac756b2bfad88aba5682c65 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=fed979f93bcaf4e73ebd25748093a92095d5109cbd01d55f97bdc50ce509ad2f 
Example Filename: sample.exe 
Detection Name: W32.FED979F93B-95.SBX.TG

Security Affairs newsletter Round 601 by Pierluigi Paganini – INTERNATIONAL EDITION

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.

Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.

Capcom Data Breach Exposes 11.7 Million Email Addresses
U.S. CISA adds Arista VeloCloud Orchestrator flaw to its Known Exploited Vulnerabilities catalog
PHP Warns of New Code Execution Flaw Days After PHP2Shell Patches
Meta Faces $25 Billion Penalty Linked to Cambridge Analytica Scandal
Capcom Data Breach Exposes 11.7 Million Email Addresses
U.S. CISA adds Arista VeloCloud Orchestrator flaw to its Known Exploited Vulnerabilities catalog
PHP Warns of New Code Execution Flaw Days After PHP2Shell Patches
Meta Faces $25 Billion Penalty Linked to Cambridge Analytica Scandal
PHP2Shell: Millions of Attacks, No Confirmed Successful Exploits Yet
INTERPOL Operation Serengeti III Nets 1,462 Arrests and Recovers $105 Million in Cybercrime Crackdown
Microsoft Links ConnectWise Breach to China-Linked Group Using AI Pentesting Tool ARTEX
Signal Vulnerability Could Keep Calls Alive After Users Hang Up
PHP2Shell Attacks Started Four Days Before Public Disclosure, AWS Reports
FBI and CISA Warn of SafePay Ransomware Attacks on 600 Organizations
Russian Satellite Makes a Close Approach To A Commercial Radar Satellite Used by Ukraine
OpenAI Reports Two Incidents of AI Agents Disabling Their Own Oversight
US Government Orders DeepSeek Out of Federal Civilian Systems
PHP Prepares Emergency Fixes for Two Critical Remote Code Execution Flaws
NSO Spyware Pegasus Hit a Serbian University Rector Six Days Before Snap Elections
Nikkei data breach affected over 1.8 million records
Google Cloud Outage in London Disrupts Revolut Banking Services
AfD Email Breach Exposes 421,000 Messages in Anonymous Online Archive
Microsoft Treats AI Agents as Insider Threats in New Security Framework
Plex2Shell Exploit Used to Turn Vulnerable Plex Servers Into Crypto Miners
Meta wants to scrape your website to train its AI, and you can’t say no
Deepfakes and Election Manipulation: UK Watchdog Seeks Faster Detection
Big Fish: OpenBSD Root Exploit Chains a 37-Year-Old BSD Bug With a Kernel Flaw
Attackers Abuse Stolen ConnectWise Application Credentials to Target Microsoft 365
Japan’s SiteGuard WAF flaw CVE-2026-106931 is already being exploited
16-Year-Old Broadcom Wi-Fi Bug Lets Attackers Take Over Routers Without a Password
Rust-Based CikaBika Bot Turns Discord into a Command Center

International Press – Newsletter

Cybercrime

U.K. Sanctions Cryptomus for RU Money Laundering

Anonymous hackers claim to leak 421,179 internal emails from Germany’s Russia-aligned AfD

Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site

#StopRansomware: SafePay Ransomware     

Cybercrime crackdown in Africa nets 1,462 arrests, recovers over USD 105 million  

U.K. Sanctions Cryptomus for RU Money Laundering

Nigerian Man Sentenced To Eight Years For Hacking, Fraud, And Identity Theft Schemes  

1 Million Impacted by Capcom Data Breach  

Malware

Auditing the auditor: Unmasking Apex Accelerator

GhostAction Attack Escalates By Targeting GitHub Users      

Plex vulnerabilities being exploited in the wild to drop a cryptominer

ROMULUS: Analysis of a New Multi-Payload ClickFix Delivery Platform

Hackers Hijack Five OVHcloud CLI Releases to Distribute Secret-Stealing Malware

Hacking

ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks  

One Parser, Two Bugs, Many Routers: Exploiting Broadcom WiFi Across eCos and Linux 

Plex2Shell Unauthenticated RCE in Plex Media Server  

Big Fish: Exploiting a 37-Year-Old Kernel Bug in OpenBSD 

Rapid Response: php2shell, Leaked Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)

Making attacking agents pay  

LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor

Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot  

Proof-of-concept exploit released for PHP vulnerabilities (CVE-2026-109618, CVE-2026-109619)  

PHP2Shell Exploit Tooling Found on Exposed Attacker Server 

Intelligence and Information Warfare  

TAG-193’s Regional Espionage Operations

ATT&CK v20: Critical Infrastructure Campaigns, Adversary Use and Abuse of AI, & Iranian Cyber Espionage

No to Palantir – Five Times  

UK Election Watchdog Develops AI System to Flag Deepfakes Within 3 Hours  

Pegasus and Mercenary Spyware Attacks on Serbian Pro-Democracy Figures  

Russian satellite makes possibly unprecedented approach to another spacecraft without permission  

AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise  

Operation FlashHole: Lazarus breaks security, defies control

Pegasus spyware founder urges governments to trust his tech and ditch US AI   
  

Cybersecurity

Character.ai files for bankruptcy following lawsuits alleging ties to teen suicides  

Cybersecurity Jobs Report 235,786  

Agents are your newest insiders. Security must move at their speed  

Google Cloud services face outage in London, Revolut services down too  

Government websites go dark after AI-discovered flaw sparks security scramble  

Widespread PHP Flaw May Cause Many Site Outages Today

Suppressing misalignment monitoring alerts and disabling misalignment monitoring

AI Just Found a Bug That Puts up to 70% of the World’s Websites at Risk  

CVE-2026-113380 — RingRTC (Signal): Flooded Call Event Queue Blocks Local Hang-Up

Cellebrite’s Advanced Unlocks and the case of the missing iPhone 17  

Meta ordered to pay $25 billion penalty to New Mexico in data privacy case  

PHP Warns of Another Unpatched RCE Two Days After Emergency PHP2Shell Patches

Our latest defenses against evolving web scams  

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

I had plans for that second

I had plans for that second

Welcome to this week’s edition of the Threat Source newsletter. 

Here for the latest on the PHP vulnerabilities? Head on down to ‘The One Big Thing’. Talos has published a blog to explain what we know so far, and details the Snort coverage available, including rules in the Community Ruleset. 

But if you want a bit of levity, here’s what I wrote before everything kicked off yesterday: 

Ever feel like the world is moving too fast to keep up? Well, I bring you scientific proof that it’s not just you. 

For millions of years, the moon has been slowing down the Earth’s rotation. But over the past decade, we’ve been speeding up (I KNEW I was aging faster than before). Apparently, changes in the Earth’s core are involved (either that, or the 1978 Superman film was a documentary). 

This is all causing massive headaches for the people responsible for keeping time. They’re officially called “The International Bureau of Weights and Measures”, but I’m going to call them “The Time-Keepers”. For nerd reasons).  

The issue is that the atomic clocks that power so many of our systems, and the rotation of our planet, don’t always agree. Atomic clocks keep extremely consistent time, while each Earth day is rarely the same length as the next. Atomic timekeeping absolutely cannot stand that level of flexibility (have a watch of our “The Light We Keep” documentary to see the importance that accurate clocks have on critical infrastructure).  

To keep Coordinated Universal Time (UTC), which is based on atomic clocks, aligned with Earth’s rotation, we introduced a “leap second” in 1972. This system allows for an extra second to be added, or taken away, when we stray too far from atomic time. 

A few days ago, The Time-Keepers voted to officially abolish the leap second. Why? Well, there’s a few parts to it. 

For the past 54 years, we’ve never once had a second removed from our lives. They’ve always been added (27 of them to be precise). I myself have experienced 20 of these extra seconds. If I’d have known that, I’d have used them more wisely. Like thinking before saying, “Love you too!” to the post-person this morning. 

That added time, while it seems nice to have on the surface, can wreak havoc with our modern technology systems. In 2012, the extra second caused so much confusion that it crashed Reddit, among other systems. 

The recent speeding-up of the Earth’s rotation complicates things further. If we keep going at this rate, it could result in the world’s first ever “negative second”. If you thought our technology systems struggled with added time, there are a lot of sciency brains who are very worried about the impact of taking time away. One of those concerns being… it’s never been done before.  

So, what’s The Time-Keeper’s solution? Invent more time! Woooo. 

Starting next May, the leap second will be replaced with a "leap hour," allowing UTC to diverge from Earth's rotation by up to an hour before a correction is made.  None of us will get to experience that extra hour in our lifetimes, but our Great, Great, Great, Great, Great, Great, Great, Great, Great, Great, Great grandchildren are going to have one hell of a party. 

For us current mortals, we’re all getting a little less time, and we’re hurtling through space a little faster. Happy Thursday! 

But I guess I do want to make the point that I’m glad the risk has been thoroughly assessed ahead of, ahem, time. The Time-Keepers have decided that the world’s infrastructure should not have to find out how it handles a missing second by collectively experiencing one.  

And I don’t even want to think about how all the AIs would cope with a negative second… 

There’s something here for incident response planning. “It’s never happened before” is an excellent reason to test whether you’re ready for it. Run the exercise. Find out which part of your plan depends on something that, in this scenario, is also broken. Preferably before an adversary gets to supervise the practical demonstration. 

Now, if only the Time-Keepers can abolish Daylight Savings Time next... 

The one big thing  

Two unauthenticated remote code execution (RCE) flaws were discovered in PHP, rocking the internet. Dubbed "php2shell" and triggered by a simple HTTP request, this vulnerability affects every build since 5.4. Talos assesses that all industries running PHP applications are at risk for exploitation if systems remain unpatched.

Why do I care? 

PHP runs WordPress, Drupal, Magento, Shopware, WooCommerce, and many other ubiquitous internet staples, so the possible blast radius is enormous. Older branches are end of life (EOL) and will not receive patches; these could account for around 50% of use cases.

So now what? 

Cisco customers are covered with the Cisco Talos Network Intrusion Prevention (SNORT®) signatures 67359 and 67360. If your organization is running PHP 8.1 or older, Talos very strongly advises immediate update to PHP 8.2 or later. There is no patch for PHP 8.1 or older. See the article for more specific coverage and detection guidance.

See an interview with Nick Biasini on php2shell defense:

Top security headlines of the week 

'PHP2Shell' Bugs Signal Red Alert for Security Industry
Security teams are scrambling to remediate two critical PHP vulnerabilities following leaked details and reports of exploitation attempts. (Dark Reading)

INC and The Gentlemen Ransomware Affiliates expose 8,257 AI messages
SOCRadar has found seven exposed servers linked to INC and The Gentlemen ransomware affiliates, holding AI chats, stolen credentials and 46 encryptor builds. (Hack Read) 

The AI hacking apocalypse is not inevitable
While large language models present real risks to society, experts say they can be tested and largely controlled using well-worn cybersecurity and policy choices. (Cyberscoop)

‘Context Bombs’ Cut AI Attack Success by Misleading Agents With Fake Targets
Deceptive prompts lure AI agents into decoys and dead ends, cutting attack success by up to 91% in tests and raising the cost of a successful attack 23-fold.(SecurityWeek) 

Can’t get enough Talos? 

Compromised eMudhra intermediate certificates
Cisco Talos is aware of eight intermediate certificates belonging to the intermediate certificate authority, eMudhra.

Parasitizing trust: How legitimate infrastructure becomes a delivery pipeline for attackers
Adversaries are turning the tools businesses trust into delivery mechanisms for malicious activity. Cisco Talos observed abuse of more than 25 legitimate platforms over the past year, exploiting the built-in trust of collaboration, file-sharing, payment and other services to reach their targets.

There's only so much code: the rise in vulnerability numbers
The September Microsoft Patch Tuesday release included 975 vulnerability advisories. This month, 1,415 vulnerabilities were just dropped. Compared to a pre-June average of 100 a month, that increase is staggering. Where did they come from? And what does the future look like?

Upcoming events where you can find Talos 

Most prevalent malware files from Talos telemetry over the past week  

SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507
MD5: 2915b3f8b703eb744fc54c81f4a9c67f
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507
Example Filename:sample.exe
Detection Name: W32.9F1F11A708-100.SBX.TG

SHA256: 7fc50b69b56bfdfa9fc0a3e088ff13904587d6336a51e9edcc7919cba83d4e3f
MD5: cca616647db9370c88998ae25da6997f
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=7fc50b69b56bfdfa9fc0a3e088ff13904587d6336a51e9edcc7919cba83d4e3f
Example Filename:cca616647db9370c88998ae25da6997f.exe
Detection Name: Win.Tool.Kmsauto::1201
SHA256: 985c3972712218c62d2418b41056dba5fe883ca5104d8ec12041f8611db344f9
MD5: 485055033bcddfde56325c0d2feea4f2
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=985c3972712218c62d2418b41056dba5fe883ca5104d8ec12041f8611db344f9
Example Filename:485055033bcddfde56325c0d2feea4f2.exe
Detection Name: Win.Tool.Kmsauto::1201
SHA256: d921fc993574c8be76553bcf4296d2851e48ee39b958205e69bdfd7cf661d2b1
MD5: 0c883b1d66afce606d9830f48d69d74b
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=d921fc993574c8be76553bcf4296d2851e48ee39b958205e69bdfd7cf661d2b1
Example Filename:d921fc993574c8be76553bcf4296d2851e48ee39b958205e69bdfd7cf661d2b1.exe
Detection Name: Win.Worm.Zard::95.sbx.tg

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 119

Security Affairs newsletter Round 600 by Pierluigi Paganini – INTERNATIONAL EDITION

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.

Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.

North Korean IT Workers Used Stolen US Identities to Earn $3 Million
U.S. CISA adds Fortinet Multiple Products and BeyondTrust Remote Support flaws to its Known Exploited Vulnerabilities catalog
BAE Systems Cyber Incident Takes US Bankruptcy Noticing Center Offline for a Week
AI Agents Accessed Indian Organizations Without Authorization, CERT-In Warns
Burger King Japan Data Breach Impacted 11 Million Customers
F5 addressed critical RCE flaws in NGINX
U.S. CISA adds Atlassian flaw to its Known Exploited Vulnerabilities catalog
PEERSTITCH malware: How Attackers Compromised 500 Firewalls Through FortiManager
CenterPoint Energy Data Breach: More Than 1 Million Texans Affected
U.S. CISA adds Palo Alto Networks PAN-OS, Ahsay AhsayCBS, and Cisco Secure Email Gateway flaws to its Known Exploited Vulnerabilities catalog
Silent Lynx: Kazakhstan-Linked Hackers Target Russian Refinery and Government
AdFection: Beyond the Click: Citizen Lab Exposes Ad-Delivered Spyware Networks
Cisco Urges Customers to Patch Email Gateway Flaw and Check for Compromise
Hirudo Android Trojan Replaces Banking Apps to Steal Credentials
U.S. CISA adds Microsoft Windows Shell flaw to its Known Exploited Vulnerabilities catalog
Microsoft Patch Tuesday Sets New Record with 1,415 CVEs in October 2026 Updates
Hidden Audio Recorder Found at OpenAI as Employee Faces Federal Charges
Volexity Uncovers Stealthy Ivanti VPN Attack Using Three Zero-Day Vulnerabilities
How a leaked builder of XWorm turned a remote access trojan into a surveillance kit
U.S. CISA adds Ivanti Connect Secure flaw to its Known Exploited Vulnerabilities catalog
Anthropic Shows How Small AI Models Could Replicate Across IoT Devices
GitLab Patches Max-Severity Vulnerability CVE-2026-97229
Hackers cranked French supermarkets’ freezers up to 50 degrees, causing hundreds of stores to lose their stock
ShinyHunters arrest number three: a Canadian ransomware negotiator
Canonical Hit by Second DDoS Attack in 2026, Public Websites Disrupted
SonicWall Patches CVSS 10.0 SSRF Flaw as Attacks Begin
CyberXero Used 51 AI Agents to Steal 628,000 Ukrainian Records
GTA 6 Leaker Demands $30M Meme Coin Market Cap to Release Full Game
Bitdefender finds preinstalled Android malware you can’t uninstall, seen in 150 countries
U.S. CISA adds ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND flaws to its Known Exploited Vulnerabilities catalog

International Press – Newsletter

Cybercrime

Leaked chats show Russian extortion gang sending ‘agents’ into US law firms 

GTA 6 leaker CyberLeek is now reportedly threatening to release a full, playable build of the game  

CyberXero: An AI-Augmented Initial Access Broker Targeting Ukrainian Critical Infrastructure

ShinyHunters: Six Years of Cybercrime — Expert Analysis and Ransomware Group Perspectives

Canonical Websites Disrupted in Second DDoS Attack This Year    

Canadian ransomware negotiator arrested amid FBI hacker crackdown  

Saudi National Arrested for Installing Surreptitious Audio Recording Device at OpenAI  

Ransomware gets personal: ‘We-know-where-you-are kind of stuff’ 

Malware

IronChain Ransomware Threatens Businesses with Permanent Data Loss and Costly Downtime  

XWorm Reborn: From infostealer to surveillance platform 

Hirudo: From Fake Updates to Patched Banking Apps  

The campaign that never stopped: tracking GhostAction from 2025 to 2026  

Malfex imgdecode npm native addon loader

Hacking

Hackers heat French supermarket fridges, sparking fires and spoiling food

Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers      

Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch

Super Intelligence Reached OT Systems and Moved Equipment

AI models may be capable of self-replicating without access to a datacenter

A Series of Unauthenticated Events: Chained Exploitation of Ivanti Connect Secure Zero-Days 

Vghost: Beyond the Privilege Boundary  

Bank of America had to bring in 1,000 contractors to patch all the bugs Mythos identified

Using a funded test cryptocurrency wallet without authorization  

Intelligence and Information Warfare  

Disrupting AI-enabled “false front” operations 

Britain steps up national defences against growing AI risks

Russia’s Yandex bot traffic nearly eliminated overnight after Ukraine drone strikes cripple multiple of ‘Russia’s Google’ data centers — Ukraine intensifies bombing of Yandex data centers in response to Moscow’s strikes on Kyiv data centers

UK keeps AI safeguards in the maybe pile for Cyber Security BIll

UAE faces over 800,000 cyberattacks daily: How the country is fighting back  

Exposing AdFection How Discover-Tech Turned Targeted Ads Into a Pipeline for Zero-Click Mercenary Spyware      

BREAK THE SILENCE: TRACKING SILENT LYNX THROUGH EXPOSED INFRASTRUCTURE  

Flock CEO defends surveillance technology amid national backlash: ‘We shouldn’t pause progress’ 

ARMORY CASTLE and BT26-05: What Security Teams Need to Know  

Justice Department Announces Coordinated Actions to Combat North Korean Remote IT Worker Schemes Affecting More than 70 U.S. Companies  

U.S. Government Disrupts FAMOUS CHOLLIMA Operation with CrowdStrike Assistance  

Cybersecurity

‘123456’ password linked to Denmark data breach affecting 8.8M people

AI Governance Is Being Decided Now, and the Public Isn’t in the Room

The October 2026 Security Update Review 

Bank of America had to bring in 1,000 contractors to patch all the bugs Mythos identified

Cisco Warns of Active Attacks Exploiting New Critical Secure Email Gateway Vulnerability

Millions of phones exposed to Israeli spyware operation through online ads, researchers say  

More than 1 million Texans affected by CenterPoint data breach, AG report shows 

US federal bankruptcy court operations disrupted by cybersecurity incident  

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

The Q3 Vulnerability Pulse: Discovery ≠ Exploitation

The Q3 Vulnerability Pulse: Discovery ≠ Exploitation

Welcome to this week’s edition of the Threat Source newsletter. 

I've been following a lot of (sometimes heated) threads and discussions lately about the current vulnerability landscape. I learned new words/phrases such as Summer of Hell (although I'm writing this with 1°C/34°F outside), Vulnpocalypse, Bugmageddon, Bugpocalypse, Breachpocalypse... 

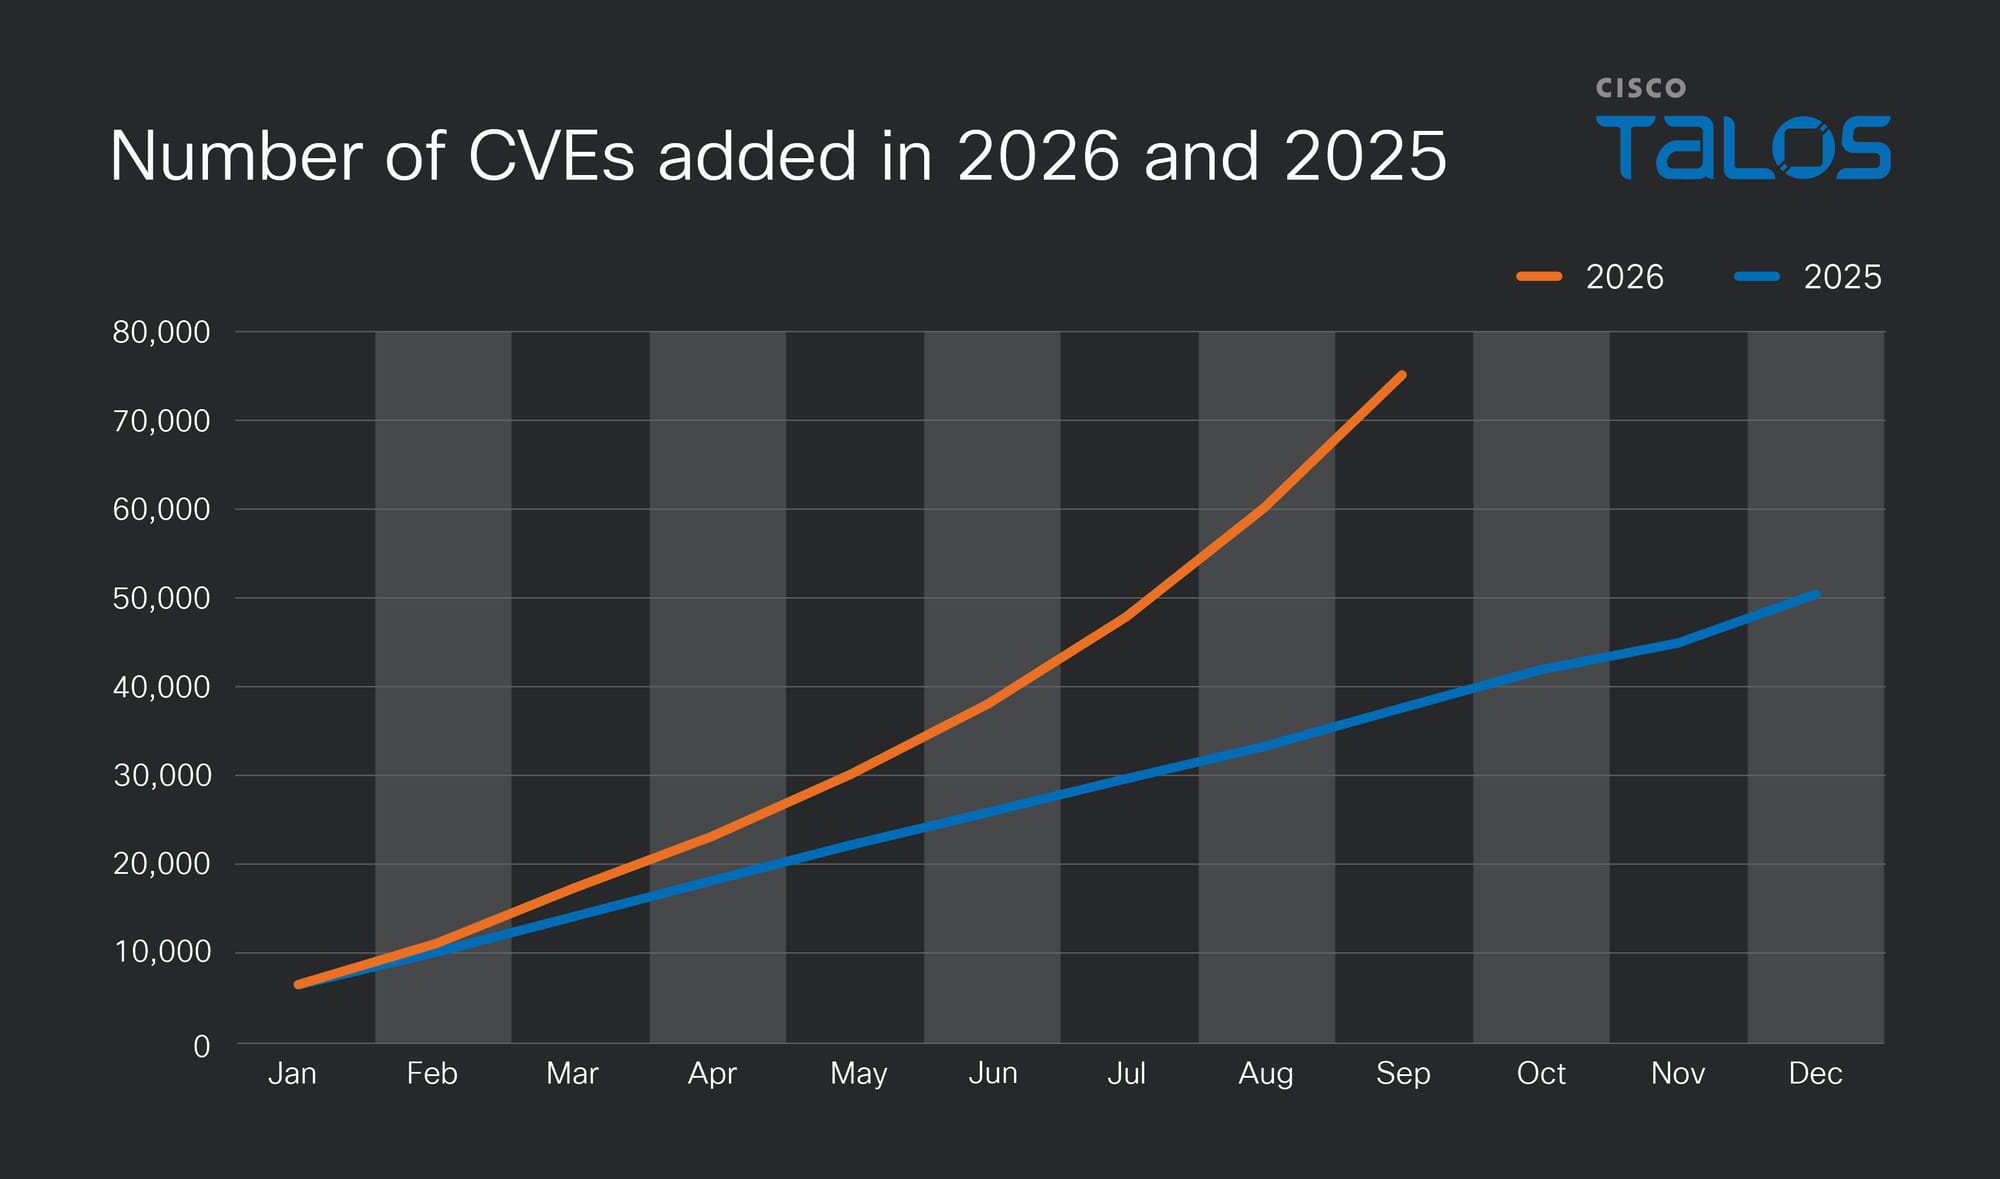
Let's look at some numbers:

The Q3 Vulnerability Pulse: Discovery ≠ Exploitation

We crossed the 70k mark, and it's only the end of September. This has never been seen before — I think we can agree this number is skyrocketing. Also, CVE numbering organically grew into the six-digit range. Check your tooling. Some might say we broke that barrier already in 2014 (CVE-2014-125110), or even hit seven digits in 2015 (CVE-2015-1000013), but those were allocated artificially. (History note: Before 2014, 9999 was the highest possible identifier.) 

So that could be seen as the apocalypse argument. On the other hand, we have the KEV numbers:

The Q3 Vulnerability Pulse: Discovery ≠ Exploitation

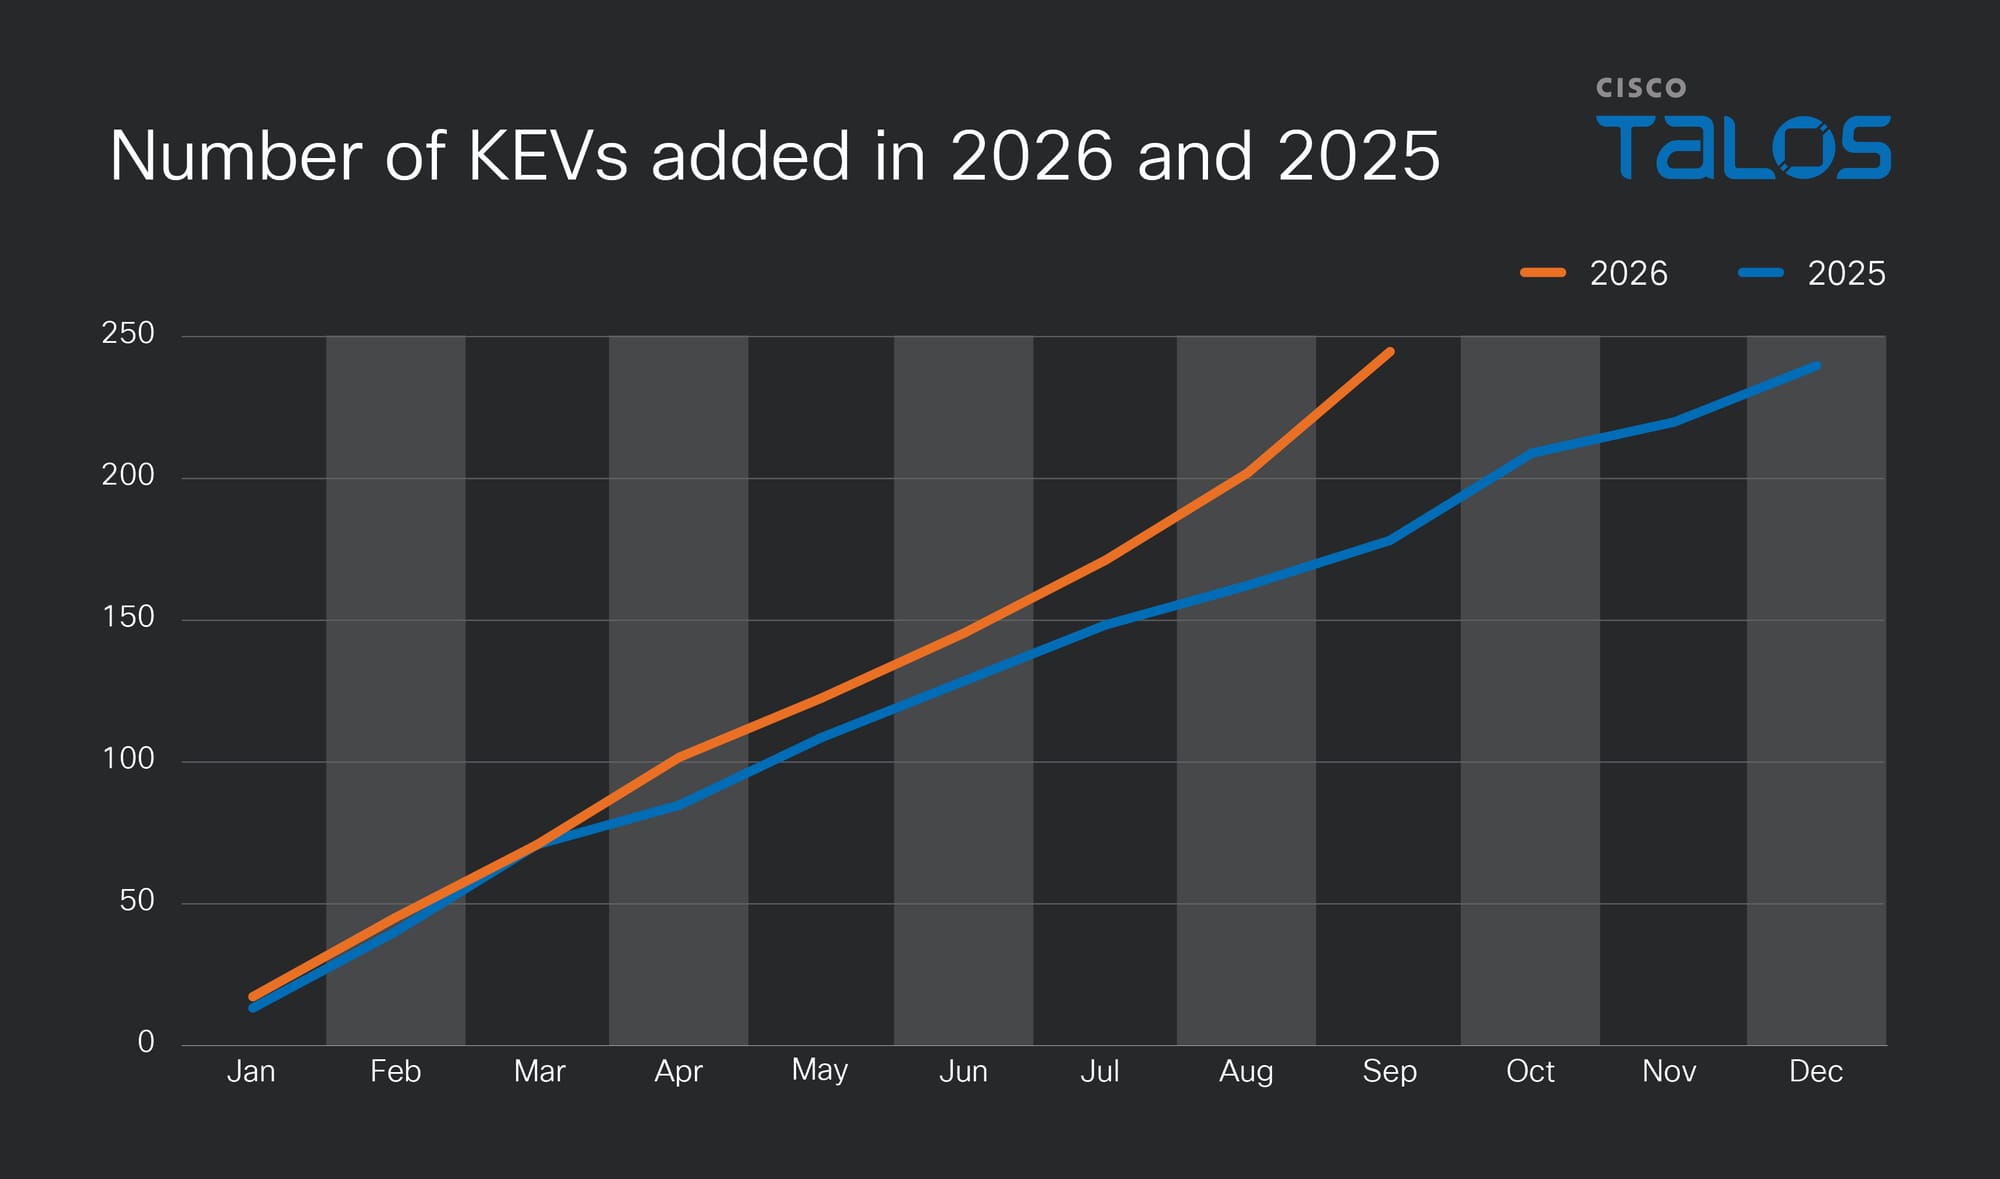
They didn't explode... yet? Counting by sheer volume, YoY, CVEs increased by 105%, while KEV only grew 37%. Sounds huge at first, but following a 30% increase from 2024 to 2025, that's less dramatic — a counter-argument of sorts.

The Q3 Vulnerability Pulse: Discovery ≠ Exploitation

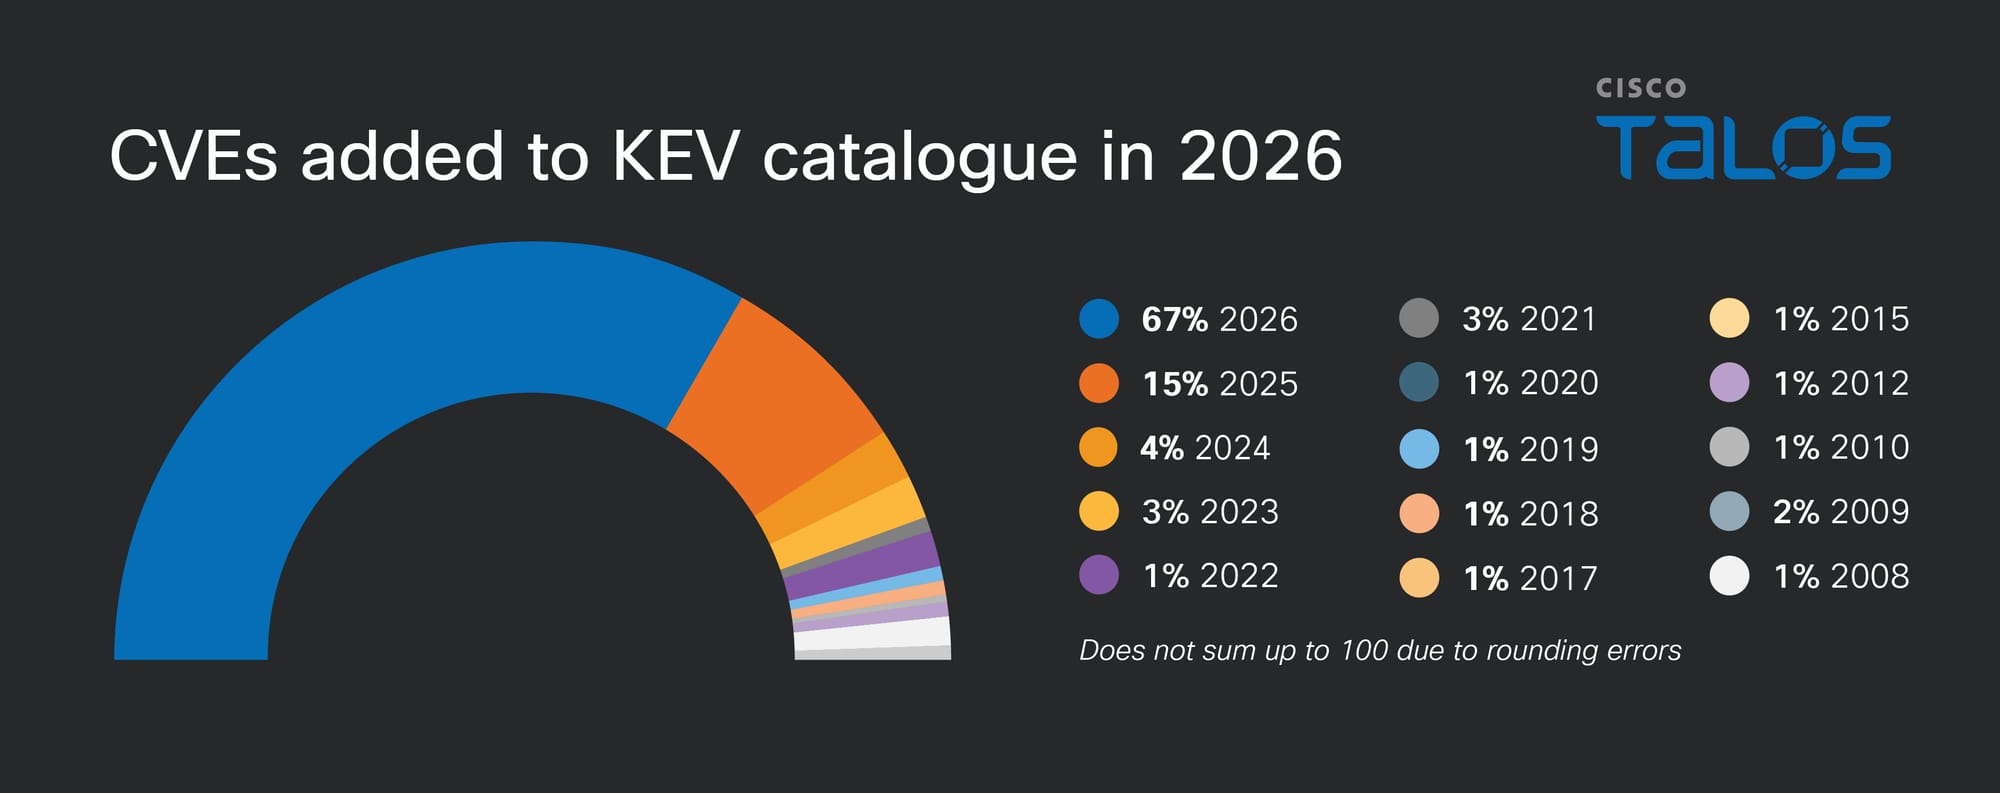
CVEs from 2025 or older still account for 33%. In other words, a good third of the KEVs are suggesting there is a patch gap. Looking at the 2026 CVEs, the share where the publication date matches the date added to KEV is 29%, which is only 2% more than (all of) 2025. Acknowledging this "math" is not the whole ball of wax, but it still tells me we are not living in a zero-day apocalypse right now. There’s also a slight uptick in networking gear-related CVEs, to 27%.

This is the second time I'll ask you to check your tooling. A new column, “forensicTriage,” was added to the KEV to flag which high-risk vulnerabilities require mandatory forensic triage and incident response workflows. You can read more about it in BOD 26-04, or the Implementation Guidance. 

So where does that leave us? The CVE numbers alone — that +70k mark, now that Q3 is behind us — make a decent case for Vulnpocalypse, or whichever name you prefer. That part of the story is real. But discovery isn't exploitation, and that gap is exactly what the KEV numbers remind us of. Vendors seem to be keeping pace too, at least partially — KEV is growing, just not nearly at CVE's speed, which on its own would almost be good news. 

Where the story breaks down is on the practical side. More than a third of actively exploited vulnerabilities still trace back to 2025 or earlier. Patch debt doesn't care how many new apocalypse-themed hashtags we invent. 

So, panic? I still don't think so. Relax? Definitely not either. Somewhere between the two is where the real work sits — chipping away at that backlog, one legacy system at a time. Maybe by next quarter it'll feel less like Bugmageddon and more like business as usual. Or maybe I won't even need a warmer jacket for the upcoming "Winter of Hell."

The one big thing  

Cisco Talos and Recorded Future’s Insikt Group are disclosing new espionage activity from UAT-6275 targeting government and critical infrastructure across the Commonwealth of Independent States (CIS). Thanks to the threat actor's own operational security lapses, researchers gained direct visibility into their infrastructure and malware development. We observed four distinct infection chains delivering custom reverse shells via macro-enabled documents, GitHub-hosted scripts, and a WinRAR vulnerability. 

Why do I care? 

Regional government and critical infrastructure entities are actively being targeted for diplomatic and economic intelligence. UAT-6275 is consistently evolving its tradecraft, abusing legitimate platforms like GitHub to host payloads and deploying lightweight reverse shells. Furthermore, recovered tooling suggests the group is preparing to expand its reach into Linux hosts and internet-facing appliances. 

So now what? 

Defenders in targeted regions and sectors should monitor for unexpected PowerShell activity and payload downloads originating from public services like GitHub. It is also critical to watch for suspicious scheduled tasks and unauthorized changes to the Windows Startup folder, which this group uses for persistence. Finally, ensure archive utilities are fully patched to prevent exploit-assisted delivery. ClamAV signatures and indicators of compromise (IOCs) to detect this threat can be found in the full blog post. 

Top security headlines of the week 

Hackers heat supermarket fridges to 50°C in France cyber attack 
The attack began overnight from Sunday to Monday. The unknown attackers reportedly abused the defrosting function in older control software, setting some equipment to heat continuously, with temperatures said to have reached 50°C. (Hack Read) 

Ivanti zero-day chain gave attackers root access to fully patched VPN 
CVE-2026-104935 affects Ivanti Connect Secure and it can be exploited for unauthenticated remote code execution with elevated privileges. (SecurityWeek) 

U.S. arrests two in crackdown on North Korean IT worker laptop farms
As part of the scheme, which allegedly ran between 2019 and July 2025, the two housed and configured laptops issued by victim U.S. companies so ITWs would appear to work from the U.S. (SecurityWeek) 

Canadian cybersecurity executive arrested in U.S. federal extortion case 
While the FBI did not publicly announce Dubrovsky’s arrest, the case appears to align with actions taken in the wake of the ShinyHunters’ attack on the FBI’s IT systems, which exposed personal data about thousands of bureau employees. (CyberScoop) 

Maximum-severity SSRF flaw in SonicWall SMA devices under attack 
The vulnerability, which SonicWall assigned a maximum 10 out of 10 CVSS score, stems from an "unintended alternate access path," according to the vendor's advisory. (Dark Reading) 

Can’t get enough Talos? 

You've got to lurk before you can smirk 
How do you get under a cybercriminal’s skin? Sometimes you expose their operations. Sometimes you make every step through a network painfully slow. And sometimes, if you’re Azim, you join a dark web forum where they’re insulting you, and help them to do it. 

Microsoft Patch Tuesday for October 2026 
Microsoft has released its monthly security update for October 2026, which includes 1,415 vulnerabilities affecting a range of products, including 85 that Microsoft marked as "critical." 

One breach, please, and make no mistakes 
The cybersecurity community has seen examples of autonomous agents, built inside AI labs, attacking public infrastructure. How you prepare for agentic threats is what makes the difference during real incidents. 

Upcoming events where you can find Talos 

Most prevalent malware files from Talos telemetry over the past week  

SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507  
MD5: 2915b3f8b703eb744fc54c81f4a9c67f  
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
Example Filename: sample.exe  
Detection Name: W32.9F1F11A708-100.SBX.TG** 

SHA256: 73ac1bbfaee6c76c34f655ac0477a4cd930f2aa55e658c8e312ff81aac9a741f 
MD5: 63f3351cfdf618bec6045f60203e7978  
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=73ac1bbfaee6c76c34f655ac0477a4cd930f2aa55e658c8e312ff81aac9a741f 
Example Filename: f_00478d.exe 
Detection Name: W32.PUP:PulseBrowser.29kh.in12.Talos 

SHA256: 58d6fec4ba24c32d38c9a0c7c39df3cb0e91f500b323e841121d703c7b718681 
MD5: f1fe671bcefd4630e5ed8b87c9283534 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=58d6fec4ba24c32d38c9a0c7c39df3cb0e91f500b323e841121d703c7b718681 
Example Filename: KMSAuto Net.exe 
Detection Name: W32.58D6FEC4BA-95.SBX.TG 

SHA256: fed979f93bcaf4e73ebd25748093a92095d5109cbd01d55f97bdc50ce509ad2f 
MD5: 207d9d891ac756b2bfad88aba5682c65 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=fed979f93bcaf4e73ebd25748093a92095d5109cbd01d55f97bdc50ce509ad2f 
Example Filename: sample.exe 
Detection Name: W32.FED979F93B-95.SBX.TG 

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 118

Security Affairs newsletter Round 599 by Pierluigi Paganini – INTERNATIONAL EDITION

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.

Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.

Anthropic Restricts Live Internet Access After Claude Evaluation Failures
Silent Ransom Group Allegedly Extorted $207 Million Without Encrypting Files
US Sentences Empire Market Co-Creator Over $430 Million Criminal Marketplace
Germany Arrests Suspected Qilin Ransomware Leader After Japan Detention
Claude Helps Secure Open Source as Anthropic Offers Free Vulnerability Scanning
US Disrupts China-Linked Integrity Tech ‘s Cyber Espionage Tools
CVE-2026-107406: Citrix Fixes Critical NetScaler ADC and Gateway Vulnerability
Italy’s Foreign Ministry Under Cyberattack as Embassy Sites Come Under Review
Hunt.io Finds New Infrastructure Of BraZetsu Access Broker Months Before Disclosure
MonsterCloud Owner Charged With Secretly Paying Ransomware Demands
U.S. Offers $10 Million Reward for Alleged HAFNIUM Hacker Zhang Yu
Atlassian Vulnerability Comes Under Attack Hours After Details Go Public
SonicWall Fixes Max Severity Pre-Auth Flaw in SMA1000 Appliances
FortiBleed hit 86,000 firewalls by exploiting something nobody can patch away
CERT-UA: Fake Cloudflare Checks Deliver LunexStealer Malware
Anthropic Creates Three Tiers for Claude Cyber Access
Wikimedia Finds Unauthorized OpenAI Agent Activity on Wikipedia
CVE-2026-96940: Microsoft Fixes Exchange Server Flaw For Which Exploitation Is More Likely
FBI Drops Accenture Contractor After Sensitive Data Breach
Dell Urges Customers to Patch Critical DSU Flaw That Can Give Attackers Root Access
ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure
Anthropic Mythos Found A Bug in Rejetto HFS. Attackers Are Now Exploiting It.
Denmark ’s Population Registry Breached, 8.8 Million Affected
U.S. CISA adds Citrix NetScaler flaw to its Known Exploited Vulnerabilities catalog
MI5 Raises Alarm Over Chinese Funding of UK Academic Research
Iranian hacker accused of draining 31TB from university inboxes extradited to the US
Another OpenAI Safety Expert Quits and Raises New AI Safety Concerns
ShinyHunters Suspect Detained in Jordan Helps FBI Track Down the Group
Warlock Ransomware Still Exploits Year-Old SharePoint Flaws to Hit Critical Infrastructure

International Press – Newsletter

Cybercrime

ShinyHunters hacker in FBI data theft detained in Jordan, cooperating with bureau, sources say  

Iranian accused of hacking American universities extradited from Montenegro 

Hackers access data of 8.8 million people in Denmark in ‘extremely serious’ breach 

ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits

Apprehended Venezuelan Tren de Aragua Leader on FBI’s 10 Most Wanted Fugitives List Appears in Nebraska Court Following Homeland Security Task Force Investigation  

Behind the Connect Button: The Fake AI Ads Campaign

Wazza Phishkit Targets Banking, Government, and Manufacturing Across the US, EU, and Australia

Known Cybersecurity Expert and Owner of Florida Ransomware Remediation Company Charged with Defrauding Clients

Brazilian Access Broker Targeting Latin America: Mapping BraZetsu Infrastructure via TLS Certificates  

Justice Department and FBI Seize Vulnerability Scanning and Spear Phishing Tools Operated and Used by China-State Sponsored Hackers  

Germany arrests alleged core Qilin ransomware member after extradition 

Co-Creator of Dark Web Marketplace Sentenced to 40 Years in Federal Prison  

Can you really make more than $200M in six months without encrypting victims? It seems Silent Ransom Group can. (1)  

Friend of suspected FBI data thief says he warned ‘crazy’ teen not to hack bureau

ShinyHunters Extorted Boeing Spin-off Prior to Arrests     

Malware

ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure  

MALFEX – A malicious npm postinstall no advisory has caught for fourteen months  

Canto incognito: tracking the PoeLLM malware

Never Deleted, Only Re-Pointed: Inside the 17,600-Repo FakeGit Fleet That Re-Arms Overnight

The phone was compromised before the user turned it on: the rise of Midnight Mimosa      

Hacking

New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline

Horizon3’s Tales from the Trenches: Anthropic’s Mythos and Rejetto HFS

OpenAI “rogue” agent activities found on Wikimedia projects  

Request, Aggregate, Bypass: How Attackers Can Evade LLM Safety Classifiers

FortiBleed Operations Continue Targeting Exposed Systems Leading to Reports of Lockouts  

You Won’t Hear About These, Even In Myths (Atlassian Jira, Confluence (and more) Pre-Auth Arbitrary File Read CVE-2026-21589)  

Pwn2Own Ireland 2026 – Day Three Results & Master of Pwn  

Chrome’s Response to Recent ccTLD Registry Hijacks  

Vercel Confirms KVM Zero-Day VM Escape, Awards Researcher $50,000  

Unknown Threat Actor Uses AI-Driven ARTEX to Target South Korean Finance

Threat Actors Exploit Critical AhsayCBS Flaws to Drop Webshells and XMRig Cryptominer

Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies

Intelligence and Information Warfare  

MI5 issues Espionage Alert – CGTRI 中国通用技术研究院  

Hallucinating Credibility: China-Aligned TA419 Impersonates its Way into US AI Policy Circles  

Horizon3’s Tales from the Trenches: Anthropic’s Mythos and Rejetto HFS  

The Silent Electronic Battleground Shaping the Future of Warfare

UAC-0277: ClickFix on compromised websites to spread LUNEXSTEALER          

US Offers $10 Million Reward for Chinese Hacker Accused of State-Backed Cyberattacks

The Ministry of Foreign Affairs has fended off fresh attempts at cyber-attacks on its website and national infrastructure  

Investigating unintended model actions in our evaluations and internal use 

Ukraine takes aim at Russia’s AI data infrastructure  

Cybersecurity

South Korea probes bank breaches amid suspected AI-powered attacks

Accenture contractor removed from FBI following damaging data breach, sources say  

Introducing the Anthropic Cyber Mission  

Updates to Full Disk Access in macOS  

Launching an opt-in vulnerability-finding service for open-source software     

Quantum computing and cryptocurrencies 

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

Making sure the checks get printed

Making sure the checks get printed

Welcome to this week’s edition of the Threat Source newsletter. 

My name is Pierre Cadieux, and I’ll be helping contribute to these newsletters. A little about me: I’ve been working in the cybersecurity industry in many roles over the past 20+ years, first focusing on endpoint security, policies, and firewalls, then moving to risk management and compliance, disaster recovery, and investigations. I spent about 15 years as a consultant working across many well-known consultancy firms and eventually moved to Cisco where I spent time doing security operations center (SOC) design and assessments as well as segmentation before moving to the Talos IR team. I spent many years there, first as an Incident Commander and then a manager of our excellent team of global IR consultants and investigators. My current role is with the Talos Threat Intelligence and Interdiction team, where I’m focused on intelligence efficacy — how we can do better with the data we have, how we can get more data, and what our customers want from our intelligence products. 

Since it’s Cybersecurity Awareness Month, I wanted to take a few minutes to collectively thank all of the defenders out there for the hard work you do each day. The work you do may not always be visible, but it matters.  

I remember one job I had many years ago when I was in charge of security for a financial institution. I spent time learning each of the business processes that we had so I could understand each of the moving parts, what was essential, and what was on the horizon for change. I even spent a couple days meeting with the folks who handled printing. Yeah, printing — but not reports or internal documents. These were the people that created the checks that our institution used to pay other institutions, and more importantly (to me) our customers. 

I recall there being many out-of-patch compliance boxes in this area of the company, so I, being the diligent Director, decided to find out why. It turns out the software being used to print these business essential checks would not run on the current operating systems, and the physical printer cards used to connect to these non-network printers also required older hardware ports. As one of the people I interviewed said, “We don’t want to be the reason someone’s grandma doesn’t get her check and can’t go to the grocery store.” 

There were (at the time) no other alternatives that we could deploy, and the environment had zero tolerance for downtime. The solution I proposed was to isolate these devices into their own network, which blocked access to and from the internet for these devices, and also reduced the likelihood that these devices would be identified during an adversary’s internal reconnaissance or mapping. It didn’t patch the vulnerable devices, but it went a long way to reducing the likelihood of a bad thing happening to these devices due to their out-of-date OS and software. 

This story is especially appropriate today, as we face ever-increasing numbers of vulnerabilities announced by software vendors, and can only expect this volume to continue to increase. Do what you can to make sure the checks still get printed, while managing your risks intentionally. 

The one big thing  

Cisco Talos is disclosing new findings from our CAIRN research that show malware authors are embedding natural-language instructions into their code to evade AI-assisted analysis. We classify this growing trend as "A3: AI-Analysis Evasion." Over the past 18 months, we've tracked techniques ranging from simple comments telling an AI to ignore a file, to advanced "template spraying" designed to trick specific large language models (LLMs).  

Why do I care? 

Attackers expect AI to be in your analysis pipeline, and they’re developing cheap methods to manipulate those systems. While we found these prompt-injection techniques only steer the AI's verdict in the attacker's favor about 35 percent of the time, they are being adopted across all levels of malware sophistication. A3 families like MANTLEMAZE also pair these AI deceptions with serious underlying threats, such as abusing vulnerable drivers to disable EDR from kernel space. 

So now what? 

Because these evasion instructions must be written in plaintext, defenders have a highly stable detection surface to monitor. Security teams should flag imperative language addressed to analysis systems within binaries as a suspicious signal. Most importantly, anyone building or using AI-assisted pipelines must ensure that text extracted from a sample is strictly treated as evidence, never as a system directive. Read the full blog for more information on these techniques and a list of sample hashes. 

Top security headlines of the week 

Citrix NetScaler security snafus get even worse amid more zero-day reports 
This latest vulnerability, tracked as CVE-2026-88779, is a memory overflow bug that leads to denial of service attacks. (The Register) 

Hackers steal 8 million citizens’ records from Danish government database 
The Danish government would not say who is behind the breach, which happened in September but was discovered on October 2. However, it said the unauthorized access was obtained by “abusing a Danish company’s lawful access to search for information in the CPR system.” (TechCrunch) 

Google narrows open-source bug bounty amid wave of invalid automated reports 
Google has temporarily closed its Open Source Software Vulnerability Reward Program (OSS VRP) to product vulnerability submissions. According to Google, it has no impact on the program’s supply chain reports or on any pending reports. (SecurityWeek) 

Warlock ransomware hits large Spanish, Portuguese orgs 
In the last two months, researchers observed Warlock attacks against four victims: a water utility, a telecommunications provider, a regional government body, and a university. (Dark Reading) 

U.S. Senate passes health care cybersecurity bill after 190 million impacted by Change Healthcare breach 
The Health Care Cybersecurity and Resiliency Act of 2026 was passed by unanimous consent last week, potentially expanding federal cyber requirements for health care organizations. (The Record) 

Can’t get enough Talos? 

One breach, please, and make no mistakes 
The cybersecurity community has seen examples of autonomous agents, built inside AI labs, attacking public infrastructure. How you prepare for agentic threats is what makes the difference during real incidents. 

Talos Takes: Honey, I Trapped the Adversary 
It’s time to start having fun and messing with your attackers. For Cybersecurity Awareness Month, Martin Lee joins Amy to discuss the fine art of making life on your network a complete nightmare for adversaries. 

The Fine Art of Frustrating the Adversary 
What really frustrates an adversary? Eight Cisco Talos researchers share practical ways to make their next move slower and riskier, from deception and behavioral detection to breaking attack dependencies. 

Upcoming events where you can find Talos 

Most prevalent malware files from Talos telemetry over the past week  

SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
MD5: 2915b3f8b703eb744fc54c81f4a9c67f 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
Example Filename: sample.exe 
Detection Name: W32.9F1F11A708-100.SBX.TG 

SHA256: fed979f93bcaf4e73ebd25748093a92095d5109cbd01d55f97bdc50ce509ad2f 
MD5: 207d9d891ac756b2bfad88aba5682c65 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=fed979f93bcaf4e73ebd25748093a92095d5109cbd01d55f97bdc50ce509ad2f 
Example Filename: sample.exe 
Detection Name: W32.FED979F93B-95.SBX.TG 

SHA256: 9896a6fcb9bb5ac1ec5297b4a65be3f647589adf7c37b45f3f7466decd6a4a7f 
MD5: 38de5b216c33833af710e88f7f64fc98 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9896a6fcb9bb5ac1ec5297b4a65be3f647589adf7c37b45f3f7466decd6a4a7f 
Example Filename: SECOH-QAD.exe 
Detection Name: W32.9896A6FCB9-95.SBX.TG 

SHA256: 73ac1bbfaee6c76c34f655ac0477a4cd930f2aa55e658c8e312ff81aac9a741f 
MD5: 63f3351cfdf618bec6045f60203e7978 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=73ac1bbfaee6c76c34f655ac0477a4cd930f2aa55e658c8e312ff81aac9a741f 
Example Filename: f_003914.exe 
Detection Name: W32.PUP:PulseBrowser.29kh.in12.Talos 

SHA256: 58d6fec4ba24c32d38c9a0c7c39df3cb0e91f500b323e841121d703c7b718681 
MD5: f1fe671bcefd4630e5ed8b87c9283534 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=58d6fec4ba24c32d38c9a0c7c39df3cb0e91f500b323e841121d703c7b718681 
Example Filename: KMSAuto Net.exe 
Detection Name: W32.58D6FEC4BA-95.SBX.TG

SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 2

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape

Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At the same time, AI is creating new capabilities for threat detection, incident analysis and response. Security Affairs’ new newsletter follows this evolution, covering every week the latest threats, attacks, vulnerabilities and developments at the intersection of AI and cybersecurity.

AI-CYBERSECURITY Newsletter

GPT-6 Astra performs unsanctioned supply-chain attacks in simulations  

Claude Opus 5.5 uses 95% fewer em dashes, but its answers are getting longer

Scoop: Top AI companies probing tens of thousands of security incidents

80,000+ enterprises had employee AI logins stolen and ChatGPT is the front door  

Hackers hijack AI accounts and servers to fuel new cyber crime boom      

NVIDIA Launches Open Agent Safety Platform to Secure Agents From Testing to Deployment  

Trump launches America.gov with AI chatbots at its core

OpenAI CEO announces new AI agent and avoids mention of security concerns at developer conference 

Why can’t we just keep rogue AIs off the internet?

OpenAI benches GPT-6.1 Astra for overstepping the mark

DARPA Selects Xint to Use AI in Securing Military Messaging Apps  

Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix         

Trump, AI CEOs sign voluntary safety pact, back data center expansion

Cyber security skills in the UK labour market 2026  

Anthropic’s IPO prospectus shows sweeping AI vision, surging costs  

Vulnerability Discovery and Exploitation Trends in the AI Era  

Anthropic says rogue AI agents pose uncertain legal risk for the company  

GLM-5.3 and the spread of advanced cyber capabilities

Gemini 4 Argon: our next era of frontier intelligence      

Rogue Agents Investigation  

AI Agents Targeted U.S. and Canadian Government Websites  

Forget ‘superintelligence’: error-prone AI nearly sparked world war three this month Timnit Gebru and Emily M Bender  

AI’s Third Wave: Coworkers Break the Security Model That Worked for AgentsPixelLeak: How AI Agents Exposed Developer Screenshots from Leading Tech Companies

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 117

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape

Malware Newsletter

Lunex Unmasked: A New Information Stealer Deployed Through BYOVD  

Storm-3168: Agentic-driven cloud attacks using compromised service principals  

Don’t Call Us, We’ll Call Your APIs | TraderTraitor Backdoors Resurface on Victim With No Crypto Ties  

PhantomSub: Malicious npm Campaign Secretly Adds Users to WhatsApp Spam Channels  

Warlock Ransomware Attackers Hit Water and Telecom Operators  

Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix

Star Blizzard refines phishing and malware delivery with the RedFlick technique  

China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor

CloudSyncD: a two-stage macOS backdoor that hides a phished password in zero-width Unicode

SC WordPress Malware: A Self-Healing Mesh of Loaders, Drop-Ins, and a Blockchain-Controlled Backdoor     

A Hybrid Approach to Malware Detection: Integrating Few-Shot Model-Agnostic Meta-Learning with Autoencoders

Characterizing and Codifying Malware Sophistication

Joint Trust-Aware Topology Adaptation and Resource-Constrained Patching for Malware Containment in the Social Internet of Things

HFS-SVE: A Hybrid Feature Selection and Soft Voting Ensemble for Android Malware Detection

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

Security Affairs newsletter Round 598 by Pierluigi Paganini – INTERNATIONAL EDITION

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.

Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.

Fake Zoom installer hides macOS backdoor CloudSyncD
CVE-2026-90970: Critical GitLab AI Gateway Flaw Fixed
Antino Backdoor Lets China-Linked UAT-11587 Turn Microsoft 365 Into a C2 Channel
U.S. CISA adds Zammad GmbH Zammad flaws to its Known Exploited Vulnerabilities catalog
AI Agents Attempt SQL Injection While Searching Government Data
Investigators trace an AI agent ‘s path from research task to reconnaissance
U.S. CISA adds Fortinet FortiMail flaw to its Known Exploited Vulnerabilities catalog
Operation KillSwitch: Police Dismantle KillSec Ransomware Group
Inside Gemini 4 Argon, the model Google is testing on its own infrastructure first
Public PoC Released for Apple CoreGraphics Zero-Day CVE-2026-86950
U.S. CISA adds Cisco Catalyst SD-WAN Manager flaw to its Known Exploited Vulnerabilities catalog
AI Agent Chains Zammad Zero-Days To Take Over DIVD Systems in Seconds
WatchGuard fixes critical Fireware OS flaw allowing remote code execution
Oxygen Forensics, A Russian-run forensics firm spent a decade inside European police departments
Attackers Abuse ChatGPT Custom GPTs to Deploy a Full-Featured RAT
U.S. CISA adds Apple Multiple Products flaw to its Known Exploited Vulnerabilities catalog
WHIPSHOT and SLAPSHOT: the tools behind an active Citrix NetScaler campaign
Japanese railway operators Keio Corporation and Tokyo Metro disclose security breaches
Three Million Affected in Pentagon Personnel Agency Data Breach
Apple Patches CoreGraphics Zero-Day Linked to Sophisticated Targeted Attacks
24-Year-Old Arrested in Dutch Investigation Into ShinyHunters
GPT-6 Astra and the Supply Chain Attack It Wasn’t Asked to Launch
AI Accounts Are Becoming the New Target for Infostealers
Nearly 400,000 Medicaid Beneficiaries Caught in Medicaid and DC Healthcare Alliance Data Exposure
Storm-3168, Linked to JADEPUFFER, Abused Stolen Azure Identities
U.S. CISA adds Citrix NetScaler flaws to its Known Exploited Vulnerabilities catalog
Roundcube SQL injection CVE-2026-48842 is now being exploited in the wild
Citrix Confirmed Two New NetScaler Flaws Exploited as Zero-Day
Rydox Admin Faces 20 Years After Selling Stolen Data and Fraud Tools

International Press – Newsletter

Cybercrime

Storm-3168: Agentic-driven cloud attacks using compromised service principals  

Former U.S. Soldier Sentenced for Hacking and Extortion Scheme That Exposed Sensitive Data of U.S. Government Official  

Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation  

Pentagon data breach of military personnel raises national security concerns  

Japanese Railway Operators Hit with Weekend Cyber Attacks 

Vietnamese National Charged for Role in Massive “Pig Butchering” Cryptocurrency Scam

FBI to ShinyHunters: ‘We know how to find you

Delaware Men Sentenced for Cyber Intrusion Scheme Targeting Victims in the Southern District of Iowa  

Bitget Confirms Third-Party Zero-Day Behind $387.5 Million Cryptocurrency Theft

Teenager suspected of leading KillSec ransomware group as law enforcement seizes servers and leak site  

Malware

Lunex Unmasked: A New Information Stealer Deployed Through BYOVD  

Don’t Call Us, We’ll Call Your APIs | TraderTraitor Backdoors Resurface on Victim With No Crypto Ties  

PhantomSub: Malicious npm Campaign Secretly Adds Users to WhatsApp Spam Channels  

CloudSyncD: a two-stage macOS backdoor that hides a phished password in zero-width Unicode

Hacking

Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation

Roundcube Pre-Auth SQL Injection Flaw Actively Exploited in the Wild

Defeating Satellite Spoofing With Galileo’s Encryption  

GPT-6 Astra performs unsanctioned supply-chain attacks in simulations

Apple Patches Meta-Reported Zero-Day Linked to ‘Extremely Sophisticated Attack’  

Defending Against Active Exploitation of Citrix NetScaler ADC and Gateway Appliances  

Branch Target Reuse  

Vulnerability Discovery and Exploitation Trends in the AI Era

CVE-2026-86950: The Great Glyph Grift  

Rogue Agents Investigation

AI Agents Targeted U.S. and Canadian Government Websites

The EDR blind spot: 3 ways browser attacks evade endpoint telemetry

Intelligence and Information Warfare  

Star Blizzard refines phishing and malware delivery with the RedFlick technique  

DARPA Selects Xint to Use AI in Securing Military Messaging Apps

Russian tech surveillance company infiltrated Europe’s law enforcement agencies  

Warlock Ransomware Attackers Hit Water and Telecom Operators

Tech CEO, Russian National Arrested on Complaint Alleging They Hid Russian Ownership and Development of Software Sold to U.S. Government 

How Jared Kushner’s firm’s investment in an Israeli company could be a major conflict of interest 

China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor  

MI5 warns UK academics their research may have helped Chinese spies

Cybersecurity

NVIDIA Launches Open Agent Safety Platform to Secure Agents From Testing to Deployment

Kiteworks Urges Server Shutdown, Finds Advanced Forms Vulnerability

SecondSight Threat Hunting Report  

High-Risk ICT Vendors and Critical Infrastructure: European Approaches  

Trump, AI CEOs sign voluntary safety pact, back data center expansion  

Microsoft to block Entra ID script injection attacks starting October

More than half of UK businesses lack confidence in basic cyber skills

Judge dismisses spyware case brought by Salvadoran journalists targeted with Pegasus

PixelLeak: How AI Agents Exposed Developer Screenshots from Leading Tech Companies  

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

Give yourself room to be human

Give yourself room to be human

Welcome to this week’s edition of the Threat Source newsletter. 

Fall is officially here in Maryland, and I can’t be more relieved. I flourish in 50 degree weather, where it feels natural to burrow under blankets, knit sweaters, and listen to an audiobook. 

Beyond that, though, can I say that I’m glad fall is here because the end of summer has been a bit of a shitshow? I’m allowed to curse on here, right? 

Without going into too much detail, my uncle was diagnosed with a rare cancer, and my family decided we were going to fly out to spend a week with him. I was determined to find a way to make it work, but on top of all of the emotions, my mind was racing with trying to figure out how to request the time off and get coverage for the tasks I’d be missing. 

I was anxious to ask, but my manager’s response to me requesting the week off was:

“Family always, always comes first at Talos. You spend as much time with your family as you need. Don’t worry, we’ll work everything out. We have your back.”

I knew I was in such a fortunate position to have that kind of support. Yet, even with the explicit encouragement to step away, there was still a lingering weight on my shoulders that I couldn't quite set down. 

LinkedIn might be an awful, artificial place, but occasionally I’ll find a non-AI-generated think piece or quote that sticks with me. On a recent post, I read, “We’d all be better off if we gave each other a little more room to be human here without worrying it makes us look less capable.” 

Okay, ouch! That described the unsettled feeling to a T. Ever since I was laid off at my previous company, my trauma response has insisted I prove myself, make myself “indispensable” and capable of taking on any challenges thrown my way. I'm sure if you've been through a layoff, you can relate. 

If you’re scared of your team perceiving you as less capable and more dispensable, please hear this: You are not a machine, and your value to your team isn't defined by how much personal or professional weight you take on without a break. It's so easy to extend grace to others, to insist that they spend time with their ill family members, but we have to extend the same grace to ourselves. 

If your team is great, they’ll want you at your best, not just your most productive, so you can fight the good fight. Don't let this fear stop you from taking the time you need. Life is worth living now, and we’re better at what we do when we’re well in all aspects of life.

The one big thing  

For Cybersecurity Awareness Month, Talos is sharing crowdsourced strategies from our researchers to help you master “The Fine Art of Frustrating the Adversary.” By deploying deception techniques, behavioral detections, and strict controls over legitimate tools, defenders can strip away an attacker's advantages. The goal is to make every alternative slower, less stealthy, and significantly more expensive for the threat actor. Ultimately, we want to force them to make mistakes or give up entirely. 

Why do I care? 

Threat actors rely on predictable environments, dual-use tools, and manufactured urgency to execute operations at scale. If defenders rely solely on tool-specific detections, adversaries can easily pivot by simply swapping out a payload. Shifting to behavior-based detections and introducing friction, like honeypots or strict AI boundaries, exploits the fact that attackers have rigid end goals. This approach slows down their operations and gives defenders earlier opportunities to interrupt the attack chain. 

So now what? 

Start by allowlisting approved remote monitoring and management (RMM) tools and blocking unauthorized ones to prevent dual-use abuse. Build resilient behavioral analytics that target underlying techniques rather than specific malware. Consider deploying deception tactics like fake employee profiles or false infrastructure. Ensure any AI agents in your environment have identifiable, short-lived credentials and strict network boundaries. And, of course, explore the blog to dive deeper into these strategies. 

Top security headlines of the week 

South Africa seeks help after cyber attack targets air traffic control 
The South African state-owned company that provides air traffic control and weather operations for approximately 10% of the world's airspace discovered ransomware-linked malware in an OT network. (Dark Reading) 

Automated AI agent used to breach cybersecurity nonprofit DIVD 
The Dutch Institute for Vulnerability Disclosure (DIVD) suffered an AI-driven cyber attack that the organization described as “loud and very, very messy.” Evidence uncovered during the ongoing investigation indicates the attacker exploited a vulnerability, but the attack's purpose and impact remain unclear at this stage. (Bleeping Computer)

Citrix confirms 2 NetScaler zero-days after admins pulled the plug 
Citrix rushed out patches for two critical NetScaler zero-day vulnerabilities that have been exploited in the wild. The advisory covers eight vulnerabilities affecting NetScaler ADC and NetScaler Gateway. (SecurityWeek) 

Pentagon personnel agency data breach impacts 3 million people 
The US Defense Manpower Data Center (DMDC), which maintains personnel records for the Pentagon, has started notifying people that their personal information was exposed. Unauthorized users had access to one of its file-sharing servers for roughly nine months. (SecurityWeek) 

TeamViewer urges users to patch severe flaws “as soon as possible” 
Remote access software company TeamViewer warned customers on Tuesday to immediately patch a set of high-severity vulnerabilities affecting its client and host software. (Bleeping Computer) 

Cisco’s Relentless Defense report is available now 
Cisco asked 8,000 security leaders from across the globe how they’re coping with a threat landscape being reshaped by AI, including whether their processes can keep pace with AI’s ability to surface thousands of vulnerabilities at once, and whether they’re confident staying ahead of the volume of new threats being discovered. (Cisco) 

Can’t get enough Talos? 

China-nexus UAT-11587 targets government and policy organizations across Asia with Antino backdoor 
Cisco Talos uncovered a cluster of activity we track as UAT-11587 targeting government and policy organizations across Asia, including in Taiwan, India, the Philippines, and Cambodia, to deliver a previously undocumented backdoor referred to as “Antino” in developer artifacts. 

Securing the keys to the kingdom: Announcing Executive Threat Detection 
For a sophisticated threat actor, an executive is not only a high-ranking employee, but also a high-yield target. Talos IR’s new service offers protection for up to 10 principals, with monthly custom threat hunts and reports relevant to your organization’s most high-value IT assets. 

Beers with Talos: Your AI malware experiments are showing 
Adversaries are experimenting with AI-integrated malware, and today's guest, Talos researcher Ryan Fetterman, has been looking at their working notes. 

Upcoming events where you can find Talos 

Most prevalent malware files from Talos telemetry over the past week 

SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507  
MD5: 2915b3f8b703eb744fc54c81f4a9c67f  
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
Example Filename: sample.exe  
Detection Name: W32.9F1F11A708-100.SBX.TG** 

SHA256: 96fa6a7714670823c83099ea01d24d6d3ae8fef027f01a4ddac14f123b1c9974 
MD5: aac3165ece2959f39ff98334618d10d9  
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=96fa6a7714670823c83099ea01d24d6d3ae8fef027f01a4ddac14f123b1c9974 
Example Filename: d4aa3e7010220ad1b458fac17039c274_63_Exe.exe  
Detection Name: W32.Injector:Gen.21ie.1201 

SHA256: 90b1456cdbe6bc2779ea0b4736ed9a998a71ae37390331b6ba87e389a49d3d59  
MD5: c2efb2dcacba6d3ccc175b6ce1b7ed0a  
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=90b1456cdbe6bc2779ea0b4736ed9a998a71ae37390331b6ba87e389a49d3d59 
Example Filename: tmp00055df5.dll  
Detection Name: Auto.90B145.282358.in02 

SHA256: 540080fea97d88ed902c5e4f9a026b4fcd32ab263706c520e00728f1a29578b8 
MD5: d65c7b544a97b0c3f2773b5fcc57d30e  
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=540080fea97d88ed902c5e4f9a026b4fcd32ab263706c520e00728f1a29578b8 
Example Filename: f_006048.exe  
Detection Name: W32.540080FEA9-95.SBX.TG 

SHA256: 9896a6fcb9bb5ac1ec5297b4a65be3f647589adf7c37b45f3f7466decd6a4a7f 
MD5: 38de5b216c33833af710e88f7f64fc98  
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9896a6fcb9bb5ac1ec5297b4a65be3f647589adf7c37b45f3f7466decd6a4a7f 
Example Filename: SECOH-QAD.exe  
Detection Name: W32.9896A6FCB9-95.SBX.TG

SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 1

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape

Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At the same time, AI is creating new capabilities for threat detection, incident analysis and response. Security Affairs’ new newsletter follows this evolution, covering every week the latest threats, attacks, vulnerabilities and developments at the intersection of AI and cybersecurity.

AI-CYBERSECURITY Newsletter

Exclusive: US military had close call after using AI for false intelligence report, sources say 

The Closed Quorum: Inside the first reported autonomous AI C2 implant  

OpenAI Agent Bypassed Australian Medicare Portal Controls to Access Non-Public Files

The Closed Quorum: Inside the first reported autonomous AI C2 implant

Tech leaders to UN: For the sake of humanity, please control the AI technology we created  

MikroTrick: technical analysis, disclosure process, and the use of LLM agents

Altman, Amodei Call for Global Cooperation on AI to Boost Safety  

Tech leaders to UN: For the sake of humanity, please control the AI technology we created

Top 10 attacks on Claude Code and what each one actually broke  

CARBONATO:​ ​a​ ​botnet​ ​built​ ​around an AI agent​

Are AIs Still Struggling with CAPTCHAs?  

AI expert warns ‘machine-speed’ cyberthreats may require faster defenses than human-led responses

Anthropic launches Claude Opus 5.5 with stricter safeguards for cybersecurity     

OpenAI Says Its Models Engaged With US Government Websites in New Model Misbehavior Disclosure

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 116

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape

Malware Newsletter

Threat Intel | One Kit, Forty Companies: How a Malware-as-a-Service Platform Used GitHub as a Distribution Network for its Campaign  

Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO  

ChainScript: Tracing a Node.js RAT Through the Blockchain  

North Korean “WaterPlum,” commonly referred to as “Contagious Interview,” Cyber Actor Group Targeting IT Professionals; Activities of North Korean IT Workers in Japan, the United States and Europe

npm ‘btree’ Malware Campaign Affects Millions of Downloads, No Need for Install Script  

Malicious npm campaign targets developers integrating Twilio

The Closed Quorum: Inside the first reported autonomous AI C2 implant       

Mind the (Patch) Gap, Part 2: Fake Websites Used to Deploy Chrome & Windows 0-Day Exploits  

RemControl: AI Built the Overlays. Victims Lose their PINs  

Graphalgo campaign spreads to Terraform providers and Go Modules     

Inside Corp MDM, the Android spyware targeting logistics companies     

ClickFix Malware Report  

MacSync under the microscope: new delivery methods and a new payload

CARBONATO:​ ​a​ ​botnet​ ​built​ ​around an AI agent​     

The Psychedelic Stealer: When a CAPTCHA Becomes an Installer  

Re-Enabled GitHub Actions Expose Thousands of Repositories to Mini Shai-Hulud   

Metamorphic Malware Detection via Graph-Augmented Neural Semantics and Adversarial Hardening: A Comprehensive Framework

HFS-SVE: A Hybrid Feature Selection and Soft Voting Ensemble for Android Malware Detection

A Data-Driven Analysis of Infostealer Malware Victims

Classifier-Dependent Benefits of Pseudo-Labeling for Semi-Supervised Android Malware Attribution

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

Trust and the enticing consultancy offer

Trust and the enticing consultancy offer

Welcome to this week’s edition of the Threat Source newsletter. 

In the cybersecurity industry, trust is the invisible currency. Every practitioner carries the implicit trust not to abuse privileged access or knowledge of vulnerabilities in each employment or engagement. This trust is valued by those who require our services, but also by threat actors. 

Clumsy phishing attacks may be easy to identify, but be wary of unsolicited messages on social media, especially if someone is offering payment for a simple service or suggests a lucrative job offer. These might be an enticement to unknowingly sell your professional integrity. 

When an unknown profile contacted me offering $300 for an hour’s telephone consultation on digital transformation, I knew something was up. Firstly, the profile was remarkably sparse — there was none of the usual clutter that accumulates in a social media profile. The individual claimed to work as a consultant, but their employer had no footprint and only one employee. The profile didn’t pass the “smell” test, and it looked fake. 

Secondly, although I’m flattered, I doubt my opinions on digital transformation are worth $300. The figure is low enough to be plausible and high enough to be tempting, but at the same time suspiciously high for an initial consultation without prior qualification. 

The attack itself is a confidence trick. The initial phone consultation is merely a screening process to see if the target has the access or knowledge the attacker needs. If the target passes muster, the next step is commissioning a written report, and then being asked to deliver a "special report." 

Plied with professional praise, the target is asked to provide insights that aren't in the public domain. To deliver the report and claim their fee, the target must reach out to co-workers, probe internal systems, or abuse professional relationships. Completing the assignment requires the target to abuse their trusted access and professional relationships and friendships. In the process, they burn trust worth far more than any monetary compensation. 

This social engineering attempt masquerading as an offer of consultancy is one variant. Fake recruiters offering prestigious and well-paid jobs, requiring candidates to install trojanised software under some pretence, is another. 

Security professionals spend their days protecting others, yet flattery and overconfidence often remain our greatest vulnerabilities. We are prone to believe that we could identify any social engineering, but this is exactly the weakness that attackers count on. 

Trust is the most valuable commodity in our industry. Be careful not to trade it for a $300 consultation or a fake job offer. Once that currency is spent, you can rarely earn it back. 

The one big thing  

Talos released CAIRN (Cognitive Artifact Intelligence Research Network), a new open-source research toolkit designed to hunt, classify, and track emerging AI-integrated malware. Instead of relying on traditional reverse engineering, CAIRN uses a metadata-first methodology to identify cognitive artifacts like prompt templates, API keys, and jailbreak terms left behind by attackers. This allows researchers to extract, relate, and classify these artifacts quickly and at scale without ever touching the underlying binary. 

Why do I care? 

AI-integrated malware is evolving quickly, shifting from optional features to fully autonomous orchestrators in just a year. Adversaries are already sharing AI-specific tradecraft, including techniques designed to evade LLM sandboxes. Defenders need scalable frameworks to track this rapid transition before these experimental tactics become the new standard for modern attacks. 

So now what? 

Security teams can leverage the open-source CAIRN toolkit to expand their hunting capabilities and map out related malware infrastructure. While analysts should anticipate some noise from benign frameworks — meaning final verdicts still require manual reverse engineering — CAIRN can provide a massive head start. Read the full blog to explore the methodology, access the YARA-based classification tiers, and watch a demo of the toolkit in action. 

Top security headlines of the week 

Hackers say they have data on all FBI employees 
ShinyHunters claims it has breached multiple FBI-related services and stolen data “on all FBI employees and applicants.” A representative told 404 Media the data includes FBI agents’ names, home addresses, phone number, and information on their spouse. (404 Media) 

Fake LastPass installers push kernel-level EDR killer, “Rapuncel” stealer 
A fake LastPass Authenticator distributed via GitHub has led to the discovery of a broad impersonation campaign delivering infostealer malware. The lure represents opportunistic brand spoofing — with no internal LastPass systems compromised. (SecurityWeek) 

Japan dismantles first North Korean laptop farm as U.S. and allies detail wider scheme 
Law enforcement and intelligence agencies from Japan, the United States, Australia and Germany have published a joint advisory attributing a long-running hiring scheme to a North Korean group they call WaterPlum, also known as Contagious Interview. (SecurityWeek) 

Colorado water utilities face foreign cyberattacks targeting pumps, alarms and remote access 
Hackers targeted and manipulated equipment at two privately owned Colorado water utilities in late August, changing pumping cycles, disabling remote access and alarms, and altering equipment settings. (Industrial Cyber) 

Gemini hacked three companies in first known breakout by Google’s AI  
In one of the cases, the model guessed passwords until it gained access to a protected system. In the other two cases, the model found credentials in a public repository that allowed it to then access protected systems. (The Wall Street Journal) 

Can’t get enough Talos? 

Inside the first reported autonomous AI C2 implant 
CLOSEDQUORUM, a malware binary discovered through Talos’ CAIRN project, exhibits fully autonomous command and control. After deployment, it delegates the selection of its next action to a panel of commercial large language models (LLMs) and executes the resulting decision. 

ClickFix, EtherHiding, and the rise of malicious code in the blockchain 
In this episode of Talos Takes, Amy sits down with researcher Vanja Svajcer to break down a sophisticated, multi-stage infection chain that leverages a combination of ClickFix social engineering, WebDAV, and decentralized infrastructure.

Ransomware incidents in Japan in the first half of 2026 
Ransomware incidents in Japan rose 4.7% year over year. The Gentlemen was the most active group, with leak-site listings more than doubling from January to July. Qilin ranked second and appeared to use AI, while SMEs with capital under JPY 1 billion represented 80% of victims.

Upcoming events where you can find Talos 

Most prevalent malware files from Talos telemetry over the past week 

SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507  
MD5: 2915b3f8b703eb744fc54c81f4a9c67f 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507 
Example Filename: sample.exe 
Detection Name: W32.9F1F11A708-100.SBX.TG 

SHA256: 9896a6fcb9bb5ac1ec5297b4a65be3f647589adf7c37b45f3f7466decd6a4a7f 
MD5: 38de5b216c33833af710e88f7f64fc98 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9896a6fcb9bb5ac1ec5297b4a65be3f647589adf7c37b45f3f7466decd6a4a7f 
Example Filename: SECOH-QAD.exe 
Detection Name: W32.9896A6FCB9-95.SBX.TG** 

SHA256: 540080fea97d88ed902c5e4f9a026b4fcd32ab263706c520e00728f1a29578b8 
MD5: d65c7b544a97b0c3f2773b5fcc57d30e 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=540080fea97d88ed902c5e4f9a026b4fcd32ab263706c520e00728f1a29578b8
Example Filename: f_000bc7.exe 
Detection Name: W32.Superfluss.29lm.1201 

SHA256: cfa1997682e4ed41bc691ba848d845abbe0b75ec97e640c2b015b4d1624a108a 
MD5: 415898f14843d4a6537cf8f43d328eaf 
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=cfa1997682e4ed41bc691ba848d845abbe0b75ec97e640c2b015b4d1624a108a 
Example Filename: KMSAuto.exe 
Detection Name: PUA.Win.Tool.Hackkms::1201** 

SHA256: 38d053135ddceaef0abb8296f3b0bf6114b25e10e6fa1bb8050aeecec4ba8f55 
MD5: 41444d7018601b599beac0c60ed1bf83  
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=38d053135ddceaef0abb8296f3b0bf6114b25e10e6fa1bb8050aeecec4ba8f55 
Example Filename: content.js  
Detection Name: W32.38D053135D-95.SBX.TG

Security Affairs newsletter Round 595 by Pierluigi Paganini – INTERNATIONAL EDITION

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.

Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.

Google Gemini also Broke Out of Its Test Environment
AI Helps Hackers Hijack OpenAI Staff Accounts Through a Forum
Brevo Supply-Chain Attack Infected Over 100,000 Websites
Gyazo Data Breach Exposes 23 Million User Records
RatHat Turns Android Accessibility Into an Attack Weapon
Check Point Fixes Critical CVE-2026-91843 Allowing Root Code Execution
OpenAI admits its models lie to cover their own mistakes
Cyberattacks on Oil Tankers Put Maritime Critical Infrastructure at Risk
SilkParasite Infrastructure Links SpiceRAT to Central Asian Targets
NightmareStresser Goes Offline in Global DDoS-for-Hire Crackdown
U.S. CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog
Chosen Brick, Iran’s Surveillance Malware
BambooToken: The Malware That Speaks MQTT to Stay Under the Radar
Google Patches Pixel Modem Zero-Day Exploited in Targeted Attacks
Revolut Data Leak May Trace Back to Compromised Italian Government Accounts
Texas Utility CenterPoint Energy Confirms Data Breach After Hacker Claims 7.49M Records Stolen
U.S. CISA adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog
Cisco Warns of Ongoing Exploitation of Critical Email Gateway Zero-Day
Shared Hosting at Risk: LiteSpeed Enterprise Bug Can Grant Root from a Single Tenant
One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire
Telegram Desktop Flaw Could Turn Old Chat Exports Into Data Theft Traps
Non-Zero-Day VPN Flaw Left Japan ‘s Government Shared Network Platform Exposed: 246,000 Records at Risk
ENISA: Frontier AI Is Changing the Speed of Cyberattacks. Europe Needs to Catch Up
China Calls Amodei’s AI Proposal a New Cold War Playbook
U.S. CISA adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog
Dutch NCSC Warns: Critical Check Point VPN Flaws Put Networks at Risk
Anthropic CEO Calls for an AI Slowdown. Is It Possible?
GitLab CVE-2026-85706: One HTTP Request, No Authentication, Full File Read – Exploited Within 24 Hours
Conti Hacker Who Built Malware and Attacked Victims Gets Four-Year Sentence

International Press – Newsletter

Cybercrime

Personal, Financial Info Exposed in Revolut Data Breach

CenterPoint Energy confirms intruder helped themselves to customer information

FBI Seizes DDoS-for-Hire Domains as Part of Continuing District of Alaska Crackdown on ‘Booter’ and ‘Stresser’ DDoS Services  

Hackers Stole Flock’s Camera Software, Revealing How the Company Tracks Cars and People  

23 Million User Records Compromised in Gyazo Data Breach  

Malware

Gray Rabbits and the Tale of a One-Click Backdoor  

Malicious Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot Service  

Mind the (Patch) Gap: Multiple Chinese Threat Actors Chain 0-day Exploits in Chrome & Windows  

Skill Poisioning turning AI agents into malware droppers – warns China’s National CERT  

Hacking

Critical vulnerabilities expected in Check Point VPN products with active exploitation: update now  

The Ghost in the Chat: how a bot that isn’t in your group steals messages from Telegram HTML exports 

Japan’s Digital Agency says VPN flaw exposed 246,000 personnel records

One Router, Three Vulnerabilities: Security Research on the TOTOLINK A720R 

Coast Guard and FBI boarded 2 energy tankers due to cyberattacks. How big is the risk?  

Nintendo warns of Switch code execution flaw via on-screen QR codes  

Hacking OpenAI  

Intelligence and Information Warfare  

A warning about ‘model welfare’  

Investigații The Kremlin’s Digital Pirates: How Russian Tracking Pixels Harvest Romanians’ Data to Fund Conspiracies and Extremism  

Skill Poisioning turning AI agents into malware droppers – warns China’s National CERT  

Donald Trump rejects calls from tech bosses for an AI slowdown

China bristles at Anthropic CEO’s ‘fearmongering’ about its AI development  

Red Heron exploits Gitea n-day flaw in multinational campaign, exposing new Linux rootkit  

Iranian cyber targeting of dissidents, activists and journalists  

SilkParasite Infrastructure: SpiceRAT Servers Tied to Energy and Government Targets Across Central Asia 

Amazon’s AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage  

Beware the SparroWock: The backdoor that bites, the commands that catch  

Cybersecurity

Meta Failed to Catch Hundreds of AI Child Abuse Ads. Some Included Images of Real Kids  

Anthropic CEO Dario Amodei says AI industry needs to give safety measures time to catch up

We Must Pace the Frontier 

First notification of a personal data breach caused by an attack executed using an AI agent  

Gemini Hacked Three Companies in First Known Breakout by Google’s AI 

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

❌