
Overnight, while shoppers slept, hundreds of French supermarkets were quietly cooking their own stock. In a French supermarket cyberattack confirmed by retailers on Monday, hackers took remote control of internet-connected refrigeration systems and pushed fridge and freezer temperatures as high as 50 degrees Celsius (122F). By morning, tonnes of food had perished, some equipment had melted, and in some stores the heat had sparked fires.
The
cyberattack did not rely on a new exploit. It targeted ageing connected devices that were still online years after their manufacturer stopped supporting them, a weakness experts say is common across retail and industry.
What Happened in the French Supermarket Cyberattack
The attackers struck when shops were closed, raising temperatures remotely through the refrigeration control systems. French TV channel BFM reported that they appeared to trigger a forced defrost option, keeping units heating instead of cooling.
Five of France's major retail groups were hit: E.Leclerc, Intermarché, Carrefour, Monoprix and Coopérative U. At least 300 Intermarché and Netto stores were affected. Coopérative U reported more than 100 stores, Carrefour said 80, and Monoprix said about 5 percent of its roughly 490 stores were targeted.
The full scale is still unclear. Some reports put the total above 500 shops. Bruce Hallas, CEO at Re-thinking the Human Factor, who lives in France,
noted on LinkedIn that current estimates sit around 400 stores, with some individual branches reporting losses of about €250,000. Retailers say millions of euros worth of food was spoiled.
Danfoss Refrigeration Controllers at the Center
France's government
cybersecurity agency, ANSSI, identified the targeted systems as Danfoss refrigeration controllers, including the AK-SM800 and AK-SC355 models. The
Danish manufacturer told AFP that most affected units were legacy products running outdated firmware, and that it had previously advised supermarkets to update them.
ANSSI has urged companies using the affected models to disconnect them from the
internet or restrict access, and to install software updates immediately. Authorities have opened an investigation and are liaising with other European countries that may have been affected. It remains unclear who carried out the attack.
The incident follows President Emmanuel Macron's order last month to protect France's critical infrastructure from Russian "hybrid attacks." Officials have not linked the supermarket attack to any group or country.
Exclusive: Why These Devices Were Left Exposed
In comments shared exclusively with The Cyber Express,
Neil Carter, Managing Director of CRAReady.co.uk, explained why systems like these remain vulnerable for so long.
"Most of these devices were never designed to be updated in the field. A supermarket refrigeration controller is installed by a contractor, commissioned once and then left alone for ten or fifteen years. Nobody owns it as an IT asset, so nobody is watching for firmware releases.
There's also a mismatch in lifetimes. The hardware lasts far longer than the vendor's support for it. Danfoss ended support for the AK-SM 800 in 2021 and the AK-SC 355 in 2016, but those boxes were still running cold chains in 2026.
The third problem is how they're connected.
Remote access is added for the maintenance company's convenience and simply left open to the internet. Updating carries risk too: if a firmware update fails on a controller running a store's freezers overnight, the stock is lost. So the safest-looking choice is always to leave it alone."
A Night-Long Threat to the Cold Chain
The overnight timing turned a technical breach into a major cold chain failure. Mark Eccleston, Senior Software Engineer at OxBlue,
pointed out on LinkedIn that a fridge can go about four hours without power before food is at risk. "Hackers got a whole night with hundreds of them," he wrote.
Retailers were forced to discard fresh and frozen products to avoid health
risks, and the incident has raised wider questions about how much of Europe's food supply depends on internet-connected equipment running legacy firmware.
What Businesses Should Learn From the French Supermarket Cyberattack
Carter outlined clear steps for businesses running connected equipment: "First, know what you have. Treat building and plant controllers as part of your attack surface and keep an inventory with support end dates.
Second, nothing operational should be directly reachable from the internet. Remote maintenance should go through a
VPN or be restricted to the contractor's addresses.
Third, ask about end of life when you buy, not after. Under the
EU Cyber Resilience Act, manufacturers will have to declare a support period that matches realistic product lifetimes. Buyers should already be asking for that in writing.
This attack didn't need a zero-day. It needed old, forgotten kit on the open internet, and there's a lot of that out there."

 Entrar


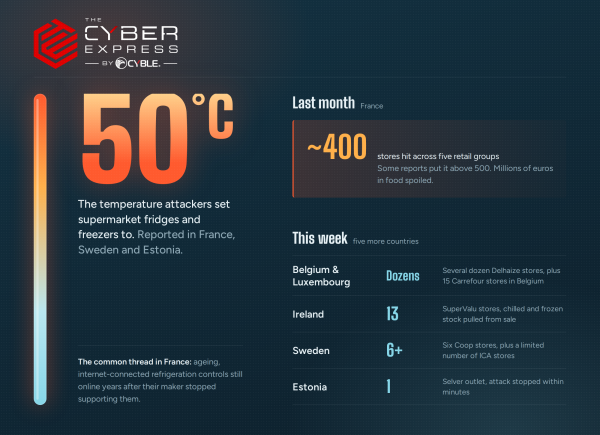 In Ireland, Musgrave Group said refrigeration systems in 13 SuperValu stores were affected by the "cyber incident." Chilled and frozen products were removed from sale as a precaution. By Monday afternoon, the company said the incident had been "fully resolved" and that restocking of chilled and frozen ranges was "well under way."
In Estonia, refrigeration technology company Kitman Coldtech said attackers had accessed a computer controlling a client's refrigeration system and raised the temperature to 50 degrees Celsius, public broadcaster ERR reported. Chief executive Jann Mutso declined to name the store but said the attack was addressed within minutes and caused no significant damage. The Selver supermarket chain confirmed that one of its outlets was affected.
