Entrar

The Cyber Express Weekly Roundup: FBI Blames North Korea for $6B Binance Hack, Hackers Turn Up the Heat on Europe’s Fridges and More


The Binance hack hit USD 6.34B via a fake job interview, an abused AI tool and EIP-7702 delegation. The FBI points to North Korea.
Related Posts:
The post Binance Hack Report Details Fake Job Interview, AI Tool Abuse and EIP-7702 Wallet Drain appeared first on Daily CyberSecurity.

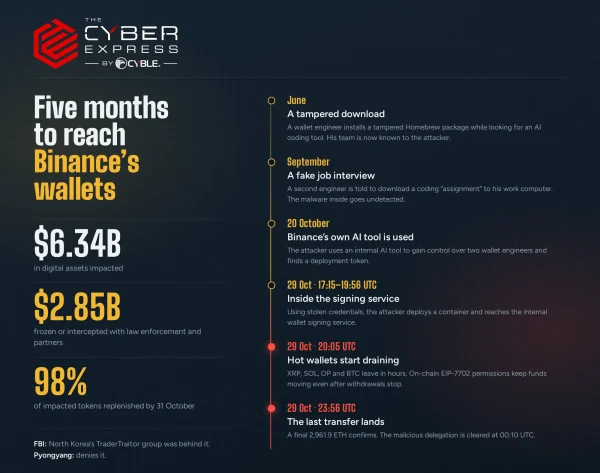 In the second round, held on a popular chat app, Engineer B was told to download an "assignment" onto his work computer. It contained malicious code that ran during setup, swapped a legitimate development tool for a malicious version, and connected to an attacker-controlled server. The zero-day malware was not detected by endpoint security tools at the time.
On October 20, the attackers used Engineer B's compromised computer and an internal AI tool to gain control over Engineer A and another wallet engineer, Engineer C. They then found that Engineer A had a container deployment permission token on his machine.

Polymarket users who had the site open during a short window on October 29 watched their positions get sold and their funds leave their wallets without doing anything themselves. The Polymarket hack did not start inside Polymarket.
It came through a small piece of code from an outside company that loaded on every visit to polymarket.com. The cryptocurrency-based prediction market now says it is returning $3.9 million to affected traders.
In a post-mortem published on October 31, Polymarket said a third-party vendor whose performance-monitoring script ran on polymarket.com had been compromised. The attacker swapped the vendor’s legitimate code for a compromised script built specifically to target Polymarket users.
The attacker did not need anyone’s password. For users who had the site open at the time, the malicious script used their active session to sell positions and move funds out of their wallets. Anyone logged in and browsing during that window was exposed. The vendor has publicly confirmed the compromise.
Polymarket’s status page first reported “unauthorized activity affecting user wallets” on October 29 and marked the incident as resolved later that day.
Performance-monitoring company DebugBear released its own update on the incident. It said its initial findings point to its domain registrar as the point of entry.
“Our DNS records were compromised through our domain registrar,” the company said on X. “We are currently unable to receive emails sent to our domain. Based on our initial investigation this attack targeted the website of a specific customer.”
[caption id="attachment_115172" align="aligncenter" width="538"]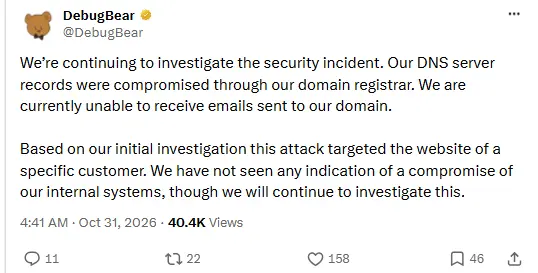 Source- Twitter[/caption]
DebugBear added that it has “not seen any indication of a compromise of our internal systems,” though it is continuing to investigate.
This is the part of the story that should worry other website operators. According to the statements from both companies, the attacker appears to have gone after a vendor’s domain setup rather than Polymarket’s own systems, and used that position to put malicious code in front of Polymarket’s users. DebugBear’s own internal systems, by its account, show no sign of being breached.
Polymarket listed the steps it took once the attack was identified:
The trading pause stopped the bleeding, but it created a second set of losses for traders who were not directly hit by the script.
Polymarket is returning $3.9 million in total. Of that, $2.7 million covers the initial losses from the attack, and $1.2 million covers losses tied to the hours-long shutdown.
As of its post-mortem, the company said 95% of affected wallets had been refunded in full, through a mix of reimbursements for drained wallets and goodwill payments.
The refunds cover more than drained wallets. Polymarket said it also made goodwill payments in two cases:
Users do not need to file claims or tickets. Polymarket said it identified eligible wallets using on-chain and trading data. Anyone who thinks their amount is wrong, or believes they should have received a payment, can submit a form for the company to recheck.
Some questions are still open. Neither company has named the threat actor. DebugBear has said the attack targeted a single customer, but its investigation is ongoing, and it still cannot receive email sent to its domain. Polymarket has also not said exactly how many wallets were affected, only that 95% have been made whole.
The incident shows how much trust a website places in every outside script it loads. Polymarket’s own systems were not the entry point, yet its users still lost money, and it took a trading halt, a session reset and a removal of the vendor’s code to stop it.

The Binance hack investigation reveals a $6.3B breach tied to TraderTraitor, prompting massive stablecoin freezes and an infrastructure overhaul.
Related Posts:
The post Binance Hack Investigation Traces Historic $6.3B Breach appeared first on Daily CyberSecurity.
Binance says a security incident affected approximately $6.3 billion in cryptocurrency. Its initial investigation points to a compromised DevOps engineer’s laptop as a possible entry point.
The exchange says it has frozen around $3 billion with help from blockchain partners. It has promised to cover all losses using its emergency fund and company funds. Binance is reportedly the largest cryptocurrency exchange by daily trading volume.
In an update on October 30, Binance said attackers may have used a compromised laptop belonging to a DevOps engineer to access a service container and submit unauthorized withdrawal transactions. The company said:
“We have found no evidence of any wallet private key leak.”
This doesn’t mean that one employee could simply transfer billions of dollars. Binance co-CEO Richard Teng told BleepingComputer the attacker did not simply use one engineer’s permissions. The incident involved a more complex process, rather than a single “one-click” action. Binance also said investigators had identified additional breach points.
Blockchain intelligence firms TRM Labs and Chainalysis have linked the theft to TraderTraitor, a North Korean hacking group associated with previous cryptocurrency thefts. TRM Labs estimates that about $6.36 billion left Binance wallets across ten blockchains, with most of it moving within about 20 minutes.
Binance says approximately $3 billion has been frozen on-chain, while blockchain analysts have reported somewhat different totals. For now, those figures should be treated as developing estimates rather than a final accounting of recovered funds or the exchange’s ultimate losses.
Binance.com users (Binance.US was not affected) should check their accounts, avoid follow-up scams, and respond quickly if they spot signs of a separate compromise.
Pro tip: Unsure whether a message is a scam? Check it with Malwarebytes’ Scam Guard for an assessment and advice on what to do next.
Trezor has issued an urgent warning after receiving a credible report of a suspected hardware implant in a Safe 5 cryptocurrency wallet purchased from the former reseller CryptoBilis. The company has not independently verified the device, and so far, no CryptoBilis customers have reported losing funds to Trezor. According to Trezor’s security advisory, the wallet […]
The post Trezor Warns of Suspected Spy Implant That Could Steal Crypto Wallet Recovery Phrases appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Discover details of the Ledger hardware wallet hack. Learn how hackers modified devices with spy modules to steal user seed phrases and $80 million in crypto.
Related Posts:
The post The Devastating Ledger Security Breach appeared first on Daily CyberSecurity.


Confirming a ~$7M hack. Still investigating exactly what happened and how. Until we have clarity, Duelbits stays offline. User funds are safe. Next steps: finish the investigation, re-top hot wallets, and bring Duelbits back online, launch Duelbits 2.0. I'll keep posting updates as I have them. Duelbits will be back up asap. Updates to follow"Joe said the platform would stay offline until the investigation is finished and the hot wallets have been refilled. No one has independently verified his claim that user funds are safe.
Crypto casino Duelbits has confirmed a cybersecurity breach that drained approximately $7 million from its hot wallets. In response, the company has taken its platform offline while it investigates the incident. Co-founder Joe said they are still determining “exactly what happened and how,” while assuring customers their funds are safe. Multi-Chain Wallet Drain The incident […]
The post Duelbits Hot Wallet Hack Drains $7 Million, Forces Platform Offline appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Crypto exchange Bitget has confirmed unauthorized transfers from part of its hot wallet infrastructure, resulting in estimated losses of about $351.6 million. To conduct a security review, the company has temporarily suspended withdrawals; however, deposits and trading will remain operational, according to its official incident notice. Bitget Hot Wallet Hack Bitget reported that its security […]
The post Bitget Confirms $351.6 Million Hot Wallet Hack, Suspends Withdrawals appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Group-IB uncovered Iranian HEAVYGRAM malware campaigns. The HEAVYGRAM malware abuses Telegram channels for command execution and data theft.
Related Posts:
The post HEAVYGRAM Malware Abuses Telegram for Cyberespionage appeared first on Daily CyberSecurity.
An ongoing data extortion attack targeting the widely-used education technology platform Canvas disrupted classes and coursework at school districts and universities across the United States today, after a cybercrime group defaced the service’s login page with a ransom demand that threatened to leak data from 275 million students and faculty across nearly 9,000 educational institutions.
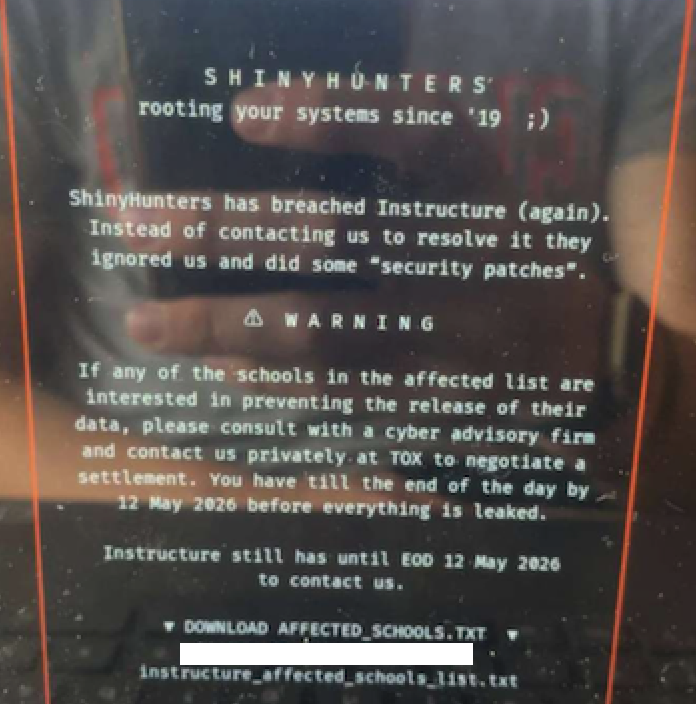
A screenshot shared by a reader showing the extortion message that was shown on the Canvas login page today.
Canvas parent firm Instructure responded to today’s defacement attacks by disabling the platform, which is used by thousands of schools, universities and businesses to manage coursework and assignments, and to communicate with students.
Instructure acknowledged a data breach earlier this week, after the cybercrime group ShinyHunters claimed responsibility and said they would leak data on tens of millions of students and faculty unless paid a ransom. The stated deadline for payment was initially set at May 6, but it was later pushed back to May 12.
In a statement on May 6, Instructure said the investigation so far shows the stolen information includes “certain identifying information of users at affected institutions, such as names, email addresses, and student ID numbers, as well as as messages among users.” The company said it found no evidence the breached data included more sensitive information, such as passwords, dates of birth, government identifiers or financial information.
The May 6 update stated that Canvas was fully operational, and that Instructure was not seeing any ongoing unauthorized activity on their platform. “At this stage, we believe the incident has been contained,” Instructure wrote.
However, by mid-day on Thursday, May 7, students and faculty at dozens of schools and universities were flooding social media sites with comments saying that a ransom demand from ShinyHunters had replaced the usual Canvas login page. Instructure responded by pulling Canvas offline and replacing the portal with the message, “Canvas is currently undergoing scheduled maintenance. Check back soon.”
“We anticipate being up soon, and will provide updates as soon as possible,” reads the current message on Instructure’s status page.
While the data stolen by ShinyHunters may or may not contain particularly sensitive information (ShinyHunters claims it includes several billion private messages among students and teachers, as well as names, phone numbers and email addresses), this attack could hardly have come at a worse time for Instructure: Many of the affected schools and universities are in the middle of final exams, and a prolonged outage could be highly damaging for the company.
The extortion message that greeted countless Canvas users today advised the affected schools to negotiate their own ransom payments to prevent the publication of their data — regardless of whether Instructure decides to pay.
“ShinyHunters has breached Instructure (again),” the extortion message read. “Instead of contacting us to resolve it they ignored us and did some ‘security patches.'”
A source close to the investigation who was not authorized to speak to the press told KrebsOnSecurity that a number of universities have already approached the cybercrime group about paying. The same source also pointed out that the ShinyHunters data leak blog no longer lists Instructure among its current extortion victims, and that the samples of data stolen from Canvas customers were removed as well. Data extortion groups like ShinyHunters will typically only remove victims from their leak sites after receiving an extortion payment or after a victim agrees to negotiate.
Dipan Mann, founder and CEO of the security firm Cloudskope, slammed Instructure for referring to today’s outage as a “scheduled maintenance” event on its status page. Mann said Shiny Hunters first demonstrated they’d breached Instructure on May 1, prompting Instructure’s Chief Information Security Officer Steve Proud to declare the following day that the incident had been contained. But Mann said today’s attack is at least the third time in the past eight months that Instructure has been breached by ShinyHunters.
In a blog post today, Mann noted that in September 2025, ShinyHunters released thousands of internal University of Pennsylvania files — donor records, internal memos, and other confidential materials — through what the Daily Pennsylvanian and other outlets later determined was, in part, a Canvas/Instructure-mediated access path.
“Penn was the named victim,” Mann wrote. “Instructure was the mechanism. The incident was treated as a Penn-specific story by most of the national press and quietly handled by Instructure as a customer-specific matter. That framing was wrong then. It is dramatically more wrong in light of the May 2026 events, which now look like the planned escalation of an attack pattern that ShinyHunters had been working against Instructure’s environment for at least eight months prior. The September 2025 Penn breach was the proof of concept. The May 1, 2026 incident was the production run. The May 7, 2026 recompromise was ShinyHunters demonstrating publicly that the May 2 ‘containment’ did not happen.”
In February, a ShinyHunters spokesperson told The Daily Pennsylvanian that Penn failed to pay a $1 million ransom demand. On March 5, ShinyHunters published 461 megabytes worth of data stolen from Penn, including thousands of files such as donor records and internal memos.
ShinyHunters is a prolific and fluid cybercriminal group that specializes in data theft and extortion. They typically gain access to companies through voice phishing and social engineering attacks that often involve impersonating IT personnel or other trusted members of a targeted organization.
Last month, ShinyHunters relieved the home security giant ADT of personal information on 5.5 million customers. The extortion group told BleepingComputer they breached the company by compromising an employee’s Okta single sign-on account in a voice phishing attack that enabled access to ADT’s Salesforce instance. BleepingComputer says ShinyHunters recently has taken credit for a number of extortion attacks against high-profile organizations, including Medtronic, Rockstar Games, McGraw Hill, 7-Eleven and the cruise line operator Carnival.
The attack on Canvas customers is just one of several major cybercrime campaigns being launched by ShinyHunters at the moment, said Charles Carmakal, chief technology officer at the Google-owned Mandiant Consulting. Carmakal declined to comment specifically on the Canvas breach, but said “there are multiple concurrent and discrete ShinyHunters intrusion and extortion campaigns happening right now.”
Cloudskope’s Mann said what happens next depends largely on whether Instructure’s customers — the universities, K-12 districts, and education ministries paying for Canvas — choose to apply pressure or absorb the breach quietly.
“The history of education-vendor incidents suggests the path of least resistance is the second one,” he concluded.
Update, May 8, 11:05 a.m. ET: Instructure has published an incident update page that includes more information about the breach. Instructure said its Canvas portal is functioning normally again, and that the hackers exploited an issue related to Free-for-Teacher accounts.
“This is the same issue that led to the unauthorized access the prior week,” Instructure wrote. “As a result, we have made the difficult decision to temporarily shut down Free-for-Teacher accounts. These accounts have been a core part of our platform, and we’re committed to resolving the issues with these accounts.”
Instructure said affected organizations were notified on May 6.
“If your organization is affected, Instructure will contact your organization’s primary contacts directly,” the update states. “Please don’t rely on third-party lists or social media posts naming potentially affected organizations as those lists aren’t verified. Instructure will confirm validated information through direct outreach to all affected organizations.”
Update, May 11, 10:16 p.m. ET: Instructure posted an update saying they paid their extortionists in exchange for a promise to destroy the stolen data. “The data was returned to us,” the update reads. “We received digital confirmation of data destruction (shred logs). We have been informed that no Instructure customers will be extorted as a result of this incident, publicly or otherwise.”
A hacktivist group with links to Iran’s intelligence agencies is claiming responsibility for a data-wiping attack against Stryker, a global medical technology company based in Michigan. News reports out of Ireland, Stryker’s largest hub outside of the United States, said the company sent home more than 5,000 workers there today. Meanwhile, a voicemail message at Stryker’s main U.S. headquarters says the company is currently experiencing a building emergency.
Based in Kalamazoo, Michigan, Stryker [NYSE:SYK] is a medical and surgical equipment maker that reported $25 billion in global sales last year. In a lengthy statement posted to Telegram, a hacktivist group known as Handala (a.k.a. Handala Hack Team) claimed that Stryker’s offices in 79 countries have been forced to shut down after the group erased data from more than 200,000 systems, servers and mobile devices.
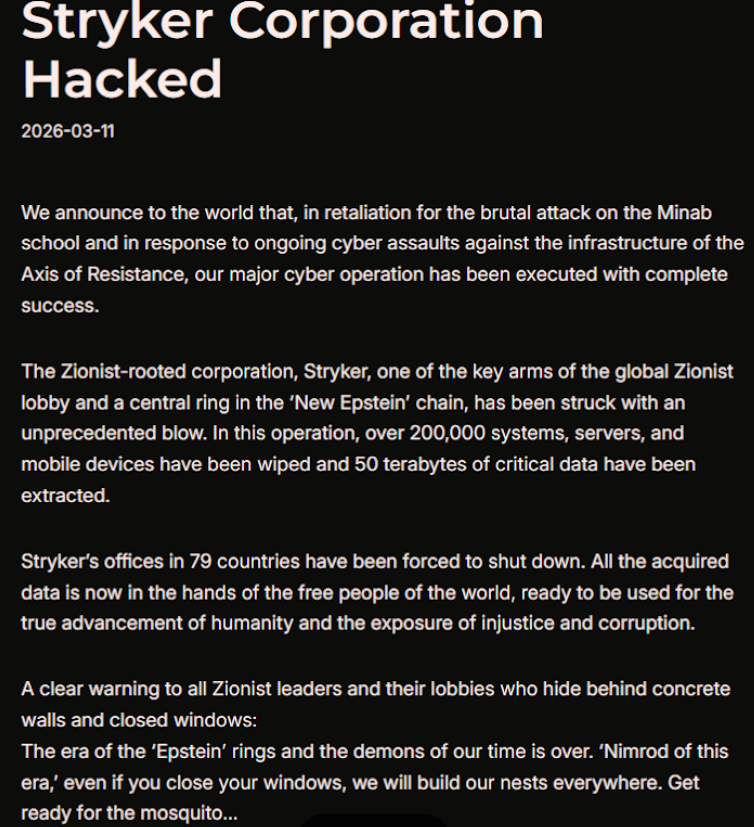
A manifesto posted by the Iran-backed hacktivist group Handala, claiming a mass data-wiping attack against medical technology maker Stryker.
“All the acquired data is now in the hands of the free people of the world, ready to be used for the true advancement of humanity and the exposure of injustice and corruption,” a portion of the Handala statement reads.
The group said the wiper attack was in retaliation for a Feb. 28 missile strike that hit an Iranian school and killed at least 175 people, most of them children. The New York Times reports today that an ongoing military investigation has determined the United States is responsible for the deadly Tomahawk missile strike.
Handala was one of several hacker groups recently profiled by Palo Alto Networks, which links it to Iran’s Ministry of Intelligence and Security (MOIS). Palo Alto says Handala surfaced in late 2023 and is assessed as one of several online personas maintained by Void Manticore, a MOIS-affiliated actor.
Stryker’s website says the company has 56,000 employees in 61 countries. A phone call placed Wednesday morning to the media line at Stryker’s Michigan headquarters sent this author to a voicemail message that stated, “We are currently experiencing a building emergency. Please try your call again later.”
A report Wednesday morning from the Irish Examiner said Stryker staff are now communicating via WhatsApp for any updates on when they can return to work. The story quoted an unnamed employee saying anything connected to the network is down, and that “anyone with Microsoft Outlook on their personal phones had their devices wiped.”
“Multiple sources have said that systems in the Cork headquarters have been ‘shut down’ and that Stryker devices held by employees have been wiped out,” the Examiner reported. “The login pages coming up on these devices have been defaced with the Handala logo.”
Wiper attacks usually involve malicious software designed to overwrite any existing data on infected devices. But a trusted source with knowledge of the attack who spoke on condition of anonymity told KrebsOnSecurity the perpetrators in this case appear to have used a Microsoft service called Microsoft Intune to issue a ‘remote wipe’ command against all connected devices.
Intune is a cloud-based solution built for IT teams to enforce security and data compliance policies, and it provides a single, web-based administrative console to monitor and control devices regardless of location. The Intune connection is supported by this Reddit discussion on the Stryker outage, where several users who claimed to be Stryker employees said they were told to uninstall Intune urgently.
Palo Alto says Handala’s hack-and-leak activity is primarily focused on Israel, with occasional targeting outside that scope when it serves a specific agenda. The security firm said Handala also has taken credit for recent attacks against fuel systems in Jordan and an Israeli energy exploration company.
“Recent observed activities are opportunistic and ‘quick and dirty,’ with a noticeable focus on supply-chain footholds (e.g., IT/service providers) to reach downstream victims, followed by ‘proof’ posts to amplify credibility and intimidate targets,” Palo Alto researchers wrote.
The Handala manifesto posted to Telegram referred to Stryker as a “Zionist-rooted corporation,” which may be a reference to the company’s 2019 acquisition of the Israeli company OrthoSpace.
Stryker is a major supplier of medical devices, and the ongoing attack is already affecting healthcare providers. One healthcare professional at a major university medical system in the United States told KrebsOnSecurity they are currently unable to order surgical supplies that they normally source through Stryker.
“This is a real-world supply chain attack,” the expert said, who asked to remain anonymous because they were not authorized to speak to the press. “Pretty much every hospital in the U.S. that performs surgeries uses their supplies.”
John Riggi, national advisor for the American Hospital Association (AHA), said the AHA is not aware of any supply-chain disruptions as of yet.
“We are aware of reports of the cyber attack against Stryker and are actively exchanging information with the hospital field and the federal government to understand the nature of the threat and assess any impact to hospital operations,” Riggi said in an email. “As of this time, we are not aware of any direct impacts or disruptions to U.S. hospitals as a result of this attack. That may change as hospitals evaluate services, technology and supply chain related to Stryker and if the duration of the attack extends.”
According to a March 11 memo from the state of Maryland’s Institute for Emergency Medical Services Systems, Stryker indicated that some of their computer systems have been impacted by a “global network disruption.” The memo indicates that in response to the attack, a number of hospitals have opted to disconnect from Stryker’s various online services, including LifeNet, which allows paramedics to transmit EKGs to emergency physicians so that heart attack patients can expedite their treatment when they arrive at the hospital.
“As a precaution, some hospitals have temporarily suspended their connection to Stryker systems, including LIFENET, while others have maintained the connection,” wrote Timothy Chizmar, the state’s EMS medical director. “The Maryland Medical Protocols for EMS requires ECG transmission for patients with acute coronary syndrome (or STEMI). However, if you are unable to transmit a 12 Lead ECG to a receiving hospital, you should initiate radio consultation and describe the findings on the ECG.”
This is a developing story. Updates will be noted with a timestamp.
Update, 2:54 p.m. ET: Added comment from Riggi and perspectives on this attack’s potential to turn into a supply-chain problem for the healthcare system.
Update, Mar. 12, 7:59 a.m. ET: Added information about the outage affecting Stryker’s online services.