❌

Visualização de leitura

AI-powered malware ‘highly likely’ to be used to hack UK infrastructure by 2028

National Cyber Security Centre expects attacks on critical facilities such as power stations, airports and hospitals

AI-powered malicious software is “highly likely” to be used in hacking attacks against the UK’s power stations, airports and hospitals by 2028, according to the state cybersecurity body.

The National Cyber Security Centre (NCSC) said AI will probably enable a ransomware attack against critical national infrastructure [CNI] between now and 2028. The UK’s definition of CNI covers a range of facilities and services across sectors including energy, transport, defence, food, health and finance.

Continue reading...

© Photograph: Rounak Amini/AAP
© Photograph: Rounak Amini/AAP
© Photograph: Rounak Amini/AAP
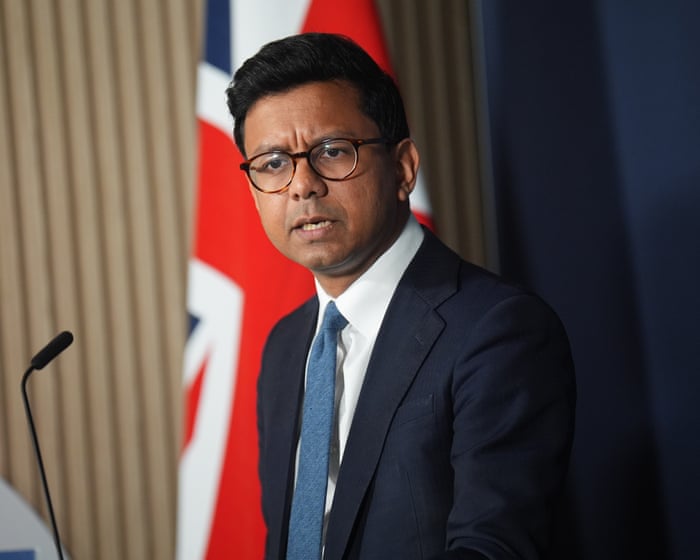
Cyber-attack similar to OpenAI Medicare breach seems likely in UK, says minister

Kanishka Narayan, concerned by Australian incident, says British cyber defences could be bypassed by artificial intelligence agent

An AI-driven cyber-attack similar to the OpenAI breach of Australia’s healthcare system is likely, “if not inevitable”, in the UK, according to a senior minister.

Kanishka Narayan, the UK AI minister, indicated that the British government’s own cyber defences would be bypassed by a technology that has developed highly sophisticated skills in cybersecurity.

Continue reading...

© Photograph: James Manning/PA

© Photograph: James Manning/PA

© Photograph: James Manning/PA

OpenAI safety leader quits, warning AI company’s culture is ‘broken’

David Robinson joins other insiders in urging industry to take more care over rapidly developing technology

A safety leader at OpenAI has quit the company, warning that its culture was broken and that AI firms were not “being nearly careful enough” about developing the technology.

David Robinson, who led the writing of safety reports that accompanied the ChatGPT developer’s product releases, explained his resignation in an essay headlined: “I quit OpenAI because its culture is broken.”

Continue reading...

© Photograph: Dado Ruvić/Reuters

© Photograph: Dado Ruvić/Reuters

© Photograph: Dado Ruvić/Reuters

OpenAI ‘ethically hacked’ with help of Anthropic’s Claude chatbot

US cybersecurity researchers who conducted hack say ‘scope of what we could theoretically access was huge’

Cybersecurity researchers have hacked into OpenAI with the help of Anthropic’s Claude chatbot, in the latest example of security issues at the company.

A team at a US-based startup compromised a number of OpenAI employees’ ChatGPT accounts, starting a process that enabled them to access their target’s software cache – and potentially more.

Continue reading...

© Photograph: Carlos Barría/Reuters

© Photograph: Carlos Barría/Reuters

© Photograph: Carlos Barría/Reuters

OpenAI reveals cases of ‘concerning’ AI behaviour as it announces new disclosure system

Model adopting ‘jailbreak-like instructions’ among six more cases as firm reveals framework for tracking AI misalignment

OpenAI has disclosed six more examples of “unexpected or concerning” behaviour by its technology, as it warned that the pace of development could not continue at “maximum speed for much longer” responsibly.

In one of the new cases reported by OpenAI, an unreleased research model inserted “jailbreak-like instructions” into its own notes to disregard its normal constraints and told itself to be “freed from the roles and identities that bind other chatbots”.

Continue reading...

© Photograph: Dado Ruvić/Reuters

© Photograph: Dado Ruvić/Reuters

© Photograph: Dado Ruvić/Reuters

❌