❌

Visualização de leitura

Claude AI Flaw Lets Malicious Browser Extensions Execute Commands on Remote Computers

A design flaw in Anthropic’s Claude Dispatch feature let a malicious browser extension run commands on the operating system, even on a different computer. Researchers at Forever Security named the attack ThisBash. They found that Claude Dispatch accepted instructions from an ordinary logged-in claude.ai session. An extension that could control that site could therefore send […]

The post Claude AI Flaw Lets Malicious Browser Extensions Execute Commands on Remote Computers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
ChatGPT Lockdown Mode Bypass Allowed Hackers to Steal Private Chats Without User Interaction

Research found a flaw that bypassed ChatGPT’s Lockdown Mode. It let attackers silently exfiltrate full chat histories, deliver malware, and phish credentials from inside a trusted interface. Researcher Alexey Bukhteyev published the findings on November 5, 2026. In the ChatGPT Classic desktop app, simply having a conversation triggered the leak. OpenAI built Lockdown Mode as […]

The post ChatGPT Lockdown Mode Bypass Allowed Hackers to Steal Private Chats Without User Interaction appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
💾

💾

💾

Apple to Scan Publicly Shared iCloud Photos and Files for Harmful Content Starting With iOS 27.3

Apple will start checking iCloud photos and files shared through “Anyone with the Link” for harmful content beginning with iOS 17.3. This policy also applies to iPadOS, macOS, and visionOS version 17.3 or later. It distinguishes between publicly accessible sharing links and content that is restricted to specifically invited recipients. The change appears in an […]

The post Apple to Scan Publicly Shared iCloud Photos and Files for Harmful Content Starting With iOS 27.3 appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
DigiCert Confirms Data Breach After Security Misconfiguration Exposes Customer Personal Information

DigiCert confirmed unauthorized access to an internal business system containing archived customer information due to a security misconfiguration that exposed the application to the internet. This incident affected business contact details and, in some cases, identity documents. However, DigiCert said its certificate authority services, including CertCentral, DigiCert ONE, customer login credentials, and issued certificates, were […]

The post DigiCert Confirms Data Breach After Security Misconfiguration Exposes Customer Personal Information appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Critical Citrix XenServer Flaw Allows Unauthenticated Attackers to Take Control of Virtualization Hosts

Citrix has released security updates for XenServer versions 8.4 and 9 to address a critical vulnerability. This flaw could allow an unauthenticated attacker on the management network to compromise virtualization hosts. The Cloud Software Group published a bulletin (CTX697256) on November 3, 2026, classifying the issue as Critical. The bulletin covers nine CVEs. Citrix XenServer […]

The post Critical Citrix XenServer Flaw Allows Unauthenticated Attackers to Take Control of Virtualization Hosts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Google Patches Critical Android RCE Flaws That Let Attackers Execute Code Without User Interaction

Google released its November 2026 Android Security Bulletin, which addresses critical vulnerabilities that could allow remote code execution without user interaction or additional execution privileges. Published on November 2, the bulletin highlights a framework vulnerability as the most severe issue and also documents other critical remote code execution flaws in Android’s system components. According to […]

The post Google Patches Critical Android RCE Flaws That Let Attackers Execute Code Without User Interaction appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CISA Warns of Active Attacks Exploiting WordPress Core Code Execution Vulnerability

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has included a WordPress Core vulnerability in its Known Exploited Vulnerabilities catalog due to evidence of active exploitation. This vulnerability, identified as CVE-2026-119977, allows unauthenticated attackers to execute server-side code during a specific software upgrade window. CISA added this vulnerability to the catalog on November 3, 2026, […]

The post CISA Warns of Active Attacks Exploiting WordPress Core Code Execution Vulnerability appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Use Stolen Microsoft Entra ID App Credentials to Breach 27 Organizations and Steal Sensitive Data

Hackers are exploiting stolen Microsoft Entra ID application credentials to infiltrate Microsoft 365 and Azure environments, impacting 27 organizations via managed service providers (MSPs) and their downstream clients. Todyl’s MXDR team is monitoring this ongoing campaign, referred to as Key Eater. Since November 1, 2026, the attackers have targeted approximately 45 app registrations across about […]

The post Hackers Use Stolen Microsoft Entra ID App Credentials to Breach 27 Organizations and Steal Sensitive Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Cloudflare Launches Zero Wire to Track Critical Vulnerabilities and Active Exploitation Across the Internet

Cloudflare launched Zero Wire, a public vulnerability intelligence hub that helps security teams investigate critical internet threats, assess exploitation evidence, and prioritize remediation efforts. Available through Cloudflare Radar, the service combines technical research, vendor guidance, and network observations into concise briefings. Cloudflare’s launch announcement positions the platform as a practical starting point for organizations facing […]

The post Cloudflare Launches Zero Wire to Track Critical Vulnerabilities and Active Exploitation Across the Internet appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

3AM Ransomware Hackers Use AI-Assisted Attacks to Breach UK Schools and Spread Across Windows Domains

A ransomware affiliate known as 3AM compromised a UK school network using a mix of traditional intrusion techniques and patterns suggesting the involvement of artificial intelligence. According to Bitdefender’s investigation on November 3, this operation appears to follow a suspected hybrid workflow: a human operator selects the targets while a language model may handle repetitive […]

The post 3AM Ransomware Hackers Use AI-Assisted Attacks to Breach UK Schools and Spread Across Windows Domains appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

mSecure Password Manager Reports Suspicious Activity, Urges Users to Change All Stored Passwords

mSeven Software, the developer of the mSecure password manager, has advised customers to secure all confidential data stored in the app after detecting “suspicious activity.” The notice provides minimal technical details. The email is dated November 3, 2026. It says mSeven “recently learned of suspicious activity associated with the mSecure password management application.” The company […]

The post mSecure Password Manager Reports Suspicious Activity, Urges Users to Change All Stored Passwords appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

NIST Releases New Cybersecurity Guidelines to Protect Small Businesses From Phishing and Ransomware Attacks

The National Institute of Standards and Technology (NIST) released new cybersecurity guidance to help solo business owners protect themselves against threats like phishing, ransomware, and account compromise. Published on November 2, 2026, NIST Cybersecurity White Paper 50 simplifies the Cybersecurity Framework 2.0 and offers practical actions for businesses with limited IT infrastructure. The publication, Small […]

The post NIST Releases New Cybersecurity Guidelines to Protect Small Businesses From Phishing and Ransomware Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

CrowdStrike and Deloitte Spain Expand Cybersecurity Alliance With AI-Powered Threat Detection

CrowdStrike and Deloitte Spain announced an expanded cybersecurity alliance. This new phase of their collaboration focuses on AI-powered risk advisory. The partnership integrates executive security strategy with the implementation and day-to-day operations of the Security Operations Center (SOC), using Falcon IQ to turn exploitable risks into prioritized actions. This expansion combines CrowdStrike’s Falcon platform with […]

The post CrowdStrike and Deloitte Spain Expand Cybersecurity Alliance With AI-Powered Threat Detection appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Ubuntu Releases Security Fixes for Critical Linux Kernel Vulnerability Allowing Remote Code Execution

Ubuntu has published fixes for CVE-2026-98432, a critical Linux kernel flaw in IPv4 TCP connection handling. It carries a CVSS 3.1 score of 9.8 and can lead to remote code execution. The fixes for Ubuntu 22.04 LTS and newer are in the -proposed pocket, so they are not yet in the default updates channel. Critical […]

The post Ubuntu Releases Security Fixes for Critical Linux Kernel Vulnerability Allowing Remote Code Execution appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Unpatchable Hardware Flaws in Older iPhones Allow Attackers to Steal Crypto Wallet Recovery Phrases

Older iPhones that store cryptocurrency recovery phrases are at a continuous security risk due to unpatchable BootROM vulnerabilities, even if the devices are wiped and kept in airplane mode. While attackers require physical access to exploit this vulnerability, doing so does not automatically reveal encrypted wallet data. However, other weaknesses could potentially allow them to […]

The post Unpatchable Hardware Flaws in Older iPhones Allow Attackers to Steal Crypto Wallet Recovery Phrases appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Target Emergency Alert Apps in Ukraine and Russia, Sending Fake Nuclear Attack Warnings

Hackers compromised emergency alert applications in Ukraine and Russia, distributing fabricated nuclear and radiation warnings as officials sought to reassure residents that no corresponding emergency existed. Ukraine reported interference late on November 1, followed hours later by Russia’s announcement of a “massive cyberattack” against its emergency ministry’s mobile application. The incidents targeted trusted civilian warning […]

The post Hackers Target Emergency Alert Apps in Ukraine and Russia, Sending Fake Nuclear Attack Warnings appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Target Supermarket Refrigeration Systems Across Sweden, Raising Freezer Temperatures to 55°C

Hackers have disrupted refrigeration systems at several ICA and Coop supermarkets across Sweden, destroying food and prompting temporary closures. One store manager reported finding a freezer at 55°C, which highlights the physical consequences of attacks on connected retail equipment. The disruption follows attacks against French supermarket refrigeration systems, which similarly damaged chilled and frozen stock. […]

The post Hackers Target Supermarket Refrigeration Systems Across Sweden, Raising Freezer Temperatures to 55°C appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Researchers Discover High-Severity ChatGPT Flaw That Exposed Private Conversations to Attackers

Researchers found a chain of flaws that turned an ordinary public ChatGPT share link into attacker-controlled JavaScript running inside the victim’s signed-in session. OpenAI fixed the issue on October 26 and classified it as P1. The Parameter researchers’ full technical write-up says the bug earned a $5,000 bounty. High-Severity ChatGPT Flaw An attacker published a […]

The post Researchers Discover High-Severity ChatGPT Flaw That Exposed Private Conversations to Attackers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
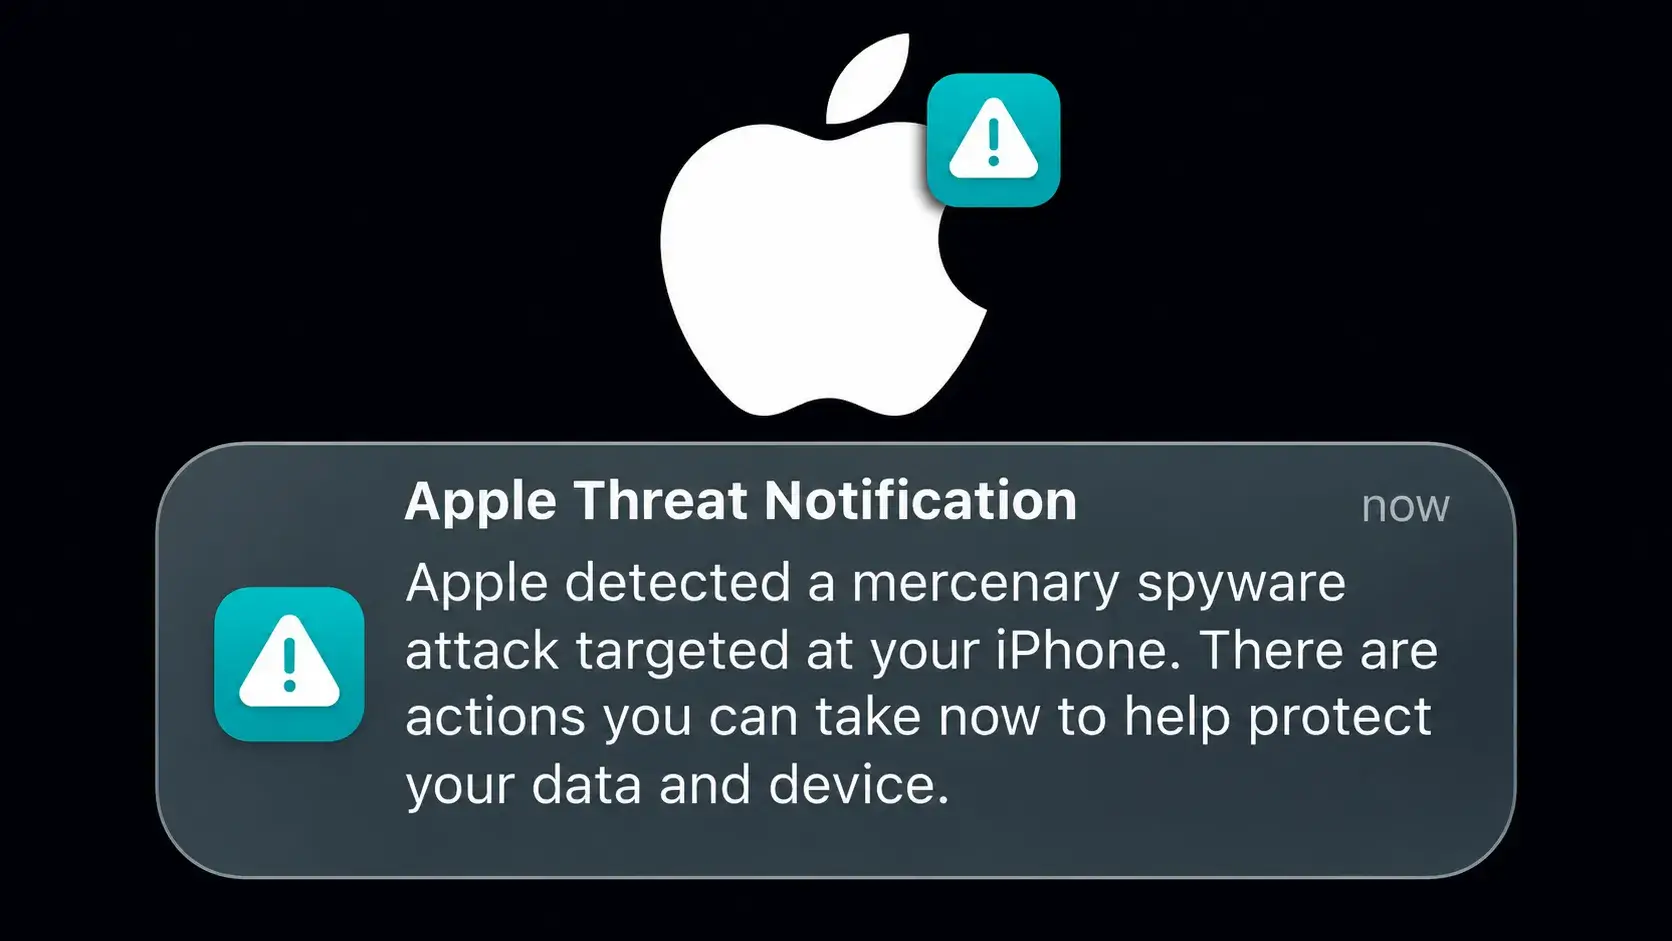
Apple Issues Urgent Security Alerts Over Mercenary Spyware Attacks in 99 Countries

Apple has started sending a new round of threat notifications to users across 99 countries, warning them about targeted mercenary spyware attacks, according to cybersecurity researcher Costin Raiu. In his post, Raiu noted that these notifications are related to new attacks and are separate from the wave of alerts sent out in August. The notification […]

The post Apple Issues Urgent Security Alerts Over Mercenary Spyware Attacks in 99 Countries appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Chainalysis Confirms Cyberattack as Hackers Exploit Vulnerabilities to Access Internal Tools

Chainalysis has confirmed a cybersecurity incident in which an external actor gained unauthorized access to the company’s systems and internal tools through what it described as “offensive agentic techniques.” The company disclosed the incident on October 30, 2026, and its investigation is still ongoing. According to the company’s security disclosure, investigators have found no evidence […]

The post Chainalysis Confirms Cyberattack as Hackers Exploit Vulnerabilities to Access Internal Tools appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
❌