❌

Visualização de leitura

The October 2026 Security Update Review

Another month of patches equals another new record for Microsoft patches. It’s a good thing I survive Pwn2Own Ireland, because between these and the Adobe patches, there’s much to discuss. I’m also looking at different ways I can represent the bugs at this level of volume, so let me know if you have ideas. (Seriously – I’m out of ideas). If you’d rather watch the full video recap covering the entire release, you can check it out here:

Adobe Patches for October 2026

For the first part of the October release, Adobe released 11 bulletins addressing 174 unique CVEs in Adobe Dimension, Commerce, Substance 3D Sampler, ColdFusion, Photoshop, FrameMaker, Experience Manager, Substance 3D Stager, Content Credentials SDK, Bridge, and Substance 3D Designer.

Here’s this month’s overview table:

Adobe Patches for October 2026

Adobe Patches for October 2026

Bulletin ID Product CVE Count Highest Severity Highest CVSS Exploited Deployment Priority
APSB26-152 Adobe Experience Manager 33 Critical 10.0 No 2
APSB26-144 Adobe ColdFusion 32 Critical 10.0 No 2
APSB26-153 Adobe Commerce 11 Critical 10.0 No 2
APSB26-163 Content Credentials SDK 30 High 8.6 No 3
APSB26-171 Adobe Dimension 7 High 8.6 No 3
APSB26-158 Adobe Photoshop 18 High 8.2 No 3
APSB26-170 Adobe Substance 3D Stager 16 High 7.8 No 3
APSB26-172 Adobe FrameMaker 10 High 7.8 No 3
APSB26-169 Adobe Substance 3D Designer 9 High 7.8 No 3
APSB26-159 Adobe Substance 3D Sampler 4 High 7.8 No 3
APSB26-167 Adobe Bridge 4 High 7.8 No 3
TOTAL 11 bulletins 174

The one I’d treat as most urgent is the patch for ColdFusion despite the Priority 2 rating. In addition to the CVSS 10 bug, the 10 Critical CVEs include unrestricted file upload (CWE-434), code injection (CWE-94), SSRF, and incorrect authorization — a classic pre-auth RCE profile on an internet-facing server product. Impacts run from arbitrary code execution and privilege escalation to arbitrary file read/write. Up next is the bulletin covering Commerce. It may have the smallest count, but it’s a high-value target, and it follows last month’s actively exploited Commerce zero-day (CVE-2026-75650). The Critical bugs include template-engine injection and incorrect authorization, yielding code execution, privilege escalation, and arbitrary file write. Adobe’s table also flags whether authentication is required per CVE, which is useful for triage here. Finally, the other Priority 2 update covers Experience Manager and is the broadest of the three. Beyond the usual XSS volume (stored, reflected, and DOM-based), it includes genuinely serious server-side bugs: OS command injection, SQL injection, XXE, XML injection, and path traversal, leading to code execution, privilege escalation, and security feature bypass. Worth noting the Vulnerability Details table has 34 rows, but CVE-2026-106631 is listed twice, so it’s 33 distinct CVEs.

Aside from the bugs mentioned, all other Adobe patches are Deployment Priority 3. None of the other Adobe bugs receiving patches this month are listed as publicly known or under active attack at the time of release.

Microsoft Patches for October 2026

Before we get into this month’s Microsoft release, let’s talk about what they changed. Microsoft is introducing “risk cohorts”. According to Microsoft, “They are an exploratory way to help customers organize their own analysis. They are not official Microsoft vulnerability categories, do not change Microsoft update guidance, and do not replace the assessment of individual CVEs.” Back in my day, we called these security bulletins. One component could have multiple CVEs in a single bulletin. Microsoft is reintroducing this concept at the group level. I applaud this change as it mirrors my analysis from last month (and this month). Time will tell if enterprises can capitalize on these “cohorts”, but any move made to make the monthly release more manageable is a welcome one. You can read the full details on Microsoft’s site here.

Now on to our regularly scheduled analysis.

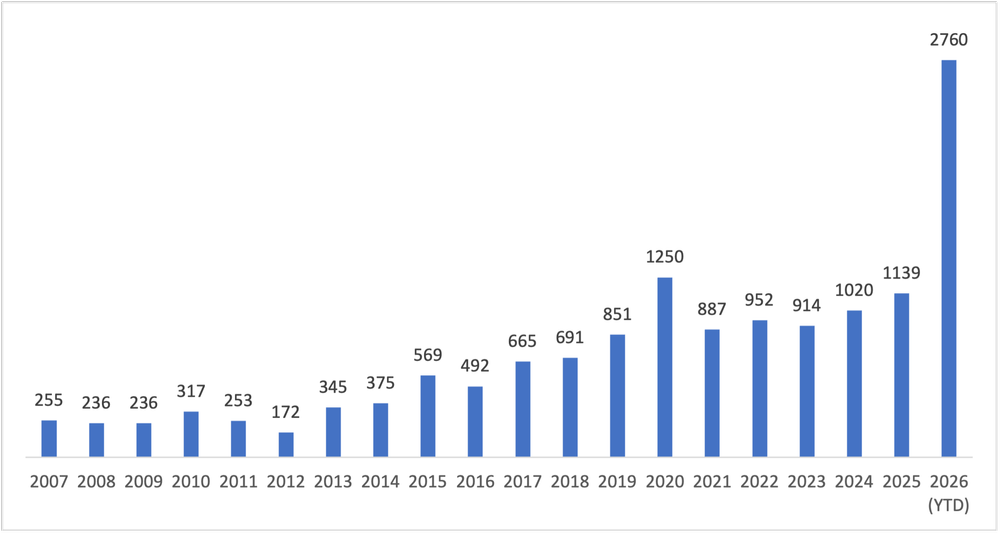
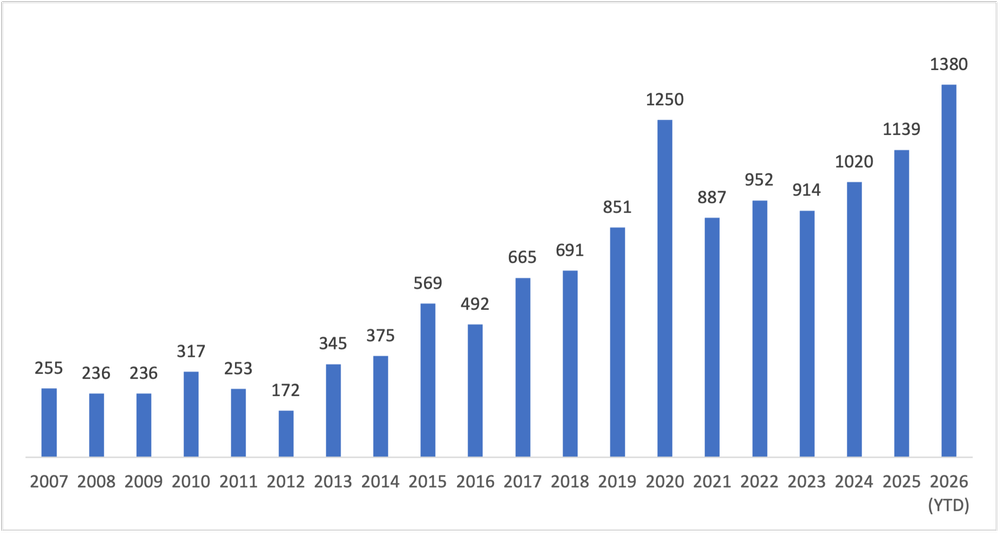
Well, it’s a new record release from Microsoft, again. This is also the first four-digit volume we have ever seen and includes six-digit CVEs. As always, counting this load is tricky, but I see 1,415 new CVEs from Microsoft. That puts this month at a greater volume than any previous YEAR from Microsoft. I’m starting to think I don’t like this new normal. As for the products affected by this release, we have Windows and Windows components, Office and Office Components, Developer Tools and .NET, SharePoint, Linux kernel, Skype for Business and Microsoft Lync, SQL Server and Dynamics, Azure and cloud services, and Exchange server.

Still, if there’s solace to be had, it’s in the fact that only one of these bugs is under active attack. If you go back to the “Hot 0-day Summer” of 2023, there were 17 Microsoft 0-days between January and October as opposed to 15 this year during the same period. The total number of Microsoft CVEs in 2023? Just 914. So, AI is certainly helping in bug discovery (and likely in bug patching), but we haven’t seen the same increase in the exploitation of 0-days – yet. As witnessed at the last Pwn2Own, AI-assisted exploitation is most certainly a thing. It just hasn’t hit the mainstream yet, even though other incidents are on the rise.

Hundreds of CVEs in a single release used to be the exception; now it’s the baseline. Is AI to blame? Partly. It’s accelerating bug-hunting on both sides of the fence, so vendors are finding (and fixing) more flaws, and researchers are finding them faster too. But AI isn’t creating these bugs out of thin air. It’s just shortening the time between a vulnerability existing and someone noticing it. What matters is that discovery is scaling faster than exploitation, so teams that triage by sheer CVE count instead of exploitability are burning cycles on the wrong bugs. Patch what’s proven, prioritized, and public, and treat everything else as this month’s new normal.

Two bugs in this release are listed as publicly known: CVE-2026-108398, a .NET Framework security feature bypass that could let an attacker evade Windows Defender Application Control (WDAC) enforcement, and CVE-2026-92707, a denial-of-service bug in MessagePack-CSharp that was released by a third party and is now included in Microsoft’s release. Neither is listed as under active attack. As always, we’ll start with the bug under active attack and move on from there.

-              CVE-2026-96951 - Windows Shell Security Feature Bypass Vulnerability
This is the lone bug listed as under active attack, and it’s certainly a type of bug we’ve seen before. Going back to 2024, attackers have used multiple methods to avoid Mark of the Web (MotW) protections. This time, it’s Shell instead of SmartScreen, but the result is the same. As with any bug under active attack, test and deploy this patch quickly

-              CVE-2026-102866 – Microsoft Office SharePoint Elevation of Privilege Vulnerability
There are lots of SharePoint bugs this month, but this one stands out. It’s the only Critical-rated SharePoint CVE (CVSS 8.1), and the only one an unauthenticated attacker can exploit. It’s an improper cryptographic signature verification bug. An attacker who obtains a valid proof token for a targeted user could modify it, submit it to the server, and authenticate as that user. The only caveat is that the attacker has to obtain that token first, but there are multiple methods this could be achieved.

-              CVE-2026-65674 – Microsoft SQL Server Remote Code Execution Vulnerability
Like SharePoint, there’s lots to choose from in the SQL component. This one is the highest-scoring CVSS at 8.8 and has the best exploitability rating of any SQL Server bug this month. It’s a deserialization of untrusted data. An authenticated attacker connects to an affected SQL Server and sends a specially crafted request to run code on the server. No user interaction is needed. Definitely check this on any SQL Server directly connected to the internet.

-              CVE-2026-70571 - Microsoft Exchange Server Remote Code Execution Vulnerability
Technically speaking, this is a wormable bug in Exchange Server. However, I wouldn’t count on that happening. Microsoft states, “Exploitation requires an attacker to have a deep understanding of the target environment and is not guaranteed to succeed.” While the wording is obtuse, it generally means the likelihood of stars aligning to exploit the Exchange Server through this bug is minuscule. 

Speaking of Wormable…

 I normally call out every bug I think is wormable, but there are just too many this month. Let me sum up. A total of 59 of the October CVEs fit my definition of wormable. Specifically, 57 contain both “An unauthenticated attacker could exploit this vulnerability by sending a specially crafted packet to an affected service over the network” and “No authentication or user interaction is required.” Two more, CVE-2026-70147 and CVE-2026-88178, use variant wording but also require no authentication or user interaction. These bugs are as follows:

•        DHCP Server (6): CVE-2026-96934, 88117, 88119, 88120, 96320, 69830

•        Network Policy Server (4): CVE-2026-100222, 85806, 85371, 85799

•        Windows Error Reporting (4): CVE-2026-83519, 83693, 83748, 97815

•        Remote Desktop Gateway (3): CVE-2026-70187, 100218, 84012

•        Text Shaping (3): CVE-2026-102210, 83770, 97814

•        Two each (14): QUIC (CVE-2026-100219, 105016), Schannel (CVE-2026-105008, 105005), DNS Server (CVE-2026-83869, 70127), Media Foundation (CVE-2026-83517, 85814), Microsoft XML (CVE-2026-83935, 83914), RRAS (CVE-2026-85792, 85809) and PostScript Printer Driver (CVE-2026-70147, 70153)

•        One each (25): Windows Search (CVE-2026-105010), TCP/IP (CVE-2026-69913), IIS (CVE-2026-70024), libarchive (CVE-2026-70062), Rich Text Edit Control (CVE-2026-70096), System Information Console (CVE-2026-70157), .NET (CVE-2026-70197), Active Directory Domain Services (CVE-2026-70229), PowerShell (CVE-2026-83578), CCFFilter Driver (CVE-2026-83780), Shell (CVE-2026-83782), Paint (CVE-2026-83844), Network Load Balancing (CVE-2026-83862), RPC Runtime (CVE-2026-83910), PPP EAP-TLS (CVE-2026-84015), Volume Manager Extension Driver (CVE-2026-85928), Failover Cluster (CVE-2026-88102), Failover Cluster Virtual Driver (CVE-2026-96864), LSASS (CVE-2026-96219), BitLocker (CVE-2026-96909), OLE (CVE-2026-96924), PowerPoint (CVE-2026-88178), Message Queuing (CVE-2026-108460), OpenSSH for Windows (CVE-2026-97816) and Partition Management Driver (CVE-2026-97805)

I may be wrong about some of these – there are a few where the description is somewhat…er…ambiguous, but regardless, this number of wormable bugs in 2026 should cause some level of concern. Not panic. There’s no need for that, but it is disconcerting to see this many juicy targets sitting out there. Please do your best to test and deploy these fixes in a timely manner.

Here’s the full list of CVEs released by Microsoft for October 2026:

October 2026 Microsoft Security Update CVEs
CVETitleSeverityCVSSPublicExploitedType
CVE-2026-96951Windows Shell Security Feature Bypass VulnerabilityImportant8.8NoYesSFB
CVE-2026-108398.NET Framework Security Feature Bypass VulnerabilityImportant8.8YesNoSFB
CVE-2026-92707 *MessagePack-CSharp Denial of Service VulnerabilityModerate5.3YesNoDoS
CVE-2026-96222Active Directory Federation Services (AD FS) Spoofing VulnerabilityCritical7.4NoNoSpoofing
CVE-2026-108131Active Directory Federation Services (AD FS) Spoofing VulnerabilityCritical7.5NoNoSpoofing
CVE-2026-83943 **Azure API Center Information Disclosure VulnerabilityCritical8.7NoNoInfo
CVE-2026-77900 **Azure App Service Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-83947 **Azure Event Grid Spoofing VulnerabilityCritical7.7NoNoSpoofing
CVE-2026-69435 **Azure SRE Agent Elevation of Privilege VulnerabilityCritical9.6NoNoEoP
CVE-2026-108400HEVC Video Extensions Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-62840Linux Kernel Elevation of Privilege VulnerabilityCritical7NoNoEoP
CVE-2026-94510 **Microsoft Bookings Elevation of Privilege VulnerabilityCritical9.9NoNoEoP
CVE-2026-88131 **Microsoft Dataverse Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-105718Microsoft Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-70571Microsoft Exchange Server Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-100215Microsoft Graphics Component Remote Code Execution VulnerabilityCritical7.8NoNoRCE
CVE-2026-100209Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-100210Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-100211Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97739Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97745Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97755Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97756Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97758Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97759Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97765Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97778Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97780Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97741Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97742Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97753Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97761Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97767Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97776Microsoft Office Excel Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-70242Microsoft Office Outlook Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-70291Microsoft Office Outlook Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-88156Microsoft Office Outlook Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-97016Microsoft Office Outlook Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-97749Microsoft Office Outlook Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-88178Microsoft Office PowerPoint Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-70215Microsoft Office PowerPoint Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-88144Microsoft Office PowerPoint Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-88207Microsoft Office PowerPoint Remote Code Execution VulnerabilityCritical7.5NoNoRCE
CVE-2026-102866Microsoft Office SharePoint Elevation of Privilege VulnerabilityCritical8.1NoNoEoP
CVE-2026-102855Microsoft Office Visio Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-102856Microsoft Office Visio Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-102857Microsoft Office Visio Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-70269Microsoft Office Word Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-88185Microsoft Office Word Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-70300Microsoft Office Word Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-96207 **Microsoft Partner Center Elevation of Privilege VulnerabilityCritical10NoNoEoP
CVE-2026-70147Microsoft PostScript Printer Driver Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-70153Microsoft PostScript Printer Driver Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-108467Microsoft PostScript Printer Driver Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-100219Microsoft QUIC Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-105016Microsoft QUIC Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-96952Microsoft Windows Media Foundation Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-108457Microsoft Windows PDF Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-69802Network Device Enrollment Service (NDES) Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-21413 *Raw Image Extension Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-70229Windows Active Directory Domain Services Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-83917Windows ALPC Elevation of Privilege VulnerabilityCritical7NoNoEoP
CVE-2026-88174Windows Deployment Services Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-70250Windows DHCP Client Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-96934Windows DHCP Server Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-88117Windows DHCP Server Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-88119Windows DHCP Server Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-88120Windows DHCP Server Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-88171Windows DHCP Server Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-83934Windows GDI+ Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-88073Windows Graphics Kernel Elevation of Privilege VulnerabilityCritical8.8NoNoEoP
CVE-2026-108399Windows Hyper-V Elevation of Privilege VulnerabilityCritical7.2NoNoEoP
CVE-2026-102214Windows Hyper-V Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-105733Windows Hyper-V Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-96913Windows Kernel Elevation of Privilege VulnerabilityCritical8.8NoNoEoP
CVE-2026-100220Windows Media Video Decoder Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-100202Windows Message Queuing Queue Manager Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-108460Windows Message Queuing Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-96202Windows Raw Image Extension Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-96943Windows Raw Image Extension Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-69789Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution VulnerabilityCritical7.5NoNoRCE
CVE-2026-70187Windows Remote Desktop Services Remote Code Execution VulnerabilityCritical8.1NoNoRCE
CVE-2026-102225Windows Text Shaping Remote Code Execution VulnerabilityCritical8.8NoNoRCE
CVE-2026-97814Windows Text Shaping Remote Code Execution VulnerabilityCritical9.8NoNoRCE
CVE-2026-96914Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege VulnerabilityCritical8.8NoNoEoP
CVE-2026-108130Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege VulnerabilityCritical7.8NoNoEoP
CVE-2026-88074Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege VulnerabilityCritical7.8NoNoEoP
CVE-2026-102211Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege VulnerabilityCritical7NoNoEoP
CVE-2026-108471Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege VulnerabilityCritical8.8NoNoEoP
CVE-2026-102869.NET and Visual Studio Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-58280.NET Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-69651.NET Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-84008.NET Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96958.NET Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96959.NET Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96960.NET Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70162.NET Denial of Service VulnerabilityImportant5.9NoNoDoS
CVE-2026-96225.NET Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96231.NET Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70161.NET Elevation of Privilege VulnerabilityImportant7.3NoNoEoP
CVE-2026-70190.NET Elevation of Privilege VulnerabilityImportant7.3NoNoEoP
CVE-2026-70165.NET Elevation of Privilege VulnerabilityImportant6.7NoNoEoP
CVE-2026-85363.NET Framework Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-70007.NET Framework Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70035.NET Framework Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70194.NET Framework Security Feature Bypass VulnerabilityImportant6.5NoNoSFB
CVE-2026-97801.NET Framework Tampering VulnerabilityImportant7.5NoNoTampering
CVE-2026-96232.NET Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-96229.NET Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-66822.NET Information Disclosure VulnerabilityImportant5.9NoNoInfo
CVE-2026-96234.NET Information Disclosure VulnerabilityImportant5.3NoNoInfo
CVE-2026-70174.NET Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83520.NET Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-87697.NET Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-96224.NET Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-96235.NET Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70197.NET Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-96237.NET Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-96957.NET Security Feature Bypass VulnerabilityImportant8.8NoNoSFB
CVE-2026-96238.NET Security Feature Bypass VulnerabilityImportant6.5NoNoSFB
CVE-2026-83666Active Directory Certificate Services (AD CS) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83645Active Directory Federation Services (AD FS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-85319Active Directory Federation Services (AD FS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-85321Active Directory Federation Services (AD FS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-85324Active Directory Federation Services (AD FS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-97788Active Directory Federation Services (AD FS) Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-69982Active Directory Federation Services (AD FS) Security Feature Bypass VulnerabilityImportant5.9NoNoSFB
CVE-2026-70005Active Directory Federation Services (AD FS) Security Feature Bypass VulnerabilityImportant5.9NoNoSFB
CVE-2026-96252Active Directory Federation Services (AD FS) Spoofing VulnerabilityImportant9.1NoNoSpoofing
CVE-2026-83674Active Directory Federation Services (AD FS) Spoofing VulnerabilityImportant8.1NoNoSpoofing
CVE-2026-83511Active Directory Federation Services (AD FS) Spoofing VulnerabilityImportant7.4NoNoSpoofing
CVE-2026-103576Active Directory Federation Services (AD FS) Spoofing VulnerabilityImportant6.5NoNoSpoofing
CVE-2026-83646Active Directory Federation Services (AD FS) Spoofing VulnerabilityImportant4.8NoNoSpoofing
CVE-2026-70159ASP.NET Core Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70181ASP.NET Core Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70186ASP.NET Core Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96233ASP.NET Core Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96236ASP.NET Core Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70196ASP.NET Core Denial of Service VulnerabilityImportant5.9NoNoDoS
CVE-2026-70175ASP.NET Core Elevation Of Privilege VulnerabilityImportant8.1NoNoEoP
CVE-2026-70179ASP.NET Core Elevation Of Privilege VulnerabilityImportant7.5NoNoEoP
CVE-2026-70183ASP.NET Core Elevation Of Privilege VulnerabilityImportant7.5NoNoEoP
CVE-2026-102870ASP.NET Core Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-96230ASP.NET Core Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70188ASP.NET Core Security Feature Bypass VulnerabilityImportant9.1NoNoSFB
CVE-2026-88092ASP.NET Core Tampering VulnerabilityImportant9.4NoNoTampering
CVE-2026-85916Azure Active Directory Information Disclosure VulnerabilityImportant6.2NoNoInfo
CVE-2026-96204Azure Arc Elevation of Privilege VulnerabilityImportant6.5NoNoEoP
CVE-2026-100207Azure CycleCloud Remote Code Execution VulnerabilityImportant7.3NoNoRCE
CVE-2026-69877Azure DevOps Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-85891Azure HDInsight Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-85925Azure Key Vault Client SDK Elevation of Privilege VulnerabilityImportant8.2NoNoEoP
CVE-2026-88132Azure Key Vault Information Disclosure VulnerabilityImportant5.9NoNoInfo
CVE-2026-85922Azure Key Vault Security Feature Bypass VulnerabilityImportant7.4NoNoSFB
CVE-2026-88094Azure Storage Library Elevation of Privilege VulnerabilityImportant8.1NoNoEoP
CVE-2026-85861Clipboard User Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85863Clipboard User Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85912Clipboard User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88075Configuration Manager Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-83846Connected Devices Platform Service (Cdpsvc) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-95943Connected Devices Platform Service (Cdpsvc) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69880Desktop Window Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69926Desktop Window Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70228Desktop Window Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70255Desktop Window Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88093Desktop Window Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96108Desktop Window Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70234Desktop Window Manager Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69974Desktop Window Manager Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-102226Dynamics Business Central Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-105728Dynamics Business Central Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-100214Dynamics Business Central Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83670Function Discovery Service (fdwsd.dll) Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-69326Graphic Fonts Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105003HID Class Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-97804HID Class Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-105006HID Class Driver Elevation of Privilege VulnerabilityImportant6.4NoNoEoP
CVE-2026-83569HID Parser Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70128HID Parser Library Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83887HID Parser Library Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83898HID Parser Library Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83904HID Parser Library Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70208HTTP.sys Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83705HTTP.sys Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83714HTTP.sys Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70247HTTP.sys Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-85856Internet Connection Sharing (ICS) Remote Code Execution VulnerabilityImportant7.1NoNoRCE
CVE-2026-83741Internet Explorer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69963Kernel Streaming Service Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69966Kernel Streaming Service Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69964Kernel Streaming Service Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69970Kernel Streaming Service Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83847Microsoft Account Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85329Microsoft Account Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69454Microsoft Azure Attestation service and Device Health Attestation Service Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-69577Microsoft Azure Attestation service and Device Health Attestation Service Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-96844Microsoft Bluetooth Driver Elevation of Privilege VulnerabilityImportant8NoNoEoP
CVE-2026-83868Microsoft Bluetooth Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83760Microsoft Bluetooth Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69909Microsoft COM for Windows Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-105726Microsoft Defender Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70264Microsoft Defender Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-88158Microsoft Digest Authentication Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-105727Microsoft Dynamics 365 Business Central Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-77910Microsoft Exchange Server Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-96940Microsoft Exchange Server Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-87692Microsoft Exchange Server Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-87695Microsoft Exchange Server Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-87696Microsoft Exchange Server Elevation of Privilege VulnerabilityImportant7.5NoNoEoP
CVE-2026-70279Microsoft Exchange Server Spoofing VulnerabilityImportant9.3NoNoSpoofing
CVE-2026-88102Microsoft Failover Cluster Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-96864Microsoft Failover Cluster Virtual Driver Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-70123Microsoft Graphics Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85338Microsoft Graphics Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102209Microsoft Graphics Component Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88101Microsoft Input Method Editor (IME) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-78459Microsoft Internet Information Services Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83778Microsoft Internet Messaging API Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83919Microsoft Internet Messaging API Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-70049Microsoft Intune Elevation of Privilege VulnerabilityImportant8NoNoEoP
CVE-2026-83722Microsoft Local Security Authority (LSA) Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-87710Microsoft Local Security Authority (LSA) Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102204Microsoft Microsoft Defender for Endpoint Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70343Microsoft MPEG-2 Video Extension Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-94506Microsoft Office Access Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-102849Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-102850Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105591Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105593Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105595Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105596Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105597Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105598Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105716Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105717Microsoft Office Access Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105592Microsoft Office Access Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-105714Microsoft Office Access Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-88109Microsoft Office Click-To-Run Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-97774Microsoft Office Click-to-Run Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85340Microsoft Office Click-to-Run Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70276Microsoft Office Click-to-Run Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69922Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70219Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88151Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88153Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88154Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88172Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88175Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88184Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88190Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88192Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88195Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88201Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97740Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97743Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97760Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97779Microsoft Office Excel Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70214Microsoft Office Excel Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-97014Microsoft Office Excel Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-100212Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70254Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-77902Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88145Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97003Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97004Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97007Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97008Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97010Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97011Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97017Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97738Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97746Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97747Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97748Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97750Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97751Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97752Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97754Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97757Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97762Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97763Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97766Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97768Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97769Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97770Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97771Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97772Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97773Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97775Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97777Microsoft Office Excel Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97009Microsoft Office Excel Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-105731Microsoft Office Graphics Component Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85881Microsoft Office Graphics Elevation of Privilege VulnerabilityImportant8NoNoEoP
CVE-2026-96997Microsoft Office OneNote Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102858Microsoft Office OneNote Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97781Microsoft Office OneNote Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70281Microsoft Office Outlook Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-70256Microsoft Office Outlook Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70257Microsoft Office Outlook Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70282Microsoft Office Outlook Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97012Microsoft Office Outlook Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88183Microsoft Office PowerPoint Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88203Microsoft Office PowerPoint Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97005Microsoft Office PowerPoint Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-97744Microsoft Office PowerPoint Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-105599Microsoft Office PowerPoint Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-88196Microsoft Office Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88197Microsoft Office Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-102860Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-102861Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-102862Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-102863Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-70246Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-70266Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-88198Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-88200Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-96044Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-70202Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant7.5NoNoEoP
CVE-2026-70251Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant7.5NoNoEoP
CVE-2026-88206Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant7.5NoNoEoP
CVE-2026-105720Microsoft Office SharePoint Elevation of Privilege VulnerabilityImportant4.3NoNoEoP
CVE-2026-102865Microsoft Office SharePoint Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70259Microsoft Office SharePoint Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70298Microsoft Office SharePoint Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-85932Microsoft Office SharePoint Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70217Microsoft Office SharePoint Information Disclosure VulnerabilityImportant4.9NoNoInfo
CVE-2026-69943Microsoft Office SharePoint Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-85900Microsoft Office SharePoint Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88155Microsoft Office SharePoint Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88166Microsoft Office SharePoint Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-105013Microsoft Office SharePoint Remote Code Execution VulnerabilityImportant7.4NoNoRCE
CVE-2026-70267Microsoft Office SharePoint Remote Code Execution VulnerabilityImportant7.2NoNoRCE
CVE-2026-88163Microsoft Office SharePoint Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97783Microsoft Office SharePoint Spoofing VulnerabilityImportant8.1NoNoSpoofing
CVE-2026-88204Microsoft Office SharePoint Spoofing VulnerabilityImportant7.3NoNoSpoofing
CVE-2026-105713Microsoft Office SharePoint Spoofing VulnerabilityImportant5.7NoNoSpoofing
CVE-2026-102859Microsoft Office SharePoint Spoofing VulnerabilityImportant4.6NoNoSpoofing
CVE-2026-102864Microsoft Office SharePoint Spoofing VulnerabilityImportant4.6NoNoSpoofing
CVE-2026-88208Microsoft Office SharePoint Spoofing VulnerabilityImportant4.6NoNoSpoofing
CVE-2026-88209Microsoft Office SharePoint Spoofing VulnerabilityImportant4.6NoNoSpoofing
CVE-2026-97782Microsoft Office SharePoint Tampering VulnerabilityImportant6.8NoNoTampering
CVE-2026-96995Microsoft Office Word Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70206Microsoft Office Word Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70263Microsoft Office Word Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88167Microsoft Office Word Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-88169Microsoft Office Word Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-102867Microsoft Office Word Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70268Microsoft Office Word Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70287Microsoft Office Word Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70301Microsoft Office Word Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70302Microsoft Office Word Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83891Microsoft Office Word Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88150Microsoft Office Word Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88186Microsoft Office Word Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88202Microsoft Office Word Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70220Microsoft Office Word Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-96996Microsoft Office Word Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-97001Microsoft Office Word Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-105715Microsoft Office Word Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-88210Microsoft Office Word Security Feature Bypass VulnerabilityImportant7.8NoNoSFB
CVE-2026-70163Microsoft OpenSSH for Windows Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-83769Microsoft OpenSSH for Windows Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83871Microsoft OpenSSH for Windows Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-97811Microsoft OpenSSH for Windows Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83923Microsoft OpenSSH for Windows Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88157Microsoft OpenSSH for Windows Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83754Microsoft OpenSSH for Windows Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-97816Microsoft OpenSSH for Windows Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-70092Microsoft PostScript Printer Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70110Microsoft PostScript Printer Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70109Microsoft PostScript Printer Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70213Microsoft Power Apps Remote Code Execution VulnerabilityImportant8NoNoRCE
CVE-2026-83578Microsoft PowerShell Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-85817Microsoft PowerShell Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-96251Microsoft PowerShell Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70052Microsoft PowerShell Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-70185Microsoft PowerShell Security Feature Bypass VulnerabilityImportant8.8NoNoSFB
CVE-2026-85805Microsoft PowerShell Security Feature Bypass VulnerabilityImportant6.5NoNoSFB
CVE-2026-96303Microsoft PowerShell Security Feature Bypass VulnerabilityImportant6.5NoNoSFB
CVE-2026-96188Microsoft PowerToys Elevation of Privilege VulnerabilityImportant7.3NoNoEoP
CVE-2026-83681Microsoft PowerToys Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-85790Microsoft QUIC Information Disclosure VulnerabilityImportant5.9NoNoInfo
CVE-2026-103577Microsoft QUIC Security Feature Bypass VulnerabilityImportant7.5NoNoSFB
CVE-2026-88193Microsoft Scripting Engine Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-105719Microsoft SharePoint Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-67626Microsoft SQL Server Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-88084Microsoft SQL Server Denial of Service VulnerabilityImportant5.3NoNoDoS
CVE-2026-94520Microsoft SQL Server Denial of Service VulnerabilityImportant4.9NoNoDoS
CVE-2026-68883Microsoft SQL Server Elevation of Privilege VulnerabilityImportant8.5NoNoEoP
CVE-2026-85876Microsoft SQL Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85919Microsoft SQL Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88082Microsoft SQL Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88088Microsoft SQL Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88085Microsoft SQL Server Elevation of Privilege VulnerabilityImportant6.4NoNoEoP
CVE-2026-85888Microsoft SQL Server Information Disclosure VulnerabilityImportant7.7NoNoInfo
CVE-2026-88081Microsoft SQL Server Information Disclosure VulnerabilityImportant7.7NoNoInfo
CVE-2026-88086Microsoft SQL Server Information Disclosure VulnerabilityImportant5.3NoNoInfo
CVE-2026-67628Microsoft SQL Server Information Disclosure VulnerabilityImportant4.9NoNoInfo
CVE-2026-65674Microsoft SQL Server Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-67625Microsoft SQL Server Remote Code Execution VulnerabilityImportant8.5NoNoRCE
CVE-2026-85886Microsoft SQL Server Remote Code Execution VulnerabilityImportant8.5NoNoRCE
CVE-2026-88083Microsoft SQL Server Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-70189Microsoft SQL Server Remote Code Execution VulnerabilityImportant6.7NoNoRCE
CVE-2026-88089Microsoft SQL Server Remote Code Execution VulnerabilityImportant6.7NoNoRCE
CVE-2026-83945Microsoft SQL Server Remote Code Execution VulnerabilityImportant6.6NoNoRCE
CVE-2026-70260Microsoft Trace Data Helper Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70261Microsoft Trace Data Helper Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-102199Microsoft Windows Codecs Library Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-102201Microsoft Windows Media Foundation Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70131Microsoft Windows Media Foundation Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70278Microsoft Windows Media Foundation Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96186Microsoft Windows Media Foundation Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70044Microsoft Windows Media Foundation Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83517Microsoft Windows Media Foundation Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-85814Microsoft Windows Media Foundation Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-70258Microsoft Windows Media Foundation Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-87712Microsoft Windows QoS Scheduler Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-105010Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant9.8NoNoEoP
CVE-2026-70177Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83704Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83829Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83850Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85869Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88182Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88191Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96324Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96911Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70086Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70115Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70136Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70150Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70156Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88160Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96937Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-108136Microsoft Windows Search Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70141Microsoft Windows Search Component Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70173Microsoft Windows Search Component Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83686Microsoft Windows Search Component Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96910Microsoft Windows Search Component Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83725Microsoft Windows Search Component Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-69978Microsoft Windows VMSwitch Denial of Service VulnerabilityImportant5.6NoNoDoS
CVE-2026-83935Microsoft XML Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83914Microsoft XML Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-96861Network Device Enrollment Service (NDES) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96866Network Device Enrollment Service (NDES) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-85323Network Device Enrollment Service (NDES) Spoofing VulnerabilityImportant6.8NoNoSpoofing
CVE-2026-83655Network Policy Server (NPS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96246Network Policy Server (NPS) Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-100222Network Policy Server (NPS) Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-85806Network Policy Server (NPS) Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-85371Network Policy Server (NPS) Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-85799Network Policy Server (NPS) Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-70207Network Policy Server (NPS) Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-85811Network Policy Server (NPS) Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-85864Python Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69977Quality Windows Audio/Video Experience (QWAVE) service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85943Reliable Multicast Transport Driver (RMCAST) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-84015Remote Access Point-to-Point Protocol (PPP) EAP-TLS Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-103575Remote Desktop Client Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83688Remote Desktop Client Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-69976Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69984Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69986Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69987Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69988Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69991Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69994Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69995Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69996Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69997Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-69998Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-70004Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-70006Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-70012Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-97789Remote Desktop Client Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-108458Remote Desktop Client Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-96321Remote Desktop Display Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-84007Remote Desktop Gateway Service Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-100218Remote Desktop Gateway Service Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-69992Remote Desktop Services Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-83635Role: DNS Server Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-88122Role: DNS Server Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-88123Role: DNS Server Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-88125Role: DNS Server Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-88129Role: DNS Server Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-88130Role: DNS Server Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-108127Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-108128Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-108129Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97817Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97819Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97820Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97821Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97822Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97823Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97824Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97825Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97826Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97827Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97828Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97829Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97831Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97832Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97833Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97834Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97835Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97836Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97837Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97838Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97839Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97840Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97841Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97842Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97843Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97844Role: DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70087Role: DNS Server Security Feature Bypass VulnerabilityImportant5.5NoNoSFB
CVE-2026-103560Role: DNS Server Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-70071Role: DNS Server Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-70083Role: DNS Server Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-70085Role: DNS Server Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-96926Role: DNS Server Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-96300RPC Endpoint Mapper Service Denial of Service VulnerabilityImportant5.9NoNoDoS
CVE-2026-83518RPC Runtime Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83908RPC Runtime Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83515RPC Runtime Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-83910RPC Runtime Library Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-88219RPC Runtime Library Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-102203RPC Runtime Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83506Servicing Stack Updates Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83863Servicing Stack Updates Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85318Servicing Stack Updates Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85365Servicing Stack Updates Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96939Servicing Stack Updates Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83719Servicing Stack Updates Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85835Servicing Stack Updates Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83746Skype for Business Elevation of Privilege VulnerabilityImportant8.1NoNoEoP
CVE-2026-85873Skype for Business Elevation of Privilege VulnerabilityImportant6.5NoNoEoP
CVE-2026-70297Skype for Business Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-108464Software Protection Platform (SPP) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96956SQL Server Elevation of Privilege VulnerabilityImportant8NoNoEoP
CVE-2026-94512SQL Server Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-69867SQLite Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-105732SysInternals Elevation of Privilege VulnerabilityImportant7.3NoNoEoP
CVE-2026-100205SysInternals Elevation of Privilege VulnerabilityImportant7.1NoNoEoP
CVE-2026-105729SysInternals Elevation of Privilege VulnerabilityImportant7.1NoNoEoP
CVE-2026-49785UEFI Secure Boot Security Feature Bypass VulnerabilityImportant7.8NoNoSFB
CVE-2026-70252Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege VulernabilityImportant7NoNoEoP
CVE-2026-103555Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-109453Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102229Visual Studio Code Information Disclosure VulnerabilityImportant6.8NoNoInfo
CVE-2026-102238Visual Studio Code Remote Code Execution VulnerabilityImportant9.6NoNoRCE
CVE-2026-102235Visual Studio Code Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-69370Visual Studio Code Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70098Visual Studio Code Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-102233Visual Studio Code Security Feature Bypass VulnerabilityImportant7.8NoNoSFB
CVE-2026-102231Visual Studio Code Security Feature Bypass VulnerabilityImportant7.7NoNoSFB
CVE-2026-102234Visual Studio Code Security Feature Bypass VulnerabilityImportant7.4NoNoSFB
CVE-2026-102232Visual Studio Code Security Feature Bypass VulnerabilityImportant7NoNoSFB
CVE-2026-102851Visual Studio Code Security Feature Bypass VulnerabilityImportant6.1NoNoSFB
CVE-2026-103572Visual Studio Tools for Applications and SQL Server Management Studio Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-85846Web Account Manager Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88136Web Distributed Authoring and Versioning (WEBDAV) Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-102217WebDAV Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-70262WebDAV Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-88126WebDAV Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88135WebDAV Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96843WebDAV Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96847WebDAV Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85370WebDAV Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85827WebDAV Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85828WebDAV Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88137WebDAV Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-96846WebDAV Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-87714WebDAV Security Feature Bypass VulnerabilityImportant6.5NoNoSFB
CVE-2026-83721Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83732Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83757Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83762Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83755Win32k Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70211Win32k Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70284Win32k Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70288Win32k Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70292Win32k Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70293Win32k Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70294Win32k Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70295Win32k Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96113Windows Domain Name Service Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83869Windows Domain Name Service Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-70167Windows Domain Name Service Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83642Windows Domain Name Service Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-85903Windows Domain Name Service Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88112Windows Domain Name Service Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88114Windows Domain Name Service Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88116Windows Domain Name Service Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70127Windows Domain Name Service Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-83647Windows Active Directory Domain Services Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-83648Windows Active Directory Domain Services Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-83667Windows Active Directory Domain Services Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-88165Windows Active Directory Domain Services Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-84019Windows Advanced Rasterization Platform Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83870Windows Aggregated Data Platform Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69923Windows AI Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85866Windows ALPC Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-70225Windows Ancillary Function Driver for WinSock Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70245Windows Ancillary Function Driver for WinSock Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70168Windows Ancillary Function Driver for WinSock Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70205Windows Ancillary Function Driver for WinSock Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70237Windows Ancillary Function Driver for WinSock Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83738Windows Ancillary Function Driver for WinSock Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88149Windows Ancillary Function Driver for WinSock Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70195Windows Ancillary Function Driver for WinSock Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-72955Windows Application Compatibility Cache Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69945Windows AppX Deployment Extensions Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-85849Windows AppX Deployment Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85934Windows AppX Deployment Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69914Windows AppX Deployment Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69969Windows AppX Deployment Service Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-69979Windows AppX Deployment Service Security Feature Bypass VulnerabilityImportant5.5NoNoSFB
CVE-2026-69905Windows AppX Deployment Service Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-96220Windows Assigned Access Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-97799Windows Audio Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70118Windows Audio Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70140Windows Audio Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70230Windows Audio Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83644Windows Audio Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83571Windows Audio Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96314Windows Audio Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-108134Windows Autopilot Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96215Windows Autopilot Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85832Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85843Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85848Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88118Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88152Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88146Windows Background Intelligent Transfer Service (BITS) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88142Windows Background Intelligent Transfer Service (BITS) Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88159Windows Background Intelligent Transfer Service (BITS) Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88173Windows Background Intelligent Transfer Service (BITS) Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-88121Windows Background Intelligent Transfer Service (BITS) Remote Code Execution VulnerabilityImportant8NoNoRCE
CVE-2026-70184Windows Backup Engine Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-108135Windows Backup Engine Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-62687Windows Backup Engine Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70299Windows Bind Filter Driver Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-70274Windows Bind Filter Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83692Windows Bind Filter Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88168Windows Bind Filter Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83852Windows Bind Filter Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83900Windows Bind Filter Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85812Windows Bind Filter Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85831Windows Biometric Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83634Windows BitLocker Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88070Windows BitLocker Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85920Windows BitLocker Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96909Windows BitLocker Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83500Windows BitLocker Security Feature Bypass VulnerabilityImportant6.1NoNoSFB
CVE-2026-83838Windows Bluetooth A2DP driver Elevation of Privilege VulnerabilityImportant8NoNoEoP
CVE-2026-83776Windows Bluetooth Driver Elevation of Privilege VulnerabilityImportant6.8NoNoEoP
CVE-2026-83827Windows Bluetooth Port Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-87713Windows Bluetooth Port Driver Remote Code ExecutionImportant7.5NoNoEoP
CVE-2026-70126Windows Bluetooth Port Driver Remote Code ExecutionImportant7.1NoNoRCE
CVE-2026-83777Windows Bluetooth Service Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-83739Windows Bluetooth Service Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-102196Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88105Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-97809Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102193Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102195Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102197Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-103554Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-103565Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-105722Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88103Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88113Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96919Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-97808Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70122Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant6.5NoNoEoP
CVE-2026-97806Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-97807Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-108461Windows Broadcast DVR User Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70148Windows Broadcast DVR User Service Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-103567Windows Broadcast DVR User Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85938Windows Broadcast DVR User Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83771Windows Camera Frame Server Monitor Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-83753Windows Camera Frame Server Monitor Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85803Windows Camera Frame Server Monitor Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85367Windows Cash Drawer Protocol Provider Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83780Windows CCFFilter Driver Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-85377Windows CD-ROM Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83888Windows CD-ROM Driver Elevation of Privilege VulnerabilityImportant6.5NoNoEoP
CVE-2026-70041Windows CD-ROM Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70275Windows CD-ROM File System Driver Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-69850Windows Certificates Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69840Windows Certificates Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69949Windows Client for NFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70113Windows Client for NFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69940Windows Client for NFS Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-69955Windows Client for NFS Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-96912Windows Client License Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-100201Windows Client License Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70149Windows Client Side Caching driver (csc.sys) Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-96948Windows Client Side Caching driver (csc.sys) Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70068Windows Client-Side Caching (CSC) Service Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-83698Windows Client-Side Caching (CSC) Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83699Windows Client-Side Caching (CSC) Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83580Windows Client-Side Caching (CSC) Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69795Windows Clipboard Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83764Windows Clipboard User Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83893Windows Clipboard User Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83696Windows Cloud Files Mini Filter Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88106Windows Cloud Files Mini Filter Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88107Windows Cloud Files Mini Filter Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83830Windows COM+ Event System Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83848Windows COM+ Event System Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96933Windows COM+ Event System Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83785Windows COM+ Event System Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70233Windows Common Log File System Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85355Windows Common Log File System Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85868Windows Common Log File System Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85870Windows Common Log File System Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83835Windows Common Log File System Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85823Windows Composite Image File System Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85824Windows Composite Image File System Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70169Windows Connected Devices Platform Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83687Windows Connected User Experiences and Telemetry Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70223Windows Console Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102202Windows Container Isolation FS Filter Driver (unionfs.sys) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-97792Windows Container Isolation FS Filter Driver (unionfs.sys) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-97794Windows Container Isolation FS Filter Driver (unionfs.sys) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-97787Windows Container Isolation FS Filter Driver (unionfs.sys) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-97810Windows Container Isolation FS Filter Driver (unionfs.sys) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-97790Windows Container Isolation FS Filter Driver (unionfs.sys) Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-70270Windows Container Isolation FS Filter Driver Elevation of Privilege VulnerabilityImportant5.5NoNoEoP
CVE-2026-69918Windows Core Messaging Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-83587Windows Core Messaging Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70580Windows Credential Guard Spoofing VulnerabilityImportant8.8NoNoSpoofing
CVE-2026-69736Windows Credential Manager Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-103568Windows Credential Providers Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69919Windows Cryptographic Services Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70055Windows Cryptographic Services Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70014Windows Cryptographic Services Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-88096Windows DCOM Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83679Windows Defender Firewall Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85332Windows Device Association Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83710Windows Device Association Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-84014Windows Device Association Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85342Windows Device Association Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85352Windows Device Association Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85904Windows Device Association Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85331Windows Device Association Service Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70227Windows Device Association Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85336Windows Device Association Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85815Windows Device Association Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96854Windows Device Association Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83792Windows Device Install Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83877Windows Devices Human Interface Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83677Windows DHCP Client Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-83665Windows DHCP Server Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70201Windows DHCP Server Denial of Service VulnerabilityImportant5.5NoNoDoS
CVE-2026-83691Windows DHCP Server Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70066Windows DHCP Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96320Windows DHCP Server Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-70069Windows DHCP Server Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-69830Windows DHCP Server Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-70058Windows DHCP Server Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-85841Windows DHCP Server Remote Code Execution VulnerabilityImportant6.6NoNoRCE
CVE-2026-83787Windows DHCP Server Security Feature Bypass VulnerabilityImportant5.5NoNoSFB
CVE-2026-85865Windows DHCP Server Security Feature Bypass VulnerabilityImportant5.5NoNoSFB
CVE-2026-83915Windows Diagnostic Policy Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83896Windows Direct Composition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83902Windows Direct Composition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83903Windows Direct Composition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83912Windows Direct Composition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83922Windows Direct Composition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85902Windows Direct Composition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85906Windows Direct Composition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70151Windows Direct Composition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70021Windows Direct Composition Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-105723Windows Distributed File System (DFS) Elevation of Privilege VulnerabilityImportant7.5NoNoEoP
CVE-2026-96938Windows Distributed File System (DFS) Elevation of Privilege VulnerabilityImportant6.7NoNoEoP
CVE-2026-85931Windows Distributed File System (DFS) Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-85798Windows Distributed File System (DFS) Remote Code Execution VulnerabilityImportant7.2NoNoRCE
CVE-2026-70082Windows DNS Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70079Windows DNS Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70155Windows DNS Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70166Windows DNS Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-70074Windows DNS Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70119Windows DNS Remote Code Execution VulnerabilityImportant6.5NoNoRCE
CVE-2026-70244Windows DNS Server Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-83889Windows DNS Server Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83726Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88128Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88177Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88179Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88180Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88181Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88188Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88189Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88194Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85853Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85854Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85855Windows DWM Core Library Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83765Windows DWM Core Library Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-84016Windows EAPHost Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85914Windows Embedded Mode Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96932Windows Embedded Mode Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83784Windows Encrypting File System (EFS) Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-85791Windows Encrypting File System (EFS) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83683Windows Encrypting File System (EFS) Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-83565Windows Encrypting File System (EFS) Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83759Windows Encrypting File System (EFS) Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-88162Windows Encrypting File System (EFS) Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-69452Windows Enterprise App Management Elevation of Privilege VulnerabilityImportant7.1NoNoEoP
CVE-2026-69354Windows Error Reporting Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69363Windows Error Reporting Elevation of Privilege VulnerabilityImportant8NoNoEoP
CVE-2026-70103Windows Error Reporting Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83669Windows Error Reporting Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83826Windows Error Reporting Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83840Windows Error Reporting Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85800Windows Error Reporting Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69387Windows Error Reporting Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83689Windows Error Reporting Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83750Windows Error Reporting Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85354Windows Error Reporting Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83658Windows Error Reporting Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83747Windows Error Reporting Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83519Windows Error Reporting Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83693Windows Error Reporting Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83748Windows Error Reporting Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-97815Windows Error Reporting Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83643Windows Error Reporting Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83758Windows Error Reporting Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-83916Windows Error Reporting Remote Code Execution VulnerabilityImportant7NoNoRCE
CVE-2026-97798Windows Error Reporting Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83715Windows Error Reporting Tampering VulnerabilityImportant7.1NoNoTampering
CVE-2026-83695Windows Event Logging Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83723Windows Event Logging Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-95904Windows Event Logging Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83856Windows Event Logging Service Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-70134Windows Event Tracing Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83707Windows Event Tracing Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83874Windows Event Tracing Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83836Windows Event Tracing Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-70235Windows Event Tracing Spoofing VulnerabilityImportant5.5NoNoSpoofing
CVE-2026-85840Windows Event Viewer Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-83881Windows exFAT File System Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85822Windows exFAT File System Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102192Windows Failover Cluster Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96945Windows Failover Cluster Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-88099Windows Failover Cluster Denial of Service VulnerabilityImportant5.9NoNoDoS
CVE-2026-85826Windows Fast FAT Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70277Windows Fast FAT File System Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-87707Windows Fax and Scan Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83860Windows GDI Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-69884Windows GDI Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83651Windows GDI Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-85797Windows GDI Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70089Windows GDI Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83929Windows GDI Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83583Windows Geotag Broker Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70286Windows Graphics Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85901Windows Graphics Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85908Windows Graphics Component Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96118Windows Graphics Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102194Windows Graphics Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88110Windows Graphics Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83582Windows Graphics Kernel Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-100217Windows Group Policy Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83932Windows Group Policy Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85884Windows Health and Optimized Experiences Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96183Windows Health and Optimized Experiences Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83740Windows Hello Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83790Windows Hello Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83853Windows Hello Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83849Windows Hello Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83907Windows Hello Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70280Windows Hello Security Feature Bypass VulnerabilityImportant4.4NoNoSFB
CVE-2026-83926Windows Hello Security Feature Bypass VulnerabilityImportant4.4NoNoSFB
CVE-2026-96248Windows Host Guardian Service Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-88072Windows Host Guardian Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-87709Windows Host Guardian Service Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-83875Windows Human Interface Device Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83884Windows Human Interface Device Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83892Windows Human Interface Device Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70248Windows Hyper-V Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-83636Windows Hyper-V Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-85369Windows Hyper-V Elevation of Privilege VulnerabilityImportant8.2NoNoEoP
CVE-2026-70023Windows Hyper-V Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85343Windows Hyper-V Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88071Windows Hyper-V Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96223Windows Hyper-V Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83839Windows Hyper-V Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83671Windows Hyper-V Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-97813Windows Hyper-V Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-83716Windows Hyper-V Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83931Windows Hyper-V Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-87705Windows Hyper-V Security Feature Bypass VulnerabilityImportant7.4NoNoSFB
CVE-2026-83766Windows Hyper-V Security Feature Bypass VulnerabilityImportant4.2NoNoSFB
CVE-2026-83728Windows Hyper-V Spoofing VulnerabilityImportant8.8NoNoSpoofing
CVE-2026-103569Windows IKE Extension Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-83521Windows IKE Extension Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-83522Windows IKE Extension Spoofing VulnerabilityImportant8.1NoNoSpoofing
CVE-2026-85842Windows Image Acquisition Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85930Windows Image Acquisition Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83523Windows Image Acquisition Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-96859Windows Imaging Component Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69886Windows Imaging Component Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-77496Windows Imaging Component Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83763Windows Input System Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69471Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83767Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83779Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85358Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85366Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85796Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-87694Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-87700Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-87711Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88080Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96308Windows Installer Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70272Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83676Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83680Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83702Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83708Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83717Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83718Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83752Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83775Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83899Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85361Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85364Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85941Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-87693Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-87704Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-87708Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-87715Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88076Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88124Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96302Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96305Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96307Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69635Windows Installer Elevation of Privilege VulnerabilityImportant6.6NoNoEoP
CVE-2026-108468Windows Installer Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85374Windows Installer Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85830Windows Installer Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83672Windows Installer Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-96244Windows Internal System User Profile Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83845Windows Internet (wininet.dll) Spoofing VulnerabilityImportant8.4NoNoSpoofing
CVE-2026-83865Windows Internet (wininet.dll) Tampering VulnerabilityImportant4.7NoNoTampering
CVE-2026-97830Windows Internet Information Services Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-70024Windows Internet Information Services Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83795Windows Internet Key Exchange (IKE) Extension Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-83843Windows Internet Key Exchange (IKE) Extension Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-83685Windows Internet Key Exchange (IKE) Extension Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-70008Windows IP Over USB Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70011Windows IP Over USB Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70031Windows iSCSI Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-69644Windows iSCSI Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69721Windows iSCSI Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69521Windows iSCSI Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-69634Windows iSCSI Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-69705Windows iSCSI Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-69883Windows iSCSI Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-70013Windows iSCSI Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-70038Windows iSCSI Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-70095Windows iSCSI Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-70064Windows Kerberos Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70241Windows Kerberos Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83720Windows Kerberos Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-108132Windows Kerberos Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70170Windows Kernel Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-108466Windows Kernel Denial of Service VulnerabilityImportant5.3NoNoDoS
CVE-2026-70111Windows Kernel Elevation of Privilege VulnerabilityImportant8.1NoNoEoP
CVE-2026-69898Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70106Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70114Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70121Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70303Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83690Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83735Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83768Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83796Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83833Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83882Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83913Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83918Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85836Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85837Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85850Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85945Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88134Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96312Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96317Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96929Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102207Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70160Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70243Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83675Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83924Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85372Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88139Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88141Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96216Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96868Windows Kernel Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-103578Windows Kernel Elevation of Privilege VulnerabilityImportant6.8NoNoEoP
CVE-2026-83736Windows Kernel Elevation of Privilege VulnerabilityImportant5.5NoNoEoP
CVE-2026-97803Windows Kernel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102187Windows Kernel Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70199Windows Kernel Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70232Windows Kernel Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70063Windows Kernel Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-70077Windows Kernel Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-83925Windows Kernel Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-108462Windows Kernel Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85939Windows Kernel Security Feature Bypass VulnerabilityImportant5.3NoNoSFB
CVE-2026-83573Windows Kernel-Mode Driver Elevation of Privilege VulnerabilityImportant6.8NoNoEoP
CVE-2026-83568Windows Kernel-Mode Drivers Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83637Windows Kernel-Mode Drivers Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83837Windows Kernel-Mode Drivers Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85871Windows Kernel-Mode Drivers Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96915Windows Kernel-Mode Drivers Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83834Windows Kernel-Mode Drivers Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69971Windows Kernel-Mode Drivers Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85857Windows Kernel-Mode Drivers Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96247Windows Kernel-Mode Drivers Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96849Windows Kernel-Mode Drivers Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-68836Windows kernel32.dll Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69650Windows Key Distribution Center Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69640Windows Key Distribution Center Security Feature Bypass VulnerabilityImportant5.3NoNoSFB
CVE-2026-88140Windows Key Storage Provider Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69506Windows Key Storage Provider Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-69639Windows libarchive Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-69985Windows libarchive Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70062Windows libarchive Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-69968Windows libarchive Tampering VulnerabilityImportant6.5NoNoTampering
CVE-2026-69973Windows libarchive Tampering VulnerabilityImportant6.5NoNoTampering
CVE-2026-88161Windows Local Security Authority (LSA) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83516Windows Local Security Authority Subsystem Service (LSASS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-83649Windows Local Security Authority Subsystem Service (LSASS) Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-70015Windows Local Security Authority Subsystem Service (LSASS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96219Windows Local Security Authority Subsystem Service (LSASS) Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83928Windows Local Security Authority Subsystem Service (LSASS) Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83783Windows Management Instrumentation Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88091Windows Management Instrumentation Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96856Windows Management Instrumentation Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83724Windows Management Instrumentation Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85362Windows Management Instrumentation Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85852Windows Management Instrumentation Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96851Windows Management Instrumentation Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-87691Windows Management Services Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83641Windows Media Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83650Windows Media Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96096Windows Media Player Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-96071Windows Media Remote Code Execution VulnerabilityImportant7.5NoNoRCE
CVE-2026-85859Windows Message Queuing Queue Manager Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-85860Windows Message Queuing Queue Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85334Windows Message Queuing Queue Manager Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-96921Windows Message Queuing Queue Manager Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85874Windows Message Queuing Queue Manager Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-83828Windows MIDI Service Module Elevation of Privileges VulnerabilityImportant7.8NoNoEoP
CVE-2026-83751Windows MIDI Service Module Elevation of Privileges VulnerabilityImportant7NoNoEoP
CVE-2026-88079Windows MIDI Service Module Elevation of Privileges VulnerabilityImportant7NoNoEoP
CVE-2026-83773Windows MIDI Service Module Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-97800Windows Mobile Broadband Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70216Windows Mobile Device Management Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-108133Windows Modern Device Management (MDM) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83654Windows Modern Device Management (MDM) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85833Windows Modern Device Management (MDM) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-108396Windows Modern Device Management (MDM) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96850Windows Modern Device Management (MDM) Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83657Windows Modern Device Management (MDM) Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-96855Windows Modern Device Management (MDM) Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-83656Windows Modern Device Management (MDM) Tampering VulnerabilityImportant4.7NoNoTampering
CVE-2026-83697Windows Modern Device Management (MDM) Tampering VulnerabilityImportant4.7NoNoTampering
CVE-2026-105007Windows NDIS Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-70054Windows NetBIOS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70072Windows Netlogon Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-70025Windows Netlogon Denial of Service VulnerabilityImportant5.3NoNoDoS
CVE-2026-70090Windows Netlogon Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96209Windows Network File System Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69675Windows Network File System Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-102186Windows Network File System Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-70143Windows Network File System Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-96311Windows Network List Service Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-83862Windows Network Load Balancing Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83854Windows Notification Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83700Windows Now Playing Session Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83701Windows Now Playing Session Manager Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83706Windows NTFS Elevation of Privilege VulnerabilityImportant6.7NoNoEoP
CVE-2026-69916Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70010Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70172Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83508Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83567Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83585Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83652Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83859Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96217Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96916Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96918Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96928Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96931Windows NTFS Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69915Windows NTFS Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-81971Windows NTFS Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83737Windows NTFS Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83864Windows NTFS Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96925Windows NTFS Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96927Windows NTFS Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96935Windows NTFS Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83786Windows NTFS Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-83640Windows NTFS Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-83712Windows NTFS Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-96867Windows NTFS Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-69902Windows NTFS Remote Code Execution VulnerabilityImportant6.7NoNoRCE
CVE-2026-83709Windows NTLM Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70210Windows OLE DB Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-70059Windows OLE Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70138Windows OLE Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96924Windows OLE Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-105004Windows Overlay Filter Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69950Windows Overlay Filter Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69952Windows Overlay Filter Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69953Windows Overlay Filter Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69957Windows Overlay Filter Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83727Windows Overlay Filter Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83749Windows Overlay Filter Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83879Windows Overlay Filter Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69954Windows Overlay Filter Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69967Windows Overlay Filter Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-69942Windows Overlay Filter Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-69959Windows Overlay Filter Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-69947Windows Overlay Filter Remote Code Execution VulnerabilityImportant6.8NoNoRCE
CVE-2026-69958Windows Overlay Filter Remote Code Execution VulnerabilityImportant6.8NoNoRCE
CVE-2026-96315Windows Overlay Filter Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-83844Windows Paint Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-83851Windows Partition Management Driver Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-103553Windows Partition Management Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83514Windows Partition Management Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83797Windows Partition Management Driver Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-97805Windows Partition Management Driver Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-96917Windows PCI Bus Driver Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-85915Windows PCI Bus Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-61931Windows Perception Simulation Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85359Windows Performance Monitor Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85333Windows Performance Monitor Elevation of Privilege VulnerabilityImportant6.7NoNoEoP
CVE-2026-85357Windows Phone Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-88133Windows Portable Device Enumerator Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70132Windows Portable Device File System Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83664Windows Portable Device File System Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-102206Windows Portable Device MTP Driver Elevation of Privilege VulnerabilityImportant6.8NoNoEoP
CVE-2026-83794Windows Portable Device MTP Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85327Windows Print Spooler Components Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85376Windows Print Spooler Components Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85933Windows Print Spooler Components Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-84018Windows Print Spooler Components Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85353Windows Print Spooler Components Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-85847Windows Print Spooler Components Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-83733Windows Print Spooler Components Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85320Windows Print Spooler Components Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83781Windows Program Compatibility Assistant Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96920Windows Program Compatibility Assistant Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69596Windows Program Compatibility Assistant Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69743Windows Program Compatibility Assistant Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-72934Windows Program Compatibility Assistant Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-72968Windows Program Compatibility Assistant Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-72969Windows Program Compatibility Assistant Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85328Windows Projected File System Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70084Windows Projected File System Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96857Windows Projected File System Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-84009Windows Projected File System Tampering VulnerabilityImportant4.7NoNoTampering
CVE-2026-83867Windows Push Notifications Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70198Windows Push Notifications Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96313Windows Push Notifications Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83927Windows Registry Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85867Windows Remote Access Connection Manager Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70137Windows Remote Access Connection Manager Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-87698Windows Remote Access Service Infrastructure Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85337Windows Remote Desktop Client Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-70033Windows Remote Desktop Gateway (RD Gateway) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-83861Windows Remote Desktop Protocol Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96322Windows Remote Desktop Protocol Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102198Windows Remote Desktop Protocol Information Disclosure VulnerabilityImportant5.3NoNoInfo
CVE-2026-59116Windows Remote Desktop Security Feature Bypass VulnerabilityImportant6.8NoNoSFB
CVE-2026-84012Windows Remote Desktop Services Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-70135Windows Remote POS Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83586Windows Resilient File System (ReFS) Deduplication Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70048Windows Resilient File System (ReFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102227Windows Resilient File System (ReFS) Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-70116Windows Resilient File System (ReFS) Security Feature Bypass VulnerabilityImportant4.2NoNoSFB
CVE-2026-87702Windows Resource Management (MRM) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96318Windows Resume Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70093Windows Rich Text Edit Control Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70096Windows Rich Text Edit Control Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83788Windows rndismp6.sys Information Disclosure VulnerabilityImportant4.6NoNoInfo
CVE-2026-103558Windows Routing and Remote Access Service (RRAS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-84017Windows Routing and Remote Access Service (RRAS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-85808Windows Routing and Remote Access Service (RRAS) Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-84020Windows Routing and Remote Access Service (RRAS) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85322Windows Routing and Remote Access Service (RRAS) Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-96245Windows Routing and Remote Access Service (RRAS) Information Disclosure VulnerabilityImportant7.5NoNoInfo
CVE-2026-85794Windows Routing and Remote Access Service (RRAS) Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85792Windows Routing and Remote Access Service (RRAS) Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-85809Windows Routing and Remote Access Service (RRAS) Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-70158Windows Routing and Remote Access Service (RRAS) Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-85339Windows Routing and Remote Access Service (RRAS) Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70057Windows Routing and Remote Access Service (RRAS) Security Feature Bypass VulnerabilityImportant5.5NoNoSFB
CVE-2026-96316Windows Routing and Remote Access Service (RRAS) Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-70566Windows Schannel Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-105005Windows Schannel Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-105008Windows Schannel Spoofing VulnerabilityImportant9NoNoSpoofing
CVE-2026-85818Windows Schannel Spoofing VulnerabilityImportant9NoNoSpoofing
CVE-2026-83570Windows Search Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83920Windows Search Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83564Windows Search Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83574Windows Search Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83575Windows Search Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83921Windows Search Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102221Windows Secure Boot Security Feature Bypass VulnerabilityImportant4.4NoNoSFB
CVE-2026-70026Windows Secure Kernel Mode Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96865Windows Secure Kernel Mode Information Disclosure VulnerabilityImportant5.6NoNoInfo
CVE-2026-70017Windows Secure Kernel Mode Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-88147Windows Secure Socket Tunneling Protocol (SSTP) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85926Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-96858Windows Security Account Manager Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-105725Windows Security App Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70212Windows Security Center Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-71347Windows Security Center Elevation of Privilege VulnerabilityImportant6.4NoNoEoP
CVE-2026-88098Windows Security Support Provider Interface Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83639Windows Sensor Data Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88115Windows Server for NFS Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-81969Windows Server Update Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83499Windows Server Update Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-105009Windows Server Update Service Elevation of Privilege VulnerabilityImportant7.5NoNoEoP
CVE-2026-97793Windows Setup and Deployment Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-73027Windows Setup Files Cleanup Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83505Windows Setup Files Cleanup Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83509Windows Setup Files Cleanup Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83510Windows Setup Files Cleanup Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70222Windows Shell Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83873Windows Shell Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83876Windows Shell Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83905Windows Shell Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-83782Windows Shell Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-85936Windows Shell Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-83906Windows Shell Spoofing VulnerabilityImportant6.5NoNoSpoofing
CVE-2026-83579Windows Smart Card Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83584Windows Smart Card Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70051Windows SmartScreen Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85851Windows SmartScreen Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83504Windows SmartScreen Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-108463Windows SmartScreen Security Feature Bypass VulnerabilityImportant8.8NoNoSFB
CVE-2026-62879Windows SmartScreen Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-83789Windows SMB Client Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-84011Windows SMB Client Security Feature Bypass VulnerabilityImportant5.5NoNoSFB
CVE-2026-70133Windows SMB Server Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-96325Windows SMB Server Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-88127Windows SMB Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69934Windows Spaceport.sys Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70102Windows Spaceport.sys Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83832Windows Spaceport.sys Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96862Windows Spaceport.sys Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70112Windows Spaceport.sys Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-102216Windows StateRepository API Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70218Windows StateRepository API Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85911Windows StateRepository API Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85910Windows StateRepository API Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-100216Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-100225Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102189Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-102191Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69763Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69766Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69856Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69931Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69935Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83911Windows Storage Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96944Windows Storage Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-102188Windows Storage Port Driver Elevation of Privilege VulnerabilityImportant6.8NoNoEoP
CVE-2026-96863Windows Storage Port Driver Elevation of Privilege VulnerabilityImportant6.8NoNoEoP
CVE-2026-88226Windows Storage Port Driver Information Disclosure VulnerabilityImportant4.6NoNoInfo
CVE-2026-87716Windows Storage Spaces Controller Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-87706Windows Storage Spaces Controller Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70238Windows Storage Spaces Controller Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88100Windows Storage Spaces Controller Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-88143Windows Storage Spaces Controller Elevation of Privilege VulnerabilityImportant6.7NoNoEoP
CVE-2026-85872Windows Storage VSP Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69765Windows Storport Miniport Driver Remote Code Execution VulnerabilityImportant8.8NoNoRCE
CVE-2026-70027Windows Subsystem for Linux Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96309Windows Subsystem for Linux Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85879Windows Subsystem for Linux Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96206Windows Subsystem for Linux Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-96306Windows Sysmain Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85793Windows Sysmain Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70157Windows System Information Console Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83678Windows TCP/IP Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85368Windows TCP/IP Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70164Windows TCP/IP Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83682Windows TCP/IP Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83842Windows TCP/IP Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85834Windows TCP/IP Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96852Windows TCP/IP Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83872Windows TCP/IP Local Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69913Windows TCP/IP Remote Code Execution VulnerabilityImportant8.1NoNoRCE
CVE-2026-84013Windows Telephony Server Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85810Windows Telephony Server Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85795Windows Text Services Framework Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102210Windows Text Shaping Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-83770Windows Text Shaping Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-85905Windows UI Immersive Server API Elevation of Privilege VulnerabilityImportant8.8NoNoEoP
CVE-2026-102205Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102215Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102218Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83513Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83857Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85820Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96946Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96947Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96950Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85825Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96949Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85821Windows Universal Disk Format File System Driver (UDFS) Information Disclosure VulnerabilityImportant6.5NoNoInfo
CVE-2026-83713Windows Universal Disk Format File System Driver (UDFS) Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85909Windows Universal Disk Format File System Driver (UDFS) Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96930Windows Universal Disk Format File System Driver (UDFS) Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96953Windows Universal Disk Format File System Driver (UDFS) Remote Code Execution VulnerabilityImportant7.8NoNoRCE
CVE-2026-85373Windows Universal Plug and Play (UPnP) Device Host Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85375Windows Universal Plug and Play (UPnP) Device Host Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85927Windows Universal Plug and Play (UPnP) Device Host Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85918Windows Universal Plug and Play (UPnP) Device Host Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-108465Windows Update Delivery Optimization Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69633Windows Update Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69673Windows Update Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69718Windows Update Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69733Windows Update Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69783Windows Update Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-69882Windows Update Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96323Windows Update Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69999Windows Update Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83793Windows Update Orchestrator Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83886Windows Update Orchestrator Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83930Windows Update Orchestrator Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-97812Windows Update Orchestrator Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83507Windows Update Orchestrator Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83933Windows Update Orchestrator Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-81964Windows Update Orchestrator Service Security Feature Bypass VulnerabilityImportant5.5NoNoSFB
CVE-2026-70139Windows Update Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70142Windows Update Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-100200Windows Update Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-100203Windows Update Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70056Windows Update Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83798Windows Update Stack Spoofing VulnerabilityImportant5.5NoNoSpoofing
CVE-2026-96218Windows Update Stack Tampering VulnerabilityImportant5.5NoNoTampering
CVE-2026-83588Windows USB Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83638Windows USB Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85935Windows USB Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-96250Windows USB Print Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96253Windows USB Print Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96254Windows USB Print Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96301Windows USB Print Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96304Windows USB Print Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96310Windows USB Print Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96319Windows USB Print Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96860Windows USB Print Driver Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-85341Windows USB Video Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85807Windows USB Video Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83659Windows User Profile Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102220Windows VHD miniport driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83791Windows Virtual Input Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70075Windows Virtualization-Based Security (VBS) Enclave Security Feature Bypass VulnerabilityImportant4.4NoNoSFB
CVE-2026-70097Windows Virtualization-Based Security (VBS) Enclave Spoofing VulnerabilityImportant5.6NoNoSpoofing
CVE-2026-83885Windows Virtualization-Based Security (VBS) Enclave Spoofing VulnerabilityImportant5.6NoNoSpoofing
CVE-2026-85356Windows Volume Manager Extension Driver Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83694Windows Volume Manager Extension Driver Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85928Windows Volume Manager Extension Driver Remote Code Execution VulnerabilityImportant9.8NoNoRCE
CVE-2026-96243Windows WalletService Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83703Windows Wi-Fi Driver Denial of Service VulnerabilityImportant6.5NoNoDoS
CVE-2026-85816Windows Wi-Fi Driver Information Disclosure VulnerabilityImportant5.7NoNoInfo
CVE-2026-83756Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83761Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85804Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85858Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-96249Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-102208Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83901Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-85802Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83895Windows Win32 Kernel Subsystem Elevation of Privilege VulnerabilityImportant6.8NoNoEoP
CVE-2026-96848Windows Win32 Kernel Subsystem Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-83774Windows Win32 Kernel Subsystem Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-83897Windows Win32 Kernel Subsystem Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-83909Windows Win32 Kernel Subsystem Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-96853Windows Win32 Kernel Subsystem Information Disclosure VulnerabilityImportant4.7NoNoInfo
CVE-2026-70067Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70060Windows Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70104Windows Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70108Windows Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70117Windows Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70285Windows Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83883Windows Win32k Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-70076Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70144Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70176Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70209Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70236Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70249Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70253Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70271Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-70273Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83566Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83841Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-83866Windows Win32k Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-69798Windows Wired AutoConfig Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-85829Windows Wired AutoConfig Service Elevation of Privilege VulnerabilityImportant7.8NoNoEoP
CVE-2026-83855Windows WLAN Service Denial of Service VulnerabilityImportant7.5NoNoDoS
CVE-2026-83668Windows WLAN Service Information Disclosure VulnerabilityImportant5.5NoNoInfo
CVE-2026-70045Windows Work Folders Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-96923Windows Workstation Service Elevation of Privilege VulnerabilityImportant7NoNoEoP
CVE-2026-87699Winlogon Elevation of Privilege VulnerabilityImportant7.8NoNoEoP

As with last month, I’ll do my best to summarize everything else in this release but assume there are details I miss or that will be revised after the release.

Local Privilege Escalations: To say these bugs are prevalent is an understatement. However, of the 677 EoP bugs in the data, 606 (90%) lead to SYSTEM, administrator or root privileges. There are also a few integrity-level or sandbox escapes. There are 10 bugs where the attacker moves from low to medium integrity, and six where they escape a Low Integrity Level or AppContainer sandbox. There are seven bugs where the advisory says only “ELEVATED privileges,” or describes a cloud identity or data-access issue. There are nearly two dozen others where the attacker runs as another user or service account, creates or deletes files in a privileged context, or reaches Local Service. This includes CVE-2026-70190, which lets the attacker create, modify or delete files as SYSTEM but doesn’t give SYSTEM privileges. Frustratingly, there are 23 that have no “what privileges” FAQ at all, and some of these may be cloud fixes with no action needed. If I can be bothered to read them all, they should be bothered to write them all.

Office-Related Bugs: I’ve already mentioned a couple of these above, but that still leaves a lot to cover. Counting Skype for Business and Bookings, there are 139 Office-related CVEs (including those mentioned above): 100 RCE, 29 info disclosure, nine EoP and one security feature bypass. Thirty-five are Critical and 104 are Important. I would focus on Outlook, with five Critical RCEs at CVSS 9.8. All five say simply viewing the email in the Reading Pane triggers the bug, with no click and no authentication. That makes them the closest thing to wormable in Office. Then there are the 69 Excel bugs; 51 RCEs and 18 info leaks. Nineteen of these RCEs are Critical at 8.8 (for example CVE-2026-100209). Most of these are the open-and-own variety. Four Excel bugs do list the Preview Pane: CVE-2026-70254 and 88145 (RCE, 8.8), and 88154 and 88175 (info leaks). Word adds 22 more. Most of the RCEs and info leaks name the Preview Pane as a vector. The rest are an EoP and a security feature bypass. There are 12 Access RCEs and three Critical Visio RCEs that are open-and-own. Access also has one info. PowerPoint rounds things out with three Critical RCEs, all of which name the Preview Pane. The other four are info leaks.

DNS and DNS Server Bugs: There are 58 CVEs in Windows DNS and DNS Server: 52 tagged DNS Server (role) and six tagged Windows DNS. All 58 are Important, including CVE-2026-96113, an RCE scored at CVSS 9.8. There are still a few where the advisories describe the impact as unauthorized attackers executing code over the network, but without the exact wormable wording. Four of these are untrusted pointer dereferences and one is type confusion. The majority of these bugs (31) are info disclosures. Five are tampering bugs and one is a security feature bypass, but all of these require authentication.

Windows Kernel and the Win32k Subsystem: Alright – don’t @me. I know the difference between kernel and Win32k components, but they’re similar enough that I group them together. There are 94 CVEs in the Windows Kernel and Win32K components: Windows Kernel (46), Win32 Kernel Subsystem (36), Win32K (8), Win32K GRFX (3) and Win32K ICOMP (1). By type, 71 are elevation of privilege, 20 are info disclosure, 2 are DoS and 1 is a security feature bypass. Most of these just lead to SYSTEM access as expected. Of the info disclosure bugs, these primarily leak random portions of memory. The only real outlier here is CVE-2026-70111, whose advisory says the attacker elevates privileges “over a network.” That’s unusual for a kernel EoP.

Windows DHCP Client and Server: There are 18 CVEs in Windows DHCP: 16 in DHCP Server and 2 in DHCP Client. We’ve already discussed the wormable ones, so I won’t rehash them here. Of the remaining 12 DHCP bugs, two are Critical. CVE-2026-88171 is an unauthenticated double free in DHCP Server that just misses being wormable, and CVE-2026-70250 is a DHCP Client use-after-free that requires an adjacent network. The rest are a mix of authenticated RCEs, two unauthenticated DoS bugs, two EoPs and two security feature bypasses, none rated above “Exploitation Less Likely” by Microsoft.

SharePoint Server: Besides the Critical bug already mentioned, SharePoint has 34 other CVEs this month: 13 EoP, seven spoofing, seven RCE, six info disclosure and one tampering bug. All of the rest are Important. The seven RCEs all lean on authentication, but the bar is low. CVE-2026-85900 needs only Site Member permissions, and CVE-2026-88155, 88163 and 88166 need Manage List. CVE-2026-105013 and 70267 don’t say what level an attacker needs, so assume these default permissions only. The bug classes read more like a web-app pentest report than memory corruption: seven of the EoPs are authorization and access-control failures, three more are SSRF, and the spoofing bugs are mostly stored script. The one other unauthenticated bug is CVE-2026-97783, a spoofing flaw at CVSS 8.1. Given SharePoint’s recent history of “Exploitation Less Likely” turning into “in the wild,” don’t skip the RCEs just because they need credentials.

SQL Server and Client: Beyond the RCE already mentioned, SQL Server and its client tools have 23 other CVEs this month: nine RCE, seven EoP, four info disclosure, and three DoS. All are Important. The pattern here is authenticated memory corruption: heap and stack overflows, use-after-frees, and out-of-bounds reads. The template is simple: log in, submit a crafted request, corrupt memory, run code on the server. That’s why the CVSS 8.8 bugs here are less scary than they score; an attacker already needs database credentials, but it’s also textbook post-compromise lateral movement. The odd one out is CVE-2026-103572, which isn’t a database bug at all. It’s in SQL Server Management Studio, where a prompt injection through Copilot can turn into code execution. As AI features creep (sneak?) into admin tools, I expect to see more of this.

Windows Installer: Windows Installer is the largest component I haven’t mentioned yet, with 38 CVEs: 35 EoPs and three info disclosure bugs. Every one of these bugs are local, every one is Important, and none top CVSS 7.8. Thirty-four of the 35 EoPs end in SYSTEM. The bug classes are the usual memory-safety suspects, with use-after-frees (20) leading, followed by heap overflows (6) and stack overflows (3). It’s the same story we see every month with Installer: an attacker who already has a foothold abuses the repair and rollback paths to get to SYSTEM. None of these will get a headline by themselves, but this is exactly what ransomware crews chain after phishing a user, so don’t skip them.

Windows NTFS: NTFS has 26 CVEs this month: 16 EoP, six info disclosure and four RCE. All are Important, none is above CVSS 7.8, and 21 of the 26 are local. The EoPs all lead to SYSTEM, and five of them (CVE-2026-96217, 96916, 96918, 96928 and 96931) are sandbox escapes caused by reparse points created by sandboxed processes. That means a compromised browser or app sandbox could use them to break out. The four RCEs all require an authorized local attacker, so they’re closer to EoPs with extra steps than real remote bugs. Everything else is memory corruption: out-of-bounds reads lead, then use-after-frees and heap overflows.

Remote Desktop and Remote Access: Remote Desktop has 30 CVEs across its components: 22 RCE, four info disclosure, two EoP, one DoS and one security feature bypass. Only one is Critical (CVE-2026-70187 in Remote Desktop Gateway, already covered with the wormable bugs). The Remote Desktop Client accounts for 19, 18 of them RCEs, and nearly all are use-after-frees. These are the reverse of the usual direction: the attacker needs a user to connect to a malicious server, so they’re social-engineering bugs. Gateway adds a DoS (CVE-2026-70033) and an info leak (CVE-2026-84007) beyond the three wormable RCEs. Windows Remote Desktop Protocol has two EoPs to SYSTEM, CVE-2026-83861 and -96322. RRAS adds 13 more, including four RCEs, two of which are the 9.8 wormable bugs.

Hyper-V Server: Hyper-V has 18 CVEs: seven EoP, four RCE, two each of DoS, info disclosure and security feature bypass, and one spoofing bug. Two are Critical RCEs at CVSS 8.8, CVE-2026-102214 and 105733. The first is the classic guest-to-host scenario, in which an authenticated user on a guest runs a crafted app to execute code on the host. That’s the scenario that matters for anyone running multi-tenant hosts or shared virtualization. CVE-2026-83716 and 83931 are two more guest-triggered RCEs, scored 8.8 and 7.8. The newest Critical addition, CVE-2026-108399, is an EoP at 7.2. Of the other bugs, CVE-2026-85369 is an EoP at 8.2, and CVE-2026-87705 is an unauthenticated security feature bypass over an adjacent network (7.4). Everything is rated “Exploitation Less Likely” except one at “Unlikely,” but test and deploy these before the Hyper-V hosts that carry the most sensitive workloads.

A few additional bugs deserve at least a brief mention. The Windows Message Queuing service receives a Critical-rated, 9.8 use-after-free (CVE-2026-100202) that could allow remote code execution via a crafted message, though MSMQ isn’t enabled by default. Five VBS Enclave bugs are also rated Critical and could allow a local attacker to reach SYSTEM. Several 9.8-rated RCEs in Imaging Component, libarchive, Media Player and iSCSI require an in-network attacker. Newer additions to the release include Critical RCEs in Windows PDF (CVE-2026-108457), the PostScript Printer Driver (CVE-2026-108467) and HEVC Video Extensions (CVE-2026-108400), along with a Critical AD FS spoofing bug (CVE-2026-108131). The Exchange XSS (CVE-2026-70279) and the VS Code project-open RCE (CVE-2026-102238) round out the higher-scoring items.

The remaining ~850 fixes are mostly lower-profile: local EoPs, information disclosures, and denial-of-service bugs. They are spread across Windows Search, .NET and ASP.NET Core, Windows Error Reporting, Broadcast DVR, UDFS, the Overlay Filter driver, AD FS, WebDAV and DWM. Seven cloud fixes (Partner Center, Azure App Service, Dataverse, Azure SRE Agent, API Center, Bookings and Event Grid) are rated Critical but need no customer action.

No new advisories are being released this month.

Looking Ahead

The next Patch Tuesday will be on November 10. Regardless of how big (or how small!) the release may be, I’ll be back to do my best to discern what you need to know. Until then, stay safe, happy patching, and may all your reboots be smooth and clean!
Pwn2Own Ireland 2026 - Day Three Results & Master of Pwn

Day Three of Pwn2Own Ireland 2026 wrapsup with 17 attempts scheduled, roughly $1.33 million on the board.

The headliner is the Google Pixel 10, which draws three separate attempts: Xint at 11:15 AM, Ikotas Labs at 2:00 PM, and the Valsamaras/Ken Gannon (Djini.ai)/Valsamara team closing things out at 6:30 PM — by far the single biggest payday in play all week. The Samsung Galaxy S26 gets one more run too, from BunkyoWesterns at 4:15 PM. Smart Home stays busy with three attempts on the Philips Hue Bridge Pro and two closing attempts on Home Assistant Green, while AI Infrastructure sees two more shots at Oracle's Autonomous AI Database plus a single run at Chroma. Printers round things out with steady, lower-stakes attempts on the Brother, Canon, and Lexmark targets — and with Team MAMMOTH's 7:00 PM attempt as the last scheduled slot, the Master of Pwn title could still be unsettled heading into the final hour.

Stay tuned for live results as we have them.

FAILURE - Unfortunately, Polina Smirnova (@moe_hw), Mikhail Evdokimov (@konatabrk) and Mate Zombor (@r4bbit_zm) of White Noise Clubm couldn't get their exploit of the Garmin Index BPM working within the time allotted

SUCCESS / COLLISION - Results are in! Nikolaos Mourousias (@deltaclock) and Bruno Halltari (@BrunoModificato) of OtterSec successfully exploited the Oracle Autonomous AI Database with 4 bug chain of 3 collisions and 1 zero-day winning them $6,250 and 2.5 Master of Pwn points

SUCCESS / COLLISION - Sina Kheirkhah (@SinSinology) and Aaron Christophel (@ATC1441) of Summoning Team (@SummoningTeam) collided through the walls of the Philips Hue Bridge Pro with a 5 bug, full collision, securing a $5k payout and 2.5 Master of Pwn Points

SUCCESS - Brother what? Brother exploited! Lucas Van Haaren (vhash, @LucasVanHaaren) and Hugo Leclercq (0xnasu) of FuzzingLabs (@FuzzingLabs) exploited Brother MFC-L8970CDW with a single zero-day earning $20,000 and 2 Master of Pwn points

SUCCESS / COLLISION - Results are in and Tim Becker (@tjbecker) and Yves Bieri (@yves_bieri) of Xint (@xint_official) have secured their lead in the race to the Master of Pwn with their successful remote exploit of Google Pixel 10 through a single bug collision, earning them $150,000 and 15 - Master of Pwn points

SUCCESS / COLLISION - Boom chaka laka! Ben Koo (@kiddo_pwn) and Evangelos Daravigkas (@freddo_1337) of Team DDOS exploitted confirmed with a 5 bug chain, including 1 zero-day targeting Home Assistant Green with a pay out in $4,500 and 2 Master of Pwn points #Pwn2Own

SUCCESS / COLLISION - $6000 and 2.5 Master of Pwn points secured by Connor Laidlaw & Matthew Keeley of Platform Security for successfully targeting Oracle Autonomous AI Database through a 5 bugs - 4 collisions and 1 unique chain #Pwn2Own

SUCCESS - Canon Ball!!!! Sina Kheirkhah (@SinSinology) and Aaron Christophel (@ATC1441) of Summoning Team (@SummoningTeam) exploited Canon imageFORCE 1643F Multifunction Copier with a bug chain of 4 unique bugs winning total of $5,000 and 2 Master of Pwn points

SUCCESS / COLLISION - Bye bye bridge @_McCaulay exploited the Philips Hue Bridge Pro winning $5,000 and 2 Master of Pwn points with a 4 bug collision #Pwn2Own

SUCCESS / COLLISION - $300,000!!!!! and 30 Master of Pwn points officially makes Ikotas Labs, Inc. the Master of Pwn as they jump to the top of the leader board after they chained multiple issues together to successfully exploit the Google Pixel 10 #Pwn2Own

SUCCESS - 2 unique bugs and down went the Lexmark CX532adwe as Cong Thanh (@ExLuck99), Duc Hieu (@gr4ss341) and Nam Dung (@greengrass19000) earned $5,000 and 2 Master of Pwn points in their successful exploit attempt #Pwn2Own

SUCCESS / COLLISION - Howdy Buckaroos, the very own BunkyoWesterns (@BunkyoWesterns) succeed in their remote lasso-ing of the Samsung Galaxy S26, with their 2 bug chain, 1 collission + 1 unique, earning them $8250 and 3.75 Master of Pwn points #Pwn2Own #P2OIreland

SUCCESS / COLLISION Booya! Cens-ational exploit by Dimitrios Valsamaras (@Ch0pin), Ken Gannon / 伊藤 剣 (@yogehi) using http://Djini.ai from Mobile Hacking Lab, Tenia Valsamara (@ir3l14) from CENSUS Labs targeting Google Pixel 10 - Remote in the Mobile Phone category for a total of $112,500 and 22.50 Master of Pwn points with a 2 bug chain, 1 collission and 1 zero-day #Pwn2Own

SUCCESS - A Mammoth of a bug chain of 6 zero days closes out #Pwn2OwnIreland by Chulhan Park, Mingeun Kim, SeokHun Lee, Inhyung Lee, Sehyun Baek, Nayeon Lee, Junseok Kim of Team MAMMOTH targeting Home Assistant Green in the Smart Home category for a total of $7500 and 3 Master of Pwn points #Pwn2Own

Pwn2Own Ireland 2026 - Day Two Results

Day Two of Pwn2Own Ireland 2026 has 24 attempts on the docket, with roughly $780,000 up for grabs, running 9:30 AM to 7:30 PM IST.

Samsung's Galaxy S26 will be attempted three separate times — by Valsamaras/Ken Gannon (using Djini.ai)/Valsamara at 1:00 PM, Kyeongmin Kim at 3:15 PM, and PetoWorks at 5:30 PM — worth watching since only the first successful demo claims the cash. Home Assistant Green is the day's most-attempted device, with five researchers scheduled to take a run at it. AI Infrastructure stays active with four attempts on tap (Dynamo, two at Chroma, two at Oracle's Autonomous AI Database), Wellness has just one attempt scheduled, and Printers see steady action with three separate attempts on the Lexmark CX532adwe.

Yesterday, we awarded $388,500 for 32 unique 0-days. Stay tuned for all of today’s results!

FAILURE - Unfortunately, the printers continue to be a challenge with Thanh Do ( @nyanctl ) of Team Confused unsuccessful in their targeting of Brother MFC-L8970CDW in the Printers category #Pwn2Own

SUCCESS - The grass may not be greener but the exploits sure were as Yves Bieri (@yves_bieri) of Xint (@xint_official) just won $30k and 3 Master of Pwn points in his takedown of Home Assistant Green #Pwn2Own

FAILURE - Another one bites the dust - with seconds left on the clock, unfortunately Eugene ( @k3vg3n ) targeting Chroma in the #AIInfrastructure category was unsuccessful in his final attempt #Pwn2Own

SUCCESS - A dynamite takedown of Dynamo in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points by HaeJung Yang (@haehaeYang) of Out of Bounds (@oobs_io) #Pwn2Own

SUCCESS / COLLISION We have another collision! Yassine Bengana (@cousky_), and Maxence Schmitt (@maxenceschmitt) of Doyensec (@doyensec) used 3 bugs to exploit the Home Assistant Green, but all 3 bugs were previously known. They still earn $7,500 and 1.5 Master of Pwn points. #Pwn2Own

SUCCESS - Confirmed! @_McCaulay used 3 bugs (incl Hard-coded Credentials, Missing Authentication for Critical Function, Command Injection) to exploit the Canon imageFORCE 1643F. His 2nd round win nets him $10,000 and 2 Master of Pwn points. #Pwn2Own

SUCCESS / COLLISION - Against the clock in the final round.... Jack Dates of RET2 Systems (@ret2systems) locked in his win against the Sonos Era 300. The pot has been confirmed, with 1 zero day and 1 collision, he will take home $9.5K and 3.75 Master of Pwn points #Pwn2Own

SUCCESS / COLLISION - Boom! With 3 collisions and 2 unique zero-days Taisic Yun ( @taisic_ ) of Xint ( @xint_official ) breached Oracle Autonomous AI Database capturing their pot of gold of $14k at #Pwn2OwnIreland and 3 Master of Pwn points #Pwn2Own

FAILURE - A valiant effort but Shio Kudo ( @shiosa1t ) of GMO Flatt Security Inc. ( @flatt_security ) was unsuccessful in their attempts at targeting Home Assistant Green in the Smart Home category #Pwn2Own

SUCCESS - 1 bug wonder! With an Confused Deputy (CWE-441) bug Dimitrios Valsamaras (@Ch0pin), Ken Gannon / 伊藤 剣 (@yogehi) using Djini.ai from Mobile Hacking Lab, Tenia Valsamara (@ir3l14) from CENSUS Labs PwN'ed the Samsung Galaxy S26 #Pwn2Own

SUCCESS / COLLISION - And the results are in! Nguyen Thanh Dat (@rewhiles), dungnm (@dungnm_) of Viettel Cyber Security (@vcslab) targeting Sonos Era 300 with 1 collision & 2 zero-days for a total of $10.5K and 4.25 Master of Pwn points #Pwn2Own

SUCCESS - It was DOOMsday for the Lexmark CX532adwe printer as Interrupt Labs (@InterruptLabs) claimed victory and earned $5k & 2 Master of Pwn points! #Pwn2Own #DoomHack

SUCCESS / COLLISION - Green means go! And boy did PetoWorks (@petoworks) go straight into the Home Assistant Green with a chain of 5 bugs including 2 collisions and 3 unique, securing $12k and 2.5 Master of Pwn points in the Smart Home category #Pwn2Own

SUCCESS / COLLISION - Direct connection - NOT needed for Kyeongmin Kim (@hareh4ru) of KAIST Hacking Lab who remotely breached the Samsung Galaxy S26 with 1 unique bug and 2 collision winning $8.5k and 3.5 Master of Pwn points #Pwn2Own

SUCCESS - Confused? Well Ikotas Labs, Inc. sure wasn't as they unleased a 7-chain bug ending with a Use-After-Free and a Type Confusion on Oracle Autonomous AI Database securing a win of $10,000 and 4 Master of Pwn points #Pwn2Own

SUCCESS / COLLISION - @_McCaulay climbs the leaderboard with his third target earning another 1.5 master of Pwn points and $6750 for his exploit of Garmin Index BPM with 1 collision and 1 unique bug.

SUCCESS / COLLISION - Confirmed! 1 zero-day & 3 collisions by Kyeongmin Kim (@hareh4ru) of KAIST Hacking Lab successfully exploited the Home Assistant Green in the Smart Home category earning him $4,750 and 2 Master of Pwn points #Pwn2Own

SUCCESS - Another printer bites the dust by Rick de Jager and Filippo Cremonese of @zellic_io/@v12sec earning him $5k and 2 Master of Pwn points in his successful exploit of Lexmark CX532adwe #Pwn2Own

SUCCESS / COLLISION - Boom! With 3 bug collisions PetoWorks (@petoworks) successfully accessed the Samsung Galaxy S26 remotely, earning them a net $6250 and 2.5 Master of Pwn points #Pwn2Own

SUCCESS / COLLISION - A mammoth win by team MAMMOTH, with Mingeun Kim, Chulhan Park, SeokHun Lee, Inhyung Lee, Sehyun Baek, Nayeon Lee, Junseok Kim of Team MAMMOTH exploiting Chroma in the AI Infrastructure category with 2 collisions and 1 zero-day for a net total win of $12,000 and 1.25 Master of Pwn points #Pwn2Own

SUCCESS - 2 bugs + Sina Kheirkhah (@SinSinology) of Summoning Team = exploited Sonos Era 300 and $12,500 and 5 Master of Pwn points won! #Pwn2Own

SUCCESS / COLLISION - Exploit Confirmed! @BoredPentester successfully exploited Lexmark CX532adwe in the Printers category with 1 collision & 2 unique bugs for a net total of $4250 and 1.25 Master of Pwn points #Pwn2Own

SUCCESS / COLLISION - @_McCaulay strikes again and down goes Home Assistant Green once again! With a 6 bug chain, including 1 collision and 5 zero-days, the net total winnings is $7k & 2.75 Master of Pwn points #Pwn2Own

SUCCESS / COLLISION - An impressive disclosure from Alessandro Fanio Gonzalez targeting Chroma with a 2 N-days & 1 collision in the AI Infrastructure category for a net total win of $4,500 and 1 Master of Pwn points #Pwn2Own

Pwn2Own Ireland 2026 - Day One Results

Welcome to Day One of Pwn2Own Ireland 2026! Today, 21 entries took the Pwn2Own stage to target multiple categories - including multiple Samsung attempts and our first Pixel entry.

Follow the action live! We’ll be posting real-time updates and results throughout the competition on our blog and across social media. Stay up to date by following us on Twitter, Mastodon, LinkedIn, and Bluesky, and join the conversation using #Pwn2Own Ireland and #P2OIreland for continuous coverage. 

Here are the results of Day One:

FAILURE - Unfortunately, Ikotas Labs, Inc. (@ikotas00) could not get their exploit of the Brother MFC-L8970CDWworking within the time allotted.

Ikotas Labs, Inc. (@ikotas00) targeting the Brother printer

SUCCESS - @_McCaulay combined an OOB Write and a format string(!) bug to exploit the #Sonos Era 300. He earns $50,000 and 5 Master of Pwn points.

McCaulay Hudson displays his successful exploit

SUCCESS - Taisic Yun (@taisic_) of Xint (@xint_official) used an Improper Input Validation bug along with code injection to get his reverse shell on LiteLLM. He earned $40,000 and 4 Master of Pwn points.

Xint focuses on his LiteLLM exploit

FAILURE - Printers continue to prove to be a time challenge as unfortunately Hyeop Jung (@hyoub9un), Hyunwoo Kim (@hwhw_kr), Jinyoung Choi (@hmema_), and Jihun Lee (@dyrandy_) of Team T-X Lab team (@TX_Lab_) hit the time limit on their exploit attempt of Lexmark CX532adwe in the Printers category.

SUCCESS/COLLISION - Nguyen Thanh Dat (@rewhiles) of Viettel Cyber Security (@vcslab) used 4 bugs to exploit the Samsung Galaxy S26, but 3 were known by the vendor. They still earn 31,250 and 3.25 Master of Pwn points.

Team Viettel shows their access to the Samsung handset

SUCCESS/COLLISION - Another bug collision! linhlhq (@linhlhq) and Son Dinh (@_sondt_) of VinSOC exploited the #Sonos Era 300 with 2 bugs, but one was publicly known. They still earn $17,500 and 3.5 Master of Pwn points.

VinSOC took over the Sonos, but one bug was publicly known

SUCCESS/COLLISION - Another Collision 💥 4 bugs - 3 collisions & 1 zero-day successfully exploit the Samsung Galaxy S26 and Interrupt Labs (@InterruptLabs) takes home $15,750 and 3.25 Master of Pwn points.

FAILURE - The Garmin Index BPM withstood Aaron Christophel (@ATC1441) of Summoning Team (@SummoningTeam) targeting as exploit attempts were unsuccessful before the clock ran out.

SUCCESS - A slam dunk success with 7 zero-days bugs disclosed from Vũ Chí Thành (@vcth4nh) and Huỳnh Đức Tin ( @ductinm ) of VinSOC during their exploit of Philips Hue Bridge Pro in the Smart Home category, taking home a total of $40,000 and 4 Master of Pwn points #Pwn2Own

SUCCESS/COLLISION - Out of Bounds ( @oobs_io ) results are confirmed as a Collision! HaeJung Yang ( @haehaeYang ), and ByungYoung Yi ( @yibarrack ) used 4 bugs - 2 of which were previously known. They still take home $15k and 3 Master of Pwn points in their exploit of LiteLLM in the #AIInfrastructure category.

SUCCESS - Confirmed! Thanh Do ( @nyanctl ) of Team Confused showed no confusion at all as he used a single use-after-free on the Lexmark CX532adwe to win $20,000 and 2 Master of Pwn points.

SUCCESS/COLLISION - Confirmed (w/ a collision)! Ikotas Labs, Inc. used 4 bugs to exploit the #Samsung Galaxy S26, but one was already known to the vendor (yet unpatched). They still earn $11,000 and 4.5 Master of Pwn points.

FAILURE - Unfortunately, Mikhail Evdokimov ( @konatabrk ), Polina Smirnova ( @moe_hw ) and Mate Zombor ( @r4bbit_zm ) of White Noise Club could not get their exploit of the Google Pixel 10 working within the time allotted. #Pwn2Own

SUCCESS/COLLISION - It seems to be a day for collisions. ByungYoung Yi ( @yibarrack ), and KeunHo Kim ( @gn0sis__ ) of Out of Bounds ( @oobs_io ) used 5 bugs to exploit the Phillips Hue Bridge Pro, but 4 of those bugs were previously known. They still earn $12,000 and 2.5 Master of Pwn points. #Pwn2Own

SUCCESS - Confirmed! Sina Kheirkhah ( @SinSinology ) of Summoning Team used a single bug to exploit the Lexmark CX532adwe printer. The second round win nets him $10,000 and 2 Master of Pwn points. #Pwn2Own

SUCCESS - Verified! Nam Nguyen ( @namberinos ), Thanh Vu ( @vcth4nh ), and Tin Huynh ( @ductinm ) of VinSOC combined 5 bugs to exploit the #Oracle Autonomous AI Database. They win $40,000 and 4 Master of Pwn points. Outstanding work!

SUCCESS - Confirmed! Ikotas Labs, Inc. used a single argument injection bug to exploit OpenAI Codex. They win $40,000 and 4 more Master of Pwn points. More outstanding research on display.

FAILURE - Unfortunately, the team of Nam Nguyen ( @namberinos ) and Thai Son Dinh ( @sondt ) and Hoang Tien Minh ( @cr0nica1 ) of VinSOC couldn't get their exploit of Chroma working within the time allotted.

SUCCESS - Verified! The 1st full win the the Wellness category has Interrupt Labs ( @InterruptLabs ) using an OOB Read and an OOB Write to exploit the Garmin Index BPM. They win $20,000 and 2 Master of Pwn points.

SUCCESS/COLLISION - Ending Day 1 with collisions seems apropos. Joohyun Park ( @cdor1 ) of Xint ( @xint_official ) used 5 different bugs in his exploit of the Philips Hue Bridge Pro, but 4 were previously known. His 3rd round success still nets him $6,000 and 2.5 Master of Pwn points. #Pwn2Own

Pwn2Own Ireland 2026 - The Full Schedule

Fáilte! Pwn2Own Ireland 2026 has arrived in Cork, and the world's top security researchers are ready. We've got more phone entries than we've ever had, and more than 60 entries total.

Earlier today, we held the random draw to determine attempt order. Below is the official schedule. All times are Irish Standard Time (IST) and may change as the competition progresses. You can find our live leaderboard here. This will be updated throughout the day.

Jump to:


-- Day One
-- Day Two
-- Day Three

DAY ONE

Tuesday, October 6 - 9:30 AM

Nguyen Thanh Dat (@rewhiles) of Viettel Cyber Security (@vcslab) targeting Samsung Galaxy S26 - Remote in the Mobile Phone category for a total of $50,000 and 5 Master of Pwn points

@_McCaulay targeting Sonos Era 300 in the Smart Home category for a total of $50,000 and 5 Master of Pwn points

Taisic Yun (@taisic_) of Xint (@xint_official) targeting LiteLLM in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points

Ikotas Labs, Inc. targeting Brother MFC-L8970CDW in the Printers category for a total of $20,000 and 2 Master of Pwn points

Tuesday, October 6 - 11:15 AM

HaeJung Yang (@haehaeYang), and ByungYoung Yi (@yibarrack) of Out of Bounds (@oobs_io) targeting LiteLLM in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points

Tuesday, October 6 - 11:45 AM

linhlhq (@linhlhq) and Son Dinh (@sondt) of VinSOC targeting Sonos Era 300 in the Smart Home category for a total of $50,000 and 5 Master of Pwn points

Interrupt Labs (@InterruptLabs) targeting Samsung Galaxy S26 - Remote in the Mobile Phone category for a total of $50,000 and 5 Master of Pwn points

Hyeop Jung (@hyoub9un), Hyunwoo Kim (@hwhw_kr), Jinyoung Choi (@hmema_), and Jihun Lee (@dyrandy_) of Team T-X Lab (@TX_Lab_) targeting Lexmark CX532adwe in the Printers category for a total of $20,000 and 2 Master of Pwn points

Tuesday, October 6 - 2:00 PM

Vũ Chí Thành (@vcth4nh) and Huỳnh Đức Tin (@ductinm) of VinSOC targeting Philips Hue Bridge Pro in the Smart Home category for a total of $40,000 and 4 Master of Pwn points

Tuesday, October 6 - 2:30 PM

Aaron Christophel (@ATC1441) of Summoning Team (@SummoningTeam) targeting Garmin Index BPM in the Wellness category for a total of $20,000 and 2 Master of Pwn points

Thanh Do (@nyanctl) of Team Confused targeting Lexmark CX532adwe in the Printers category for a total of $20,000 and 2 Master of Pwn points

Ikotas Labs, Inc. targeting Samsung Galaxy S26 - Remote in the Mobile Phone category for a total of $50,000 and 5 Master of Pwn points

Tuesday, October 6 - 4:15 PM

ByungYoung Yi (@yibarrack), and KeunHo Kim (@gn0sis__) of Out of Bounds (@oobs_io) targeting Philips Hue Bridge Pro in the Smart Home category for a total of $40,000 and 4 Master of Pwn points

Nam Nguyen (@namberinos), Thanh Vu (@vcth4nh), and Tin Huynh (@ductinm) of VinSOC targeting Oracle Autonomous AI Database in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points

Interrupt Labs (@InterruptLabs) targeting Garmin Index BPM in the Wellness category for a total of $20,000 and 2 Master of Pwn points

Tuesday, October 6 - 4:45 PM

Sina Kheirkhah (@SinSinology) of Summoning Team targeting Lexmark CX532adwe in the Printers category for a total of $20,000 and 2 Master of Pwn points

Tuesday, October 6 - 5:15 PM

Mikhail Evdokimov (@konatabrk), Polina Smirnova (@moe_hw) and Mate Zombor (@r4bbit_zm) of White Noise Club targeting Google Pixel 10 - Remote in the Mobile Phone category for a total of $300,000 and 30 Master of Pwn points

Tuesday, October 6 - 6:00 PM

Ikotas Labs, Inc. targeting OpenAI Codex in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Tuesday, October 6 - 6:30 PM

Nam Nguyen (@namberinos) and Thai Son Dinh (@sondt) and Hoang Tien Minh (@cr0nica1) of VinSOC targeting Chroma in the AI Infrastructure category for a total of $20,000 and 2 Master of Pwn points

Joohyun Park (@cdor1) of Xint (@xint_official) targeting Philips Hue Bridge Pro in the Smart Home category for a total of $40,000 and 4 Master of Pwn points

Tuesday, October 6 - 7:00 PM

Cong Thanh (@ExLuck99), Duc Hieu (@gr4ss341) and Nam Dung (@greengrass19000) targeting Canon imageFORCE 1643F Multifunction Copier in the Printers category for a total of $20,000 and 2 Master of Pwn points

Back to top

DAY TWO

Wednesday, October 7 - 9:30 AM

Kyeongmin Kim (@hareh4ru) of KAIST Hacking Lab targeting Google Pixel 10 - USB in the Mobile Phone category for a total of $75,000 and 7.5 Master of Pwn points

HaeJung Yang (@haehaeYang) of Out of Bounds (@oobs_io) targeting Dynamo in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points

Thanh Do (@nyanctl) of Team Confused targeting Brother MFC-L8970CDW in the Printers category for a total of $20,000 and 2 Master of Pwn points

Yves Bieri (@yves_bieri) of Xint (@xint_official) targeting Home Assistant Green in the Smart Home category for a total of $30,000 and 3 Master of Pwn points

Wednesday, October 7 - 10:30 AM

Eugene (@k3vg3n) targeting Chroma in the AI Infrastructure category for a total of $20,000 and 2 Master of Pwn points

Wednesday, October 7 - 11:15 AM

Team: Yassine Bengana (@cousky_), and Maxence Schmitt (@maxenceschmitt) of Doyensec (@doyensec) targeting Home Assistant Green in the Smart Home category for a total of $30,000 and 3 Master of Pwn points

Wednesday, October 7 - 11:45 AM

@_McCaulay targeting Canon imageFORCE 1643F Multifunction Copier in the Printers category for a total of $20,000 and 2 Master of Pwn points

Jack Dates of RET2 Systems (@ret2systems) targeting Sonos Era 300 in the Smart Home category for a total of $50,000 and 5 Master of Pwn points

Wednesday, October 7 - 1:00 PM

Dimitrios Valsamaras (@Ch0pin), Ken Gannon / 伊藤 剣 (@yogehi) using Djini.ai from Mobile Hacking Lab, Tenia Valsamara (@ir3l14) from CENSUS Labs targeting Samsung Galaxy S26 - Remote in the Mobile Phone category for a total of $50,000 and 5 Master of Pwn points

Taisic Yun (@taisic_) of Xint (@xint_official) targeting Oracle Autonomous AI Database in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points

Wednesday, October 7 - 1:30 PM

Shio Kudo (@shiosa1t) of GMO Flatt Security Inc. (@flatt_security) targeting Home Assistant Green in the Smart Home category for a total of $30,000 and 3 Master of Pwn points

Wednesday, October 7 - 2:30 PM

Nguyen Thanh Dat (@rewhiles), dungnm (@dungnm_) of Viettel Cyber Security (@vcslab) targeting Sonos Era 300 in the Smart Home category for a total of $50,000 and 5 Master of Pwn points

Interrupt Labs (@InterruptLabs) targeting Lexmark CX532adwe in the Printers category for a total of $20,000 and 2 Master of Pwn points

Wednesday, October 7 - 3:15 PM

Kyeongmin Kim (@hareh4ru) of KAIST Hacking Lab targeting Samsung Galaxy S26 - Remote in the Mobile Phone category for a total of $50,000 and 5 Master of Pwn points

PetoWorks (@petoworks) targeting Home Assistant Green in the Smart Home category for a total of $30,000 and 3 Master of Pwn points

Wednesday, October 7 - 3:30 PM

Ikotas Labs, Inc. targeting Oracle Autonomous AI Database in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points

Wednesday, October 7 - 4:45 PM

@_McCaulay targeting Garmin Index BPM in the Wellness category for a total of $20,000 and 2 Master of Pwn points

Rick de Jager and Filippo Cremonese of @zellic_io/@v12sec targeting Lexmark CX532adwe in the Printers category for a total of $20,000 and 2 Master of Pwn points

Wednesday, October 7 - 5:30 PM

Kyeongmin Kim (@hareh4ru) of KAIST Hacking Lab targeting Home Assistant Green in the Smart Home category for a total of $30,000 and 3 Master of Pwn points

PetoWorks (@petoworks) targeting Samsung Galaxy S26 - Remote in the Mobile Phone category for a total of $50,000 and 5 Master of Pwn points

Wednesday, October 7 - 5:45 PM

Mingeun Kim, Chulhan Park, SeokHun Lee, Inhyung Lee, Sehyun Baek, Nayeon Lee, Junseok Kim of Team MAMMOTH targeting Chroma in the AI Infrastructure category for a total of $20,000 and 2 Master of Pwn points

Wednesday, October 7 - 6:30 PM

Sina Kheirkhah (@SinSinology) of Summoning Team targeting Sonos Era 300 in the Smart Home category for a total of $50,000 and 5 Master of Pwn points

Wednesday, October 7 - 7:00 PM

@BoredPentester targeting Lexmark CX532adwe in the Printers category for a total of $20,000 and 2 Master of Pwn points

Wednesday, October 7 - 7:15 PM

@_McCaulay targeting Home Assistant Green in the Smart Home category for a total of $30,000 and 3 Master of Pwn points

Wednesday, October 7 - 7:30 PM

Alessandro Fanio Gonzalez targeting Chroma in the AI Infrastructure category for a total of $20,000 and 2 Master of Pwn points

Back to top

DAY THREE


Thursday, October 8 - 10:00 AM

Sina Kheirkhah (@SinSinology) and Aaron Christophel (@ATC1441) of Summoning Team (@SummoningTeam) targeting Philips Hue Bridge Pro in the Smart Home category for a total of $40,000 and 4 Master of Pwn points

Nikolaos Mourousias (@deltaclock) and Bruno Halltari (@BrunoModificato) of OtterSec targeting Oracle Autonomous AI Database in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points

Polina Smirnova (@moe_hw), Mikhail Evdokimov (@konatabrk) and Mate Zombor (@r4bbit_zm) of White Noise Club targeting Garmin Index BPM in the Wellness category for a total of $20,000 and 2 Master of Pwn points

Lucas Van Haaren (vhash, @LucasVanHaaren) and Hugo Leclercq (0xnasu) of FuzzingLabs (@FuzzingLabs) targeting Brother MFC-L8970CDW in the Printers category for a total of $20,000 and 2 Master of Pwn points

Thursday, October 8 - 11:15 AM

Tim Becker (@tjbecker) and Yves Bieri (@yves_bieri) of Xint (@xint_official) targeting Google Pixel 10 - Remote in the Mobile Phone category for a total of $300,000 and 30 Master of Pwn points

Thursday, October 8 - 12:15 PM

Ben Koo (@kiddo_pwn) and Evangelos Daravigkas (@freddo_1337) of Team DDOS targeting Home Assistant Green in the Smart Home category for a total of $30,000 and 3 Master of Pwn points

Thursday, October 8 - 1:00 PM

Connor Laidlaw & Matthew Keeley of Platform Security targeting Oracle Autonomous AI Database in the AI Infrastructure category for a total of $40,000 and 4 Master of Pwn points

Sina Kheirkhah (@SinSinology) and Aaron Christophel (@ATC1441) of Summoning Team (@SummoningTeam) targeting Canon imageFORCE 1643F Multifunction Copier in the Printers category for a total of $20,000 and 2 Master of Pwn points

Thursday, October 8 - 2:00 PM

Ikotas Labs, Inc. targeting Google Pixel 10 - Remote in the Mobile Phone category for a total of $300,000 and 30 Master of Pwn points

Thursday, October 8 - 2:30 PM

@_McCaulay targeting Philips Hue Bridge Pro in the Smart Home category for a total of $40,000 and 4 Master of Pwn points

Thursday, October 8 - 3:15 PM

Cong Thanh (@ExLuck99), Duc Hieu (@gr4ss341) and Nam Dung (@greengrass19000) targeting Brother MFC-L8970CDW in the Printers category for a total of $20,000 and 2 Master of Pwn points

Rintaro Kawasugi (@fubukiyokiyoki) of GMO Flatt Security Inc. (@flatt_security) targeting Chroma in the AI Infrastructure category for a total of $20,000 and 2 Master of Pwn points

Thursday, October 8 - 4:15 PM

BunkyoWesterns (@BunkyoWesterns) targeting Samsung Galaxy S26 - Remote in the Mobile Phone category for a total of $50,000 and 5 Master of Pwn points

Thursday, October 8 - 4:45 PM

Hank Chen (@Hank0438) of InnoEdge Labs targeting Philips Hue Bridge Pro in the Smart Home category for a total of $40,000 and 4 Master of Pwn points

Thursday, October 8 - 5:30 PM

Cong Thanh (@ExLuck99), Duc Hieu (@gr4ss341) and Nam Dung (@greengrass19000) targeting Lexmark CX532adwe in the Printers category for a total of $20,000 and 2 Master of Pwn points

Thursday, October 8 - 6:30 PM

Dimitrios Valsamaras (@Ch0pin), Ken Gannon / 伊藤 剣 (@yogehi) using Djini.ai from Mobile Hacking Lab, Tenia Valsamara (@ir3l14) from CENSUS Labs targeting Google Pixel 10 - Remote in the Mobile Phone category for a total of $300,000 and 30 Master of Pwn points

Thursday, October 8 - 7:00 PM

Chulhan Park, Mingeun Kim, SeokHun Lee, Inhyung Lee, Sehyun Baek, Nayeon Lee, Junseok Kim of Team MAMMOTH targeting Home Assistant Green in the Smart Home category for a total of $30,000 and 3 Master of Pwn points


Follow the action live! We'll be posting real-time updates and results throughout the competition on our blog and across social media. Stay up to date by following us on Twitter, Mastodon, LinkedIn, and Bluesky, and join the conversation using #Pwn2Own Ireland and #P2OIreland for continuing coverage.

The Apple Security Update Review for September 2026

Welcome back to our monthly look at Apple security patches. This release shows Apple is not immune to the new normal of AI-assisted vulnerability discovery as they release patches for 273 total CVEs.

For the September 2026 release, Apple released 273 unique CVEs across macOS 27 (Golden Gate), macOS Sequoia 15.8, macOS Tahoe 26.7, iOS / iPadOS 27, visionOS 27, watchOS 27, tvOS 27, iOS / iPadOS 26.7, Safari 27, and Xcode 27. This patch release actually happened a couple of days ago, but since Apple doesn’t provide CVSS scores or other severity information, it takes a couple of days to understand the full severity. Even with the additional time, there are many CVEs without a severity score. However, looking at the one that do have severity assigned by NVD or CISA-ADP, there are a few that truly stand out, including one under active exploit.

CVE-2026-65400 — Screen Sharing Server (9.8 CRITICAL, ⚠ CISA KEV).
This bug is confirmed by CISA to be actively exploited. A network attacker can authenticate to Screen Sharing without valid credentials, without user interaction. This component was first patched on August 6 and relisted in v27 as macOS 27/Tahoe 26.7 now carries the fix.

CVE-2026-65414 — Bluetooth (9.8 CRITICAL).
This is the highest-scored non-exploited bug in the release. It’s remote, network-vector arbitrary code execution with no privileges or interaction, and CISA tagged it "automatable: yes, technical impact: total." It spans all eight OS platforms, which is the broadest-reach critical vulnerability in the release and the most likely candidate to become a KEV entry.

CVE-2026-65346 — ImageIO (8.8 HIGH).
The bug sits at the top of the HIGH tier and is the most dangerous remote content bug: processing a malicious image leads to arbitrary code execution. ImageIO is the canonical zero-/one-click surface (images auto-rendered in Messages, previews), so it carries high real-world weaponization potential.

Two honorable mentions that matter because of a data caveat: CVE-2026-84607 (AVEVideoEncoder) — a sandbox-to-kernel arbitrary-code-execution bug — and CVE-2026-43790 (Kernel) — remote kernel memory corruption — are arguably more severe by impact than #3, but NVD hasn't scored either yet (both TBD), so they don't rank on the current evidence. Also worth noting: CVE-2026-43692 (CUPS) remote code execution and CVE-2026-84568 (autofs) root RCE both sit at the top of the HIGH band.

Here’s the full table of Apple patches and the products they affect:

Apple Security Updates — September 14, 2026 (v27) 273Total CVEs 134Scored 139TBD 2CRITICAL 46HIGH 84MEDIUM 2LOW

CVSS is the NVD primary score where available, otherwise CISA-ADP secondary; TBD = NVD has not scored it yet (most v27 CVEs are still under analysis). ⚠ KEV marks CVEs in CISA's Known Exploited Vulnerabilities catalog.

Apple security release — September 14, 2026 (version 27), 273 CVEs. CVSS/Severity from NVD (National Vulnerability Database) as of Sept 16, 2026. CVE IDs link to NVD. "Yes/No" indicates whether each update is affected.
CVE IDComponentImpactCVSSSeverity iOS / iPadOS 27 iOS / iPadOS 26.7 macOS 27 (Golden Gate) macOS Tahoe 26.7 macOS Sequoia 15.8 tvOS 27 watchOS 27 visionOS 27 Safari 27 Xcode 27
CVE-2026-65400 Screen Sharing Server An attacker on the network may be able to authenticate to Screen Sharing without valid credentials 9.8⚠ KEV CRITICAL NoNoYesYesNoNoNoNoNoNo
CVE-2026-65414 Bluetooth A remote attacker may be able to cause unexpected app termination or arbitrary code execution 9.8CRITICAL YesYesYesYesYesYesYesYesNoNo
CVE-2026-43692 CUPS A remote user may cause an unexpected app termination or arbitrary code execution 8.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-65346 ImageIO Processing an image may lead to arbitrary code execution 8.8HIGH NoNoNoNoYesYesYesYesNoNo
CVE-2026-43686 Kernel Connecting to a malicious NFS server may lead to kernel memory corruption 8.8HIGH YesYesYesYesYesYesYesYesNoNo
CVE-2026-65374 WebDAV Connecting to a malicious WebDAV server may result in code execution 8.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-43715 WebKit Processing maliciously crafted web content may lead to memory corruption 8.8HIGH NoYesNoNoNoNoNoNoNoNo
CVE-2026-43794 WebKit Processing maliciously crafted web content may lead to memory corruption 8.8HIGH NoNoNoNoNoYesYesYesNoNo
CVE-2026-65390 WebRTC Processing maliciously crafted web content may lead to memory corruption 8.8HIGH NoNoNoNoNoYesYesYesNoNo
CVE-2026-65391 WebRTC Processing maliciously crafted web content may lead to memory corruption 8.8HIGH NoNoNoNoNoYesYesYesNoNo
CVE-2026-43760 Screen Sharing Server An app may be able to access user-sensitive data 8.6HIGH NoNoNoYesNoNoNoNoNoNo
CVE-2026-84581 HFS Mounting a maliciously crafted disk image may cause unexpected system termination or corrupt kernel memory 8.4HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-84535 Automator An app may be able to break out of its sandbox 8.2HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-84516 CUPS Processing a maliciously crafted file may result in unexpected app termination or disclosure of process memory 8.1HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-65415 Kernel A local user may be able to cause unexpected system termination or read kernel memory 8.1HIGH YesNoYesNoNoYesYesYesNoNo
CVE-2026-84568 autofs An attacker with control of a network directory server may be able to execute arbitrary code with root privileges 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-84607 AVEVideoEncoder A sandboxed app may be able to execute arbitrary code with kernel privileges 7.8HIGH YesYesYesYesYesYesYesYesNoNo
CVE-2026-84631 Bluetooth An app may be able to gain root privileges 7.8HIGH NoNoYesNoNoNoNoNoNoNo
CVE-2026-43786 CoreServices An app may be able to gain root privileges 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-84575 CoreUI Processing a maliciously crafted file may lead to unexpected app termination 7.8HIGH YesNoYesYesYesYesYesYesNoNo
CVE-2026-43691 CUPS An app may be able to gain root privileges 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-43698 CUPS An app may be able to gain root privileges 7.8HIGH NoNoYesYesNoNoNoNoNoNo
CVE-2026-84505 Directory Utility An app may be able to gain root privileges 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-65362 Disk Images An app may be able to gain root privileges 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-64758 ImageIO Processing a maliciously crafted file may lead to unexpected app termination 7.8HIGH NoYesNoNoYesNoNoNoNoNo
CVE-2026-43684 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory 7.8HIGH NoYesYesNoYesNoNoNoNoNo
CVE-2026-43689 Kernel A malicious app may be able to gain root privileges 7.8HIGH YesYesYesNoNoNoNoYesNoNo
CVE-2026-86917 Kernel An app may be able to gain root privileges 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-64712 odproxyd An app may be able to gain root privileges 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-84515 SMB Connecting to a malicious SMB server may lead to kernel memory corruption 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-84506 udf An app may be able to execute arbitrary code with kernel privileges 7.8HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-64761 Accessibility An app may be able to identify what other apps a user has installed 7.5HIGH YesNoNoNoNoNoNoNoNoNo
CVE-2026-86895 CloudKit A local app may be able to read a persistent account identifier 7.5HIGH YesNoNoNoNoYesYesYesNoNo
CVE-2026-84563 CUPS An app may be able to cause unexpected system termination 7.5HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-84606 iCloud An app may be able to identify a user across reinstalls 7.5HIGH YesNoYesNoNoNoNoYesNoNo
CVE-2026-43661 ImageIO Processing a maliciously crafted image may corrupt process memory 7.5HIGH NoYesNoNoNoNoNoNoNoNo
CVE-2026-28969 IOKit An app may be able to cause unexpected system termination 7.5HIGH YesNoYesYesYesYesYesYesNoNo
CVE-2026-65343 Kernel A remote attacker may be able to cause unexpected system termination 7.5HIGH NoNoNoNoNoYesYesYesNoNo
CVE-2026-65364 Kernel A remote attacker may be able to cause unexpected system termination 7.5HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-86894 libxpc An app may be able to break out of its sandbox 7.5HIGH NoNoYesNoNoNoNoNoNoNo
CVE-2026-84543 SMB Connecting to a malicious SMB server may cause unexpected system termination or corrupt kernel memory 7.5HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-84553 smbx A remote attacker may be able to cause a denial-of-service 7.5HIGH NoNoYesYesYesNoNoNoNoNo
CVE-2026-28930 Spotlight An app may be able to access protected user data 7.5HIGH NoNoNoNoYesNoNoNoNoNo
CVE-2026-86904 Watch App An app may be able to track users across apps and websites without permission 7.5HIGH YesYesNoNoNoNoYesNoNoNo
CVE-2026-64752 CoreMedia Processing a maliciously crafted image may lead to arbitrary code execution 7.3HIGH YesNoYesNoNoNoNoYesNoNo
CVE-2026-84611 SceneKit Processing a maliciously crafted 3D model may lead to memory corruption 7.3HIGH YesYesYesYesYesYesYesYesNoNo
CVE-2026-84632 SceneKit Processing a maliciously crafted 3D model may lead to memory corruption 7.3HIGH YesYesYesYesYesYesYesYesNoNo
CVE-2026-64736 IOMobileFrameBuffer An app may be able to cause unexpected system termination or corrupt kernel memory 7.1HIGH NoNoNoNoYesYesYesYesNoNo
CVE-2026-65349 Kernel An app may be able to cause unexpected system termination or read kernel memory 6.6MEDIUM NoNoNoNoYesYesYesYesNoNo
CVE-2026-84537 SMB An app may be able to cause unexpected system termination or corrupt kernel memory 6.6MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-43788 Spotlight Processing a maliciously crafted file may lead to a denial-of-service or potentially disclose memory contents 6.6MEDIUM NoNoYesNoNoNoNoNoNoNo
CVE-2026-86882 Accelerate Framework Processing a maliciously crafted image may lead to unexpected process termination 6.5MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-84519 AppleDouble Mounting a disk image with maliciously crafted files may lead to unexpected system termination 6.5MEDIUM YesYesYesYesYesNoNoNoNoNo
CVE-2026-86879 Baseband A remote attacker may be able to cause a denial-of-service 6.5MEDIUM YesNoNoNoNoNoNoNoNoNo
CVE-2026-86885 Baseband An attacker in radio range may be able to cause unexpected system termination 6.5MEDIUM YesNoNoNoNoNoNoNoNoNo
CVE-2026-65412 CoreText Processing web content may lead to a denial-of-service 6.5MEDIUM YesYesYesYesYesNoYesYesNoNo
CVE-2026-84596 CoreText Processing a maliciously crafted font may result in the disclosure of process memory 6.5MEDIUM YesNoYesNoNoYesYesYesNoNo
CVE-2026-84597 FontParser Processing a maliciously crafted font may result in the disclosure of process memory 6.5MEDIUM YesNoYesNoNoYesYesYesNoNo
CVE-2022-3437 Heimdal A user in a privileged network position may be able to leak sensitive user information 6.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-28934 HFS Mounting a malicious disk image may cause unexpected system termination 6.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-65347 ImageIO Processing an image may lead to a denial-of-service 6.5MEDIUM NoNoNoNoNoYesYesYesNoNo
CVE-2026-65395 ImageIO Processing a maliciously crafted image may result in memory corruption 6.5MEDIUM YesYesYesYesYesYesNoYesNoNo
CVE-2026-43687 Kernel Connecting to a malicious NFS server may disclose kernel memory 6.5MEDIUM YesYesYesYesNoYesYesYesNoNo
CVE-2026-65330 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory 6.5MEDIUM NoNoNoNoYesYesYesYesNoNo
CVE-2026-84538 Kernel A remote attacker may be able to cause a denial-of-service 6.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-84588 Kernel Mounting a maliciously crafted disk image may cause unexpected system termination or corrupt kernel memory 6.5MEDIUM NoNoYesNoNoNoNoNoNoNo
CVE-2026-84487 SceneKit Processing a maliciously crafted file may result in disclosure of process memory 6.5MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-43719 SMB Mounting a maliciously crafted SMB network share may lead to system termination 6.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-65365 SMB Connecting to a malicious SMB share may disclose kernel memory 6.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-84536 SMB Connecting to a malicious SMB server may lead to unexpected system termination 6.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-43677 WebDAV Connecting to a malicious WebDAV server may lead to unexpected app termination 6.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-64715 WebKit Processing maliciously crafted web content may lead to an unexpected process crash 6.5MEDIUM NoNoNoNoNoYesYesYesNoNo
CVE-2026-64753 WebKit Processing maliciously crafted web content may disclose sensitive user information 6.5MEDIUM YesNoYesNoNoYesYesYesYesNo
CVE-2026-64787 WebKit Processing maliciously crafted web content may lead to an unexpected process termination 6.5MEDIUM NoNoNoNoNoYesYesYesNoNo
CVE-2026-64778 WebKit History Visiting a maliciously crafted website may leak sensitive data 6.5MEDIUM NoNoNoNoNoYesYesYesNoNo
CVE-2026-84560 Bluetooth An app may gain unauthorized access to Bluetooth 6.1MEDIUM YesNoYesNoNoYesYesYesNoNo
CVE-2026-84619 Kernel An app may be able to cause unexpected system termination or write kernel memory 6.1MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-84554 CUPS An attacker in a privileged network position may be able to cause a denial-of-service 5.9MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-43664 Accessibility An app may be able to access sensitive user data 5.5MEDIUM YesYesYesYesYesYesYesNoNoNo
CVE-2026-65404 Accounts A malicious application may be able to bypass Privacy preferences 5.5MEDIUM YesNoYesNoNoNoNoNoNoNo
CVE-2026-84523 APFS An app may be able to cause unexpected system termination or write kernel memory 5.5MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-84586 Apple Account A malicious application may be able to leak sensitive user information 5.5MEDIUM NoNoYesNoNoNoYesNoNoNo
CVE-2026-65407 AppleAVD An app may be able to cause unexpected system termination 5.5MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-84593 AppleKeyStore An app may be able to cause unexpected system termination 5.5MEDIUM YesNoNoNoNoNoNoNoNoNo
CVE-2026-43763 ATS An app may be able to read files outside of its sandbox 5.5MEDIUM NoNoNoYesYesNoNoNoNoNo
CVE-2026-86905 Authentication Services An app may be able to delete credentials stored in Keychain 5.5MEDIUM YesNoYesNoNoNoNoYesNoNo
CVE-2026-43737 CoreMotion An app may be able to access motion data from headphones without user consent 5.5MEDIUM YesYesYesYesYesYesYesNoNoNo
CVE-2026-43738 CoreUI Processing a maliciously crafted asset catalog may result in disclosure of process memory 5.5MEDIUM YesNoYesNoNoNoNoNoNoNo
CVE-2026-84489 CoreUI An app may be able to cause a denial of service 5.5MEDIUM YesNoYesNoNoNoNoNoNoNo
CVE-2026-84534 file_cmds Extracting a maliciously crafted archive may allow an attacker to write arbitrary files 5.5MEDIUM YesYesYesYesYesNoNoYesNoNo
CVE-2026-65409 Foundation An app may be able to cause a denial of service 5.5MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-64756 Image Capture An app may be able to access user-sensitive data 5.5MEDIUM YesNoYesYesYesNoNoNoNoNo
CVE-2026-64760 IOSurfaceAccelerator An app may be able to leak sensitive kernel state 5.5MEDIUM YesNoYesNoNoYesYesYesNoNo
CVE-2026-65401 Kernel An app may be able to cause unexpected system termination 5.5MEDIUM NoNoYesYesNoNoNoNoNoNo
CVE-2026-65402 Kernel An app may be able to cause unexpected system termination 5.5MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-65405 Kernel An app may be able to determine kernel memory layout 5.5MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-84517 Kernel An app may be able to cause unexpected system termination 5.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-84521 Kernel An app may be able to cause unexpected system termination 5.5MEDIUM YesYesYesYesYesNoNoYesNoNo
CVE-2026-86903 Kernel An app may be able to disclose kernel memory 5.5MEDIUM YesNoYesNoNoYesYesYesNoNo
CVE-2026-86883 Managed Configuration An app may be able to access sensitive user data 5.5MEDIUM YesNoNoNoNoNoNoYesNoNo
CVE-2026-43741 Messages An app may be able to access protected user data 5.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-84491 Photos Storage An app may be able to access sensitive user data 5.5MEDIUM YesYesYesNoNoYesYesYesNoNo
CVE-2026-84576 QuartzCore An app may be able to access sensitive user data 5.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-84555 Sandbox An app may be able to access sensitive user data 5.5MEDIUM NoNoYesNoYesNoNoNoNoNo
CVE-2026-65413 SceneKit An app may be able to cause a denial of service 5.5MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-28937 Terminal An app may be able to access sensitive user data 5.5MEDIUM NoNoYesNoNoNoNoNoNoNo
CVE-2026-64718 WebKit Canvas Processing maliciously crafted web content may lead to an unexpected Safari crash 5.5MEDIUM YesYesYesNoNoNoNoYesYesNo
CVE-2026-65393 Xcode IDE An app may be able to access user-sensitive data 5.5MEDIUM NoNoYesNoNoNoNoNoNoYes
CVE-2026-84617 XPC An app may be able to access sensitive user data 5.5MEDIUM YesYesYesYesYesYesNoNoNoNo
CVE-2026-64788 IOGPUFamily Processing maliciously crafted web content may lead to memory corruption 5.4MEDIUM NoNoNoNoNoNoYesYesNoNo
CVE-2026-65341 WebKit Processing maliciously crafted web content may lead to memory corruption 5.4MEDIUM NoNoNoNoNoYesYesYesNoNo
CVE-2026-34979 CUPS An attacker in a privileged network position may be able to cause a denial-of-service 5.3MEDIUM NoNoYesNoNoNoNoNoNoNo
CVE-2026-86876 CoreMedia A sandboxed process may be able to circumvent sandbox restrictions 5.2MEDIUM YesYesYesYesYesNoYesYesNoNo
CVE-2026-86889 Security An attacker in a privileged network position may be able to intercept network traffic 4.8MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-84492 Graphics An app may be able to cause unexpected system termination 4.7MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-84630 Kernel An app may be able to cause unexpected system termination 4.7MEDIUM YesYesYesYesYesYesYesYesNoNo
CVE-2026-43690 SMB A local user may be able to read kernel memory 4.7MEDIUM NoNoYesYesYesNoNoNoNoNo
CVE-2026-84518 Safari A malicious website may be able to determine what apps a user has installed 4.3MEDIUM YesNoYesNoNoNoNoNoYesNo
CVE-2026-43795 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-64780 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-64781 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-64784 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65331 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65332 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65333 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65334 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65335 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65336 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65337 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65338 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65340 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-65351 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 4.3MEDIUM NoNoNoNoNoNoNoYesNoNo
CVE-2026-64782 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash 3.1LOW NoNoNoNoNoNoNoYesNoNo
CVE-2026-64779 WebKit Storage Processing maliciously crafted web content may lead to an unexpected Safari crash 3.1LOW NoNoNoNoNoNoNoYesNoNo
CVE-2026-86910 APFS An application may be able to access restricted files TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-86888 App Store A local app may be able to read a persistent account identifier TBDTBD YesNoYesYesNoYesYesYesNoNo
CVE-2026-84587 AppKit An app may be able to access protected user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-20683 Apple Account An app may be able to use the Sign In With Apple authentication flow to access the user's Apple Account TBDTBD YesNoYesYesYesNoNoYesNoNo
CVE-2026-84601 Apple Intelligence An app may be able to bypass Apple Intelligence security prompts TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-65408 Apple Neural Engine An app may be able to cause unexpected system termination TBDTBD YesYesYesYesYesNoNoNoNoNo
CVE-2026-84520 AppleFDEKeyStore A local attacker may be able to cause unexpected system termination or corrupt kernel memory TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-65381 AppleMobileFileIntegrity A malicious app may be able to break out of its sandbox TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84522 Archive Utility An app may be able to access sensitive user data TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84584 Archive Utility An app may be able to break out of its sandbox TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-65342 ATS An app may be able to access sensitive user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84525 ATS An app may be able to access user-sensitive data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-65339 Audio An app may be able to leak sensitive user information TBDTBD NoNoNoNoYesYesYesYesNoNo
CVE-2026-84583 AuthKit A local app may be able to read a persistent account identifier TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84570 autofs An app may be able to bypass Gatekeeper checks TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-65410 AVEVideoEncoder An app may be able to cause unexpected system termination TBDTBD YesYesYesYesNoYesYesYesNoNo
CVE-2026-84616 AVEVideoEncoder An app may be able to cause unexpected system termination TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-65406 BackgroundAssets An app may be able to access sensitive user data TBDTBD YesYesYesYesYesYesNoYesNoNo
CVE-2026-86878 Camera An app may be able to access sensitive user data TBDTBD YesNoNoNoNoNoNoNoNoNo
CVE-2026-84567 cd9660 An app may be able to cause unexpected system termination TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-86893 CloudKit An app may be able to read device name TBDTBD YesNoNoNoNoYesYesYesNoNo
CVE-2026-65399 copyfile An archive may be able to bypass Gatekeeper TBDTBD YesYesYesYesYesNoYesYesNoNo
CVE-2026-86891 Core Bluetooth An app may be able to access Bluetooth device information TBDTBD NoNoYesYesYesNoYesNoNoNo
CVE-2026-43683 CoreDrag An app may be able to cause unexpected process termination or disclose process memory TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-43789 CoreMedia An app may be able to access user-sensitive data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-65344 CoreMedia Processing a maliciously crafted video file may lead to unexpected app termination TBDTBD YesYesYesYesYesYesNoYesNoNo
CVE-2026-43702 CoreMedia Video Toolbox Processing a maliciously crafted video file may lead to unexpected app termination or corrupt process memory TBDTBD NoYesNoYesYesNoNoNoNoNo
CVE-2026-84624 CoreML A sandboxed app may be able to access restricted files TBDTBD YesYesYesYesYesNoNoYesNoNo
CVE-2026-84559 CoreServices A malicious application may be able to access restricted files TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84574 CoreServices An app may be able to bypass Privacy preferences TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84511 CoreUI Processing a maliciously crafted asset catalog may lead to unexpected process termination TBDTBD YesNoYesYesYesYesYesYesNoNo
CVE-2026-84571 CoreUI Processing a maliciously crafted image may lead to unexpected app termination TBDTBD YesNoYesNoNoYesYesYesNoNo
CVE-2026-64790 CUPS An app may be able to gain elevated privileges TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84540 CUPS An app may be able to access sensitive user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84541 CUPS An application may be able to access restricted files TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84612 DeviceCheck An app may be able to read persistent device identifiers TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84512 Disk Images Mounting a maliciously crafted disk image may cause unexpected system termination or corrupt kernel memory TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84550 Disk Images An app may be able to cause unexpected system termination TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84552 Disk Images An app may be able to cause unexpected system termination TBDTBD YesYesYesYesYesNoNoNoNoNo
CVE-2026-84565 Disk Images Processing a maliciously crafted disk image may lead to unexpected app termination TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84510 exFAT Mounting a maliciously crafted volume may lead to unexpected system termination TBDTBD YesYesYesYesYesNoNoNoNoNo
CVE-2026-86900 exFAT Mounting a maliciously crafted exFAT volume may cause unexpected system termination or kernel memory disclosure TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-86901 exFAT Mounting a maliciously crafted exFAT volume may cause unexpected system termination or kernel memory disclosure TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-43785 File Bookmark An app may be able to modify a file it only had permission to read TBDTBD YesNoYesYesYesYesNoYesNoNo
CVE-2026-43688 Filters Processing a maliciously crafted file may lead to unexpected app termination TBDTBD YesNoYesNoNoNoNoNoNoNo
CVE-2026-84524 FontParser Processing a maliciously crafted font file may lead to unexpected app termination TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84569 Foundation An app may be able to access sensitive user data TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-86911 Foundation A malicious app may be able to bypass clickjacking protections for secure prompts TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84618 Game Center An app may be able to access sensitive user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84533 Heimdal An attacker in a privileged network position may be able to modify network traffic TBDTBD YesNoYesNoNoYesYesNoNoNo
CVE-2026-64714 ImageIO Processing a maliciously crafted image may lead to a denial-of-service TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84564 ImageIO Processing a maliciously crafted image may result in disclosure of process memory TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-86869 ImageIO Processing a maliciously crafted image may lead to unexpected app termination TBDTBD NoYesYesNoNoNoNoNoNoNo
CVE-2026-43743 IOGPUFamily An app may be able to cause unexpected system termination TBDTBD NoYesNoYesNoNoNoNoNoNo
CVE-2026-65398 IOMobileFrameBuffer An app may be able to cause unexpected system termination or corrupt kernel memory TBDTBD YesNoYesNoNoYesYesYesNoNo
CVE-2026-65354 iWork A malicious app may be able to break out of its sandbox TBDTBD YesNoYesNoNoNoNoNoNoNo
CVE-2026-28935 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory TBDTBD NoNoNoNoYesYesYesYesNoNo
CVE-2026-28968 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-43790 Kernel A remote attacker may be able to cause unexpected system termination or corrupt kernel memory TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-65358 Kernel An app may be able to cause unexpected system termination TBDTBD YesNoYesYesYesYesYesYesNoNo
CVE-2026-65359 Kernel A local user may be able to cause unexpected system termination or read kernel memory TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-65360 Kernel An app may be able to cause unexpected system termination TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-65369 Kernel A malicious application may bypass Gatekeeper checks TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-65371 Kernel An app may be able to disclose kernel memory TBDTBD NoNoNoNoYesNoNoNoNoNo
CVE-2026-65377 Kernel An app may be able to cause unexpected system termination TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84507 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84530 Kernel An app may be able to disclose kernel memory TBDTBD YesYesYesYesNoYesYesYesNoNo
CVE-2026-84544 Kernel Connecting to a malicious NFS server may cause unexpected system termination or corrupt kernel memory TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84549 Kernel Connecting to a malicious NFS server may cause unexpected system termination or corrupt kernel memory TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84558 Kernel An app may be able to cause unexpected system termination TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84561 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84566 Kernel A local attacker may be able to cause unexpected system termination or corrupt kernel memory TBDTBD YesYesYesYesYesNoNoNoNoNo
CVE-2026-84602 Kernel An app may be able to cause unexpected system termination TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84622 Kernel An app with root privileges may be able to read uninitialized kernel memory TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84514 Kext Management An app may be able to modify protected parts of the file system TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84556 Keychain Access An app may be able to access sensitive user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-65382 LaunchServices An app may be able to access sensitive user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-86870 libarchive Processing a maliciously crafted file may lead to unexpected app termination TBDTBD YesYesYesNoNoNoYesYesNoNo
CVE-2026-84577 libxpc An app may be able to bypass sandbox restrictions TBDTBD NoNoYesYesNoNoNoNoNoNo
CVE-2026-43787 Mail An attacker in a privileged network position may be able to leak sensitive user information TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84573 Mail An app may be able to access sensitive user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84628 MediaRemote A sandboxed app may be able to access the System Keychain TBDTBD YesNoYesNoNoYesYesYesNoNo
CVE-2026-86924 MobileAccessoryUpdater Connecting a malicious accessory may cause unexpected system termination TBDTBD YesYesYesYesNoNoNoNoNoNo
CVE-2026-65411 MobileBackup An app may be able to modify protected parts of the file system TBDTBD YesYesNoNoNoNoNoYesNoNo
CVE-2026-84598 MobileBackup An attacker with physical access to a trust-paired device may be able to read and write arbitrary files TBDTBD YesYesNoNoNoNoNoNoNoNo
CVE-2026-84497 Model I/O Opening a maliciously crafted file may lead to unexpected process termination TBDTBD YesYesYesYesYesYesNoYesNoNo
CVE-2026-84615 Music An app may be able to access sensitive user data TBDTBD YesYesNoNoNoYesNoYesNoNo
CVE-2026-43695 NetworkExtension An app may be able to access sensitive user data TBDTBD YesNoYesYesYesYesYesYesNoNo
CVE-2026-84585 NetworkExtension An app may be able to access local network devices without user consent TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84626 NetworkExtension An app may be able to identify what other apps a user has installed TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-86902 NSDocument An app may be able to access sensitive user data TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84629 Photos Storage An app may be able to fingerprint the user TBDTBD YesNoNoNoNoYesYesYesNoNo
CVE-2026-84623 Power Management An app may be able to fingerprint the device TBDTBD YesYesNoNoNoNoNoNoNoNo
CVE-2026-84578 quarantine An app may be able to break out of its sandbox TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84580 quarantine An app may be able to break out of its sandbox TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84548 Quick Look Processing a maliciously crafted document may lead to an out-of-bounds read TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-28966 RealityKit Processing a maliciously crafted file may lead to unexpected app termination TBDTBD YesYesYesYesYesYesNoYesNoNo
CVE-2026-84532 RealityKit Opening a maliciously crafted file may cause unexpected process termination or disclose process memory TBDTBD YesYesYesYesYesYesNoYesNoNo
CVE-2026-65403 Reminders An app may be able to access sensitive user data TBDTBD YesYesYesYesYesNoYesYesNoNo
CVE-2026-86897 Safe Browsing An app may be able to access sensitive user data TBDTBD YesYesYesNoNoNoNoYesYesNo
CVE-2026-65380 Sandbox An app may be able to access protected user data TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84551 Sandbox An app may be able to bypass network restrictions TBDTBD YesNoYesNoNoNoYesYesNoNo
CVE-2026-84603 Sandbox Profiles An app may be able to access sensitive user data TBDTBD YesNoNoNoNoNoYesYesNoNo
CVE-2026-84625 Sandbox Profiles An app may be able to fingerprint the user TBDTBD YesNoYesNoNoNoYesYesNoNo
CVE-2026-43697 SceneKit Processing a maliciously crafted 3D file may lead to an out-of-bounds read TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84526 SceneKit Processing a maliciously crafted 3D scene may lead to unexpected process termination TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84546 SceneKit Processing a maliciously crafted 3D model may lead to memory corruption TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84620 SceneKit Processing a maliciously crafted 3D model may lead to memory corruption TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84531 Security Processing maliciously crafted NTLM input may lead to unexpected app termination TBDTBD YesNoYesNoNoNoNoNoNoNo
CVE-2026-86881 Security An attacker with a compromised intermediate certificate authority may be able to issue certificates with arbitrary extended key usages TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-84600 Shortcuts A malicious shortcut may be able to send messages without user confirmation TBDTBD YesNoYesNoNoYesYesYesNoNo
CVE-2026-86884 Siri An app may be able to access sensitive user data TBDTBD YesNoYesNoNoYesYesNoNoNo
CVE-2026-86890 Siri Suggestions An attacker with physical access to a locked device may be able to view sensitive user information TBDTBD YesYesNoNoNoNoNoNoNoNo
CVE-2026-65376 SMB An app may be able to cause unexpected system termination TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84509 SMB Connecting to a malicious SMB server may lead to unexpected system termination TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84609 Software Update An app may be able to modify protected system files TBDTBD YesNoYesYesYesYesYesYesNoNo
CVE-2026-65361 SoftwareUpdate An app may be able to access sensitive user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-65378 Spotlight An app may be able to access sensitive user data TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84621 Spotlight An app may be able to access sensitive user data TBDTBD YesYesYesYesYesNoNoNoNoNo
CVE-2026-86892 SpringBoard An app may be able to cause a denial-of-service TBDTBD YesYesNoNoNoNoNoYesNoNo
CVE-2026-65345 Storage An app may be able to access user-sensitive data TBDTBD YesYesYesYesYesNoNoNoNoNo
CVE-2026-65348 Storage An app may be able to modify protected parts of the file system TBDTBD YesYesYesYesYesNoNoNoNoNo
CVE-2026-43791 StorageKit An app may be able to read arbitrary files TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-84513 Symptom Framework A malicious application may be able to determine a user's current location TBDTBD YesYesYesYesYesYesYesYesNoNo
CVE-2026-65383 System Settings An app may bypass Gatekeeper checks TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-86909 System Settings An app may be able to bypass Gatekeeper checks TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84527 TCC An app may be able to access sensitive user data TBDTBD YesNoYesYesYesYesYesYesNoNo
CVE-2026-84589 TCC An app may be able to modify Privacy preferences TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-86886 TCC An app may be able to modify protected system files TBDTBD YesYesNoNoNoNoYesNoNoNo
CVE-2026-65329 Telephony An attacker in a privileged network position may be able to bypass IPSec authentication and intercept network traffic TBDTBD YesNoNoNoNoNoNoNoNoNo
CVE-2026-86887 Time Zone An app may be able to bypass certain Privacy preferences TBDTBD YesYesNoNoNoNoNoYesNoNo
CVE-2026-43696 Touch Bar An app may be able to capture Touch Bar content without authorization TBDTBD NoNoYesNoNoNoNoNoNoNo
CVE-2026-84572 udf An app may be able to cause unexpected system termination or read kernel memory TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-28899 WebDAV An app may bypass Gatekeeper checks TBDTBD NoNoYesYesYesNoNoNoNoNo
CVE-2026-65375 WebDAV An app may be able to cause unexpected system termination TBDTBD NoNoYesNoYesNoNoNoNoNo
CVE-2026-84635 WebKit Processing maliciously crafted web content may lead to an unexpected process termination TBDTBD YesNoYesNoNoYesYesYesYesNo
CVE-2026-86898 WebKit Opening a maliciously crafted webarchive file may lead to universal cross-site scripting TBDTBD YesNoYesNoNoNoNoYesYesNo
CVE-2026-84636 Wi-Fi Connectivity An app may be able to access sensitive user data TBDTBD YesNoNoNoNoYesYesYesNoNo
CVE-2026-43674 Wi-Fi3 An attacker with physical access to an unlocked device may be able to view Wi-Fi passwords without authentication TBDTBD YesNoNoNoNoNoNoNoNoNo

We’ll continue these macOS updates if people find them useful. Stay tuned for the regularly schedule Patch Tuesday blog covering Adobe and Microsoft.

The September 2026 Security Update Review

Whelp, here we are. Deep into the new normal. With nearly 1,000 CVEs coming out from Microsoft and a healthy release from Adobe as well, there’s a phrase from my military days that comes to mind: embrace the suck. Take an extended break from your regularly scheduled activities as we take a look at the latest security patches from Adobe and Microsoft. If you’d rather watch the full video recap covering the entire release, you can check it out here:

Adobe Patches for September 2026

For the first part of the August release, Adobe released 10 bulletins addressing 172 unique CVEs in Adobe ColdFusion, Acrobat Reader, Commerce (two bulletins), Campaign Classic, Experience Manager, Photoshop, Illustrator, Animate, and Adobe Photoshop Mobile. A total of 22 of these were submitted through the ZDI program.

Here’s this month’s overview table:

Adobe Patches for September 2026

Adobe Patches for September 2026

Bulletin ID Product CVE Count Highest Severity Highest CVSS Exploited Deployment Priority
APSB26-146 Adobe Commerce 1 Critical 10.0 Yes 1
APSB26-142 Adobe Campaign Classic 1 Critical 10.0 No 1
APSB26-119 Adobe ColdFusion 9 Critical 9.9 No 1
APSB26-98 Adobe Experience Manager 107 Critical 9.9 No 2
APSB26-138 Adobe Commerce 8 Critical 9.3 No 2
APSB26-141 Adobe Acrobat and Reader 32 Critical 8.8 No 2
APSB26-130 Adobe Photoshop 8 Critical 8.6 No 3
APSB26-131 Adobe Illustrator 3 Critical 8.6 No 3
APSB26-132 Adobe Animate 1 Critical 8.2 No 3
APSB26-136 Adobe Photoshop Mobile 2 Important 7.4 No 3
TOTAL 10 bulletins 172

APSB26-146 (Adobe Commerce) is an out-of-band advisory posted September 7, 2026 addressing CVE-2026-75650, a CVSS 10.0 template-engine injection that Adobe reports is being exploited in the wild. All other bulletins were released on Patch Tuesday, September 8, 2026. No public proof-of-concept is noted for any bulletin.

Clearly, the priority here is the Commerce bug currently under active attack. Campaign Classic and ColdFusion also clock in with a deployment priority of 1. The Acrobat Reader should also be a priority. It contains 32 CVEs, including many code execution bugs, and PDFs are a favorite of attackers. The Experience Manager has plenty of CVEs being patched and also rates a deployment priority of 2.

Besides the one bug in Commerce, none of the other Adobe bugs receiving patches this month are listed as publicly known or under active attack at the time of release.

Microsoft Patches for September 2026

It’s a new record release from Microsoft, but, again, that seems to be the new normal. As always, counting this beast is tricky, but I see 972 new CVEs rolling out from Redmond this month. As with last month, only a single CVE is listed as being under active attack, so that’s something, I suppose. As for the products affected by this release, we have Windows and Windows components, Office and Office Components, Azure and Azure Components, .NET and Visual Studio, Active Directory, Copilot Studio, Dynamics, Edge (Chromium-based), DHCP Server and Client, DNS Server, Exchange Server, Teams for Android, OpenSSH, Remote Desktop Client and Server, Skype for Business, Biometric Service, SQL Server, Windows Hello, Xbox, and Defender. Along with the external and Chromium bugs being documented this month, this drives the total CVE count to a staggering 997. Of these new CVEs, 114 are rated Critical, with the rest being rated Important.

To provide a little historical context on how many CVEs have been patched by Microsoft this year, let’s take a look at some year-over-year totals:

On the one hand, congrats to the security gnomes at Microsoft for being able to patch bugs at this rate. On the other hand, AI-assisted vulnerability discovery shows no signs of slowing down. However, we have not seen a correlating spike in active exploits – yet.  

As always, we’ll start with the bugs under active attack and move on from there.  

-              CVE-2026-81963 - Windows Update Stack Elevation of Privilege Vulnerability
This is the first bug being exploited in the wild, but we know little about how broadly that exploitation is. The bug itself is a privilege escalation in the Update Stack, which is worrisome, but I doubt the automatic update process itself is compromised. More likely is that this bug is being combined with a code execution bug to spread malware or ransomware. Patch this one quickly.

-              CVE-2026-85880 - Windows Advanced Local Procedure Call (ALPC) Elevation of Privilege Vulnerability
This is the other bug currently being exploited, and it is also a privilege escalation bug. These types of bugs must be triggered by the user, but they can hide within documents, PDFs, and other attachments. As with the Update Stack EoP, we don’t know how widespread these exploits may be, so assume they are coming for you and patch quickly.

-              CVE-2026-55007 - Microsoft Exchange Server Remote Code Execution Vulnerability
There are several Exchange patches this month, but despite the CVSS rating, I find this one most important. A remote, unauthenticated attacker could get code execution on an affected Exchange server just by sending an email with a malicious Visio attachment. The code execution occurs when the server processes the mail – no need even for the Preview Pane. Microsoft states the exploit would be unreliable, but the attacker only needs to get it right once. Schedule your downtime and update your Exchange servers with haste.

 -              CVE-2026-80097 - Microsoft Authenticator Elevation of Privilege Vulnerability
This is the worst type of privilege escalation as it uses a bug in the authentication system itself. An attacker would need to install a malicious app on an Android device, then convince a user to complete the authentication sequence. Once done, the attacker gets the auth tokens and can access resources as the affected user. If you have a large Android user base, best not to ignore this one.

-              CVE-2026-69465 - Microsoft Office SharePoint Remote Code Execution Vulnerability
I count 17 different SharePoint bugs in this release, with four leading to code execution. On its own, this bug doesn’t look like the worst, but SharePoint has been a popular target recently, and these are the types of bugs being used. An authenticated user can submit a page that bypasses a control-safety check, causing the affected server to load code from a filesystem under the attacker’s control. If you have SharePoint servers accessible from the internet, test and deploy these updates quickly.

-              CVE-2026-65669 - Microsoft SQL Server Elevation of Privilege Vulnerability
Speaking of AI-assisted code audits, there are over 60 patches for SQL Server in the September release. This bug even has an AI component, as the attacker would need to convince a user to submit specially crafted instructions to SQL Copilot in SQL Server Management Studio. So there’s the user interaction component, but if they succeed, the attacker could gain access to the database at the user’s permission level. Patching SQL Server will not be trivial this month, so take your time with your testing and really guard those SQL Servers that may be connected to the Internet.

-              CVE-2026-69525 - Remote Desktop Services Remote Code Execution Vulnerability
This CVSS 9.8 bug allows remote, unauthenticated attackers to run arbitrary code on affected systems via a Use-After-Free bug. Microsoft notes it needs to be an “in-network attacker”, but the CVSS still says Network. Since many enterprises rely on RDP, I would treat this one seriously and test and deploy the patch soonest.

So where are the wormable bugs, you may ask? Well, quite frankly, there are too many to single out. I count 20 different patches that could all be classified as wormable.  In each of these cases, a remote, unauthenticated attacker could get arbitrary code execution on affected systems with no user interaction. While some might be more exploitable than others, having 20 of them in a single release is something else. These are the ones I found (presented in no particular order):

  • CVE-2026-69510 – Windows DHCP Server Remote Code Execution Vulnerability

  • CVE-2026-69524 – Windows Active Directory Domain Services Remote Code Execution Vulnerability

  • CVE-2026-69530 – Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability

  • CVE-2026-69579 – Windows Message Queuing Remote Code Execution Vulnerability

  • CVE-2026-69590 – Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability

  • CVE-2026-69595 – Windows Services for NFS ONCRPC XDR Driver Remote Code Execution Vulnerability

  • CVE-2026-69730 – Windows DNS Server Remote Code Execution Vulnerability (SigRed’s spiritual successor)

  • CVE-2026-69858 – Windows DNS Server Remote Code Execution Vulnerability

  • CVE-2026-72936 – Windows SMB Client Remote Code Execution Vulnerability

  • CVE-2026-72979 – Windows DHCP Server Remote Code Execution Vulnerability

  • CVE-2026-72981 – IP Helper Remote Code Execution Vulnerability

  • CVE-2026-72982 – Windows Netlogon Remote Code Execution Vulnerability

  • CVE-2026-72983 – Internet Connection Sharing (ICS) Remote Code Execution Vulnerability

  • CVE-2026-72987 – Windows DNS Remote Code Execution Vulnerability

  • CVE-2026-73009 – Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability

  • CVE-2026-73010 – Microsoft Failover Cluster Remote Code Execution Vulnerability

  • CVE-2026-78444 – Microsoft Failover Cluster Remote Code Execution Vulnerability

  • CVE-2026-78449 – Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability

  • CVE-2026-78450 – Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability

  • CVE-2026-83997 – Windows Message Queuing Remote Code Execution Vulnerability

Here’s the full list of CVEs released by Microsoft for September 2026:

CVE Title Severity CVSS Public Exploited Type
CVE-2026-85880 Windows Advanced Local Procedure Call (ALPC) Elevation of Privilege Vulnerability Important 7.8 No Yes EoP
CVE-2026-81963 Windows Update Stack Elevation of Privilege Vulnerability Important 7.8 No Yes EoP
CVE-2026-70352 ** Azure AI Language Elevation of Privilege Vulnerability Critical 10 No No EoP
CVE-2026-69857 ** Azure Cosmos DB Spoofing Vulnerability Critical 8.5 No No Spoofing
CVE-2026-80098 ** Copilot Studio Elevation of Privilege Vulnerability Critical 9.3 No No EoP
CVE-2026-73006 DirectWrite Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-83941 ** Entra ID Elevation of Privilege Vulnerability Critical 9.9 No No EoP
CVE-2026-72986 Graphic Fonts Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-73018 Graphic Fonts Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-73017 Graphics Kernel Remote Code Execution Vulnerability Critical 7.5 No No RCE
CVE-2026-58599 HEVC Video Extensions Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-72981 IP Helper Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-72983 Internet Connection Sharing (ICS) Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-83711 ** Microsoft Azure Active Directory B2C Elevation of Privilege Vulnerability Critical 10 No No EoP
CVE-2026-62906 ** Microsoft Discovery Studio Information Disclosure Vulnerability Critical 7.4 No No Info
CVE-2026-65772 Microsoft Dynamics 365 On-Premises Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-62916 ** Microsoft Entra ID Elevation of Privilege Vulnerability Critical 9.1 No No EoP
CVE-2026-81948 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-81949 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-81950 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-81951 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-81953 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-81959 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-70178 ** Microsoft Fabric Elevation of Privilege Vulnerability Critical 8.5 No No EoP
CVE-2026-73010 Microsoft Failover Cluster Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-78444 Microsoft Failover Cluster Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-78439 Microsoft Office Graphics Component Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-78520 Microsoft Office Outlook Information Disclosure Vulnerability Critical 6.5 No No Info
CVE-2026-78509 Microsoft Office Outlook Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-78519 Microsoft Office Outlook Remote Code Execution Vulnerability Critical No No RCE
CVE-2026-78525 Microsoft Office Outlook Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69678 Microsoft Office PowerPoint Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69767 Microsoft Office PowerPoint Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69797 Microsoft Office PowerPoint Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69285 Microsoft Office Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69632 Microsoft Office Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-77898 Microsoft Office Remote Code Execution Vulnerability Critical 7.5 No No RCE
CVE-2026-78505 Microsoft Office Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-77504 Microsoft Office Word Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-65669 Microsoft SQL Server Elevation of Privilege Vulnerability Critical 9.6 No No EoP
CVE-2026-67378 Microsoft SQL Server Remote Code Execution Vulnerability Critical 8.5 No No RCE
CVE-2026-67631 Microsoft SQL Server Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-67636 Microsoft SQL Server Remote Code Execution Vulnerability Critical 8.5 No No RCE
CVE-2026-67643 Microsoft SQL Server Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-70351 Microsoft WebP Image Extension Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69601 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-78510 Microsoft Word Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-81952 Microsoft Word Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-65818 ** Power Automate Elevation of Privilege Vulnerability Critical 8.5 No No EoP
CVE-2026-69649 Raw Image Extension Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-66302 Skype for Business Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-69854 Spring Cloud Azure Elevation of Privilege Vulnerability Critical 9 No No EoP
CVE-2026-81355 Virtual Hard Disk (VHD) Miniport Driver Remote Code Execution Vulnerability Critical 7.5 No No RCE
CVE-2026-81352 Web Media Extensions Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69874 Windows ALPC Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-72958 Windows Credential Guard Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-69845 Windows DHCP Server Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-72979 Windows DHCP Server Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-72987 Windows DNS Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-69730 Windows DNS Server Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-69813 Windows DNS Server Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-69827 Windows DNS Server Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-69858 Windows DNS Server Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-77505 Windows DNS Server Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-72954 Windows Deployment Services Remote Code Execution Vulnerability Critical 7.5 No No RCE
CVE-2026-72957 Windows Deployment Services Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-77493 Windows Graphics Component Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-81955 Windows Graphics Component Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69769 Windows HTTP Print Provider Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-69710 Windows Hello Elevation of Privilege Vulnerability Critical 7.5 No No EoP
CVE-2026-69725 Windows Hello Elevation of Privilege Vulnerability Critical 7.8 No No EoP
CVE-2026-69740 Windows Hello Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-69784 Windows Hello Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-69799 Windows Hello Elevation of Privilege Vulnerability Critical 7.8 No No EoP
CVE-2026-69820 Windows Hello Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-69864 Windows Hello Elevation of Privilege Vulnerability Critical 7.8 No No EoP
CVE-2026-81354 Windows Hello Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-72980 Windows Hello Security Feature Bypass Vulnerability Critical 4.4 No No SFB
CVE-2026-72961 Windows Hyper-V Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-69603 Windows Hyper-V Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-80083 Windows Hyper-V Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69499 Windows Imaging Component Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69860 Windows Imaging Component Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-70296 Windows Imaging Component Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-73013 Windows Imaging Component Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-73023 Windows Imaging Component Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-77495 Windows Imaging Component Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69676 Windows Kerberos Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69712 Windows Key Distribution Center Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-70203 Windows Media Player Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-72960 Windows Media Player Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69579 Windows Message Queuing Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-72982 Windows Netlogon Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-70586 Windows Paint Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69530 Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-78449 Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-78450 Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-69518 Windows Remote Desktop Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69590 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-69852 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability Critical 7.5 No No RCE
CVE-2026-72950 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-72959 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-69501 Windows Secure Kernel Mode Elevation of Privilege Vulnerability Critical 7 No No EoP
CVE-2026-69846 Windows Secure Kernel Mode Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-69906 Windows Secure Kernel Mode Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-83939 Windows Secure Kernel Mode Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-73009 Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-69595 Windows Services for NFS ONCRPC XDR Driver Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-70585 Windows Services for NFS ONCRPC XDR Driver Remote Code Execution Vulnerability Critical 7 No No RCE
CVE-2026-78445 Windows Services for NFS ONCRPC XDR Driver Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-69829 Windows Shell Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-72962 Windows USB Video Driver Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-69890 Windows Virtual Trusted Platform Module Elevation of Privilege Vulnerability Critical 7.5 No No EoP
CVE-2026-83498 Windows Virtualization-Based Security (VBS) Enclave Elevation of Privilege Vulnerability Critical 7.8 No No EoP
CVE-2026-83501 Windows Virtualization-Based Security (VBS) Information Disclosure Vulnerability Critical 5.5 No No Info
CVE-2026-69805 .NET Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-69806 .NET Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-58649 .NET Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69439 .NET and Visual Studio Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-69522 .NET and Visual Studio Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-71328 .NET and Visual Studio Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-57099 ASP.NET Core Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69304 ASP.NET Core Denial of Service Vulnerability Important 5.9 No No DoS
CVE-2026-62810 Active Directory Certificate Services (AD CS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69821 Active Directory Certificate Services (AD CS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69395 Active Directory Certificate Services (AD CS) Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69624 Active Directory Certificate Services (AD CS) Tampering Vulnerability Important 6.5 No No Tampering
CVE-2026-69359 Active Directory Domain Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72978 Active Directory Federation Services (AD FS) Denial of Service Vulnerability Important 5.9 No No DoS
CVE-2026-69401 Audio Video Control Transport Protocol Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62895 Azure Arc SQL Server Extension Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-77909 Azure CycleCloud Information Disclosure Vulnerability Important 7.7 No No Info
CVE-2026-81349 Azure HDInsight Ambari Elevation of Privilege Vulnerability Important 7.2 No No EoP
CVE-2026-69329 BranchCache Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69516 Connected Devices Platform Service (Cdpsvc) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68824 Connected User Experiences and Telemetry Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68847 Connected User Experiences and Telemetry Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69470 Connected User Experiences and Telemetry Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69625 Connected User Experiences and Telemetry Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-73014 Data Sharing Service Client Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73016 DirectWrite Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-81380 GitHub Copilot and Visual Studio Code Information Disclosure Vulnerability Important 5.3 No No Info
CVE-2026-81381 GitHub Copilot and Visual Studio Code Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69576 Graphic Fonts Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-81353 HEIF Image Extensions Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-58600 HEVC Video Extensions Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69731 HID Class Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68895 Internet Storage Name Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69275 Kernel Streaming WOW Thunk Service Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69900 Kernel Streaming WOW Thunk Service Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68850 Microsoft Account Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68852 Microsoft Account Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-84003 Microsoft Authentication Library (MSAL) for Node.js Spoofing Vulnerability Important 7.4 No No Spoofing
CVE-2026-80097 Microsoft Authenticator Elevation of Privilege Vulnerability Important 8.6 No No EoP
CVE-2026-83948 Microsoft Azure CLI Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-69299 Microsoft COM for Windows Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69294 Microsoft COM for Windows Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69491 Microsoft DirectMusic Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-77908 Microsoft Dynamics 365 On-Premises Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-81387 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81390 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81391 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81392 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81393 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81394 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81395 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81399 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81400 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81401 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81958 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-81386 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81388 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81389 Microsoft Excel Remote Code Execution Vulnerability Important 7 No No RCE
CVE-2026-81396 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81397 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81398 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81947 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81954 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81956 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81957 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-81960 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-69378 Microsoft Exchange Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69380 Microsoft Exchange Server Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-69641 Microsoft Exchange Server Elevation of Privilege Vulnerability Important 9.1 No No EoP
CVE-2026-69382 Microsoft Exchange Server Information Disclosure Vulnerability Important 5.9 No No Info
CVE-2026-55007 Microsoft Exchange Server Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69355 Microsoft Exchange Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69356 Microsoft Exchange Server Spoofing Vulnerability Important 9.3 No No Spoofing
CVE-2026-69361 Microsoft Exchange Server Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-69375 Microsoft Exchange Server Tampering Vulnerability Important 6.5 No No Tampering
CVE-2026-69467 Microsoft Graphics Component Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83990 Microsoft Graphics Component Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-84000 Microsoft Graphics Component Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-69605 Microsoft Install Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69325 Microsoft JScript Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69438 Microsoft JScript Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69277 Microsoft Local Security Authority (LSA) Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69365 Microsoft Local Security Authority (LSA) Server Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69594 Microsoft Local Security Authority (LSA) Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69477 Microsoft Office Access Remote Code Execution Vulnerability Important 7.3 No No RCE
CVE-2026-69529 Microsoft Office Access Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69614 Microsoft Office Access Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69778 Microsoft Office Access Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-72974 Microsoft Office Excel Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-78515 Microsoft Office Excel Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-85875 Microsoft Office Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-78518 Microsoft Office Excel Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69626 Microsoft Office Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69739 Microsoft Office Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80076 Microsoft Office Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80078 Microsoft Office Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80082 Microsoft Office Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80087 Microsoft Office Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80089 Microsoft Office Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80091 Microsoft Office Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80073 Microsoft Office Outlook Information Disclosure Vulnerability Important No No Info
CVE-2026-80084 Microsoft Office Outlook Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69629 Microsoft Office Outlook Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-72938 Microsoft Office PowerPoint Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-72956 Microsoft Office PowerPoint Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-72975 Microsoft Office PowerPoint Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-72977 Microsoft Office PowerPoint Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-78513 Microsoft Office PowerPoint Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-80086 Microsoft Office PowerPoint Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80081 Microsoft Office PowerPoint Remote Code Execution Vulnerability Important No No RCE
CVE-2026-69742 Microsoft Office Publisher Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-81385 Microsoft Office Publisher Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69442 Microsoft Office Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78524 Microsoft Office Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69464 Microsoft Office SharePoint Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-69716 Microsoft Office SharePoint Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-69409 Microsoft Office SharePoint Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69636 Microsoft Office SharePoint Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69683 Microsoft Office SharePoint Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69904 Microsoft Office SharePoint Information Disclosure Vulnerability Important 3.5 No No Info
CVE-2026-69268 Microsoft Office SharePoint Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69273 Microsoft Office SharePoint Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69282 Microsoft Office SharePoint Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69465 Microsoft Office SharePoint Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69724 Microsoft Office SharePoint Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69804 Microsoft Office SharePoint Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69402 Microsoft Office SharePoint Spoofing Vulnerability Important 7.3 No No Spoofing
CVE-2026-69417 Microsoft Office SharePoint Spoofing Vulnerability Important 7.3 No No Spoofing
CVE-2026-69615 Microsoft Office SharePoint Spoofing Vulnerability Important 3.5 No No Spoofing
CVE-2026-69690 Microsoft Office SharePoint Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-64918 Microsoft Office Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-68843 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69719 Microsoft Office Word Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69734 Microsoft Office Word Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-72976 Microsoft Office Word Information Disclosure Vulnerability Important 5 No No Info
CVE-2026-77911 Microsoft Office Word Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-78502 Microsoft Office Word Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-78503 Microsoft Office Word Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-78506 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-78522 Microsoft Office Word Information Disclosure Vulnerability Important No No Info
CVE-2026-80079 Microsoft Office Word Information Disclosure Vulnerability Important No No Info
CVE-2026-80088 Microsoft Office Word Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-80090 Microsoft Office Word Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-83949 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-83951 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69360 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69556 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69671 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69686 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69722 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69759 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69764 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-72972 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-72973 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-77901 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78504 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78507 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78511 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78512 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78514 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78517 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78521 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78526 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-80080 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-80085 Microsoft Office Word Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69397 Microsoft OpenSSH for Windows Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-77897 Microsoft Power Automate Desktop Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62801 Microsoft PowerShell Security Feature Bypass Vulnerability Important 6.5 No No SFB
CVE-2026-57098 Microsoft Remote Desktop App for Windows Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-67376 Microsoft SQL Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-67633 Microsoft SQL Server Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-67641 Microsoft SQL Server Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-66814 Microsoft SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-66818 Microsoft SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-66819 Microsoft SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-67368 Microsoft SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-67370 Microsoft SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-67381 Microsoft SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-67369 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67383 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67386 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67389 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67390 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67393 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67624 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67629 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67630 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67645 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-67648 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-68776 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-68777 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-68778 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-68779 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-68780 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-68781 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-68784 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69562 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-73029 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-77488 Microsoft SQL Server Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-47297 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-67373 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-67379 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.5 No No RCE
CVE-2026-67380 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-67384 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-67385 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-67388 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-67638 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-67639 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-67642 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-68775 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-68785 Microsoft SQL Server Remote Code Execution Vulnerability Important 4.9 No No RCE
CVE-2026-68786 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-68787 Microsoft SQL Server Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-77481 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-77482 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-77484 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-77486 Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-66816 Microsoft SQL Server Security Feature Bypass Vulnerability Important 6.5 No No SFB
CVE-2026-68885 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68888 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68889 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-68890 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68892 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68897 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69269 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69271 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69272 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69313 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69336 Microsoft Standard XPS Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-68881 Microsoft Standard XPS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68891 Microsoft Standard XPS Information Disclosure Vulnerability Important 4.7 No No Info
CVE-2026-69308 Microsoft Standard XPS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69345 Microsoft Standard XPS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69367 Microsoft Standard XPS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69376 Microsoft Standard XPS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69824 Microsoft Standard XPS Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-72946 Microsoft Storage Port Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65812 Microsoft Teams for Android Information Disclosure Vulnerability Important 6.8 No No Info
CVE-2026-69559 Microsoft Teams for Android Information Disclosure Vulnerability Important 5.8 No No Info
CVE-2026-56198 Microsoft Trace Data Helper Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69276 Microsoft UxTheme Library (uxtheme.dll) Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69420 Microsoft VOLSNAP.SYS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69427 Microsoft VOLSNAP.SYS Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-72933 Microsoft WDAC OLE DB provider for SQL Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-62706 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-62744 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69386 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69408 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69511 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69586 Microsoft Windows PDF Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-78451 Microsoft Windows SCSI Class System File Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-78452 Microsoft Windows SCSI Class System File Information Disclosure Vulnerability Important 4.6 No No Info
CVE-2026-78453 Microsoft Windows SCSI Class System File Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-68896 Microsoft Windows Search Component Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69305 Microsoft Windows Search Component Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69322 Microsoft Windows Search Component Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69585 Microsoft Windows Search Component Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69600 Microsoft Windows Search Component Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69608 Microsoft Windows Search Component Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69911 Microsoft Windows Search Component Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69507 Microsoft Windows Search Component Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-70145 Microsoft Windows Search Component Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69453 Microsoft Windows Search Component Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-69554 Microsoft Windows Search Component Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-69444 Microsoft Windows Speech Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69456 Microsoft Windows Speech Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69531 Microsoft Windows Speech Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-62804 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-69807 PowerShell Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69303 Push Message Routing Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69819 RPC Runtime Library Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-68828 Remote Desktop Client Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69358 Remote Desktop Client Remote Code Execution Vulnerability Important 7.1 No No RCE
CVE-2026-69485 Remote Desktop Client Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-78463 Remote Desktop Client Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-80074 Remote Desktop Client Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-80077 Remote Desktop Client Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-83998 Remote Desktop Client Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69292 Remote Desktop Gateway Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69338 Remote Desktop Gateway Service Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-68893 Remote Desktop Licensing Service Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69514 Remote Desktop Services Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69525 Remote Desktop Services Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69536 Remote Desktop Services Remote Code Execution Vulnerability Important 7.1 No No RCE
CVE-2026-69539 Remote Desktop Services Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69599 Remote Desktop Services Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69509 Role: Windows Fax Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69621 Role: Windows Fax Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-72944 Role: Windows Fax Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-66820 SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-73028 SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-77480 SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-77483 SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-77485 SQL Server Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-77487 SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-78456 SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-66304 Skype for Business Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-66306 Skype for Business Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-63523 Skype for Business Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-66305 Skype for Business Spoofing Vulnerability Important 7.1 No No Spoofing
CVE-2026-69642 Skype for Business Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-69646 Skype for Business Spoofing Vulnerability Important 8.3 No No Spoofing
CVE-2026-66303 Skype for Business and Lync Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-66307 Skype for Business and Lync Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-66308 Skype for Business and Lync Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-69568 Storage Spaces Controller Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69431 Telnet Client Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69384 Virtual Hard Disk (VHD) Miniport Driver Denial of Service Vulnerability Important 7.1 No No DoS
CVE-2026-69541 Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability Important 7.8 No No EoP
CVE-2026-69549 Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability Important 7 No No EoP
CVE-2026-69611 Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability Important 7 No No EoP
CVE-2026-69681 Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability Important 8 No No EoP
CVE-2026-70574 Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability Important 7.8 No No EoP
CVE-2026-81383 Visual Studio Code Information Disclosure Vulnerability Important 7.4 No No Info
CVE-2026-70334 Visual Studio Code Security Feature Bypass Vulnerability Important 7.8 No No SFB
CVE-2026-78461 Visual Studio Code Security Feature Bypass Vulnerability Important 7.4 No No SFB
CVE-2026-78462 Visual Studio Code Security Feature Bypass Vulnerability Important 8.8 No No SFB
CVE-2026-81356 Visual Studio Code Security Feature Bypass Vulnerability Important 8.2 No No SFB
CVE-2026-81357 Visual Studio Code Security Feature Bypass Vulnerability Important 8.2 No No SFB
CVE-2026-81376 Visual Studio Code Security Feature Bypass Vulnerability Important 9.6 No No SFB
CVE-2026-81378 Visual Studio Code Security Feature Bypass Vulnerability Important 8.2 No No SFB
CVE-2026-81379 Visual Studio Code Security Feature Bypass Vulnerability Important 8.2 No No SFB
CVE-2026-81377 Visual Studio Code Tampering Vulnerability Important 6.5 No No Tampering
CVE-2026-77906 Visual Studio Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-77907 Visual Studio Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69407 Volume Manager Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69418 Volume Manager Driver Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69432 Volume Manager Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72985 Volume Shadow Copy Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-69609 Win32k Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69808 Win32k Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69832 Win32k Information Disclosure Vulnerability Important 5.6 No No Info
CVE-2026-69853 Win32k Information Disclosure Vulnerability Important 4.7 No No Info
CVE-2026-70290 Win32k Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70565 Windows AF_UNIX Socket Provider Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69834 Windows ALPC Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69654 Windows Accounts Control Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69816 Windows Accounts Control Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62762 Windows Active Directory Domain Services Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-69809 Windows Active Directory Domain Services Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-62813 Windows Active Directory Domain Services Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69524 Windows Active Directory Domain Services Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69546 Windows Active Directory Domain Services Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-50349 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-70342 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-69311 Windows Audio Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69394 Windows Audio Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69447 Windows Audio Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69540 Windows Audio Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69604 Windows Audio Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69692 Windows Audio Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69801 Windows Audio Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70562 Windows Audio Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-73005 Windows Authentication Methods Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-73004 Windows Autopilot Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-68825 Windows Bind Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69293 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69298 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69323 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69352 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69476 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69489 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69580 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69583 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69589 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69593 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69727 Windows Biometric Service Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69738 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69773 Windows Biometric Service Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69787 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69826 Windows Biometric Service Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-70572 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70573 Windows Biometric Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-70581 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72941 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72988 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72990 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72991 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72992 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72993 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72994 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72995 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72996 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72997 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73000 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73001 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73002 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73007 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73011 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73015 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73020 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73021 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73026 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-77489 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-78447 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-78448 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83954 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83955 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83967 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83968 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83969 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83970 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83971 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83972 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83973 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83974 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83975 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83976 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83977 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83978 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83979 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83980 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83981 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83982 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83983 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83985 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83986 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83987 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83988 Windows Biometric Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-73008 Windows Biometric Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69458 Windows BitLocker Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69449 Windows BitLocker Remote Code Execution Vulnerability Important 6.7 No No RCE
CVE-2026-69817 Windows Bluetooth Port Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68849 Windows Bluetooth Port Driver Information Disclosure Vulnerability Important 4.7 No No Info
CVE-2026-69388 Windows Bluetooth Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69398 Windows Bluetooth Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69448 Windows Bluetooth Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69889 Windows Bluetooth Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-77892 Windows Boot Manager Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-69735 Windows Broadcast DVR User Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69391 Windows Broker Infrastructure Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69283 Windows CD-ROM Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69561 Windows CD-ROM Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-78454 Windows CD-ROM Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-78508 Windows CD-ROM Driver Information Disclosure Vulnerability Important 4.6 No No Info
CVE-2026-69542 Windows Camera Frame Server Monitor Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69279 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-80093 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-83991 Windows Cloud Files Mini Filter Driver Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-69445 Windows Compressed Folder Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70019 Windows Compressed Folder Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69496 Windows Compressed Folder Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69267 Windows Connected User Experiences and Telemetry Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69771 Windows Container Manager Service Security Feature Bypass Vulnerability Important 4.7 No No SFB
CVE-2026-70583 Windows Core Messaging Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70584 Windows Core Messaging Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70578 Windows Credential Guard Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69790 Windows Credential Providers Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69814 Windows Credential Providers Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69729 Windows Credential Providers Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69284 Windows DCOM Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69781 Windows DHCP Client Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-69777 Windows DHCP Client Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69342 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69405 Windows DHCP Server Denial of Service Vulnerability Important 5.7 No No DoS
CVE-2026-69416 Windows DHCP Server Denial of Service Vulnerability Important 5.7 No No DoS
CVE-2026-69497 Windows DHCP Server Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-69637 Windows DHCP Server Denial of Service Vulnerability Important 5.7 No No DoS
CVE-2026-69679 Windows DHCP Server Denial of Service Vulnerability Important 5.7 No No DoS
CVE-2026-70065 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77494 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77498 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77499 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77501 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77502 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77886 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77888 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77889 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77890 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77893 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-77895 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69415 Windows DHCP Server Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-69297 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69803 Windows DHCP Server Information Disclosure Vulnerability Important 5.9 No No Info
CVE-2026-69929 Windows DHCP Server Information Disclosure Vulnerability Important 5.9 No No Info
CVE-2026-69930 Windows DHCP Server Information Disclosure Vulnerability Important 5.9 No No Info
CVE-2026-70124 Windows DHCP Server Information Disclosure Vulnerability Important 5.9 No No Info
CVE-2026-69266 Windows DHCP Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69412 Windows DHCP Server Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-69510 Windows DHCP Server Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69547 Windows DHCP Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69620 Windows DHCP Server Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69847 Windows DHCP Server Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-69876 Windows DHCP Server Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-69878 Windows DHCP Server Remote Code Execution Vulnerability Important 6.4 No No RCE
CVE-2026-77887 Windows DHCP Server Remote Code Execution Vulnerability Important 6.4 No No RCE
CVE-2026-77891 Windows DHCP Server Remote Code Execution Vulnerability Important 6.4 No No RCE
CVE-2026-69631 Windows DNS Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-70091 Windows DNS Denial of Service Vulnerability Important 5.9 No No DoS
CVE-2026-69310 Windows DNS Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-72948 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-69369 Windows DNS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69672 Windows DNS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-78523 Windows DNS Server Denial of Service Vulnerability Important 5.9 No No DoS
CVE-2026-69551 Windows DNS Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69782 Windows DNS Server Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69989 Windows DNS Server Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-72928 Windows DNS Server Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69680 Windows DNS Spoofing Vulnerability Important 8.1 No No Spoofing
CVE-2026-69775 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-70568 Windows Defender Firewall Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68831 Windows Defender Firewall Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69607 Windows Deployment Services Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-72943 Windows Deployment Services Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69314 Windows Device Association Broker Service Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69693 Windows Device Association Broker Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69296 Windows Device Association Service Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69478 Windows Device Association Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69488 Windows Device Association Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69574 Windows Device Association Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69581 Windows Device Association Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69711 Windows Device Association Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69714 Windows Device Association Service Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69791 Windows Device Association Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69866 Windows Device Association Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-77500 Windows Device Association Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83940 Windows Device Association Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69443 Windows Device Health Attestation (DHA) Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-69472 Windows Devices Human Interface Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69715 Windows Direct Show Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-70567 Windows Display Enhancement Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-78446 Windows Distributed File System (DFS) Denial of Service Vulnerability Important 5.3 No No DoS
CVE-2026-69424 Windows Distributed File System (DFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69430 Windows Embedded Mode Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69688 Windows Encrypting File System (EFS) Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69841 Windows Encrypting File System (EFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69794 Windows Encrypting File System (EFS) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69481 Windows Enterprise App Management Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69907 Windows Enterprise App Management Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68894 Windows Error Reporting Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69362 Windows Error Reporting Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69433 Windows Error Reporting Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69436 Windows Error Reporting Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69450 Windows Error Reporting Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69462 Windows Error Reporting Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69513 Windows Error Reporting Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69612 Windows Error Reporting Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69896 Windows Error Reporting Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-83996 Windows Error Reporting Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-69684 Windows Error Reporting Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69482 Windows Error Reporting Tampering Vulnerability Important 7.1 No No Tampering
CVE-2026-69493 Windows Event Logging Service Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69494 Windows Event Logging Service Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69495 Windows Event Logging Service Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-71338 Windows Failover Cluster Elevation of Privilege Vulnerability Important 6.4 No No EoP
CVE-2026-72989 Windows Failover Cluster Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-68878 Windows Fast FAT Driver Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69347 Windows Fast FAT Driver Remote Code Execution Vulnerability Important 7.4 No No RCE
CVE-2026-68837 Windows File History Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-71340 Windows File History Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-72947 Windows File History Service Elevation of Privilege Vulnerability Important 6.4 No No EoP
CVE-2026-77491 Windows GDI Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68827 Windows GDI+ Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69288 Windows GDI+ Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69717 Windows Group Policy Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69623 Windows HTTP Print Provider Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-69597 Windows HTTP.sys Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69682 Windows Host Guardian Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69553 Windows Hyper-V Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69910 Windows Hyper-V Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69694 Windows IP Address Management (IPAM) Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69341 Windows Image Acquisition Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69500 Windows Image Acquisition Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69613 Windows Image Acquisition Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69483 Windows Image Acquisition Information Disclosure Vulnerability Important 4.7 No No Info
CVE-2026-69318 Windows Imaging Component Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-83992 Windows Imaging Component Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-62694 Windows Installer Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69441 Windows Installer Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-71339 Windows Installer Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-72929 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-77894 Windows Installer Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-72926 Windows Internet Connection Sharing (ICS) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-72964 Windows Internet Connection Sharing (ICS) Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-69587 Windows Internet Key Exchange (IKE) Extension Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69881 Windows Internet Key Exchange (IKE) Extension Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69429 Windows Internet Key Exchange (IKE) Protocol Extensions Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69744 Windows Kerberos Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69760 Windows Kerberos Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69685 Windows Kerberos Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69822 Windows Kerberos Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68846 Windows Kernel Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-68884 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69366 Windows Kernel Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69466 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69473 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69578 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-83942 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-85360 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69406 Windows Kernel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69723 Windows Kernel Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-69669 Windows Kernel Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69421 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-84001 Windows Key Distribution Center Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69428 Windows LDAP - Lightweight Directory Access Protocol Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69281 Windows License Manager Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69315 Windows License Manager Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69732 Windows Link Layer Topology Discovery Protocol Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69440 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 7 No No EoP
CVE-2026-69508 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 7.8 No No EoP
CVE-2026-69720 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 7.8 No No EoP
CVE-2026-78464 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 7 No No EoP
CVE-2026-68842 Windows MIDI Service Module Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69339 Windows MIDI Service Module Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69451 Windows Management Instrumentation Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-70582 Windows Management Instrumentation Elevation of Privilege Vulnerability Important 6.4 No No EoP
CVE-2026-77905 Windows Management Instrumentation Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69349 Windows Management Instrumentation Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-73012 Windows Management Services Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-69891 Windows Media Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69645 Windows Message Queuing Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68887 Windows Message Queuing Queue Manager Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-72932 Windows Message Queuing Queue Manager Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-83997 Windows Message Queuing Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-70579 Windows Mobile Broadband Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-69377 Windows Modern Device Management (MDM) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69460 Windows Modern Device Management (MDM) Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-70577 Windows Modern Device Management (MDM) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-73003 Windows Modern Device Management (MDM) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-73022 Windows Modern Device Management (MDM) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69674 Windows Modern Device Management (MDM) Security Feature Bypass Vulnerability Important 5.5 No No SFB
CVE-2026-72963 Windows Modern Execution Server Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69357 Windows NDIS Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69396 Windows NDIS Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-71334 Windows NFS Portmapper Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68832 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68834 Windows NTFS Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-68838 Windows NTFS Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-68841 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69265 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69312 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69332 Windows NTFS Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69340 Windows NTFS Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69379 Windows NTFS Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69505 Windows NTFS Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69532 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69567 Windows NTFS Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69875 Windows NTFS Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-72935 Windows NTFS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-77503 Windows NTFS Elevation of Privilege Vulnerability Important 8.4 No No EoP
CVE-2026-83995 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68851 Windows NTFS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69504 Windows NTFS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69591 Windows NTFS Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-68833 Windows NTFS Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-68875 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-69461 Windows NTFS Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69463 Windows NTFS Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69479 Windows NTFS Remote Code Execution Vulnerability Important 8.4 No No RCE
CVE-2026-69566 Windows NTFS Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-69638 Windows NTFS Remote Code Execution Vulnerability Important 8.4 No No RCE
CVE-2026-69709 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-71329 Windows NTFS Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-69425 Windows NTFS Tampering Vulnerability Important 4.7 No No Tampering
CVE-2026-62759 Windows Netlogon Spoofing Vulnerability Important 7.5 No No Spoofing
CVE-2026-72967 Windows Network Connection Broker Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68886 Windows Network Connection Broker Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69372 Windows Network File System Denial of Service Vulnerability Important 5.7 No No DoS
CVE-2026-69772 Windows Network File System Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69648 Windows Notification Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-78441 Windows OLE DB Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-78442 Windows OLE DB Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69564 Windows Online Certificate Status Protocol (OCSP) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69350 Windows Overlay Filter Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-69368 Windows Overlay Filter Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69371 Windows Overlay Filter Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69373 Windows Overlay Filter Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-69316 Windows Overlay Filter Information Disclosure Vulnerability Important 4.7 No No Info
CVE-2026-69343 Windows Overlay Filter Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69474 Windows Overlay Filter Information Disclosure Vulnerability Important 4.8 No No Info
CVE-2026-69480 Windows Partition Management Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69492 Windows Partition Management Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-71341 Windows Partition Management Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69324 Windows Performance Monitor Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69459 Windows Power Dependency Coordinator Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69321 Windows Power Dependency Coordinator Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-69569 Windows Print Spooler Components Denial of Service Vulnerability Important 5.7 No No DoS
CVE-2026-68835 Windows Print Spooler Components Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-68848 Windows Print Spooler Components Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69309 Windows Print Spooler Components Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69346 Windows Print Spooler Components Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69364 Windows Print Spooler Components Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69838 Windows Print Spooler Components Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69921 Windows Print Spooler Components Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70564 Windows Print Spooler Components Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69344 Windows Print Spooler Components Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69552 Windows Print Spooler Components Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-85877 Windows Print Spooler Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69602 Windows PrintWorkflowUserSvc Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-68845 Windows Program Compatibility Assistant Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68876 Windows Program Compatibility Assistant Service Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69534 Windows Program Compatibility Assistant Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69563 Windows Program Compatibility Assistant Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68873 Windows Program Compatibility Assistant Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68874 Windows Program Compatibility Assistant Service Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-62697 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69280 Windows Push Notifications Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69300 Windows Push Notifications Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69548 Windows RNDIS Information Disclosure Vulnerability Important 4.6 No No Info
CVE-2026-69768 Windows RNDIS Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69337 Windows Registry Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69331 Windows Remote Access Connection Manager Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69455 Windows Remote Access Connection Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-71333 Windows Remote Access Connection Manager Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-71342 Windows Remote Access Connection Manager Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-71343 Windows Remote Access Connection Manager Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-71352 Windows Remote Access Connection Manager Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-72966 Windows Remote Access Connection Manager Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-77896 Windows Remote Desktop Client Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-69317 Windows Remote Desktop Client Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-69627 Windows Remote Desktop Licensing Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70587 Windows Remote Desktop Protocol Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-69287 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69475 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-80096 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-69616 Windows Remote Desktop Services Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-83999 Windows Resilient File System (ReFS) Deduplication Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69617 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-83952 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-72939 Windows Routing and Remote Access Service (RRAS) Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-71351 Windows Routing and Remote Access Service (RRAS) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-71353 Windows Routing and Remote Access Service (RRAS) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-70570 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-69544 Windows SMB Client Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69572 Windows SMB Client Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-69618 Windows SMB Client Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-72936 Windows SMB Client Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69374 Windows SMB Server Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-69403 Windows SMB Server Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-72949 Windows SMB Server Network Transport Driver (srvnet.sys) Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-70575 Windows Schannel Denial of Service Vulnerability Important 5.3 No No DoS
CVE-2026-72940 Windows Schannel Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69713 Windows Secure Boot Security Feature Bypass Vulnerability Important 4.4 No No SFB
CVE-2026-72931 Windows Secure Socket Tunneling Protocol (SSTP) Denial of Service Vulnerability Important 4.7 No No DoS
CVE-2026-71332 Windows Secure Socket Tunneling Protocol (SSTP) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-72930 Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability Important 7 No No RCE
CVE-2026-77899 Windows Security Center Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-78457 Windows Security Health Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-56177 Windows Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-83989 Windows Services for NFS ONCRPC XDR Driver Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-73024 Windows Services for NFS ONCRPC XDR Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-71330 Windows Services for NFS ONCRPC XDR Driver Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-69289 Windows Setup Files Cleanup Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69383 Windows Shell Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69392 Windows Shell Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69528 Windows Shell Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69606 Windows Shell Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-70563 Windows Shell Spoofing Vulnerability Important 8.1 No No Spoofing
CVE-2026-69785 Windows Smart Card Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69512 Windows Spaceport.sys Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69535 Windows Spaceport.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69643 Windows Spaceport.sys Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69691 Windows Spaceport.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70569 Windows Spaceport.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69390 Windows Spaceport.sys Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69393 Windows Spaceport.sys Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-69741 Windows Spaceport.sys Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69770 Windows Spaceport.sys Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69895 Windows Spaceport.sys Information Disclosure Vulnerability Important 4.7 No No Info
CVE-2026-72942 Windows Spaceport.sys Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-69538 Windows Spaceport.sys Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-71345 Windows Spaceport.sys Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-71348 Windows Spaceport.sys Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-71349 Windows Spaceport.sys Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-71350 Windows Spaceport.sys Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-72952 Windows Spaceport.sys Remote Code Execution Vulnerability Important 7 No No RCE
CVE-2026-69328 Windows Storage Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-78516 Windows Storage Information Disclosure Vulnerability Important 4.3 No No Info
CVE-2026-69389 Windows Storage Management Provider Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-71337 Windows Storage Management Provider Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69381 Windows Storage Port Driver Information Disclosure Vulnerability Important 4.6 No No Info
CVE-2026-72937 Windows Storage Port Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-77492 Windows Storage Port Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69290 Windows Storage Spaces Controller Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69575 Windows Storage Spaces Controller Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68844 Windows Storage Spaces Controller Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68877 Windows Storage Spaces Controller Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-69588 Windows TCP/IP Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-69385 Windows TCP/IP Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69404 Windows TCP/IP Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69757 Windows TCP/IP Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69761 Windows TCP/IP Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69793 Windows TCP/IP Security Feature Bypass Vulnerability Important 7.5 No No SFB
CVE-2026-72945 Windows Task Scheduler Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69353 Windows Text Shaping Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69786 Windows Text Shaping Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-69434 Windows URL Moniker Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-73019 Windows URL Moniker Security Feature Bypass Vulnerability Important 4.3 No No SFB
CVE-2026-69286 Windows USB Audio Class Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69270 Windows USB Audio Class driver (usbaudio.sys) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69307 Windows USB Audio Class driver (usbaudio.sys) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69413 Windows USB Audio Class driver (usbaudio.sys) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69469 Windows USB Audio Class driver (usbaudio.sys) Elevation of Privilege Vulnerability Important 6.6 No No EoP
CVE-2026-69571 Windows USB Audio Class driver (usbaudio.sys) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69687 Windows USB Audio Class driver (usbaudio.sys) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69707 Windows USB Audio Class driver (usbaudio.sys) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69859 Windows USB Audio Class driver (usbaudio.sys) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68840 Windows USB Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69295 Windows USB Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69503 Windows USB Driver Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-72953 Windows USB Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69457 Windows USB Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-72999 Windows USB Hub Driver Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-69490 Windows USB Mass Storage Class Driver Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-69527 Windows USB Mass Storage Class Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68839 Windows USB Mass Storage Class Driver Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-69319 Windows USB Video Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69422 Windows USB Video Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69423 Windows USB Video Driver Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69584 Windows USB Video Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69573 Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69592 Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69758 Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68830 Windows Universal Plug and Play (UPnP) Device Host Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69351 Windows Universal Plug and Play (UPnP) Device Host Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-56172 Windows VHD miniport driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69426 Windows VOLSNAP.SYS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-69468 Windows Volume Manager Extension Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69582 Windows Volume Manager Extension Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-77904 Windows Volume Manager Extension Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69291 Windows Volume Manager Extension Driver Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69334 Windows Volume Manager Extension Driver Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69708 Windows Web Platform Storage Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-72965 Windows WebClient Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69792 Windows Win32K Security Feature Bypass Vulnerability Important 4.7 No No SFB
CVE-2026-68880 Windows Win32k Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69274 Windows Win32k Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69301 Windows Win32k Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69333 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69335 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69348 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69410 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69498 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69610 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69630 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69652 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69689 Windows Win32k Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69706 Windows Win32k Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-69762 Windows Win32k Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-69779 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69818 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69844 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70283 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-70289 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69517 Windows Wireless Networking Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-69862 Windows Wireless Wide Area Network Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-69560 Windows Work Folder Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-71336 Windows Work Folder Service Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-80075 Windows Work Folders Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-69619 Windows exFAT File System Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-68898 Windows iSCSI Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-69598 Windows iSCSI Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69628 Windows iSCSI Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-73025 Windows iSCSI Security Feature Bypass Vulnerability Important 9.8 No No SFB
CVE-2026-69839 Windows iSCSI Target Service Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-72927 Winsock Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-58611 Xbox Gaming Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-78455 Xbox Information Disclosure Vulnerability Important 4.3 No No Info
CVE-2026-84353 * Chromium: CVE-2026-84353 Use after free in Shared Tab Groups Critical N/A No No RCE
CVE-2026-84324 * Chromium: CVE-2026-84324 Use after free in Proxy High N/A No No RCE
CVE-2026-84325 * Chromium: CVE-2026-84325 Improper input validation in DataTransfer High N/A No No RCE
CVE-2026-84326 * Chromium: CVE-2026-84326 Uninitialized resource in V8 High N/A No No RCE
CVE-2026-84359 * Chromium: CVE-2026-84359 Information leak in Skia High N/A No No Info
CVE-2026-84357 * Chromium: CVE-2026-84357 Improper input validation in Omnibox High N/A No No RCE
CVE-2026-84349 * Chromium: CVE-2026-84349 Use after free in Browser High N/A No No RCE
CVE-2026-84351 * Chromium: CVE-2026-84351 Buffer overflow in GPU High N/A No No RCE
CVE-2026-84354 * Chromium: CVE-2026-84354 Incorrect authorization in FileSystem High N/A No No RCE
CVE-2026-84323 * Chromium: CVE-2026-84323 Missing authorization in FileSystem Medium N/A No No RCE
CVE-2026-84328 * Chromium: CVE-2026-84328 Missing authorization in FileSystem Medium N/A No No RCE
CVE-2026-84332 * Chromium: CVE-2026-84332 Incorrect authorization in SiteSettings Medium N/A No No RCE
CVE-2026-84334 * Chromium: CVE-2026-84334 Incorrect authorization in Chromoting Medium N/A No No EoP
CVE-2026-84335 * Chromium: CVE-2026-84335 Incorrect authorization in TabStrip Medium N/A No No EoP
CVE-2026-84347 * Chromium: CVE-2026-84347 Use after free in WebRTC Medium N/A No No RCE
CVE-2026-84348 * Chromium: CVE-2026-84348 Information leak in MediaCapture Medium N/A No No Info
CVE-2026-84355 * Chromium: CVE-2026-84355 Incorrect authorization in Navigation Medium N/A No No EoP
CVE-2026-84358 * Chromium: CVE-2026-84358 Improper privilege management in Downloads Medium N/A No No EoP
CVE-2026-84327 * Chromium: CVE-2026-84327 Incorrect authorization in Autofill Low N/A No No Spoofing
CVE-2026-84329 * Chromium: CVE-2026-84329 Confused deputy in CredentialProvider Low N/A No No EoP
CVE-2026-84331 * Chromium: CVE-2026-84331 Incorrect authorization in Actor Low N/A No No SFB
CVE-2026-84350 * Chromium: CVE-2026-84350 Use after free in TabStrip Low N/A No No RCE
CVE-2026-84356 * Chromium: CVE-2026-84356 UI misrepresentation in FullScreen Low N/A No No Spoofing

* Indicates this CVE had been released by a third party and is now being included in Microsoft releases.

** Indicates this CVEs has already been resolved by Microsoft, and no further action is needed by the end user.

† Indicates further administrative actions are required to fully address the vulnerability.


As with last month, I’ll do my best to summarize everything else in this release but assume there are details I miss that are relevant to your environment.

There are roughly 90+ Critical rated bug remaining, and I’ll do my best to call out which ones you should care about. First, ignore those CVSS 10 bugs. They’ve already been patched by Microsoft, so there’s no action for you. But don’t ignore the EoP in Spring Cloud Azure. It’s a complex scenario, but Microsoft still lists it as exploitation more likely. There’s a plethora of server-side bugs rated at a CVSS of 9.8, including Skype for Business (remember that one?).

From here on out, I’ll try to break things down by component rather than severity rating or impact. It may make it easier. We’ll see. ¯\_(ツ)_/¯

Windows DHCP Server: Windows DHCP Server chimes in with 36 bugs: 12 RCE, 18 DoS, five info leaks, and one EoP. Nothing exploited or disclosed, but 22 of the 36 require no authentication. It's the third-largest single-component pile of the month, and it's all one story: someone pointed a (likely AI-assisted) fuzzer at DHCP packet parsing. In addition to the two wormable bugs already mentioned, there are three more that didn’t carry the exact wormable verbiage but look like close cousins: CVE-2026-69845 (9.8, heap overflow), CVE-2026-69266 (8.8, integer overflow), and CVE-2026-69620 (8.1, stack overflow). If you're being generous, that's five wormable-shaped bugs in DHCP Server alone. The remaining seven RCEs need an authorized attacker. CWE spread is pure memory corruption: heap, stack, UAF, integer overflow. There are 18 DoS bugs, and 13 are unauthenticated at a CVSS score of 7.5. Malformed packet in, service crash out. Individually boring, but collectively, an unauthenticated attacker on the network has 13 different ways to take out DHCP, and when DHCP dies, clients stop getting leases and the helpdesk phone starts ringing. Finally, there are a couple of oddballs here: CVE-2026-69297 is an info leak that could expose passwords stored in a recoverable format, which is a configuration-secrets problem rather than a memory bug. The lone EoP is missing authentication on a critical function.

Windows Biometric Service: 64 bugs here, and 63 of them look almost identical. It's one bug class, stamped 56 times. CWE-122 heap-based buffer overflow accounts for 56 of them, with 5 integer overflows, 2 use-after-frees, and a NULL dereference rounding out the memory-corruption set. There are two worth noting: CVE-2026-69727. It has an outlier exploit vector: it reads “elevate privileges over a network” rather than locally, which is not what you want to see in a biometric service. The other is CVE-2026-73008. The lone info disclosure and it's CWE-359: exposure of private personal information. A biometric service leaking PII with high confidentiality impact is a worse look than the score implies. It also makes it a natural companion to the Hello cleartext tampering bug.

Windows Hello: Nine bugs here, with eight being Critical EoPs that result in an attacker gaining Virtual Trust Level 1 privileges. Code execution across the VTL0-to-VTL1 boundary into the secure world where VBS keeps credentials and biometric templates. That's the same trust line as Key Guard, and it's why they're rated Critical despite local vectors.

Exchange Server: Only nine bugs here, but there are some whoppers. Three different bugs rate CVSS 9.1 or higher. CVE-2026-69380 is an interesting exploit. A low-privileged user with a mailbox abuses request/token validation to impersonate any user and take over every mailbox: read, send, download attachments. Post-phish, this turns one compromised account into the whole org's mail. An unauthenticated mail-processing RCE plus a mailbox-takeover EoP in the same release is a chainable pair on paper. Initial access and lateral movement in one Cumulative Update. The other unauthenticated bug to mention is CVE-2026-69356, an specially crafted calendar invite; victim clicks the Join link, and script runs in their context. XSS wearing a spoofing label. Neat.

Microsoft Office Components: There are 110 Office-family bugs this month (excluding SharePoint's 17): 64 RCE, 45 info disclosure, and 1 spoofing. Most are of the open-and-own variety, but a few stick out, namely a CVSS 98 bug in Outlook’s CVSS 9.8 duo. CVE-2026-78509 is a Critical RCE. It has a network vector, no user interaction per the metrics, and explicitly lists the Preview Pane as an attack vector. That's the worst combination Office offers: code execution from a message you merely preview. There are a few other Preview Pane bugs in Office and Word.

SharePoint Server: This month’s release includes 16 SharePoint bugs: six RCE, two EoP, four spoofing, and four info disclosure. All Important, none exploited or publicly disclosed, nothing rated above “Exploitation Less Likely”, but given SharePoint's recent history of “Less Likely” becoming “in the KEV catalog,” the RCE set deserves respect. The RCE bugs do all require authentication, but the level is pretty basic, although the bug classes (deserialization, SQLi, SSRF, XSS, auth bypass) read like a web-app pentest report rather than memory corruption. The EoPs continue the theme of web-app sins in a server product: CVE-2026-69716 is a SQL injection letting a low-privileged user run database commands with elevated privileges; CVE-2026-83950 is an SSRF-based EoP; 69464 is an unnecessary-privileges flaw at CVSS 8.8.

Microsoft SQL Server: As previously mentioned, there are over 62 SQL Server bugs in this release: 61 in SQL Server proper plus the Azure Arc SQL Server Extension. Here’s the breakdown: 23 RCE, 14 EoP, 21 info disclosure, three DoS, and one SFB. Five are Critical. The overwhelming pattern is authenticated memory corruption. 55 of 62 require an authorized attacker, and the CWE spread is dominated by heap overflows (15 of the RCEs are CWE-122 alone) and out-of-bounds reads (13 of the info leaks). The template is CVE-2026-67378’s: log in, submit a crafted query, corrupt memory, run code on the server. That's why the 8.8s here are less scary than they score; an attacker already needs database credentials, but it's also textbook post-compromise lateral movement.

Windows DNS Server: There are 18 bugs here: 10 RCE, three DoS, two EoP, two info leaks, and one spoofing. Overwhelmingly use-after-frees in the server’s record handling: another single-component sweep, but this one lands on domain controllers. We’ve already mentioned a couple of wormable bugs, but the remaining RCE are not far off, but require either beating a race condition or non-default components. Unlike the DHCP pile, this one carries one of only two “More Likely” unauthenticated 9.8. Patch your domain controllers, then patch them again just to be sure.

Windows NTFS: We have 30 bugs in this component: 16 EoP, 10 RCE, three info leaks, and one link-following oddball. All Important except the two 9.8 Critical RCEs. Like Biometric and DHCP, it's one bug class on repeat: 28 of 30 are memory-safety flaws (heap overflows lead at 12, then out-of-bounds reads). The headliner is CVE-2026-69463; simple heap-overflow RCE at 9.8, unauthenticated, network vector. The FAQ only offers the vague “in-network attacker calling arbitrary endpoints” phrasing, which likely means the remote path is something like SMB-reachable file operations rather than a raw packet, but a 9.8 in the file system driver everyone runs is still a top-tier patch either way. CVE-2026-69461 (8.8, stack overflow, unauth network) rides along just below them. Everything else can be somewhat dismissed as local-only noise, but remember the mount-a-drive trio that where “requires physical access” describes every USB port in the building.

The USB Stack: There are 23 bugs impacting the USB stack, but I really only want to talk about one. CVE-2026-68839 (USB Mass Storage Class Driver) with a CVSS of 9.8 and a network vector. The FAQ offers only the generic “in-network attacker calling arbitrary endpoints” boilerplate, which doesn't explain how a USB class driver is network-reachable. Either the metric is scored to worst case or there's a remote path (RDP device redirection would be the plausible one). I'd treat the score skeptically in print but patch like it's real.

Kerberos and the KDC: Six different bugs affect these components, but it’s the two Critical rated ones that raised my eyebrows. Six bugs across Kerberos and the KDC — two Critical RCEs, two EoPs, and two DoS. Nothing exploited or disclosed, but one carries the rating that matters. CVE-2026-69676 is an RCE in Kerberos with a CVSS of 8.8 and classified as Exploitation More Likely. An authenticated attacker with low-level access sends a crafted request and executes code on the server, no user interaction. “The server” here means a domain controller, and any authenticated attacker means any domain user. So the realistic read is: one phished workstation account, one crafted request, code execution on the DC. That's a domain-compromise primitive, and Microsoft expects to see it exploited. CVE-2026-69712 is in KDC and reads almost identical to the previous: authenticated, low-level access, crafted request, code on the server, no interaction, but this one's a use-after-free in the KDC itself, the component that mints every ticket in the domain. Its practical impact is identical to 69676; only the exploitability rating separates them.

Exploitation More Likely: If you prioritize by Microsoft’s Exploit Index (XI), which I don’t recommend, there are a couple of bugs not mentioned yet: CVE-2026-72940 (Schannel RCE, CVSS 8.8, TLS stack), CVE-2026-72957 (Windows Deployment Services RCE, CVSS 7.8, PXE infrastructure), CVE-2026-71343 (Remote Access Connection Manager RCE, CVSS 7.8), and CVE-2026-70585 (a third NFS ONCRPC XDR RCE, CVSS 7.0). Again, I take all of these rating with a gigantic grain of salt, but you do you.

The Remnants: Another ~100 bugs land in six familiar components: Win32k (25), Standard XPS (18), WER (13), Device Association (13), Search (11), Print Spooler (11). Almost all are local EoPs to SYSTEM, but don't skim past them: 19 are rated More Likely, and XPS smuggles in an unauthenticated 9.8 RCE (CVE-2026-69824).

No new advisories are being released this month.

Looking Ahead

The next Patch Tuesday will be on October 13. Assuming I survive the fun that is Pwn2Own Ireland, I’ll be back then to give you my full thoughts on the release – no matter how large it may be. Until then, stay safe, happy patching, and may all your reboots be smooth and clean!
The August 2026 Security Update Review

I’ve successfully survived Hacker Summer Camp, and I have returned with a new outlook on patch density. When even Linus Torvalds says that huge updates are the “new normal”, it’s time to readjust what we consider a true bug apocalypse. This month’s release is thankfully smaller than last months, but still huge by historical standards. Take a break from your regularly scheduled activities as we take a look at the latest security patches from Adobe and Microsoft. If you’d rather watch the full video recap covering the entire release, you can check it out here:

Adobe Patches for August 2026

For the first part of the August release, Adobe released five bulletins addressing 51 unique CVEs in Adobe ColdFusion, Commerce, Lightroom Classic, Content Credentials SDK, and Adobe Campaign Classic.

Here’s this month’s overview table:

Adobe Patches for August 2026

Adobe Patches for August 2026

Bulletin ID Product CVE Count Highest Severity Highest CVSS Exploited Deployment Priority
APSB26-90 Adobe ColdFusion 15 Critical 10.0 No 1
APSB26-123 Adobe Campaign Classic 3 Critical 10.0 No 1
APSB26-92 Adobe Commerce 7 Critical 9.1 No 2
APSB26-94 Adobe Lightroom Classic 11 Critical 8.6 No 3
APSB26-111 Content Credentials SDK 15 Critical 7.5 No 3
TOTAL 5 bulletins 51

If you’re running Campaign Classic, that’s your priority. Not only is it a deployment priority of 1, but it also contains two different CVSS 10 bugs and supersedes the patch that was just released on August 3. ColdFusion is also deployment priority 1 and also contains a CVSS 10 bug. Adobe Commerce rates a priority 2 with code execution bugs as high as CVSS 9.1. The patches for Lightroom Classic and Content Credentials SDK are packed with CVEs, but only rate a deployment priority of 3.

None of the Adobe bugs receiving patches this month are listed as publicly known or under active attack at the time of release.

Microsoft Patches for August 2026

There are a couple of things to point out right at the beginning. Again, counting is difficult due to the size, but I see 398 new CVEs to go along with the other updates documented this month. However, there is only one listed being under active attack, so we’ve got that going for us, which is nice. The release impacts Windows and Windows components, Office and Office Components, AMD Zen, Azure and Azure Components, GitHub Copilot, Windows Defender, Exchange Server, SharePoint, OneDrive for macOS, Teams, Power BI, .NET and Visual Studio, DHCP Server and Client, DNS Server, and Windows TPM. Minecraft is absent from this release.  All told, there are 62 rated Critical, one rated Moderate, with the rest rated Important in severity. Eight of these bugs were submitted through the ZDI program.

This volume of updates indeed seems to be the new normal – at least for now. What is interesting is that, while there is an explosion of bugs being reported (and fixed), there has been no equivalent increase in the number of bugs being actively exploited, at least as 0-days.

Again, we’ll start with the bug under active attack and move on from there.

-              CVE-2026-68820 - Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability
This bug allows attackers to execute code at SYSTEM level. Bugs of this type are often paired with code execution bugs to take over a system, often through phishing or ransomware. One nitpick here: Microsoft lists the Exploit Code Maturity in the CVSS as “Unproven” but calls this out as actively exploited. Somewhere, that math ain’t mathing.

-              CVE-2026-62878 - Windows DNS Server Remote Code Execution Vulnerability
There are several DNS-related patches this month, but this one stands out by far. It allows a remote, unauthenticated attacker to execute code with elevated privileges without user interaction. It’s a good ol’ fashioned stack-based buffer overflow that ends up wormable. Microsoft states exploitation is less likely, but I wouldn’t count on that. I suggest testing and deploying this one quickly, especially to your Internet-facing DNS servers.

 -              CVE-2026-62893 - Windows Deployment Services TFTP Server Remote Code Execution Vulnerability
This bug came through the ZDI program and allows for code execution without user authentication or user interaction. TFTP has no auth mechanism and is available remotely vid UDP port 69. Any WDS server serving Windows Imaging Format (WIM) files via TFTP (the standard PXE boot scenario) is vulnerable. The issue results from the lack of validating the existence of an object prior to performing operations on the object. UDP port 69 should be blocked at your perimeter, but this could easily be used by attackers for lateral movement within an enterprise. Again, test and deploy this one quickly if you’re using WDS for deployments in your enterprise.

 -              CVE-2026-62815 - Microsoft QUIC Remote Code Execution Vulnerability
Here we have another remote, unauthenticated code execution bug that doesn’t require user interaction. This one is in the QUIC component. If you aren’t familiar with it, QUIC is an IETF-standardized transport protocol that runs over UDP instead of TCP, and it's the foundation for HTTP/3. Roughly 13.5 million websites rely on it. If you are one of those millions, test and deploy this patch rapidly.

 -              CVE-2026-59124 - Microsoft High Performance Computing (HPC) Pack Remote Code Execution Vulnerability
Don’t let the Important severity rating fool you; this is still a CVSS 9.8 bug. It gets knocked down since HPC isn’t on by default. However, it’s a hugely growing segment, and this is another remote, unauthenticated code execution bug that does not require user interaction. It might not be applicable to everyone, but if you’re using HPC in your environment, this is not one to sleep on, especially since Microsoft lists this as “exploitation more likely”.

 -              CVE-2026-62911 - Microsoft Exchange Server Elevation of Privilege Vulnerability
There are several Exchange bugs in this release, but this one really stands out. It could allow a privilege escalation via an authentication bypass. If successful, an attacker could “take over the mailboxes of all Exchange users, attackers can send emails, read emails, download attachments.” This bug was one of the ones demonstrated at Pwn2Own Berlin, so ignore Microsoft’s exploitability and Exploit Code Maturity ratings. We handed them working exploits, so this is a real threat. As always, test out those Exchange updates before deploying, but don’t hurry up and schedule that downtime for your upgrade.

Here’s the full list of CVEs released by Microsoft for August 2026:

CVE Title Severity CVSS Public Exploited Type
CVE-2026-68820 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No Yes EoP
CVE-2026-62832 Windows User Profile Service Elevation of Privilege Vulnerability Important 7.8 Yes No EoP
CVE-2026-49163 ** Application Insights Profiler Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-50481 ** Azure Active Directory Elevation of Privilege Vulnerability Critical 9.9 No No EoP
CVE-2026-68823 ** Azure Confidential Ledger Remote Code Execution Vulnerability Critical 9.1 No No RCE
CVE-2026-62869 ** Azure Entra ID Spoofing Vulnerability Critical 8.8 No No Spoofing
CVE-2026-56161 ** Azure Logic Apps Information Disclosure Vulnerability Critical 9.6 No No Info
CVE-2026-50515 ** Azure Service Bus Remote Code Execution Vulnerability Critical 9.9 No No RCE
CVE-2026-56162 ** Azure SQL Database Elevation of Privilege Vulnerability Critical 10 No No EoP
CVE-2026-63522 ** Azure SQL Database Elevation of Privilege Vulnerability Critical 7.8 No No EoP
CVE-2026-62836 ** Azure SQL Managed Instance Elevation of Privilege Vulnerability Critical 8.7 No No EoP
CVE-2026-62830 ** Azure SRE Agent Elevation of Privilege Vulnerability Critical 9.9 No No EoP
CVE-2026-62873 ** Microsoft 365 Admin Center Elevation of Privilege Vulnerability Critical 9.8 No No EoP
CVE-2026-50516 ** Microsoft Azure Kubernetes Service Elevation of Privilege Vulnerability Critical 9.4 No No EoP
CVE-2026-59115 ** Microsoft Entra Provisioning Service Elevation of Privilege Vulnerability Critical 9.9 No No EoP
CVE-2026-68794 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-68804 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-68816 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-62911 Microsoft Exchange Server Elevation of Privilege Vulnerability Critical 8 No No EoP
CVE-2026-63513 Microsoft Office Graphics Component Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-63519 Microsoft Office Graphics Component Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-63526 Microsoft Office Graphics Component Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-65664 Microsoft Office Graphics Component Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-66807 Microsoft Office Graphics Component Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-63515 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-63532 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-64898 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-64903 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-64909 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-64910 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-64911 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-65657 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-70130 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-70332 ** Microsoft Office SharePoint Spoofing Vulnerability Critical 9.6 No No Spoofing
CVE-2026-63518 Microsoft Office Word Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-63525 Microsoft Office Word Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-64907 Microsoft Office Word Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-63508 ** Microsoft Planetary Computer Pro Elevation of Privilege Vulnerability Critical 10 No No EoP
CVE-2026-59118 ** Microsoft Power Apps Elevation of Privilege Vulnerability Critical 9.3 No No EoP
CVE-2026-65668 ** Microsoft Purview eDiscovery Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-62815 Microsoft QUIC Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-62827 Microsoft SharePoint Server Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-64921 Microsoft SharePoint Server Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-65665 Microsoft SharePoint Server Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-62896 ** Microsoft Teams Elevation of Privilege Vulnerability Critical 9.6 No No EoP
CVE-2026-65667 ** Microsoft Teams Elevation of Privilege Vulnerability Critical 10 No No EoP
CVE-2026-62918 ** Microsoft Teams Spoofing Vulnerability Critical 7.5 No No Spoofing
CVE-2026-62824 Remote Desktop Client Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-62818 Windows Active Directory Certificate Services (AD CS) Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-62893 Windows Deployment Services TFTP Server Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-66802 Windows Device Health Attestation (DHA) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-71331 Windows Device Health Attestation (DHA) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-62823 Windows DHCP Server Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-62817 Windows DNS Server Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-62820 Windows DNS Server Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-62878 Windows DNS Server Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-65789 Windows DNS Server Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-62890 Windows GDI+ Elevation of Privilege Vulnerability Critical 7.8 No No EoP
CVE-2026-62822 Windows GDI+ Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-65791 Windows iSCSI Target Service Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-66799 Windows Key Guard Elevation of Privilege Vulnerability Critical 7.8 No No EoP
CVE-2026-62816 Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-62819 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-62889 Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-70354 .NET Core Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-62901 .NET Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-58641 .NET Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62871 .NET Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62886 .NET Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62909 .NET Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62872 .NET Framework Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-65810 .NET Framework Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62897 .NET Framework Remote Code Execution Vulnerability Important 7 No No RCE
CVE-2026-62900 .NET Information Disclosure Vulnerability Important 5.9 No No Info
CVE-2026-62902 .NET Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62899 .NET Security Feature Bypass Vulnerability Important 5.9 No No SFB
CVE-2026-65777 Active Directory Security Feature Bypass Vulnerability Important 5.3 No No SFB
CVE-2026-59130 AMD Zen Information Disclosure Vulnerability Important 5.6 No No Info
CVE-2026-59131 AMD Zen Information Disclosure Vulnerability Important 5.6 No No Info
CVE-2026-62898 Microsoft QUIC Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-61357 Application Information Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70340 Azure CycleCloud Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-65806 Azure CycleCloud Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-47299 Azure Monitor Agent Elevation of Privilege Vulnerability Important 7.2 No No EoP
CVE-2026-57104 Azure Storage Explorer Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-62892 Capability Access Management Service (camsvc) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65675 CoPilot Chat Security Feature Bypass Vulnerability Important 7.1 No No SFB
CVE-2026-65786 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65787 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65788 Desktop Window Manager Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-70335 GitHub Copilot and Visual Studio Code Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-64906 Microsoft Access Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-64908 Microsoft Access Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-64912 Microsoft Access Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-64914 Microsoft Access Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-64919 Microsoft Access Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-64920 Microsoft Access Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-59136 Microsoft COM for Windows Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-54123 Microsoft Defender for Endpoint for Mac Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62698 Microsoft Digest Authentication Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-66301 Microsoft Dynamics 365 (On-Premises) Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-65815 Microsoft Dynamics 365 On-Premises Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-40375 Microsoft Dynamics Business Central Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-65673 Microsoft Entra Connect Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-68797 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68799 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68802 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68808 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68813 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70318 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70327 Microsoft Excel Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-70328 Microsoft Excel Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-65807 Microsoft Excel Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-68793 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68795 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68796 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68798 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68800 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68801 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68803 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68805 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68806 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68807 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68810 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68811 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68812 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68814 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68815 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-68817 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-62912 Microsoft Exchange Server Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-62910 Microsoft Exchange Server Elevation of Privilege Vulnerability Important 7.2 No No EoP
CVE-2026-65813 Microsoft Exchange Server Elevation of Privilege Vulnerability Important 6.5 No No EoP
CVE-2026-62913 Microsoft Exchange Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-62915 Microsoft Exchange Server Security Feature Bypass Vulnerability Important 6.5 No No SFB
CVE-2026-62914 Microsoft Exchange Server Spoofing Vulnerability Important 7.3 No No Spoofing
CVE-2026-59133 Microsoft High Performance Computing (HPC) Pack Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-59124 Microsoft High Performance Computing (HPC) Pack Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-62784 Microsoft Local Security Authority Server (lsasrv) Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-68792 Microsoft Office Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62842 Microsoft Office Graphics Component Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-63517 Microsoft Office Graphics Component Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-66809 Microsoft Office Graphics Component Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-63524 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-63529 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-64899 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70314 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70315 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70317 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70323 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-63533 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-64904 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-65656 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-65661 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-57105 Microsoft Office SharePoint Spoofing Vulnerability Important 8 No No Spoofing
CVE-2026-70306 Microsoft Office SharePoint Spoofing Vulnerability Important 9.3 No No Spoofing
CVE-2026-63521 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-63528 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-63530 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-63531 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-64917 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-66806 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-66810 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70319 Microsoft Office Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-63527 Microsoft Office Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-64905 Microsoft Office Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-64915 Microsoft Office Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-70311 Microsoft Office Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-65680 Microsoft OneDrive for MacOS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-70329 Microsoft Outlook Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-62882 Microsoft Outlook Spoofing Vulnerability Important 4.3 No No Spoofing
CVE-2026-70313 Microsoft PowerPoint Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-70337 Microsoft PowerShell Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-70338 Microsoft PowerShell Security Feature Bypass Vulnerability Important 7.8 No No SFB
CVE-2026-59138 Microsoft Remote Registry Service Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-61345 Microsoft Remote Registry Service Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-70324 Microsoft SharePoint Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-70321 Microsoft SharePoint Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-70326 Microsoft SharePoint Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-70355 Microsoft SharePoint Server Elevation of Privilege Vulnerability Important 7.3 No No EoP
CVE-2026-62837 Microsoft SharePoint Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-63514 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-63520 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-64901 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-65658 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-65663 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-66805 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-66808 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-58639 Microsoft SharePoint Server Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-62829 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-62839 Microsoft SharePoint Server Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-62917 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-63516 Microsoft SharePoint Server Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-64897 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-64900 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-64902 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-64916 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-64922 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-65660 Microsoft SharePoint Server Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-63512 Microsoft SharePoint Server Tampering Vulnerability Important 6.5 No No Tampering
CVE-2026-65767 Microsoft Teams for Android and iOS Spoofing Vulnerability Important 8.8 No No Spoofing
CVE-2026-65769 Microsoft Teams iOS Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-65768 Microsoft Teams Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-66804 Microsoft Windows Cross Device Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-59135 Microsoft Windows Search Component Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-65814 Microsoft Windows Storage Port Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70310 Microsoft Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-58651 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-6726 * MITRE: CVE-2026-6726 TPM 2.0 Improper Object Slot Reuse Important 7.9 No No
CVE-2026-6727 * MITRE: CVE-2026-6727 TPM 2.0 RSA OAEP Timing Side-Channel Vulnerability Important 5.9 No No
CVE-2026-65811 Power BI Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-68809 Powerpoint Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70312 Powerpoint Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70316 Powerpoint Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70320 Powerpoint Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70322 Powerpoint Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70325 Powerpoint Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-59119 PowerShell Elevation of Privilege Vulnerability Important 7.3 No No EoP
CVE-2026-58612 PowerShell Information Disclosure Vulnerability Important 7.4 No No Info
CVE-2026-65671 Remote Access API Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65672 Remote Access API Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-42976 Remote Access Management service/API (RPC server) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-59134 Remote Desktop Client Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-61352 Remote Desktop Client Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-61363 Remote Desktop Client Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-54113 Remote Procedure Call Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-62781 RPC Runtime Library Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-59125 Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability Important 7 No No EoP
CVE-2026-47285 Visual Studio Code Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-54981 Visual Studio Code Python Extension Security Feature Bypass Vulnerability Important 7.8 No No SFB
CVE-2026-59113 Visual Studio Code Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-69320 Visual Studio Code Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-70336 Visual Studio Code Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-58650 Visual Studio Code Security Feature Bypass Vulnerability Important 7.8 No No SFB
CVE-2026-69278 Visual Studio Code Security Feature Bypass Vulnerability Important 7.8 No No SFB
CVE-2026-69306 Visual Studio Code Security Feature Bypass Vulnerability Important 8.2 No No SFB
CVE-2026-62743 Win32k Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62746 Win32k Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62786 Win32k Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62798 Win32k Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-61358 Windows Accessibility Infrastructure (ATBroker.exe) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49179 Windows Active Directory Domain Services Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-61348 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-70307 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65778 Windows Autopilot Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65779 Windows Autopilot Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65780 Windows Autopilot Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65781 Windows Autopilot Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65782 Windows Autopilot Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65783 Windows Autopilot Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62908 Windows Backup Engine Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-61927 Windows Bind Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-61934 Windows Bind Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62705 Windows Bind Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62722 Windows Bind Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62713 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62771 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62728 Windows Common Log File System Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62772 Windows Container Isolation FS Filter Driver (unionfs.sys) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62775 Windows Container Isolation FS Filter Driver (unionfs.sys) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-72971 Windows Container Isolation FS Filter Driver (unionfs.sys) Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-61936 Windows Defender Firewall Service Security Feature Bypass Vulnerability Important 5.5 No No SFB
CVE-2026-62710 Windows Device Association Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62747 Windows Device Association Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65785 Windows DHCP Client Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-62736 Windows DHCP Client Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62755 Windows DHCP Client Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61361 Windows DHCP Client Remote Code Execution Vulnerability Important 7 No No RCE
CVE-2026-62761 Windows DHCP Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62776 Windows DHCP Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62803 Windows DHCP Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62807 Windows DHCP Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62812 Windows DHCP Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62714 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62715 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62716 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62718 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62720 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62742 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62745 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62814 Windows DHCP Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-61923 Windows Display Enhancement Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62769 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-62778 Windows DNS Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-62881 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-62883 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-65795 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-65797 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-65798 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-65799 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-70304 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-70330 Windows DNS Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-61920 Windows DNS Server Remote Code Execution Vulnerability Important 6.6 No No RCE
CVE-2026-62787 Windows DNS Server Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-61932 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62888 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62894 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61933 Windows DWM Core Library Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62703 Windows DWM Core Library Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-59128 Windows Encrypting File System (EFS) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-59126 Windows Event Logging Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-59137 Windows Event Logging Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-61347 Windows Event Logging Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-61360 Windows GDI Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-65662 Windows GDI Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62709 Windows GDI+ Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62702 Windows Graphics Kernel Denial of Service Vulnerability Important 6.8 No No DoS
CVE-2026-61346 Windows Graphics Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62774 Windows Graphics Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-61928 Windows Hello Tampering Vulnerability Important 5.5 No No Tampering
CVE-2026-62750 Windows HTTP Protocol Stack Tampering Vulnerability Important 6.5 No No Tampering
CVE-2026-61937 Windows HTTP.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62735 Windows HTTP.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62739 Windows HTTP.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62741 Windows HTTP.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62753 Windows HTTP.sys Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62811 Windows HTTP.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61368 Windows Hyper-V Information Disclosure Vulnerability Important 5 No No Info
CVE-2026-62740 Windows Imaging Component Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-54984 Windows Imaging Component Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-59127 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61925 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61938 Windows Installer Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62768 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65774 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70344 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70345 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70346 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-70347 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65681 Windows iSCSI Target Service Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-65796 Windows iSCSI Target Service Denial of Service Vulnerability Important 5.9 No No DoS
CVE-2026-65679 Windows iSCSI Target Service Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-62752 Windows Kerberos Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62754 Windows Kerberos Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62766 Windows Kerberos Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62773 Windows Kerberos Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-61929 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-61930 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62708 Windows Kernel Elevation of Privilege Vulnerability Important 6.4 No No EoP
CVE-2026-62737 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62749 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62780 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62788 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65773 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62785 Windows LDAP - Lightweight Directory Access Protocol Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-62795 Windows LDAP - Lightweight Directory Access Protocol Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-62777 Windows License Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50472 Windows LUA File Virtualization Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62738 Windows Management Instrumentation Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-70348 Windows Management Services Denial of Service Vulnerability Important 5.5 No No DoS
CVE-2026-62717 Windows Message Queuing Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62719 Windows Message Queuing Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65790 Windows Message Queuing Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62688 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 7.8 No No EoP
CVE-2026-62693 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 7 No No EoP
CVE-2026-62707 Windows Modern Device Management (MDM) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56174 Windows Narrator Braille Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61366 Windows Network Connection Broker Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-68819 Windows Network File System Denial of Service Vulnerability Important 5.9 No No DoS
CVE-2026-62700 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62797 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62880 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61350 Windows NTFS Information Disclosure Vulnerability Important 4.6 No No Info
CVE-2026-62793 Windows NTFS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62796 Windows NTFS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-62887 Windows NTFS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-65784 Windows NTFS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-68821 Windows Package Manager Elevation of Privilege Vulnerability Important 7.3 No No EoP
CVE-2026-62696 Windows Program Compatibility Assistant Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62751 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62690 Windows Push Notifications Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62758 Windows Remote Access Connection Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62783 Windows Remote Access Connection Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61918 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-61921 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-61924 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-61356 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61364 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61365 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61367 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62692 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62779 Windows Schannel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62757 Windows Schannel Security Feature Bypass Vulnerability Important 5.3 No No SFB
CVE-2026-61355 Windows Sensor Data Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62770 Windows Shell Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62799 Windows SMB Client Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62782 Windows SMB Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-65794 Windows SMB Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-62790 Windows SMBv3 Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-62800 Windows SMBv3 Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-61359 Windows Storage Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62695 Windows Storage Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-59132 Windows TCP/IP Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-62792 Windows TCP/IP Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-59122 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-61353 Windows Telephony Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62701 Windows Telephony Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62723 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62724 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62725 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62726 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62729 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62732 Windows Telephony Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62734 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62748 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62699 Windows Universal Disk Format File System Driver (UDFS) Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-61926 Windows USB Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62721 Windows User-Mode Power Service (UMPS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62711 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62712 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62733 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62876 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62877 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-62885 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65678 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-65775 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-65776 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-62730 Windows Wired AutoConfig Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-61349 Windows Work Folder Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-61939 Winlogon Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-56179 Windows Network Address Translation (NAT) Spoofing Vulnerability Moderate 8.3 No No Spoofing

* Indicates this CVE had been released by a third party and is now being included in Microsoft releases.

** Indicates this CVEs has already been resolved by Microsoft, and no further action is needed by the end user.


As with last month, I’ll do my best to summarize everything else in this release, but assume there are details I miss that are relevant to your environment.

Looking at the remaining Critical-rated patches, you are safe to ignore the scariest looking ones, including the CVSS 10’s. These have already been mitigated by Microsoft and do not count towards today’s total of 398. The iSCSI Target service, however, is a CVSS 9.8, but it’s not installed by default. Microsoft notes a DHCP Server heap overflow and a SharePoint deserialization bug are both listed as “exploitation more likely”. That SharePoint bug brought two EoP siblings along for the ride. And what would a Patch Tuesday be without Preview Pane exploit vectors in Office components? There are many in August, although there are a few Office bugs listed as Critical but without the Preview Pane vector. Odd. Then there’s the mid-tier pile no one is proud of, but everybody needs to patch anyway: AD CS, RRAS, SSTP, and a matched pair in Device Health Attestation, all leaning on higher attack complexity as their only saving grace. Consider this a coin flip, not a shield. The bug in RMCAST is unauthenticated but requires an adjacent attacker. The bug in Key Guard is a bit interesting, as it could lead to an attacker gaining Virtual Trust Level 1 (VTL1) privileges. The final Critical-rated bug is in the RDP client, but it requires a user to connect to a malicious RDP server.

Moving on to the other code execution bugs, SharePoint alone accounts for seven of these, six of them the same deserialization-of-untrusted-data flaw repeated almost verbatim across different code paths, all needing only low-privilege auth and no interaction. The seventh is an input-validation miss that needs no auth at all, just a harder-to-pull-off attack chain. LDAP and SMBv3 each draw a matching pair of patches. The LDAP bugs are a heap overflow and a use-after-free, both needing a user to interact with something first; the SMBv3 pair is twin heap overflows. Visual Studio Code adds three of its own: missing authorization, OS command injection, and straight code injection, all requiring a user to open or run something. The AI-coding-tool-vuln-of-the-month tradition continues uninterrupted. The rest of the CVSS 8.1–8.8 tier is a grab bag with a common thread — LSASS and Exchange Server both go down to heap overflows with low-privilege access, Dynamics 365 On-Premises gets the SharePoint treatment (deserialization), and Active Directory Domain Services picks up a command-injection bug that needs a user's cooperation. Add one apiece for Teams, Power BI, Outlook, and a pair for Windows Media Foundation, plus a higher-complexity trio: RPC Runtime Library, Windows TCP/IP, and a second iSCSI Target Service bug. All needing unusual attack conditions to line up, which buys you a little time but not an excuse. Then the file-format mountain: seventeen Excel bugs, six in Access, four apiece in Office and Office Word, one plain Word, one PowerPoint, one .NET Core. Remote Desktop Client's other three bugs sit at a comparatively modest 7.5, but don't read too much comfort into that — all three need high attack complexity and user interaction, which is precisely the combination phishing campaigns are built to satisfy. Closing out RCE category, there are two more DNS Server bugs, a DHCP Client use-after-free needing local low-privilege access, a Universal Disk Format driver bug that requires physical media and a Windows Codecs Library.

There are nearly 180 privilege escalation bugs fixed this month, and as usual, most simply lead to local attackers executing their code at SYSTEM-level privileges or administrative privileges, so there’s not much to add without further technical details about the bugs themselves. Believe it or not, that leaves only about 20 bugs to discuss. Access control keeps failing in the same places: SharePoint draws two EoPs, then contributes a third via server-side request forgery, and a fourth through cross-site scripting (XSS) that at least needs a user to click something first. Entra Connect adds a SQL injection, .NET Framework an incorrect-authorization bug, and Azure CycleCloud adds a missing-authorization flaw, That’s five different products with the same underlying lesson about checking who’s allowed to do what. Windows Telephony Service is the surprise repeat offender, landing four separate EoPs, but four bugs in one dusty legacy service in a single release is the kind of pattern that makes you wonder who's still dialing in. The rest is a genuine grab bag: Key Guard gets a heap overflow sitting on the trust chain below the OS, DHCP Client and Narrator Braille both fall to local low-privilege bugs, .NET picks up an uncaught exception that actually changes scope, .NET Framework adds a path-traversal bug requiring a click, GitHub Copilot and VS Code get an OS command injection needing the same, Azure Storage Explorer falls to XSS, Azure Monitor Agent and OneDrive for macOS both need high privileges just to start, which caps their real-world urgency, and Exchange Server closes it out with an SSRF bug whose blast radius Microsoft itself rates as confidentiality-only, no integrity or availability hit.

There are 11 SFB bugs this month, all Important, none exploited or publicly disclosed. Visual Studio Code accounts for four, Python extension included: one fails open outright, the other three trip on bad authorization checks — all need a click, which is a low bar in a tool people click through constantly. PowerShell adds a code-injection bypass, and Copilot Chat gets one as well. Exchange Server and Windows Defender Firewall Service both via have missing authorization bugs. The .NET service has a bug via HTTP request smuggling, Active Directory via weak encryption, and Schannel via bad signature verification. In the low individual urgency category, both Schannel and AD have bugs with  “broken crypto trust” are worth a second look despite the low scores.

Looking at the info disclosure bugs, and fortunately, the vast majority of these simply result in info leaks consisting of unspecified memory contents or memory addresses. There are few others of note. The CVSS 6.5 tier is the one with more bite: Windows DHCP Server alone accounts for eight of these, three more hit Remote Desktop Client, two hit SMB Client, two hit Excel, and singles land in PowerShell, .NET, Azure CycleCloud, two Dynamics products, SharePoint, Teams iOS, and VS Code. All are unauthenticated, network-reachable memory leaks, but DHCP Server picking up eight in one release is a pattern, not noise. Everything else sits at 5.5 or below and is almost entirely "leaks unspecified memory contents," differing mainly by which component leaks it. Office file formats dominate with roughly twenty bugs split across Excel, Word, Office generically, Office Graphics, and PowerPoint. Win32k contributes four, NTFS five, GDI/GDI+ three, Event Logging and WMI two apiece, DWM Core two, AMD Zen two. The remaining singles clear out fine during a normal patch cycle without special urgency.

Moving on to spoofing patches for August, SharePoint dominates with eleven bugs, mostly stored XSS letting an authenticated attacker spoof content, plus a mixed bag of deserialization, code injection, SSRF, and credential exposure at the low end. Outside SharePoint, Teams for Android/iOS gets a high-CVSS (8.8) XSS bug. Exchange Server gets one too. Windows NAT has a scope-changing origin-validation flaw reachable from an adjacent network, and Outlook closes it out with a credential-exposure spoofing bug.

There are 14 DoS bugs getting patched this month. NULL pointer dereferences dominate: TCP/IP, iSCSI Target Service, Windows Graphics Kernel, and Remote Registry Service (twice) all crash the same way, unauthenticated over the network. iSCSI Target Service adds a second DoS via heap overflow, with three hits total this release counting its RCE. Resource-exhaustion bugs cover .NET, RPC, DHCP Client, and Microsoft Identity - all unauthenticated, all just flood-and-crash. The rest need local or elevated access: Exchange Server, Windows Network File System, and path/link-resolution bug in Windows Management Services. In other words, nothing exotic. Just patch it in the normal cycle, with a nod to Remote Registry Service and iSCSI Target Service for repeat appearances.

Finally, there are a handful of tampering bugs receiving patches this month. They start with SharePoint via incorrect authorization. The Windows HTTP Protocol Stack has a bug via a partial string comparison flaw reachable from an adjacent network, and Windows Hello via cleartext storage of sensitive data locally. The Hello one is the one worth a second glance. Biometric auth storing something in the clear isn't a great look, even at a modest 5.5.

No new advisories are being released this month.

Looking Ahead

The next Patch Tuesday will be on September 8, just after Labor Day here is the US. I’ll be back then to give you my full thoughts on the release – no matter how large it may be. Until then, stay safe, happy patching, and may all your reboots be smooth and clean!
The July 2026 Apple Security Update Review

Welcome to our monthly look at Apple security patches. This release shows that Apple is not immune to the bug apocalypse that is impacting other vendors. Last month, they released 37 unique CVEs compare to this month’s 210. Quite a jump.

For July 2026, Apple released 210 unique CVEs across iOS/iPadOS 26.6, macOS Tahoe 26.6, macOS Sequoia 15.7.8, macOS Sonoma 14.8.8, tvOS 26.6, watchOS 26.6, visionOS 26.6, and Safari 26.6. Since Apple doesn’t provide CVSS scores or other severity information, we’re left to speculate on which of these bugs is the most severe. However, there are a couple that stand out.

·      CVE-2026-43818 (ImageIO) – This bug could allow the “Processing [of] a maliciously crafted image may lead to arbitrary code execution." ImageIO is the classic zero-/one-click remote surface on Apple platforms (images auto-parsed in Messages, previews, notifications), so this is the highest real-world remote-exploitation risk in the release. It’s also present across iOS and all macOS versions. Depending on delivery path, this is the one most likely to be weaponized into a remote foothold.

·      CVE-2026-64747 (AVEVideoEncoder) – According to Apple, “An app may be able to execute arbitrary code with kernel privileges.” Kernel-level code execution is the maximum-impact outcome on an Apple device: full compromise, defeats the sandbox and most mitigations. It's also unusually broad, shipping to iOS/iPadOS, all three macOS versions, tvOS, watchOS, and visionOS. Local-app precondition is its only limiter, and it's exactly the second stage a remote bug chains into.

·      CVE-2026-64767 (afpfs) – In this case, “A remote attacker may be able to cause unexpected system termination or corrupt kernel memory.” This bug is a network-reachable, apparently unauthenticated path to kernel memory corruption via Apple Filing Protocol. Remote plus kernel is a dangerous combination.  Also, the “remote attacker” versus “remote user” wording suggests no authentication required. This bug affects macOS only, which is the only reason it sits at #3 rather than higher.

Honorable mentions: CVE-2026-43776 (AppleDouble) and the SceneKit set (CVE-2026-64763/64/65/66) are additional file-parsing paths to arbitrary code execution. CVE-2026-43750 (Wi‑Fi) allows code execution out of the sandbox with elevated privileges. And finally, CVE-2026-64696 (SMB) / CVE-2026-43810 (Kernel) are further remote kernel-corruption bugs.

Here’s the full table of Apple patches and the products they affect:

Apple Security Updates — July 27, 2026 210Total CVEs 9Code Execution 26Elevation of Privilege 11Sandbox Escape 9Security Feature Bypass 15Memory Corruption 55Information Disclosure 2Spoofing / UI 75Denial of Service 8Other
Apple security release — July 27, 2026 (iOS/iPadOS 26.6, macOS Tahoe 26.6, macOS Sequoia 15.7.8, macOS Sonoma 14.8.8, tvOS 26.6, watchOS 26.6, visionOS 26.6, Safari 26.6). "Yes/No" indicates whether each update is affected. CVE IDs link to NVD.
CVE ID Component Impact iOS / iPadOS 26.6 macOS Tahoe 26.6 macOS Sequoia 15.7.8 macOS Sonoma 14.8.8 tvOS 26.6 watchOS 26.6 visionOS 26.6 Safari 26.6
CVE-2026-64732 Accessibility An attacker with physical access may be able to access sensitive user data during iPhone Mirroring YesNoNoNoNoNoNoNo
CVE-2026-43749 Accounts An app may be able to gain root privileges NoYesYesYesNoNoNoNo
CVE-2026-43819 Accounts An app may be able to access sensitive user data NoYesNoNoNoNoNoNo
CVE-2026-64733 Accounts Framework An app may be able to fingerprint the user YesYesNoNoYesYesYesNo
CVE-2026-64767 afpfs A remote attacker may be able to cause unexpected system termination or corrupt kernel memory NoYesYesYesNoNoNoNo
CVE-2026-23918 apache A remote attacker may be able to cause a denial-of-service NoYesYesYesNoNoNoNo
CVE-2026-64695 APFS A remote user may be able to cause unexpected system termination or corrupt kernel memory NoYesYesYesNoNoNoNo
CVE-2026-43801 App Store An app may be able to access sensitive user data YesYesYesYesYesYesYesNo
CVE-2026-43781 Apple Account An app may be able to access sensitive user data NoYesYesYesNoNoNoNo
CVE-2026-64737 Apple Account A malicious app may be able to break out of its sandbox NoYesYesYesNoNoNoNo
CVE-2026-28928 Apple Neural Engine An app may be able to cause unexpected system termination YesYesNoNoYesYesNoNo
CVE-2026-43748 Apple Neural Engine An app may be able to cause unexpected system termination NoYesYesNoNoNoNoNo
CVE-2026-43776 AppleDouble Processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution YesYesYesNoNoNoNoNo
CVE-2026-43681 AppleRAID A local user may be able to read kernel memory NoYesYesYesNoNoNoNo
CVE-2026-43672 Assets A malicious application may be able to bypass Privacy preferences NoYesYesYesNoNoNoNo
CVE-2026-43763 ATS An app may be able to read files outside of its sandbox NoYesYesYesNoNoNoNo
CVE-2026-64702 Audio An app may be able to break out of its sandbox NoYesYesYesNoNoNoNo
CVE-2026-64725 Audio An app may be able to cause a denial-of-service YesYesYesYesYesYesYesNo
CVE-2026-43730 AuthKit An app may be able to fingerprint the user YesYesNoNoYesYesYesNo
CVE-2026-64747 AVEVideoEncoder An app may be able to execute arbitrary code with kernel privileges YesYesYesYesYesYesYesNo
CVE-2026-64762 AVEVideoEncoder An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-64707 BackgroundAssets An app may be able to delete files for which it does not have permission YesYesYesYesNoNoYesNo
CVE-2026-28849 BOM A maliciously crafted ZIP archive may bypass Gatekeeper checks NoNoYesYesNoNoNoNo
CVE-2026-43811 Books An app may be able to modify protected parts of the file system YesNoNoNoNoNoNoNo
CVE-2026-64698 cd9660 An app may be able to cause unexpected system termination or read kernel memory NoYesYesYesNoNoNoNo
CVE-2026-43813 CloudAttestation A maliciously crafted app may be able to bypass code signing enforcement YesYesNoNoYesYesYesNo
CVE-2026-43797 Contacts An app may be able to access information about a user's contacts YesYesNoNoNoNoNoNo
CVE-2026-64734 Contacts Processing a maliciously crafted contact may leak sensitive data YesYesYesYesNoYesYesNo
CVE-2026-64746 Contacts An app may be able to add contacts without user authorization YesYesNoNoNoYesYesNo
CVE-2026-43756 Control Center An app may be able to access user-sensitive data NoYesYesYesNoNoNoNo
CVE-2026-43693 Core Services An app may be able to gain root privileges NoYesYesYesNoNoNoNo
CVE-2026-43673 CoreAudio Processing a maliciously crafted audio file may corrupt process memory YesYesYesYesYesYesYesNo
CVE-2026-43744 CoreAudio Processing an audio stream in a maliciously crafted media file may terminate the process YesYesYesYesYesYesYesNo
CVE-2026-43803 CoreAudio A remote attacker may be able to cause unexpected system termination YesYesYesYesYesYesYesNo
CVE-2026-43711 CoreMedia Processing a maliciously crafted video file may lead to unexpected app termination YesYesYesYesYesYesYesNo
CVE-2026-43759 CoreMedia An app may be able to access sensitive user data NoYesNoNoNoYesNoNo
CVE-2026-43775 CoreMedia An app may be able to access sensitive user data NoYesYesNoNoNoNoNo
CVE-2026-28936 CoreServices Processing a maliciously crafted file may lead to unexpected app termination NoNoYesYesNoNoNoNo
CVE-2026-43738 CoreUI Processing a maliciously crafted asset catalog may result in disclosure of process memory NoNoYesYesNoNoNoNo
CVE-2026-43802 CoreVideo An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-64710 Crash Reporter An app may be able to leak sensitive user information NoYesYesYesNoNoNoNo
CVE-2026-39875 CUPS A malicious app may be able to gain root privileges NoYesYesYesNoNoNoNo
CVE-2026-43698 CUPS An app may be able to gain root privileges NoNoYesYesNoNoNoNo
CVE-2026-3783 curl Authentication credentials may be sent to a server on another origin YesYesYesYesYesYesNoNo
CVE-2026-3784 curl Authentication credentials may be sent to a server on another origin YesYesYesYesYesYesNoNo
CVE-2026-43758 Data Detectors UI An app may be able to access sensitive user data NoYesYesYesNoYesNoNo
CVE-2026-64708 DesktopServices An app may bypass Gatekeeper checks NoYesYesYesNoNoNoNo
CVE-2026-28926 Disk Images An app may be able to elevate privileges NoNoYesYesNoNoNoNo
CVE-2026-28945 Disk Images An app may be able to bypass network restrictions NoYesYesYesNoNoNoNo
CVE-2026-43747 Disk Images Parsing a maliciously crafted file may lead to an unexpected app termination NoYesYesYesNoNoNoNo
CVE-2026-64694 Disk Images An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-64776 Disk Images An app may be able to disclose kernel memory NoYesYesYesNoNoNoNo
CVE-2026-43753 DriverKit An attacker with physical access to a locked device may be able to view sensitive user information YesYesYesYesNoNoNoNo
CVE-2026-43793 DriverKit An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-43714 Foundation A malicious app may be able to access protected user data YesYesYesYesNoYesYesNo
CVE-2026-64742 FrontBoard An app may be able to access sensitive user data YesNoNoNoYesYesYesNo
CVE-2026-43796 Game Center An app may be able to access sensitive user data YesYesYesYesYesYesYesNo
CVE-2026-64740 Game Center A malicious app may be able to break out of its sandbox YesYesYesYesYesNoNoNo
CVE-2026-64691 GPU Drivers An app may be able to cause unexpected system termination NoYesNoNoNoNoNoNo
CVE-2026-64692 Heimdal An app may be able to cause a denial-of-service YesYesYesYesYesYesYesNo
CVE-2026-28981 HFS Processing a maliciously crafted image may lead to arbitrary code execution NoYesYesYesNoNoNoNo
CVE-2026-43682 HFS A remote user may be able to cause unexpected system termination or corrupt kernel memory NoYesYesYesNoNoNoNo
CVE-2026-43710 HFS An attacker may be able to cause unexpected system termination or corrupt kernel memory NoYesYesYesNoNoNoNo
CVE-2026-43764 HFS An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-43767 HFS An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-43773 HFS Mounting a maliciously crafted disk image may cause unexpected system termination or corrupt kernel memory NoYesYesYesNoNoNoNo
CVE-2026-64697 HFS An app may be able to cause unexpected system termination or corrupt kernel memory NoYesYesYesNoNoNoNo
CVE-2025-43325 Icons An app may be able to access sensitive user data NoNoYesYesNoNoNoNo
CVE-2026-43661 ImageIO Processing a maliciously crafted image may corrupt process memory NoNoYesYesNoNoNoNo
CVE-2026-43780 ImageIO Processing a maliciously crafted texture may lead to unexpected app termination YesYesYesYesYesYesYesNo
CVE-2026-43818 ImageIO Processing a maliciously crafted image may lead to arbitrary code execution YesYesYesYesNoNoNoNo
CVE-2026-64693 ImageIO Processing a maliciously crafted image may lead to a denial-of-service YesYesYesYesYesYesYesNo
CVE-2026-64716 ImageIO Processing a maliciously crafted image may corrupt process memory YesYesYesYesYesYesYesNo
CVE-2026-64754 ImageIO Processing a maliciously crafted file may lead to a denial-of-service YesYesYesYesYesYesYesNo
CVE-2026-64758 ImageIO Processing a maliciously crafted file may lead to unexpected app termination YesYesNoNoYesYesYesNo
CVE-2026-43743 IOGPUFamily An app may be able to cause unexpected system termination NoNoNoNoYesYesNoNo
CVE-2026-43805 IOKit An app may be able to cause unexpected system termination or write kernel memory YesYesYesYesNoYesNoNo
CVE-2026-39877 IOSkywalkFamily An app may be able to disclose kernel memory NoNoYesYesNoNoNoNo
CVE-2026-28931 Kernel Connecting to a malicious NFS server may lead to kernel memory corruption YesYesNoNoYesYesNoNo
CVE-2026-28982 Kernel A remote user may be able to cause unexpected system termination or corrupt kernel memory NoYesYesYesNoNoNoNo
CVE-2026-39868 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory NoNoYesYesYesYesYesNo
CVE-2026-43722 Kernel An app may be able to leak sensitive kernel state NoNoYesYesNoNoNoNo
CVE-2026-43724 Kernel An app may be able to cause unexpected system termination or write kernel memory NoNoYesYesYesYesYesNo
CVE-2026-43739 Kernel An app may be able to cause unexpected system termination YesYesNoNoYesYesYesNo
CVE-2026-43754 Kernel An app may be able to leak sensitive kernel state NoYesYesYesNoNoNoNo
CVE-2026-43757 Kernel An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-43769 Kernel An app may be able to cause unexpected system termination YesYesYesYesYesYesYesNo
CVE-2026-43778 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory YesYesYesYesYesYesYesNo
CVE-2026-43782 Kernel An app may be able to access sensitive user data NoYesYesYesNoNoNoNo
CVE-2026-43799 Kernel An app may be able to cause unexpected system termination YesYesYesYesYesYesYesNo
CVE-2026-43809 Kernel An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-43810 Kernel A remote user may be able to cause unexpected system termination or corrupt kernel memory YesYesYesYesYesYesYesNo
CVE-2026-43814 Kernel An app may be able to cause unexpected system termination YesYesNoNoYesYesNoNo
CVE-2026-43816 Kernel An app may be able to cause unexpected system termination YesYesNoNoYesYesYesNo
CVE-2026-43817 Kernel An app may be able to cause unexpected system termination YesYesNoNoYesYesYesNo
CVE-2026-43822 Kernel An app may be able to cause unexpected system termination YesYesYesYesYesYesYesNo
CVE-2026-64700 Kernel An app may be able to cause unexpected system termination YesYesYesYesYesYesYesNo
CVE-2026-64709 Kernel An app may be able to disclose kernel memory YesYesYesYesYesYesYesNo
CVE-2026-64720 Kernel An app may be able to cause unexpected system termination YesYesNoNoYesYesNoNo
CVE-2026-64721 Kernel An app may be able to access sensitive user data YesYesYesYesYesYesYesNo
CVE-2026-64723 Kernel An app may be able to access sensitive user data NoYesYesYesNoNoNoNo
CVE-2026-64727 Kernel An app may be able to cause unexpected system termination NoYesNoNoYesNoNoNo
CVE-2026-64729 Kernel An app may be able to cause unexpected system termination YesYesNoNoYesYesYesNo
CVE-2026-64735 Kernel A remote attacker may be able to bypass network filters YesYesYesYesYesYesYesNo
CVE-2026-64744 Kernel An app may be able to disclose kernel memory NoYesYesYesNoNoNoNo
CVE-2026-64749 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory YesYesYesNoNoNoYesNo
CVE-2026-64751 Kernel An app may be able to cause unexpected system termination or write kernel memory YesYesNoNoYesYesYesNo
CVE-2026-64775 Kernel An app may be able to cause unexpected system termination YesYesYesYesYesYesYesNo
CVE-2026-20672 LaunchServices An app may be able to access sensitive user data NoNoYesYesNoNoNoNo
CVE-2026-28983 LaunchServices A remote attacker may be able to cause a denial of service NoNoYesYesNoNoNoNo
CVE-2026-28900 libarchive A maliciously crafted ZIP archive may bypass Gatekeeper checks NoNoYesYesNoNoNoNo
CVE-2026-4424 libarchive Processing a maliciously crafted file may result in disclosure of process memory YesYesYesYesNoNoYesNo
CVE-2026-28973 libc A malicious app may be able to break out of its sandbox YesYesYesYesNoYesNoNo
CVE-2026-64739 Libnotify An attacker may be able to cause unexpected app termination YesYesYesYesYesYesYesNo
CVE-2026-43703 libxslt Processing maliciously crafted web content may lead to an unexpected process crash NoNoYesYesYesYesYesNo
CVE-2026-43706 libxslt Processing maliciously crafted web content may lead to an unexpected process crash NoNoYesYesYesYesYesNo
CVE-2026-43766 LoginWindow An attacker with physical access to a locked device may be able to view sensitive user information NoYesYesYesNoNoNoNo
CVE-2026-64743 Managed Configuration An app may be able to access sensitive user data YesYesNoNoYesYesYesNo
CVE-2026-64738 Maps A malicious app may be able to break out of its sandbox NoYesYesYesNoNoNoNo
CVE-2026-43653 mDNSResponder An attacker on the local network may be able to cause a denial-of-service NoNoYesNoNoNoNoNo
CVE-2026-43806 mDNSResponder A local attacker may be able to cause a denial of service NoYesNoNoNoNoNoNo
CVE-2026-64724 mDNSResponder An attacker on the local network may be able to cause a denial-of-service YesYesYesYesYesYesYesNo
CVE-2026-43723 MediaRemote An app may be able to gain root privileges YesYesYesYesYesYesYesNo
CVE-2026-28911 Metal A malicious app may be able to corrupt memory of a system process NoYesNoYesNoNoNoNo
CVE-2026-43807 MobileAccessoryUpdater A malicious accessory may be able to cause unexpected app termination NoNoYesYesYesYesYesNo
CVE-2026-43729 Model I/O Processing a maliciously crafted image may corrupt process memory YesYesYesNoYesNoYesNo
CVE-2026-43733 Model I/O Processing a maliciously crafted image may corrupt process memory YesYesYesNoNoNoNoNo
CVE-2026-64722 Model I/O Processing a 3D model may result in disclosure of process memory YesYesYesNoNoNoNoNo
CVE-2026-64768 Model I/O A remote attacker may cause an unexpected app termination YesYesYesYesYesNoYesNo
CVE-2026-64769 Model I/O A remote attacker may be able to cause unexpected application termination or heap corruption YesYesYesYesYesNoYesNo
CVE-2026-64770 Model I/O A remote attacker may be able to cause unexpected application termination or heap corruption YesYesYesYesYesNoYesNo
CVE-2026-64771 Model I/O A remote attacker may be able to cause unexpected application termination or heap corruption YesYesYesNoYesNoYesNo
CVE-2026-64772 Model I/O A remote attacker may be able to cause unexpected application termination or heap corruption YesYesYesNoYesNoYesNo
CVE-2026-64774 Model I/O A remote attacker may be able to cause unexpected application termination or heap corruption YesYesYesYesYesNoYesNo
CVE-2026-43771 Net-SNMP An app may be able to cause a denial-of-service NoYesYesYesNoNoNoNo
CVE-2026-43772 NetFSFramework An app may be able to break out of its sandbox NoYesYesYesNoNoNoNo
CVE-2026-28961 Network Extensions An attacker with physical access to a locked device may be able to view sensitive user information NoNoYesYesNoNoNoNo
CVE-2026-64711 NSColorPanel An app may be able to leak sensitive user information YesYesYesYesNoNoNoNo
CVE-2026-28912 PackageKit A user may be able to elevate privileges NoYesYesNoNoNoNoNo
CVE-2026-43765 PackageKit An app may be able to modify protected parts of the file system NoYesYesYesNoNoNoNo
CVE-2026-28896 ppp An attacker may be able to cause unexpected system termination or read kernel memory NoNoYesYesNoNoNoNo
CVE-2026-64731 Printing A malicious app may be able to break out of its sandbox NoYesYesNoNoNoNoNo
CVE-2026-43812 Pro Res An app may be able to cause unexpected system termination YesYesYesNoYesNoYesNo
CVE-2026-43694 quarantine An app may be able to cause unexpected system termination or write kernel memory NoYesYesYesNoNoNoNo
CVE-2026-39874 Remote Management A malicious app may be able to gain root privileges NoYesYesYesNoNoNoNo
CVE-2026-43792 Safari An app may be able to access sensitive user data NoYesNoNoNoNoNoYes
CVE-2026-64741 Sandbox Profiles An app may be able to read a persistent device identifier YesNoNoNoYesYesYesNo
CVE-2026-64763 SceneKit Processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution YesYesYesYesYesYesYesNo
CVE-2026-64764 SceneKit Processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution YesYesYesYesYesYesYesNo
CVE-2026-64765 SceneKit Processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution YesYesYesYesYesYesYesNo
CVE-2026-64766 SceneKit Processing a maliciously crafted file may lead to unexpected app termination or arbitrary code execution YesYesYesYesYesYesYesNo
CVE-2026-43665 Screen Sharing Server A local attacker may be able to determine the legacy VNC password configured for Screen Sharing NoNoYesYesNoNoNoNo
CVE-2026-43760 Screen Sharing Server An app may be able to access user-sensitive data NoYesNoYesNoNoNoNo
CVE-2026-43777 Screen Sharing Server A remote attacker may be able to cause a denial of service NoYesYesYesNoNoNoNo
CVE-2026-43779 Screen Sharing Server An app may be able to intercept network connections intended for another process NoYesYesYesNoNoNoNo
CVE-2026-43728 Security An attacker may be able to modify the state of the Keychain NoYesNoNoNoNoNoNo
CVE-2026-43755 SecurityAgent An app may be able to gain root privileges NoYesNoYesNoNoNoNo
CVE-2026-43800 Siri An app may be able to access sensitive user data YesYesNoNoYesYesNoNo
CVE-2026-64745 Siri A person with physical access to a locked device may be able to access contacts and photos NoYesYesNoNoNoNoNo
CVE-2026-39873 SMB Connecting to a malicious SMB server may lead to unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-64696 SMB A remote user may be able to cause unexpected system termination or corrupt kernel memory NoYesYesYesNoNoNoNo
CVE-2026-64704 SMB An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-43774 Spotlight An app may be able to access sensitive user data NoYesYesYesNoNoNoNo
CVE-2026-43770 StorageKit An app may be able to access sensitive user data NoYesYesYesYesNoNoNo
CVE-2026-43768 udf An app may be able to cause unexpected system termination NoYesYesYesNoNoNoNo
CVE-2026-43704 Web Extensions A malicious web extension may be able to cause an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-64699 WebDAV An app may be able to disclose kernel memory NoYesYesYesNoNoNoNo
CVE-2026-64703 WebDAV An app may be able to cause a denial-of-service NoYesYesYesNoNoNoNo
CVE-2026-39872 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43663 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43676 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash NoNoNoNoNoYesYesNo
CVE-2026-43699 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43700 WebKit Processing maliciously crafted web content may disclose sensitive user information NoNoNoNoYesYesYesNo
CVE-2026-43701 WebKit A malicious website may be able to process restricted web content outside the sandbox NoNoNoNoYesYesYesNo
CVE-2026-43705 WebKit Processing maliciously crafted web content may lead to memory corruption NoNoNoNoYesYesYesNo
CVE-2026-43707 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43708 WebKit A malicious website may exfiltrate data cross-origin NoNoNoNoYesYesYesNo
CVE-2026-43709 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43712 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43713 WebKit Visiting a website may leak sensitive data NoNoNoNoYesYesYesNo
CVE-2026-43715 WebKit Processing maliciously crafted web content may lead to memory corruption NoNoNoNoYesYesYesNo
CVE-2026-43725 WebKit A malicious website may be able to process restricted web content outside the sandbox NoNoNoNoYesYesYesNo
CVE-2026-43726 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43727 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash NoNoNoNoNoYesYesNo
CVE-2026-43731 WebKit Processing maliciously crafted web content may lead to memory corruption NoNoNoNoYesYesYesNo
CVE-2026-43732 WebKit Processing maliciously crafted web content may disclose sensitive user information NoNoNoNoYesYesYesNo
CVE-2026-43734 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43735 WebKit A malicious website may exfiltrate data cross-origin NoNoNoNoYesYesYesNo
CVE-2026-43740 WebKit Processing maliciously crafted web content may result in the disclosure of process memory YesNoNoNoYesYesYesYes
CVE-2026-43742 WebKit Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43745 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash NoNoNoNoYesYesYesNo
CVE-2026-43804 WebKit Visiting a website may lead to an app denial-of-service YesYesNoNoNoNoYesYes
CVE-2026-43821 WebKit An app may be able to read files outside of its sandbox YesYesNoNoYesYesYesYes
CVE-2026-64713 WebKit Websites may know if the user has visited a given link YesYesNoNoYesYesYesYes
CVE-2026-64728 WebKit Maliciously crafted web content may violate iframe sandboxing policy YesYesNoNoYesYesYesYes
CVE-2026-64730 WebKit Visiting a website that frames malicious content may lead to UI spoofing YesYesNoNoYesYesYesYes
CVE-2026-64757 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash YesYesNoNoNoYesYesYes
CVE-2026-64783 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash YesYesNoNoNoYesYesYes
CVE-2026-43720 WebKit Canvas Processing maliciously crafted web content may lead to an unexpected Safari crash NoNoNoNoYesYesYesNo
CVE-2026-64718 WebKit Canvas Processing maliciously crafted web content may lead to an unexpected Safari crash YesYesNoNoYesYesYesYes
CVE-2026-43721 WebKit Storage A malicious website may be able to silently hijack clipboard data NoNoNoNoYesYesYesNo
CVE-2026-28979 WebRTC Processing maliciously crafted web content may lead to an unexpected process crash NoNoNoNoYesYesYesNo
CVE-2026-43717 WebRTC Processing maliciously crafted web content may lead to an unexpected Safari crash NoNoNoNoYesYesNoNo
CVE-2026-43718 WebRTC Processing maliciously crafted web content may lead to an unexpected Safari crash NoNoNoNoYesYesYesNo
CVE-2026-64719 WebRTC Processing maliciously crafted web content may lead to an unexpected Safari crash YesYesNoNoYesYesYesYes
CVE-2026-43750 Wi-Fi An app may be able to execute arbitrary code out of its sandbox or with certain elevated privileges NoYesYesYesNoNoNoNo
CVE-2026-64726 Wi-Fi An attacker in physical proximity may be able to corrupt process memory YesYesNoNoYesYesYesNo
CVE-2026-64755 WorkoutKit An app may be able to access sensitive user data YesNoNoNoNoNoNoNo
CVE-2026-28932 xar An app may be able to cause a denial of service NoYesYesYesNoNoNoNo
CVE-2026-28914 zip A maliciously crafted ZIP archive may bypass Gatekeeper checks NoNoYesYesNoNoNoNo

We’ll continue these macOS updates if people find them useful. Stay tuned for the regularly schedule Patch Tuesday blog covering Adobe and Microsoft.

Pwn2Own Ireland 2026 – New Targets and Categories

If you just want to read the rules, you can find them here.


Pwn2Own Ireland returns for 2026, and it’s the third year for this event in the Emerald Isle. Despite the dreary Irish skies (and the threat of a random banshee), we had an amazing event, even if we did end up in a jail at the end. With that in mind, we’re excited to return to Cork this fall for yet another great Pwn2Own event. We’ll also be returning to some of the great pubs Ireland has to offer in the evenings and wrapping the event up at a special location (stay tuned for that announcement).

As for the contest itself, it will run from October 6-9, 2026. As always, we’ll have a random drawing to determine the schedule of attempts on the first day of the contest, and we will proceed from there. Registration closes at 5:00 p.m. Irish Standard Time on Oct 1st, 2026. There are no exceptions for late entries, so if you have questions, please contact us at pwn2own@trendmicro.com (note the address). We will be happy to address your issues or concerns directly.

Due to the overwhelming amount of registrations and last-minute entries for our Pwn2Own Berlin event, we’re changing who can enter the contest a bit to ensure it’s fair for all researchers. To enter, you must have received an aggregate bounty payment totaling at least $15,000 during their life-time participation in ZDI. This includes past Pwn2Own events and our regular bug bounty program. We recognize there may be some who haven’t participated in the past with great exploits to demonstrate, so we will also accept up to 10 new contestants at our discretion. We’re capping the number of entries to 80 this year. Once we have 80 qualifying entries, we will close registration. That means if you want to enter, it is in your best interest to contact us sooner rather than later. Please read the rules thoroughly to ensure you meet all the requirements.

Now on to this year’s target categories. We’ll have seven different categories for this year’s event:


-- Mobile Phones
-- Smart Home Devices
-- Wellness
-- Printers
-- Messaging
-- AI Infrastructure
-- AI Coding Agents

Let’s take a look at each category in more detail, starting with mobile phones.

The Target Phones

Back in Amsterdam where this contest originated, it was originally dubbed “Mobile Pwn2Own” and our focus was strictly on phones. Mobile handsets remain at the heart of this event, and some of the Samsung entries from last year were absolutely smashing. As always, these phones will be running the latest version of their respective operating systems with all available updates installed. Last year we also introduced the USB attack vector, but no one submitted an entry for it. We’ll see if that changes this year.

Otherwise, contestants must compromise the device by browsing to content in the default browser for the target under test or by communicating with the following short-distance protocols: near field communication (NFC), Wi-Fi, or Bluetooth. The awards for this category are:

Back to top

Smart Home Devices

As you might have noticed, we have eliminated most of the consumer-related devices from this year’s event. However, there are still a few “pro-sumer” devices that still could have an impact on enterprises, and the first of these categories are the devices that control other devices and services. An attempt in this category must be launched against the target’s exposed network services, RF attack surface, or exposed features from the contestant’s laptop within the contest network.

Back to top

Wellness Category

This is one of the new categories this year and our first foray into the world of healthcare devices. However, we don’t intend to make this too easy. Entries that require physically pressing any button on the target, or the use of any information, code or PIN printed on the device, are out of scope. Entries that require the contestant to be paired to the target prior to the start of the attempt are not in scope. An attempt in this category must be launched against the target’s exposed network services, RF attack surface, or exposed features from the contestant’s laptop within the contest network.

Back to top

Rage Against the Printers

Printers have long been the source of jokes and memes, but they are also an often overlooked attack surface in your office. The printer category always produces some interesting results, often by playing music it shouldn’t or the occasional Rick Roll. We’ve reduced the number of targets in this category this year, but we still expect to see some interesting exploits in these oft unheralded targets.

Back to top

The Messaging Category

We introduced WhatsApp as a target last year and came close to seeing a functioning exploit. Sadly, that didn’t happen. However, WhatsApp is used by more than three billion people globally, and some of the messages transmitted can be quite sensitive. That’s why we are bringing it back and hoping for some better results. We know the bugs are out there. We’re just hoping the right researcher decides to show us an exploit that leads to code execution. All of the target handset will be available as clients. Here’s the full prize list for Messaging category:

Back to top

AI Infrastructure Category

We introduced these targets at Pwn2Own Berlin, and we saw such…uh…enthusiasm from the community that we decided to immediately bring them back for our Ireland event. An attempt in this category must be launched from the contestant’s laptop. Here’s a look at the targets and awards in the AI Infrastructure category:

Back to top

AI Coding Agent Category

Let’s face it. At some point or another, we’ve probably all vibe coded something. There’s no shame in that, but how secure are the tools we use for vibe coding? Well, let’s take the most popular choices and find out. A successful entry must interact with a contestant-controlled resource (e.g. web page, repository, media file) to exploit a vulnerability within the coding agent. The attack vector of the entry must be a common coding agent use case. There are few things out of scope here as well. UI spoofing or misrepresentation unrelated to permission prompts, model jailbreaks or prompt outputs that do not cross security boundaries, and vulnerabilities that require unsafe or permission-less modes are just a few of the things not allowed. As this is a recently updated category, please read the rules carefully to ensure your entry qualifies. Here’s a look at the targets and awards in the AI Coding Agent category:

Back to top

Master of Pwn

No Pwn2Own contest would be complete without crowning a Master of Pwn, which signifies the overall winner of the competition. Earning the title results in a slick trophy, a different sort of wearable, and brings with it an additional 65,000 ZDI reward points (instant Platinum status in 2027).

For those not familiar with how it works, points are accumulated for each successful attempt. While only the first demonstration in a category wins the full cash award, each successful entry claims the full number of Master of Pwn points. Since the order of attempts is determined by a random draw, those who receive later slots can still claim the Master of Pwn title – even if they earn a lower cash payout. As with previous contests, there are penalties for withdrawing from an attempt once you register for it. If the contestant decides to remove an Add-on Bonus during their attempt, the Master of Pwn points for that Add-on Bonus will be deducted from the final point total for that attempt. For example, someone registers for the Apple iPhone 15 with the Kernel Bonus Add-on. During the attempt, the contestant drops the Kernel Bonus Add-on but completes the attempt. The final point total will be 20 Master of Pwn points.

The Complete Details

The full set of rules for Pwn2Own Ireland 2026 can be found here. They may be changed at any time without notice. We highly encourage potential entrants to read the rules thoroughly and completely should they choose to participate. We also encourage contestants to read this blog covering what to expect when participating in Pwn2Own.

Registration is required to ensure we have sufficient resources on hand at the event. Please contact ZDI at pwn2own@trendmicro.com to begin the registration process. (Email only, please; queries via social media, blog post, or other means will not be acknowledged or answered.) If we receive more than one registration for any category, we’ll hold a random drawing to determine the contest order. Registration closes at 5:00 p.m. Irish Standard Time on Oct 1st, 2025.

The Results

We’ll be blogging and tweeting results in real-time throughout the competition. Be sure to keep an eye on the blog for the latest information. Follow us on Twitter at @thezdi and @trendaisecurity, and keep an eye on the #P2OIreland hashtag for continuing coverage.

We look forward to seeing everyone in Cork, and we look forward to seeing what new exploits and attack techniques they bring with them.


©2026 Trend Micro Incorporated. All rights reserved. PWN2OWN, ZERO DAY INITIATIVE, ZDI, TrendAI, and Trend Micro are trademarks or registered trademarks of Trend Micro Incorporated. All other trademarks and trade names are the property of their respective owners.

The July 2026 Security Update Review

Well folks. Here we are. The bug apocalypse has fully descended upon us. I’ll do my best to sort this out in some way meaningful, but this month’s release shows us the nay-sayers were right, and I’ve got to hand it to the nay-sayers here. Excellent call. Take an extended break from your regularly scheduled activities as we let’s take a look at the latest security patches from Adobe and Microsoft. If you’d rather watch the full video recap covering the entire release, you can check it out here:

Adobe Patches for July 2026

Adobe has now moved to a bimonthly release schedule, which means they will be releasing patches on the second and fourth Tuesdays of the month. I’ll continue to cover the second Tuesday release here and update this blog should the fourth Tuesday release contain anything significant. I think this is a smart way to break up a monster release into something a bit more manageable. Apple has said they are taking a similar approach. We’ll see if other vendors follow their lead.

For the first part of the July release, Adobe released 12 bulletins addressing 88 unique CVEs in Adobe ColdFusion, Commerce, After Effects, Animate, Audition, Bridge, Creative Cloud Desktop Application, Experience Manager, Illustrator, Media Encoder, Premiere Pro, and the Content Credentials SDK.

Here’s this month’s overview table:

Bulletin ID Product CVE Count Highest Severity Highest CVSS Exploited Deployment Priority
APSB26-82 Adobe ColdFusion 13 Critical 9.9 No 1
APSB26-73 Adobe Commerce 13 Critical 9.6 No 2
APSB26-78 Adobe After Effects 3 Critical 7.8 No 3
APSB26-83 Adobe Animate 6 Critical 8.6 No 3
APSB26-71 Adobe Audition 6 Critical 7.8 No 3
APSB26-81 Adobe Bridge 6 Critical 7.8 No 3
APSB26-77 Adobe Creative Cloud Desktop Application 2 Critical 8.1 No 3
APSB26-74 Adobe Experience Manager 13 Critical 9.6 No 3
APSB26-79 Adobe Illustrator 5 Critical 9.3 No 3
APSB26-72 Adobe Media Encoder 5 Critical 7.8 No 3
APSB26-76 Adobe Premiere Pro 4 Critical 7.8 No 3
APSB26-80 Content Credentials SDK 12 Critical 8.2 No 3
TOTAL 12 bulletins 88

While nothing is under active exploit, I would prioritize the Cold Fusion and Commerce patches first. The patch for Cold Fusion even clocks in with a CVSS 9.9 bug. Beyond that, most of these updates are pretty straightforward. If you’re using these products, patch them. However, you can use you regular patch cadence here.

Microsoft Patches for July 2026

Here it is. The Mother of All Releases. To call this record-breaking is an understatement. How to count this mess is anyone’s guess, but I see new Microsoft 621 CVEs for the month of July. Some of these are in online services where no user action is required. They also list about 480 bugs in Chromium and Microsoft Edge (Chromium-based) that I won’t cover here. Here’s how I put this in context. I looked at the last 20 years of Microsoft releases. The CVE count year-to-date exceeds all other years’ totals.

The products covered this month are also astonishing. There are patches for Windows and Windows components, Office and Office Components, Microsoft Edge (Chromium-based), Azure, .NET and Visual Studio, Github Copilot, Defender, Exchange Server, Hyper-V, Ages of Empire II, and Minecraft Server (really!). That phrase “Windows components” does some pretty heavy lifting here, too, as just about everything you’ve ever heard of is getting patched. All told, there are 63 rated Critical, six rated Moderate, one rated Low, with the rest rated Important in severity. Eight of these bugs were submitted through the ZDI program (more on that later). Two CVEs are listed as under active exploit while one other is listed as publicly known.

So how do we eat this elephant? One byte at a time (pun intended). Let’s start by looking a closer look at some of the more interesting updates for this month, starting with the bugs being exploited in the wild.

-    CVE-2026-56155 - Active Directory Federation Services Elevation of Privilege Vulnerability
This is one of several AD FS being patched this month, but it’s the only one being actively exploited. It stems from insufficient access-control granularity and does require local access and low privileges to start, but AD FS is exactly the kind of identity infrastructure attackers love to pivot through once they're in. It can also be paired with an RCE as we often see in ransomware. Test and deploy this patch quickly.

-    CVE-2026-56164 - Microsoft SharePoint Server Elevation of Privilege Vulnerability
The other bug being exploited in the wild this month is a modest CVSS 5.3 – but it shows why Moderate severity bugs still matter. It's a missing-authentication flaw, meaning an unauthenticated attacker can hit it over the network with no user interaction required. When something this reachable is being actively abused, patch it now and worry about the score later.

-    CVE-2026-57092 - Microsoft Windows VMSwitch Elevation of Privilege Vulnerability
This patch rates the highest CVSS score for the month: a solid 9.9. It’s a use-after-free that lets a low-privileged attacker escalate to full host compromise across a VM boundary. We saw something like this demonstrated at Pwn2Own Berlin on ESXi, but it clearly isn’t alone. If you’re using VMSwitch in your Hyper-V deployments (and you likely are), test and deploy this one quickly.

-    CVE-2026-50522/58644 - Microsoft SharePoint Remote Code Execution Vulnerability
This matching pair of CVSS 9.8 bugs results from the deserialization-of-untrusted-data and are reachable without authentication or user interaction. CVE-2026-50522 was demonstrated during Pwn2Own Berlin, so it’s odd to see Microsoft list it as “Exploit Maturity Unknown” since we literally handed them a working exploit. Just another reason to do your own risk assessment and not rely 100% on the vendor. If you have any Internet accessible SharePoint servers, test and deploy this patch quickly.

-    CVE-2026-56190 - Remote Desktop Protocol Remote Code Execution Vulnerability
This patch covers an unauthenticated, network-reachable, no user interaction required bug. The root cause is a classic one: use of uninitialized resource (CWE-908), meaning specially crafted RDP traffic can interact with memory that was never properly initialized, letting an attacker corrupt memory and potentially steer code execution. RDP Servers are a common target, so audit your systems to see which are internet accessible and start from there.

-    CVE-2026-55008 - Microsoft Exchange Server Spoofing Vulnerability
Ignore the title here and treat this like the XSS bug it is. The vulnerability is listed as a CVSS 9.6 since it’s a stored cross-site scripting flaw in Outlook Web Access, with a scope-changed impact that lets it break out of the web app context entirely. An attacker sends a specially crafted email, and if the victim simply opens it in OWA, arbitrary JavaScript executes in their browser session — no attachment needed, no macro warning, just viewing the message does it. If you’re using OWA, test and deploy this one quickly.

-    CVE-2026-50518 - Windows DHCP Server Remote Code Execution Vulnerability
There are a couple of these DHCP RCE patches in this release, but the other has caveats while this one does not. Both are heap-based buffer overflows scoring CVSS 9.8, both unauthenticated and network-reachable. If you're running DHCP Server role on anything Internet-adjacent (you're not, right?), these move to the top of the list.

-    CVE-2026-56188 - Windows Server Network driver Remote Code Execution Vulnerability
Another Critical-rated bug, this one is caused by a race condition. It’s always fun to see a TOCTOU bug rated this high, since race conditions are notoriously finicky to exploit reliably. While it may prove tricky to exploit, this bug could allow an attacker to execute privileged code over the network without user interaction. Don’t let the race condition lull you to sleep on a wormable bug.

-    CVE-2026-55010 - Minecraft Bedrock Dedicated Server Remote Code Execution Vulnerability
File this in the “why not” category. This bug is a heap-based buffer overflow in Minecraft Bedrock Dedicated Server, also CVSS 9.8 and also unauthenticated RCE. Yes, your kid’s Minecraft server (it is your kid’s server, right?) is exposed to the same class of bug as your DHCP infrastructure. Patch it anyway.

Here’s the full list of CVEs released by Microsoft for July 2026:

CVE Title Severity CVSS Public Exploited Type
CVE-2026-56155 Active Directory Federation Services Elevation of Privilege Vulnerability Important 7.8 No Yes EoP
CVE-2026-56164 Microsoft SharePoint Server Elevation of Privilege Vulnerability Moderate 5.3 No Yes EoP
CVE-2026-50661 Windows BitLocker Security Feature Bypass Vulnerability Important 6.1 Yes No SFB
CVE-2026-54121 Active Directory Certificate Services Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-45499 ** Azure OpenAI Elevation of Privilege Vulnerability Critical 9.9 No No EoP
CVE-2026-48564 DHCP Server Service Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-50370 DHCP Server Service Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-56159 DHCP Server Service Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-50382 DirectX Graphics Kernel Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-41106 ** Microsoft 365 Copilot Elevation of Privilege Vulnerability Critical 9.3 No No EoP
CVE-2026-26145 ** Microsoft Azure Synapse Elevation of Privilege Vulnerability Critical 4.8 No No EoP
CVE-2026-48561 Microsoft Copilot Remote Code Execution Vulnerability Critical 9.6 No No RCE
CVE-2026-55011 Microsoft Defender Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55012 Microsoft Defender Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55944 Microsoft Dynamics NAV and Microsoft Dynamics 365 Business Central (On Premises) Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-57100 ** Microsoft Entra Provisioning Service Elevation of Privilege Vulnerability Critical 9.9 No No EoP
CVE-2026-55041 Microsoft Excel Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-54998 ** Microsoft Exchange Online Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-55008 Microsoft Exchange Server Spoofing Vulnerability Critical 9.6 No No Spoofing
CVE-2026-54992 Microsoft Message Queuing Queue Manager Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-50314 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-50467 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55018 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55022 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55045 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-55049 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55129 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55056 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55140 Microsoft Office Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55043 Microsoft PowerPoint Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55123 Microsoft PowerPoint Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55120 Microsoft PowerPoint Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-50522 Microsoft SharePoint Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-58644 Microsoft SharePoint Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-55040 Microsoft SharePoint Server Security Feature Bypass Vulnerability Critical 9.1 No No SFB
CVE-2026-54117 Microsoft SQL Server Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-54118 Microsoft SQL Server Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-50655 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-56189 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-57090 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-57094 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-57087 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-57092 Microsoft Windows VMSwitch Elevation of Privilege Vulnerability Critical 9.9 No No EoP
CVE-2026-55033 Microsoft Word Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55127 Microsoft Word Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55132 Microsoft Word Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-55010 Minecraft Bedrock Dedicated Server Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-50474 Remote Desktop Client Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-49164 Windows Active Directory Domain Services Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-54128 Windows DHCP Client Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-50518 Windows DHCP Server Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-49796 Windows GDI+ Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-50380 Windows GDI+ Remote Code Execution Vulnerability Critical 9.6 No No RCE
CVE-2026-54127 Windows Hyper-V Elevation of Privilege Vulnerability Critical 7.4 No No EoP
CVE-2026-50680 Windows Hyper-V Elevation of Privilege Vulnerability Critical 8.2 No No EoP
CVE-2026-50327 Windows Media Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-58542 Windows Media Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-58608 Windows Print Spooler Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-54982 Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-54995 Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-42982 Windows Secure Kernel Mode Elevation of Privilege Vulnerability Critical 7.8 No No EoP
CVE-2026-50392 Windows Secure Kernel Mode Elevation of Privilege Vulnerability Critical 7 No No EoP
CVE-2026-50694 Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-56188 Windows Server Network driver Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-50444 Windows Server Update Service (WSUS) Elevation of Privilege Vulnerability Critical 8.8 No No EoP
CVE-2026-54999 Windows TCP/IP Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-47302 .NET Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50525 .NET Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50651 .NET Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-57108 .NET Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50524 .NET Framework Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50527 .NET Framework Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50648 .NET Framework Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50650 .NET Framework Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50646 .NET Framework Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50649 .NET Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-47304 .NET Security Feature Bypass Vulnerability Important 8.1 No No SFB
CVE-2026-50528 .NET Security Feature Bypass Vulnerability Important 8.2 No No SFB
CVE-2026-50659 .NET Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-50526 .NET Tampering Vulnerability Important 7 No No Tampering
CVE-2026-50682 Active Directory Denial of Service Vulnerability Important 7.1 No No DoS
CVE-2026-55001 Active Directory Domain Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50647 Active Directory Federation Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50684 Active Directory Federation Server Spoofing Vulnerability Important 4.8 No No Spoofing
CVE-2026-56170 ASP.NET Core Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-47300 ASP.NET Core Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-47303 ASP.NET Core Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50652 Azure Active Directory Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50653 Azure Active Directory Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-57969 Azure CycleCloud Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-58279 Azure CycleCloud Elevation of Privilege Vulnerability Important 6.5 No No EoP
CVE-2026-47632 Azure Monitor Agent Metrics Extension Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50338 Azure Spring Apps Elevation of Privilege Vulnerability Important 8.2 No No EoP
CVE-2026-50488 Clipboard User Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50491 Code Integrity DLL (ci.dll) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50381 Composite Image File System driver (cimfs.sys) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50427 Content Delivery Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50692 Desktop Window Manager Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-58633 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58634 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50296 DirectX Graphics Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50375 DirectX Graphics Kernel Elevation of Privilege Vulnerability Important 6.3 No No EoP
CVE-2026-50353 DirectX Graphics Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50493 DirectX Graphics Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56643 DirectX Graphics Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56644 DirectX Graphics Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58629 DirectX Graphics Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-49174 DNS Client Tampering Vulnerability Important 6.1 No No Tampering
CVE-2026-50495 DNS Client Tampering Vulnerability Important 6.1 No No Tampering
CVE-2026-57088 Extensible Storage Engine (ESENT) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50663 Game: Age of Empires II: Definitive Edition Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-47282 GitHub Copilot and Visual Studio Code Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-41109 GitHub Copilot and Visual Studio Code Security Feature Bypass Vulnerability Important 8.8 No No SFB
CVE-2026-50510 GitHub Copilot Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-49787 HTTP.sys Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50420 HTTP.sys Information Disclosure Vulnerability Important 6.2 No No Info
CVE-2026-49788 HTTP/2 Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50696 Internet Key Exchange (IKE) Protocol Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-58617 M365 Copilot for iOS Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-58595 Microsoft Bing App for IOS Spoofing Vulnerability Important 8.1 No No Spoofing
CVE-2026-49162 Microsoft Brokering File System Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50305 Microsoft Brokering File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50361 Microsoft Brokering File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50466 Microsoft Brokering File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50458 Microsoft Brokering File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50658 Microsoft Defender for Endpoint for Mac Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-56178 Microsoft Defender for Endpoint for Mac Elevation of Privilege Vulnerability Important 5.5 No No EoP
CVE-2026-50657 Microsoft Defender for Endpoint for Mac Information Disclosure Vulnerability Important 4.7 No No Info
CVE-2026-50329 Microsoft DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58541 Microsoft DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58596 Microsoft Edge (Chromium-based) Elevation of Privilege Vulnerability Important 8.3 No No EoP
CVE-2026-57991 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability Important 7.4 No No Info
CVE-2026-58291 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability Important 6.1 No No Info
CVE-2026-57981 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-57984 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-57985 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.6 No No RCE
CVE-2026-57986 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-57988 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.1 No No RCE
CVE-2026-57992 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-58276 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-56645 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-57974 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-57975 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-58281 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.3 No No RCE
CVE-2026-58284 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.3 No No RCE
CVE-2026-58285 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.3 No No RCE
CVE-2026-58287 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.3 No No RCE
CVE-2026-58288 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.3 No No RCE
CVE-2026-58289 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 9 No No RCE
CVE-2026-58290 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-58292 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-58293 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-58294 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-57983 Microsoft Edge (Chromium-based) Security Feature Bypass Vulnerability Important 8.7 No No SFB
CVE-2026-58295 Microsoft Edge (Chromium-based) Security Feature Bypass Vulnerability Important 8.3 No No SFB
CVE-2026-58525 Microsoft Edge (Chromium-based) Security Feature Bypass Vulnerability Important 8.2 No No SFB
CVE-2026-57987 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-58278 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 5.4 No No Spoofing
CVE-2026-56646 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-57977 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 7.1 No No Spoofing
CVE-2026-57993 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 7.4 No No Spoofing
CVE-2026-58282 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 8.1 No No Spoofing
CVE-2026-58283 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 8.1 No No Spoofing
CVE-2026-58286 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 8.1 No No Spoofing
CVE-2026-58298 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 7.2 No No Spoofing
CVE-2026-58524 Microsoft Edge (Chromium-based) Spoofing Vulnerability Important 5.4 No No Spoofing
CVE-2026-58296 Microsoft Edge for Android Information Disclosure Vulnerability Important 7.1 No No Info
CVE-2026-58297 Microsoft Edge for Android Information Disclosure Vulnerability Important 7.1 No No Info
CVE-2026-58300 Microsoft Edge for Android Information Disclosure Vulnerability Important 6.2 No No Info
CVE-2026-58522 Microsoft Edge for Android Information Disclosure Vulnerability Important 6.8 No No Info
CVE-2026-58299 Microsoft Edge for Android Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-58523 Microsoft Edge for Android Security Feature Bypass Vulnerability Important 6.5 No No SFB
CVE-2026-50678 Microsoft Excel Information Disclosure Vulnerability Important 6.6 No No Info
CVE-2026-54988 Microsoft Excel Information Disclosure Vulnerability Important 6.1 No No Info
CVE-2026-48580 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50408 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55046 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55138 Microsoft Excel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55054 Microsoft Excel Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-55122 Microsoft Excel Information Disclosure Vulnerability Important 7.1 No No Info
CVE-2026-55898 Microsoft Excel Information Disclosure Vulnerability Important 6.1 No No Info
CVE-2026-50675 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55899 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55948 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-58618 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-47642 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55024 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55025 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55031 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55048 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55029 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55039 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55136 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55141 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55036 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55044 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55037 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55058 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55137 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55053 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55131 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-54131 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55947 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55949 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-56156 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55006 Microsoft Exchange Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-55009 Microsoft Exchange Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-55005 Microsoft Exchange Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-56642 Microsoft Fabric Data Warehouse Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-50343 Microsoft Install Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50439 Microsoft Message Queuing Queue Manager Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-58537 Microsoft NAT Helper Components (ipnathlp.dll) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56193 Microsoft Office Information Disclosure Vulnerability Important 7.1 No No Info
CVE-2026-55023 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55026 Microsoft Office Information Disclosure Vulnerability Important 6.2 No No Info
CVE-2026-55027 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55028 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55047 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55035 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55057 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55121 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55042 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55139 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50665 Microsoft Office Information Disclosure Vulnerability Important 7.8 No No Info
CVE-2026-56192 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-56195 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-47290 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50301 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55017 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55125 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55133 Microsoft OneNote Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-58636 Microsoft PC Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50438 Microsoft PC Manager Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-58647 Microsoft PowerBI Report Server Spoofing Vulnerability Important 8 No No Spoofing
CVE-2026-55052 Microsoft SharePoint Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-58277 Microsoft SharePoint Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-55051 Microsoft SharePoint Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-54108 Microsoft SharePoint Server Spoofing Vulnerability Important 6.5 No No Spoofing
CVE-2026-55016 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-55019 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-55020 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-55021 Microsoft SharePoint Server Spoofing Vulnerability Important 7.3 No No Spoofing
CVE-2026-55030 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-55034 Microsoft SharePoint Server Spoofing Vulnerability Important 7.3 No No Spoofing
CVE-2026-55126 Microsoft SharePoint Server Spoofing Vulnerability Important 7.3 No No Spoofing
CVE-2026-55135 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-56157 Microsoft SharePoint Server Spoofing Vulnerability Important 5.4 No No Spoofing
CVE-2026-47296 Microsoft SQL Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-55002 Microsoft SQL Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-47295 Microsoft SQL Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50468 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-54116 Microsoft SQL Server Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-42900 Microsoft Windows App Store Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-49784 Microsoft Windows App Store Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50356 Microsoft Windows App Store Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-49165 Microsoft Windows App Store Information Disclosure Vulnerability Important 7.1 No No Info
CVE-2026-54993 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-58610 Microsoft Windows Media Foundation Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55050 Microsoft Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55124 Microsoft Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55142 Microsoft Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-55032 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55055 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55038 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55134 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55128 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-55130 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50359 Microsoft XML Core Services Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-57097 Microsoft XML Security Feature Bypass Vulnerability Important 6.4 No No SFB
CVE-2026-50346 Netlogon RPC Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50402 NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50506 OData for ASP.NET and ASP.NET Core Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-45646 OData for ASP.NET and ASP.NET Core Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-54989 Quality Windows Audio/Video Experience (QWAVE) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50365 Remote Access Management service/API (RPC server) Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-54990 Remote Desktop Client Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-58594 Remote Desktop Client Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-56190 Remote Desktop Protocol Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-49783 Secure Boot Security Feature Bypass Vulnerability Important 7.8 No No SFB
CVE-2026-42990 SQL Server ODBC driver Elevation of Privilege Vulnerability Important 9.8 No No EoP
CVE-2026-49168 Storage Spaces Direct Elevation of Privilege Vulnerability Important 6.2 No No EoP
CVE-2026-48581 Surface Broker SDMA Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49180 Universal Plug and Play (upnp.dll) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50455 Universal Plug and Play (upnp.dll) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-54111 Universal Print Management Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-58543 Universal Print Management Service Elevation of Privilege Vulnerability Important 6.3 No No EoP
CVE-2026-58601 Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability Important 7.8 No No EoP
CVE-2026-50520 Visual Studio Code Remote Code Execution Vulnerability Important 8.4 No No RCE
CVE-2026-45496 Visual Studio Code Security Feature Bypass Vulnerability Important 5.5 No No SFB
CVE-2026-57101 Visual Studio Code Security Feature Bypass Vulnerability Important 7.1 No No SFB
CVE-2026-57102 Visual Studio Code Security Feature Bypass Vulnerability Important 8.8 No No SFB
CVE-2026-47305 Visual Studio Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-49805 Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50297 Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50325 Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50489 Win32k Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-57095 Win32k Elevation of Privilege Vulnerability Important 6.2 No No EoP
CVE-2026-50416 Win32k Information Disclosure Vulnerability Important 3.3 No No Info
CVE-2026-56184 Win32k Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50432 Window Virtual Filtering Platform (VFP) Denial of Service Vulnerability Important 5.3 No No DoS
CVE-2026-54119 Windows Active Directory Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-57976 Windows Active Directory Domain Services Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-50366 Windows Active Directory Domain Services Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-49178 Windows Active Directory Domain Services Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-58529 Windows Active Directory Federation Services (ADFS) Information Disclosure Vulnerability Important 7.1 No No Info
CVE-2026-54983 Windows Active Directory Federation Services Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50695 Windows Active Directory Federation Services Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50304 Windows Active Directory Federation Services Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50368 Windows Active Directory Federation Services Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50324 Windows Active Directory Federation Services Denial of Service Vulnerability Important 5.9 No No DoS
CVE-2026-50355 Windows Active Directory Federation Services Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50411 Windows Active Directory Federation Services Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-58631 Windows Admin Center (WAC) Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-56196 Windows Admin Center (WAC) Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-56197 Windows Admin Center (WAC) Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-56169 Windows Admin Center Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-57107 Windows Admin Center Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56185 Windows Admin Center Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-50312 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 4.7 No No EoP
CVE-2026-50462 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-57093 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-34346 Windows Ancillary Function Driver for WinSock Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-48572 Windows App Package Installer Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-48571 Windows App Package Installer Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50400 Windows App Package Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50331 Windows Application Model Core API Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49803 Windows AppX Deployment Extensions Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50351 Windows Audio Compression Manager (ACM) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50440 Windows Audio Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34328 Windows Audio Service Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50406 Windows Backup Engine Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50364 Windows Backup Service Elevation of Privilege Vulnerability Important 7.3 No No EoP
CVE-2026-42975 Windows Bluetooth Port Driver Remote Code Execution Important 8 No No RCE
CVE-2026-58538 Windows Bluetooth Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58638 Windows Boot Loader Security Feature Bypass Vulnerability Important 6 No No SFB
CVE-2026-58637 Windows Client-Side Caching Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50384 Windows Clip Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-49183 Windows Clipboard Server Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50689 Windows Clipboard Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50374 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 6.3 No No EoP
CVE-2026-58536 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58613 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50401 Windows Cloud Files Mini Filter Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50697 Windows Common Log File System Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50667 Windows Common Log File System Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50421 Windows Connected User Experiences and Telemetry Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50428 Windows Container Isolation FS Filter Driver (unionfs.sys) Information Disclosure Vulnerability Important 7.1 No No Info
CVE-2026-50352 Windows Cryptographic Services Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50302 Windows Cryptographic Services Security Feature Bypass Vulnerability Important 4.2 No No SFB
CVE-2026-55144 Windows Cryptography API: Next Generation (CNG) Tampering Vulnerability Important 7.1 No No Tampering
CVE-2026-50347 Windows Data.dll Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-49181 Windows DHCP Client Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-50683 Windows DHCP Client Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-58627 Windows DHCP Server Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50685 Windows DHCP Server Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-49807 Windows DirectX Information Disclosure Vulnerability Important 6.2 No No Info
CVE-2026-49175 Windows DNS Client Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50487 Windows DNS Client Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-50465 Windows DNS Client Tampering Vulnerability Important 7.1 No No Tampering
CVE-2026-49169 Windows DNS Server Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-50426 Windows DNS Server Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-50424 Windows Domain Controller Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-50300 Windows DWM Core Library Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50437 Windows DWM Core Library Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-34348 Windows Event Logging Service Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-50502 Windows Event Logging Service Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-33842 Windows File Explorer Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-40422 Windows File Explorer Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-41087 Windows File Explorer Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50473 Windows File Explorer Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50442 Windows File Explorer Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50389 Windows File Explorer Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50456 Windows File Explorer Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-57084 Windows File Explorer Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-57091 Windows File History Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50405 Windows Filtering Platform Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49172 Windows FTP Service Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-50387 Windows GDI Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-54122 Windows GDI+ Remote Code Execution Vulnerability Important 8.4 No No RCE
CVE-2026-50483 Windows Graphics Component Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-58609 Windows Graphics Component Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50391 Windows Group Policy Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50310 Windows Human Interface Device Information Disclosure Vulnerability Important 4.7 No No Info
CVE-2026-50485 Windows Hyper-V Denial of Service Vulnerability Important 4.5 No No DoS
CVE-2026-54129 Windows Hyper-V Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50315 Windows Image Acquisition Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58534 Windows Input Method Editor (IME) Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50490 Windows Installer Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-58540 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50425 Windows Internal System User Profile Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50293 Windows Internal Task Bar Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49167 Windows Kernel Elevation of Privilege Vulnerability Important 4.7 No No EoP
CVE-2026-49173 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-54132 Windows Kernel Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-49795 Windows Kernel Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-49798 Windows Kernel Elevation of Privilege Vulnerability Important 9.3 No No EoP
CVE-2026-49808 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50354 Windows Kernel Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-50332 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50377 Windows Kernel Elevation of Privilege Vulnerability Important 5.5 No No EoP
CVE-2026-50390 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50423 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50397 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50436 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50399 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50459 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50477 Windows Kernel Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50478 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50484 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50673 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58532 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50294 Windows Kernel Information Disclosure Vulnerability Important 6.2 No No Info
CVE-2026-50316 Windows Kernel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50419 Windows Kernel Information Disclosure Vulnerability Important 3.3 No No Info
CVE-2026-50463 Windows Kernel Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-50475 Windows Kernel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50429 Windows Kernel Information Disclosure Vulnerability Important 8.2 No No Info
CVE-2026-58614 Windows Kernel Security Feature Bypass Vulnerability Important 5.5 No No SFB
CVE-2026-58545 Windows Kernel Security Feature Bypass Vulnerability Important 5.5 No No SFB
CVE-2026-58602 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50393 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50396 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50378 Windows Key Guard Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50303 Windows Key Guard Security Feature Bypass Vulnerability Important 5.5 No No SFB
CVE-2026-40378 Windows Local Security Authority Subsystem Service (LSASS) Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-49799 Windows Local Security Authority Subsystem Service (LSASS) Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-50371 Windows LUA File Virtualization Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-58544 Windows Management Services Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50404 Windows Media Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50358 Windows Media Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50336 Windows Media Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50398 Windows Media Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50414 Windows Media Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-50379 Windows Media Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-50433 Windows Media Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50676 Windows Media Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50677 Windows Media Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34349 Windows Media Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50394 Windows Media Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50415 Windows Media Information Disclosure Vulnerability Important 5.3 No No Info
CVE-2026-57083 Windows Media Photo Codec Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-54115 Windows Message Queuing (MSMQ) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50447 Windows Message Queuing Service (MSMQ) Remote Code Execution Vulnerability Important 9.8 No No RCE
CVE-2026-50505 Windows Message Queuing Service (MSMQ) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-50342 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 8.8 No No EoP
CVE-2026-56183 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 7 No No EoP
CVE-2026-56187 Windows MIDI Service Module Elevation of Privileges Vulnerability Important 7 No No EoP
CVE-2026-58635 Windows Narrator Braille Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50500 Windows Netlogon Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-50476 Windows Network Connections Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50450 Windows Network Connections Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56650 Windows Network File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56649 Windows Network File System Remote Code Execution Vulnerability Important 5.9 No No RCE
CVE-2026-50470 Windows Network Policy Server SNMP Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-50496 Windows Network Policy Server SNMP Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-56194 Windows NFS Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-56648 Windows NFS Server Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-50337 Windows Notification Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49789 Windows NTFS Elevation of Privilege Vulnerability Important 7.3 No No EoP
CVE-2026-50412 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50422 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50672 Windows NTFS Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-56175 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56182 Windows NTFS Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50341 Windows NTFS Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-58640 Windows NTFS Remote Code Execution Vulnerability Important 7.3 No No RCE
CVE-2026-49184 Windows NTFS Remote Code Execution Vulnerability Important 8.4 No No RCE
CVE-2026-49797 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50308 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50386 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50309 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50313 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50388 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50448 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50471 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50461 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50417 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50482 Windows NTFS Remote Code Execution Vulnerability Important 7.3 No No RCE
CVE-2026-50494 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50344 Windows OLE Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50686 Windows OLE Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-50335 Windows Operating Systems Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50317 Windows Operating Systems Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-54987 Windows Overlay Filter Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50435 Windows Overlay Filter Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50409 Windows Overlay Filter Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-40400 Windows PowerShell Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-49166 Windows Print Configuration Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-55004 Windows Print Configuration Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50499 Windows Print Spooler Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50383 Windows Print Spooler Information Disclosure Vulnerability Important 6.1 No No Info
CVE-2026-57085 Windows Print Spooler Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50469 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50434 Windows Push Notification Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50339 Windows Push Notification Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50430 Windows Push Notification Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50334 Windows Push Notification Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-44800 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50363 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50431 Windows Quality of Service (QoS) Packet Scheduler Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50372 Windows Redirected Drive Buffering System Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50666 Windows Remote Access Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-56647 Windows Remote Access Service Infrastructure Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50330 Windows Remote Desktop Client Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-50376 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-50504 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-58533 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-58535 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-58546 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-58539 Windows Remote Desktop Client Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-55003 Windows Remote Desktop Protocol (RDP) Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-57979 Windows Remote Desktop Protocol (RDP) Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-50445 Windows Remote Desktop Protocol (RDP) Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-50497 Windows Remote Desktop Protocol (RDP) Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-54126 Windows Remote Desktop Protocol (RDP) Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-57982 Windows Remote Desktop Protocol (RDP) Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-50369 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-58626 Windows Remote Desktop Services Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-55014 Windows Remote Help Defense Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50318 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50407 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50357 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50441 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50668 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-54109 Windows Resilient File System (ReFS) Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-49792 Windows Resilient File System (ReFS) Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-49793 Windows Resilient File System (ReFS) Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50362 Windows Resilient File System (ReFS) Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50492 Windows Resilient File System (ReFS) Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-50501 Windows Resilient File System (ReFS) Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-58530 Windows Resilient File System (ReFS) Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-49791 Windows Routing and Remote Access Service (RRAS) Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-50451 Windows Routing and Remote Access Service (RRAS) Elevation of Privilege Vulnerability Important 7.1 No No EoP
CVE-2026-57096 Windows Routing and Remote Access Service (RRAS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50323 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50452 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50348 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50345 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50322 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50340 Windows Runtime Elevation of Privilege Vulnerability Important 8.5 No No EoP
CVE-2026-50410 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50449 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50460 Windows Runtime Elevation of Privilege Vulnerability Important 8.1 No No EoP
CVE-2026-50403 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50385 Windows Runtime Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50413 Windows Runtime Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50457 Windows Runtime Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50486 Windows Runtime Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50503 Windows Runtime Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-54125 Windows Runtime Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58527 Windows Runtime Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50373 Windows Search Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50679 Windows Search Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-44806 Windows Secure Channel Denial of Service Vulnerability Important 5.3 No No DoS
CVE-2026-50681 Windows Secure Channel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-56186 Windows Secure Channel Information Disclosure Vulnerability Important 8.1 No No Info
CVE-2026-50367 Windows Sensor Data Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58619 Windows Sensor Data Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50311 Windows Server Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50328 Windows Server Update Service (WSUS) Tampering Vulnerability Important 7.5 No No Tampering
CVE-2026-58531 Windows SMB Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-54997 Windows SMB Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-49801 Windows SMB Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50690 Windows SMB Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-56168 Windows SMB Server Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-50360 Windows SMB Server Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-57089 Windows SMB Server Network Transport Driver (srvnet.sys) Remote Code Execution Vulnerability Important 7.5 No No RCE
CVE-2026-50333 Windows Spaceport.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50298 Windows Spaceport.sys Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49171 Windows Speech Runtime Elevation of Privilege Vulnerability Important 7.5 No No EoP
CVE-2026-49170 Windows StateRepository API Server file Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58526 Windows Storage Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50299 Windows Storage Spaces Direct Remote Code Execution Vulnerability Important 6.8 No No RCE
CVE-2026-57968 Windows Subsystem for Linux (WSL2) Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-57973 Windows Subsystem for Linux (WSL2) Kernel Tampering Vulnerability Important 6.3 No No Tampering
CVE-2026-50418 Windows System Secure Feature Bypass Vulnerability Important 5.1 No No SFB
CVE-2026-50306 Windows TCP/IP Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50307 Windows TCP/IP Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-49177 Windows TCP/IP Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50669 Windows Telephony Server Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-54124 Windows Terminal Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-50350 Windows Trusted Runtime Interface Driver Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-50326 Windows Unified Consent System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49790 Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege Vulnerability Important 7.3 No No EoP
CVE-2026-50498 Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58547 Windows Universal Plug and Play (UPnP) Device Host Elevation of Privilege Vulnerability Important 5.5 No No EoP
CVE-2026-49794 Windows USB Audio Class Driver Information Disclosure Vulnerability Important 4.6 No No Info
CVE-2026-50453 Windows USB Audio Class Driver Information Disclosure Vulnerability Important 6.1 No No Info
CVE-2026-58528 Windows USB Audio Class Driver Information Disclosure Vulnerability Important 6.8 No No Info
CVE-2026-50321 Windows USB Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50479 Windows USB Hub Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-55000 Windows USB Print Driver Elevation of Privilege Vulnerability Important 6.4 No No EoP
CVE-2026-54991 Windows USB Print Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-54996 Windows USB Print Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-49802 Windows USB Print Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-49806 Windows USB Print Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-50674 Windows USB Print Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-49804 Windows USB Video Driver Elevation of Privilege Vulnerability Important 6.6 No No EoP
CVE-2026-50454 Windows User Interface Core Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49176 Windows WalletService Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-49800 Windows Web Proxy Auto-Discovery Protocol (WPAD) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50480 Windows Web Proxy Auto-Discovery Protocol (WPAD) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-56173 Windows WebView Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-58632 Windows Win32 Kernel Subsystem Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-54107 Windows Win32k Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-54986 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-54112 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-54114 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50670 Windows Win32k Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-50688 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50687 Windows Win32k Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-56176 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-58628 Windows Wireless Network Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-50295 Windows Zero Trust DNS Security Feature Bypass Vulnerability Important 5.5 No No SFB
CVE-2026-50509 Wireless Wide Area Network Service (WwanSvc) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-55945 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability Moderate 4.2 No No Info
CVE-2026-45488 Microsoft Edge (Chromium-based) Spoofing Vulnerability Moderate 5.4 No No Spoofing
CVE-2026-45489 Microsoft Edge (Chromium-based) Spoofing Vulnerability Moderate 6.5 No No Spoofing
CVE-2026-55145 Outlook Copilot Tampering Vulnerability Moderate 6.3 No No Tampering
CVE-2026-56181 Windows Network Address Translation (NAT) Spoofing Vulnerability Moderate 8.3 No No Spoofing
CVE-2026-58597 Microsoft Edge (Chromium-based) Spoofing Vulnerability Low 4.3 No No Spoofing

** Indicates this CVEs has already been resolved by Microsoft, and no further action is needed by the end user.


I’ll do my best to summarize everything else in this release, but no promises. I’m only human after all.


Looking at the remaining Critical-rated patches, Office is its own weather system: fourteen Word/Excel/PowerPoint/Office RCEs clustered at CVSS 7.8, plus five Windows Media Foundation RCEs. Outside of the Preview Pane attack vector, they are individually unremarkable; collectively, patch Office and reboot. Always reboot. We’ve already mentioned DHCP some, but DHCP Server can't catch a break. Beyond the one already covered, add CVE-2026-56159, CVE-2026-48564, CVE-2026-50370, and DHCP Client cousin CVE-2026-54128. Five DHCP RCEs in one release. Rounding things out, Print Spooler (CVE-2026-58608), Windows TCP/IP (CVE-2026-54999), and a SQL Server RCE pair (CVE-2026-54117/54118) all receive patches, and all are rated a CVSS 8.8. VE-2026-55944 (Dynamics NAV/Business Central On-Prem RCE, 9.8) is the same deserialization flavor as the SharePoint pair; it’s unauthenticated, network-reachable, and easy to overlook since it's not SharePoint. CVE-2026-48561 (Microsoft Copilot RCE, 9.6) and CVE-2026-50380 (Windows GDI+ RCE, 9.6) round out the near-top tier. Don't forget CVE-2026-55040, a SharePoint Security Feature Bypass (9.1) — patch it in the same pass as the SharePoint RCE pair since it's the same product family. Identity and infrastructure get hit too: CVE-2026-54121 (AD Certificate Services EoP, 8.8) and CVE-2026-50444 (WSUS EoP, 8.8). The obscure Reliable Multicast Transport Driver (RMCAST) takes two RCEs (CVE-2026-54982, CVE-2026-54995), and CVE-2026-50474 gives Remote Desktop Client its own RCE, separate from the RDP one already covered. The rest is a long tail: Defender RCE x2, GDI+ again, Windows Media x2, Secure Kernel Mode EoP x2, and a second Hyper-V EoP. You can consider these “normal” as far as patch cadence goes.

That leaves us with 95 RCE to discuss. I would explain, but there is too much, so let me sum up. CVE-2026-55944 (Dynamics NAV/Business Central On-Prem, 9.8) is the same deserialization flavor as the SharePoint pair: unauthenticated, easy to miss since it's not SharePoint. CVE-2026-54990 (Remote Desktop Client), CVE-2026-49172 (Windows FTP Service), and CVE-2026-50447 (MSMQ) all hit 9.8 too, proof severity labels lag CVSS sometimes. CVE-2026-48561 (Copilot) and CVE-2026-50380 (GDI+) sit at 9.6.

The pattern worth watching: 14 Windows NTFS and 7 ReFS RCEs/ That makes 21 filesystem-driver bugs, an unusually large cluster suggesting a shared root cause. Microsoft Edge (Chromium-based) contributes 21 more that are genuinely Microsoft's to patch, not Chromium re-listing noise. Remote Desktop Client racks up a second and third RCE (CVE-2026-50474, CVE-2026-58594), and Windows Admin Center picks up two (CVE-2026-56196/56197) — WAC exposure keeps creeping into these releases. Exchange Server (CVE-2026-55005) and AD Domain Services (CVE-2026-49178) both land at 8.8.

And because this release wouldn't be complete without it: CVE-2026-50663, an RCE in Age of Empires II: Definitive Edition. Yes, really. Patch your civilization anyway.

There are close to 260 EoP bugs in this month’s release. Microsoft could have just published the EoPs and still had a record-setting month. As usual, most simply lead to local attackers executing their code at SYSTEM-level privileges or administrative privileges, so there’s not much to add without further technical details about the bugs themselves. What’s really frustrating is that 94 have no explicit privilege statement at all. Microsoft just says “elevate privileges” with no detail. By my count, that leaves around 25 bugs to consider. Some don’t elevate at all. The FAQ literally says the attacker just gets “the rights of the user running the affected application.” That covers Win32k, Clip Service, Search Service, MSMQ, and SharePoint. A few get a Low-to-Medium integrity bump. There are also a couple that lead to downgraded service accounts or arbitrary file deletion, but nothing else I’ve seen really stands out too much.

There are 20 Security Feature Bypass (SFB) bugs this month, and it's a genuinely mixed bag. CVE-2026-55040 leads at Critical, CVSS 9.1 as it’s weak authentication in SharePoint Server. Patch it in the same pass as the SharePoint RCE pair since it's the same product. The AI-coding-tool trend continues: GitHub Copilot and Visual Studio Code and Visual Studio all land SFB bugs, mostly injection or path-traversal flavored. BitLocker is this month's lone publicly disclosed bug. It’s not exploited yet, but public disclosure is a countdown clock, not a free pass. It requires physical access, as does the bug in Microsoft XML. The firmware/boot cluster is worth a second look: Secure Boot, Boot Loader, and Key Guard all touch the trust chain below the OS. Meaning, despite a low CVSS score, “if this fails, nothing above it can be trusted” stakes. Rounding out the SFB patches, there are two .NET SFBs, two Windows Kernel SFBs, and a DNS/Cryptographic Services bringing up the rear.

The July release includes 31Spoofing bugs this month, and we’ve already covered the most important (Exchange). SharePoint Server accounts for another ten with almost all the same root cause: stored XSS letting an authenticated attacker spoof content in the browser. Microsoft Edge (Chromium-based) contributes fifteen more spanning access-control failures, SSRF, type confusion, and UI misrepresentation. All genuinely Microsoft's to patch, not re-listed Chromium noise. The remaining six round out the usual suspects: a Windows NAT spoofing bug reachable from an adjacent network, a Bing app flaw on iOS, a PowerBI Report Server XSS issue, a .NET output-encoding bug, and an AD FS spoofing flaw. None publicly disclosed, none exploited, but with SharePoint's history this year, don't let "just Spoofing" lull you into deprioritizing the patch cycle.

Of 111 Information Disclosure bugs, the overwhelming majority of these simply result in info leaks consisting of unspecified memory contents or memory addresses. GitHub Copilot is the standout. Here, the bug insufficiently protected credentials, meaning actual secrets leak, not memory scraps. The Windows Admin Center flaw discloses data via improper authentication. A management console leaking to an unauthorized party is a bigger deal than it sounds. SharePoint uses SSRF to pull data server-side, and the Event Logging Service is a protection-mechanism failure, not a memory bug at all. Edge picks up three genuinely file-system-flavored disclosures — improper authorization, files/directories accessible to external parties, and link-following — plus Edge for Android exposing “private personal information” twice and two path-traversal bugs. The remaining 40+ are mostly one-line “exposure of sensitive information to an unauthorized actor” entries scattered across File Explorer, Push Notifications, Cryptographic Services, and Win32k.

Only 8 Tampering bugs this month, the smallest bucket, but a couple stand out. The top of the list is a WSUS bug, caused by an uncaught exception that lets an unauthenticated attacker tamper with the update service over the network. That’s your patch-management infrastructure itself being the target, which always deserves extra attention. Windows CNG (the crypto API) picks up a missing-cryptographic-step flaw, and Windows DNS Client shows up three separate times across the list, twice for improper access control and once for missing authentication on a critical function. DNS resolution having this many tampering paths in one release is worth flagging as a pattern rather than three unrelated bugs. The one genuinely different entry is Outlook Copilot, described simply as vulnerable to “malicious uses” enabling tampering over the network. That’s a fantastically vague phrasing for an AI-assistant feature, continuing this year's running theme of Copilot-branded features showing up somewhere in every release. Finally, a .NET link-following bug and a WSL2 kernel race condition receive patches. Both require local/authorized access to trigger.

Still with me? Good, because we have 35 DoS bugs to cover, and this is really an identity-infrastructure story more than a grab-bag. Active Directory Federation Services alone accounts for seven of them, all sitting at CVSS 7.5, all stack-based buffer overflows or infinite loops that let an unauthenticated attacker knock the service over the network. The .NET ecosystem is the other big cluster: .NET, .NET Framework, and ASP.NET Core/OData contribute nine bugs combined, almost all “allocation of resources without limits or throttling”.  HTTP.sys and HTTP/2 pick up the same flavor. LSASS shows up twice, which is always worth a second look given what that process actually holds. Rounding out the list are patches for Windows DHCP Server, SMB Server, Secure Channel, Hyper-V, and IKE Protocol each take a single hit, mostly requiring authorized or adjacent-network access rather than being wide open to the internet.

No new advisories are being released this month.

Looking Ahead

The next Patch Tuesday will be on August 11, just after Hacker Summer Camp in sunny Las Vegas. Should I survive the heat, I’ll be back then to give you my full thoughts on the release – no matter how large it may be. Until then, stay safe, happy patching, and may all your reboots be smooth and clean!
The June 2026 Apple Security Update Review

We’re back with our look at the Apple macOS and iOS security updates. As this is a new feature for us, please let us know your feedback on the blog.

For June 2026, Apple released 37 unique CVEs across iOS 26.5.2 / iPadOS 26.5.2, macOS Tahoe 26.5.2, Safari 26.5.2. Since Apple doesn’t provide CVSS scores or other severity information, we’re left to speculate on which of these bugs is the most severe. The overwhelming majority (31 of 37) are WebKit/WebRTC bugs reachable through malicious web content. Most of those are crash/DoS bugs rather than code execution, so the real risk lives in the small set of kernel bugs and the handful of WebKit sandbox escapes. However, there are a couple that stand out.

-    CVE-2026-43724 (Kernel) – According to Apple, “An app may be able to cause unexpected system termination or write kernel memory.” A kernel memory write is the highest-value primitive here: it's the privilege-escalation half of a full exploit chain and leads to complete device control. The bug was credited to Hyunwoo Kim (@v4bel), who is known to be a serious kernel researcher.

-    CVE-2026-39868 (Kernel) – Another kernel bug, this one could “cause unexpected system termination or corrupt kernel memory.” This is kernel memory corruption, and notably credited to a roster of elite offensive researchers (STAR Labs, Positive Technologies, Baidu Security). This kind of attribution usually signals a weaponizable, possibly Pwn2Own-grade bug rather than a theoretical crash.

-    CVE-2026-43725 / CVE-2026-43701 (WebKit) – Apple states these bugs could allow a website to process restricted web content outside the sandbox. I'm flagging this sandbox-escape pair over the many WebKit crash bugs because a sandbox escape is the bridge that turns a web-content bug into a path toward the kernel issues above. It's the most dangerous remotely-triggered class in the release.

Here’s a look at all the bugs released by Apple this month:

Apple Security Update – June 29, 2026 37Total CVEs 22Denial of Service 7Information Disclosure 3Memory Corruption 2Elevation of Privilege 2Sandbox Escape 1Spoofing
Apple security release — June 29, 2026. "Yes/No" indicates whether each update is affected. CVE IDs link to NVD.
CVE ID Component Impact iOS 26.5.2 / iPadOS 26.5.2 macOS Tahoe 26.5.2 Safari 26.5.2
CVE-2026-43743 IOGPUFamily An app may be able to cause unexpected system termination Yes Yes No
CVE-2026-39868 Kernel An app may be able to cause unexpected system termination or corrupt kernel memory Yes Yes No
CVE-2026-43722 Kernel An app may be able to leak sensitive kernel state Yes Yes No
CVE-2026-43724 Kernel An app may be able to cause unexpected system termination or write kernel memory Yes Yes No
CVE-2026-43703 libxslt Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes No
CVE-2026-43706 libxslt Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes No
CVE-2026-43704 Web Extensions A malicious web extension may be able to cause an unexpected process crash Yes Yes Yes
CVE-2026-39872 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43663 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43676 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash Yes Yes Yes
CVE-2026-43699 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43700 WebKit Processing maliciously crafted web content may disclose sensitive user information Yes Yes Yes
CVE-2026-43701 WebKit A malicious website may be able to process restricted web content outside the sandbox Yes Yes Yes
CVE-2026-43705 WebKit Processing maliciously crafted web content may lead to memory corruption Yes Yes Yes
CVE-2026-43707 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43708 WebKit A malicious website may exfiltrate data cross-origin Yes Yes Yes
CVE-2026-43709 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43712 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43713 WebKit Visiting a website may leak sensitive data Yes Yes Yes
CVE-2026-43715 WebKit Processing maliciously crafted web content may lead to memory corruption Yes Yes Yes
CVE-2026-43716 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash Yes Yes Yes
CVE-2026-43725 WebKit A malicious website may be able to process restricted web content outside the sandbox Yes Yes Yes
CVE-2026-43726 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43727 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash Yes Yes Yes
CVE-2026-43731 WebKit Processing maliciously crafted web content may lead to memory corruption Yes Yes Yes
CVE-2026-43732 WebKit Processing maliciously crafted web content may disclose sensitive user information Yes Yes Yes
CVE-2026-43734 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43735 WebKit A malicious website may exfiltrate data cross-origin Yes Yes Yes
CVE-2026-43740 WebKit Processing maliciously crafted web content may result in the disclosure of process memory Yes Yes Yes
CVE-2026-43742 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43745 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash Yes Yes Yes
CVE-2026-43720 WebKit Canvas Processing maliciously crafted web content may lead to an unexpected Safari crash Yes Yes Yes
CVE-2026-43721 WebKit Storage A malicious website may be able to silently hijack clipboard data Yes Yes Yes
CVE-2026-28979 WebRTC Processing maliciously crafted web content may lead to an unexpected process crash Yes Yes Yes
CVE-2026-43717 WebRTC Processing maliciously crafted web content may lead to an unexpected Safari crash Yes Yes Yes
CVE-2026-43718 WebRTC Processing maliciously crafted web content may lead to an unexpected Safari crash Yes Yes Yes
CVE-2026-43746 WebRTC Processing maliciously crafted web content may lead to an unexpected Safari crash Yes Yes Yes

We’ll continue these macOS updates if people find them useful. Stay tuned for the regularly schedule Patch Tuesday blog covering Adobe and Microsoft.

The June 2026 Security Update Review

I’ve made it through Pwn2Own Berlin, had a little vacation, and now I’m back for Patch Tuesday. Microsoft and Adobe didn’t disappoint. In fact, they have heralded my return with the largest Patch Tuesday release ever. Thanks? Take a break from your regularly scheduled activities and let’s take a look at the latest security patches from Adobe and Microsoft. If you’d rather watch the full video recap covering the entire release, you can check it out here:

Adobe Patches for June 2026

For June, Adobe released 11 bulletins addressing 123 unique CVEs in Adobe Acrobat Reader, ColdFusion, Experience Manager, Experience Manager Forms, InDesign, InCopy, Substance 3D Sampler, Content Credentials SDK, Dreamweaver, Format Plugins, and Adobe Campaign Classic. A total of 11 of these CVEs were reported through the ZDI program.

Here’s this month’s overview table:

Bulletin ID Product CVE Count Highest Severity Highest CVSS Exploited Deployment Priority
APSB26-66 Adobe Campaign Classic 2 Critical 10.0 No 1
APSB26-64 Adobe ColdFusion 7 Critical 9.6 No 1
APSB26-63 Adobe Acrobat Reader 20 Critical 7.8 No 2
APSB26-57 Adobe Experience Manager Forms 3 Critical 9.3 No 2
APSB26-62 Adobe Dreamweaver 5 Critical 8.6 No 3
APSB26-65 Adobe Format Plugins 2 Critical 7.8 No 3
APSB26-59 Adobe InCopy 3 Critical 7.8 No 3
APSB26-58 Adobe InDesign 12 Critical 7.8 No 3
APSB26-60 Adobe Substance 3D Sampler 4 Critical 7.8 No 3
APSB26-61 Content Credentials SDK 8 Critical 7.5 No 3
APSB26-56 Adobe Experience Manager 57 Important 5.4 No 3
TOTAL 11 bulletins 123

Obviously, the update for Campaign Classic should be on the top of your deployment list if you’re a user. A CVSS 10 is rare; two in the same bulletin is pretty much a unicorn. Adobe says there are no active attacks, but I would expect heavy research into creating one. The update for Coldfusion is also a Priority 1, but again, no known attacks is the wild. I suspect the Reader patch will also receive a lot of attention as malicious PDFs are common in ransomware attacks. The update for Experience Manager may be large, but it’s mostly just cross-site scripting (XSS) bugs.

Microsoft Patches for June 2026

This month, Microsoft released a new record 208 CVEs Windows and Windows components, Office and Office Components, Microsoft Edge (Chromium-based), Azure, .NET and Visual Studio, Github Copilot, Defender, Exchange Server, Hyper-V, Secure Boot, and BitLocker. At least, that’s my count. Microsoft’s tools seem to be having some issues, as they initially included a CVE from 2020 in this release. Regardless, the count is over 200, and I counted several times.

One of these bugs came through the ZDI program, but bugs submitted during Pwn2Own Berlin remain unpatched. If you include the Chromium and other third-party bugs, the total CVE count for June comes to a staggering 571 CVEs. 38 of these cases are rated Critical while the rest are rated Important in severity.

I’ve been counting CVEs on Patch Tuesday since 2017, and this is by far the largest monthly release in that time. The previous record was 177 set last year. It is extraordinary that Microsoft can produce so many patches in a single month, but it does raise concerns. How many of these cases were found using AI tools? How many patches were generated using AI to assist in coding or testing? What quality issues may exist in these patches? And likely most importantly, is this the new normal? The last two months were also large releases. Should sysadmins adjust their processes for prioritization and patch deployment based on this new volume of updates? Unfortunately, Microsoft is not providing those answers right now. Hopefully that changes in the future. BTW – just a note – the current number of CVEs shipped by Microsoft this year exceeds the total number of CVEs shipped in all of 2018.

One of the bugs patched by Microsoft this month is listed as under active exploitation and three others are listed as publicly known at the time of release. Let’s take a closer look at some of the more interesting updates for this month, starting with the bug being exploited in the wild.

-   CVE-2026-41091 - Microsoft Defender Elevation of Privilege Vulnerability
Since Microsoft doesn’t provide info on how widespread exploitation is, we must read some tea leaves. For this patch, several different people were acknowledged, which indicates multiple parties say this is in the wild, meaning exploitation is likely significant. The good news is that most people won’t need to take action as Defender updates itself. However, if you don’t have this configured or are in an isolated environment, you’ll need to update to the latest version.

-    CVE-2026-45657 - Windows Kernel Remote Code Execution Vulnerability
This CVSS 9.8 bug allows remote, unauthenticated attackers to execute code at SYSTEM level without user interaction. Yup – this is wormable. The problem lies in the way the kernel handles TCP/IP. This was listed as “Exploitation Less Likely” by Microsoft, but rest assured that every researcher and bug shop on the planet is reversing this patch right now trying to create an exploit. Test and deploy this patch quickly.

-    CVE-2026-47291 - HTTP.sys Remote Code Execution Vulnerability
Our second CVSS 9.8 bug of the month, this also allows remote, unauthenticated attackers to execute code on affected systems without user interaction. However, there is a caveat. Systems using the default MaxRequestBytes registry value used by the Windows HTTP stack are not affected by this bug. You can edit your registry settings if you need protection while you test and deploy the patch. The bulletin includes instructions and even a PowerShell script for doing this action. Microsoft lists this as “Exploitation more likely”, so I would definitely check your registry settings.

-    CVE-2026-44815 - DHCP Client Service Remote Code Execution Vulnerability
Here’s another CVSS 9.8 that has an odd incongruity. Although the CVSS says no permissions are required for exploitation, the write-up states it must be an “authenticated” user. I would err on the side of caution here and believe the CVSS. If that’s correct, then we have another bug where a remote, unauthenticated attacker could execute code on affected systems without user interaction. And since the DHCP client is on every OS, it’s a juicy target. This is another one to test and deploy with haste.

-    CVE-2026-45585/CVE-2026-50507 - Windows BitLocker Security Feature Bypass Vulnerability
If you’ve followed the ongoing saga of Nightmare Eclipse vs. MSRC, the bugs should look familiar. One is definitely a fix for “YellowKey”, while the other appears to be a fix for “GreenPlasma”. The researcher has promised a “bone shattering” drop on June 14, so let’s hope Microsoft is able to reach some understanding with the researcher before more 0-days are released. Also, there is a script provided by Microsoft as a mitigation, but the better strategy is to test and deploy the updates.

 Here’s the full list of CVEs released by Microsoft for June 2026:

CVE Title Severity CVSS Public Exploited XI Type
CVE-2026-41091 Microsoft Defender Elevation of Privilege Vulnerability Important 7.8 Yes Yes 0 EoP
CVE-2026-49160 HTTP.sys Denial of Service Vulnerability Important 7.5 Yes No 1 DoS
CVE-2026-50507 Windows BitLocker Security Feature Bypass Vulnerability Important 6.8 Yes No 1 SFB
CVE-2026-45586 Windows Collaborative Translation Framework (CTFMON) Elevation of Privilege Vulnerability Important 7.8 Yes No 1 EoP
CVE-2025-10263 * ARM: CVE-2025-10263 Completion of affected memory accesses might not be guaranteed by completion of a TLBI [kernel] Critical 9.3 No No 2 EoP
CVE-2026-48567 Azure HorizonDB Elevation of Privilege Vulnerability Critical 10 No No N/A EoP
CVE-2026-32193 Azure Kubernetes Service (AKS) Remote Code Execution Vulnerability Critical 8.8 No No 3 RCE
CVE-2026-47644 Copilot Chat (Microsoft Edge) Information Disclosure Vulnerability Critical 6.5 No No 2 Info
CVE-2026-44815 DHCP Client Service Remote Code Execution Vulnerability Critical 9.8 No No 2 RCE
CVE-2026-47291 HTTP.sys Remote Code Execution Vulnerability Critical 9.8 No No 1 RCE
CVE-2026-42824 M365 Copilot Information Disclosure Vulnerability Critical 6.5 No No N/A Info
CVE-2026-45476 Microsoft Azure Network Adapter Elevation of Privilege Vulnerability Critical 8.2 No No 2 EoP
CVE-2026-44810 Microsoft Cryptographic Services Elevation of Privilege Vulnerability Critical 8.4 No No 2 EoP
CVE-2026-48579 Microsoft Exchange Online Information Disclosure Vulnerability Critical 9.1 No No N/A Info
CVE-2026-47655 Microsoft Graph Information Disclosure Vulnerability Critical 6.5 No No N/A Info
CVE-2026-45497 Microsoft M365 Copilot Remote Code Execution Vulnerability Critical 7.7 No No N/A RCE
CVE-2026-45460 Microsoft Office Information Disclosure Vulnerability Critical 4.7 No No 3 Info
CVE-2026-45472 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-45474 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-45461 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-45463 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-45456 Microsoft Outlook and Word Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-45458 Microsoft Outlook and Word Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-47635 Microsoft Outlook and Word Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-26142 Nuance PowerScribe Remote Code Execution Vulnerability Critical 9.8 No No 2 RCE
CVE-2026-47289 Remote Desktop Client Remote Code Execution Vulnerability Critical 8.8 No No 2 RCE
CVE-2026-47654 Remote Desktop Client Remote Code Execution Vulnerability Critical 7.5 No No 3 RCE
CVE-2026-48563 Remote Desktop Client Remote Code Execution Vulnerability Critical 7.5 No No 2 RCE
CVE-2026-42992 Remote Desktop Client Remote Code Execution Vulnerability Critical 7.5 No No 2 RCE
CVE-2026-44799 Remote Desktop Client Remote Code Execution Vulnerability Critical 7.5 No No 2 RCE
CVE-2026-44801 Remote Desktop Client Remote Code Execution Vulnerability Critical 7.5 No No 2 RCE
CVE-2026-42985 Remote Desktop Client Remote Code Execution Vulnerability Critical 8.8 No No 1 RCE
CVE-2026-45648 Windows Active Directory Domain Services Remote Code Execution Vulnerability Critical 8.8 No No 3 RCE
CVE-2026-42987 Windows Deployment Services (WDS) Remote Code Execution Critical 8.1 No No 2 RCE
CVE-2026-33828 Windows Device Health Attestation (DHA) Elevation of Privilege Vulnerability Critical 7.8 No No 3 EoP
CVE-2026-44803 Windows Graphics Component Remote Code Execution Vulnerability Critical 7.8 No No 1 RCE
CVE-2026-44812 Windows Graphics Component Remote Code Execution Vulnerability Critical 7.8 No No 1 RCE
CVE-2026-45607 Windows Hyper-V Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-45641 Windows Hyper-V Remote Code Execution Vulnerability Critical 8.4 No No 2 RCE
CVE-2026-47652 Windows Hyper-V Remote Code Execution Vulnerability Critical 8.2 No No 2 RCE
CVE-2026-47288 Windows Kerberos Key Distribution Center (KDC) Remote Code Execution Critical 7.1 No No 3 RCE
CVE-2026-45657 Windows Kernel Remote Code Execution Vulnerability Critical 9.8 No No 2 RCE
CVE-2026-48574 Windows Media Remote Code Execution Vulnerability Critical 7.8 No No 2 RCE
CVE-2026-45490 .NET SDK Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-45491 .NET Tampering Vulnerability Important 6.2 No No 3 Tampering
CVE-2026-45591 ASP.NET Core Denial of Service Vulnerability Important 7.5 No No 2 DoS
CVE-2026-47643 Azure Stack Edge Remote Code Execution Vulnerability Important 9.8 No No 3 RCE
CVE-2026-41098 Azure Stack Edge Spoofing Vulnerability Important 8.4 No No 2 Spoofing
CVE-2026-45642 Microsoft Azure Attestation service and Device Health Attestation Service Spoofing Vulnerability Important 3.9 No No 2 Spoofing
CVE-2026-45650 Microsoft Bing Search Spoofing Vulnerability Important 4.3 No No 2 Spoofing
CVE-2026-45637 Microsoft DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-45647 Microsoft Defender for Endpoint for Mac Elevation of Privilege Vulnerability Important 5.5 No No 2 EoP
CVE-2026-40371 Microsoft Dynamics 365 (on-premises) Elevation of Privilege Vulnerability Important 8.8 No No 2 EoP
CVE-2026-44822 Microsoft Excel Information Disclosure Vulnerability Important 8.2 No No 3 Info
CVE-2026-45455 Microsoft Excel Information Disclosure Vulnerability Important 3.3 No No 2 Info
CVE-2026-45469 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-44817 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No 3 RCE
CVE-2026-44818 Microsoft Excel Remote Code Execution Vulnerability Important 7 No No 2 RCE
CVE-2026-44820 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-44823 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-45459 Microsoft Excel Security Feature Bypass Vulnerability Important 3.3 No No 2 SFB
CVE-2026-45504 Microsoft Exchange Server Elevation of Privilege Vulnerability Important 8.8 No No 3 EoP
CVE-2026-45502 Microsoft Exchange Server Information Disclosure Vulnerability Important 5 No No 3 Info
CVE-2026-45503 Microsoft Exchange Server Information Disclosure Vulnerability Important 8.1 No No 3 Info
CVE-2026-45583 Microsoft Exchange Server Remote Code Execution Vulnerability Important 7.5 No No 2 RCE
CVE-2026-45500 Microsoft Exchange Server Spoofing Vulnerability Important 6.1 No No 2 Spoofing
CVE-2026-45501 Microsoft Exchange Server Spoofing Vulnerability Important 6.5 No No 2 Spoofing
CVE-2026-47631 Microsoft Exchange Server Spoofing Vulnerability Important 8.1 No No 2 Spoofing
CVE-2026-42986 Microsoft Graphics Component Elevation of Privilege Vulnerability Important 7.8 No No 1 EoP
CVE-2026-41092 Microsoft Kinect Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-45644 Microsoft Live Share Canvas SDK Elevation of Privilege Vulnerability Important 8 No No 2 EoP
CVE-2026-47293 Microsoft Office Click-To-Run Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-45485 Microsoft Office Information Disclosure Vulnerability Important 3.3 No No 2 Info
CVE-2026-44821 Microsoft Office Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-45483 Microsoft Office Project Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-45475 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-44819 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-44824 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-45645 Microsoft Office Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-49161 Microsoft PC Manager Security Feature Bypass Vulnerability Important 7.8 No No 3 SFB
CVE-2026-42902 Microsoft PowerToys Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-45484 Microsoft SharePoint Elevation of Privilege Vulnerability Important 8.8 No No 2 EoP
CVE-2026-45454 Microsoft SharePoint Remote Code Execution Vulnerability Important 6.5 No No 2 RCE
CVE-2026-47298 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8 No No 2 RCE
CVE-2026-45467 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-45468 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-45479 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-45453 Microsoft SharePoint Server Spoofing Vulnerability Important 5.4 No No 2 Spoofing
CVE-2026-47636 Microsoft SharePoint Server Spoofing Vulnerability Important 5.4 No No 2 Spoofing
CVE-2026-47637 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-47638 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-47639 Microsoft SharePoint Server Spoofing Vulnerability Important 5.4 No No 3 Spoofing
CVE-2026-47641 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-33113 Microsoft SharePoint Server Spoofing Vulnerability Important 5.4 No No 2 Spoofing
CVE-2026-45462 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-45464 Microsoft SharePoint Server Spoofing Vulnerability Important 5.4 No No 2 Spoofing
CVE-2026-45465 Microsoft SharePoint Server Spoofing Vulnerability Important 5.4 No No 2 Spoofing
CVE-2026-47634 Microsoft SharePoint Server Spoofing Vulnerability Important 7.3 No No 1 Spoofing
CVE-2026-47640 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 3 Spoofing
CVE-2026-45481 Microsoft SharePoint Server Spoofing Vulnerability Important 7.3 No No 1 Spoofing
CVE-2026-48560 Microsoft SharePoint Server Spoofing Vulnerability Important 5.4 No No 2 Spoofing
CVE-2026-48562 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No 2 Spoofing
CVE-2026-42835 Microsoft Teams for Android Information Disclosure Vulnerability Important 8.1 No No 2 Info
CVE-2026-45606 Microsoft UxTheme Library (uxtheme.dll) Denial of Service Vulnerability Important 5.5 No No 2 DoS
CVE-2026-45482 Microsoft Visual Studio Code CoPilot Chat Extension Security Feature Bypass Vulnerability Important 8.4 No No 2 SFB
CVE-2026-45466 Microsoft Word Information Disclosure Vulnerability Important 3.3 No No 3 Info
CVE-2026-45471 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-45486 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-45643 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-45457 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-42980 NT OS Kernel Elevation of Privilege Vulnerability Important 7.8 No No 1 EoP
CVE-2026-42916 NT OS Kernel Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-45649 Office for Android Spoofing Vulnerability Important 7.1 No No 3 Spoofing
CVE-2026-47653 Remote Desktop Client Remote Code Execution Vulnerability Important 8.8 No No 3 RCE
CVE-2026-42909 Remote Desktop Client Remote Code Execution Vulnerability Important 7.5 No No 3 RCE
CVE-2026-42913 Remote Desktop Client Remote Code Execution Vulnerability Important 7.5 No No 3 RCE
CVE-2026-42993 Remote Desktop Client Remote Code Execution Vulnerability Important 7.5 No No 2 RCE
CVE-2026-45588 Secure Boot Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-48568 Secure Boot Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-48570 Secure Boot Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-48573 Secure Boot Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-48575 Secure Boot Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-48576 Secure Boot Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-48578 Secure Boot Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-45654 Secure Boot Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-45656 UEFI Secure Boot Security Feature Bypass Vulnerability Important 7.8 No No 2 SFB
CVE-2026-8863 UEFI Secure Boot Security Feature Bypass Vulnerability Important 7.8 No No 2 SFB
CVE-2026-40376 Visual Studio Code Elevation of Privilege Vulnerability Important 7.5 No No 2 EoP
CVE-2026-47281 Visual Studio Code Elevation of Privilege Vulnerability Important 9.6 No No 3 EoP
CVE-2026-47284 Visual Studio Code Information Disclosure Vulnerability Important 6.5 No No 2 Info
CVE-2026-47292 Visual Studio Code MSSQL Extension Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-48569 Visual Studio Code Security Feature Bypass Vulnerability Important 7.1 No No 2 SFB
CVE-2026-47287 Visual Studio Code Tampering Vulnerability Important 6.5 No No 2 Tampering
CVE-2026-42829 Windows Administrator Protection Secure Feature Bypass Vulnerability Important 7.8 No No 2 SFB
CVE-2026-34335 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No 3 EoP
CVE-2026-45601 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-45598 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-45596 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-45638 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-45603 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-42911 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-45594 Windows Application Identity (AppID) Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-45655 Windows BitLocker Security Feature Bypass Vulnerability Important 5.3 No No 2 SFB
CVE-2026-45658 Windows BitLocker Security Feature Bypass Vulnerability Important 7.8 No No 1 SFB
CVE-2026-45640 Windows Bluetooth Port Driver Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-45605 Windows Bluetooth Service Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-47656 Windows Boot Manager Security Feature Bypass Vulnerability Important 7.9 No No 2 SFB
CVE-2026-44809 Windows Common Log File System Driver Elevation of Privilege Vulnerability Important 7.8 No No 3 EoP
CVE-2026-45634 Windows DHCP Client Information Disclosure Vulnerability Important 5.5 No No 3 Info
CVE-2026-45608 Windows DHCP Client Information Disclosure Vulnerability Important 6.8 No No 3 Info
CVE-2026-41108 Windows DNS Client Elevation of Privilege Vulnerability Important 7 No No 3 EoP
CVE-2026-42905 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 1 EoP
CVE-2026-44811 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-44808 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-44807 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-42983 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-44802 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-44813 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-44804 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-48566 Windows DWM Core Library Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-44814 Windows DWM Core Library Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-45602 Windows Dynamic Host Configuration Protocol (DHCP) Tampering Vulnerability Important 9.1 No No 2 Tampering
CVE-2026-42836 Windows Function Discovery Service (fdwsd.dll) Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-42910 Windows Hotpatch Monitoring Service Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-42972 Windows Hyper-V Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-45592 Windows Internet (wininet.dll) Elevation of Privilege Vulnerability Important 7.8 No No 3 EoP
CVE-2026-42903 Windows Kerberos Denial of Service Vulnerability Important 6.5 No No 3 DoS
CVE-2026-42914 Windows Kerberos Denial of Service Vulnerability Important 5.3 No No 2 DoS
CVE-2026-48583 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-45653 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No 3 EoP
CVE-2026-42984 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No 3 EoP
CVE-2026-45600 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability Important 7.8 No No 3 EoP
CVE-2026-45604 Windows Managed Installer Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-45595 Windows Mark of the Web Security Feature Bypass Vulnerability Important 5.4 No No 2 SFB
CVE-2026-45636 Windows NTFS Remote Code Execution Vulnerability Important 7.8 No No 2 RCE
CVE-2026-50508 Windows NTLM Spoofing Vulnerability Important 6.5 No No 1 Spoofing
CVE-2026-48565 Windows Narrator Braille Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-44805 Windows Network Controller (NC) Host Agent Denial of Service Vulnerability Important 5.5 No No 3 DoS
CVE-2026-42981 Windows Performance Monitor Remote Code Execution Vulnerability Important 8.1 No No 2 RCE
CVE-2026-42974 Windows Performance Monitor Remote Code Execution Vulnerability Important 8.1 No No 2 RCE
CVE-2026-45487 Windows Program Compatibility Assistant Service Elevation of Privilege Vulnerability Important 7.8 No No 3 EoP
CVE-2026-42828 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-42837 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-42969 Windows Push Notification Information Disclosure Vulnerability Important 5.5 No No 3 Info
CVE-2026-42971 Windows Push Notification Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-42970 Windows Push Notification Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-42973 Windows Push Notification Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-42978 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No 3 EoP
CVE-2026-42977 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No 3 EoP
CVE-2026-42979 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No 3 EoP
CVE-2026-42991 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No 3 EoP
CVE-2026-45639 Windows Remote Desktop Protocol (RDP) Information Disclosure Vulnerability Important 7.5 No No 2 Info
CVE-2026-42908 Windows Remote Desktop Protocol (RDP) Information Disclosure Vulnerability Important 7.5 No No 2 Info
CVE-2026-45593 Windows SDK Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-42906 Windows Shell Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-42907 Windows Shell Information Disclosure Vulnerability Important 6.5 No No 2 Info
CVE-2026-47648 Windows Storage Elevation of Privilege Vulnerability Important 7 No No 3 EoP
CVE-2026-42915 Windows TCP/IP Denial of Service Vulnerability Important 5.7 No No 2 DoS
CVE-2026-42904 Windows TCP/IP Elevation of Privilege Vulnerability Important 9.6 No No 3 EoP
CVE-2026-42968 Windows Telephony Server Information Disclosure Vulnerability Important 5.5 No No 2 Info
CVE-2026-42912 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No 2 EoP
CVE-2026-45597 Windows UI Automation Manager (uiamanager.dll) Elevation of Privilege Vulnerability Important 7 No No 3 EoP
CVE-2026-45599 Windows UPnP Device Host Remote Code Execution Vulnerability Important 8.1 No No 2 RCE
CVE-2026-45635 Windows UPnP Device Host Remote Code Execution Vulnerability Important 8.1 No No 2 RCE
CVE-2026-40409 Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-40404 Windows Universal Disk Format File System Driver (UDFS) Elevation of Privilege Vulnerability Important 7.8 No No 2 EoP
CVE-2026-42989 Winlogon Elevation of Privilege Vulnerability Important 7.8 No No 1 EoP

* Indicates this CVE had been released by a third party and is now being included in Microsoft releases.

† Indicates further administrative actions are required to fully address the vulnerability.


Looking at the other Critical-rated bugs in this release, the scariest-looking one is actually nothing to concern yourself with at all. The CVSS 10 bug in Azure HorizonDB has already been addressed by Microsoft and is just being documented now. That’s also the case for five others. Of course, there wouldn’t be a release without Office bugs that have the Preview Pane as an attack vector. There are multiple in June. There’s a handful of bugs in the Remote Desktop Client, but these rely on connecting to a malicious RDP server. There are three patches for Hyper-V that allow for guest-to-host code execution. The bug in Active Directory requires authentication, but any authenticated user can hit it. For the Windows Directory Service vulnerability, it needs to be listening for TFTP. You have blocked that everywhere, right? The bug in Azure Network Adapter is somewhat unique as you need to update your Linux kernel to be protected. The bug in Azure Kubernetes allows an attacker to break out of a container and gain control of the AKS worker node. Finally, the bug in the Kerberos Key Distribution Center (KDC) seems unlikely, but if exploited, it could allow authenticated attackers to get code execution on affected systems.

Moving on to the other code execution bugs, there are the ubiquitous open-an-own bugs in Office components like Excel and Word. The code injection bug in Exchange Server looks troubling, but it requires a machine-in-the-middle (MiTM), so exploitation is unlikely. The bugs in SharePoint require authentication, but you should note that the patch applies to both SharePoint Server 2016 and SharePoint Enterprise Server 2016. The two bugs in UPnP are interesting. Both can lead to code execution by causing an error during the handling of specially crafted data, which could lead to a Use After Free (UAF) bug. The bugs in RDP Client all require connecting to a malicious RDP server, but it’s not clear why some are rated Critical and some are rated Important. The NTFS vulnerability requires a user to mount a virtual hard drive on an affected system. The last RCE bug this month is in Azure Stack Edge and requires the attacker to send a specially crafted file upload request that includes a manipulated file name or path, leading to code execution.

There are more than 60 Elevation of Privilege (EoP) bugs in this month’s release, and as usual, most simply lead to local attackers executing their code at SYSTEM-level privileges or administrative privileges, so there’s not much to add without further technical details about the bugs themselves. A notable exception is in Exchange Server, where a user on Outlook Web Access (OWA) could gain access to other mailboxes. The bug in Visual Studio Code could allow attackers to gain permissions associated with the MCP Server’s managed identity. The bugs in Windows SDK and Windows UI Automation Manager could let attacker go from low integrity up to medium integrity code execution. The bug in Bluetooth just allows “elevated” privileges without really describing what elevated might be.

Moving on to the more than 20 security feature bypass (SFB) bugs in the June release, there are a total of 10 that impact Secure Boot. All carry scope change (S:C) in the CVSS, meaning successful exploitation affects security boundaries beyond the vulnerable component itself — specifically the ability to load untrusted code at boot, bypass Virtual Secure Mode, and undermine boot integrity guarantees. CVE-2026-45654 explicitly calls out VSM exposure. The bulk of these are credited to Alon Leviev (STORM), which is notable given his prior BootKitty/BlackLotus-adjacent research. The bugs in the Windows Boot Manager have a similar impact as the Secure Boot bugs. The UEFI Secure Boot vulnerabilities go a layer deeper. They require either local admin or physical access but could allow for the running of untrusted code even before the OS loads. Rootkits anyone? The four bugs in BitLocker all require physical access but could yield encrypted data if exploited. The bug in Windows Administration Protection allows attackers to bypass the feature that prevents standard-user apps from performing admin-level actions. The bug in Visual Studio Copilot Chat could be the most interesting non-boot bug here as it allows authentication impersonation. Mark of the Web (MotW) and Excel vulns could bypass user warnings. Lastly, the bug in PC Manager bypasses expected user controls.

Turning our attention to the mass of spoofing bugs in the release, we instantly see 18 impacting SharePoint Server. Fortunately, these are simply cross-site scripting (XSS) bugs. It’s the Exchange bugs we should really watch for. One is an XSS that an attacker can exploit by convincing an Exchange administrator to open a malicious link or message, which then runs code in the admin's web session. That's a meaningful privilege escalation path. Another is listed as an SSRF-based attack, but no other details are available. The last is a lower-impact XSS with limited confidentiality/integrity loss. The bug in Bing Search (remember Bing?) is a classic search result spoofing. The bug in Azure Stack Edge is interesting as it could allow access to resources outside the vulnerable component's security boundary. The bug in Office for Android requires user interaction. The Office Project Server bug is an authenticated XSS with low impact. The final spoofing bug is in Azure Attestation but has already been addressed. You should still verify you are protected by following the instructions in the write-up from Microsoft.

There are 30 different information disclosure bugs in this release, and fortunately, the vast majority of these simply result in info leaks consisting of unspecified memory contents or memory addresses. The two bugs in Visual Studio require user interaction and could “disclose information over a network.” How obtuse. The bug in GitHub Copilot and Visual Studio Code could disclose discloses a sign-in access token for a user's work account. That's a meaningful credential exposure, not just random memory. That leaves the two bugs in Exchange Server. One could allow an authenticated user to gain information about which network services that the Exchange server can reach. The other sounds much like the spoofing bug in OWA as it allows attackers to see information in mailboxes they should not have access to.

I’ve never been a fan of the “tampering” category, as it could mean so many different things. For example, the bug in .NET simply says it could allow an unauthorized attacker to perform tampering locally. Similarly, the bug in Visual Studio says the same, expect here the tampering occurs over a network. Microsoft doesn’t even bother with a CWE for the tampering bug in the DHCP Server, so your guess is as good as mine.

There are seven DoS bugs in the June release, and as usual, Microsoft provides little to no actionable information about the vulnerabilities. The most interesting is the bug in HTTP.sys, which is listed as publicly known. This is an uncontrolled resource consumption, rated "Exploitation More Likely," and publicly disclosed. Since, HTTP.sys sits at the core of IIS and Windows web services, a network-accessible DoS here can take down any Windows server running HTTP-based services. Based on the Acknowledgement, it looks like this bug may have been found using AI. There are no real details for the other bugs, but based simply on the impact, I would focus on the Kerberos and TCP/IP bugs if you had to prioritize.

No new advisories are being released this month.

Looking Ahead

The next Patch Tuesday will be on July 14 and will be the last one before Black Hat/DEFCON. It’s usually a big release, so strap in and hang on. I’ll be back then to give you my full thoughts. Until then, stay safe, happy patching, and may all your reboots be smooth and clean!
 

Pwn2Own Berlin 2026: Day Three Results and Master of Pw

Following two days of intense competition, Day Three of Pwn2Own Berlin 2026 brought the curtain down on an incredible event. Security researchers delivered their final exploits, pushing enterprise systems to the limit one last time as the race for Master of Pwn came to a close.

Day Three added to an already historic event, bringing the final totals to $1,298,250 awarded for 47 unique 0-day vulnerabilities across three days of competition. DEVCORE claimed the title of Master of Pwn with a commanding 50.5 points and $505,000 — a dominant performance across all three days. STARLabs SG finished in second with 25 points and $242,500, followed by Out Of Bounds in third with 12.75 points and $95,750.

Congratulations to all the researchers who participated, and a special thank you to OffensiveCon for hosting. We'll see you at the next Pwn2Own.

Here are the results of Day Three:

SUCCESS/COLLISION - Sina Kheirkhah (@SinSinology) of Summoning Team (@SummoningTeam) used two bugs to exploit Red Hat Linux, but one of the bugs was previously known. He still earns $7,000 and 1.5 Master of Pwn points.

SUCCESS - Le Tran Hai Tung (@tacbliw), dungnm (@dungnm_) and hieuvd (@gr4ss341) of Viettel Cyber Security (@vcslab) used an integer overflow to escalate privileges on #Windows 11. Their 5th round win nets them $7,500 and 3 Master of Pwn points.

SUCCESS - Satoki Tsuji (@satoki00) of Ikotas Labs, Inc. abused an external control to exploit OpenAI Codex and pop a host of calcs. He earns $20,000 and 4 Master of Pwn points.

FAILURE - Unfortunately, Giuseppe Calì of Summoning Team (@SummoningTeam) could not get their exploit of VMware ESXi working within the time allotted.

COLLISON - Although successful on stage, Emanuele Barbeno, Cyrill Bannwart, Yves Bieri, Lukasz D., Urs Mueller (@compasssecurity) of Compass Security targeted Anthropic Claude Code, hitting a one-vulnerability collision with a previous attempt and earning $20,000 and 2 Master of Pwn points.

SUCCESS - Hyunwoo Kim (@v4bel) chained a use-after-free and uninitialized memory bug to escalate privileges on Red Hat Enterprise Linux for Workstations in the fourth round, earning $5,000 and 2 Master of Pwn points.

SUCCESS - splitline (@splitline) of DEVCORE Research Team chained 2 bugs to exploit Microsoft SharePoint, earning $100,000 and 10 Master of Pwn points.

SUCCESS - Nguyen Hoang Thach (@hi_im_d4rkn3ss) of STARLabs SG (@starlabs_sg) used a Memory Corruption bug to exploit VMware ESXi with the Cross-tenant Code Execution add-on, earning $200,000 and 20 Master of Pwn points.

COLLISON - While Byung Young Yi (@yibarrack) of Out Of Bounds successfully demonstrated their exploit of Anthropic Claude Code, the bug used had been previously disclosed. They still earn $20,000 and 2 Master of Pwn points.

Pwn2Own Berlin 2026 - Day Two Results

Day Two of Pwn2Own Berlin 2026 and the stakes continue to rise! Security researchers are back on the Pwn2Own stage, pushing enterprise systems to their limits as the competition heats up. More exploits, more surprises, and more standout moments are unfolding, so follow along here for live updates as the race for Master of Pwn intensifies. There were plenty of big targets on the schedule today, including SharePoint, Exchange, and Safari.

Following an action-packed Day One where $523,000 was awarded for 24 unique 0-day vulnerabilities, Day Two added another $385,750 and 15 unique 0-days, bringing event totals to $908,750 with 39 unique vulnerabilities overall. DEVCORE holds a commanding lead for Master of Pwn with 40.5 points and $405,000, but with one day still to go, anything can happen. Here are the standings as of Day Two but we'll see what the final day of the contest brings. Stay tuned!

We’ll be posting real-time updates and results throughout the competition right here on our blog and across social media. Stay up to date by following us on Twitter, Mastodon, LinkedIn, and Bluesky, and join the conversation using #Pwn2Own Berlin and #P2OBerlin for continuous coverage. 

FAILURE - Unfortunately, Tao Yan & Edouard Bochin of Palo Alto Networks could not get their exploit of Apple Safari – Renderer Only working within the time allotted.

FAILURE - Unfortunately, Stephen Fewer of Rapid7 could not get their exploit of Microsoft SharePoint working within the time allotted.

SUCCESS - Ben Koo (@kiddo_pwn) of Team DDOS used a use-after-free bug to escalate privileges on Red Hat Enterprise Linux for Workstations in the second round, earning $10,000 and 1 Master of Pwn point.

SUCCESS - Dialed in! Nikolaos Mourousias (@deltaclock), Caue Obici (@caueobici) & Bruno Halltari (@BrunoModificato) of OtterSec used a Code Injection bug to exploit LM Studio in the second round, earning $20,000 and 4 Master of Pwn points. Full win!

COLLISON - Although successful on stage, Sina Kheirkhah (@SinSinology) of Summoning Team (@SummoningTeam) targeting Claude Desktop in the Coding Agent category used a bug that was previously known. They still earn $10,000 and 2 Master of Pwn points.

SUCCESS - Le Duc Anh Vu (@vulda17) of Viettel Cyber Security (@vcslab) exploited Cursor, earning $30,000 and 3 Master of Pwn points. Full win!

WITHDRAWAL - Kiyong Kwak of Kakaogames and Song Nuri of Samsung Electronics has withdrawn their entry for Apple Safari – Renderer Only in the Web Browser category.

FAILURE - Unfortunately, Ruitong of Abstract Team, University of Colorado Boulder could not get their exploit of Red Hat Enterprise Linux for Workstations working within the time allotted.

SUCCESS - Sina Kheirkhah (@SinSinology) of Summoning Team (@SummoningTeam) exploited OpenAI Codex in the second round, earning $20,000 and 4 Master of Pwn points.

COLLISON - Although successful on stage, Billy (@st424204), Bruce Chen (@bruce30262), Pan Zhenpeng (@Peterpan980927) & Weiming Shi (@bestswngs) of STARLabs SG (@starlabs_sg) targeting NVIDIA Megatron Bridge used a bug that was previously known. They still earn $2,500 and 1 Master of Pwn point.

WITHDRAWAL - Alon Ben Tsur (@iamgweej), Yahav Azran (@_yahav) have withdrawn their entry for Red Hat Enterprise Linux for Workstations in the Local Escalation of Privilege category.

SUCCESS - Orange Tsai (@orange_8361) of DEVCORE Research Team chained 3 bugs to achieve Remote Code Execution as SYSTEM on Microsoft Exchange, earning $200,000 and 20 Master of Pwn points.

SUCCESS / COLLISON - David Tae & Louis Hur of Out Of Bounds targeted Ollama, hitting a one-vulnerability collision with a previous attempt and earning $28,000 and 3 Master of Pwn points.

FAILURE - Nguyen Thanh Dat (@rewhiles) of Viettel Cyber Security (@vcslab) could not get their exploit of Mozilla Firefox – Renderer Only working within the time allotted.

SUCCESS - Cyrill Bannwart, Emanuele Barbeno, Yves Bieri, Lukasz D., Urs Mueller (@compasssecurity) of Compass Security exploited Cursor in the second round, earning $15,000 and 3 Master of Pwn points.

SUCCESS - Siyeon Wi used an integer overflow bug to escalate privileges on Microsoft Windows 11 in the fourth round, earning $7,500 and 3 Master of Pwn points.

SUCCESS / COLLISON - Byung Young Yi (@yibarrack) of Out Of Bounds targeted LiteLLM, hitting a one-vulnerability collision with a previous attempt and earning $17,750 and 3.75 Master of Pwn points.

SUCCESS - Confirmed! 0xDACA (@0xDACA) & Noam Trobishi (@NTrobishi) used a use-after-free bug to exploit NV Container Toolkit in the second round, earning $25,000 and 5 Master of Pwn points.

Pwn2Own Berlin 2026 - Day One Results

Welcome to Day One of Pwn2Own Berlin 2026! Today, 22 entries took the Pwn2Own stage to target AI Databases, Coding Agents, Local Inferences, and a separate category for NVIDIA products, as the world’s top security researchers push technology to its limits. Exploits, surprises, and breakthrough discoveries are unfolding.

After Day One, we awarded $523,000 for 24 unique 0-days! DEVCORE is currently in the lead for Master of Pwn, but a pack of teams are right on their heels. Stay tuned tomorrow for more results and surprises.

Follow the action live! We’ll be posting real-time updates and results throughout the competition on our blog and across social media. Stay up to date by following us on Twitter, Mastodon, LinkedIn, and Bluesky, and join the conversation using #Pwn2Own Berlin and #P2OBerlin for continuous coverage. 

FAILURE - Unfortunately, Le Duc Anh Vu (@vulda17) of Viettel Cyber Security (@vcslab) could not get their exploit of OpenAI Codex working within the time allotted.

SUCCESS - Orange Tsai (@orange_8361) of DEVCORE Research Team (@d3vc0r3) chained 4 logic bugs to achieve a sandbox escape on Microsoft Edge, earning $175,000 and 17.5 Master of Pwn points.

SUCCESS - chompie of IBM X-Force Offensive Research (XOR) used a single bug to exploit NV Container Toolkit, earning $50,000 and 5 Master of Pwn points.

SUCCESS - k3vg3n chained 3 bugs including SSRF and Code Injection to take down LiteLLM. $40,000 and 4 Master of Pwn points. Full win.

SUCCESS - Satoki Tsuji (@satoki00) of Ikotas Labs, Inc. used an Overly Permissive Allowed List bug to exploit NVIDIA Megatron Bridge, earning $20,000 and 2 Master of Pwn points.

FAILURE - Unfortunately, Park Jae Min could not get their exploit of Oracle Autonomous AI Database working within the time allotted. #Pwn2Own #P2OBerlin

SUCCESS - Emanuele Barbeno, Cyrill Bannwart, Yves Bieri, Lukasz D., Urs Mueller of Compass Security (@compasssecurity) used a single CWE-150 bug to exploit OpenAI Codex, earning $40,000 and 4 Master of Pwn points.

SUCCESS - Angelboy (@scwuaptx) & TwinkleStar03 (@_twinklestar03) of DEVCORE Research Team used an Improper Access Control bug to escalate privileges on Microsoft Windows 11, earning $30,000 and 3 Master of Pwn points.

WITHDRAWAL - Ben Koo (@kiddo_pwn) of Team DDOS has withdrawn their entry for Mozilla Firefox – Renderer Only in the Web Browser category

FAILURE - Unfortunately, Interrupt Labs could not get their exploit of NV Container Toolkit working within the time allotted

COLLISON - Although successful on stage, the Ikotas Labs, Inc. team targeting LiteLLM in the Local Inference category used bugs that were previously known. They still earn $8,000 and 1.75 Master of Pwn points.

SUCCESS - Yoseop Kim (@pwning_me) used a CWE-470 bug to exploit NVIDIA Megatron Bridge in the second round, earning $10,000 and 2 Master of Pwn points.

COLLISON - Although successful on stage, maitai (@MaitaiThe) of Doyensec (@Doyensec) targeting OpenAI Codex in the Coding Agent category used a bug that was previously known to the vendor. They still earn $10,000 and 2 Master of Pwn points.

WITHDRAWAL - Yoseop Kim(@pwning_me) has withdrawn their entry for Mozilla Firefox – Renderer Only in the Web Browser category

SUCCESS - haehae (@haehaeYang) of Out Of Bounds chained 2 bugs (CWE-190, CWE-362) to exploit Chroma, earning $20,000 and 2 Master of Pwn points.

SUCCESS - Billy (@st424204), Pan Zhenpeng (@Peterpan980927) & Weiming Shi (@bestswngs) of STARLabs SG (@starlabs_sg) chained 5 bugs (incl. SSRF and Code Injection) to exploit LM Studio, earning $40,000 and 4 Master of Pwn points. Full win!

SUCCESS - Marcin Wiązowski used a heap-based buffer overflow to escalate privileges on Microsoft Windows 11 in the second round, earning $15,000 and 3 Master of Pwn points.

WITHDRAWAL - Qrious Secure (@qriousec) has withdrawn their entry for LM Studio in the Local Inference category.

SUCCESS - Chompie of IBM X-Force Offensive Research (XOR) used a race condition to escalate privileges on Red Hat Enterprise Linux for Workstations, earning $20,000 and 2 Master of Pwn points.

COLLISON - Although successful on stage, Nguyen Thanh Dat (@rewhiles) of Viettel Cyber Security (@vcslab) targeting Anthropic Claude Code in the Coding Agent category used a bug that was previously known to the vendor. They still earn $20,000 and 2 Master of Pwn points

SUCCESS - haehae (@haehaeYang) of Out Of Bounds used a Path Traversal bug to exploit NVIDIA Megatron Bridge in the second round, earning $10,000 and 2 Master of Pwn points. Full win!

SUCCESS - Kentaro Kawane of GMO Cybersecurity by Ierae chained 2 Use-After-Free bugs to escalate privileges on Microsoft Windows 11 in the third round, earning $15,000 and 3 Master of Pwn points.

Pwn2Own Berlin 2026: The Full Schedule

Willkommen! (Welcome!) Pwn2Own Berlin 2026 has arrived at OffensiveCon, and the world’s top security researchers are ready. This year’s enterprise-focused competition features AI Databases, Coding Agents, Local Inferences, and a separate category for NVIDIA products.

Earlier today, we held the random draw to determine attempt order. Below is the official schedule. All times are Berlin local time (CET) and may change as the competition progresses. Check back for live updates.

In case you missed it, you can watch the draw here.

Jump to:

Day One

Day Two

Day Three

DAY ONE

Thursday, May 14 - 1030

chompie of IBM X-Force Offensive Research (XOR) targeting NV Container Toolkit in the NVIDIA category for a total of $50,000 and 5 Master of Pwn points

Le Duc Anh Vu ( @vulda ) of Viettel Cyber Security (@vcslab) targeting OpenAI Codex in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Orange Tsai (@orange_8361) of DEVCORE Research Team (@d3vc0r3) targeting Microsoft Edge – Sandbox Escape in the Web Browser category for a total of $175,000 and 17.5 Master of Pwn points

Thursday, May 14 - 1130

k3vg3n targeting LiteLLM in the Local Inference category for a total of $40,000 and 4 Master of Pwn points

Satoki Tsuji (@satoki00) / Ikotas Labs, Inc. targeting Megatron Bridge in the NVIDIA category for a total of $20,000 and 2 Master of Pwn points

Thursday, May 14 - 1300

Angelboy (@scwuaptx) of DEVCORE Research Team and TwinkleStar03 (@_twinklestar03), working with DEVCORE Internship Program targeting Microsoft Windows 11 in the Local Escalation of Privilege category for a total of $30,000 and 3 Master of Pwn points

Emanuele Barbeno, Cyrill Bannwart, Yves Bieri, Lukasz D., Urs Mueller of Compass Security (@compasssecurity) targeting OpenAI Codex in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Park Jae Min (@hiariz) targeting Oracle Autonomous AI Database in the AI Database category for a total of $40,000 and 4 Master of Pwn points

Thursday, May 14 - 1400

Satoki Tsuji (@satoki00) / Ikotas Labs, Inc. targeting LiteLLM in the Local Inference category for a total of $40,000 and 4 Master of Pwn points.

Yoseop kim(@pwning_me) targeting Megatron Bridge in the NVIDIA category for a total of $20,000 and 2 Master of Pwn points

Thursday, May 14 - 1500

Ben Koo (@kiddo_pwn) of Team DDOS targeting Mozilla Firefox – Renderer Only in the Web Browser category for a total of $50,000 and 5 Master of Pwn points

Interrupt Labs targeting NV Container Toolkit in the NVIDIA category for a total of $50,000 and 5 Master of Pwn points

Thursday, May 14 - 1530

maitai (@MaitaiThe) of Doyensec (@Doyensec) targeting OpenAI Codex in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Thursday, May 14 - 1600

Billy (@st424204), Pan Zhenpeng(@Peterpan980927), Weiming Shi (@bestswngs) of STARLabs SG (@starlabs_sg) targeting LM Studio in the Local Inference category for a total of $40,000 and 4 Master of Pwn points

Marcin Wiązowski targeting Microsoft Windows 11 in the Local Escalation of Privilege category for a total of $30,000 and 3 Master of Pwn points

Thursday, May 14 - 1630

haehae (@haehaeYang) of Out Of Bounds targeting Chroma in the AI Database category for a total of $20,000 and 2 Master of Pwn points

Thursday, May 14 - 1730

chompie of IBM X-Force Offensive Research (XOR) targeting Red Hat Enterprise Linux for Workstations in the Local Escalation of Privilege category for a total of $20,000 and 2 Master of Pwn points

Yoseop Kim(@pwning_me) targeting Mozilla Firefox – Renderer Only in the Web Browser category for a total of $50,000 and 5 Master of Pwn points

Thursday, May 14 - 1800

@rewhiles of Viettel Cyber Security (@vcslab) targeting Anthropic Claude Code in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Thursday, May 14 - 1830

Kentaro Kawane of GMO Cybersecurity by Ierae targeting Microsoft Windows 11 in the Local Escalation of Privilege category for a total of $30,000 and 3 Master of Pwn points

Qrious Secure (@qriousec) targeting LM Studio in the Local Inference category for a total of $40,000 and 4 Master of Pwn points

Thursday, May 14 - 1900

haehae (@haehaeYang) of Out of Bounds targeting Megatron Bridge in the NVIDIA category for a total of $20,000 and 2 Master of Pwn points

Back to top

DAY TWO

Friday, May 15 - 1030

Ben Koo (@kiddo_pwn) of Team DDOS targeting Red Hat Enterprise Linux for Workstations in the Local Escalation of Privilege category for a total of $20,000 and 2 Master of Pwn points

Stephen Fewer (Rapid7) targeting Microsoft SharePoint in the Server category for a total of $100,000 and 10 Master of Pwn points

Tao Yan (@Ga1ois) and Edouard Bochin (@le_douds) from Palo Alto Networks targeting Apple Safari – Renderer Only in the Web Browser category for a total of $75,000 and 7.5 Master of Pwn points

Friday, May 15 - 1130

Le Duc Anh Vu ( @vulda ) of Viettel Cyber Security (@vcslab) targeting Cursor in the Coding Agent category for a total of $30,000 and 3 Master of Pwn points

Nikolaos Mourousias (@deltaclock), Caue Obici (@caueobici) and Bruno Halltari (@BrunoModificato) of OtterSec targeting LM Studio in the Local Inference category for a total of $40,000 and 4 Master of Pwn points

Sina Kheirkhah (@SinSinology) of Summoning Team (@SummoningTeam). targeting Anthropic Claude Code in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Friday, May 15 - 1300

Ruitong from the Abstract Team at the University of Colorado Boulder targeting Red Hat Enterprise Linux for Workstations in the Local Escalation of Privilege category for a total of $20,000 and 2 Master of Pwn points

Friday, May 15 - 1330

Kiyong Kwak of Kakaogames and Song Nuri of Samsung Electronics targeting Apple Safari – Renderer Only in the Web Browser category for a total of $75,000 and 7.5 Master of Pwn points

Orange Tsai (@orange_8361) of DEVCORE Research Team targeting Microsoft Exchange in the Server category for a total of $200,000 and 20 Master of Pwn points

Friday, May 15 - 1400

Sina Kheirkhah (@SinSinology) of Summoning Team (@SummoningTeam). targeting OpenAI Codex in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Friday, May 15 - 1430

Billy (@st424204), Bruce Chen(@bruce30262), Pan Zhenpeng(@Peterpan980927), Weiming Shi (@bestswngs ) of STARLabs SG (@starlabs_sg) targeting Megatron Bridge in the NVIDIA category for a total of $20,000 and 2 Master of Pwn points

David Tae, Louis Hur of Out Of Bounds targeting Ollama in the Local Inference category for a total of $40,000 and 4 Master of Pwn points

Friday, May 15 - 1530

Team: Alon Ben Tsur (@iamgweej), Yahav Azran (@_yahav) targeting Red Hat Enterprise Linux for Workstations in the Local Escalation of Privilege category for a total of $20,000 and 2 Master of Pwn points

Friday, May 15 - 1600

@rewhiles of Viettel Cyber Security (@vcslab) targeting Mozilla Firefox – Renderer Only in the Web Browser category for a total of $50,000 and 5 Master of Pwn points

Siyeon Wi targeting Microsoft Windows 11 in the Local Escalation of Privilege category for a total of $30,000 and 3 Master of Pwn points

Friday, May 15 - 1630

Byung Young Yi (@yibarrack) of Out Of Bounds targeting LiteLLM in the Local Inference category for a total of $40,000 and 4 Master of Pwn points

Friday, May 15 - 1700

Emanuele Barbeno, Cyrill Bannwart, Yves Bieri, Lukasz D., Urs Mueller of Compass Security (@compasssecurity) targeting Cursor in the Coding Agent category for a total of $30,000 and 3 Master of Pwn points

Friday, May 15 - 1800

Daniel Cohen Hillel (@0xDACA) targeting NV Container Toolkit in the NVIDIA category for a total of $50,000 and 5 Master of Pwn points

Back to top

DAY THREE

Saturday, May 16 - 1100

Le Tran Hai Tung (@tacbliw), dungnm (@dungnm_) and hieuvd (@gr4ss341) of Viettel Cyber Security (@vcslab) targeting Microsoft Windows 11 in the Local Escalation of Privilege category for a total of $30,000 and 3 Master of Pwn points

Satoki Tsuji (@satoki00) / Ikotas Labs, Inc. targeting OpenAI Codex in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Sina Kheirkhah (@SinSinology) of Summoning Team (@SummoningTeam). targeting Red Hat Enterprise Linux for Workstations in the Local Escalation of Privilege category for a total of $20,000 and 2 Master of Pwn points

Saturday, May 16 - 1330

Emanuele Barbeno, Cyrill Bannwart, Yves Bieri, Lukasz D., Urs Mueller of Compass Security (@compasssecurity) targeting Anthropic Claude Code in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Hyunwoo Kim (@v4bel) targeting Red Hat Enterprise Linux for Workstations in the Local Escalation of Privilege category for a total of $20,000 and 2 Master of Pwn points

Team: Giuseppe Calì (@_gcali) of Summoning Team targeting VMware ESXi in the Virtualization category with the Cross-tenant Code Execution Addon add-on for a total of $200,000 and 20 Master of Pwn points

Saturday, May 16 - 1430

splitline (@_splitline_) of DEVCORE Research Team targeting Microsoft SharePoint in the Server category for a total of $100,000 and 10 Master of Pwn points

Saturday, May 16 - 1600

Byung Young Yi (@yibarrack) of Out Of Bounds targeting Anthropic Claude Code in the Coding Agent category for a total of $40,000 and 4 Master of Pwn points

Nguyen Hoang Thach (@hi_im_d4rkn3ss) of STARLabs SG (@starlabs_sg) targeting VMware ESXi in the Virtualization category with the Cross-tenant Code Execution Addon add-on for a total of $200,000 and 20 Master of Pwn points

Follow the action live! We’ll be posting real-time updates and results throughout the competition on our blog and across social media. Stay up to date by following us on Twitter, Mastodon, LinkedIn, and Bluesky, and join the conversation using #Pwn2Own Berlin and #P2OBerlin for continuous coverage. 

The May 2026 Security Update Review

I’m currently in Berlin helping set up for Pwn2Own Berlin, but that doesn’t stop Patch Tuesday from coming, and it’s another big one. At least nothing is listed as being in the wild – for now. Take a break from your regularly scheduled activities and let’s take a look at the latest security patches from Adobe and Microsoft. Due to technical difficulties, there will not be a video companion for this month.

Adobe Patches for May 2026

For May, Adobe released 10 bulletins addressing 52 unique CVEs in Adobe Commerce, After Effects, Adobe Connect, Illustrator, Media Encoder, Premiere Pro, Substance 3D Painter, Substance 3D Sampler, Content Authenticity SDK, and the Adobe Substance 3D Designer. Here’s this month’s overview table:

Bulletin ID Product CVE Count Highest Severity Highest CVSS Exploited Deployment Priority
APSB26-49 Adobe Commerce 15 Critical 8.7 No 2
APSB26-48 Adobe After Effects 4 Critical 7.8 No 3
APSB26-50 Adobe Connect 2 Critical 9.6 No 3
APSB26-51 Adobe Illustrator 4 Critical 7.8 No 3
APSB26-47 Adobe Media Encoder 2 Critical 7.8 No 3
APSB26-46 Adobe Premiere Pro 3 Critical 7.8 No 3
APSB26-55 Adobe Substance 3D Painter 2 Critical 7.8 No 3
APSB26-54 Adobe Substance 3D Sampler 1 Critical 7.8 No 3
APSB26-53 Content Authenticity SDK 14 Critical 7.5 No 3
APSB26-52 Adobe Substance 3D Designer 5 Important 6.3 No 3
TOTAL 10 bulletins 52

The obvious priority this month is the patch for Commerce, with its 15 bugs and deployment priority of 2. The Connect fix should also rank up there since both of its CVEs are CVSS 9s. Beyond those, it’s a pretty typical month for Adobe, with most of the bugs either being cross-site scripting (XSS) or open-and-own code executions.

Microsoft Patches for May 2026

This month, Microsoft released a whopping 138 new CVEs in Windows and Windows components, Office and Office Components, Microsoft Edge (Chromium-based), Azure, .NET and Visual Studio, Copilot Chat, Github Copilot, M365 Copilot, SQL Server, TCP/IP, and the Telnet Client – yes, the Telnet client. Two of these bugs were reported through the TrendAI ZDI program. 30 of these bugs are rated Critical, three are rated as Moderate, one is rated Low, and the rest are rated Important in severity.

This large volume of fixes follows the largest monthly release in Microsoft’s history and reflects the trend across the industry of a high number of submissions. While not all of these bugs were found by AI, it’s likely they had an AI-related component – even if it was just AI writing the submission. I should also point out the Pwn2Own Berlin occurs in just a few days, and it’s typical for vendors to patch as much as they can before the event.

None of the bugs patched by Microsoft this month are listed as publicly known or under active attack at the time of release, so we’ve got that going for us. Let’s take a closer look at some of the more interesting updates for this month, starting with a nasty-looking bug in DNS:

-    CVE-2026-41096 - Windows DNS Client Remote Code Execution Vulnerability
This patch fixes a heap-based buffer overflow in the DNS Client triggered by a malicious DNS response. No authentication or user interaction needed, and since the DNS Client runs on virtually every Windows machine, the attack surface is enormous. An attacker with a position to influence DNS responses (MitM, rogue server) could achieve unauthenticated RCE across your enterprise.

-    CVE-2026-41089 - Windows Netlogon Remote Code Execution Vulnerability
This update covers another CVSS 9.8 bug, which is a stack-based buffer overflow that lets an unauthenticated remote attacker execute code on a domain controller by sending a specially crafted network request — no credentials, no user interaction required. Yup – that makes it wormable. This is the highest-impact bug that requires immediate patching: a compromised domain controller is a compromised domain.

-    CVE-2026-42898 - Microsoft Dynamics 365 On-Premises Remote Code Execution Vulnerability
This bug rates a CVSS 9.9(!) and represents a code injection in Dynamics 365. It allows any authenticated user to execute code with a scope change, meaning exploitation can break out and affect resources beyond the vulnerable component itself. Scope changes are pretty rare, so if you’re running Dynamics 365 On-Prem, definitely test and deploy this patch quickly.

-    CVE-2026-40415 - Windows TCP/IP Remote Code Execution Vulnerability
This bug in the TCP/IP stack results from a use-after-free (UAF) and could allow a remote, unauthenticated threat actor to execute code without user interaction. That makes this another wormable bug. However, this one is much less likely to be exploited. The target needs to be under sustained low-memory (memory pressure) conditions, which is pretty rare. Still, no need to tempt fate here. Test and deploy this one quickly.

Here’s the full list of CVEs released by Microsoft for May 2026:

CVE Title Severity CVSS Public Exploited Type
CVE-2026-35435 Azure AI Foundry Elevation of Privilege Vulnerability Critical 8.6 No No EoP
CVE-2026-35428 Azure Cloud Shell Spoofing Vulnerability Critical 9.6 No No Spoofing
CVE-2026-42826 Azure DevOps Information Disclosure Vulnerability Critical 10 No No Info
CVE-2026-32207 Azure Machine Learning Notebook Spoofing Vulnerability Critical 8.8 No No Spoofing
CVE-2026-33109 Azure Managed Instance for Apache Cassandra Remote Code Execution Vulnerability Critical 9.9 No No RCE
CVE-2026-33844 Azure Managed Instance for Apache Cassandra Remote Code Execution Vulnerability Critical 9 No No RCE
CVE-2026-41105 Azure Monitor Action Group Notification System Elevation of Privilege Vulnerability Critical 8.1 No No EoP
CVE-2026-33111 Copilot Chat (Microsoft Edge) Information Disclosure Vulnerability Critical 7.5 No No Info
CVE-2026-26129 M365 Copilot Information Disclosure Vulnerability Critical 7.5 No No Info
CVE-2026-26164 M365 Copilot Information Disclosure Vulnerability Critical 7.5 No No Info
CVE-2026-33821 Microsoft Dynamics 365 Customer Insights Elevation of Privilege Vulnerability Critical 7.7 No No EoP
CVE-2026-42898 Microsoft Dynamics 365 On-Premises Remote Code Execution Vulnerability Critical 9.9 No No RCE
CVE-2026-40379 Microsoft Enterprise Security Token Service (ESTS) Spoofing Vulnerability Critical 9.3 No No Spoofing
CVE-2026-40363 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-40358 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-34327 Microsoft Partner Center Spoofing Vulnerability Critical 8.2 No No Spoofing
CVE-2026-40365 Microsoft SharePoint Server Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-41103 Microsoft SSO Plugin for Jira & Confluence Elevation of Privilege Vulnerability Critical 9.1 No No EoP
CVE-2026-33823 Microsoft Team Events Portal Information Disclosure Vulnerability Critical 9.6 No No Info
CVE-2026-40364 Microsoft Word Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-40366 Microsoft Word Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-40361 Microsoft Word Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-40367 Microsoft Word Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-42831 Office for Android Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-41096 Windows DNS Client Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-35421 Windows GDI Remote Code Execution Vulnerability Critical 7.8 No No RCE
CVE-2026-40403 Windows Graphics Component Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-40402 Windows Hyper-V Elevation of Privilege Vulnerability Critical 9.3 No No EoP
CVE-2026-32161 Windows Native WiFi Miniport Driver Remote Code Execution Vulnerability Critical 7.5 No No RCE
CVE-2026-41089 Windows Netlogon Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-32175 .NET Core Tampering Vulnerability Important 4.3 No No Tampering
CVE-2026-32177 .NET Elevation of Privilege Vulnerability Important 7.3 No No EoP
CVE-2026-35433 .NET Elevation of Privilege Vulnerability Important 7.3 No No EoP
CVE-2025-54518 * AMD: CVE-2025-54518 CPU OP Cache Corruption Important No No RCE
CVE-2026-42899 ASP.NET Core Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-40381 Azure Connected Machine Agent Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-42823 † Azure Logic Apps Elevation of Privilege Vulnerability Important 9.9 No No EoP
CVE-2026-33833 Azure Machine Learning Notebook Spoofing Vulnerability Important 8.2 No No Spoofing
CVE-2026-32204 Azure Monitor Agent Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-42830 Azure Monitor Agent Metrics Extension Elevation of Privilege Vulnerability Important 6.5 No No EoP
CVE-2026-33117 Azure SDK for Java Security Feature Bypass Vulnerability Important 9.1 No No SFB
CVE-2026-41109 GitHub Copilot and Visual Studio Code Security Feature Bypass Vulnerability Important 8.8 No No SFB
CVE-2026-35424 Internet Key Exchange (IKE) Protocol Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-41614 M365 Copilot for Desktop Spoofing Vulnerability Important 6.2 No No Spoofing
CVE-2026-41100 Microsoft 365 Copilot for Android Spoofing Vulnerability Important 4.4 No No Spoofing
CVE-2026-40377 Microsoft Cryptographic Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-41094 Microsoft Data Formulator Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-40417 Microsoft Dynamics 365 Business Central Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-42833 Microsoft Dynamics 365 On-Premises Remote Code Execution Vulnerability Important 9.1 No No RCE
CVE-2026-42838 Microsoft Edge (Chromium-based) Elevation of Privilege Vulnerability Important 5.4 No No EoP
CVE-2026-40360 Microsoft Excel Information Disclosure Vulnerability Important 7.8 No No Info
CVE-2026-40359 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-40362 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-42832 Microsoft Excel Spoofing Vulnerability Important 7.7 No No Spoofing
CVE-2026-34329 Microsoft Message Queuing (MSMQ) Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-40419 Microsoft Office Click-To-Run Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40418 Microsoft Office Click-To-Run Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-35436 Microsoft Office Click-To-Run Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-40420 Microsoft Office Click-To-Run Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-42893 Microsoft Outlook for iOS Tampering Vulnerability Important 7.4 No No Tampering
CVE-2026-40374 Microsoft Power Automate Desktop Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-41102 Microsoft PowerPoint for Android Spoofing Vulnerability Important 7.1 No No Spoofing
CVE-2026-35439 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-40368 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-33110 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-33112 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-40357 Microsoft SharePoint Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-32185 Microsoft Teams Spoofing Vulnerability Important 5.5 No No Spoofing
CVE-2026-41101 Microsoft Word for Android Spoofing Vulnerability Important 7.1 No No Spoofing
CVE-2026-35440 Microsoft Word Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-40421 Microsoft Word Information Disclosure Vulnerability Important 4.3 No No Info
CVE-2026-41097 Secure Boot Security Feature Bypass Vulnerability Important 6.7 No No SFB
CVE-2026-40370 † SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-41613 Visual Studio Code Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-41612 Visual Studio Code Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-41611 Visual Studio Code Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-41610 Visual Studio Code Security Feature Bypass Vulnerability Important 6.3 No No SFB
CVE-2026-33839 Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-33840 Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34330 Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34331 Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-35423 Windows 11 Telnet Client Information Disclosure Vulnerability Important 5.4 No No Info
CVE-2026-35438 Windows Admin Center Elevation of Privilege Vulnerability Important 8.3 No No EoP
CVE-2026-41086 Windows Admin Center in Azure Portal Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-34344 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34345 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-35416 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-41088 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34343 Windows Application Identity (AppID) Subsystem Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-35418 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-33835 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34337 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40407 Windows Common Log File System Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40397 Windows Common Log File System Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-42896 Windows DWM Core Library Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-35419 Windows DWM Core Library Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-34336 Windows DWM Core Library Information Disclosure Vulnerability Important 7.8 No No Info
CVE-2026-33834 Windows Event Logging Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32209 Windows Filtering Platform (WFP) Security Feature Bypass Vulnerability Important 4.4 No No SFB
CVE-2026-33841 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-35420 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40369 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34332 Windows Kernel-Mode Driver Remote Code Execution Vulnerability Important 8 No No RCE
CVE-2026-34339 Windows Lightweight Directory Access Protocol (LDAP) Denial of Service Vulnerability Important 5.5 No No DoS
CVE-2026-34341 Windows Link-Layer Discovery Protocol (LLDP) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-33838 Windows Message Queuing (MSMQ) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34342 Windows Print Spooler Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-41095 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34340 Windows Projected File System Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-40398 Windows Remote Desktop Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-21530 Windows Rich Text Edit Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-32170 Windows Rich Text Edit Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-40410 Windows SMB Client Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-35415 Windows Storage Spaces Controller Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34350 Windows Storport Miniport Driver Denial of Service Vulnerability Important 6.5 No No DoS
CVE-2026-40405 Windows TCP/IP Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-40414 Windows TCP/IP Denial of Service Vulnerability Important 7.4 No No DoS
CVE-2026-40401 Windows TCP/IP Denial of Service Vulnerability Important 6.2 No No DoS
CVE-2026-40413 Windows TCP/IP Denial of Service Vulnerability Important 7.4 No No DoS
CVE-2026-35422 Windows TCP/IP Driver Security Feature Bypass Vulnerability Important 6.5 No No SFB
CVE-2026-34351 Windows TCP/IP Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40399 Windows TCP/IP Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34334 Windows TCP/IP Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40406 Windows TCP/IP Information Disclosure Vulnerability Important 7.5 No No Info
CVE-2026-33837 Windows TCP/IP Local Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40415 Windows TCP/IP Remote Code Execution Vulnerability Important 8.1 No No RCE
CVE-2026-42825 Windows Telephony Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-34338 Windows Telephony Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40382 Windows Telephony Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-40380 Windows Volume Manager Extension Driver Remote Code Execution Vulnerability Important 6.2 No No RCE
CVE-2026-40408 Windows WAN ARP Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34333 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-34347 Windows Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-35417 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-42891 Microsoft Edge (Chromium-based) for Android Spoofing Vulnerability Moderate 6.5 No No Spoofing
CVE-2026-35429 Microsoft Edge (Chromium-based) for Android Spoofing Vulnerability Moderate 4.3 No No Spoofing
CVE-2026-41107 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability Moderate 7.4 No No Info
CVE-2026-40416 Microsoft Edge (Chromium-based) for Android Spoofing Vulnerability Low 4.3 No No Spoofing

* Indicates this CVE had been released by a third party and is now being included in Microsoft releases.

† Indicates further administrative actions are required to fully address the vulnerability.


Looking at the other Critical-rated bugs in this month’s release, there are quite a few scary-looking bugs (including a CVSS 10!), but there’s no action for the end user as Microsoft has already mitigated these bugs and is just now documenting them. There’s also this month’s crop of Office bugs where the Preview Pane is an attack vector. However, the bug in Office for Android does not have the Preview Pane vector; it’s simple open and own. The bug in the WiFi driver needs a network adjacent attacker. The SharePoint bug requires authentication, but anyone with site privileges has the authentication needed. The bug in SSO Plugin for Jira & Confluence should really be called an authentication bypass, since it allows an unauthenticated attacker to gain access to a system.

Looking at the other code execution bugs, most are of the open and own variety as expected. The bug in Dynamic 365 (On Prem) requires high privileges. The Message Queueing bug requires an adjacent attacker. The bug in SQL Server requires authentication, but as usual, patching won’t be straightforward. Finally, there’s a bug in the kernel that leads to code execution. Most kernel bugs are privilege escalations, but this one could allow code execution if an attacker sends specially crafted NVMe over Fabrics (NVMe‑oF) response messages during the connection handshake process that contains an invalid header length value. Neat.

As usual, the vast majority of the Microsoft release fixes Elevation of Privilege (EoP) bugs. Also as usual, most simply lead to local attackers executing their code at SYSTEM-level privileges or administrative privileges, so there’s not much to add without further technical details about the bugs themselves. There are also a few bugs that just state the attacker could “gain ELEVATED privileges.” How obtuse. The bugs in Azure allow an attacker to access data otherwise hidden from them. The Edge bug allows threat actors to elevate to the privileges of the running application. The bug in Visual Studio allows attackers to get permissions associated with the MCP Server’s managed identity. Finally, there are a couple of sandbox escapes, too, which are always useful.

This month's update includes six Security Feature Bypass vulnerabilities. The most severe is in the Azure SDK for Java (CVSS 9.1). An attacker over the network can bypass the integrity protection provided by authentication tags on encrypted data, effectively manipulating encrypted input in a way that slips past integrity checks during decryption. Close behind is the bypass affecting the GitHub Copilot integration in Visual Studio Code (CWE-74). This one requires a user interaction, but it allows an attacker to circumvent the path validation safeguards that normally control which files Copilot is permitted to modify. The other Visual Studio Code bypass involves cross-site scripting, improper link resolution, and information exposure triggered when a user opens or views a maliciously crafted notebook. On the Windows networking side there are two bypasses. The first hits the Windows TCP/IP driver via an authentication bypass using an alternate channel. The other impacts the Windows Filtering Platform through improper access control, allowing a local, low-privileged attacker to bypass FQDN-based network security rules. Finally, there’s a Secure Boot bypass that, you guessed it, bypasses secure boot features.

Moving on to the Information Disclosure bugs fixed this month, we have 15 different CVEs. As usual, the majority of these simply result in info leaks consisting of unspecified memory contents or memory addresses. The bug in Power Automate could expose data marked “Sensitive” within Power Automate Desktop flows. One of the Word bugs could disclose NLTM hashes. The bug in Edge could disclose your cookies, which seems rude. The bug in Visual Studio could expose file path information. Finally, there’s a bug in Telnet for Windows 11 that leaks information being used by Telnet at the time. I didn’t even realize Windows 11 still had a telnet client.

The May release contains 10 spoofing bugs (plus the ones already addressed by Microsoft). The bug in Azure Machine Learning Notebooks vulnerability requires user interaction, but it could expose info through the Azure ML web interface to the attacker. There’s a cluster of fixes for Microsoft's mobile Office suite on Android. Excel, Word, and PowerPoint for Android all carry spoofing flaws rooted in improper access control. Two Copilot products are also affected by spoofing vulns. The M365 Copilot for Desktop has no details provided. The M365 Copilot for Android variant requires low privileges and producing only limited impact on confidentiality and integrity. Microsoft Teams for Android rounds out the mobile app spoofing bugs. Three Edge bugs close things out, all involving misrepresentation of information in the browser UI.

There are two Tampering bugs in this month’s release. The one in .NET Core allows threat actors to write files to an affected system. The other is in Outlook for iOS and manifests as a command injection bug.

There are eight DoS bugs in the May release, but as always, Microsoft provides little to no actionable information about the vulnerabilities. The most interesting from a practical standpoint are two TCP/IP bugs that allow a low-privilege Hyper-V guest to crash the host. Both are triggered from the adjacent network. On the broader network-exposure side, the ASP.NET Core bug is a straightforward infinite loop condition — an unauthenticated attacker sends a crafted request over the network and the server stops responding.

No new advisories are being released this month.

Looking Ahead

Assuming I survive Pwn2Own Berlin (which is looking iffy at the moment), I’ll return on June 9th on what will hopefully be a smaller release than this one. Until then, stay safe, happy patching, and may all your reboots be smooth and clean!
The Apple macOS Security Update Review

We’ve received some feedback from those who read the Patch Blog that they would like something similar for macOS updates. Unfortunately, Apple doesn’t schedule these for a particular day, but we can provide our thoughts and analysis on the days they do release their latest patches.

For May 2026, Apple released 82 unique CVEs across the three macOS versions: 79 for macOS Tahoe 26.5, 45 for macOS Sequoia 15.7.7, and 42 for macOS Sonoma 14.8.7. Since Apple doesn’t provide CVSS scores or other severity information, we’re left to speculate on which of these bugs is the most severe. However, there are a couple that stand out.

-              CVE-2026-28819 (Wi-Fi) stands out as the strongest candidate for the most severe as it states, “An app may be able to execute arbitrary code with kernel privileges.” The combination of arbitrary code execution at the kernel level is about as bad as it gets on a severity scale. Plus, it affects all three macOS versions (Tahoe, Sequoia, and Sonoma).

-              CVE-2026-43668 (mDNSResponder) also piques my interest since, “A remote attacker may be able to cause unexpected system termination or corrupt kernel memory.” The remote attack vector with kernel memory corruption on all three OS versions makes this a serious one, especially since mDNSResponder is always running.

-              CVE-2026-28972 (Kernel) This one states that “An app may be able to cause unexpected system termination or write kernel memory.” An out-of-bounds write directly into kernel memory on all three OS versions. This one may also have implications in the upcoming Pwn2Own Berlin contest.

Here’s a look at all the bugs released by Apple this month:

82Unique CVEs 79macOS Tahoe 26.5 45macOS Sequoia 15.7.7 42macOS Sonoma 14.8.7
CVE ID Component Impact macOS Tahoe 26.5 macOS Sequoia 15.7.7 macOS Sonoma 14.8.7
CVE-2026-28991 Accelerate An app may be able to cause a denial-of-service Yes No No
CVE-2026-28988 Accounts An app may be able to bypass certain Privacy preferences Yes No No
CVE-2026-28959 APFS An app may be able to cause unexpected system termination Yes Yes Yes
CVE-2026-28995 App Intents A malicious app may be able to break out of its sandbox Yes No No
CVE-2026-1837 AppleJPEG Processing a maliciously crafted image may lead to a denial-of-service Yes No No
CVE-2026-28956 AppleJPEG Processing a maliciously crafted media file may lead to unexpected app termination or corrupt process memory Yes Yes Yes
CVE-2026-39869 Audio Processing an audio stream in a maliciously crafted media file may terminate the process Yes Yes Yes
CVE-2026-28922 CoreMedia An app may be able to access private information Yes Yes Yes
CVE-2026-28936 CoreServices Processing a maliciously crafted file may lead to unexpected app termination Yes No Yes
CVE-2026-28918 CoreSymbolication Parsing a maliciously crafted file may lead to an unexpected app termination Yes No No
CVE-2026-28878 Crash Reporter An app may be able to enumerate a user's installed apps No Yes No
CVE-2026-28915 CUPS An app may be able to gain root privileges Yes Yes Yes
CVE-2026-43659 FileProvider An app may be able to access sensitive user data Yes Yes Yes
CVE-2026-28923 GPU Drivers A malicious app may be able to break out of its sandbox Yes Yes Yes
CVE-2026-28925 HFS An app may be able to cause unexpected system termination or write kernel memory Yes Yes Yes
CVE-2025-43524 Icons An app may be able to break out of its sandbox No Yes Yes
CVE-2026-43661 ImageIO Processing a maliciously crafted image may corrupt process memory Yes No No
CVE-2026-28977 ImageIO Processing a maliciously crafted file may lead to unexpected app termination Yes Yes Yes
CVE-2026-28990 ImageIO Processing a maliciously crafted image may corrupt process memory Yes Yes Yes
CVE-2026-28978 Installer A malicious app may be able to break out of its sandbox Yes Yes Yes
CVE-2026-28992 IOHIDFamily An attacker may be able to cause unexpected app termination Yes Yes Yes
CVE-2026-28943 IOHIDFamily An app may be able to determine kernel memory layout Yes Yes Yes
CVE-2026-28969 IOKit An app may be able to cause unexpected system termination Yes Yes Yes
CVE-2026-43655 IOSurfaceAccelerator An app may be able to cause unexpected system termination or read kernel memory Yes No No
CVE-2026-43654 Kernel An app may be able to disclose kernel memory Yes Yes Yes
CVE-2026-28908 Kernel An app may be able to modify protected parts of the file system Yes Yes Yes
CVE-2026-28954 Kernel A maliciously crafted disk image may bypass Gatekeeper checks Yes Yes Yes
CVE-2026-28897 Kernel A local user may be able to cause unexpected system termination or read kernel memory Yes Yes Yes
CVE-2026-28952 Kernel An app may be able to cause unexpected system termination Yes Yes Yes
CVE-2026-28951 Kernel An app may be able to gain root privileges Yes Yes Yes
CVE-2026-28972 Kernel An app may be able to cause unexpected system termination or write kernel memory Yes Yes Yes
CVE-2026-28986 Kernel An app may be able to cause unexpected system termination Yes Yes Yes
CVE-2026-28987 Kernel An app may be able to leak sensitive kernel state Yes Yes Yes
CVE-2026-28983 LaunchServices A remote attacker may be able to cause a denial of service Yes No No
CVE-2026-28929 Mail Drafts Replying to an email could display remote images in Mail in Lockdown Mode Yes Yes Yes
CVE-2026-43653 mDNSResponder An attacker on the local network may be able to cause a denial-of-service Yes No Yes
CVE-2026-28985 mDNSResponder An attacker on the local network may be able to cause a denial-of-service Yes No No
CVE-2026-43668 mDNSResponder A remote attacker may be able to cause unexpected system termination or corrupt kernel memory Yes Yes Yes
CVE-2026-43666 mDNSResponder An attacker on the local network may be able to cause a denial-of-service Yes Yes Yes
CVE-2026-28941 Model I/O Processing a maliciously crafted file may lead to a denial-of-service or potentially disclose memory contents Yes Yes No
CVE-2026-28940 Model I/O Processing a maliciously crafted image may corrupt process memory Yes Yes No
CVE-2026-28961 Network Extensions An attacker with physical access to a locked device may be able to view sensitive user information Yes No No
CVE-2026-28906 Networking An attacker may be able to track users through their IP address Yes Yes Yes
CVE-2026-28840 PackageKit An app may be able to gain root privileges No Yes Yes
CVE-2026-43656 Quick Look Parsing a maliciously crafted file may lead to an unexpected app termination Yes Yes Yes
CVE-2026-43652 Sandbox An app may be able to access protected user data Yes No No
CVE-2026-39870 SceneKit Processing a maliciously crafted image may corrupt process memory Yes Yes Yes
CVE-2026-28846 SceneKit A remote attacker may be able to cause unexpected app termination Yes Yes Yes
CVE-2026-28993 Shortcuts An app may be able to access user-sensitive data Yes Yes Yes
CVE-2026-28848 SMB A remote attacker may be able to cause unexpected system termination Yes Yes No
CVE-2026-28930 Spotlight An app may be able to access protected user data Yes No No
CVE-2026-28974 Spotlight An app may be able to cause a denial-of-service Yes Yes No
CVE-2026-28996 Storage An app may be able to access sensitive user data Yes Yes Yes
CVE-2026-28919 StorageKit An app may be able to gain root privileges Yes Yes Yes
CVE-2026-28924 Sync Services An app may be able to access Contacts without user consent Yes Yes Yes
CVE-2026-39871 TV App An app may be able to observe unprotected user data Yes Yes Yes
CVE-2026-28976 UserAccountUpdater An app may be able to gain root privileges Yes No No
CVE-2026-43660 WebKit Processing maliciously crafted web content may prevent Content Security Policy from being enforced Yes No No
CVE-2026-28907 WebKit Processing maliciously crafted web content may prevent Content Security Policy from being enforced Yes No No
CVE-2026-28962 WebKit Processing maliciously crafted web content may disclose sensitive user information Yes No No
CVE-2026-43658 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash Yes No No
CVE-2026-28905 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28847 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28904 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28955 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28903 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28953 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28902 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28901 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28913 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28883 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28958 WebKit An app may be able to access sensitive user data Yes No No
CVE-2026-28917 WebKit Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28947 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash Yes No No
CVE-2026-28946 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash Yes No No
CVE-2026-28942 WebKit Processing maliciously crafted web content may lead to an unexpected Safari crash Yes No No
CVE-2026-28971 WebKit A malicious iframe may use another website's download settings Yes No No
CVE-2026-28944 WebRTC Processing maliciously crafted web content may lead to an unexpected process crash Yes No No
CVE-2026-28819 Wi-Fi An app may be able to execute arbitrary code with kernel privileges Yes Yes Yes
CVE-2026-28994 Wi-Fi An attacker in a privileged network position may be able to perform denial-of-service attack using crafted Wi-Fi packets Yes Yes Yes
CVE-2026-28914 zip A maliciously crafted ZIP archive may bypass Gatekeeper checks Yes No No
CVE-2026-28920 zlib Visiting a maliciously crafted website may leak sensitive data Yes Yes Yes
CVEs marked with the scarab logo were reported through the TrendAI Zero Day Initiative program.

We’ll continue these macOS updates if people find them useful. Stay tuned for the regularly schedule Patch Tuesday blog covering Adobe and Microsoft.

The April 2026 Security Update Review

It’s time once again for Patch Tuesday, and this one is huge. We’ve also got multiple exploits in the wild, which adds another layer of urgency to this month’s release. Take a break from your regularly scheduled activities, and let’s take a look at the latest security patches from Adobe and Microsoft. If you’d rather watch the full video recap covering the entire release, you can check it out here:

Adobe Patches for April 2026

For April, Adobe released 12 bulletins addressing 61 unique CVEs in Adobe Acrobat Reader, InDesign, InCopy, FrameMaker, Connect, ColdFusion, Bridge, Photoshop, Illustrator, Experience Manager Screens, and the Adobe DNG SDK. Three of the Cold Fusion bugs came through the TrendAI ZDI program. For this month, I’m introducing an Adobe table as well. I’d love to get your feedback on whether this is helpful.

Bulletin ID Product CVE Count Highest Severity Highest CVSS Exploited Deployment Priority
APSB26-43 Adobe Acrobat Reader 1 Critical 8.6 Yes 1
APSB26-44 Adobe Acrobat Reader 2 Critical 8.6 No 2
APSB26-32 Adobe InDesign 9 Critical 7.8 No 3
APSB26-33 Adobe InCopy 2 Critical 7.8 No 3
APSB26-36 Adobe FrameMaker 11 Critical 8.6 No 3
APSB26-37 Adobe Connect 9 Critical 9.6 No 3
APSB26-38 Adobe ColdFusion 7 Critical 9.3 No 1
APSB26-39 Adobe Bridge 6 Critical 7.8 No 3
APSB26-40 Adobe Photoshop 1 Critical 7.8 No 3
APSB26-42 Adobe Illustrator 1 Critical 7.8 No 3
APSB26-34 Adobe Experience Manager Screens 9 Important 5.4 No 3
APSB26-41 Adobe DNG SDK 3 Important 5.5 No 3

Obviously, the active attack in Reader is the highest priority for this month, but don’t ignore the second bunch of Reader patches. Cold Fusion also gets a deployment priority of 1, so if you’re still running that platform, make sure you get the update. Otherwise, the FrameMaker and Connect patches fix 11 and nine bugs, respectively. InDesign and Experience Manager Screens also have nine CVEs addressed.

Outside of the Reader bug, none of the other bugs fixed by Adobe this month are listed as publicly known or under active attack at the time of release. One of the Reader bugs and Cold Fusion have a deployment priority of one, the other Reader bug has a priority of two, while all of the other updates released by Adobe this month are listed as deployment priority 3.

Microsoft Patches for April 2026

This month, Microsoft released a monstrous 163 new CVEs in Windows and Windows components, Office and Office Components, Microsoft Edge (Chromium-based), Azure, .NET and Visual Studio, SQL Server, Hyper-V Server, BitLocker, and the Windows Wallet Service. Counting the third-party and a huge Chromium release, it brings the total number of CVEs to a staggering 247 updates. Six of these bugs were reported through the TrendAI ZDI program. Eight of these bugs are rated Critical, two are rated as Moderate, and the rest are rated Important in severity.

By my count, this is the second-largest monthly release in Microsoft’s history. There are many things we could speculate on to justify the size, but if Microsoft is like the other programs out there (including ours), they are likely seeing a rise in submissions found by AI tools. For us, our incoming rate has essentially tripled, making triage a challenge, to say the least. Whatever the reason, we have a lot of bugs to deal with this month. I should also point out that the Pwn2Own Berlin occurs next month, and it’s typical for vendors to patch as much as they can before the event.

There is one Microsoft bug listed as under active attack at the time of release, and one other that’s publicly known. Let’s take a closer look at some of the more interesting updates for this month, starting with the vulnerability being exploited in the wild:

-    CVE-2026-32201 - Microsoft SharePoint Server Spoofing Vulnerability
Microsoft doesn’t provide a lot of information about this bug, but Spoofing bugs in SharePoint often manifest as cross-site scripting (XSS) bugs. They do note that attackers could view information or make changes to disclosed information. As always, they don’t provide any information on how widespread these attacks are, but I wouldn’t wait to test and deploy this fix – especially if you have internet-connected SharePoint servers.

-    CVE-2026-33825 - Microsoft Defender Elevation of Privilege Vulnerability
This bug is listed as publicly known, and this time, we know exactly where it was disclosed. There have been some questions about how exploitable this bug may be, but it does look like it’s a real problem – just with some reliability issues in its current state. I won’t add on to the commentary from the researcher about working with Microsoft. I’m just glad they are offering a fix for the vulnerability. If you rely on Defender, test and deploy this one quickly.

-   CVE-2026-33827 - Windows TCP/IP Remote Code Execution Vulnerability
This vulnerability allows remote, unauthenticated attackers to exploit code on affected systems without user interaction. That adds up to a wormable bug – at least on systems with IPv6 and IPSec enabled. It is a race condition, which sets exploitability to High on the CVSS scale, but we see race conditions exploited at Pwn2Own all the time, so don’t rely on that obstacle. If you’re running IPv6, I would test and deploy this fix quickly before public exploits become available.

-    CVE-2026-33824 - Windows Internet Key Exchange (IKE) Service Extensions Remote Code Execution Vulnerability
Speaking of wormable bugs, here’s our second one this month. By the title, we can tell that systems with IKE enabled are affected, but that leaves plenty of targets for attackers. Microsoft also notes a significant mitigation for this bug. Blocking UDP ports 500 and 4500 at the perimeter prevents external attackers from reaching the affected service. However, insiders could still target this for lateral movement within an enterprise. For enterprises using IKE, get this fix tested and deployed with haste.

Here’s the full list of CVEs released by Microsoft for April 2026:

April 2026 Patch Tuesday
CVE Title Severity CVSS Public Exploited Type
CVE-2026-32201 Microsoft SharePoint Server Spoofing Vulnerability Important 6.5 No Yes Spoofing
CVE-2026-5281 * Chromium: CVE-2026-5281 Use after free in Dawn High N/A No Yes RCE
CVE-2026-33825 Microsoft Defender Elevation of Privilege Vulnerability Important 7.8 Yes No EoP
CVE-2026-23666 .NET Framework Denial of Service Vulnerability Critical 7.5 No No DoS
CVE-2026-32190 Microsoft Office Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-33114 Microsoft Word Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-33115 Microsoft Word Remote Code Execution Vulnerability Critical 8.4 No No RCE
CVE-2026-32157 Remote Desktop Client Remote Code Execution Vulnerability Critical 8.8 No No RCE
CVE-2026-33826 Windows Active Directory Remote Code Execution Vulnerability Critical 8 No No RCE
CVE-2026-33824 Windows Internet Key Exchange (IKE) Service Extensions Remote Code Execution Vulnerability Critical 9.8 No No RCE
CVE-2026-33827 Windows TCP/IP Remote Code Execution Vulnerability Critical 8.1 No No RCE
CVE-2026-26171 .NET Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-32226 .NET Framework Denial of Service Vulnerability Important 5.9 No No DoS
CVE-2026-32178 .NET Spoofing Vulnerability Important 7.5 No No Spoofing
CVE-2026-32203 .NET and Visual Studio Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-33116 .NET, .NET Framework, and Visual Studio Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2023-20585 * AMD: CVE-2023-20585 IOMMU Write Buffer Vulnerability Important 5.3 No No RCE
CVE-2026-32072 Active Directory Spoofing Vulnerability Important 6.2 No No Spoofing
CVE-2026-25184 Applocker Filter Driver (applockerfltr.sys) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32171 Azure Logic Apps Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-32168 Azure Monitor Agent Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32192 Azure Monitor Agent Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32181 Connected User Experiences and Telemetry Service Denial of Service Vulnerability Important 5.5 No No DoS
CVE-2026-27924 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32152 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32154 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27923 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32155 Desktop Window Manager Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-23653 GitHub Copilot and Visual Studio Code Information Disclosure Vulnerability Important 5.7 No No Info
CVE-2026-23653 * GitHub: CVE-2026-32631 'git clone' from manipulated repositories can leak NTLM hashes Important 7.4 No No Info
CVE-2026-33096 HTTP.sys Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-25250 * MITRE: CVE-2026-25250 Secure Boot disable Eazy Fix Important 6 No No SFB
CVE-2026-26181 Microsoft Brokering File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32219 Microsoft Brokering File System Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32091 Microsoft Brokering File System Elevation of Privilege Vulnerability Important 8.4 No No EoP
CVE-2026-26152 Microsoft Cryptographic Services Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-33103 Microsoft Dynamics 365 (On-Premises) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-32188 Microsoft Excel Information Disclosure Vulnerability Important 7.1 No No Info
CVE-2026-32189 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-32197 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-32198 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-32199 Microsoft Excel Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-32184 Microsoft High Performance Compute (HPC) Pack Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26155 Microsoft Local Security Authority Subsystem Service Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-27914 Microsoft Management Console Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26149 Microsoft Power Apps Security Feature Bypass Important 9 No No SFB
CVE-2026-32200 Microsoft PowerPoint Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-26143 Microsoft PowerShell Security Feature Bypass Vulnerability Important 7.8 No No SFB
CVE-2026-33120 † Microsoft SQL Server Remote Code Execution Vulnerability Important 8.8 No No RCE
CVE-2026-20945 Microsoft SharePoint Server Spoofing Vulnerability Important 4.6 No No Spoofing
CVE-2026-33822 Microsoft Word Information Disclosure Vulnerability Important 6.1 No No Info
CVE-2026-33095 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-23657 Microsoft Word Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-32081 Package Catalog Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-26170 PowerShell Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26183 Remote Access Management service/API (RPC server) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26160 Remote Desktop Licensing Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26159 Remote Desktop Licensing Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26151 Remote Desktop Spoofing Vulnerability Important 7.1 No No Spoofing
CVE-2026-32085 Remote Procedure Call Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-32167 SQL Server Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-32176 SQL Server Elevation of Privilege Vulnerability Important 6.7 No No EoP
CVE-2026-0390 UEFI Secure Boot Security Feature Bypass Vulnerability Important 6.7 No No SFB
CVE-2026-32220 UEFI Secure Boot Security Feature Bypass Vulnerability Important 4.4 No No SFB
CVE-2026-32212 Universal Plug and Play (upnp.dll) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-32214 Universal Plug and Play (upnp.dll) Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-32079 Web Account Manager Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-33104 Win32k Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32196 Windows Admin Center Spoofing Vulnerability Important 6.1 No No Spoofing
CVE-2026-26178 Windows Advanced Rasterization Platform Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-32073 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-26168 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26173 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-26177 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-26182 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-27922 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-33099 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-33100 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32088 Windows Biometric Service Security Feature Bypass Vulnerability Important 6.1 No No SFB
CVE-2026-27913 Windows BitLocker Security Feature Bypass Vulnerability Important 7.7 No No SFB
CVE-2026-26175 Windows Boot Manager Security Feature Bypass Vulnerability Important 4.6 No No SFB
CVE-2026-32162 Windows COM Elevation of Privilege Vulnerability Important 8.4 No No EoP
CVE-2026-20806 Windows COM Server Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-26176 Windows Client Side Caching driver (csc.sys) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27926 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32070 Windows Common Log File System Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-33098 Windows Container Isolation FS Filter Driver Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26153 Windows Encrypted File System (EFS) Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32087 Windows Function Discovery Service (fdwsd.dll) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32093 Windows Function Discovery Service (fdwsd.dll) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32086 Windows Function Discovery Service (fdwsd.dll) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32150 Windows Function Discovery Service (fdwsd.dll) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-27931 Windows GDI Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-27930 Windows GDI Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-32221 Windows Graphics Component Remote Code Execution Vulnerability Important 8.4 No No RCE
CVE-2026-27906 Windows Hello Security Feature Bypass Vulnerability Important 4.4 No No SFB
CVE-2026-27928 Windows Hello Security Feature Bypass Vulnerability Important 8.7 No No SFB
CVE-2026-26156 Windows Hyper-V Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-32149 Windows Hyper-V Remote Code Execution Vulnerability Important 7.3 No No RCE
CVE-2026-27910 Windows Installer Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27912 Windows Kerberos Elevation of Privilege Vulnerability Important 8 No No EoP
CVE-2026-26179 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26180 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32195 Windows Kernel Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-26163 Windows Kernel Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32215 Windows Kernel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-32217 Windows Kernel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-32218 Windows Kernel Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-26169 Windows Kernel Memory Information Disclosure Vulnerability Important 6.1 No No Info
CVE-2026-27929 Windows LUA File Virtualization Filter Driver Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32071 Windows Local Security Authority Subsystem Service (LSASS) Denial of Service Vulnerability Important 7.5 No No DoS
CVE-2026-20930 Windows Management Services Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26162 Windows OLE Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-33101 Windows Print Spooler Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32084 Windows Print Spooler Information Disclosure Vulnerability Important 5.5 No No Info
CVE-2026-27927 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26184 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32069 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32074 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32078 Windows Projected File System Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26167 Windows Push Notifications Elevation of Privilege Vulnerability Important 8.8 No No EoP
CVE-2026-32158 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32159 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32160 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26172 Windows Push Notifications Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-20928 Windows Recovery Environment Security Feature Bypass Vulnerability Important 4.6 No No SFB
CVE-2026-32216 Windows Redirected Drive Buffering System Denial of Service Vulnerability Important 5.5 No No DoS
CVE-2026-27909 Windows Search Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26161 Windows Sensor Data Service Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-26174 Windows Server Update Service (WSUS) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32224 Windows Server Update Service (WSUS) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-26154 Windows Server Update Service (WSUS) Tampering Vulnerability Important 7.5 No No Tampering
CVE-2026-26165 Windows Shell Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-26166 Windows Shell Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-27918 Windows Shell Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32151 Windows Shell Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-32225 Windows Shell Security Feature Bypass Vulnerability Important 8.8 No No SFB
CVE-2026-32202 Windows Shell Spoofing Vulnerability Important 4.3 No No Spoofing
CVE-2026-32082 Windows Simple Search and Discovery Protocol (SSDP) Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32083 Windows Simple Search and Discovery Protocol (SSDP) Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32068 Windows Simple Search and Discovery Protocol (SSDP) Service Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32183 Windows Snipping Tool Remote Code Execution Vulnerability Important 7.8 No No RCE
CVE-2026-32089 Windows Speech Brokered Api Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32090 Windows Speech Brokered Api Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32153 Windows Speech Runtime Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27907 Windows Storage Spaces Controller Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32076 Windows Storage Spaces Controller Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27908 Windows TDI Translation Driver (tdx.sys) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-27921 Windows TDI Translation Driver (tdx.sys) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-27915 Windows UPnP Device Host Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27919 Windows UPnP Device Host Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32075 Windows UPnP Device Host Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-27916 Windows UPnP Device Host Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27920 Windows UPnP Device Host Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32077 Windows UPnP Device Host Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27925 Windows UPnP Device Host Information Disclosure Vulnerability Important 6.5 No No Info
CVE-2026-32156 Windows UPnP Device Host Remote Code Execution Vulnerability Important 7.4 No No RCE
CVE-2026-32223 Windows USB Printing Stack (usbprint.sys) Elevation of Privilege Vulnerability Important 6.8 No No EoP
CVE-2026-32165 Windows User Interface Core Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-27911 Windows User Interface Core Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32163 Windows User Interface Core Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-32164 Windows User Interface Core Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-23670 Windows Virtualization-Based Security (VBS) Security Feature Bypass Vulnerability Important 5.7 No No SFB
CVE-2026-27917 Windows WFP NDIS Lightweight Filter Driver (wfplwfs.sys) Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32080 Windows WalletService Elevation of Privilege Vulnerability Important 7 No No EoP
CVE-2026-32222 Windows Win32k Elevation of Privilege Vulnerability Important 7.8 No No EoP
CVE-2026-21637 * HackerOne: CVE-2026-21637 TLS PSK/ALPN Callback Exceptions Bypass Error Handlers Moderate 7.5 No No SFB
CVE-2026-33119 Microsoft Edge (Chromium-based) for Android Spoofing Vulnerability Moderate 5.4 No No Spoofing
CVE-2026-33829 Windows Snipping Tool Spoofing Vulnerability Moderate 4.3 No No Spoofing
CVE-2026-5858 * Chromium: CVE-2026-5858 Heap buffer overflow in WebML Critical N/A No No RCE
CVE-2026-5859 * Chromium: CVE-2026-5859 Integer overflow in WebML Critical N/A No No RCE
CVE-2026-5272 * Chromium: CVE-2026-5272 Heap buffer overflow in GPU High N/A No No RCE
CVE-2026-5273 * Chromium: CVE-2026-5273 Use after free in CSS High N/A No No RCE
CVE-2026-5274 * Chromium: CVE-2026-5274 Integer overflow in Codecs High N/A No No RCE
CVE-2026-5275 * Chromium: CVE-2026-5275 Heap buffer overflow in ANGLE High N/A No No RCE
CVE-2026-5276 * Chromium: CVE-2026-5276 Insufficient policy enforcement in WebUSB High N/A No No SFB
CVE-2026-5277 * Chromium: CVE-2026-5277 Integer overflow in ANGLE High N/A No No RCE
CVE-2026-5279 * Chromium: CVE-2026-5279 Object corruption in V8 High N/A No No RCE
CVE-2026-5280 * Chromium: CVE-2026-5280 Use after free in WebCodecs High N/A No No RCE
CVE-2026-5283 * Chromium: CVE-2026-5283 Inappropriate implementation in ANGLE High N/A No No SFB
CVE-2026-5284 * Chromium: CVE-2026-5284 Use after free in Dawn High N/A No No RCE
CVE-2026-5285 * Chromium: CVE-2026-5285 Use after free in WebGL High N/A No No RCE
CVE-2026-5286 * Chromium: CVE-2026-5286 Use after free in Dawn High N/A No No RCE
CVE-2026-5287 * Chromium: CVE-2026-5287 Use after free in PDF High N/A No No RCE
CVE-2026-5289 * Chromium: CVE-2026-5289 Use after free in Navigation High N/A No No RCE
CVE-2026-5290 * Chromium: CVE-2026-5290 Use after free in Compositing High N/A No No RCE
CVE-2026-5860 * Chromium: CVE-2026-5860 Use after free in WebRTC High N/A No No RCE
CVE-2026-5861 * Chromium: CVE-2026-5861 Use after free in V8 High N/A No No RCE
CVE-2026-5862 * Chromium: CVE-2026-5862 Inappropriate implementation in V8 High N/A No No SFB
CVE-2026-5863 * Chromium: CVE-2026-5863 Inappropriate implementation in V8 High N/A No No SFB
CVE-2026-5864 * Chromium: CVE-2026-5864 Heap buffer overflow in WebAudio High N/A No No RCE
CVE-2026-5865 * Chromium: CVE-2026-5865 Type Confusion in V8 High N/A No No RCE
CVE-2026-5866 * Chromium: CVE-2026-5866 Use after free in Media High N/A No No RCE
CVE-2026-5867 * Chromium: CVE-2026-5867 Heap buffer overflow in WebML High N/A No No RCE
CVE-2026-5868 * Chromium: CVE-2026-5868 Heap buffer overflow in ANGLE High N/A No No RCE
CVE-2026-5869 * Chromium: CVE-2026-5869 Heap buffer overflow in WebML High N/A No No RCE
CVE-2026-5870 * Chromium: CVE-2026-5870 Integer overflow in Skia High N/A No No RCE
CVE-2026-5871 * Chromium: CVE-2026-5871 Type Confusion in V8 High N/A No No RCE
CVE-2026-5872 * Chromium: CVE-2026-5872 Use after free in Blink High N/A No No RCE
CVE-2026-5873 * Chromium: CVE-2026-5873 Out of bounds read and write in V8 High N/A No No RCE
CVE-2026-5291 * Chromium: CVE-2026-5291 Inappropriate implementation in WebGL Medium N/A No No SFB
CVE-2026-5292 * Chromium: CVE-2026-5292 Out of bounds read in WebCodecs Medium N/A No No Info
CVE-2026-5874 * Chromium: CVE-2026-5874 Use after free in PrivateAI Medium N/A No No RCE
CVE-2026-5875 * Chromium: CVE-2026-5875 Policy bypass in Blink Medium N/A No No SFB
CVE-2026-5876 * Chromium: CVE-2026-5876 Side-channel information leakage in Navigation Medium N/A No No Info
CVE-2026-5877 * Chromium: CVE-2026-5877 Use after free in Navigation Medium N/A No No RCE
CVE-2026-5878 * Chromium: CVE-2026-5878 Incorrect security UI in Blink Medium N/A No No Spoofing
CVE-2026-5879 * Chromium: CVE-2026-5879 Insufficient validation of untrusted input in ANGLE Medium N/A No No SFB
CVE-2026-5880 * Chromium: CVE-2026-5880 Incorrect security UI in browser UI Medium N/A No No Spoofing
CVE-2026-5881 * Chromium: CVE-2026-5881 Policy bypass in LocalNetworkAccess Medium N/A No No SFB
CVE-2026-5882 * Chromium: CVE-2026-5882 Incorrect security UI in Fullscreen Medium N/A No No Spoofing
CVE-2026-5883 * Chromium: CVE-2026-5883 Use after free in Media Medium N/A No No RCE
CVE-2026-5884 * Chromium: CVE-2026-5884 Insufficient validation of untrusted input in Media Medium N/A No No SFB
CVE-2026-5885 * Chromium: CVE-2026-5885 Insufficient validation of untrusted input in WebML Medium N/A No No SFB
CVE-2026-5886 * Chromium: CVE-2026-5886 Out of bounds read in WebAudio Medium N/A No No Info
CVE-2026-5887 * Chromium: CVE-2026-5887 Insufficient validation of untrusted input in Downloads Medium N/A No No SFB
CVE-2026-5888 * Chromium: CVE-2026-5888 Uninitialized Use in WebCodecs Medium N/A No No RCE
CVE-2026-5889 * Chromium: CVE-2026-5889 Cryptographic Flaw in PDFium Medium N/A No No SFB
CVE-2026-5890 * Chromium: CVE-2026-5890 Race in WebCodecs Medium N/A No No RCE
CVE-2026-5891 * Chromium: CVE-2026-5891 Insufficient policy enforcement in browser UI Medium N/A No No SFB
CVE-2026-5892 * Chromium: CVE-2026-5892 Insufficient policy enforcement in PWAs Medium N/A No No SFB
CVE-2026-5893 * Chromium: CVE-2026-5893 Race in V8 Medium N/A No No RCE
CVE-2026-5894 * Chromium: CVE-2026-5894 Inappropriate implementation in PDF Low N/A No No SFB
CVE-2026-5895 * Chromium: CVE-2026-5895 Incorrect security UI in Omnibox Low N/A No No Spoofing
CVE-2026-5896 * Chromium: CVE-2026-5896 Policy bypass in Audio Low N/A No No SFB
CVE-2026-5897 * Chromium: CVE-2026-5897 Incorrect security UI in Downloads Low N/A No No Spoofing
CVE-2026-5898 * Chromium: CVE-2026-5898 Incorrect security UI in Omnibox Low N/A No No Spoofing
CVE-2026-5899 * Chromium: CVE-2026-5899 Incorrect security UI in History Navigation Low N/A No No Spoofing
CVE-2026-5900 * Chromium: CVE-2026-5900 Policy bypass in Downloads Low N/A No No SFB
CVE-2026-5901 * Chromium: CVE-2026-5901 Policy bypass in DevTools Low N/A No No SFB
CVE-2026-5902 * Chromium: CVE-2026-5902 Race in Media Low N/A No No RCE
CVE-2026-5903 * Chromium: CVE-2026-5903 Policy bypass in IFrameSandbox Low N/A No No SFB
CVE-2026-5904 * Chromium: CVE-2026-5904 Use after free in V8 Low N/A No No RCE
CVE-2026-5905 * Chromium: CVE-2026-5905 Incorrect security UI in Permissions Low N/A No No Spoofing
CVE-2026-5906 * Chromium: CVE-2026-5906 Incorrect security UI in Omnibox Low N/A No No Spoofing
CVE-2026-5907 * Chromium: CVE-2026-5907 Insufficient data validation in Media Low N/A No No SFB
CVE-2026-5908 * Chromium: CVE-2026-5908 Integer overflow in Media Low N/A No No RCE
CVE-2026-5909 * Chromium: CVE-2026-5909 Integer overflow in Media Low N/A No No RCE
CVE-2026-5910 * Chromium: CVE-2026-5910 Integer overflow in Media Low N/A No No RCE
CVE-2026-5911 * Chromium: CVE-2026-5911 Policy bypass in ServiceWorkers Low N/A No No SFB
CVE-2026-5912 * Chromium: CVE-2026-5912 Integer overflow in WebRTC Low N/A No No RCE
CVE-2026-5913 * Chromium: CVE-2026-5913 Out of bounds read in Blink Low N/A No No Info
CVE-2026-5914 * Chromium: CVE-2026-5914 Type Confusion in CSS Low N/A No No RCE
CVE-2026-5915 * Chromium: CVE-2026-5915 Insufficient validation of untrusted input in WebML Low N/A No No SFB
CVE-2026-5918 * Chromium: CVE-2026-5918 Inappropriate implementation in Navigation Low N/A No No SFB
CVE-2026-5919 * Chromium: CVE-2026-5919 Insufficient validation of untrusted input in WebSockets Low N/A No No SFB
CVE-2026-33118 Microsoft Edge (Chromium-based) Spoofing Vulnerability Low 4.3 No No Spoofing

* Indicates this CVE had been released by a third party and is now being included in Microsoft releases.

† Indicates further administrative actions are required to fully address the vulnerability.


Looking at the other Critical-rated bugs in this month’s release, there are three Office-related bugs where the Preview Pane is once again listed as an exploit vector. I would still like to have a full-proof way of disabling the Preview Pane, but I don’t see that as an option. There’s a bug in the RDP client, but that involves connecting to a malicious RDP server. The bug in Active Directory requires authentication and a network adjacent attacker. The final Critical-rated bug is an interesting DoS in .NET Framework. An unauthenticated attacker could deny service over a network – presumably crippling any affected app made in .NET. You rarely see Critical-rated DoS bugs, but this one deserves the moniker.

Moving on to the other code execution bugs, you have quite a few open-and-own bugs in Office components, most notably Excel, where the Preview Pane is not an attack vector. The bug in SQL Server requires authentication, and as usual, additional steps are needed to ensure you have the correct update to remediate this vulnerability. The two bugs in Hyper-V almost reads like a privilege escalation since it allows unauthorized attackers to execute code locally. That’s the same for the bugs in the Windows Snipping Tool and the UPnP Device host.

More than half of this release addresses Elevation of Privilege (EoP) bugs. However, most simply lead to local attackers executing their code at SYSTEM-level privileges or administrative privileges, so there’s not much to add without further technical details about the bugs themselves. The bugs in SQL Server could allow an attacker to gain SQL sysadmin privileges. One of the kernel bugs simply states an attacker could “elevate privileges locally”. How obtuse. That’s similar for the bug in afd.sys and Desktop Windows Manager, but Microsoft also states that these bugs could crash an affected system. There are several bugs that result in a sandbox escape, including Windows Push Notifications, AFD for Winsock, Management Services, and User Interface Core. Of these, CVE-2026-26167 (Push Notifications) is the most notable — it's the only one with low attack complexity, meaning no race condition needed. The rest all require winning a race condition (AC:H). The bugs in UPnP are interesting as they allow attackers to gain access to a limited set of administrator-protected objects. Not a full escalation but definitely getting access to resources they shouldn’t. The vulnerability in the Brokering File System allows attackers to gain the level of the logged on user, so don’t do your normal activities as a user with admin privileges. The bug in Azure Monitor Agent leads to root-level access.

There are a dozen different security features bypass bugs in the April release. Some of these are obvious by the title alone. For example, the bugs in Windows Hello bypass safety features within the Hello app itself. The bug in the Biometric Service allows attackers to bypass biometric protections. The vulns in BitLocker and Secure Boot bypass protections in those components. The bug in Power Apps allows attackers to bypass a security warning dialog and trick targets into triggering an external protocol call that performs unintended actions on the user’s device. The bug in Windows Shell allows attackers to bypass Mark of the Web (MotW) protections. The bug in PowerShell could almost be described as a code execution bug as exploiting it bypasses dynamic-expression security checks, which could result in code execution. The vulnerability in the Windows Recovery Environment allows local attackers to bypass BitLocker device encryption. Finally, the bug in Virtualization‑Based Security (VBS) is the most interesting of the bunch – and not just because VBS is a (relatively) new feature. The problem allows attackers to manipulate allow a compromised Windows kernel to modify memory belonging to the secure kernel, breaking the intended isolation guarantees provided by VBS. Somewhat of a sandbox escape, but this time, you’re escaping from Virtual Trust Level 0 (VTL0) to Virtual Trust Level 1 (VTL1). Neat.

Moving on to the Information Disclosure bugs fixed this month, we have 20 different CVEs. Fortunately, most of these simply result in info leaks consisting of unspecified memory contents or memory addresses. While useful in crafting exploits, they aren’t exactly exciting on their own. There are also several bugs that disclose addresses from an object a contained in a sandboxed execution environment. This includes bugs in the Print Spooler, Package Catalog, and Web Account Manager. The bug in Dynamics 365 discloses the ever ineffable “sensitive information”. There are three different info disclosure bugs in UPnP. Two allow an attacker to read from the file system, while the third discloses anything available to the LOCAL SERVICE account. The final info disclosure bug resides in Copilot and Visual Studio and allows attackers to disclose the contents of the Model Context Protocol (MCP) when using Copilot. There are those who think MCP is dead (thanks to agentic AI agents), but if you’re using a custom MCP, I doubt you would want it leaked.

The April release contains just a handful of Spoofing bugs. Some, like the bugs in .NET, Active Directory, and Windows Shell, just say that they allow spoofing over a network. Others, like the bug in Windows Snipping Tool, say similar but also note that it could be used to relay NTLMv2 hashes. The patch for RDP notes that there are new warning dialogs coming this month. The bug in the Windows Admin Center would allow an attacker to interact with other tenant’s applications and content. Finally, the spoofing bug in SharePoint is another XSS issue.

There are eight DoS bugs in the April release, but as always, Microsoft provides no actionable information about the vulnerabilities. Microsoft does offer a mitigation for the http.sys bug that can be applied while you test and deploy the patch, but I would rely on the patch rather than the mitigation. Another exception is the bug for Connected User Experiences and Telemetry Service, which allows attackers to deny service locally rather than over the network.

The final(!) bug in the April release is a Tampering bug in WSUS that reads like a DoS. According to Microsoft, “An attacker can send specially crafted packets which could affect availability of the service and result in Denial of Service (DoS).” But sure – let’s call it Tampering.

No new advisories are being released this month.

Looking Ahead

I will be in Berlin for the next Patch Tuesday, which will be May 12, and I’ll provide my full thoughts then on what will hopefully be a smaller release than this one. Until then, stay safe, happy patching, and may all your reboots be smooth and clean!
❌